• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: rent one

Why is my connection speed slower?

TeamFlashRouters · Jun 4, 2019 ·

The encryption provided by a VPN connection almost always results in slower connection speed. In some cases you may have noticed that your computer or tablet was working faster when running a VPN client application or program, that is because a computer has a processor that is normally about 4-6x times as strong as a the processor on a router, and that is for managing a single VPN connection. A router has a smaller processor and is managing an entire network of devices. Encrypting an entire network does take considerable processing power.

Speed test results while connected to VPN are never going to be accurate. A speed test measures the rate at which a data packet travels from one server to another, however when you are connecting to VPN the data packets travel to an extra server where they are encrypted and then sent back into the route. We strongly recommend disabling the FlashRouter’s VPN connection when testing speeds to make sure there isn’t and issue with the router.

Connection Types

Ethernet: Wired ethernet connections will almost always be the most stable and reliable connection. To speed up your internet connection, use an ethernet cable to wire your devices to the FlashRouter.

Wireless (5.0GHz): The 5.0GHz WiFi frequency has less range than the standard 2.4GHz WiFi, but also transmits your internet connection at a significantly faster speed. If you were previously using the 2.4GHz network and experiencing slow speeds please connect to the 5GHz wireless network which should improve your speed.

Connect to the closest VPN server

Our supported VPN providers offer many servers in different countries and regions. If a server has slower connection speed we recommend connecting to the server closest to your actual location.

The process for changing servers is detailed in your provider’s setup instructions.

FlashRouters Privacy App

DD-WRT Manual VPN Configuration

Select a UDP server

UDP servers do not authenticate every data packets the way TCP servers do which results in faster connection speeds.

VPN provider server recommendation

Contact your VPN provider for a server recommendation that should provide the fastest speeds for you.
How to Access Your GL.iNet FlashRouter Settings

TeamFlashRouters · Feb 26, 2024 ·

This quick guide walk you through connecting to your GL.iNet FlashRouter (Flint, Slate, Beryl, or Marble) and logging into the admin settings page. You’ll use either WiFi or an Ethernet cable, then access the router dashboard through your browser.

Step 1. Connect Your Device to the Router

You can connect by WiFi or Ethernet:

  • WiFi: Look for a network name like FlashRouter24 or FlashRouter50
    • The WiFi password has been set to: Wireless#9483C
    • ⚠️ Be sure to capitalize the “W” in
  • Ethernet: Plug an Ethernet cable from your computer into one of the router’s LAN ports (usually marked or color-coded differently from the WAN port).

👉 Pro tip: Disconnect from any other WiFi networks during setup.

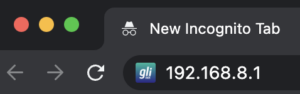
Step 2. Open the Router Login Page

  1. Open a web browser (Chrome, Safari, Firefox, Edge).
  2. In the address bar, type: 192.168.8.1
  3. Press Enter.
GL.iNet router access

This is the local router dashboard address (not a public website). If the page doesn’t load:

  • Try a different browser.
  • Clear your cache.
  • Ensure your device is connected to the FlashRouter network.

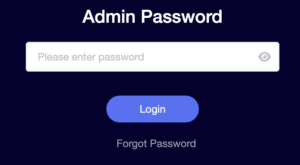
Step 3. Log In to the Router Settings

  • Default password: glopenwrt1 or openwrt
  • This is the factory default for all GL.iNet routers shipped by FlashRouters.
GL.iNet admin password enter

💡 Once you’re in, you can update your admin password in the settings for extra security.

Next Steps

Now that you’ve accessed your GL.iNet FlashRouter, you can:

  • Set up your VPN service
  • Customize your WiFi name and password
  • Adjust device controls and security settings

Check our support library for your specific VPN setup guide.

Wireless Access Point Setup

TeamFlashRouters · Apr 23, 2019 ·

A Wireless Access Point is a setup that has the FlashRouter using an existing network’s DHCP instead of assigning its own. The FlashRouter’s WAN/Internet port should be not be connected to your modem or other router while performing this setup.

Preparing for Wireless Access Point Setup

Locate the Local IP Address of the existing wireless network

Locate the Local IP Address of the existing router that the FlashRouter will be bridged to.

DD-WRT Router Setup for Wireless Access Point

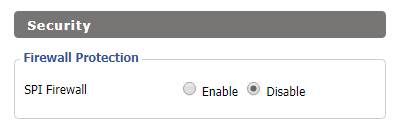
Disable Firewall

Navigate to Security > Firewall

Wireless Client Bridge Setup on FlashRouter DD-WRT - Disable Firewall
  1. Set SPI Firewall to Disable.
  2. Click Save.

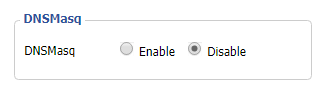
Disable DNSmasq

Navigate to Services > Services

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable DNSMasqButton
  1. Set DNSmasq to Disable.
  2. Click Save.

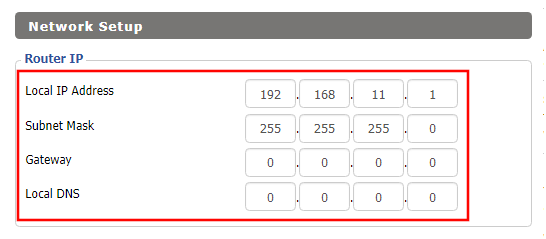
Change the FlashRouter's Local IP Address

Navigate to Setup > Basic Setup

Wireless Client Bridge Setup on FlashRouter DD-WRT - Set Local IP
  1. Set the Local IP Address to a different address on the same subnet as the existing network that you noted early. (example: if the existing network is 192.168.1.1 then set the Local IP Address to 192.168.1.2)
  2. Set the Gateway to the Local IP Address of the existing network. (example: 192.168.1.1)
  3. Set the Local DNS to the Local IP Address of the existing network. (example: 192.168.1.1)
  4. Click Save.

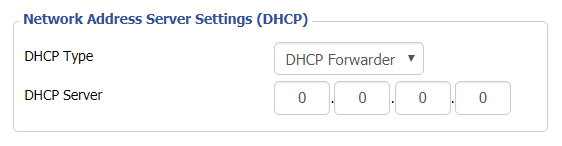
Change the FlashRouter's DHCP settings

DHCP Forwarder Setup for DD-WRT
  1. Set the DHCP Type to DHCP Forwarder.
  2. Click Save.

Change the FlashRouter's Operating Mode

Navigate to Setup > Advanced Routing

DHCP Forwarder Setup for DD-WRT
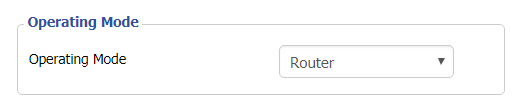
  1. Set the Operating Mode to Router.
  2. Click Apply Settings.

Reboot your FlashRouter

  • Power off the FlashRouter for 30 seconds and connect from the other router’s LAN port to one of the FlashRouter’s LAN port then power it back on.  When it boots back up you will be able to access the FlashRouter’s settings at the new Local IP Address that you set.

Back up your settings

Navigate to the Administration > Backup page.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Surfshark Manual OpenVPN Setup

TeamFlashRouters · Apr 24, 2019 ·

Preparing for Manual Surfshark Setup

Obtain your Surfshark OpenVPN information

If you are not already an Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

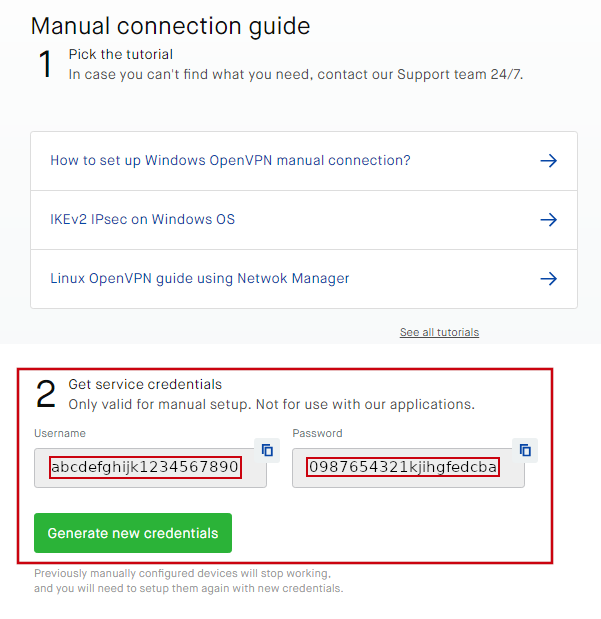
2. Successfully log in with your account information and Navigate to the Manual Connection Guide. Here you will find the OpenVPN Specific Username and Password required for manual configuration.

FlashRouters Privacy App - SurfShark OpenVPN Specific Username and Password

Surfshark Server Addresses

View a full list of Surfshark servers.

United States

Atlanta:
us-atl.prod.surfshark.com
Buffalo:
us-buf.prod.surfshark.com
Chicago:
us-chi.prod.surfshark.com
Dallas:
us-dal.prod.surfshark.com
Las Vegas:
us-las.prod.surfshark.com
Los Angeles:
us-lax.prod.surfshark.com
Miami:
us-mia.prod.surfshark.com
New York City:
us-nyc.prod.surfshark.com
Phoenix:
us-phx.prod.surfshark.com
San Fransisco:
us-sfo.prod.surfshark.com
Seattle:
us-sea.prod.surfshark.com

DD-WRT Router Setup for Surfshark

Navigate to Services > VPN

Enter Surfshark settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Surfshark connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

None

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
b02cb1d7c6fee5d4f89b8de72b51a8d0
c7b282631d6fc19be1df6ebae9e2779e
6d9f097058a31c97f57f0c35526a44ae
09a01d1284b50b954d9246725a1ead1f
f224a102ed9ab3da0152a15525643b2e
ee226c37041dc55539d475183b889a10
e18bb94f079a4a49888da566b9978346
0ece01daaf93548beea6c827d9674897
e7279ff1a19cb092659e8c1860fbad0d
b4ad0ad5732f1af4655dbd66214e552f
04ed8fd0104e1d4bf99c249ac229ce16
9d9ba22068c6c0ab742424760911d463
6aafb4b85f0c952a9ce4275bc821391a
a65fcd0d2394f006e3fba0fd34c4bc4a
b260f4b45dec3285875589c97d3087c9
134d3a3aa2f904512e85aa2dc2202498
-----END OpenVPN Static key V1-----

Additional Config

remote-cert-tls server
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping-timer-rem
reneg-sec 0
cipher AES-256-GCM
log /tmp/vpn.log

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFTTCCAzWgAwIBAgIJAMs9S3fqwv+mMA0GCSqGSIb3DQEBCwUAMD0xCzAJBgNV
BAYTAlZHMRIwEAYDVQQKDAlTdXJmc2hhcmsxGjAYBgNVBAMMEVN1cmZzaGFyayBS
b290IENBMB4XDTE4MDMxNDA4NTkyM1oXDTI4MDMxMTA4NTkyM1owPTELMAkGA1UE
BhMCVkcxEjAQBgNVBAoMCVN1cmZzaGFyazEaMBgGA1UEAwwRU3VyZnNoYXJrIFJv
b3QgQ0EwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDEGMNj0aisM63o
SkmVJyZPaYX7aPsZtzsxo6m6p5Wta3MGASoryRsBuRaH6VVa0fwbI1nw5ubyxkua
Na4v3zHVwuSq6F1p8S811+1YP1av+jqDcMyojH0ujZSHIcb/i5LtaHNXBQ3qN48C
c7sqBnTIIFpmb5HthQ/4pW+a82b1guM5dZHsh7q+LKQDIGmvtMtO1+NEnmj81BAp
FayiaD1ggvwDI4x7o/Y3ksfWSCHnqXGyqzSFLh8QuQrTmWUm84YHGFxoI1/8AKdI
yVoB6BjcaMKtKs/pbctk6vkzmYf0XmGovDKPQF6MwUekchLjB5gSBNnptSQ9kNgn
TLqi0OpSwI6ixX52Ksva6UM8P01ZIhWZ6ua/T/tArgODy5JZMW+pQ1A6L0b7egIe
ghpwKnPRG+5CzgO0J5UE6gv000mqbmC3CbiS8xi2xuNgruAyY2hUOoV9/BuBev8t
tE5ZCsJH3YlG6NtbZ9hPc61GiBSx8NJnX5QHyCnfic/X87eST/amZsZCAOJ5v4EP
SaKrItt+HrEFWZQIq4fJmHJNNbYvWzCE08AL+5/6Z+lxb/Bm3dapx2zdit3x2e+m
iGHekuiE8lQWD0rXD4+T+nDRi3X+kyt8Ex/8qRiUfrisrSHFzVMRungIMGdO9O/z
CINFrb7wahm4PqU2f12Z9TRCOTXciQIDAQABo1AwTjAdBgNVHQ4EFgQUYRpbQwyD
ahLMN3F2ony3+UqOYOgwHwYDVR0jBBgwFoAUYRpbQwyDahLMN3F2ony3+UqOYOgw
DAYDVR0TBAUwAwEB/zANBgkqhkiG9w0BAQsFAAOCAgEAn9zV7F/XVnFNZhHFrt0Z
S1Yqz+qM9CojLmiyblMFh0p7t+Hh+VKVgMwrz0LwDH4UsOosXA28eJPmech6/bjf
ymkoXISy/NUSTFpUChGO9RabGGxJsT4dugOw9MPaIVZffny4qYOc/rXDXDSfF2b+
303lLPI43y9qoe0oyZ1vtk/UKG75FkWfFUogGNbpOkuz+et5Y0aIEiyg0yh6/l5Q
5h8+yom0HZnREHhqieGbkaGKLkyu7zQ4D4tRK/mBhd8nv+09GtPEG+D5LPbabFVx
KjBMP4Vp24WuSUOqcGSsURHevawPVBfgmsxf1UCjelaIwngdh6WfNCRXa5QQPQTK
ubQvkvXONCDdhmdXQccnRX1nJWhPYi0onffvjsWUfztRypsKzX4dvM9k7xnIcGSG
EnCC4RCgt1UiZIj7frcCMssbA6vJ9naM0s7JF7N3VKeHJtqe1OCRHMYnWUZt9vrq
X6IoIHlZCoLlv39wFW9QNxelcAOCVbD+19MZ0ZXt7LitjIqe7yF5WxDQN4xru087
FzQ4Hfj7eH1SNLLyKZkA1eecjmRoi/OoqAt7afSnwtQLtMUc2bQDg6rHt5C0e4dC
LqP/9PGZTSJiwmtRHJ/N5qYWIh9ju83APvLm/AGBTR2pXmj9G3KdVOkpIC7L35dI
623cSEC3Q3UZutsEm/UplsM=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Surfshark connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Surfshark server

  1. Visit the Surfshark Manual setup page and scroll down to Section 3.
  2. Copy and paste one of the server IP Address into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Cudy Internet Setup

TeamFlashRouters · Feb 26, 2024 ·

Follow this article when you receive your new Cudy FlashRouter to connect it to the Internet.

1. Connect the ethernet cable that came with the router from an open LAN ethernet port on your ISP modem or other router to the WAN port if you purchased a Cudy AX3000 or to ethernet port #1 of the device marked Primary if you purchased a Cudy M1800 or Cudy M3000.

Cudy Mesh internet wiring

2. Connect the power to the router and wait about 2 minutes for the router to fully boot up.

3. Connect your computer, phone, or tablet to the Cudy router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

4. Once connected via wireless or ethernet on your device open your browser and go to 192.168.10.1

Cudy local IP access

5. Enter openwrt as the admin password to access the Cudy firmware settings.

Cudy router access

6. Verify that your Cudy FlashRouter is reporting as Internet and WAN Connected.

Cudy Verify Internet

6. Verify that your Cudy FlashRouter is reporting as Internet and WAN Connected.

7. If you purchased a Cudy M1800 or Cudy M3000 mesh package you can now take the unit labeled Node to the location you want it connecting from and power it up. It will connect to the Primary network that was just setup automatically. You will then see the Mesh Units number increase according to the number that you have purchased shortly.

Cudy Verify Mesh connection

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Cudy Access Router Settings

TeamFlashRouters · Feb 26, 2024 ·

Follow this guide to access the router settings of your Cudy FlashRouter.

1. Connect your computer, phone, or tablet to the Cudy router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to 192.168.10.1

Cudy local IP access

3. Enter openwrt1 or openwrt as the admin password to access the Cudy firmware settings.

Cudy router access

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Cudy Change Wi-Fi name and password

TeamFlashRouters · Feb 26, 2024 ·

Follow this guide to change the Wi-Fi name and password on your Cudy FlashRouter.

1. Connect your computer, phone, or tablet to the Cudy router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to 192.168.10.1

Cudy local IP access

3. Enter openwrt as the admin password to access the Cudy firmware settings.

Cudy router access

3. Click General Settings.

Cudy General Settings

4. Click Wireless.

Cudy Wireless tab

5. Change the SSID and Password fields for both 2.4GHz and 5GHz bands.The SSIDs should be unique and NOT a duplicate of an existing network. Click Save & Apply.

Cudy Change Wifi Name and password

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PrivateInternetAccess (PIA) Cudy OpenVPN Setup

TeamFlashRouters · Feb 29, 2024 ·

Preparing for PIA Cudy Setup

Download your PIA .ovpn file

If you are not already a PIA user Sign Up Now.

1. Log in to your account on the PIA website.

PIA login

2. Successfully log in with your account information then go to PIA’s OpenVPN Config Generator.

3. On the OpenVPN Configuration Generator select the following:

OpenVPN Version: OpenVPN 2.4 or newer

Select Platform: Linux

Select Region: Choose the server location you’d like to connect to

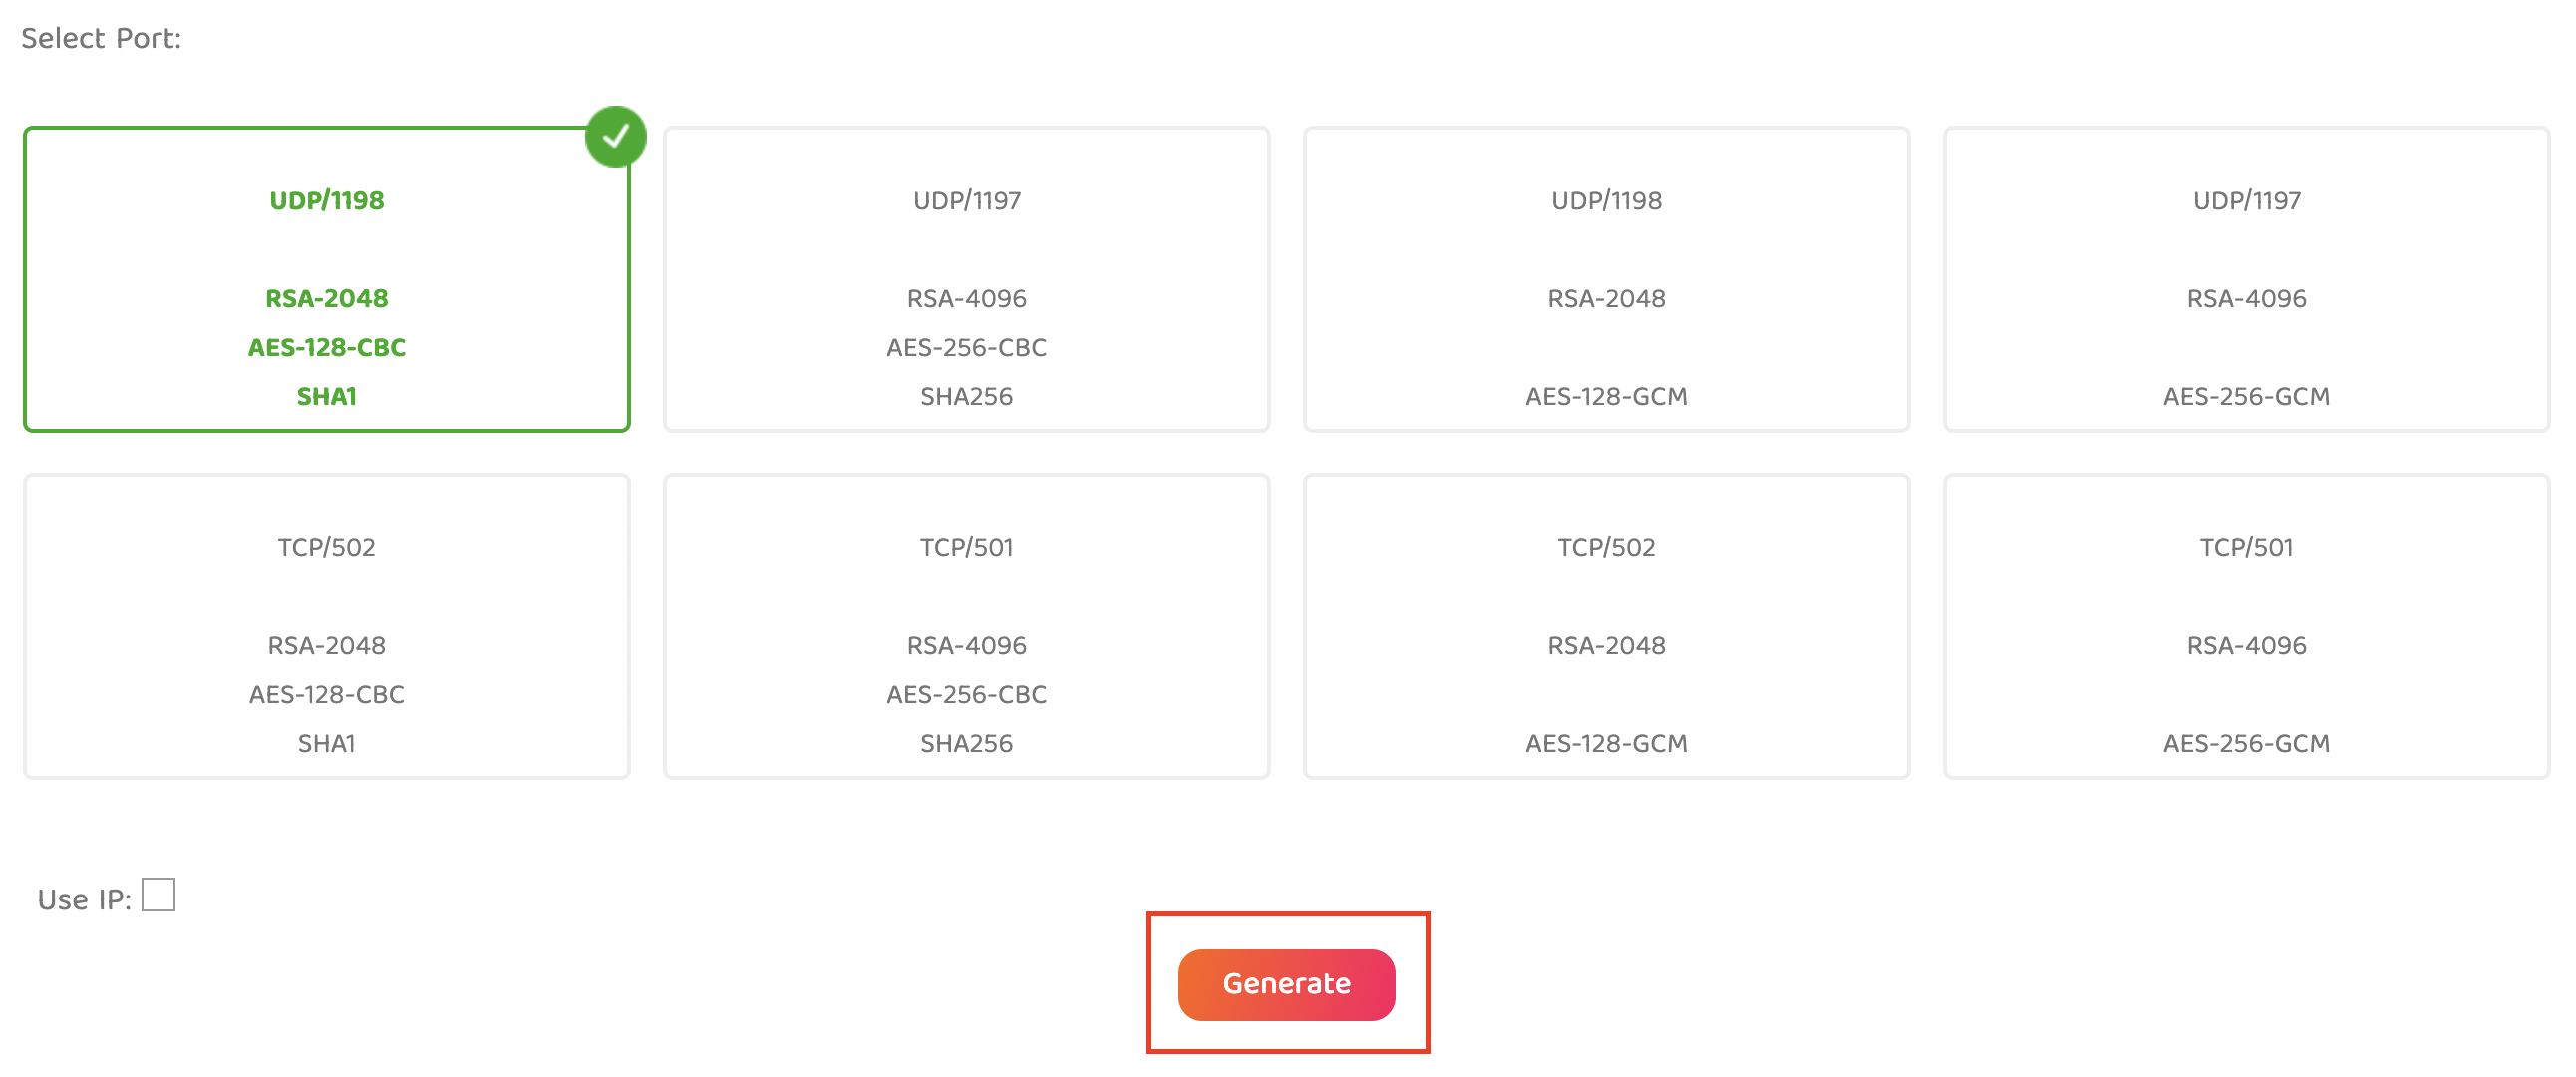
Select Port: Typically we recommend UDP/1198 RSA-2048 AES-128-CBC SHA1 for best speeds but feel free to select the one you want to use.

4. Click Generate to download the .ovpn file. Do not open this file once it is downloaded.

PIA Generate .ovpn file

Cudy Router Setup for PIA

Login to Cudy firmware settings in a browser on any computer or smart device connected to the Cudy FlashRouter’s network.

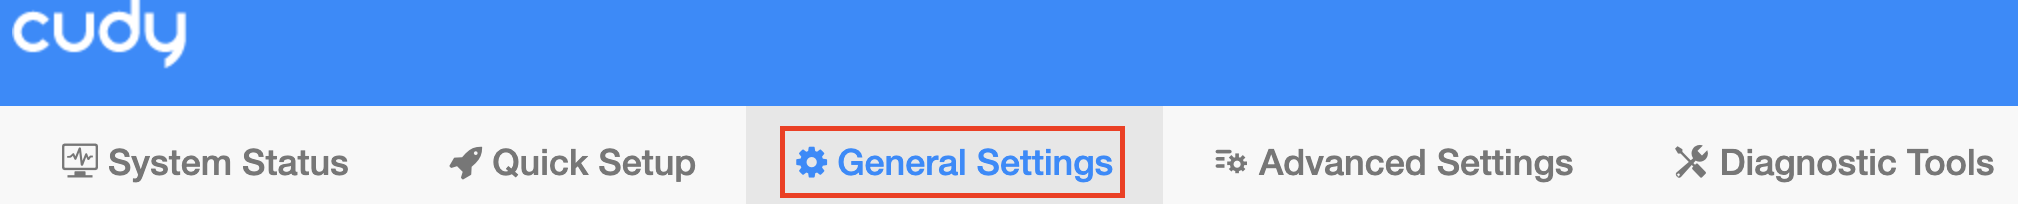
1. Click General Settings.

Cudy General Settings

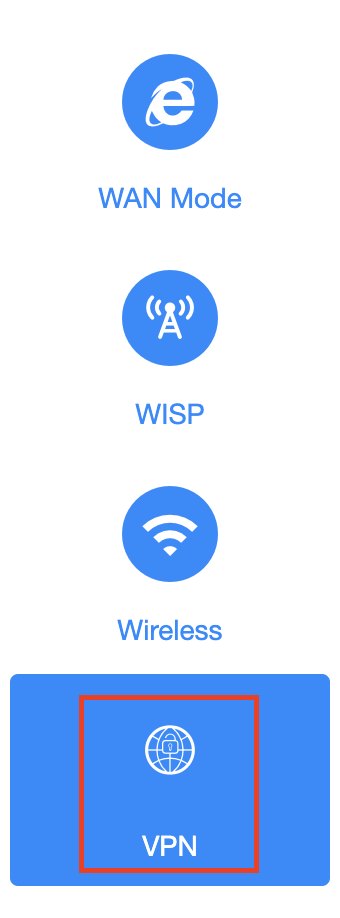
2. Click VPN.

Cudy VPN Tab

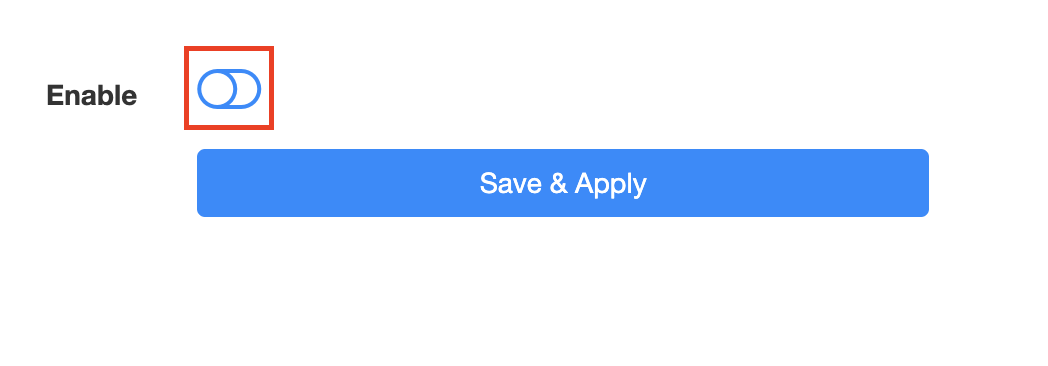
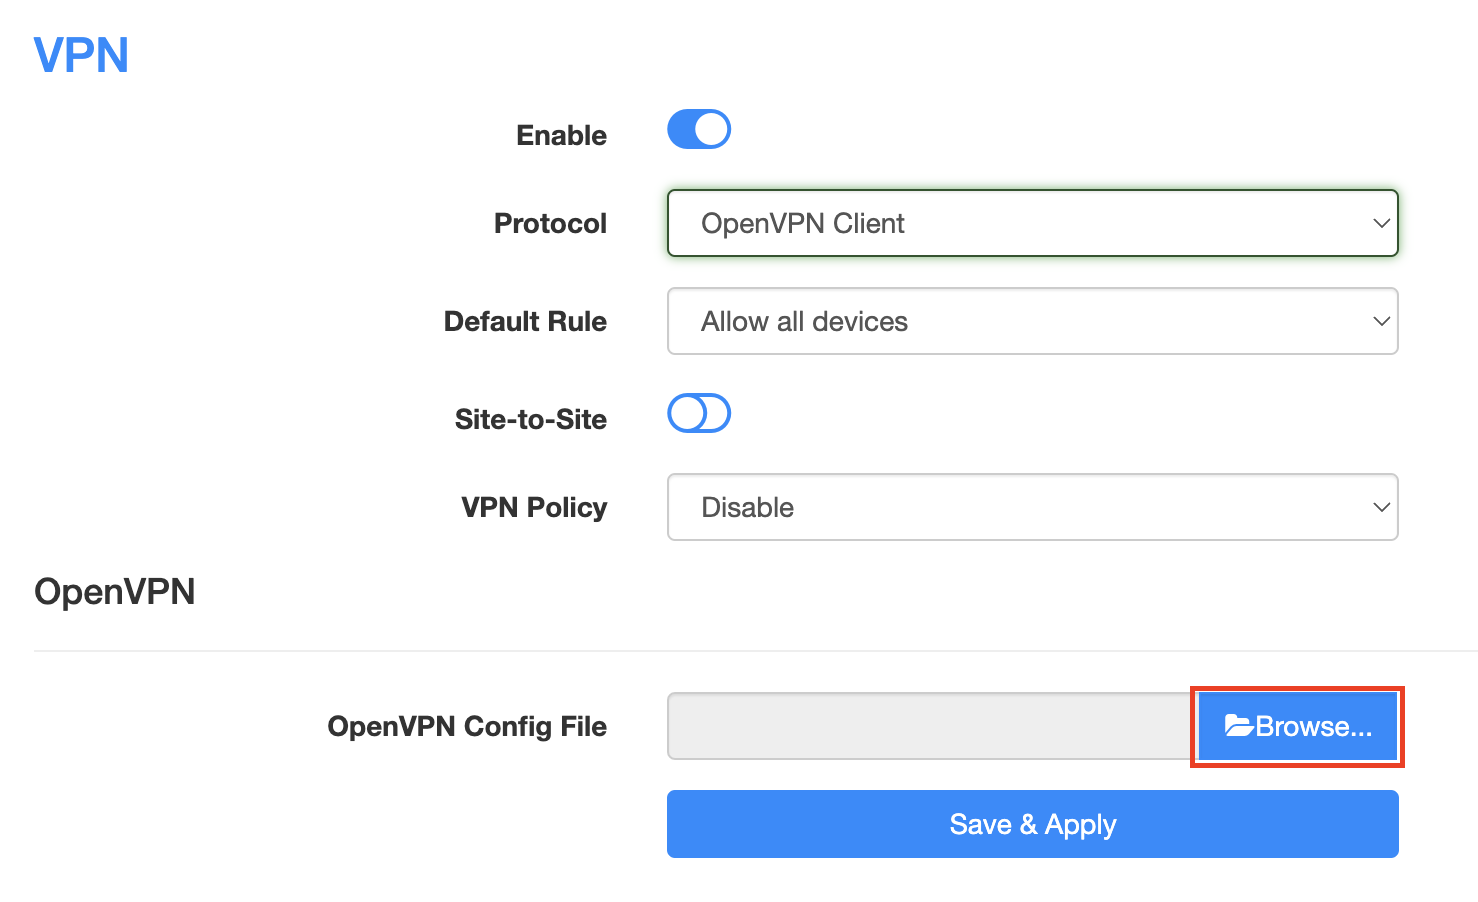
3. Toggle the Enable switch to On.

Cudy enable VPN

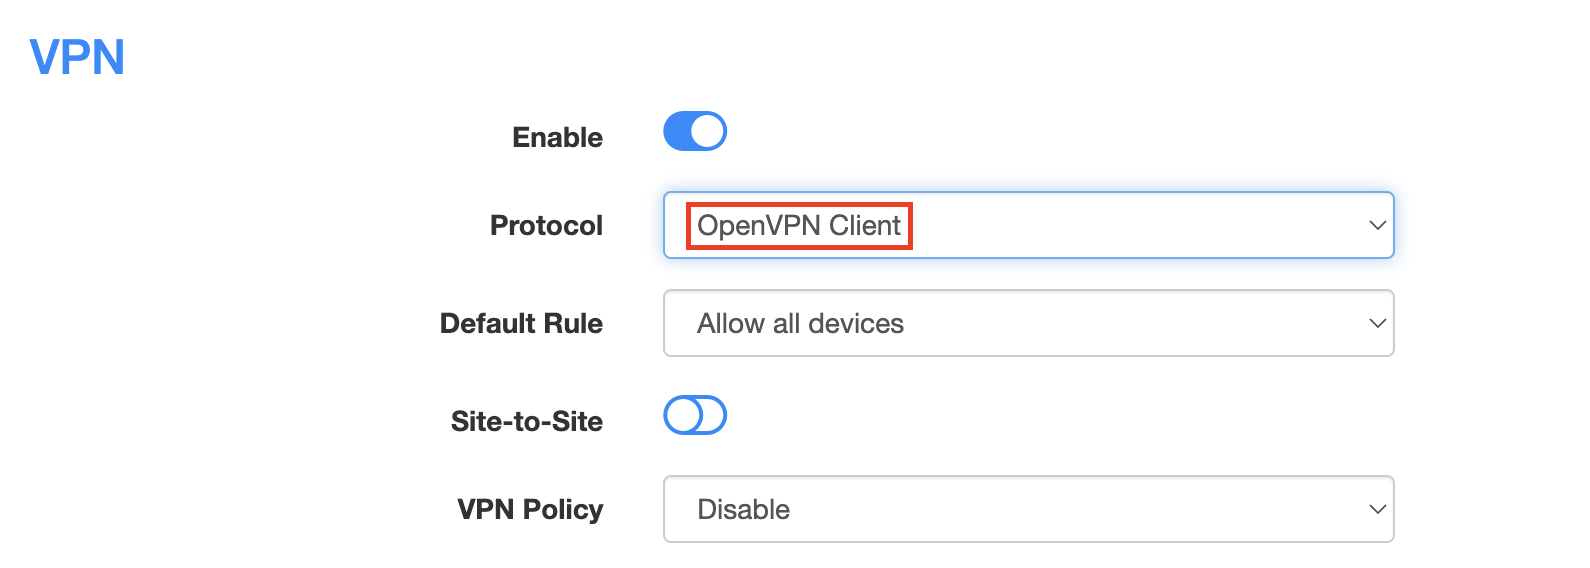
4. Select OpenVPN Client from the Protocol dropdown.

Cudy select OpenVPN Client

5. Click Browse and select the .ovpn file you downloaded earlier. You should see the server file name listed next to Current Config File after doing so.

Cudy OpenVPN Browse button

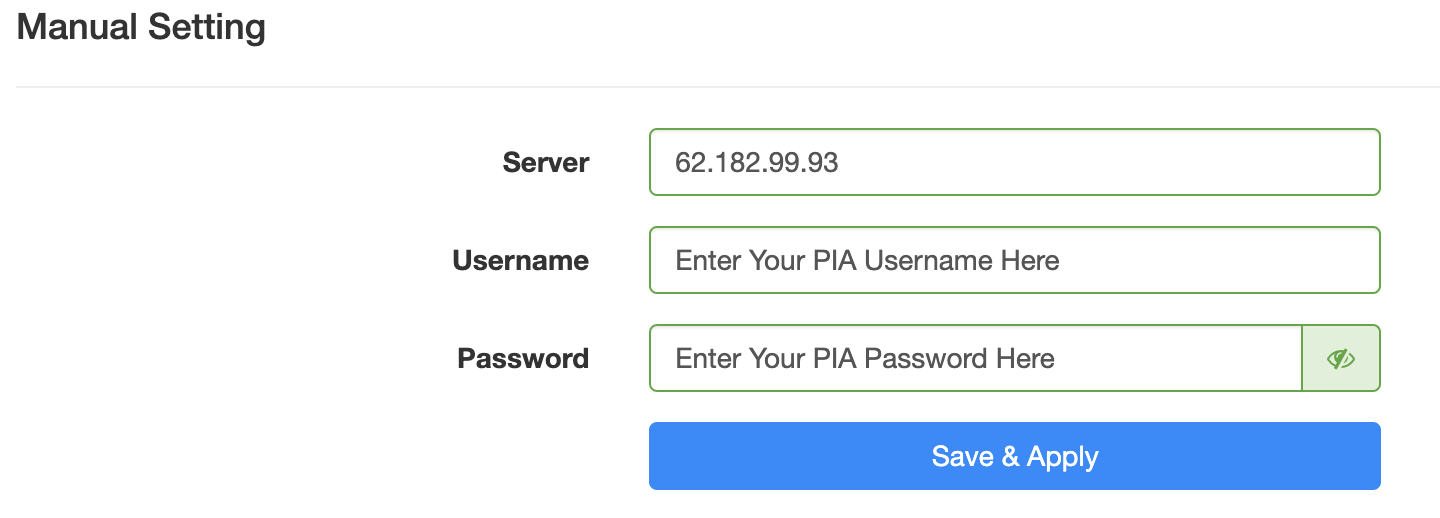
6. Enter your PIA account login username and password in the Username and Password.

Cudy PIA enter username and password

7. Click Save & Apply at the bottom of the page.

Verify a successful PIA connection

  1. You should now see a CONNECTED message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

How to change the PIA server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PrivateInternetAccess (PIA) Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual PIA Setup

Verify your PIA login information

If you are not already a PIA user Sign Up Now.

Log in to your account on the PIA website.

FlashRouters Privacy App - PIA Login

PIA Server Addresses

The below servers are the only servers compatible with PIA router connections. Dedicated IP Addresses are not able to connect via routers.

United States

us-california.privacy.network
us-newjersey.privacy.network
us-chicago.privacy.network
us-texas.privacy.network
us-florida.privacy.network
us-seattle.privacy.network
us3.privacy.network
us-siliconvalley.privacy.network
us-newyorkcity.privacy.network
us-washingtondc.privacy.network
us-atlanta.privacy.network
us-houston.privacy.network
us-denver.privacy.network

United Kingdom

uk-london.privacy.network
uk-manchester.privacy.network

Canada

ca-toronto.privacy.network
ca-montreal.privacy.network

Australia

au-sydney.privacy.network
aus-melbourne.privacy.network
aus-perth.privacy.network

Germany

de-berlin.privacy.network
de-frankfurt.privacy.network

Rest of the World

ae.privacy.network
austria.privacy.network
dz.privacy.network
ad.privacy.network
ar.privacy.network
yerevan.privacy.network
bahamas.privacy.network
bangladesh.privacy.network
brussels.privacy.network
sofia.privacy.network
cambodia.privacy.network
china.privacy.network
cyprus.privacy.network
czech.privacy.network
denmark.privacy.network
egypt.privacy.network
fi.privacy.network
france.privacy.network
georgia.privacy.network
greenland.privacy.network
hungary.privacy.network
is.privacy.network
in.privacy.network
iran.privacy.network
ireland.privacy.network
man.privacy.network
israel.privacy.network
italy.privacy.network
japan.privacy.network
kazakhstan.privacy.network
liechtenstein.privacy.network
lu.privacy.network
macau.privacy.network
malta.privacy.network
mexico.privacy.network
md.privacy.network
monaco.privacy.network
mongolia.privacy.network
montenegro.privacy.network
morocco.privacy.network
nl-amsterdam.privacy.network
nz.privacy.network
nigeria.privacy.network
no.privacy.network
panama.privacy.network
philippines.privacy.network
poland.privacy.network
qatar.privacy.network
ro.privacy.network
rs.privacy.network
saudiarabia.privacy.network
spain.privacy.network
srilanka.privacy.network
sweden.privacy.network
swiss.privacy.network
sg.privacy.network
tr.privacy.network
taiwan.privacy.network
ua.privacy.network
venezuela.privacy.network
vietnam.privacy.network
za.privacy.network

DD-WRT Router Setup for PIA

Navigate to Services > VPN

PIA offers two different Encryption levels.
Default Encryption (AES-128) typically provides faster speeds.
Strong Encryption (AES-256) provides stronger encryption.
Follow the table below of the one that fits your needs.

Enter PIA settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1198

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA1

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFqzCCBJOgAwIBAgIJAKZ7D5Yv87qDMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzM1
MThaFw0zNDA0MTIxNzM1MThaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAPXD
L1L9tX6DGf36liA7UBTy5I869z0UVo3lImfOs/GSiFKPtInlesP65577nd7UNzzX
lH/P/CnFPdBWlLp5ze3HRBCc/Avgr5CdMRkEsySL5GHBZsx6w2cayQ2EcRhVTwWp
cdldeNO+pPr9rIgPrtXqT4SWViTQRBeGM8CDxAyTopTsobjSiYZCF9Ta1gunl0G/
8Vfp+SXfYCC+ZzWvP+L1pFhPRqzQQ8k+wMZIovObK1s+nlwPaLyayzw9a8sUnvWB
/5rGPdIYnQWPgoNlLN9HpSmsAcw2z8DXI9pIxbr74cb3/HSfuYGOLkRqrOk6h4RC
OfuWoTrZup1uEOn+fw8CAwEAAaOCAVQwggFQMB0GA1UdDgQWBBQv63nQ/pJAt5tL
y8VJcbHe22ZOsjCCAR8GA1UdIwSCARYwggESgBQv63nQ/pJAt5tLy8VJcbHe22ZO
sqGB7qSB6zCB6DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAkNBMRMwEQYDVQQHEwpM
b3NBbmdlbGVzMSAwHgYDVQQKExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4G
A1UECxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBAMTF1ByaXZhdGUg
SW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQpExdQcml2YXRlIEludGVybmV0IEFjY2Vz
czEvMC0GCSqGSIb3DQEJARYgc2VjdXJlQHByaXZhdGVpbnRlcm5ldGFjY2Vzcy5j
b22CCQCmew+WL/O6gzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBDQUAA4IBAQAn
a5PgrtxfwTumD4+3/SYvwoD66cB8IcK//h1mCzAduU8KgUXocLx7QgJWo9lnZ8xU
ryXvWab2usg4fqk7FPi00bED4f4qVQFVfGfPZIH9QQ7/48bPM9RyfzImZWUCenK3
7pdw4Bvgoys2rHLHbGen7f28knT2j/cbMxd78tQc20TIObGjo8+ISTRclSTRBtyC
GohseKYpTS9himFERpUgNtefvYHbn70mIOzfOJFTVqfrptf9jXa9N8Mpy3ayfodz
1wiqdteqFXkTYoSDctgKMiZ6GdocK9nMroQipIQtpnwd4yBDWIyC6Bvlkrq5TQUt
YDQ8z9v+DMO6iwyIDRiU
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter PIA settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1197

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIHqzCCBZOgAwIBAgIJAJ0u+vODZJntMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzQw
MzNaFw0zNDA0MTIxNzQwMzNaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBALVk
hjumaqBbL8aSgj6xbX1QPTfTd1qHsAZd2B97m8Vw31c/2yQgZNf5qZY0+jOIHULN
De4R9TIvyBEbvnAg/OkPw8n/+ScgYOeH876VUXzjLDBnDb8DLr/+w9oVsuDeFJ9K
V2UFM1OYX0SnkHnrYAN2QLF98ESK4NCSU01h5zkcgmQ+qKSfA9Ny0/UpsKPBFqsQ
25NvjDWFhCpeqCHKUJ4Be27CDbSl7lAkBuHMPHJs8f8xPgAbHRXZOxVCpayZ2SND
fCwsnGWpWFoMGvdMbygngCn6jA/W1VSFOlRlfLuuGe7QFfDwA0jaLCxuWt/BgZyl
p7tAzYKR8lnWmtUCPm4+BtjyVDYtDCiGBD9Z4P13RFWvJHw5aapx/5W/CuvVyI7p
Kwvc2IT+KPxCUhH1XI8ca5RN3C9NoPJJf6qpg4g0rJH3aaWkoMRrYvQ+5PXXYUzj
tRHImghRGd/ydERYoAZXuGSbPkm9Y/p2X8unLcW+F0xpJD98+ZI+tzSsI99Zs5wi
jSUGYr9/j18KHFTMQ8n+1jauc5bCCegN27dPeKXNSZ5riXFL2XX6BkY68y58UaNz
meGMiUL9BOV1iV+PMb7B7PYs7oFLjAhh0EdyvfHkrh/ZV9BEhtFa7yXp8XR0J6vz
1YV9R6DYJmLjOEbhU8N0gc3tZm4Qz39lIIG6w3FDAgMBAAGjggFUMIIBUDAdBgNV
HQ4EFgQUrsRtyWJftjpdRM0+925Y6Cl08SUwggEfBgNVHSMEggEWMIIBEoAUrsRt
yWJftjpdRM0+925Y6Cl08SWhge6kgeswgegxCzAJBgNVBAYTAlVTMQswCQYDVQQI
EwJDQTETMBEGA1UEBxMKTG9zQW5nZWxlczEgMB4GA1UEChMXUHJpdmF0ZSBJbnRl
cm5ldCBBY2Nlc3MxIDAeBgNVBAsTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAw
HgYDVQQDExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UEKRMXUHJpdmF0
ZSBJbnRlcm5ldCBBY2Nlc3MxLzAtBgkqhkiG9w0BCQEWIHNlY3VyZUBwcml2YXRl
aW50ZXJuZXRhY2Nlc3MuY29tggkAnS7684Nkme0wDAYDVR0TBAUwAwEB/zANBgkq
hkiG9w0BAQ0FAAOCAgEAJsfhsPk3r8kLXLxY+v+vHzbr4ufNtqnL9/1Uuf8NrsCt
pXAoyZ0YqfbkWx3NHTZ7OE9ZRhdMP/RqHQE1p4N4Sa1nZKhTKasV6KhHDqSCt/dv
Em89xWm2MVA7nyzQxVlHa9AkcBaemcXEiyT19XdpiXOP4Vhs+J1R5m8zQOxZlV1G
tF9vsXmJqWZpOVPmZ8f35BCsYPvv4yMewnrtAC8PFEK/bOPeYcKN50bol22QYaZu
LfpkHfNiFTnfMh8sl/ablPyNY7DUNiP5DRcMdIwmfGQxR5WEQoHL3yPJ42LkB5zs
6jIm26DGNXfwura/mi105+ENH1CaROtRYwkiHb08U6qLXXJz80mWJkT90nr8Asj3
5xN2cUppg74nG3YVav/38P48T56hG1NHbYF5uOCske19F6wi9maUoto/3vEr0rnX
JUp2KODmKdvBI7co245lHBABWikk8VfejQSlCtDBXn644ZMtAdoxKNfR2WTFVEwJ
iyd1Fzx0yujuiXDROLhISLQDRjVVAvawrAtLZWYK31bY7KlezPlQnl/D9Asxe85l
8jO5+0LdJ6VyOs/Hd4w52alDW/MFySDZSfQHMTIc30hLBJ8OnCEIvluVQQ2UQvoW
+no177N9L2Y+M9TcTA62ZyMXShHQGeh20rb4kK8f+iFX8NxtdHVSkxMEFSfDDyQ=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PIA connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the PIA server

  1. Copy the new PIA server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

TP-Link Access Router Settings

TeamFlashRouters · Apr 11, 2024 ·

Follow this guide to access the router settings of your TP-Link FlashRouter.

1. Connect your computer, phone, or tablet to the TP-Link router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

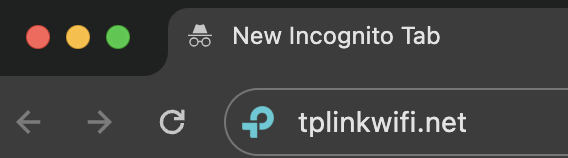
2. Once connected via wireless or ethernet on your device open your browser and go to tplinkwifi.net

TP-Link URL Access

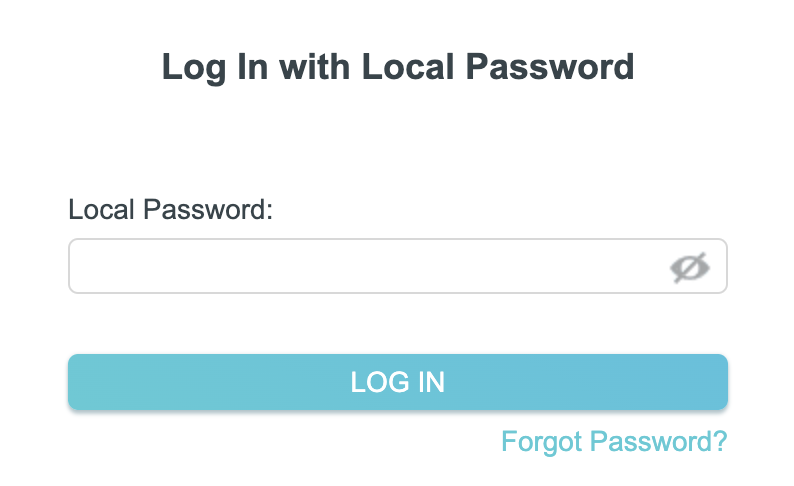
3. Enter tp-link as the admin password to access the TP-Link firmware settings.

TP-Link admin password

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

TP-Link Internet Setup

TeamFlashRouters · Apr 11, 2024 ·

Follow this article when you receive your new TP-Link FlashRouter to connect it to the Internet.

1. Connect the ethernet cable that came with the router from an open LAN ethernet port on your ISP modem or other router to the WAN port of the TP-Link.

2. Connect the power to the router and wait about 2 minutes for the router to fully boot up.

3. Connect your computer, phone, or tablet to the TP-Link router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

4. Once connected via wireless or ethernet on your device open your browser and go to tplinkwifi.net

TP-Link URL Access

5. Enter tp-link as the admin password to access the TP-Link firmware settings.

TP-Link admin password

6. Verify that your TP-Link FlashRouter is reporting as Internet and WAN Connected.

TP-Link Internet Connected

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero NordVPN Not Connecting or Showing Timeout Errors

Dave · Sep 22, 2026 ·

If NordVPN will not connect on Privacy Hero, shows a timeout error, remains stuck on Connecting, or displays Failed, the Privacy Hero router itself may still be working normally.

NordVPN connections can occasionally stop working when servers are placed into maintenance, removed or cycled out of service, account credentials change, or a previously saved NordVPN access token or manual service credential is no longer valid.

Start by confirming that Privacy Hero has normal internet access, then troubleshoot the NordVPN connection.


Jump to a Section

  • Confirm Privacy Hero Has Internet
  • Reconnect NordVPN
  • Try Another NordVPN Server
  • Update Your NordLynx Token
  • Update OpenVPN Credentials
  • Recent NordVPN Account Changes
  • Verify the VPN Connection

First: Confirm Privacy Hero Has Internet

Before changing your NordVPN settings, confirm that Privacy Hero itself has normal internet access.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. If the VPN Kill Switch is enabled, temporarily turn it Off.
  4. Turn the failed NordVPN connection off.
  5. Connect a device to the Privacy Hero network.
  6. Test normal internet access.

If internet access works normally with NordVPN and the Kill Switch disabled, the underlying Privacy Hero internet connection is working. Continue troubleshooting the NordVPN connection.

If your internet stopped working because NordVPN failed while the VPN Kill Switch was enabled, follow our Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting guide.

Reconnect NordVPN

A temporary NordVPN server or connection issue may resolve without changing your account information.

  1. Open the VPN section at app.privacyhero.com.
  2. Turn the NordVPN connection off.
  3. Wait a few seconds.
  4. Turn NordVPN back on.
  5. Allow the connection time to establish.
  6. Check whether the VPN status changes to Connected.

If NordVPN still shows Failed, Connecting, or a timeout error, continue with the steps below.

Try Another NordVPN Server

NordVPN regularly maintains, replaces, and cycles servers in its network. A specific NordVPN server that worked previously may eventually be taken offline, removed, or temporarily unavailable.

If your Privacy Hero NordVPN connection is configured to use a specific server and suddenly stops working, try another server or return to the normal country selection.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. Select your NordVPN connection.
  4. If you previously entered a specific NordVPN server under Advanced Options, remove or replace that server.
  5. Select the country or location you want to use.
  6. Save the settings.
  7. Reconnect NordVPN.
  8. Check whether the status changes to Connected.

If you specifically need to use an individual NordVPN server, make sure that server is still active before continuing to use it.

Important: A previously working specific server should not be assumed to remain available indefinitely. NordVPN may change its server network over time.

Update Your NordVPN Token for NordLynx

Privacy Hero uses a NordVPN access token to authenticate NordLynx connections.

If the saved token is expired, revoked, replaced, or otherwise no longer valid, NordLynx may show Failed, Connecting, or a timeout error.

Generating a new token is a good troubleshooting step if your NordVPN account information has changed or the existing token is no longer working.

  1. Sign in to your NordVPN account.
  2. Open the NordVPN Access Tokens page.
  3. Generate a new access token.
  4. Select Doesn’t expire if NordVPN provides that option.
  5. Copy the new token.
  6. Open app.privacyhero.com.
  7. Open the NordVPN settings.
  8. Confirm that NordLynx is the selected protocol.
  9. Replace the existing token with the newly generated token.
  10. Save the settings.
  11. Reconnect NordVPN.

Important: NordVPN access tokens are sensitive account credentials. Do not post or share your token publicly.

For complete setup instructions, see Privacy Hero NordVPN / NordLynx Setup.

Update NordVPN Manual Service Credentials for OpenVPN

If you are using OpenVPN instead of NordLynx, Privacy Hero uses NordVPN’s Manual Service Credentials.

These are different from the email address and password you normally use to sign in to the NordVPN website or application.

If the saved credentials are no longer valid, update them:

  1. Sign in to your NordVPN account.
  2. Open NordVPN Manual Service Credentials.
  3. Copy the current service username and password.
  4. Open app.privacyhero.com.
  5. Open your NordVPN settings.
  6. Confirm that OpenVPN is the selected protocol.
  7. Replace the existing manual service credentials with the current credentials from NordVPN.
  8. Save the settings.
  9. Reconnect NordVPN.

Do not enter your regular NordVPN website email address and password in place of the manual service credentials.

Did You Recently Change Your NordVPN Account Information?

If NordVPN stopped connecting after an account change, update the authentication information stored in Privacy Hero.

This is especially important after changes such as:

  • Changing your NordVPN account password.
  • Changing or updating NordVPN account security settings.
  • Generating or replacing NordVPN access tokens.
  • Changes to NordVPN manual service credentials.
  • Renewing, changing, or restoring your NordVPN subscription.

The credentials used by Privacy Hero depend on the VPN protocol:

  • NordLynx: Uses a NordVPN access token.
  • OpenVPN: Uses NordVPN manual service credentials.

Your regular NordVPN website login should not be entered as the router’s OpenVPN credentials.

If you are unsure whether the existing authentication information is still valid, retrieve current credentials directly from your NordVPN account and update Privacy Hero.

Confirm Your NordVPN Subscription Is Active

Privacy Hero cannot establish a NordVPN connection if the NordVPN account being used no longer has active VPN service.

Sign in to your NordVPN account and confirm that your subscription is active before continuing with server, token, or credential troubleshooting.

Try Another VPN Protocol

If your NordVPN account, credentials, and server selection are correct but the connection still fails, try another NordVPN protocol available in Privacy Hero.

For example, if NordLynx is not connecting, testing OpenVPN can help determine whether the issue is specific to the protocol or authentication method.

Remember that changing protocols also changes the required NordVPN authentication:

  • NordLynx requires a NordVPN access token.
  • OpenVPN requires NordVPN manual service credentials.

Important: Do Not Run Two VPNs at Once

Do not leave the NordVPN application connected directly on your phone or computer while testing the Privacy Hero VPN.

Running a VPN application on the device while also routing that device through the Privacy Hero VPN creates a double-VPN connection and can cause routing, connectivity, or IP-location problems.

Disconnect the device-level NordVPN app before testing the router VPN.

Verify the NordVPN Connection

Once Privacy Hero displays NordVPN as Connected:

  1. Connect your device to the Privacy Hero WiFi.
  2. Make sure the NordVPN app on the device is disconnected.
  3. Open a fresh private/incognito browser window.
  4. Visit NordVPN What Is My IP.
  5. Confirm that the public IP address and location correspond to your selected NordVPN location.
  6. Test several websites or applications.

If you use the Privacy Hero VPN Kill Switch, enable it only after confirming that NordVPN is connected and working.

NordVPN Is Connected but One Device Shows the Wrong IP

If Privacy Hero shows NordVPN as Connected and other devices display the correct VPN IP, the NordVPN connection itself is likely working.

Check the affected device’s Privacy Hero VPN assignment and review any VPN, privacy, DNS, browser, antivirus, firewall, or security settings running directly on that device.

See Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero NordVPN / NordLynx Setup
  • Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN

NordVPN Setup for Privacy Hero

TeamFlashRouters · Apr 3, 2023 ·

Privacy Hero supports NordVPN using both NordLynx and OpenVPN.

NordLynx is recommended for most users. OpenVPN is also available and may be required for NordVPN Dedicated IP connections. Some Dedicated IP configurations require a private OpenVPN file imported as a Custom VPN.

Privacy Hero is cloud-managed, so you can complete the setup from any device with an internet connection. You do not need to be connected to Privacy Hero WiFi to change these settings.

Choose Your NordVPN Setup

Jump straight to the setup or troubleshooting instructions you need.

NordLynx Setup →Recommended · Access token
OpenVPN Setup →Manual service credentials
Country & Server →Select a location or server hostname
Dedicated IP →Advanced Options or Custom .ovpn
Verify Connection →Confirm your VPN IP and location
Troubleshooting →Connection errors and next steps

NordVPN NordLynx Setup

NordLynx uses a NordVPN access token, not your regular NordVPN website email and password.

Open Privacy Hero and Select NordLynx

  1. From a computer, smartphone, or tablet, open app.privacyhero.com.
  2. Sign in with your Privacy Hero account email and password.
  3. Open the VPN section.
  4. Click Change and select NordVPN.
  5. Choose NordLynx.
NordVPN Protocol Privacy Hero

Generate Your NordVPN Access Token

  1. In another browser tab, open NordVPN Access Tokens and sign in to your NordVPN account.
  2. Complete any account or email verification requested by NordVPN.
  3. Select Generate new token; choose Doesn’t expire if available, then copy the token.

Important: Treat your NordVPN token as a password. Do not share it publicly.

Connect Privacy Hero to NordVPN

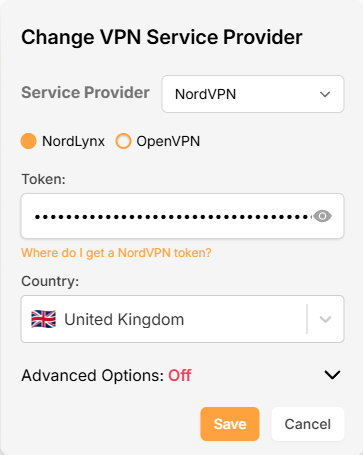
  1. Return to Privacy Hero, paste the token into the NordLynx token field, and click Save. The default country selection automatically chooses an available NordVPN server for that location.
  2. Wait for the VPN status to show Connected.
NordVPN Protocols Privacy Hero

NordVPN OpenVPN Setup

Use OpenVPN if you prefer the OpenVPN protocol or if your configuration requires it. OpenVPN requires NordVPN Manual Service Credentials, which are different from your website login email and password.

Select OpenVPN in Privacy Hero

  1. Open app.privacyhero.com and sign in.
  2. Open the VPN section.
  3. Click Change and select NordVPN.
  4. Select OpenVPN.
NordVPN Protocol Privacy Hero

Get Your Manual Service Credentials

  1. Open NordVPN Manual Service Credentials and sign in.
  2. Complete NordVPN’s verification if prompted, then copy the current Service Username and Service Password.

Important: Do not enter your normal NordVPN website email and password into Privacy Hero’s OpenVPN fields.

Save Your OpenVPN Connection

  1. Return to Privacy Hero and enter the manual service username and password in the OpenVPN credential fields. Click Save.
  2. Confirm Privacy Hero shows the connection as Connected.

Choose a NordVPN Country or Specific Server

Privacy Hero can select a NordVPN server automatically, or you can choose a country or specify a server hostname.

Choose a Country

  1. Open your NordVPN connection in Privacy Hero.
  2. Open the Country dropdown.
  3. Search for and select your preferred country.
  4. Click Save. Privacy Hero will use an available NordVPN server for the selected country.

Use a Specific NordVPN Server

  1. Open your NordVPN connection in Privacy Hero.
  2. Open Advanced Options.
  3. Enter the NordVPN server hostname, for example us12286.nordvpn.com.
  4. Click Save.

Use NordVPN’s server recommendation tool if you need a hostname. NordVPN servers can be retired or taken offline for maintenance; if your specific server stops working, choose another server or return to country selection.


NordVPN Dedicated IP Setup

NordVPN Dedicated IP can require either the regular NordVPN OpenVPN connection or a private .ovpn file imported as a Custom VPN.

Method 1: OpenVPN Advanced Options

Try this first if your Dedicated IP works with the standard NordVPN OpenVPN setup.

  1. Set up NordVPN → OpenVPN using your NordVPN Manual Service Credentials as described above.
  2. Open Advanced Options.
  3. Enter the Dedicated IP server hostname assigned to your account.
  4. Click Save and check whether the VPN connects.
  5. Verify that your public IP matches your assigned Dedicated IP.
Nord US Dedicated OpenVPN

If connected and the public IP matches, no additional configuration is needed.

Method 2: Custom VPN With a Private OpenVPN File

Some Dedicated IP servers require a private OpenVPN configuration file. If Method 1 does not connect, follow NordVPN’s Manual Dedicated IP Server Setup instructions.

Download Your Dedicated IP Configuration

  1. Sign in to the NordVPN account associated with the Dedicated IP.
  2. Locate your assigned Dedicated IP server using NordVPN’s manual setup instructions.
  3. Download its OpenVPN UDP configuration file.
  4. Save the .ovpn file to your computer or device.

Important: Use the private configuration file for your actual Dedicated IP, not a public NordVPN server file.

Upload the File as a Custom VPN

  1. Open app.privacyhero.com and select VPN → Change.
  2. Select Custom from the VPN provider dropdown, not NordVPN.
  3. Upload your Dedicated IP UDP .ovpn file.
  4. Enter your NordVPN Manual Service Username and Password.
  5. Save the configuration, enable the VPN, and wait for Connected.
  6. Verify the public IP matches your NordVPN Dedicated IP.

These are NordVPN’s separate manual service credentials, not your regular website login.


Verify Your NordVPN Connection

  1. Connect your testing device to the Privacy Hero WiFi.
  2. Disconnect any NordVPN or other VPN app running directly on that device.
  3. Open a fresh private/incognito browser window.
  4. Visit NordVPN What Is My IP.
  5. Confirm the public IP and location match your selected NordVPN server (or assigned Dedicated IP).

Running a VPN application directly on the device at the same time as the router VPN can produce double-VPN conflicts and unexpected IP or location results.

Streaming Relocation and VPN Location

If Streaming Relocation is enabled for a supported service, that service may use the Streaming Relocation region instead of your VPN server region. See Privacy Hero Streaming Relocation.


NordVPN Not Connecting?

If the VPN displays Failed, Connecting, or a timeout error, check for:

  • A server undergoing maintenance or no longer available.
  • An expired, revoked, or outdated NordLynx access token.
  • Incorrect or changed OpenVPN Manual Service Credentials.
  • Recent account changes or an inactive NordVPN subscription.
  • A protocol-specific issue.
  • A Dedicated IP that requires a private .ovpn file and Custom provider selection.

Follow Privacy Hero NordVPN Not Connecting or Showing Timeout Errors for troubleshooting.

No Internet After NordVPN Disconnects?

If internet access stops when the VPN disconnects, the VPN Kill Switch may be blocking normal traffic as intended. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected, but One Device Shows the Wrong IP?

If other devices show the correct VPN IP, check the affected device’s VPN apps, Private Relay, Private DNS, antivirus, and browser settings. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • NordVPN Not Connecting / Timeout
  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN

Separate 2.4GHz and 5GHz Wi-Fi bands on ExpressVPN/Aircove firmware

TeamFlashRouters · Mar 16, 2022 ·

By default ExpressVPN firmware bonds the 2.4GHz and 5GHz wireless networks to a single wireless network name. Your device will automatically choose which one will provide the best connection. You can separate these networks to have unique Wi-Fi names so you can control which network your devices will use.

1. Connect to the FlashRouter’s network via ethernet cable or wireless.

2. Open your web browser and enter expressvpnrouter.com or 192.168.132.1 in the URL.

ExpressVPNrouter.com
192.168.132.1

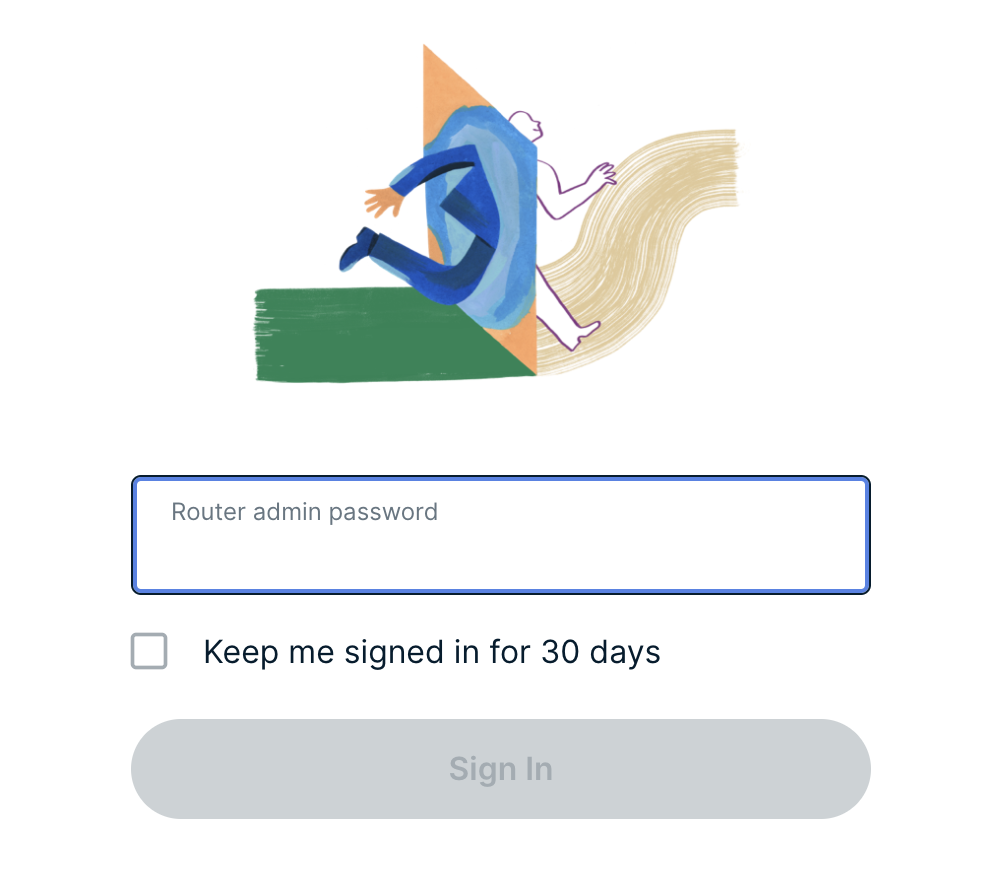
3. Login with your ExpressVPN FlashRouter admin password.

ExpressVPN Router admin login

4. Select Network Settings on the left hand side of the menu.

ExpressVPN Network Settings

5. Select Wi-Fi Settings on the left hand side of the menu.

ExpressVPN WiFi Settings

6. Click the toggle for Separate 2.4GHz and 5GHz Wi-Fi.

ExpressVPN Separate 2.4GHz and 5GHz

7. Separate Wi-Fi details for the 5GHz band will now display. You can change the name and password if you so choose or leave it with the default name and password with “-5GHz” added to the name. Click Save. Click Continue.

ExpressVPN 5GHz added

TP-Link Change Wi-Fi name and password

TeamFlashRouters · Apr 16, 2024 ·

Follow this guide to change the Wi-Fi name and password on your TP-Link FlashRouter.

1. Connect your computer, phone, or tablet to the TP-Link router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to the TP-Link firmware settings.

TP-Link URL Access

3. Enter tp-link as the admin password to access the TP-Link firmware settings.

TP-Link admin password

4. Click Wireless.

TP-Link Wireless tab

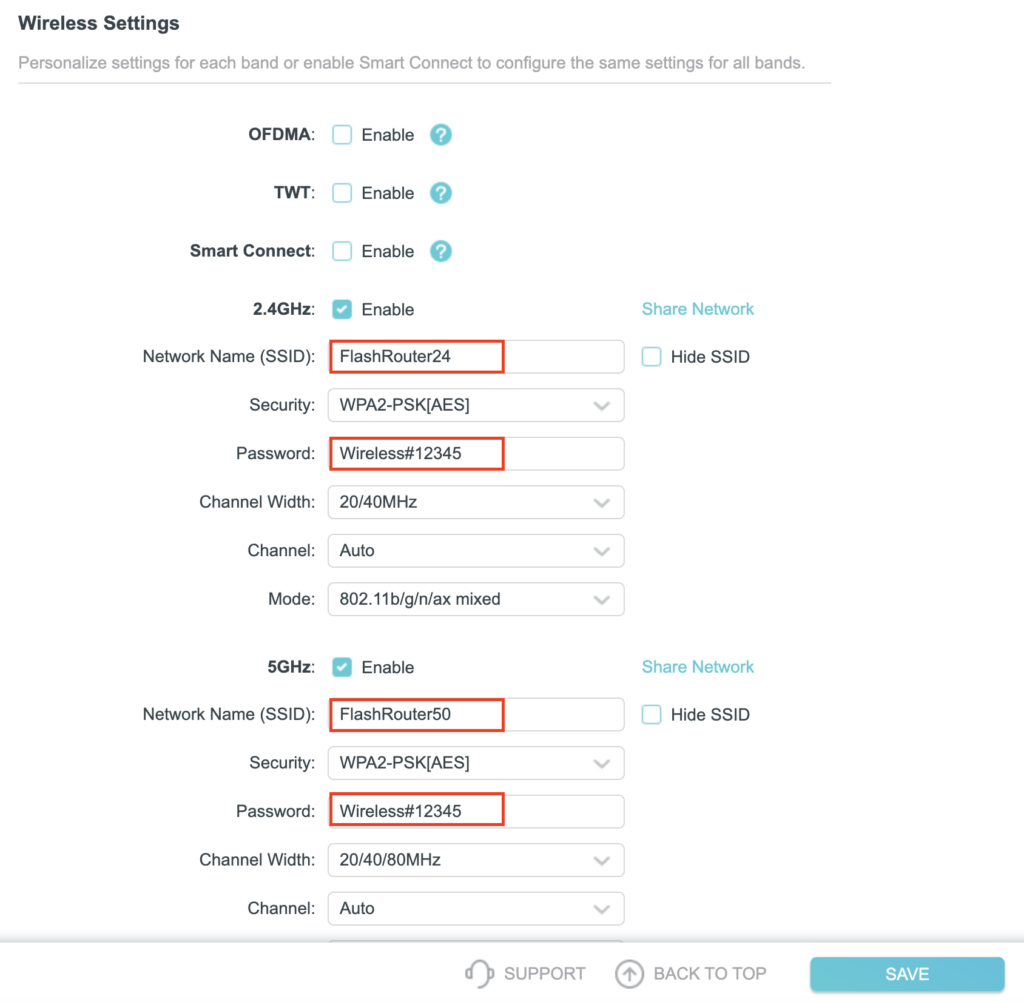
5. Change the Network Name (SSID) and Password fields to what you want to use. The SSID should be unique and NOT a duplicate of an existing network. Click Save.

TP-Link Change Wireless name and password

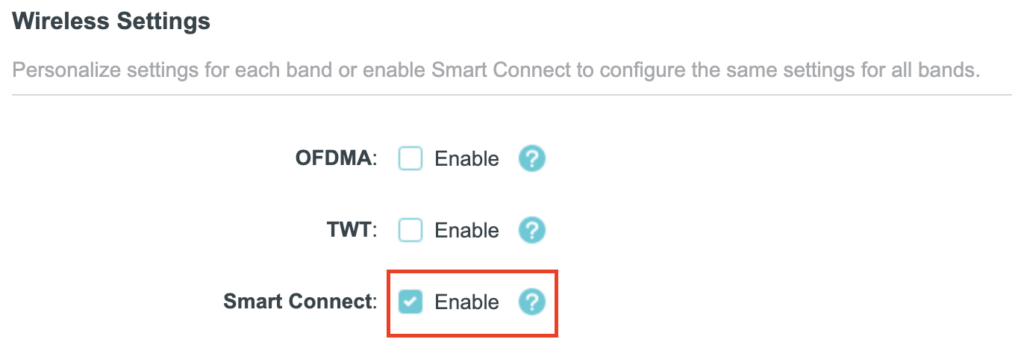
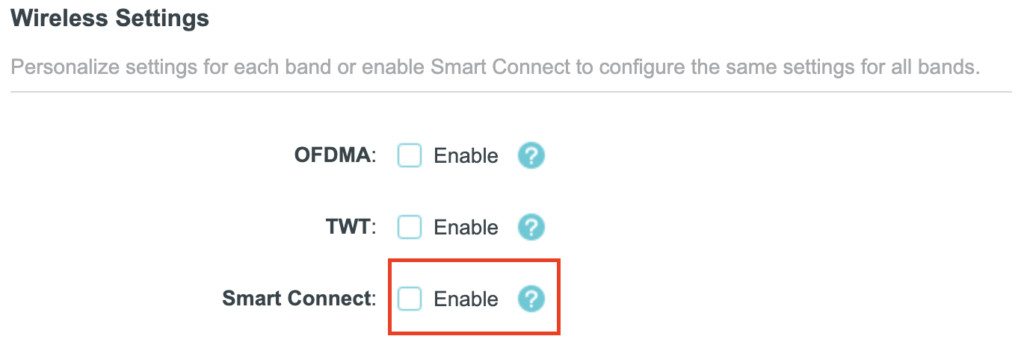
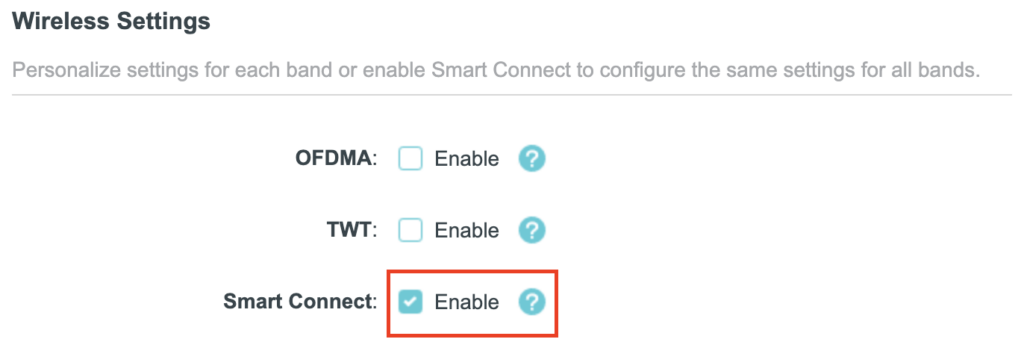
If you want both 2.4GHz and 5GHz networks to be bonded and have the same name click the Smart Connect checkbox.

TP-Link Separate Wifi

6. Connect your devices to the new wireless network.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero VPN Kill Switch Troubleshooting: No Internet or WiFi

Dave · Oct 8, 2026 ·

If your Privacy Hero router suddenly loses internet access, devices report that WiFi has no internet, or devices will not stay connected after a VPN failure, the VPN Kill Switch may be blocking normal internet traffic.

The VPN Kill Switch is designed to prevent traffic from passing through Privacy Hero without VPN protection. If the VPN disconnects or fails while the Kill Switch is enabled, normal internet access is intentionally blocked.

Important: You can still access app.privacyhero.com to manage Privacy Hero, turn off the Kill Switch, or repair the VPN connection.

Privacy Hero is cloud-managed, so you do not need to be connected to the Privacy Hero WiFi to change these settings. You can also access the dashboard using cellular data, your main router’s WiFi, or another internet connection as long as Privacy Hero remains connected to the internet and Privacy Hero cloud.


Jump to a Section

  • Common Kill Switch Symptoms
  • Restore Internet Access
  • VPN Still Fails to Connect
  • Privacy Hero Appears Offline
  • Kill Switch, WiFi, or WAN Problem?
  • Frequently Asked Questions

Common Privacy Hero Kill Switch Symptoms

A failed VPN connection combined with an enabled Kill Switch can make the Privacy Hero network appear unavailable even though the router itself may still be functioning.

Common symptoms include:

  1. Your device connects to Privacy Hero WiFi but websites and apps will not load.
  2. Your phone, computer, television, or streaming device reports that WiFi has no internet.
  3. A device refuses to remain connected because it detects that the WiFi network does not currently provide normal internet access.
  4. Your phone automatically switches from Privacy Hero WiFi to cellular data or another saved WiFi network.
  5. Your computer displays “No Internet” or “Connected without Internet.”
  6. The VPN displays Failed, Disconnected, Connecting, or a timeout error.
  7. Privacy Hero was working normally and suddenly stopped providing internet access.

If the Privacy Hero WiFi network itself is completely missing and cannot be detected by any device, that is different from normal Kill Switch behavior. Continue with WiFi or router connectivity troubleshooting instead.

Restore Internet Access

The fastest way to determine whether the Kill Switch is responsible is to temporarily disable it and test Privacy Hero without VPN.

  1. Open app.privacyhero.com.
  2. Sign in to your Privacy Hero account.
  3. Open the VPN section.
  4. Check the current VPN status.
  5. If the VPN shows Failed or Disconnected, turn the VPN Kill Switch Off.
  6. Turn the failed VPN connection off.
  7. Connect a device to the Privacy Hero network.
  8. Test normal internet access.

If internet access returns with the VPN and Kill Switch disabled, Privacy Hero’s basic internet connection is working and the problem is isolated to the VPN connection.

Important: Disabling the Kill Switch allows normal non-VPN internet traffic through Privacy Hero. Leave it disabled only while troubleshooting if continuous VPN protection is required.

VPN Still Fails to Connect

Do not turn the Kill Switch back on until the VPN is connected and working.

If you are using NordVPN and the VPN shows Failed, Connecting, or a timeout error, continue with our dedicated Privacy Hero NordVPN Not Connecting or Showing Timeout Errors guide.

That guide covers:

  • Selecting a different NordVPN server.
  • Replacing a failed Auto Country connection with a specific NordVPN server.
  • Generating a new NordVPN NordLynx access token.
  • Verifying NordVPN OpenVPN manual service credentials.
  • Avoiding double-VPN conflicts while testing.

If you use another VPN provider, try another available VPN server or protocol and verify that your VPN account and credentials remain active.

Verify the VPN Before Re-Enabling the Kill Switch

Once the VPN reconnects:

  1. Confirm Privacy Hero displays the VPN as Connected.
  2. Connect a device to the Privacy Hero WiFi.
  3. Make sure a separate VPN application is not connected directly on the testing device.
  4. Check your public IP address.
  5. Confirm the IP address and location reflect the VPN server you selected.
  6. Test normal websites and applications.
  7. Return to Privacy Hero and enable the VPN Kill Switch.

If you enable the Kill Switch while the VPN is still failing, normal internet access will be blocked again.

What If Privacy Hero Appears Offline?

If Privacy Hero shows Offline in the dashboard, the router may not currently be communicating with the Privacy Hero cloud.

  1. Confirm Privacy Hero is powered on.
  2. Confirm the Ethernet cable from your ISP gateway or primary router is connected to the Privacy Hero WAN/Internet port.
  3. Confirm your ISP gateway or primary router has working internet access.
  4. Restart Privacy Hero and allow it to finish booting.
  5. Using another internet connection, open app.privacyhero.com.
  6. Check whether Privacy Hero returns online.

If the router returns online, check the VPN and Kill Switch status before enabling the VPN again.

Privacy Hero Has a WAN IP but Devices Have No Internet

Privacy Hero can receive an IP address from your ISP gateway while the Kill Switch is still blocking normal internet traffic.

Before changing IP Passthrough, bridge mode, firewall settings, or other ISP gateway settings:

  1. Check the VPN status.
  2. Check whether the Kill Switch is enabled.
  3. Disable the VPN and Kill Switch temporarily.
  4. Test internet access again.

If internet access returns, troubleshoot the VPN connection rather than changing the ISP gateway configuration.

Kill Switch, WiFi, or WAN Problem?

WiFi Connects but There Is No Internet

If the VPN shows Failed or Disconnected and the Kill Switch is enabled, the Kill Switch is likely blocking normal internet traffic.

Device Will Not Stay Connected to Privacy Hero WiFi

Some devices automatically leave a WiFi network when they detect that it does not provide internet access. Use cellular data or another internet connection to access app.privacyhero.com and check the VPN and Kill Switch.

Privacy Hero WiFi Is Completely Missing

The Kill Switch does not normally cause the WiFi network itself to stop broadcasting. If no devices can detect the Privacy Hero WiFi network, troubleshoot the WiFi or router connection separately.

Privacy Hero Is Not Receiving a WAN IP Address

Check the Ethernet connection between Privacy Hero and your ISP gateway or primary router and confirm the upstream internet connection is working.

VPN Shows Connected but One Device Has the Wrong IP

If the VPN works correctly on other devices, the Kill Switch is probably not the issue. Check that device’s Privacy Hero VPN assignment and its own VPN, privacy, DNS, or security settings.

See Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN.

Frequently Asked Questions

Why does Privacy Hero WiFi say no internet?

If the VPN has failed while the Kill Switch is enabled, normal internet traffic is intentionally blocked. Your device may therefore report that Privacy Hero WiFi has no internet.

Can I access Privacy Hero settings while the Kill Switch is blocking internet?

Yes. Open app.privacyhero.com. You can use the Privacy Hero network, cellular data, your main router’s WiFi, or another internet connection.

Do I have to be connected to Privacy Hero WiFi to change the settings?

No. Privacy Hero is cloud-managed and can be managed remotely while the router remains connected to the Privacy Hero cloud.

Why does my phone keep leaving the Privacy Hero WiFi?

Some phones automatically switch to cellular data or another saved WiFi network when the current WiFi connection does not provide normal internet access.

Should I turn the Kill Switch back on immediately?

Only after the VPN is connected and you have confirmed that your internet traffic is using the VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero NordVPN Not Connecting or Showing Timeout Errors
  • Privacy Hero NordVPN / NordLynx Setup
  • Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN
  • Privacy Hero Router Setup Guide

Private Internet Access (PIA) Setup for Privacy Hero

TeamFlashRouters · Apr 3, 2023 ·

Privacy Hero supports Private Internet Access (PIA) with WireGuard (recommended) and OpenVPN. You need an active PIA subscription and your PIA VPN username and password.

Important difference: PIA WireGuard has a built-in provider integration in Privacy Hero. Choose Private Internet Access from the VPN provider list—not Custom WireGuard. No WireGuard configuration file or key generation is needed.

By default, Privacy Hero can automatically select an optimal available PIA server based on your location and server conditions. Alternatively, use Advanced Options to enter a specific PIA server hostname from the regional list below.

Privacy Hero is cloud-managed. You can configure your router from any device with an internet connection, whether or not you are on the Privacy Hero WiFi network.

PIA VPN Setup Guide

Choose your setup method or jump to a particular step.

PIA WireGuard →Use the built-in Privacy Hero PIA providerAutomatic or Manual Server →Select an optimal server or enter a hostnamePIA Server Hostnames →Browse the full list organized by regionOpenVPN Setup →Generate and upload an OpenVPN configurationVerify Connection →Confirm your device is using the PIA VPNTroubleshooting →Connection errors, wrong region, no internet

Set Up PIA WireGuard in Privacy Hero (Recommended)

Unlike most other providers, PIA WireGuard does not use Custom VPN file uploads in Privacy Hero. The built-in PIA integration connects using your PIA account credentials and handles the WireGuard configuration for you.
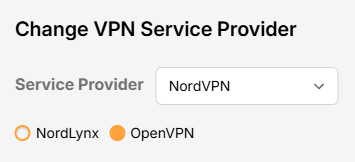
  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section. Select Change beside your current VPN provider.
  3. Choose Private Internet Access from the provider list. Do not select Custom for this WireGuard setup.
  4. Enter your PIA VPN account username and password (not your Privacy Hero dashboard credentials). You can check your account at PIA Client Control Panel.
  5. For automatic server selection, leave the optional server hostname unset, then click Save to connect. Wait until Privacy Hero displays Connected.
Privacy Hero built-in Private Internet Access provider login settings

Choose the Automatic Server or a Specific PIA Location

Privacy Hero offers two ways to select the PIA WireGuard server:

  • Automatic (recommended for most users): Leave the server hostname field blank. Privacy Hero selects an optimal available PIA location, generally favoring nearby servers and server conditions such as load. You do not need to manually maintain a server address.
  • Specific location: Enter a PIA region hostname under Advanced Options. This is useful when you need an IP address from a particular country or city.
  1. To use a specific location, open the existing Private Internet Access connection and select Advanced Options.
  2. Enter a complete PIA server hostname from the list below, for example us-newyorkcity.privacy.network or uk-london.privacy.network.
  3. Click Save, wait for Connected, then verify your new public IP address. If the selected location becomes unavailable, try another hostname or remove the hostname to return to automatic selection.
Privacy Hero Private Internet Access Advanced Options field for entering a VPN server hostname

PIA Server Hostname List by Region

Use these hostnames in PIA > Advanced Options when you prefer a specific location. Expand a region below and copy the complete hostname, including .privacy.network. This list is retained from the existing FlashRouters guide.

Server availability can change. Some hostnames, particularly those ending in -pf or marked for streaming, are specialized locations and may not be available for every connection. If a hostname no longer works, use automatic selection or check PIA’s current location list for available locations. PIA’s location list names regions; it does not necessarily provide matching hostnames.

North America (65 locations)
bahamas.privacy.networkca-ontario.privacy.networkca-toronto.privacy.networkca-vancouver.privacy.networkca-montreal.privacy.networkgreenland.privacy.networkgt-guatemala-pf.privacy.networkmexico.privacy.networkpanama.privacy.networksanjose.privacy.networkus-alabama-pf.privacy.networkus-alaska-pf.privacy.networkus-arkansas-pf.privacy.networkus-atlanta.privacy.networkus-california.privacy.networkus-chicago.privacy.networkus-connecticut-pf.privacy.networkus-denver.privacy.networkus-florida.privacy.networkus-houston.privacy.networkus-idaho-pf.privacy.networkus-indiana-pf.privacy.networkus-iowa-pf.privacy.networkus-kansas-pf.privacy.networkus-kentucky-pf.privacy.networkus-lasvegas.privacy.networkus-louisiana-pf.privacy.networkus-maine-pf.privacy.networkus-massachusetts-pf.privacy.networkus-michigan-pf.privacy.networkus-minnesota-pf.privacy.networkus-mississippi-pf.privacy.networkus-missouri-pf.privacy.networkus-montana-pf.privacy.networkus-nebraska-pf.privacy.networkus-new-hampshire-pf.privacy.networkus-new-mexico-pf.privacy.networkus-newyorkcity.privacy.networkus-north-carolina-pf.privacy.networkus-north-dakota-pf.privacy.networkus-ohio-pf.privacy.networkus-oklahoma-pf.privacy.networkus-oregon-pf.privacy.networkus-pennsylvania-pf.privacy.networkus-rhode-island-pf.privacy.networkus-seattle.privacy.networkus-siliconvalley.privacy.networkus-south-carolina-pf.privacy.networkus-south-dakota-pf.privacy.networkus-texas.privacy.networkus-tennessee-pf.privacy.networkus-vermont-pf.privacy.networkus-virginia-pf.privacy.networkus-washingtondc.privacy.networkus-west-virginia-pf.privacy.networkus-wisconsin-pf.privacy.networkus-wyoming-pf.privacy.networkus3.privacy.networkus-baltimore.privacy.networkus-honolulu.privacy.networkus-newjersey.privacy.networkus-saltlakecity.privacy.networkus-streaming-2.privacy.networkus-streaming.privacy.networkus-wilmington.privacy.network
South America (9 locations)
ar.privacy.networkbo-bolivia-pf.privacy.networkbogota.privacy.networkbr.privacy.networkec-ecuador-pf.privacy.networkpe-peru-pf.privacy.networksantiago.privacy.networkuy-uruguay-pf.privacy.networkvenezuela.privacy.network
Europe (51 locations)
al.privacy.networkad.privacy.networkaustria.privacy.networkbrussels.privacy.networkba.privacy.networksofia.privacy.networkzagreb.privacy.networkczech.privacy.networkde-berlin.privacy.networkde-frankfurt.privacy.networkdenmark.privacy.networkdenmark-2.privacy.networkspain.privacy.networkes-valencia.privacy.networkee.privacy.networkfi.privacy.networkfi-2.privacy.networkfrance.privacy.networkgr.privacy.networkhungary.privacy.networkitaly.privacy.networkitaly-2.privacy.networkis.privacy.networkireland.privacy.networkman.privacy.networklv.privacy.networkliechtenstein.privacy.networklt.privacy.networklu.privacy.networkmalta.privacy.networkmd.privacy.networkmonaco.privacy.networkmontenegro.privacy.networknl-amsterdam.privacy.networkmk.privacy.networkno.privacy.networkpoland.privacy.networkpt.privacy.networkro.privacy.networksweden.privacy.networksweden-2.privacy.networkrs.privacy.networksk.privacy.networkslovenia.privacy.networkswiss.privacy.networktr.privacy.networkuk-london.privacy.networkuk-manchester.privacy.networkuk-southampton.privacy.networkuk-2.privacy.networkua.privacy.network
Asia (26 locations)
ae.privacy.networkbangladesh.privacy.networkcambodia.privacy.networkchina.privacy.networkcyprus.privacy.networkgeorgia.privacy.networkhk.privacy.networkin.privacy.networkisrael.privacy.networkjakarta.privacy.networkjapan.privacy.networkjapan-2.privacy.networkkazakhstan.privacy.networkkr-south-korea-pf.privacy.networkkualalumpur.privacy.networkmacau.privacy.networkmongolia.privacy.networknp-nepal-pf.privacy.networkphilippines.privacy.networkqatar.privacy.networksaudiarabia.privacy.networksg.privacy.networksrilanka.privacy.networktaiwan.privacy.networkvietnam.privacy.networkyerevan.privacy.network
Oceania (7 locations)
au-adelaide-pf.privacy.networkau-australia-so.privacy.networkau-brisbane-pf.privacy.networkaus-melbourne.privacy.networkaus-perth.privacy.networkau-sydney.privacy.networknz.privacy.network
Africa (5 locations)
dz.privacy.networkegypt.privacy.networkmorocco.privacy.networknigeria.privacy.networkza.privacy.network

Set Up PIA OpenVPN in Privacy Hero

OpenVPN is the alternative when you need a manually uploaded connection or if the built-in PIA WireGuard method does not work on your network. OpenVPN uses Custom in Privacy Hero, unlike the built-in PIA WireGuard setup.

Download a PIA OpenVPN Configuration File

  1. Sign in to the PIA Client Control Panel using your PIA VPN account.
  2. Open Downloads and scroll to OpenVPN Configuration Generator or OpenVPN Configurations.
  3. If using the generator, choose OpenVPN 2.4 or newer and Linux when these options are offered, then choose an available server location.
  4. Select your preferred configuration. UDP / 1198 (AES-128-CBC) is a standard default. UDP / 1197 (AES-256-CBC) is an alternative. Use a PIA-provided TCP configuration if UDP does not work on your network.
  5. Click Generate or download a suitable pre-made configuration and save the resulting .ovpn file. Each server file is tied to its selected location/settings.

PIA also provides pre-made OpenVPN configuration bundles; see PIA’s OpenVPN file instructions.

Add PIA OpenVPN as a Custom VPN

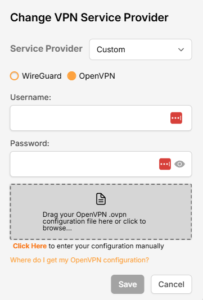
  1. Open Privacy Hero, go to VPN, click Change, and select Custom.
  2. Choose OpenVPN and upload the PIA .ovpn file downloaded in the previous section.
  3. Enter your PIA VPN username and password in the Custom OpenVPN authentication fields.
  4. Click Save and confirm Privacy Hero shows Connected.
Privacy Hero Custom OpenVPN configuration with file upload and username password fields

Note: If OpenVPN UDP cannot connect, try a TCP profile from PIA or another server. When switching protocols, make sure you upload a matching PIA configuration file.


Verify Your Private Internet Access Connection

  1. Connect a device to the Privacy Hero WiFi or LAN network.
  2. Disconnect any PIA app or other VPN running directly on the device so the router VPN can be tested independently.
  3. Open a private/incognito browser window and visit PIA What Is My IP.
  4. Confirm that your public IP address reflects the VPN connection, and that the approximate location is consistent with either the selected hostname or Privacy Hero’s automatic server selection.

Privacy Hero VPN settings can be changed remotely, but the device used to verify the VPN IP must be connected to the Privacy Hero network.

Streaming Relocation and Your PIA Location

If Streaming Relocation is enabled for a supported service, that service may use the Streaming Relocation location instead of your PIA VPN server location. See Privacy Hero Streaming Relocation.


PIA VPN Not Connecting?

If Privacy Hero reports Failed, stays on Connecting, or connected devices lose internet access, try these checks:

  1. Confirm your PIA subscription is active and enter your PIA VPN login, not your Privacy Hero email/password.
  2. For built-in PIA WireGuard, verify the provider is Private Internet Access—not Custom. No downloaded WireGuard file is required.
  3. Remove any specific server hostname to test automatic server selection. If that connects, the previous hostname may be unavailable.
  4. For Custom OpenVPN, upload a fresh PIA .ovpn file, re-enter the PIA credentials, and try a different server or a TCP configuration.
  5. Turn off the router VPN temporarily to check that normal internet access works. If the VPN Kill Switch is blocking internet traffic, temporarily disable it for testing, then restore your preferred setting.
  6. Check whether a separate VPN app, iCloud Private Relay, Private DNS, proxy, or security software on the testing device is affecting your VPN IP results.

No Internet When the VPN Disconnects?

The Privacy Hero VPN Kill Switch may intentionally block internet access if the VPN goes down. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

If other devices show the expected VPN address, review device VPN apps, iCloud Private Relay, Private DNS, and security settings.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

TP-Link Change Wireless Channel

TeamFlashRouters · Apr 16, 2024 ·

Follow this guide to change the Wireless channel on your TP-Link FlashRouter.

1. Connect your computer, phone, or tablet to the TP-Link router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to the TP-Link firmware settings.

TP-Link URL Access

3. Enter tp-link as the admin password to access the TP-Link firmware settings.

TP-Link admin password

4. Click Wireless.

TP-Link Wireless tab

5. Change the Channel setting to the number that you want to use. Click Save.

TP-Link Change Wireless Channel

6. Connect your devices to the wireless network again as they may have been disconnected when making this change.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

TP-Link Merge or Separate 2.4GHz and 5GHz Wi-Fi

TeamFlashRouters · Apr 17, 2024 ·

Your TP-Link router broadcasts a 2.4GHz and a 5GHz Wi-Fi network. These can be separated to allow you to assign your devices to the network that best suits them or merged into a single network so your devices automatically select the best band to use. Follow this guide to separate or merge your Wi-Fi bands.

1. Connect your computer, phone, or tablet to the TP-Link router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to the TP-Link firmware settings.

TP-Link URL Access

3. Enter tp-link as the admin password to access the TP-Link firmware settings.

TP-Link admin password

4. Click Wireless.

TP-Link Wireless tab

5. Check the Smart Connect checkbox to merge the two Wi-Fi bands. Uncheck the Smart Connect checkbox to separate the two Wi-Fi bands. If you have the two Wi-Fi bands separated make sure the Network Name (SSID) fields have different names for 2.4GHz and 5GHz bands. Click Save.

TP-Link Merge Wifi
TP-Link Separate Wifi

6. Connect your devices to the new wireless network.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PrivateInternetAccess (PIA) TP-Link OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for PIA TP-Link Setup

Download your PIA .ovpn file

If you are not already a PIA user Sign Up Now.

1. Log in to your account on the PIA website.

PIA login

2. Successfully log in with your account information then go to PIA’s OpenVPN Config Generator.

3. On the OpenVPN Configuration Generator select the following:

OpenVPN Version: OpenVPN 2.4 or newer

Select Platform: Linux

Select Region: Choose the server location you’d like to connect to

Select Port: Typically we recommend UDP/1198 RSA-2048 AES-128-CBC SHA1 for best speeds but feel free to select the one you want to use.

4. Click Generate to download the .ovpn file. Do not open this file once it is downloaded.

PIA Generate .ovpn file

TP-Link Router Setup for PIA

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location. Our example server was New York so I have entered in PIA New York.

Set the VPN Type to OpenVPN.

In the Username and Password fields paste in the PIA username and password you use to successfully login to your PIA website account.

Click Browse and select the .ovpn file you downloaded earlier. Then click Save.

TP-Link PIA

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link PIA Connected

Verify a successful PIA connection

  1. You should now see a CONNECTED message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

How to change the PIA server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Warranty and Returns FAQs

admin · Jan 29, 2019 ·

Warranty and Returns FAQs

At FlashRouters, we are confident that every router sold will function as advertised. We open, inspect, upgrade, configure, and then test all FlashRouters before they get shipped out. That is why we guarantee you will receive a working unit and offer our own 1-Year Hardware Warranty included with all New and Refurbished routers purchased from the FlashRouters website.

If you would like to extend the warranty coverage period to 2 years, the option is available during the FlashRouters checkout process.

Since we are so certain you will be happy with your upgraded and super secure network, all routers purchased from FlashRouters.com also come with a 30-day satisfaction guarantee.

Please read the warranty and return section in detail before placing an order or requesting an RMA. Our goal is to make the return process as smooth and transparent as possible for all customers. If the router you purchased does not work out for your needs we still want you to be satisfied with your purchasing experience.

Hardware Warranty and Return Policy

Requesting an RMA

Automated Return Merchant Authorization (RMA) requests are available from within your customer account panel. If you are eligible for a return then your RMA request will be approved. If your RMA request is not valid then it will be denied and you must e-mail FlashRouters Support for any additional information or actions. RMAs are valid for 7 days from the day they are issued. 

The following are the available options when submitting an RMA request. Continue reading for more information on all available RMA options and conditions. 

  1. Hardware Guarantee – available for 7 days after receiving your FlashRouter.
  2. Satisfaction Guarantee – available for 30 days after receiving your FlashRouter.
  3. Hardware Warranty – available for 1 year, or 2 years if upgraded when purchasing a FlashRouter.
  4. Hardware Repair – Anyone with a valid FlashRouters Support subscription is eligible for free Hardware Repair. 

Please note we can only provide prepaid labels for approved Hardware Warranty returns within the USA. Prepaid labels are not available for international customers. All return shipping for 30 Day Satisfaction refunds is paid for by the customer.

Hardware Guarantee

In the rare case you receive a faulty router, you can open a ticket to contact FlashRouter Support for an RMA or request an RMA in your customer account panel and we will work to rectify the situation immediately. If it is determined that the power supply you received was faulty, and not the router itself, our team will immediately ship you out a tested power supply at no additional cost.

Rest assured that we individually test and inspect every FlashRouter with great detail before shipment. BUT… if router gremlins (yes they do exist) snuck into your router during the shipping process and it no longer powers on, our team will supply you with a prepaid shipping label to return the unit back to our offices. As soon as we receive verified tracking on your return shipment we will ship out another thoroughly tested unit to you at no additional cost.

You must contact us within 7 days from when you received your FlashRouter to be eligible for a Hardware Guarantee prepaid shipping label from FlashRouters.

30-Day Satisfaction Guarantee

If you are not satisfied with the performance of your router after trying it out for up to 30 days, you can open a ticket to contact FlashRouter Support for an RMA or request an RMA in your customer account panel. Once the RMA is approved, you will then have the option to ship the unit back to FlashRouters.

Once we receive the return, our team inspects and refunds accordingly based on the original purchase price of your FlashRouter. Please note there is a $25 restocking fee and refunds do not include any initial shipping costs associated with your order. All restocking fees are returned as Store Credit. This means if you make another purchase at FlashRouters then your fee is refunded.

The item must also be fully functional and have no signs of cosmetic damage for you to receive the maximum refund. If you do not include the original boxing, or any router accessories you may also be charged an additional fee as indicated.

Ethernet Cable: $5

Power Source: $10 

Antennas: $5 per antenna

Router Stand: $10

Box: $10

Cosmetic Damage: Up to $25

What is covered under the 30-Day Satisfaction Guarantee?

If the VPN speeds or WiFi network speeds are not what you had hoped, if the setup is too complicated, or you just decided on another solution; these are all covered under the 30-Day Satisfaction Guarantee. 

We will not accept any returns of working routers after 30 days from the date you received your router. After 30 days, router returns/replacements will only be processed under the Hardware Warranty. 

Can I get the restocking fee waived?

If you place a new order for a different FlashRouter unit before returning your initial purchase, then we will waive the restocking fee. Otherwise the $25 restocking fee will be applied to your customer account as a store credit. You can then use this $25 store credit on any future FlashRouter purchase.

Rewards Points refunds

If you return your FlashRouter under the 30 day satisfaction guarantee then you will lose any reward points received for your initial purchase.

Hardware Warranty

A 1-year Hardware Warranty is included with the purchase of all New and Refurbished FlashRouters. If your router suffers hardware failure within 365 days from the date you received the unit then we will replace your router with another fully tested unit. You must pay for return shipping of the faulty unit back to our offices located in New Jersey, USA and our team will ship out your replacement at no additional cost.

You must contact the FlashRouter support team for an RMA number or request an RMA from your customer account panel before returning a router for warranty replacement. If you do not receive approval for a return then you will not be eligible for a replacement unit.

There are 2 options for receiving a Hardware Warranty replacement unit:

Option #1: Process another order for immediate shipping and as soon as we receive the returned device back in our offices we will issue you a refund for the initial purchase.

Option #2: Ship your faulty router back to our office, and as soon as we receive the unit our returns department will have a replacement unit shipped out to you at no extra cost.

How long do I have before my RMA expires?

RMA’s are good for 7 days from the date they are issued.

What if I upgraded to a 2 year Hardware Warranty at checkout?

All refund, replacement, RMA details, and options covered by the 1-year Warranty apply in the exact same manner for 2 year warranties over each respective warranty coverage period.

If for any reason the router you purchased is no longer in stock or discontinued then you have the option to replace your router with one of equal value or receive a refund. Hardware warranties are only eligible for refunds if we are unable to provide a replacement unit for you.
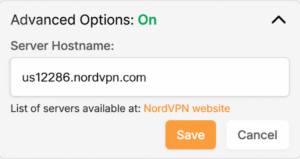
What should I do if my router is out of warranty coverage?

If your FlashRouter is out of the warranty coverage period, we are first and foremost apologetic for the passing of your router. Be sure to contact our sales team though and you can receive a special coupon as a return customer for a shiny new wireless networking centerpiece.

What is not covered with a FlashRouter Warranty?

Items that have been clearly damaged either by the customer or during the return process are not eligible for a full refund. This includes routers that have visible dents, scratches, or moving parts inside the router.

Can I upgrade to a 2 year warranty after my FlashRouter purchase?

2 year warranty upgrades are only available at the time of your FlashRouter purchase. Upgrades are not available once a FlashRouter order has been shipped. 

Can I get a Warranty on my router if I purchased a “Flash My Router” plan from FlashRouters?

Routers that have been “flashed” and configured by our support specialists for anyone who has purchased a Flash My Router Plan are not eligible for warranty coverage from FlashRouters. Only routers purchased through the FlashRouters.com website are eligible for warranty replacements or refunds.

Hardware Repair

FlashRouters is proud to offer a free repair and upgrade service for anyone with an active Silver or Gold Service Plan subscription. Any and all shipment costs associated with FlashRouter repairs or upgrade requests are the burden of the customer and will not be paid for by FlashRouters. However, the repair and upgrade service itself is FREE.

If you do choose to ship your router back to our office for repair, then you should include a prepaid shipping label in your package back to your home or office, so our team can send the router back to you whether we are able to repair the unit or not. Router accessories like power supplies, ethernet cable, or antennas do not need to be included when shipping back a unit for repair.

If our team is not able to resurrect your router from a power failure, faulty firmware upgrade, or any other reason then we can return the faulty unit back to you using the return shipping label included with your return package. Alternatively, we can destroy the unit and refund the return shipping costs if that is your preference.

Open Box Routers

What is an Open Box Router?

Open Box routers are fully functional units that have cosmetic flaws and are sold at heavy discounts. These units come with the same Support Plan options as New or RM units, which means you get the same support service with extremely discounted hardware.

Open Box routers are covered under the FlashRouter 30-Day Satisfaction Guarantee BUT come with no Hardware Warranty. We take every measure possible to ensure complete functionality and our team fully load tests these devices before shipment, but you should be very aware that you buy these discounted “open box” devices at your own risk without any Hardware Warranty.

What is the Open Box Router return policy?

Open Box Routers can only be returned within 30 days from the date you received your router. Returns will not be accepted on open box routers after 30-Day Satisfaction Guarantee window has expired. Please note that Open Box Router return shipping costs are not covered by FlashRouters and initial shipping costs are not included in any refunds. 

Accessories Warranty

All Accessories come with manufacturer warranties as listed on the respective product pages. 

FlashRouters will accept returns for refund or replacement of accessories only within 30 days from the date you received your order. After 30 days you must contact the manufacturer for any warranty replacements.

Accessories must be returned with all original packaging and with no cosmetic damage to receive a full refund. A missing box or damage to an item will result in a restocking fee per our discretion.

"Flash My Router" Refund Policy

The “Flash My Router” product offered by FlashRouters is a virtual service provided by the FlashRouters support team. This product includes a remote support session where our support team will flash your router and then complete your internet, WiFi, and VPN setup, and in certain cases support additional router features. 

Once your remote support session is completed there are absolutely no refunds on “Flash My Router” purchases. In the case we are unable to successfully flash your router we will offer a full refund for your “Flash My Router” purchase. “Flash My Router” purchases are fully refundable if you decide you would no longer like to use the service after your purchase is completed.

Service Plan Subscription Refund Policy

All FlashRouter router purchases include a recurring FlashRouters Service Plan subscription. There are 3 levels of support to choose from as either a quarterly or yearly recurring billing plan.

30-Day Satisfaction Guarantee

If you choose to return your FlashRouter under the 30-Day Satisfaction Guarantee, then you are eligible for a full refund on any Service Plan purchased with your FlashRouter.

Cancellation Policy

You may cancel your recurring billing at any time and you will not be charged again. Please note you will not be refunded for unused time from the initial billing/service period of your support plan subscription.

If you choose to cancel your 3 month FlashRouter support plan then you will retain support until the end of the 3 month period. If you choose to cancel your 1 year FlashRouter support plan then you will retain support until the end of the 1 year period. You will not lose time from your existing service plan if you cancel when a plan is active.

There is a 7-day grace period after Service Plan renewals have been charged, where you may request an immediate cancellation and full refund.

How do I change my FlashRouter Support subscription level?

How do I Upgrade my Service Plan?

You can upgrade a Service Plan at any time during a billing cycle. You must e-mail or live chat our support team and request an upgrade. Our team will then issue you store credit for any unused time on your existing Service Plan, which will then be immediately applied to your new upgraded Service Plan purchase. Your recurring billing will then continue at the new Service Plan level. Your 3 months or 1 year of upgrade service will start again from the date of the upgrade purchase. 

How do I switch from a Quarterly to a Yearly Service Plan?

If you would like to switch to a Yearly plan from a Quarterly plan of the same service level, then you must e-mail or live chat our support team and request an upgrade. Our team will then issue you store credit for any unused time on your existing Quarterly Service Plan, which will then be immediately applied to your new Yearly Service Plan purchase. Your recurring billing will then continue at the Yearly Service Plan level. Your 1 year of service will start again from the date of the upgrade purchase. 

How do I Downgrade my Service Plan?

If you are subscribed a Service Plan, but would like to switch to a lower level Service Plan then you can request that our support team cancel your recurring billing at any time. As soon your existing Service Plan is expired you can make a new purchase for the new Service Plan of your choice.

How do I switch from a Yearly to a Quarterly Service Plan?

If you would like to change the billing cycle from yearly to quarterly, you may cancel your existing subscription plan and then once your year of service has expired, you may purchase a Quarterly Service Plan instead.

If you just purchased a FlashRouter, there is a 7-day grace period from when you receive your unit if you would like an immediate change from Yearly to a Quarterly Service Plan.

How do I cancel my subscription?

You may request a Service Plan subscription cancellation by e-mailing support@flashrouters.com or from within your customer account panel at any time. You will be notified of a successful cancellation and your payment method will not be billed again.

Please note there are no refunds when cancelling your subscription. Cancellation means you will not be billed again for your Service Plan, there are no partial refunds for cancelled Service Plans.

AirVPN Manual OpenVPN Setup

TeamFlashRouters · Jun 11, 2019 ·

Preparing for Manual AirVPN Setup

Obtain your AirVPN OpenVPN Information

If you are not already a AirVPN user Sign Up Now.

1. Log in to your account on the AirVPN website.

AIRVPN OpenVPN Client Login for FlashRouter DD-WRT VPN Configuration

2. Click on the Client Area tab.

AIRVPN OpenVPN Client Area for FlashRouter DD-WRT VPN Configuration

3. Click on the Config Generator subtab.

AIRVPN OpenVPN Configuration Generator for FlashRouter DD-WRT VPN Configuration

4. Click on the Router icon under Choose your Operating System.

AIRVPN OpenVPN FlashRouter DD-WRT VPN Configuration

5. Select a Protocol under the Protocols section. We recommend UDP.

Select AIRVPN OpenVPN Encryption Protocol for FlashRouter DD-WRT VPN Configuration

6. Select one option under the Choose Servers section. AirVPN sorts these servers by Planet, Continent, Country, and Single servers. Choose whichever best suits your needs.

Sort AIRVPN OpenVPN Specific Certificates for FlashRouter DD-WRT VPN Configuration

7. Scroll down towards the bottom of the page and click on Generate.

Generate AIRVPN OpenVPN Specific Certificates for FlashRouter DD-WRT VPN Configuration

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You will be copying the Server IP/Name, client.crt and client.key from this file.

Please note, all VPN servers have different keys and certificates. If you wish to change servers in the future, you will have to go through steps 1-7 again.

DD-WRT Router Setup for AirVPN

Navigate to Services > VPN

Enter AirVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you selected in your account. Be sure there are no extra spaces or characters.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Disable

Advanced Options

Enable

TLS Cipher

None

LZO Compression

No

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

TLS Auth Key

—–BEGIN OpenVPN Static key V1—–
7bb7a23a0f5f28d01e792df68f1764ab
f2688719288808bf58e8a2d4f9354ecf
132625dfb895fc3f6330ae1e868e4dfa
c164c0931593d7f9a7da9595cf353433
8896e1d0a987a0d19838944af8fea4e5
215a3a0c76f4c67d5a4aee6a53be66a4
c88b84f850030840fb30f8550ed8068f
35c1ef34ee8f40a0ea5862dfb6f8d3c5
7ab5e27ac2799cf93e8765ff63cd8cd8
6b391b813925cd373bb202796f64d16f
003d042ca828d1b07f18ba1d0cb0323d
df3ee9287e9e084e655699efb3cffa92
3626946fa372e7beee245e7a95b4c1d8
7d16cae685218d4b8afc019b22e41083
476ee9883fe666d236301e55b2062551
4d91c8a69467a758293994df1e6fa7ae
—–END OpenVPN Static key V1—–

CA Cert

—–BEGIN CERTIFICATE—–
MIIGVDCCBDygAwIBAgIJAIzYQ+/kXyADMA0GCSqGSIb3DQEBBQUAMHkxCzAJBgNV
BAYTAklUMQswCQYDVQQIEwJJVDEQMA4GA1UEBxMHUGVydWdpYTETMBEGA1UEChMK
YWlydnBuLm9yZzEWMBQGA1UEAxMNYWlydnBuLm9yZyBDQTEeMBwGCSqGSIb3DQEJ
ARYPaW5mb0BhaXJ2cG4ub3JnMB4XDTE0MDQxMTEwMTU0NVoXDTI0MDQwODEwMTU0
NVoweTELMAkGA1UEBhMCSVQxCzAJBgNVBAgTAklUMRAwDgYDVQQHEwdQZXJ1Z2lh
MRMwEQYDVQQKEwphaXJ2cG4ub3JnMRYwFAYDVQQDEw1haXJ2cG4ub3JnIENBMR4w
HAYJKoZIhvcNAQkBFg9pbmZvQGFpcnZwbi5vcmcwggIiMA0GCSqGSIb3DQEBAQUA
A4ICDwAwggIKAoICAQDGG3ZrJbP61PNjGc4mjTx0TLkUjP7IXZ3wnpPjwF/lwK9n
HgRqoPL0KY/ABJuzMViD8ChtwthNfc7PuJ7vSPtN84lSJ4JGmTxvZkNeLQLZsu1F
f88OcSpjW5ErBM05iVBeF8/ljwaajgFfbgop9W/UK5yMji4qgq5KHxxXqsB8R4rC
eFpWHoNTwFjvXhtVyMgXiT9XAh/vBYim021m8onio4K48q7YRZ4qU8gvE79h5M0g
miIlt6v1vaZskw9cqIBbCYefGMsvBRk2x824ChPf6FazMwAnQHsuBHt6eXAARvfF
DBDanzPHlRSiCP6Je6Vod/MPyepiTZgjgk2VxYUc1ohNxEEGzPGTayeNzLJUldou
P4B+tjJ0Xly30+wvlahADlqjtz3CGQmKMj7btZjd+Uo61B7gau5YiXR/IO7ZpFAC
PCZJSbrwFs6rt9Kewqk8zslfVIro8oDndXRkVsa/c8Qmd6ZE7V+oMGl2OggdWOLl
mDEjkytzx+Bw2sSSalJRAQmOQO8V0anOI6jGYLuU2jnFDsnqSHuwIK11xb6iHmh7
ONsRLUtQ+d64TzB00w2M0fCvGqUIp0N+lf7nsZKsEcU08OoHQYUuwX75ZEOYNSZJ
rqAXohcXdVUHqgRlJRErfSkjcGMM0yqjHkvopcnBIRXKMYTDVXvzRJboyJiVpQID
AQABo4HeMIHbMB0GA1UdDgQWBBTlFdcTqJ4x49Ew1/Ef9OJj0lDIiDCBqwYDVR0j
BIGjMIGggBTlFdcTqJ4x49Ew1/Ef9OJj0lDIiKF9pHsweTELMAkGA1UEBhMCSVQx
CzAJBgNVBAgTAklUMRAwDgYDVQQHEwdQZXJ1Z2lhMRMwEQYDVQQKEwphaXJ2cG4u
b3JnMRYwFAYDVQQDEw1haXJ2cG4ub3JnIENBMR4wHAYJKoZIhvcNAQkBFg9pbmZv
QGFpcnZwbi5vcmeCCQCM2EPv5F8gAzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEB
BQUAA4ICAQCUVAQteCtgNQiZMXV0wCdqivlxlCCuj5sD+XvEuoDqb7dH70u1KQ90
OAbkeotHlIbqJU10xWtvHEjnXg8QG5VOzaWnWWev+ivdPCkGWe8E7C8shsr4WMlA
EF8PPRtzOwCKayxjR713x+Tc2Sb6/rDsXcY5LV6RNmE9HWBM6IoHdqruR8PHkYge
2CPXMuLByEADri6xmvussAjCWEDplJNY7tQsUGT7vjrwrNSNBx/SvxkXnWBj0wYa
EwNu43jrjcRfM/3eGcKDX3cQqTfRQd3j3OA7zmJOXPeExRUIWZTNCvQItGy1TJdw
JTphflw15Bui4l2mYfDqK08zm4aJODrCjoQnVVzM5uOzSTOjmneI6AHj3MjjL3A/
CFA5PCSquBhUycF4UEVf3aPGiV0vAthCBUqM4eKE+rbjWPSaxKghVdr/S82o7Wzz
9mGwnOZDqWk+8AWSsGBjamMk3mNMR45E9FRfPF/dyjOSbVyyTsd1VzlTFEJa0wjB
l3yq3r3iZAM3UtevocAyTEAu0vDYBbS6TgWmWEDOizybB0hNrTx5u/SEI0Kwcthc
rilYxD+n4kmV7TvIR0ZSaYpgYALWQV27zOqY51Ol4UT98WCOokge9HdoFcGJU2Uj
5VneGp14/Oklh7y6BxxxGC3zNGjKGNQYuHGTIgw1DoASmRUdkPkn/w==
—–END CERTIFICATE—–

Public Client Cert

Copy and paste all contents between <cert> and </cert> make sure to also include the following lines when copying and pasting:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and paste all contents between <key> and </key> make sure to also include the following lines when copying and pasting:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful AirVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit whatismyipaddress.com to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to AirVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the AirVPN server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new client.key and private.key
  4. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

What is a DNS leak and how can I prevent a DNS leak in my router?

TeamFlashRouters · Jun 11, 2019 ·

What is a DNS leak?

A DNS Leak is an instance where your ISP receives DNS requests despite being connected to a VPN tunnel.

How do I check if my DNS is leaking?

  1. Perform the extended test on DNSLeakTest.com. Be sure to do so on multiple web browsers for best accuracy.
  2. Here you should only find one server and your ISP should not be listed as your actual ISP.
  3. If your actual ISP is not listed there is no DNS leak.

How can I prevent a DNS leak in DD-WRT?

Check your device's browser settings

Updates to web browsers have added DNS settings capabilities, while this often makes your browsing experience more secure it can also effect the results of a DNS leak test. You can go into your browser’s settings and search for “DNS” and disable the DNS of the browser for more accurate DNS leak test results.

A simple web search for “DNS settings [browser name]” should return helpful information for finding the setting in your browser.

Adjust DD-WRT settings

1. On the Setup > Basic Setup page of the DD-WRT settings check the Ignore WAN DNS box.

This setting may not appear in older DD-WRT firmware builds. If it is not appearing for you, upgrade your DD-WRT firmware.

DD-WRT Check Ignore WAN DNS

2. Lower on the same page check the Forced DNS Redirection box.

DD-WRT Check Forced DNS Redirection

3. Click Apply Settings at the bottom of the page and then wait a full minute and power the FlashRouter off and back on. Reconnect to the FlashRouter’s network once it boots back up and then make sure you are connected to VPN by going to https://whatismyipaddress.com then perform the DNS leak test again.

Adding your VPN provider’s DNS servers to the router’s configuration can be helpful as well. The DNS servers are typically found on the VPN provider’s website or you can reach out to their team for a recommendation of what DNS servers to enter.

Using Device Groups to connect to multiple VPN locations on ExpressVPN/Aircove firmware

TeamFlashRouters · May 12, 2022 ·

ExpressVPN offers a great feature of connecting the FlashRouter to multiple ExpressVPN servers at the same time. You can then assign your devices to the location that you wish.

1. Connect to the FlashRouter’s network via ethernet cable or wireless.

2. Open your web browser and enter expressvpnrouter.com or 192.168.132.1 in the URL.

ExpressVPNrouter.com
192.168.132.1

3. Login with your ExpressVPN FlashRouter admin password.

ExpressVPN Router admin login

4. Select Add Group and name the new group or select one of the pre-named groups below.

ExpressVPN Add Group

5. Click the three dots next to the new server location and type in the location you want to connect to. Click the new location to connect.

ExpressVPN Change server
ExpressVPN select new server

5. Click and drag the device that you want assigned to the VPN New Group.

ExpressVPN select device
ExpressVPN device assigned

The devices assigned to new group will now connect to that location while the devices in the first VPN group will remain connected to the VPN server selected in that area.

ExpressVPN Setup for Privacy Hero

TeamFlashRouters · Aug 14, 2025 ·

Privacy Hero supports ExpressVPN using OpenVPN. To connect, you need your ExpressVPN Manual Configuration username and password and an OpenVPN (.ovpn) configuration file for your preferred server location.

Important: In Privacy Hero, choose Custom as the VPN provider. Upload the ExpressVPN .ovpn file and enter your separate Manual Configuration credentials, not your regular ExpressVPN website login.

Privacy Hero is cloud-managed, so you can complete setup from any computer, smartphone, or tablet with an internet connection. You do not need to be connected to Privacy Hero WiFi while changing the settings.

Choose Your ExpressVPN Setup Step

Jump directly to the instructions you need.

Manual Credentials →Find your ExpressVPN OpenVPN username and passwordDownload .ovpn File →Choose a server location and download its UDP fileCustom VPN Setup →Upload the file and enter credentials in Privacy HeroUDP Configuration →Check the OpenVPN protocol and save your connectionVerify Connection →Confirm your VPN IP address and server locationTroubleshooting →Connection errors, timeouts, and no internet

Get Your ExpressVPN Manual Configuration Credentials

ExpressVPN provides separate credentials for manual OpenVPN connections. These are different from your normal ExpressVPN website email and password.

  1. Open ExpressVPN Set Up Devices and sign in to your ExpressVPN account.
  2. In the left navigation, select Set Up Devices.
  3. Under Applications, expand Advanced setup and choose Manual Configuration.
  4. Find your unique Username and Password under Manual Configuration. Keep this tab open so you can copy them into Privacy Hero.

Important: Do not use your regular ExpressVPN account password, and do not share your manual configuration credentials publicly.


Download Your ExpressVPN OpenVPN Server File

Each available ExpressVPN location has its own OpenVPN configuration file. The file determines the server location used by Privacy Hero.

  1. On the same Manual Configuration page, locate the server regions, such as Americas, Europe, Asia Pacific, or Middle East & Africa.
  2. Expand your preferred region and download the UDP .ovpn file for an available location. Save it to the device you are using to configure Privacy Hero.

Only locations offered on your ExpressVPN Manual Configuration page can be used for this setup. To change locations later, download the corresponding .ovpn file and upload it to Privacy Hero.


Add ExpressVPN to Privacy Hero as a Custom VPN

ExpressVPN uses Privacy Hero’s Custom VPN configuration rather than a dedicated ExpressVPN provider option.

Upload the OpenVPN File and Enter Credentials

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section.
  3. Click Change beside the VPN provider and choose Custom.
  4. Choose OpenVPN if prompted, then upload the UDP .ovpn file downloaded from ExpressVPN.
  5. Copy the separate ExpressVPN Manual Configuration Username and Password into the corresponding Privacy Hero fields.
Privacy Hero Custom OpenVPN configuration showing file upload and manual username and password fields

Check the UDP Configuration and Connect

  1. If Privacy Hero displays the OpenVPN configuration in an editor, confirm that the downloaded UDP configuration specifies proto udp. If the directive is missing, add proto udp at the beginning of the configuration. Do not add a conflicting second protocol directive.
  2. Click Save to apply the configuration and establish the VPN connection.
  3. Confirm Privacy Hero displays Connected for the Custom OpenVPN connection.
Privacy Hero Custom OpenVPN configuration editor with proto udp directive

Verify Your ExpressVPN Connection

After Privacy Hero reports Connected, check that devices on the Privacy Hero network are actually using the VPN.

  1. Connect the testing device to the Privacy Hero WiFi or LAN network.
  2. Disconnect the ExpressVPN app or any other VPN application running directly on that device.
  3. Open a fresh private/incognito browser window.
  4. Visit ExpressVPN What Is My IP.
  5. Confirm the public IP address and approximate location correspond to the ExpressVPN server selected in your .ovpn file.

Important: You can manage Privacy Hero’s VPN settings from another network or cellular data. However, to verify the router’s VPN IP, the testing device must be connected to the Privacy Hero network. Running another VPN app on the device can produce double-VPN results.

Streaming Relocation and VPN Location

If Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation region instead of the location defined in the ExpressVPN configuration file. See Privacy Hero Streaming Relocation.


ExpressVPN Not Connecting?

If Privacy Hero shows Failed, stays on Connecting, or displays a timeout error, try these checks:

  1. Confirm your ExpressVPN subscription is active and you entered the separate Manual Configuration username and password.
  2. Check that you selected Custom in Privacy Hero, rather than another VPN provider.
  3. Download a fresh UDP .ovpn file for an available ExpressVPN server location and upload it again.
  4. Check that the OpenVPN configuration uses proto udp without conflicting protocol directives.
  5. Temporarily disable the VPN Kill Switch while testing whether normal internet access works without the VPN, then restore your preferred Kill Switch setting.
  6. Try another ExpressVPN server location or reconnect the VPN.

No Internet After the VPN Disconnects?

The Privacy Hero VPN Kill Switch may intentionally block normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected, but One Device Shows the Wrong IP?

If other devices show the correct VPN IP, check the affected device’s VPN apps, iCloud Private Relay, Private DNS, antivirus filtering, browser proxy/DNS settings, or other security software. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

ProtonVPN Setup for Privacy Hero

TeamFlashRouters · Sep 17, 2025 ·

Privacy Hero supports Proton VPN through WireGuard and OpenVPN using the Custom VPN provider option.

WireGuard is recommended for most users. It uses a downloadable .conf configuration file. OpenVPN uses a downloadable .ovpn file and a separate Proton VPN OpenVPN username and password (not your regular Proton Account login).

Privacy Hero is cloud-managed. You can configure the VPN from a computer, smartphone, or tablet connected to any internet network; you do not need to be on the Privacy Hero WiFi to change settings.

Choose Your Proton VPN Setup

Jump directly to the connection method or instructions you need.

WireGuard Setup →Recommended · Generate your .conf fileOpenVPN Setup →Manual credentials and .ovpn fileUpload WireGuard →Add a Custom WireGuard connectionUpload OpenVPN →Add the file and service credentialsVerify Connection →Confirm VPN IP address and locationTroubleshooting →Fix connection failures and no internet

Proton VPN WireGuard Setup (Recommended)

WireGuard uses a configuration file generated by Proton VPN. You do not need an OpenVPN username and password for this method.

Generate Your Proton VPN WireGuard Configuration

  1. Open your Proton VPN account and sign in.
  2. Go to Downloads → WireGuard configuration.
  3. Enter a recognizable configuration name and select Router as the platform.
  4. Choose your preferred VPN options and an available server or country. For a straightforward setup, select a standard server configuration.
  5. Click Create, then Download to save the generated WireGuard .conf file to your device.

Important: A WireGuard configuration contains a private key. Keep the downloaded file private; do not paste its contents into public posts or unprotected support messages. For detailed Proton account instructions, see Proton VPN: Download WireGuard Configuration Files.

Upload WireGuard to Privacy Hero

  1. Open app.privacyhero.com and log in to your Privacy Hero account.
  2. Open the VPN section, click Change beside the VPN provider, and choose Custom.
  3. Select WireGuard and upload the Proton VPN .conf file you downloaded.
  4. Click Save to apply the configuration and connect. Confirm that Privacy Hero reports Connected.
Privacy Hero Custom WireGuard configuration screen showing the configuration file upload

Proton VPN OpenVPN Setup

OpenVPN is an alternative to WireGuard. You need a Proton VPN OpenVPN-specific username and password and a server .ovpn configuration file.

Get Your Proton VPN OpenVPN Credentials

  1. Sign in to your Proton VPN account.
  2. Open Account → OpenVPN username to find your separate OpenVPN username and password.
  3. Copy these credentials or keep the page open. Do not use your usual Proton Account email and password for the manual OpenVPN connection.

For help locating these credentials, see Proton VPN: How to Sign In / OpenVPN Credentials.

Download Your Proton VPN OpenVPN Server File

  1. In your Proton VPN account, go to Downloads → OpenVPN configuration files.
  2. Select Router as the platform and UDP as the protocol (recommended starting point). If UDP does not work on your network, you can try a TCP configuration later.
  3. Select an available country or individual server from the standard configuration list, then click Download to save its .ovpn file.

For additional details about the file download options, see Proton VPN: Download OpenVPN Configuration Files.

Upload OpenVPN to Privacy Hero

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section, click Change, and select Custom as the VPN provider.
  3. Choose OpenVPN and upload the Proton VPN .ovpn file you downloaded.
  4. Enter your separate Proton VPN OpenVPN username and password into the Custom VPN fields.
  5. Click Save, then confirm Privacy Hero displays Connected.
Privacy Hero Custom OpenVPN setup with configuration file upload and separate VPN username and password fields

Verify Your Proton VPN Connection

After Privacy Hero reports Connected, confirm that a device on the router network is using your Proton VPN connection.

  1. Connect your testing device to the Privacy Hero WiFi or LAN network.
  2. Disable any Proton VPN app or other VPN application running directly on that device, so it does not create a second VPN connection.
  3. Open a private/incognito browser window.
  4. Visit Proton VPN’s IP Address Checker.
  5. Verify that the public IP address and approximate location correspond to the Proton VPN server configured in Privacy Hero.

Important: You can manage Privacy Hero from another WiFi network or cellular data. However, the device performing the VPN IP test must be connected to the Privacy Hero network.

Streaming Relocation and VPN Location

If Privacy Hero Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation location rather than the country selected in your Proton VPN configuration. See Privacy Hero Streaming Relocation.


Proton VPN Not Connecting?

If Privacy Hero displays Failed, remains on Connecting, or reports a timeout, work through these checks:

  1. Confirm that you selected Custom as the VPN provider in Privacy Hero and chose the protocol that matches your configuration file.
  2. For WireGuard, create and download a fresh Proton VPN .conf file for an available server, then upload it again. Do not use an OpenVPN .ovpn file in the WireGuard section.
  3. For OpenVPN, verify that you entered Proton VPN’s separate OpenVPN username and password, not your regular Proton Account login.
  4. Download a fresh configuration for a different Proton VPN server and reconnect. Proton VPN occasionally changes server configurations.
  5. If using OpenVPN UDP and the connection still fails, download and try a TCP .ovpn configuration file to test for a protocol-related issue.
  6. Temporarily disable the VPN Kill Switch while checking whether internet works without the VPN. Re-enable your preferred Kill Switch setting once testing is complete.

VPN Disconnects and Devices Have No Internet?

The VPN Kill Switch may be intentionally blocking normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

Check the affected device for a second VPN app, iCloud Private Relay, Private DNS, browser proxy settings, or filtering software. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

Wireless Guest Network Setup – Bridged (Advanced)

TeamFlashRouters · Jun 12, 2019 ·

If you would like to prevent visitors from connecting to your main WiFi network then you can create a Bridged Guest Network that will prevent access to the main router. This setup also allows you to create different rules for different WiFi SSID’s in your home ranging from QoS controls, access restrictions, VPN network segmentation, and more.

Preparing for Wireless Guest Network Setup

If you have a Dual-band or Tri-Band router you can setup a WiFi Guest Network, creating a separate VLAN (virtual local area network) for your visitors, or in order to segment your VPN networks on any band you like. We recommend using the 2.4GHz network for your DD-WRT Guest Wireless Network so it is compatible with the most possible WiFi devices. Setting up a guest network for visitors in your home allows you to keep them off of your main WiFi network.

We recommend performing this setup while connected to the FlashRouter via ethernet cable. If your computer does not have an ethernet port and you must proceed via wireless connection to the FlashRouter pay attention to the wireless connection as you may need to rejoin the FlashRouter’s network after making changes.

DD-WRT Router Setup for Wireless Guest Network

Enter Wireless settings

Navigate to Wireless > Basic Settings

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Setting SSID for Guest Network
  1. Under the 2.4GHz or 5GHz Interface click the Add button.
  2. In the Wireless Network Name (SSID) field enter the unique network name of the guest network.
  3. Click Save.

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Setting Guest Network Wireless Password
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Click Apply Settings.
  3. Reboot your router.

Create Bridge

Navigate to Setup > Networking

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Create Bridge
  1. Under Create Bridge click Add. Name the newly created bridge br1.
  2. Click Apply Settings

Assign to Bridge

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Assign Bridge
  1. Under Assign to Bridge select br1 from the Assignment dropdown. Select wl1.1 or ath1.1 depending on your router model.
  2. Click Apply Settings.

Depending on the router model and WiFi band you are using, the wireless interfaces will be labelled differently.

This setting can be labelled wl1.1, ath0.1, wl2.1, and so on. Make sure when you get up to the bridge assignment section that you are using the correct guest network Virtual Interface.

Network Configuration br1

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Configure Bridge DNS Redirection
  1. Under Network Configuration br1 select Enable for Forced DNS Redirection.
  2. Set Optional DNS Target to 208.67.220.220
  3. Set IP Address to 192.168.12.1
  4. Set Subnet Mask to 255.255.255.0
  5. Click Apply Settings.

Multiple DHCP Server

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Configure DHCP Server Settings
  1. Under Multiple DHCP Server click Add.
  2. Set the first dropdown to br1.
  3. Click Apply Settings.
  4. Reboot your router.

Firewall Rules

Navigate to Administration > Commands

  1. Copy the fire script from below and paste into the empty Commands shell
  2. Click Save Firewall.
  3. Wait one minute and then reboot your router.

iptables -I FORWARD -i br1 -o br0 -m state –state NEW -j DROP
iptables -I FORWARD -i br0 -o br1 -m state –state NEW -j DROP
iptables -I INPUT -i br1 -p tcp –dport telnet -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport ssh -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport www -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport https -j REJECT –reject-with tcp-reset

You will now have a working Bridged Guest Network on the FlashRouter. By inputting the firewall rules, this will also prevent any guests on your network from gaining access to your router settings.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

How to Access Your AsusWRT FlashRouter Settings

TeamFlashRouters · Oct 16, 2025 ·

This quick guide will walk you through connecting to your AsusWRT FlashRouter and logging into the admin settings page. You’ll use either WiFi or an Ethernet cable, then access the router dashboard through your browser.

Step 1. Connect Your Device to the Router

You can connect by WiFi or Ethernet:

  • WiFi: Look for a network name like FlashRouter24 or FlashRouter50.
    • The WiFi password is set to: Wireless#[First 5 characters of your router’s MAC]
    • Example: If your MAC is CC28A07E70A8, your WiFi password is Wireless#CC28A.
    • ⚠️ Be sure to capitalize the “W” in Wireless.
  • Ethernet: Plug an Ethernet cable from your computer into one of the router’s LAN ports (usually marked or color-coded differently from the WAN port).

👉 Pro tip: Disconnect from any other WiFi networks during setup.

Step 2. Open the Router Login Page

  1. Open a web browser (Chrome, Safari, Firefox, Edge).
  2. In the address bar, type: 192.168.50.1 or go to asusrouter.com
  3. Press Enter.
Access Asus Router

This is the local router dashboard address (not a public website). If the page doesn’t load:

  • Try a different browser.
  • Clear your cache.
  • Ensure your device is connected to the FlashRouter network.

Step 3. Log In to the Router Settings

  • Default username: flashrouter
  • Default password: asuswrt-admin1
  • Some older devices may use: asuswrt1 or asuswrt
  • This is the factory default for AsusWRT routers shipped by FlashRouters.
Asus Router Login

💡 Once you’re in, you can update your admin password in the settings for extra security.

Next Steps

Now that you’ve accessed your AsusWRT FlashRouter, you can:

  • Set up your VPN service
  • Customize your WiFi name and password
  • Adjust device controls and security settings

Check our support library for your specific VPN setup guide.

PrivateInternetAccess (PIA) AsusWRT OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for PIA AsusWRT Setup

Download your PIA .ovpn file

If you are not already a PIA user Sign Up Now.

1. Log in to your account on the PIA website.

PIA login

2. Successfully log in with your account information then go to PIA’s OpenVPN Config Generator.

3. On the OpenVPN Configuration Generator select the following:

OpenVPN Version: OpenVPN 2.4 or newer

Select Platform: Linux

Select Region: Choose the server location you’d like to connect to

Select Port: Typically we recommend UDP/1198 RSA-2048 AES-128-CBC SHA1 for best speeds but feel free to select the one you want to use.

4. Click Generate to download the .ovpn file. Do not open this file once it is downloaded.

PIA Generate .ovpn file

AsusWRT Router Setup for PIA

Login to AsusWRT firmware settings in a browser on any computer or smart device connected to the AsusWRT FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Fusion tab.

Asus VPN Fusion

3. Click Add profile.

Asus Add profile

4. In the Connection Name field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was in New York so I have entered in PIA New York.

5. In the VPN Type dropdown select OpenVPN.

6. Click Import .ovpn file and select the .ovpn file you downloaded earlier. Then click Upload.

7. In the Username and Password fields paste in the PIA username and password you use to successfully login to your PIA website account.

8. Click Apply and Enable at the bottom of the page.

Asus PIA profile

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network click into the profile and disable Apply to all devices. Then click Devices and select the devices that you want to connect to VPN.

Asus VPN devices
Asus VPN select devices

9. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Asus PIA Connected

Verify a successful PIA connection

  1. You should now see a CONNECTED message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

How to change the PIA server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Why can’t I send emails while connected to VPN?

TeamFlashRouters · Jun 4, 2019 ·

Can’t send or receive emails? Connecting to a VPN server can result in your email client not being able to send or receive emails. This can happen for several reasons:

  • The VPN provider you are connected to is blocking the ports the email client is using (SMTP).
  • Your email service is blocking access to datacenter IPs
  • Your email service is only allowing access to residential IPs
  • Your email service is only allowing access to IPs of its own country
  • Your email service is only allowing access to certain ISPs

This issue will only occur with email client applications and not with web browser email.

Steps to take if your email is not working

Change SMTP port

Access the settings of your email client and change the SMTP port to 587 or 465.

Change the VPN server

Connect to a different VPN server. The process for changing servers is detailed in your provider’s setup instructions.

FlashRouters Privacy App

DD-WRT Manual VPN Configuration

Disconnect from VPN

Disconnect from VPN on the FlashRouter and use your ISP Internet connection when using email.

Dual router setup users can leave the VPN running on the FlashRouter and simply connect to the other router’s network when using email.

Contact your VPN Service Provider

In some cases if you contact your VPN service provider they will be able to give you access to a specifically requested e-mail service.

« Previous Page

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer