• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: need a router s

Privacy Hero NordVPN Not Connecting or Showing Timeout Errors

Dave · Sep 22, 2026 ·

If NordVPN will not connect on Privacy Hero, shows a timeout error, remains stuck on Connecting, or displays Failed, the Privacy Hero router itself may still be working normally.

NordVPN connections can occasionally stop working when servers are placed into maintenance, removed or cycled out of service, account credentials change, or a previously saved NordVPN access token or manual service credential is no longer valid.

Start by confirming that Privacy Hero has normal internet access, then troubleshoot the NordVPN connection.


Jump to a Section

  • Confirm Privacy Hero Has Internet
  • Reconnect NordVPN
  • Try Another NordVPN Server
  • Update Your NordLynx Token
  • Update OpenVPN Credentials
  • Recent NordVPN Account Changes
  • Verify the VPN Connection

First: Confirm Privacy Hero Has Internet

Before changing your NordVPN settings, confirm that Privacy Hero itself has normal internet access.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. If the VPN Kill Switch is enabled, temporarily turn it Off.
  4. Turn the failed NordVPN connection off.
  5. Connect a device to the Privacy Hero network.
  6. Test normal internet access.

If internet access works normally with NordVPN and the Kill Switch disabled, the underlying Privacy Hero internet connection is working. Continue troubleshooting the NordVPN connection.

If your internet stopped working because NordVPN failed while the VPN Kill Switch was enabled, follow our Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting guide.

Reconnect NordVPN

A temporary NordVPN server or connection issue may resolve without changing your account information.

  1. Open the VPN section at app.privacyhero.com.
  2. Turn the NordVPN connection off.
  3. Wait a few seconds.
  4. Turn NordVPN back on.
  5. Allow the connection time to establish.
  6. Check whether the VPN status changes to Connected.

If NordVPN still shows Failed, Connecting, or a timeout error, continue with the steps below.

Try Another NordVPN Server

NordVPN regularly maintains, replaces, and cycles servers in its network. A specific NordVPN server that worked previously may eventually be taken offline, removed, or temporarily unavailable.

If your Privacy Hero NordVPN connection is configured to use a specific server and suddenly stops working, try another server or return to the normal country selection.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. Select your NordVPN connection.
  4. If you previously entered a specific NordVPN server under Advanced Options, remove or replace that server.
  5. Select the country or location you want to use.
  6. Save the settings.
  7. Reconnect NordVPN.
  8. Check whether the status changes to Connected.

If you specifically need to use an individual NordVPN server, make sure that server is still active before continuing to use it.

Important: A previously working specific server should not be assumed to remain available indefinitely. NordVPN may change its server network over time.

Update Your NordVPN Token for NordLynx

Privacy Hero uses a NordVPN access token to authenticate NordLynx connections.

If the saved token is expired, revoked, replaced, or otherwise no longer valid, NordLynx may show Failed, Connecting, or a timeout error.

Generating a new token is a good troubleshooting step if your NordVPN account information has changed or the existing token is no longer working.

  1. Sign in to your NordVPN account.
  2. Open the NordVPN Access Tokens page.
  3. Generate a new access token.
  4. Select Doesn’t expire if NordVPN provides that option.
  5. Copy the new token.
  6. Open app.privacyhero.com.
  7. Open the NordVPN settings.
  8. Confirm that NordLynx is the selected protocol.
  9. Replace the existing token with the newly generated token.
  10. Save the settings.
  11. Reconnect NordVPN.

Important: NordVPN access tokens are sensitive account credentials. Do not post or share your token publicly.

For complete setup instructions, see Privacy Hero NordVPN / NordLynx Setup.

Update NordVPN Manual Service Credentials for OpenVPN

If you are using OpenVPN instead of NordLynx, Privacy Hero uses NordVPN’s Manual Service Credentials.

These are different from the email address and password you normally use to sign in to the NordVPN website or application.

If the saved credentials are no longer valid, update them:

  1. Sign in to your NordVPN account.
  2. Open NordVPN Manual Service Credentials.
  3. Copy the current service username and password.
  4. Open app.privacyhero.com.
  5. Open your NordVPN settings.
  6. Confirm that OpenVPN is the selected protocol.
  7. Replace the existing manual service credentials with the current credentials from NordVPN.
  8. Save the settings.
  9. Reconnect NordVPN.

Do not enter your regular NordVPN website email address and password in place of the manual service credentials.

Did You Recently Change Your NordVPN Account Information?

If NordVPN stopped connecting after an account change, update the authentication information stored in Privacy Hero.

This is especially important after changes such as:

  • Changing your NordVPN account password.
  • Changing or updating NordVPN account security settings.
  • Generating or replacing NordVPN access tokens.
  • Changes to NordVPN manual service credentials.
  • Renewing, changing, or restoring your NordVPN subscription.

The credentials used by Privacy Hero depend on the VPN protocol:

  • NordLynx: Uses a NordVPN access token.
  • OpenVPN: Uses NordVPN manual service credentials.

Your regular NordVPN website login should not be entered as the router’s OpenVPN credentials.

If you are unsure whether the existing authentication information is still valid, retrieve current credentials directly from your NordVPN account and update Privacy Hero.

Confirm Your NordVPN Subscription Is Active

Privacy Hero cannot establish a NordVPN connection if the NordVPN account being used no longer has active VPN service.

Sign in to your NordVPN account and confirm that your subscription is active before continuing with server, token, or credential troubleshooting.

Try Another VPN Protocol

If your NordVPN account, credentials, and server selection are correct but the connection still fails, try another NordVPN protocol available in Privacy Hero.

For example, if NordLynx is not connecting, testing OpenVPN can help determine whether the issue is specific to the protocol or authentication method.

Remember that changing protocols also changes the required NordVPN authentication:

  • NordLynx requires a NordVPN access token.
  • OpenVPN requires NordVPN manual service credentials.

Important: Do Not Run Two VPNs at Once

Do not leave the NordVPN application connected directly on your phone or computer while testing the Privacy Hero VPN.

Running a VPN application on the device while also routing that device through the Privacy Hero VPN creates a double-VPN connection and can cause routing, connectivity, or IP-location problems.

Disconnect the device-level NordVPN app before testing the router VPN.

Verify the NordVPN Connection

Once Privacy Hero displays NordVPN as Connected:

  1. Connect your device to the Privacy Hero WiFi.
  2. Make sure the NordVPN app on the device is disconnected.
  3. Open a fresh private/incognito browser window.
  4. Visit NordVPN What Is My IP.
  5. Confirm that the public IP address and location correspond to your selected NordVPN location.
  6. Test several websites or applications.

If you use the Privacy Hero VPN Kill Switch, enable it only after confirming that NordVPN is connected and working.

NordVPN Is Connected but One Device Shows the Wrong IP

If Privacy Hero shows NordVPN as Connected and other devices display the correct VPN IP, the NordVPN connection itself is likely working.

Check the affected device’s Privacy Hero VPN assignment and review any VPN, privacy, DNS, browser, antivirus, firewall, or security settings running directly on that device.

See Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN.
Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero NordVPN / NordLynx Setup
  • Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN

Hotspot Shield Manual OpenVPN Setup

TeamFlashRouters · Jul 15, 2020 ·

Preparing for Manual Hotspot Shield Setup

Obtain your Hotspot Shield OpenVPN Information

If you are not already a Hotspot Shield user Sign Up Now.

1. Log in to your account on the Hotspot Shield website.

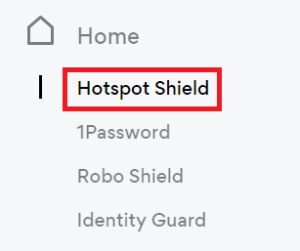
2. Click Hotspot Shield on the left side navigation.

Hotspot Shield - Website Admin

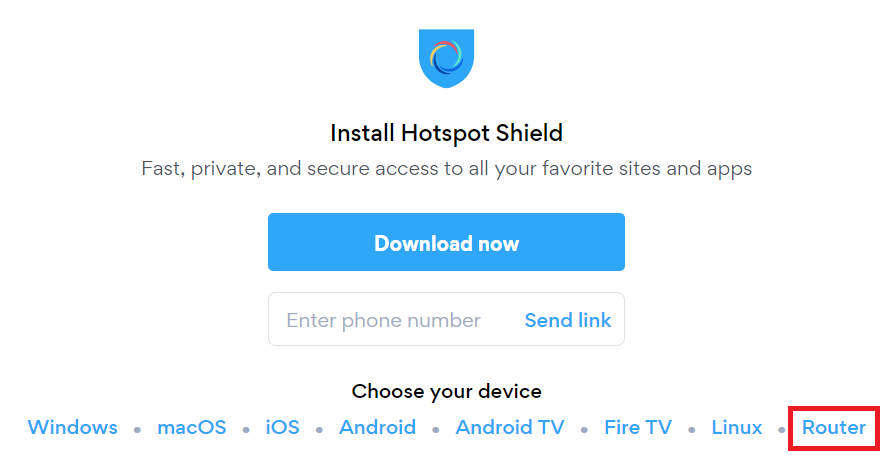
3. Under Choose your device click Router.

Hotspot Shield - Select Router

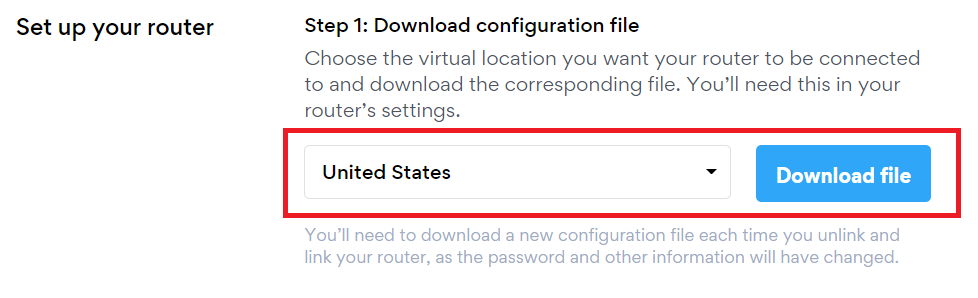
4. In the Set up your router section Select your desired virtual location and then click Download file.

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the <cert> and <key> from the .ovpn file. All Hotspot Shield servers have different keys and certificates.

Hotspot Shield - Download Configuration File

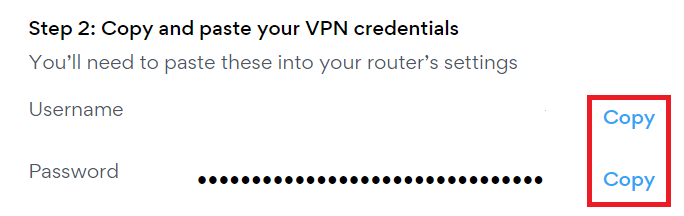
5. Copy the VPN Username, and Password that appear under Step 2 to a notepad, you will need this information later in the setup process.

Hotspot Shield - OpenVPN username and password

DD-WRT Router Setup for Hotspot Shield

Navigate to Services > VPN

Enter Hotspot Shield settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote universitycalendar.us 8041
universitycalendar.us is your Hotspot Shield server name. Enter the server name in this field.

Port

8041

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your Hotspot Shield account.

Password

Enter the Password you obtained in your Hotspot Shield account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

No

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping 15
ping-restart 0
reneg-sec 0
remote-cert-tls server

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIFazCCA1OgAwIBAgIRAIIQz7DSQONZRGPgu2OCiwAwDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTUwNjA0MTEwNDM4
WhcNMzUwNjA0MTEwNDM4WjBPMQswCQYDVQQGEwJVUzEpMCcGA1UEChMgSW50ZXJu
ZXQgU2VjdXJpdHkgUmVzZWFyY2ggR3JvdXAxFTATBgNVBAMTDElTUkcgUm9vdCBY
MTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAK3oJHP0FDfzm54rVygc
h77ct984kIxuPOZXoHj3dcKi/vVqbvYATyjb3miGbESTtrFj/RQSa78f0uoxmyF+
0TM8ukj13Xnfs7j/EvEhmkvBioZxaUpmZmyPfjxwv60pIgbz5MDmgK7iS4+3mX6U
A5/TR5d8mUgjU+g4rk8Kb4Mu0UlXjIB0ttov0DiNewNwIRt18jA8+o+u3dpjq+sW
T8KOEUt+zwvo/7V3LvSye0rgTBIlDHCNAymg4VMk7BPZ7hm/ELNKjD+Jo2FR3qyH
B5T0Y3HsLuJvW5iB4YlcNHlsdu87kGJ55tukmi8mxdAQ4Q7e2RCOFvu396j3x+UC
B5iPNgiV5+I3lg02dZ77DnKxHZu8A/lJBdiB3QW0KtZB6awBdpUKD9jf1b0SHzUv
KBds0pjBqAlkd25HN7rOrFleaJ1/ctaJxQZBKT5ZPt0m9STJEadao0xAH0ahmbWn
OlFuhjuefXKnEgV4We0+UXgVCwOPjdAvBbI+e0ocS3MFEvzG6uBQE3xDk3SzynTn
jh8BCNAw1FtxNrQHusEwMFxIt4I7mKZ9YIqioymCzLq9gwQbooMDQaHWBfEbwrbw
qHyGO0aoSCqI3Haadr8faqU9GY/rOPNk3sgrDQoo//fb4hVC1CLQJ13hef4Y53CI
rU7m2Ys6xt0nUW7/vGT1M0NPAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNV
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBR5tFnme7bl5AFzgAiIyBpY9umbbjANBgkq
hkiG9w0BAQsFAAOCAgEAVR9YqbyyqFDQDLHYGmkgJykIrGF1XIpu+ILlaS/V9lZL
ubhzEFnTIZd+50xx+7LSYK05qAvqFyFWhfFQDlnrzuBZ6brJFe+GnY+EgPbk6ZGQ
3BebYhtF8GaV0nxvwuo77x/Py9auJ/GpsMiu/X1+mvoiBOv/2X/qkSsisRcOj/KK
NFtY2PwByVS5uCbMiogziUwthDyC3+6WVwW6LLv3xLfHTjuCvjHIInNzktHCgKQ5
ORAzI4JMPJ+GslWYHb4phowim57iaztXOoJwTdwJx4nLCgdNbOhdjsnvzqvHu7Ur
TkXWStAmzOVyyghqpZXjFaH3pO3JLF+l+/+sKAIuvtd7u+Nxe5AW0wdeRlN8NwdC
jNPElpzVmbUq4JUagEiuTDkHzsxHpFKVK7q4+63SM1N95R1NbdWhscdCb+ZAJzVc
oyi3B43njTOQ5yOf+1CceWxG1bQVs5ZufpsMljq4Ui0/1lvh+wjChP4kqKOJ2qxq
4RgqsahDYVvTH9w7jXbyLeiNdd8XM2w9U/t7y0Ff/9yi0GE44Za4rF2LN9d11TPA
mRGunUHBcnWEvgJBQl9nJEiU0Zsnvgc/ubhPgXRR4Xq37Z0j4r7g1SgEEzwxA57d
emyPxgcYxn/eR44/KJ4EBs+lVDR3veyJm+kXQ99b21/+jh5Xos1AnX5iItreGCc=
—–END CERTIFICATE—–
—–BEGIN CERTIFICATE—–
MIIFjTCCA3WgAwIBAgIRANOxciY0IzLc9AUoUSrsnGowDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTYxMDA2MTU0MzU1
WhcNMjExMDA2MTU0MzU1WjBKMQswCQYDVQQGEwJVUzEWMBQGA1UEChMNTGV0J3Mg
RW5jcnlwdDEjMCEGA1UEAxMaTGV0J3MgRW5jcnlwdCBBdXRob3JpdHkgWDMwggEi
MA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCc0wzwWuUuR7dyXTeDs2hjMOrX
NSYZJeG9vjXxcJIvt7hLQQWrqZ41CFjssSrEaIcLo+N15Obzp2JxunmBYB/XkZqf
89B4Z3HIaQ6Vkc/+5pnpYDxIzH7KTXcSJJ1HG1rrueweNwAcnKx7pwXqzkrrvUHl
Npi5y/1tPJZo3yMqQpAMhnRnyH+lmrhSYRQTP2XpgofL2/oOVvaGifOFP5eGr7Dc
Gu9rDZUWfcQroGWymQQ2dYBrrErzG5BJeC+ilk8qICUpBMZ0wNAxzY8xOJUWuqgz
uEPxsR/DMH+ieTETPS02+OP88jNquTkxxa/EjQ0dZBYzqvqEKbbUC8DYfcOTAgMB
AAGjggFnMIIBYzAOBgNVHQ8BAf8EBAMCAYYwEgYDVR0TAQH/BAgwBgEB/wIBADBU
BgNVHSAETTBLMAgGBmeBDAECATA/BgsrBgEEAYLfEwEBATAwMC4GCCsGAQUFBwIB
FiJodHRwOi8vY3BzLnJvb3QteDEubGV0c2VuY3J5cHQub3JnMB0GA1UdDgQWBBSo
SmpjBH3duubRObemRWXv86jsoTAzBgNVHR8ELDAqMCigJqAkhiJodHRwOi8vY3Js
LnJvb3QteDEubGV0c2VuY3J5cHQub3JnMHIGCCsGAQUFBwEBBGYwZDAwBggrBgEF
BQcwAYYkaHR0cDovL29jc3Aucm9vdC14MS5sZXRzZW5jcnlwdC5vcmcvMDAGCCsG
AQUFBzAChiRodHRwOi8vY2VydC5yb290LXgxLmxldHNlbmNyeXB0Lm9yZy8wHwYD
VR0jBBgwFoAUebRZ5nu25eQBc4AIiMgaWPbpm24wDQYJKoZIhvcNAQELBQADggIB
ABnPdSA0LTqmRf/Q1eaM2jLonG4bQdEnqOJQ8nCqxOeTRrToEKtwT++36gTSlBGx
A/5dut82jJQ2jxN8RI8L9QFXrWi4xXnA2EqA10yjHiR6H9cj6MFiOnb5In1eWsRM
UM2v3e9tNsCAgBukPHAg1lQh07rvFKm/Bz9BCjaxorALINUfZ9DD64j2igLIxle2
DPxW8dI/F2loHMjXZjqG8RkqZUdoxtID5+90FgsGIfkMpqgRS05f4zPbCEHqCXl1
eO5HyELTgcVlLXXQDgAWnRzut1hFJeczY1tjQQno6f6s+nMydLN26WuU4s3UYvOu
OsUxRlJu7TSRHqDC3lSE5XggVkzdaPkuKGQbGpny+01/47hfXXNB7HntWNZ6N2Vw
p7G6OfY+YQrZwIaQmhrIqJZuigsrbe3W+gdn5ykE9+Ky0VgVUsfxo52mwFYs1JKY
2PGDuWx8M6DlS6qQkvHaRUo0FMd8TsSlbF0/v965qGFKhSDeQoMpYnwcmQilRh/0
ayLThlHLN81gSkJjVrPI0Y8xCVPB4twb1PFUd2fPM3sA1tJ83sZ5v8vgFv2yofKR
PB0t6JzUA81mSqM3kxl5e+IZwhYAyO0OTg3/fs8HqGTNKd9BqoUwSRBzp06JMg5b
rUCGwbCUDI0mxadJ3Bz4WxR6fyNpBK2yAinWEsikxqEt
—–END CERTIFICATE—–

Public Client Cert

In the .ovpn file Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

In the .ovpn file Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Hotspot Shield connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit Hotspot Shield’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Hotspot Shield.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Hotspot Shield server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new Public Client Cert and Private Client Key.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PPPoE Internet Setup

TeamFlashRouters · Mar 21, 2019 ·

Most ISPs do not require PPPoE credentials. If you are certain this is an ISP requirement in your setup, we kindly ask that you get in touch with your ISP to verify that they do in fact require PPPoE authentication and to provide you with the correct credentials to enter into your FlashRouter.

Before you enter your PPPoE credentials, you should have already setup your FlashRouter in a Single Router Setup with correct wiring. Once you enter PPPoE credentials you should then be able to connect to the internet.

If you are using a Dual Router Setup there is no need to enter PPPoE credentials if they are already entered in the existing router. You can disregard this article.

Enter your PPPoE credentials

DD-WRT Firmware

Navigate to Setup > Basic Setup

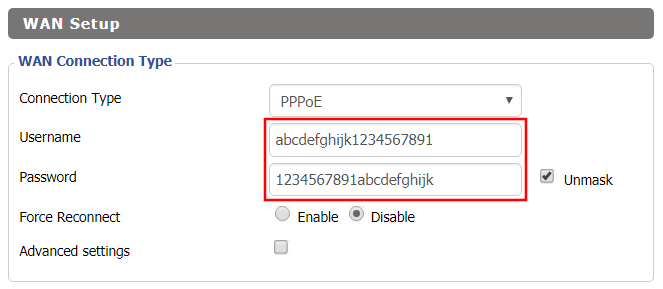
Access FlashRouters DD-WRT Admin Settings - Enter PPPOE Username and Password
  1. Set the Connection Type dropdown to PPPoE.
  2. Enter your ISP assigned PPPoE username and password.
  3. Click Apply Settings.

Power cycle your network devices

  1. Power off your ISP modem and the FlashRouter.
  2. Power on the ISP modem and wait for it to fully boot up.
  3. Power on the FlashRouter.

Verify a successful Internet connection

Once the FlashRouter is booted up connect one of your devices to the FlashRouter via Ethernet or Wireless.

Visit any website and make sure the page fully loads. Once you have verified a successful Internet connection, begin connecting your network devices to the FlashRouter via wired or WiFi.

Please be aware that our support is not able to replicate PPPoE issues on our end, which makes them challenging to troubleshoot. In the event of an issue we recommend using a Dual Router Setup.

Connecting to OpenVPN on Asus Merlin Firmware

TeamFlashRouters · Sep 22, 2021 ·

To setup VPN on your Asuswrt Merlin router, you will need to first download an OpenVPN (.ovpn) file from your VPN service provider and load it onto your router.

Review your specific VPN service instructions below. Follow these instructions to locate and upload your OpenVPN file. Depending on the VPN service, there may be additional steps and configurations required to complete the setup.

NordVPN

ExpressVPN

IPVanish

Astrill

Hide.Me

Hotspot Shield

IVPN

Mullvad

SaferVPN

StrongVPN

SurfShark

TorGuard

VPNUnlimited

VyprVPN

Windscribe

Using Asuswrt Merlin’s VPN Director, your router can store up to five different VPN connections and switch between them at will.

PureVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual PureVPN Setup

Verify your PureVPN login information

If you are not already an PureVPN user Sign Up Now.

Log in to your account on the PureVPN website.

PureVPN Website Login

Navigate to the Home page and note the VPN username on this page. You will need this specific username later on in the configuration process.
Ex: purevpn0s1234567

PureVPN Server Addresses

View a full list of PureVPN servers.

United States

Miami:
usfl1-ovpn-udp.pointtoserver.com

Seattle:
ussa-ovpn-udp.pointtoserver.com

Houston
:
ustx1-ovpn-tcp.pointtoserver.com

Georgia
:
usga1-ovpn-udp.pointtoserver.com

New Jersey
:
usnj1-ovpn-udp.pointtoserver.com

Washington
:
uswdc1-ovpn-udp.pointtoserver.com

Chicago
:
usil1-ovpn-udp.pointtoserver.com

Phoenix
:
usphx1-ovpn-udp.pointtoserver.com

Los Angeles
:
usla1-ovpn-udp.pointtoserver.com

Virginia
:
vlbr-usvc1-ovpn-udp.pointtoserver.com

San Francisco
:
vlsa-ussf1-ovpn-udp.pointtoserver.com

New York
:
usny1-ovpn-udp.pointtoserver.com

Ohio
:
vleu-usoh1-ovpn-udp.pointtoserver.com

United Kingdom

London:
ukl1-ovpn-udp.pointtoserver.com

Gosport:
ukg1-ovpn-udp.pointtoserver.com

Maidenhead:
ukm1-ovpn-udp.pointtoserver.com

Manchester
:
vlus-uk-man1-ovpn-udp.pointtoserver.com

Leicester
:
vlap-ukle1-ovpn-udp.pointtoserver.com

DD-WRT Router Setup for PureVPN

Navigate to Services > VPN

Enter PureVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PureVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

53

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

Userpass Authentication

Enable

Username

Enter the Username you noted from the Home page above.
Ex: purevpn0s1234567

Password

Enter the Password you successfully logged in to your PureVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
e30af995f56d07426d9ba1f824730521
d4283db4b4d0cdda9c6e8759a3799dcb
7939b6a5989160c9660de0f6125cbb1f
585b41c074b2fe88ecfcf17eab9a33be
1352379cdf74952b588fb161a93e13df
9135b2b29038231e02d657a6225705e6
868ccb0c384ed11614690a1894bfbeb2
74cebf1fe9c2329bdd5c8a40fe882062
4d2ea7540cd79ab76892db51fc371a3a
c5fc9573afecb3fffe3281e61d72e915
79d9b03d8cbf7909b3aebf4d90850321
ee6b7d0a7846d15c27d8290e031e951e
19438a4654663cad975e138f5bc5af89
c737ad822f27e19057731f41e1e254cc
9c95b7175c622422cde9f1f2cfd3510a
dd94498b4d7133d3729dd214a16b27fb
-----END OpenVPN Static key V1-----

Additional Config

tls-cipher “DEFAULT:@SECLEVEL=0”

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIEoTCCA4mgAwIBAgIJANysBdFD6U2oMA0GCSqGSIb3DQEBBQUAMIGRMQswCQYD
VQQGEwJISzELMAkGA1UECBMCSEsxETAPBgNVBAcTCEhvbmdLb25nMRAwDgYDVQQK
EwdQdXJlVlBOMQswCQYDVQQLEwJJVDEQMA4GA1UEAxMHUHVyZVZQTjEQMA4GA1UE
KRMHUHVyZVZQTjEfMB0GCSqGSIb3DQEJARYQbWFpbEBob3N0LmRvbWFpbjAeFw0x
NDA0MTAwNzI5NDlaFw0yNDA0MDcwNzI5NDlaMIGRMQswCQYDVQQGEwJISzELMAkG
A1UECBMCSEsxETAPBgNVBAcTCEhvbmdLb25nMRAwDgYDVQQKEwdQdXJlVlBOMQsw
CQYDVQQLEwJJVDEQMA4GA1UEAxMHUHVyZVZQTjEQMA4GA1UEKRMHUHVyZVZQTjEf
MB0GCSqGSIb3DQEJARYQbWFpbEBob3N0LmRvbWFpbjCCASIwDQYJKoZIhvcNAQEB
BQADggEPADCCAQoCggEBAJYqtUkQTlf/pHcGXuuII8S3pfI0fwFbs7l/1RP3nX3n
v1vyuvLi7h0jWsgJU0XM7LJywiRFJ8zsMLH7KZnIg7bscb50GY75WIq7C2NnWnnS
7zzyCCm2XD/2xZPym2lVRytpnWJbpemSS6Hdz7xI3q2FmixuBa1t5FeKsXfeaGGg
+ohwLvamnGHJYUYu3Nu0EWVzzy5wgT0c2C5jleGxl3kxRimD8FpnlAVdqyt0ib/f
f9XanaotSopIHUZmpYjT+udRC2+harlNKvOXYgDRl1mpimCvlzEWpZAo8dyBCxWl
xlBIT8OA8rimGi1XviknuOlWu2cGi13Ug8mCG0MjOQ0CAwEAAaOB+TCB9jAdBgNV
HQ4EFgQUt+1vJ2X2ho12PUDhdo2CsSHYXbYwgcYGA1UdIwSBvjCBu4AUt+1vJ2X2
ho12PUDhdo2CsSHYXbahgZekgZQwgZExCzAJBgNVBAYTAkhLMQswCQYDVQQIEwJI
SzERMA8GA1UEBxMISG9uZ0tvbmcxEDAOBgNVBAoTB1B1cmVWUE4xCzAJBgNVBAsT
AklUMRAwDgYDVQQDEwdQdXJlVlBOMRAwDgYDVQQpEwdQdXJlVlBOMR8wHQYJKoZI
hvcNAQkBFhBtYWlsQGhvc3QuZG9tYWluggkA3KwF0UPpTagwDAYDVR0TBAUwAwEB
/zANBgkqhkiG9w0BAQUFAAOCAQEAAhLQQmkKWJdyGqgMSKOWXSKN2WXTDjIdb9bK
Q8uHeq0LYCcPoRh8VYJg2X4UWR/KO9pKaG+iZJw4Jqz4GQJjjJLKHfsWwj790ay0
7U5KT08qmxFaxZUYn663H9b0+Zud1spTsTJjVe1eoRk6IDbbB4OMUzN9zyWEn6er
xi6llIAjQX1qtlBQasmTAbRtbSsCsZAxL2kXysULIdLrQP0iTgMQqqkv5zvpdEKN
3ciKCd8OHEhHOlAwA0/DNy3dg3Et0F2hNMDJhqMpxXsbKtGJ/rzGXQF2geEVzLZA
o42I1wBOSZLTX1fO1gl3gAGS9aYg5o31rrpBKzQewitJgIuc+Q==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PureVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PureVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PureVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the PureVPN server

  1. Copy the new PureVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Wireless Repeater Setup

TeamFlashRouters · Apr 16, 2019 ·

If you need to extend your wireless and wired connection capabilities, you can setup a FlashRouter as a Wireless Repeater. In Wireless Repeater mode the FlashRouter connects to your main router via WiFi and then creates a completely separate network segment for you. This new “repeater” network then transmits your internet signal via FlashRouter LAN ports for wired internet access while also creating a new Wireless Extender network that will expand your wireless network range throughout your home or office just like a mesh network.

Preparing for Wireless Repeater Setup

Verify your wireless information

To connect your FlashRouter wirelessly to your existing wireless network you will need the Wireless Network Name (SSID) and Wireless Password of the existing wireless network that you will repeat. Verify and note this information.

We recommend using a 2.4GHz network to repeat as this network will have more range. Be sure to click Add under the 2.4GHz settings and not the 5GHz settings.

DD-WRT Router Setup for Wireless Repeater

Disable Firewall

Navigate to Security > Firewall

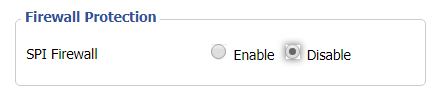
Wireless Repeater Setup on DD-WRT FlashRouter - Disable SPI Firewall
  1. Set SPI Firewall to Disable.
  2. Click Save.

Enter Wireless settings

Navigate to Wireless > Basic Settings

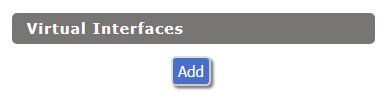
Select Add in the Virtual Interface area.

Wireless Repeater Setup on DD-WRT FlashRouter - Add Virtual Interface

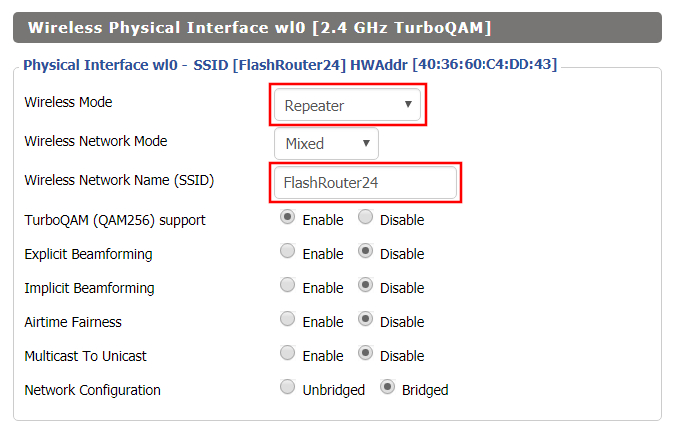
In the Wireless Physical Interface settings for the 2.4GHz network set the Wireless Mode to Repeater.

FlashRouters with a Broadcom chipset will have Repeater as an option in the dropdown but FlashRouters with an Atheroes chipset will not. Select Client or Client (Routed) if Repeater is not listed for your FlashRouter.

Change the Wireless Network Name (SSID) to match exactly with the Wireless Network Name of the network that you will repeat.

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Mode to Repeater

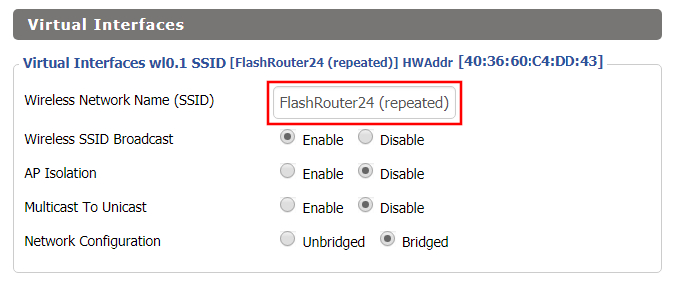
In the Virtual Interfaces settings change the Wireless Network Name (SSID) to FlashRouter24 or any other unique SSID.

Wireless Repeater Setup on DD-WRT FlashRouter - Set SSID for Repeated Band

CLICK SAVE

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Password
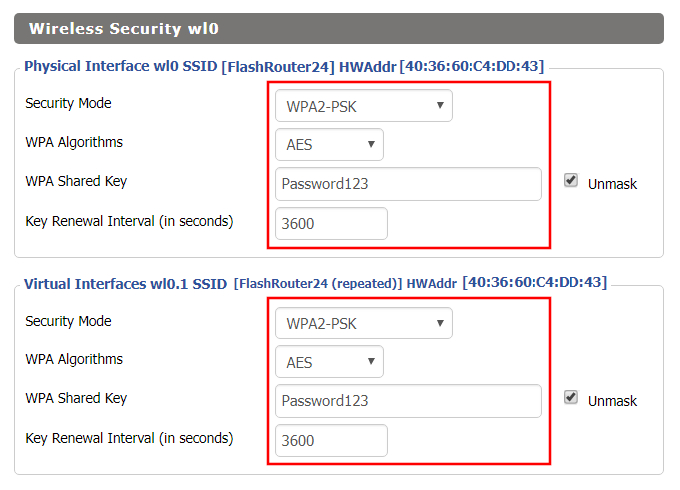
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Change the WPA Shared Key to match exactly with the Wireless Password of the network that you will repeat.
  3. Click Apply Settings.

Verify the Internet Connection

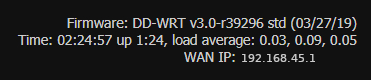
In the top right hand corner of the DD-WRT you should see the WAN IP change from 0.0.0.0 to an actual IP Address. Once this changes navigate to any website to test your Internet connection.

Wireless Repeater Setup on DD-WRT FlashRouter - Verify WAN Connection

Back up your settings

Navigate to the Administration > Backup page.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

VyprVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual VyprVPN Setup

Verify your VyprVPN login information

If you are not already a VyprVPN user Sign Up Now.

Log in to your account on the VyprVPN website.

VyprVPN - Website Login

VyprVPN Server Addresses

United States

Los Angeles, CA us1.vpn.goldenfrog.com
Washington, DC us2.vpn.goldenfrog.com
Austin, TX us3.vpn.goldenfrog.com
Miami, FL us4.vpn.goldenfrog.com
New York City, NY us5.vpn.goldenfrog.com
Chicago, IL us6.vpn.goldenfrog.com
San Francisco, CA us7.vpn.goldenfrog.com
Seattle, WA us8.vpn.goldenfrog.com

United Kingdom

 London uk1.vpn.goldenfrog.com

Canada

Toronto ca1.vpn.goldenfrog.com

Australia

Sydney au1.vpn.goldenfrog.com
Melbourne au2.vpn.goldenfrog.com
Perth au3.vpn.goldenfrog.com

Germany

Frankfurt de1.vpn.goldenfrog.com

Rest of the World

UAE – Dubai ae1.vpn.goldenfrog.com
Argentina – Buenos Aires ar1.vpn.goldenfrog.com
Austria – Vienna at1.vpn.goldenfrog.com
Belgium – Brussels be1.vpn.goldenfrog.com
Bulgaria – Sofia bg1.vpn.goldenfrog.com
Bahrain – Manama bh1.vpn.goldenfrog.com
Brazil – São Paulo br1.vpn.goldenfrog.com
Switzerland – Zurich ch1.vpn.goldenfrog.com
Colombia – Bogotá co1.vpn.goldenfrog.com
Costa Rica – San José cr1.vpn.goldenfrog.com
Czech Republic – Prague cz1.vpn.goldenfrog.com
Germany – Frankfurt de1.vpn.goldenfrog.com
Denmark – Copenhagen dk1.vpn.goldenfrog.com
Algeria – Algiers dz1.vpn.goldenfrog.com
Egypt – Cairo eg1.vpn.goldenfrog.com
Spain – Madrid es1.vpn.goldenfrog.com
Netherlands – Amsterdam eu1.vpn.goldenfrog.com
Finland – Helsinki fi1.vpn.goldenfrog.com
France – Paris fr1.vpn.goldenfrog.com
Greece – Athens gr1.vpn.goldenfrog.com
Hong Kong – Hong Kong hk1.vpn.goldenfrog.com
Indonesia – Jakarta id1.vpn.goldenfrog.com
Ireland – Dublin ie1.vpn.goldenfrog.com
Israel – Tel Aviv il1.vpn.goldenfrog.com
India – Mumbai in1.vpn.goldenfrog.com
Iceland – Reykjavík is1.vpn.goldenfrog.com
Italy – Rome it1.vpn.goldenfrog.com
Japan – Tokyo jp1.vpn.goldenfrog.com
South Korea – Seoul kr1.vpn.goldenfrog.com
Liechtenstein – Schaan li1.vpn.goldenfrog.com
Lithuania – Vilnius lt1.vpn.goldenfrog.com
Luxembourg – Luxembourg City lu1.vpn.goldenfrog.com
Latvia – Riga lv1.vpn.goldenfrog.com
Marshall Islands – Majuro mh1.vpn.goldenfrog.com
Macao – Macao mo1.vpn.goldenfrog.com
Maldives – Malé mv1.vpn.goldenfrog.com
Mexico – Mexico City mx1.vpn.goldenfrog.com
Malaysia – Kuala Lumpur my1.vpn.goldenfrog.com
Norway – Oslo no1.vpn.goldenfrog.com
New Zealand – Auckland nz1.vpn.goldenfrog.com
Panama – Panama City pa1.vpn.goldenfrog.com
Philippines – Manila ph1.vpn.goldenfrog.com
Pakistan – Karachi pk1.vpn.goldenfrog.com
Poland – Warsaw pl1.vpn.goldenfrog.com
Portugal – Lisbon pt1.vpn.goldenfrog.com
Qatar – Doha qa1.vpn.goldenfrog.com
Romania – Bucharest ro1.vpn.goldenfrog.com
Russia – Moscow ru1.vpn.goldenfrog.com
Saudi Arabia – Riyadh sa1.vpn.goldenfrog.com
Sweden – Stockholm se1.vpn.goldenfrog.com
Singapore – Singapore sg1.vpn.goldenfrog.com
Slovenia – Ljubljana si1.vpn.goldenfrog.com
Slovakia – Bratislava sk1.vpn.goldenfrog.com
El Salvador – San Salvador sv1.vpn.goldenfrog.com
Thailand – Bangkok th1.vpn.goldenfrog.com
Turkey – Istanbul tr1.vpn.goldenfrog.com
Taiwan – Taipei tw1.vpn.goldenfrog.com
Ukraine – Kiev ua1.vpn.goldenfrog.com
Uruguay – Montevideo uy1.vpn.goldenfrog.com
Vietnam – Hanoi vn1.vpn.goldenfrog.com

DD-WRT Router Setup for VyprVPN

Navigate to Services > VPN

VyprVPN offers two different Encryption levels:

Default Encryption (Blowfish-CBC)
typically provides faster speeds.

Strong Encryption (AES-256) provides stronger encryption.

Follow the table below of the one that fits your needs.

Enter VyprVPN settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change VyprVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

Blowfish-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your VyprVPN account with.

Password

Enter the Password you successfully logged in to your VyprVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
keepalive 10 60
persist-key
persist-tun
persist-remote-ip
nobind

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter VyprVPN settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change VyprVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your VyprVPN account with.

Password

Enter the Password you successfully logged in to your VyprVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
keepalive 10 60
persist-key
persist-tun
persist-remote-ip
nobind
tls-cipher TLS-DHE-RSA-WITH-AES-256-CBC-SHA

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing. Learn more here.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VyprVPN connection

Navigate to the Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit to WhatIsMyIPAddress to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to VyprVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the VyprVPN server

  1. Copy the new VyprVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field and Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN Merlin WireGuard Setup

TeamFlashRouters · Mar 30, 2023 ·

Preparing for ProtonVPN Merlin Setup

Download your ProtonVPN .conf file

If you are not already an ProtonVPN user Sign Up Now.

1. Log in to your account on the ProtonVPN website.

ProtonVPN Account Sign in

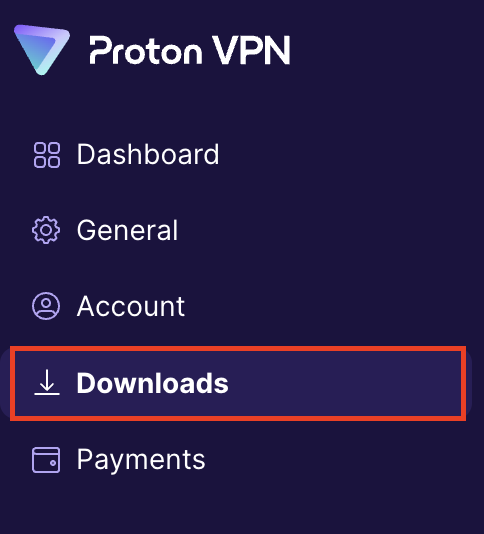
2. Click Downloads.

ProtonVPN Downloads

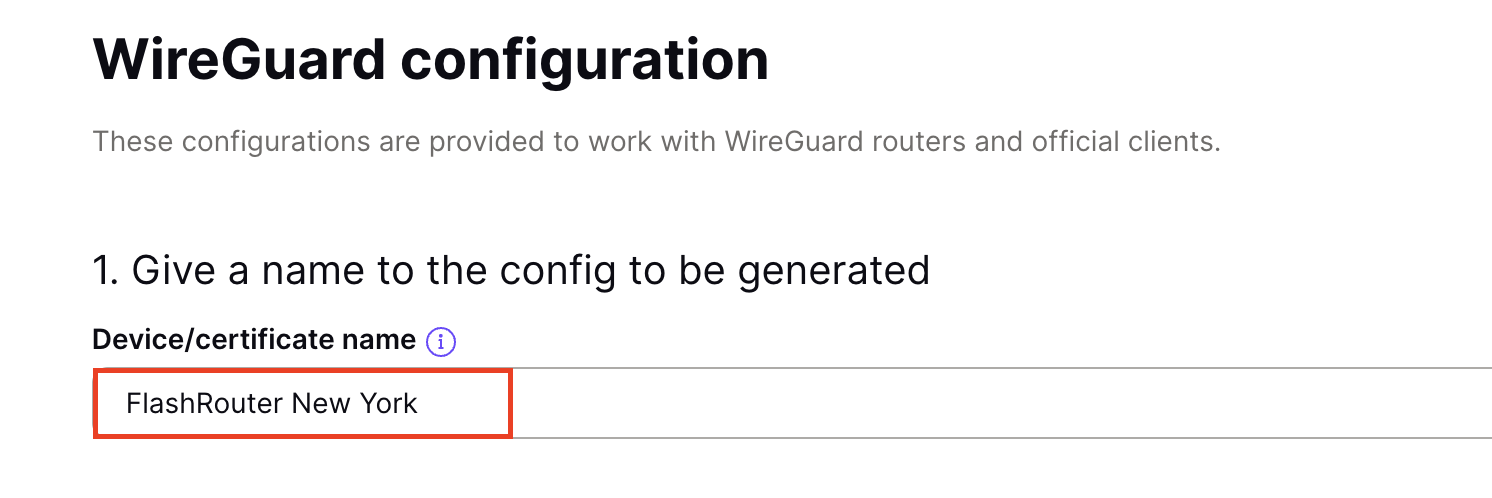
3. Scroll down to WireGuard configuration and name the device FlashRouter.

ProtonVPN WireGuard Configuration Name

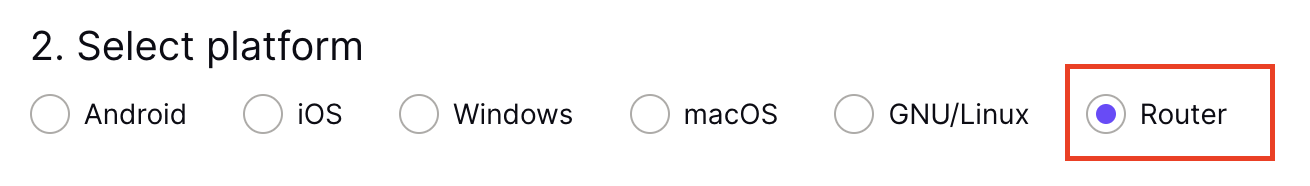
4. Select Router as the platform.

ProtonVPN WireGuard select Platform

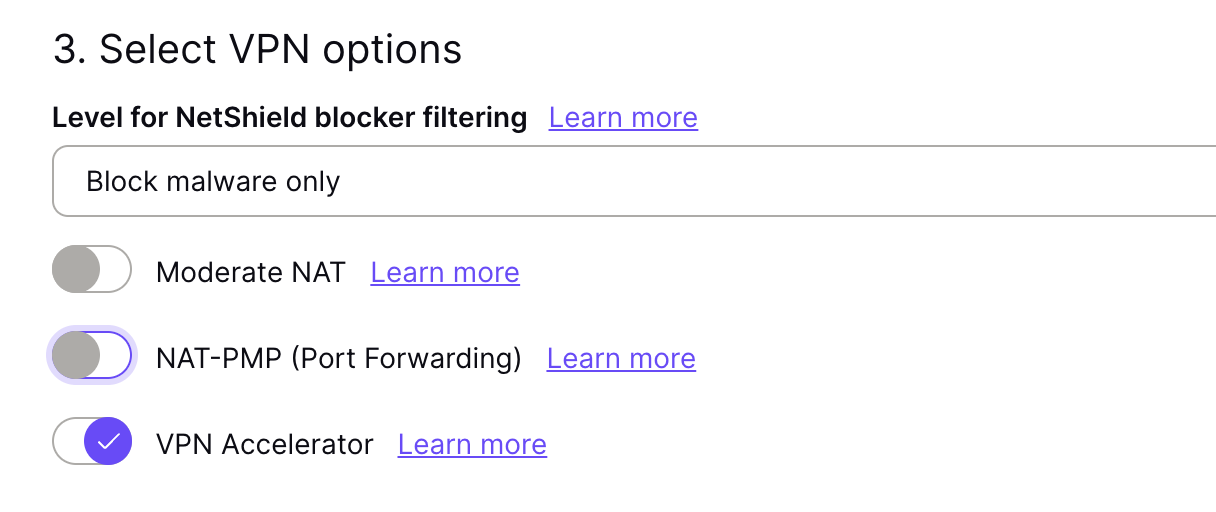
5. Select the VPN options that best fit your needs. We typically use the settings as seen in the screenshot here if you are unsure.

ProtonVPN WireGuard VPN options

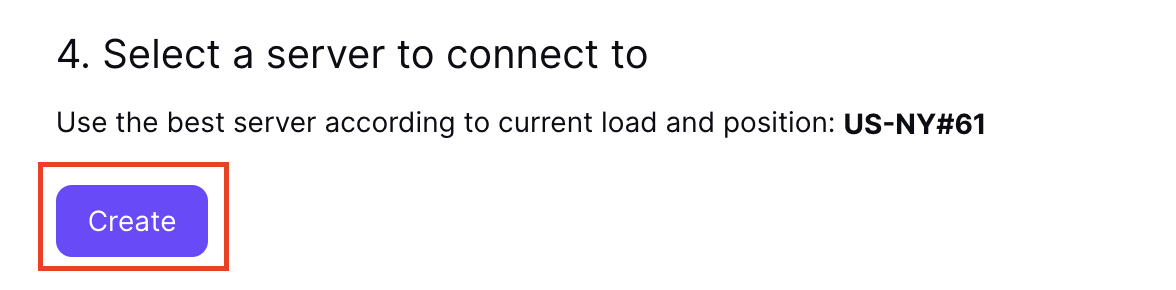
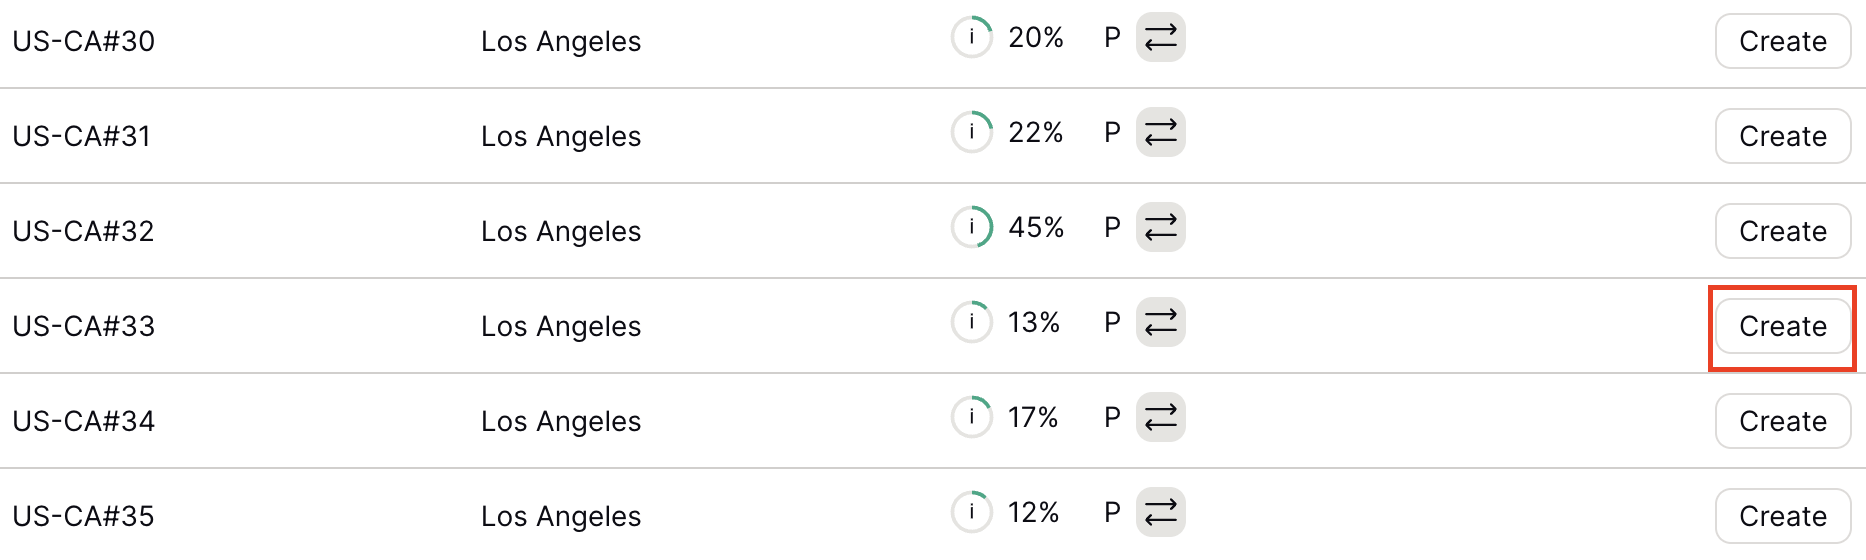
6. Next select the server that you would like to connect to and click Create. At the top of the page you’ll see ProtonVPN’s recommended server which we recommend using unless you need to connect to a specific location.

If you need a specific server location find it in the list and click Create.

ProtonVPN WireGuard recommended server
ProtonVPN WireGuard specific server

7. After clicking Create a new window will appear. Click Download to download the .conf file to your computer.

Merlin Router Setup for ProtonVPN

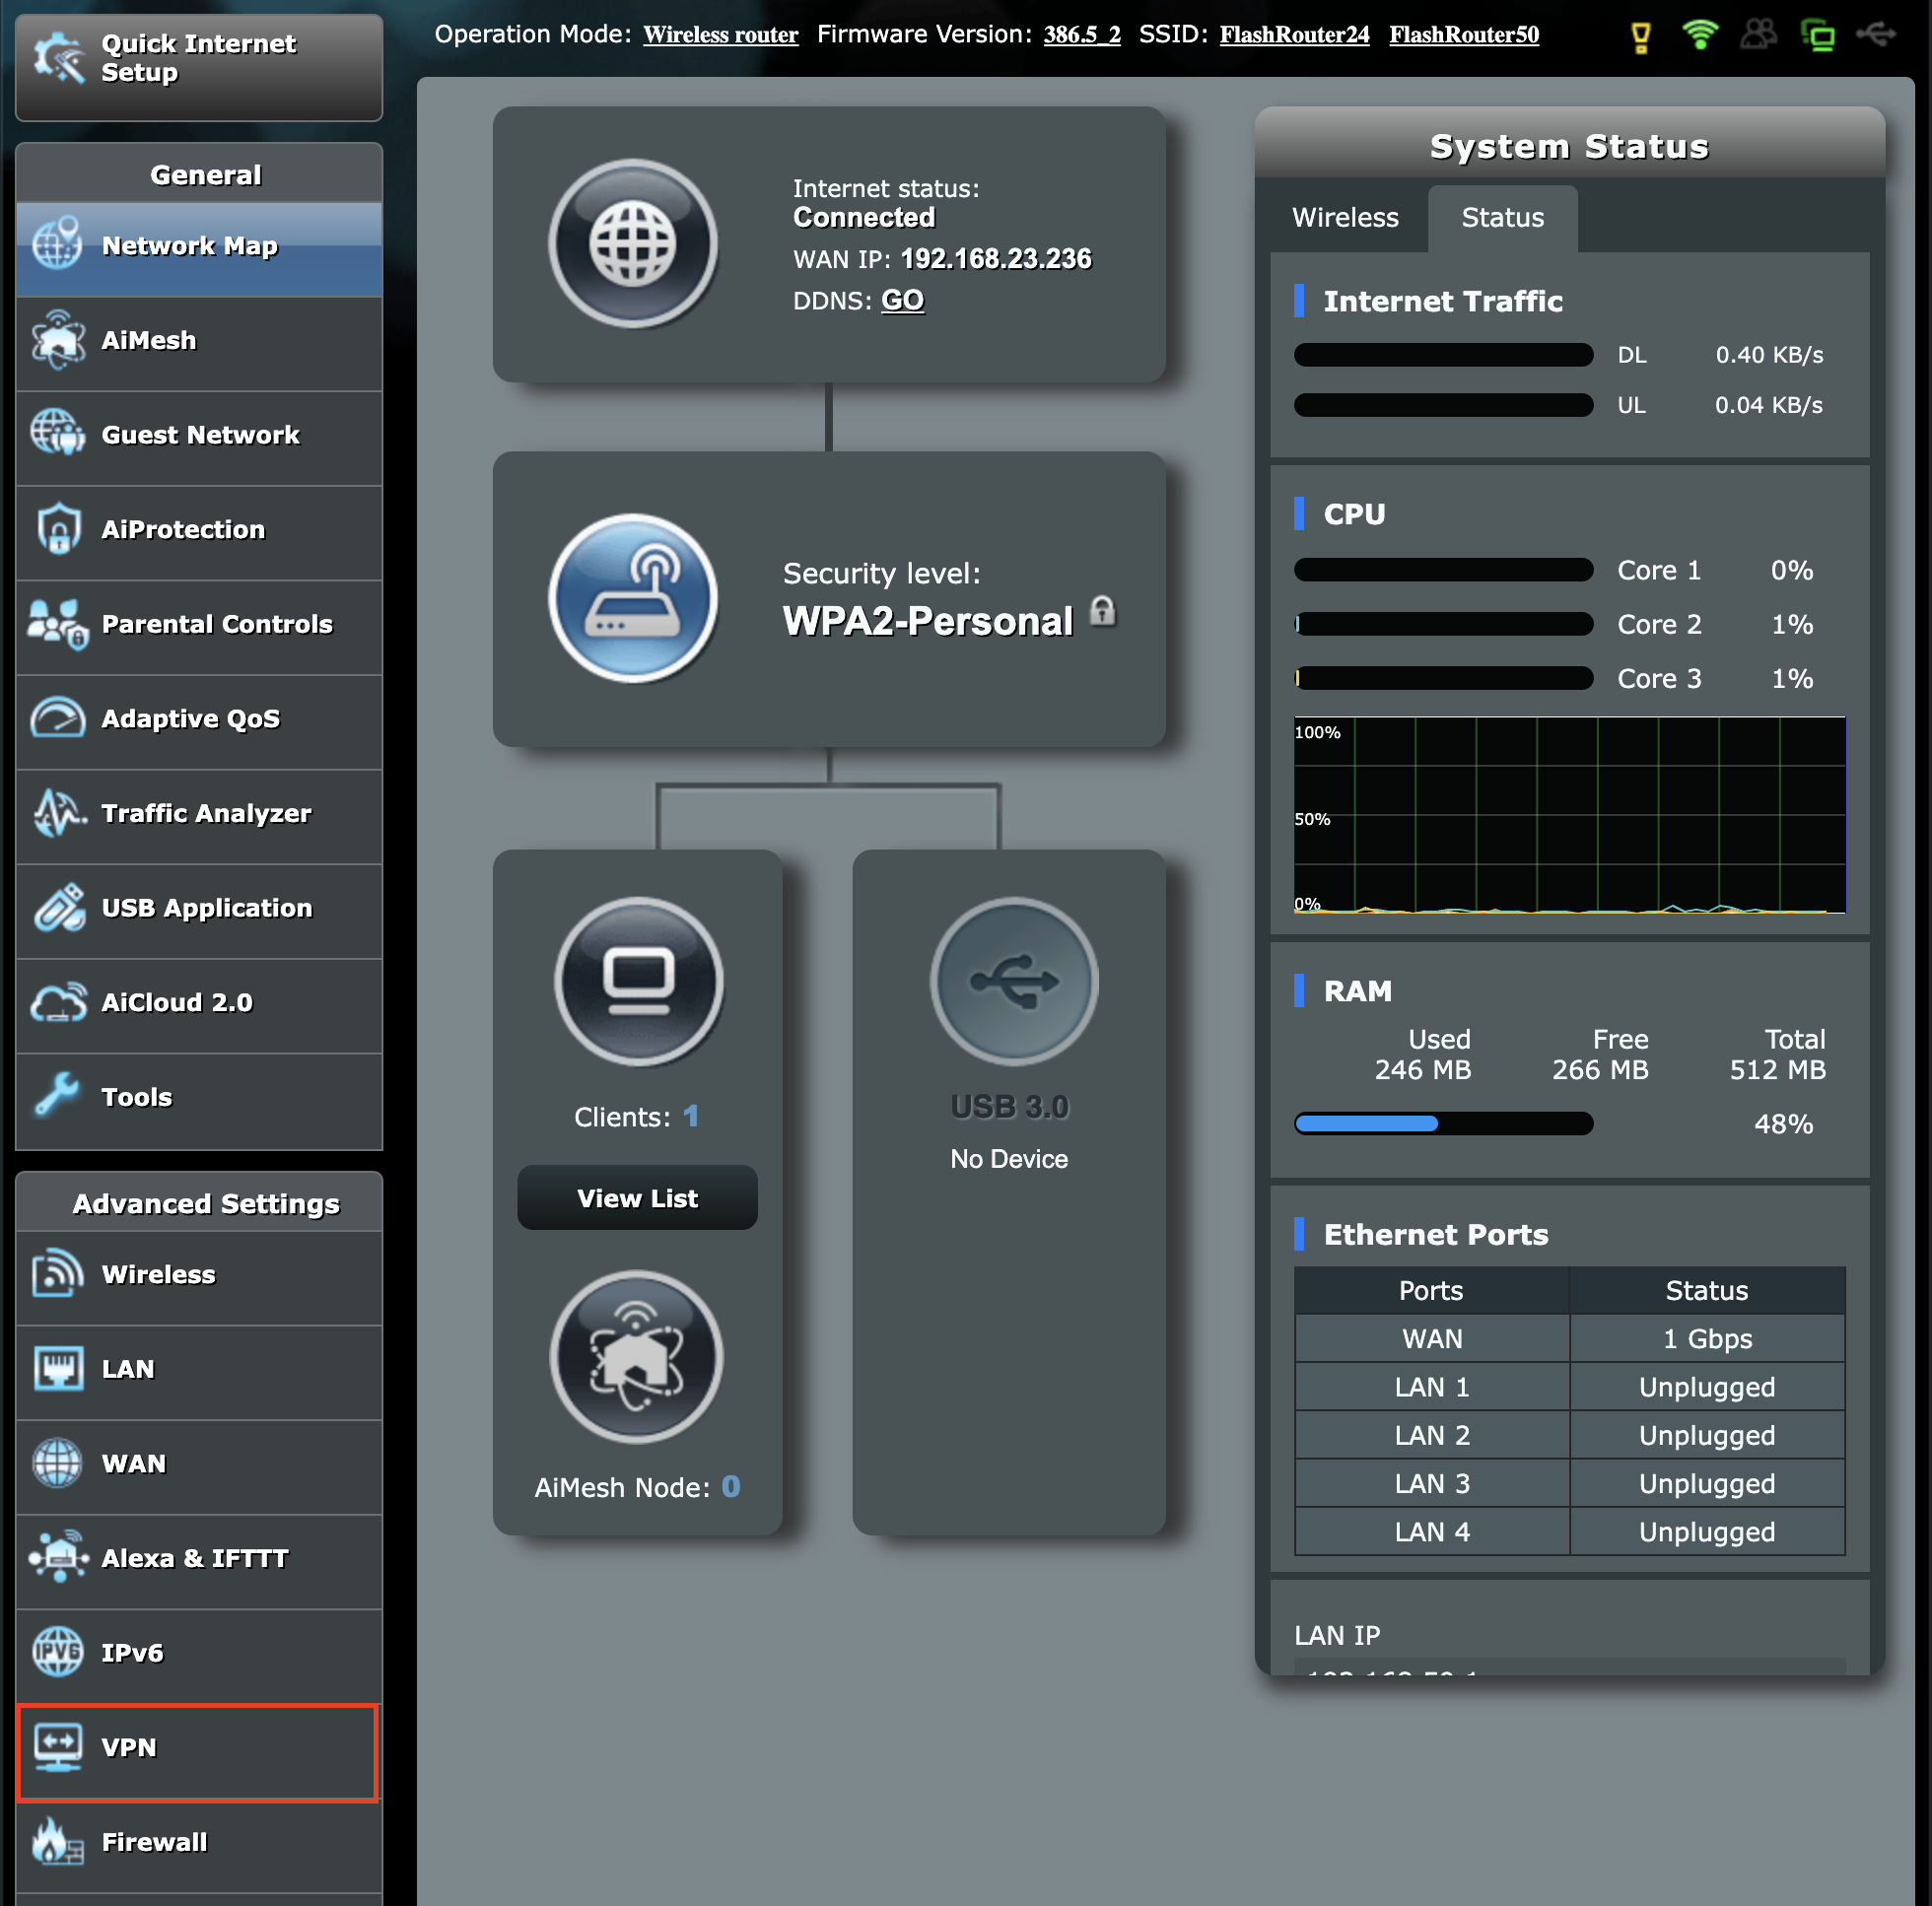
Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

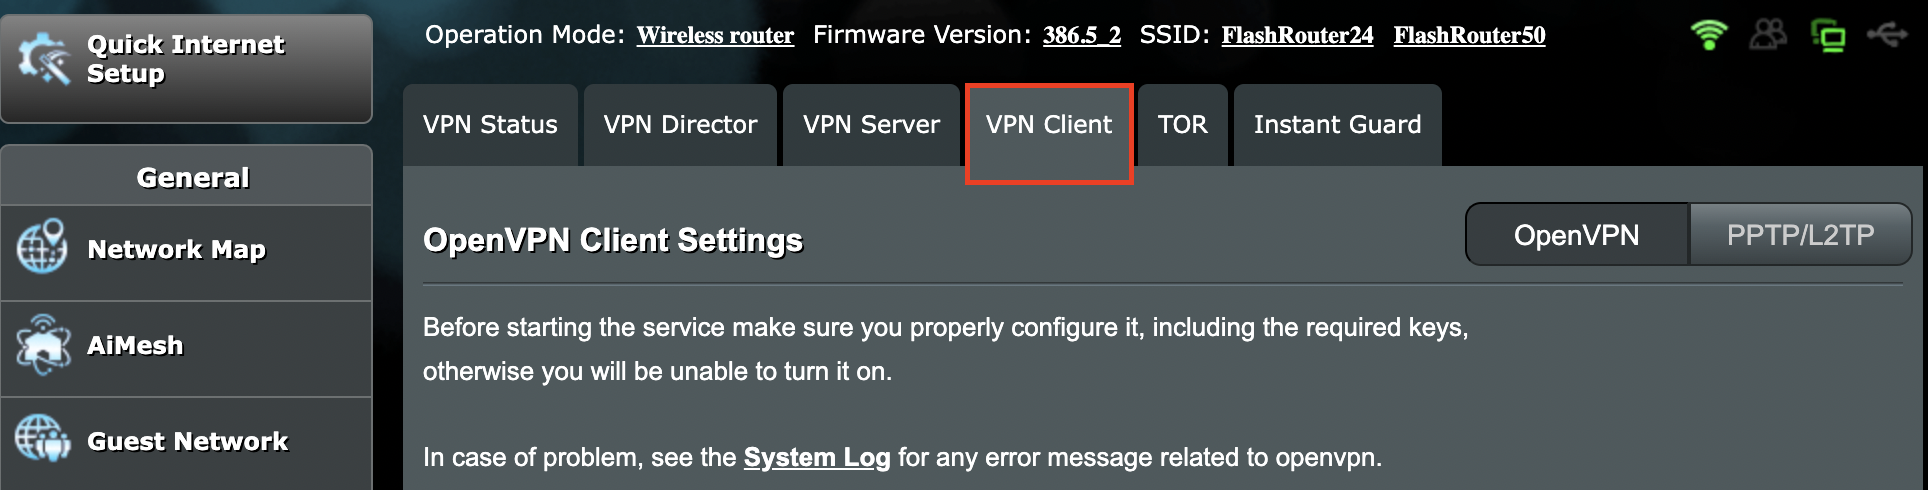
Merlin VPN Client Tab

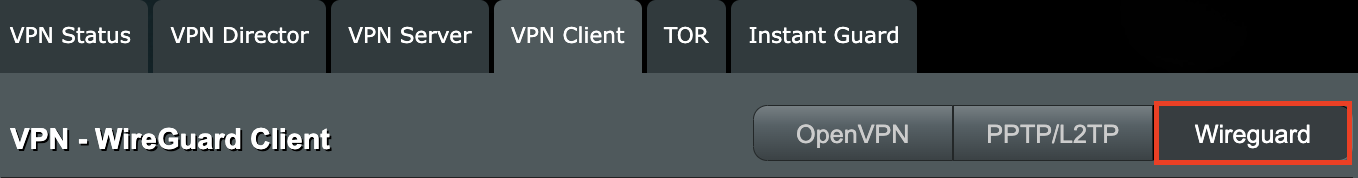
3. Select WireGuard as the VPN Protocol.

Merlin VPN Client WireGuard

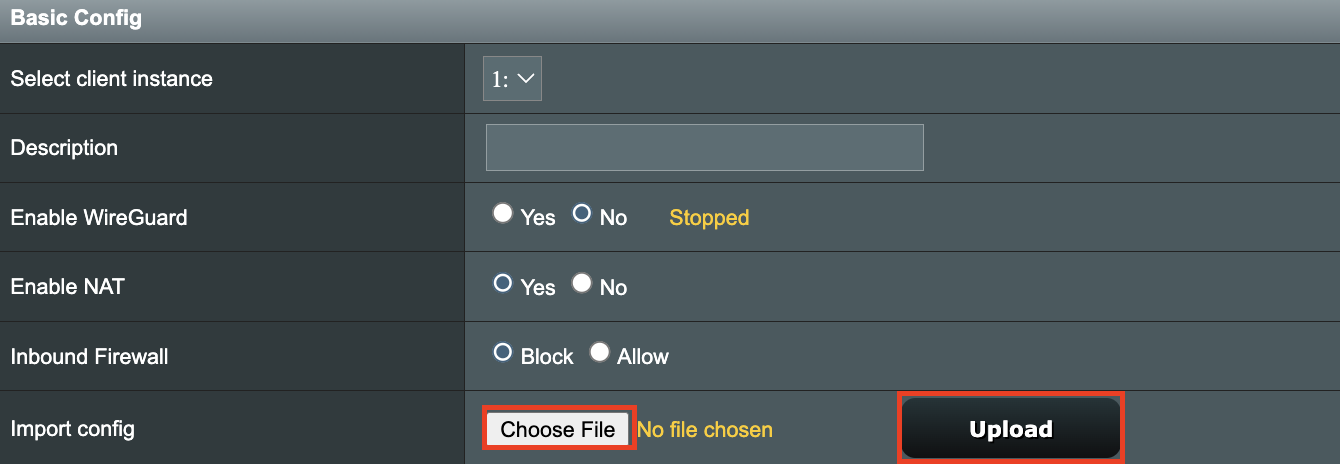
4. Click Choose file and select the .conf file you downloaded earlier. Then click Upload.

Merlin WireGuard Choose File Upload

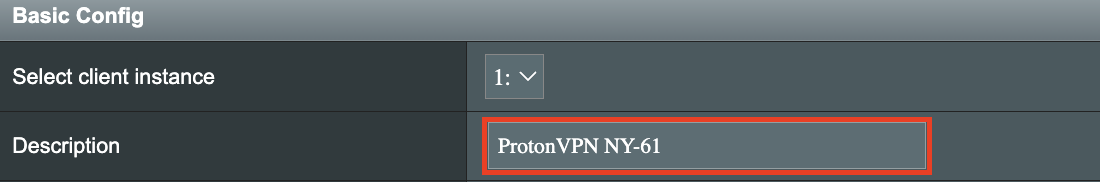
5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location here. Our example server was in US-NY#61 so I have entered in ProtonVPN NY-61.

Merlin WireGuard ProtonVPN Description

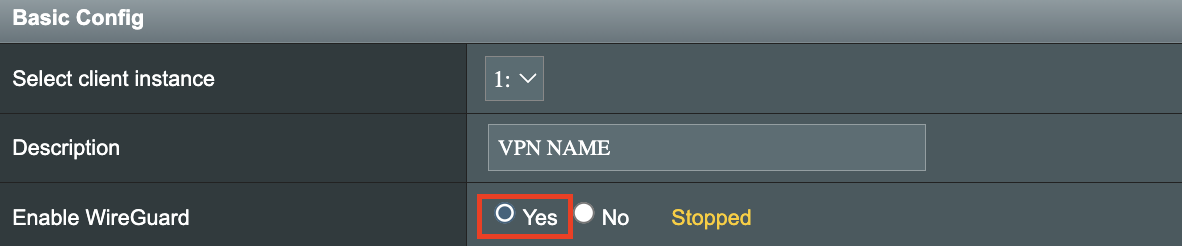
6. Set Enable WireGuard to Yes.

Merlin Enable WireGuard

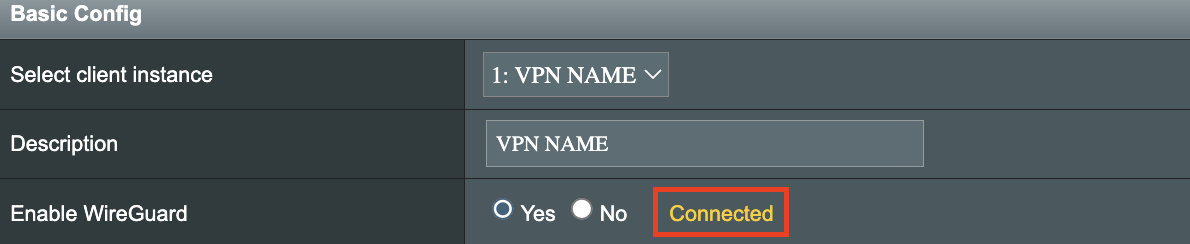
7. Click Apply at the bottom of the page and you should then see a Connected message appear.

Merlin WireGuard Connected

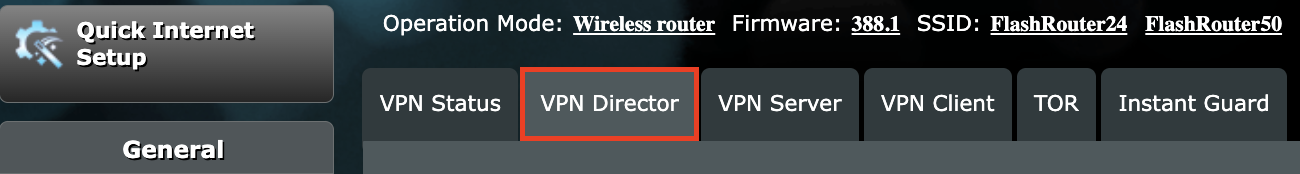
8. By default no devices are assigned to the new active WireGuard connection profile. Click the VPN Director tab to assign specific devices to the new WireGuard profile. Your IP will not be changed on your devices yet.

WireGuard select VPN Director

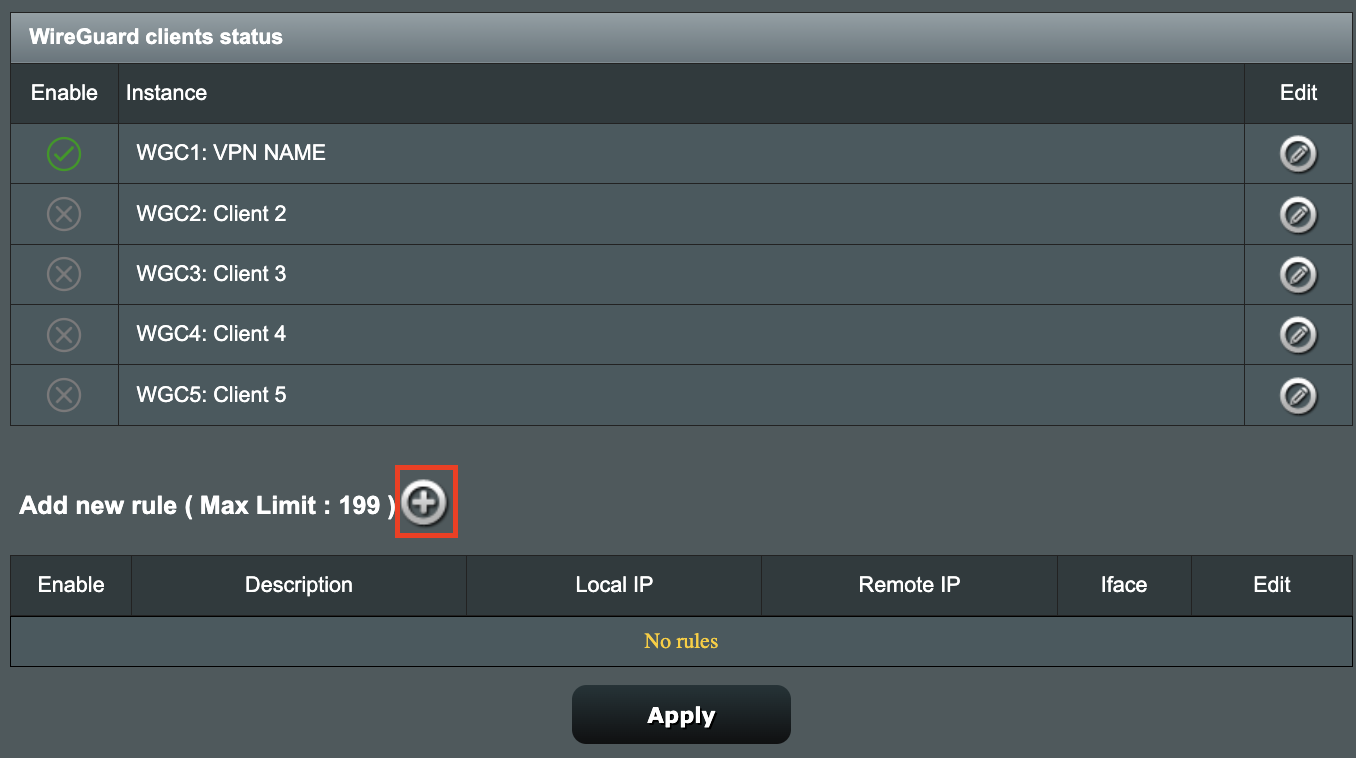
9. On the VPN Director page click the + symbol next to Add new rule.

WireGuard VPN Director Add new rule

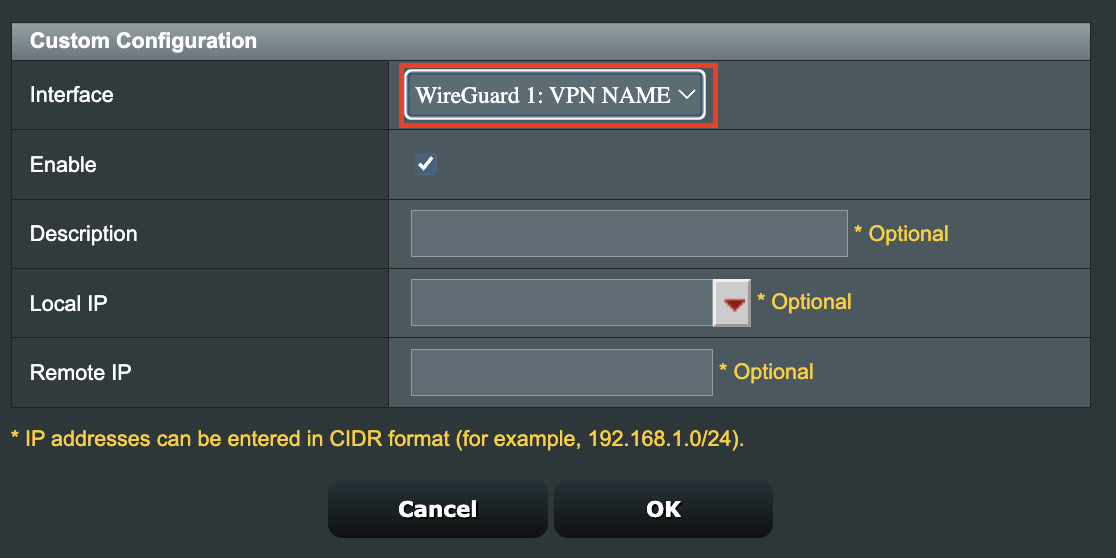
10. Select the new WireGuard profile in the Interface dropdown.

WireGuard VPN Director select Interface

11. In the Local IP field enter in 192.168.50.0/24 if you want ALL devices connected to the FlashRouter’s network to use the WireGuard VPN connection. Click OK.

If you only want certain devices to connect to the WireGuard Client profile you have setting up instead of all the devices connected to the FlashRouter’s network please complete the instructions on our VPN Director guide.

12. Then click Apply at the bottom of the page.

Verify a successful ProtonVPN connection

Visit ProtonVPN’s IP Check from a private/incognito browsing window to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

How to change the ProtonVPN server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PrivateInternetAccess (PIA) Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual PIA Setup

Verify your PIA login information

If you are not already a PIA user Sign Up Now.

Log in to your account on the PIA website.

FlashRouters Privacy App - PIA Login

PIA Server Addresses

The below servers are the only servers compatible with PIA router connections. Dedicated IP Addresses are not able to connect via routers.

United States

us-california.privacy.network
us-newjersey.privacy.network
us-chicago.privacy.network
us-texas.privacy.network
us-florida.privacy.network
us-seattle.privacy.network
us3.privacy.network
us-siliconvalley.privacy.network
us-newyorkcity.privacy.network
us-washingtondc.privacy.network
us-atlanta.privacy.network
us-houston.privacy.network
us-denver.privacy.network

United Kingdom

uk-london.privacy.network
uk-manchester.privacy.network

Canada

ca-toronto.privacy.network
ca-montreal.privacy.network

Australia

au-sydney.privacy.network
aus-melbourne.privacy.network
aus-perth.privacy.network

Germany

de-berlin.privacy.network
de-frankfurt.privacy.network

Rest of the World

ae.privacy.network
austria.privacy.network
dz.privacy.network
ad.privacy.network
ar.privacy.network
yerevan.privacy.network
bahamas.privacy.network
bangladesh.privacy.network
brussels.privacy.network
sofia.privacy.network
cambodia.privacy.network
china.privacy.network
cyprus.privacy.network
czech.privacy.network
denmark.privacy.network
egypt.privacy.network
fi.privacy.network
france.privacy.network
georgia.privacy.network
greenland.privacy.network
hungary.privacy.network
is.privacy.network
in.privacy.network
iran.privacy.network
ireland.privacy.network
man.privacy.network
israel.privacy.network
italy.privacy.network
japan.privacy.network
kazakhstan.privacy.network
liechtenstein.privacy.network
lu.privacy.network
macau.privacy.network
malta.privacy.network
mexico.privacy.network
md.privacy.network
monaco.privacy.network
mongolia.privacy.network
montenegro.privacy.network
morocco.privacy.network
nl-amsterdam.privacy.network
nz.privacy.network
nigeria.privacy.network
no.privacy.network
panama.privacy.network
philippines.privacy.network
poland.privacy.network
qatar.privacy.network
ro.privacy.network
rs.privacy.network
saudiarabia.privacy.network
spain.privacy.network
srilanka.privacy.network
sweden.privacy.network
swiss.privacy.network
sg.privacy.network
tr.privacy.network
taiwan.privacy.network
ua.privacy.network
venezuela.privacy.network
vietnam.privacy.network
za.privacy.network

DD-WRT Router Setup for PIA

Navigate to Services > VPN

PIA offers two different Encryption levels.
Default Encryption (AES-128) typically provides faster speeds.
Strong Encryption (AES-256) provides stronger encryption.
Follow the table below of the one that fits your needs.

Enter PIA settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1198

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA1

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFqzCCBJOgAwIBAgIJAKZ7D5Yv87qDMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzM1
MThaFw0zNDA0MTIxNzM1MThaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAPXD
L1L9tX6DGf36liA7UBTy5I869z0UVo3lImfOs/GSiFKPtInlesP65577nd7UNzzX
lH/P/CnFPdBWlLp5ze3HRBCc/Avgr5CdMRkEsySL5GHBZsx6w2cayQ2EcRhVTwWp
cdldeNO+pPr9rIgPrtXqT4SWViTQRBeGM8CDxAyTopTsobjSiYZCF9Ta1gunl0G/
8Vfp+SXfYCC+ZzWvP+L1pFhPRqzQQ8k+wMZIovObK1s+nlwPaLyayzw9a8sUnvWB
/5rGPdIYnQWPgoNlLN9HpSmsAcw2z8DXI9pIxbr74cb3/HSfuYGOLkRqrOk6h4RC
OfuWoTrZup1uEOn+fw8CAwEAAaOCAVQwggFQMB0GA1UdDgQWBBQv63nQ/pJAt5tL
y8VJcbHe22ZOsjCCAR8GA1UdIwSCARYwggESgBQv63nQ/pJAt5tLy8VJcbHe22ZO
sqGB7qSB6zCB6DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAkNBMRMwEQYDVQQHEwpM
b3NBbmdlbGVzMSAwHgYDVQQKExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4G
A1UECxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBAMTF1ByaXZhdGUg
SW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQpExdQcml2YXRlIEludGVybmV0IEFjY2Vz
czEvMC0GCSqGSIb3DQEJARYgc2VjdXJlQHByaXZhdGVpbnRlcm5ldGFjY2Vzcy5j
b22CCQCmew+WL/O6gzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBDQUAA4IBAQAn
a5PgrtxfwTumD4+3/SYvwoD66cB8IcK//h1mCzAduU8KgUXocLx7QgJWo9lnZ8xU
ryXvWab2usg4fqk7FPi00bED4f4qVQFVfGfPZIH9QQ7/48bPM9RyfzImZWUCenK3
7pdw4Bvgoys2rHLHbGen7f28knT2j/cbMxd78tQc20TIObGjo8+ISTRclSTRBtyC
GohseKYpTS9himFERpUgNtefvYHbn70mIOzfOJFTVqfrptf9jXa9N8Mpy3ayfodz
1wiqdteqFXkTYoSDctgKMiZ6GdocK9nMroQipIQtpnwd4yBDWIyC6Bvlkrq5TQUt
YDQ8z9v+DMO6iwyIDRiU
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter PIA settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1197

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIHqzCCBZOgAwIBAgIJAJ0u+vODZJntMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzQw
MzNaFw0zNDA0MTIxNzQwMzNaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBALVk
hjumaqBbL8aSgj6xbX1QPTfTd1qHsAZd2B97m8Vw31c/2yQgZNf5qZY0+jOIHULN
De4R9TIvyBEbvnAg/OkPw8n/+ScgYOeH876VUXzjLDBnDb8DLr/+w9oVsuDeFJ9K
V2UFM1OYX0SnkHnrYAN2QLF98ESK4NCSU01h5zkcgmQ+qKSfA9Ny0/UpsKPBFqsQ
25NvjDWFhCpeqCHKUJ4Be27CDbSl7lAkBuHMPHJs8f8xPgAbHRXZOxVCpayZ2SND
fCwsnGWpWFoMGvdMbygngCn6jA/W1VSFOlRlfLuuGe7QFfDwA0jaLCxuWt/BgZyl
p7tAzYKR8lnWmtUCPm4+BtjyVDYtDCiGBD9Z4P13RFWvJHw5aapx/5W/CuvVyI7p
Kwvc2IT+KPxCUhH1XI8ca5RN3C9NoPJJf6qpg4g0rJH3aaWkoMRrYvQ+5PXXYUzj
tRHImghRGd/ydERYoAZXuGSbPkm9Y/p2X8unLcW+F0xpJD98+ZI+tzSsI99Zs5wi
jSUGYr9/j18KHFTMQ8n+1jauc5bCCegN27dPeKXNSZ5riXFL2XX6BkY68y58UaNz
meGMiUL9BOV1iV+PMb7B7PYs7oFLjAhh0EdyvfHkrh/ZV9BEhtFa7yXp8XR0J6vz
1YV9R6DYJmLjOEbhU8N0gc3tZm4Qz39lIIG6w3FDAgMBAAGjggFUMIIBUDAdBgNV
HQ4EFgQUrsRtyWJftjpdRM0+925Y6Cl08SUwggEfBgNVHSMEggEWMIIBEoAUrsRt
yWJftjpdRM0+925Y6Cl08SWhge6kgeswgegxCzAJBgNVBAYTAlVTMQswCQYDVQQI
EwJDQTETMBEGA1UEBxMKTG9zQW5nZWxlczEgMB4GA1UEChMXUHJpdmF0ZSBJbnRl
cm5ldCBBY2Nlc3MxIDAeBgNVBAsTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAw
HgYDVQQDExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UEKRMXUHJpdmF0
ZSBJbnRlcm5ldCBBY2Nlc3MxLzAtBgkqhkiG9w0BCQEWIHNlY3VyZUBwcml2YXRl
aW50ZXJuZXRhY2Nlc3MuY29tggkAnS7684Nkme0wDAYDVR0TBAUwAwEB/zANBgkq
hkiG9w0BAQ0FAAOCAgEAJsfhsPk3r8kLXLxY+v+vHzbr4ufNtqnL9/1Uuf8NrsCt
pXAoyZ0YqfbkWx3NHTZ7OE9ZRhdMP/RqHQE1p4N4Sa1nZKhTKasV6KhHDqSCt/dv
Em89xWm2MVA7nyzQxVlHa9AkcBaemcXEiyT19XdpiXOP4Vhs+J1R5m8zQOxZlV1G
tF9vsXmJqWZpOVPmZ8f35BCsYPvv4yMewnrtAC8PFEK/bOPeYcKN50bol22QYaZu
LfpkHfNiFTnfMh8sl/ablPyNY7DUNiP5DRcMdIwmfGQxR5WEQoHL3yPJ42LkB5zs
6jIm26DGNXfwura/mi105+ENH1CaROtRYwkiHb08U6qLXXJz80mWJkT90nr8Asj3
5xN2cUppg74nG3YVav/38P48T56hG1NHbYF5uOCske19F6wi9maUoto/3vEr0rnX
JUp2KODmKdvBI7co245lHBABWikk8VfejQSlCtDBXn644ZMtAdoxKNfR2WTFVEwJ
iyd1Fzx0yujuiXDROLhISLQDRjVVAvawrAtLZWYK31bY7KlezPlQnl/D9Asxe85l
8jO5+0LdJ6VyOs/Hd4w52alDW/MFySDZSfQHMTIc30hLBJ8OnCEIvluVQQ2UQvoW
+no177N9L2Y+M9TcTA62ZyMXShHQGeh20rb4kK8f+iFX8NxtdHVSkxMEFSfDDyQ=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PIA connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the PIA server

  1. Copy the new PIA server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

CyberGhost Manual OpenVPN Setup

TeamFlashRouters · Apr 9, 2019 ·

Preparing for Manual CyberGhost Setup

Obtain your CyberGhost OpenVPN Information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

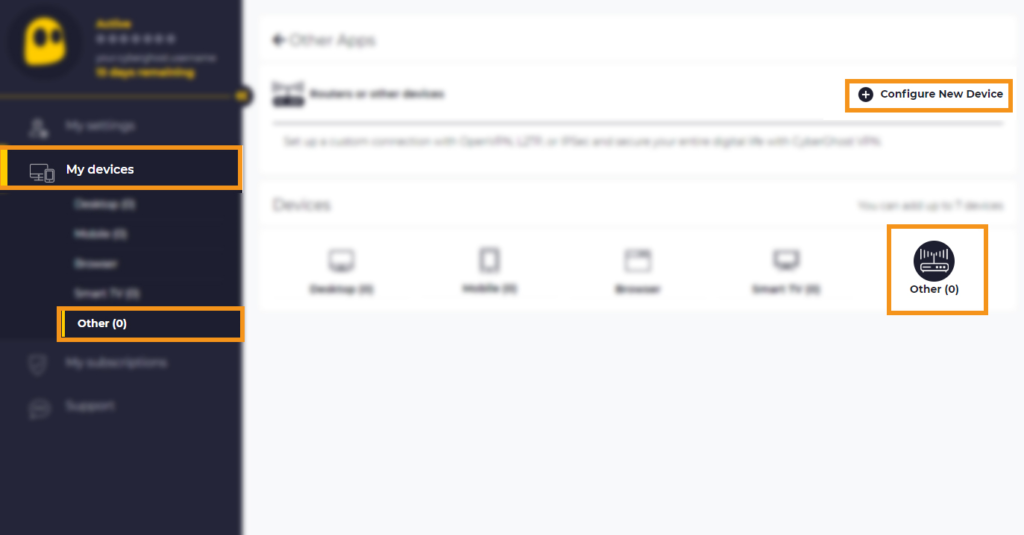
2. Select My Devices.

3. Select Other and then Configure New Device.

CyberGhost Website OpenVPN Configuration Files Generator Cyberghost - Website Screen CyberGhost Website OpenVPN Configuration Files Generator

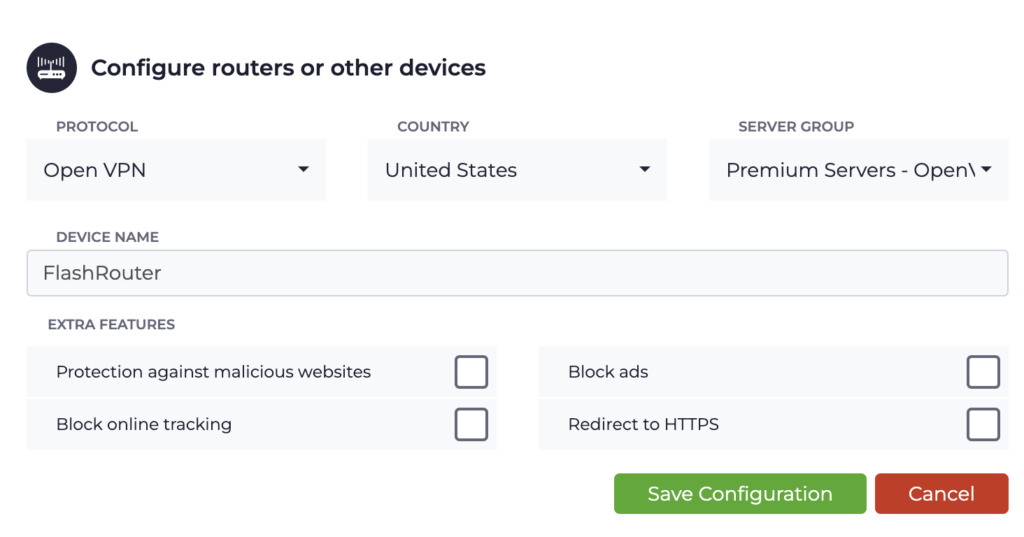
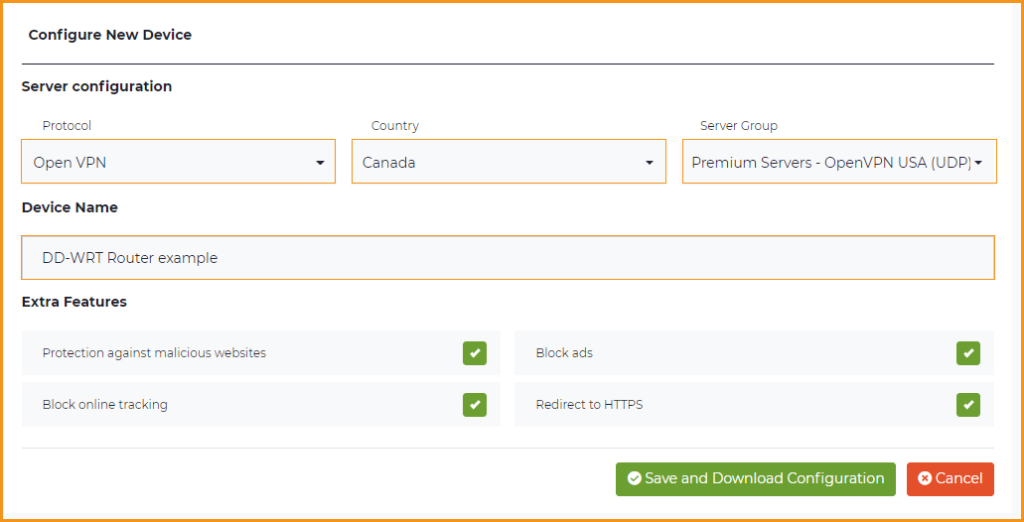
4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 3

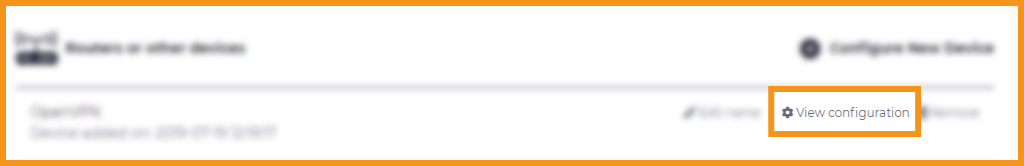
5. Press View configuration.

CyberGhost Website OpenVPN Configuration Files Generator 2

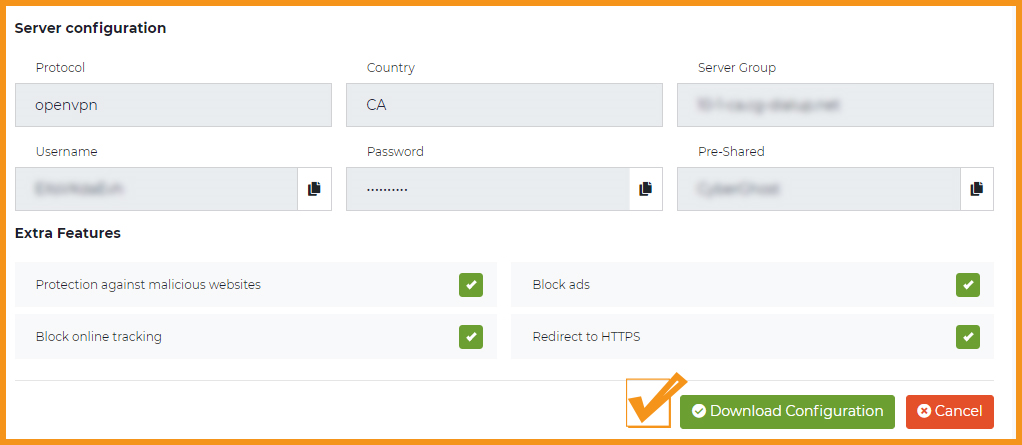
6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the ca.crt, client.crt, and client.key files. All CyberGhost servers have different keys and certificates.

DD-WRT Router Setup for CyberGhost

Navigate to Services > VPN

Enter CyberGhost settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you selected in your account. Be sure there are no extra spaces or characters.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your CyberGhost account.

Password

Enter the Password you obtained in your CyberGhost account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

tun-mtu 1500
fragment 1300
mssfix 1300

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
—–END CERTIFICATE—–

Public Client Cert

Copy and paste all contents of the client.crt file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and paste all contents of the client.key file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful CyberGhost connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit CyberGhost’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to CyberGhost.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the CyberGhost server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new ca.crt, client.crt, and client.key
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN TP-Link WireGuard Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for ProtonVPN TP-Link Setup

Download your ProtonVPN .conf file

If you are not already an ProtonVPN user Sign Up Now.

1. Log in to your account on the ProtonVPN website.

ProtonVPN Account Sign in

2. Click Downloads.

ProtonVPN Downloads

3. Scroll down to WireGuard configuration and name the device FlashRouter.

ProtonVPN WireGuard Configuration Name

4. Select Router as the platform.

ProtonVPN WireGuard select Platform

5. Select the VPN options that best fit your needs. We typically use the settings as seen in the screenshot here if you are unsure.

ProtonVPN WireGuard VPN options

6. Next select the server that you would like to connect to and click Create. At the top of the page you’ll see ProtonVPN’s recommended server which we recommend using unless you need to connect to a specific location.

If you need a specific server location find it in the list and click Create.

ProtonVPN WireGuard recommended server
ProtonVPN WireGuard specific server

7. After clicking Create a new window will appear. Click Download to download the .conf file to your computer.

TP-Link Router Setup for ProtonVPN

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

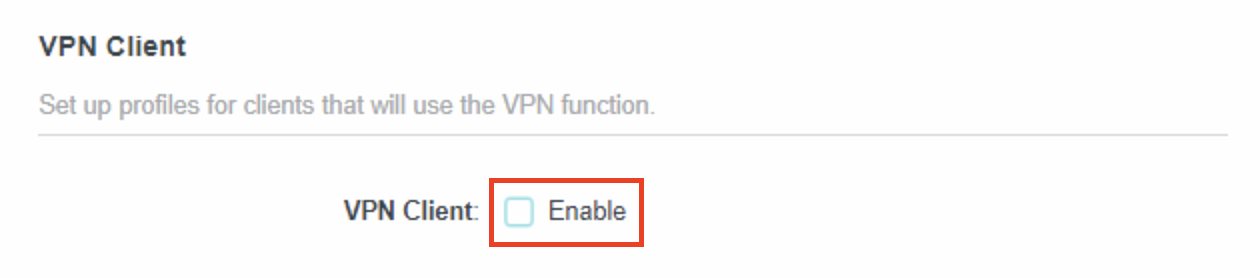
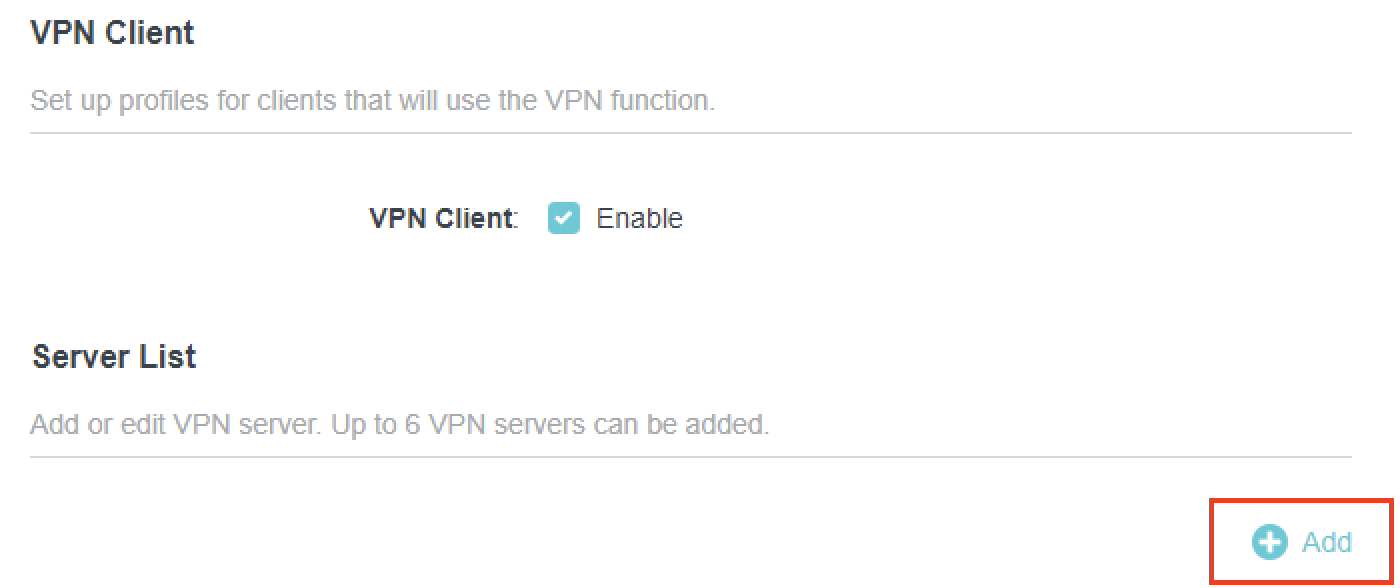
3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

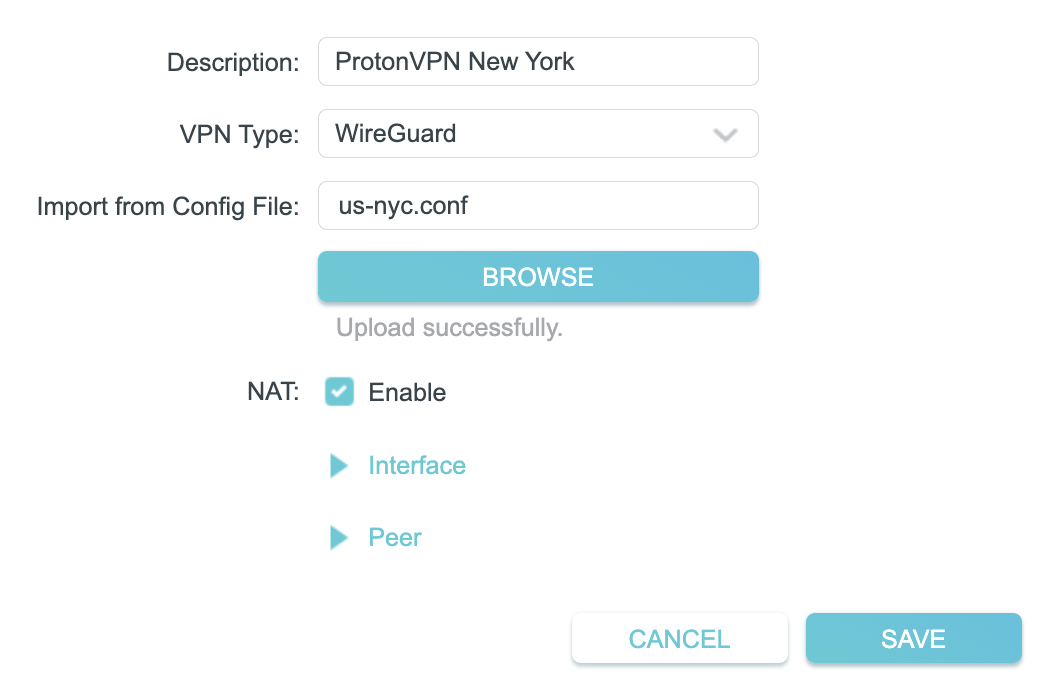
5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location. Our example server was New York so I have entered in ProtonVPN New York.

Set the VPN Type to WireGuard.

Click Browse and select the .conf file you downloaded earlier. Then click Save.

TP-Link ProtonVPN WireGuard

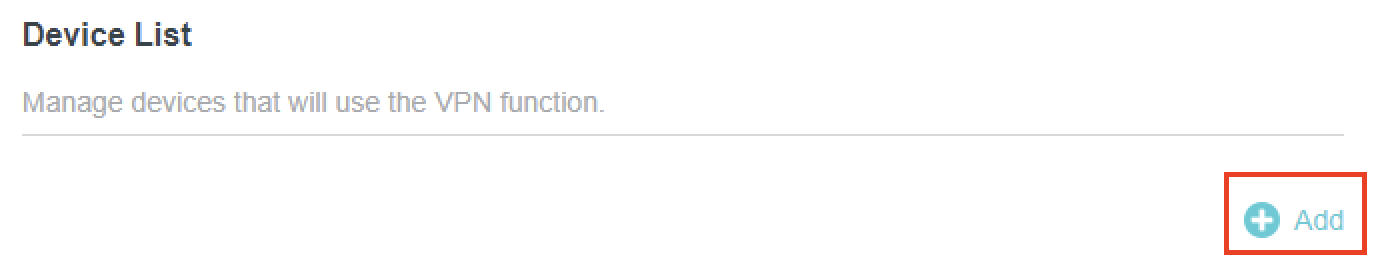
By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.
6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

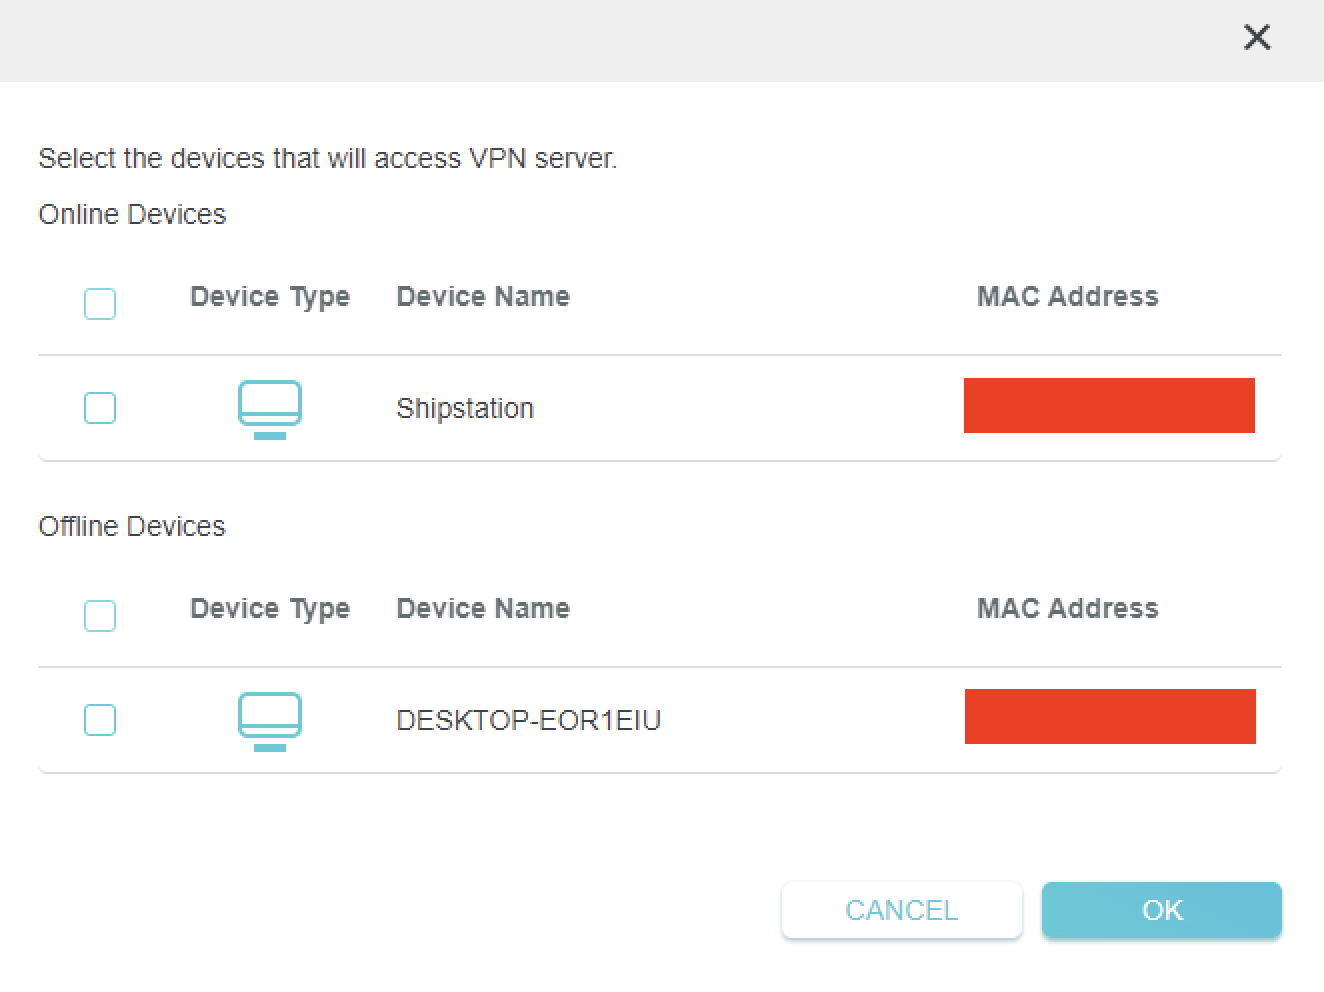
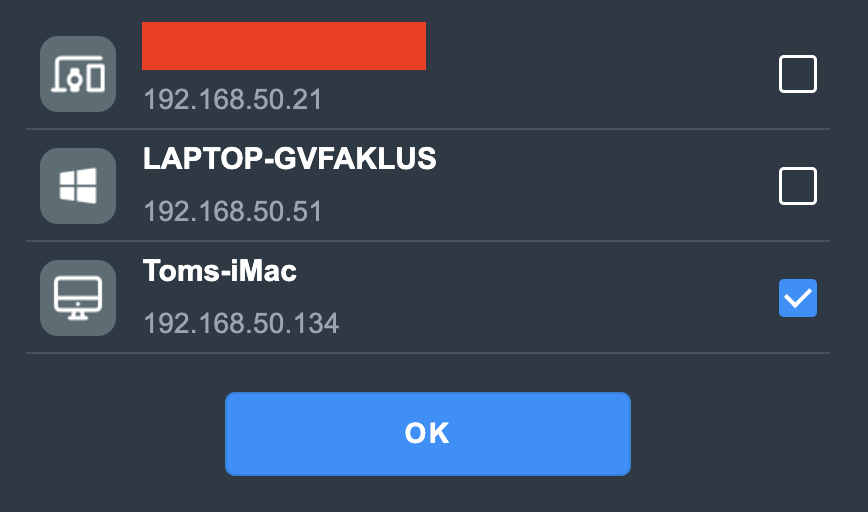
7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.
TP-Link select devices to add to VPN tunnel

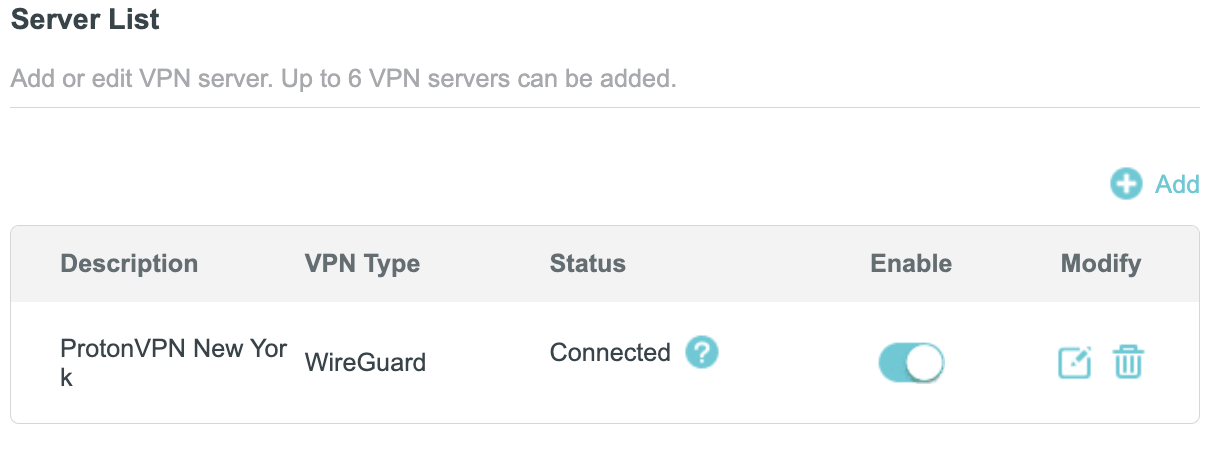
8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link ProtonVPN WireGuard connected

Verify a successful ProtonVPN connection

  1. You should now see a CONNECTED message.
  2. Visit ProtonVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.
How to change the ProtonVPN server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero Bedtime Settings (Internet Scheduler)

TeamFlashRouters · Apr 3, 2023 ·

Your Privacy Hero router uses Cloud Based router management which means you can access the router settings from anywhere on any device that has an internet connection. You can follow these steps while connected to your phone, other Wi-Fi network, or the Privacy Hero network.

The Bedtime settings feature allows users to schedule when internet access will be turned off for specific user profiles. All devices assigned to this profile will have these rules applied.

1. From any device that has a browser such as a computer, smartphone, or tablet visit app.privacyhero.com

App.PrivacyHero.com

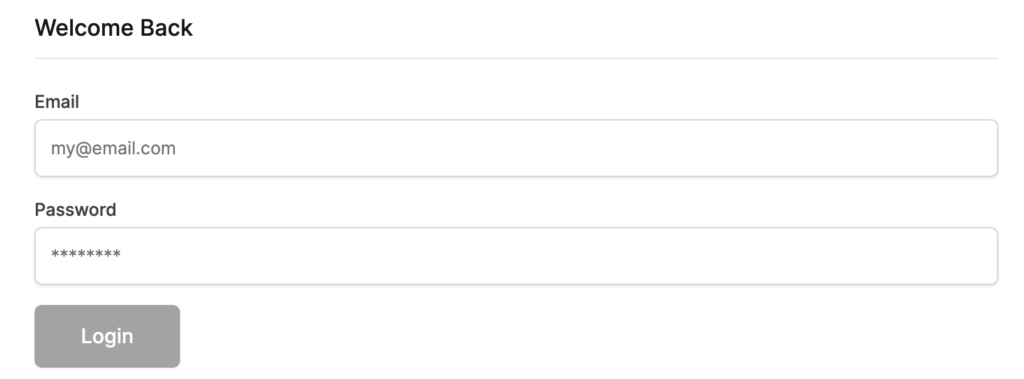
2. Enter your Privacy Hero account email and password. Click Login.

Privacy Hero Access Settings

If you have not created your Privacy Hero account yet please follow these instructions.

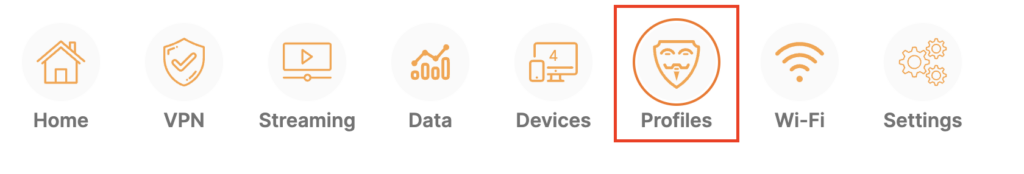
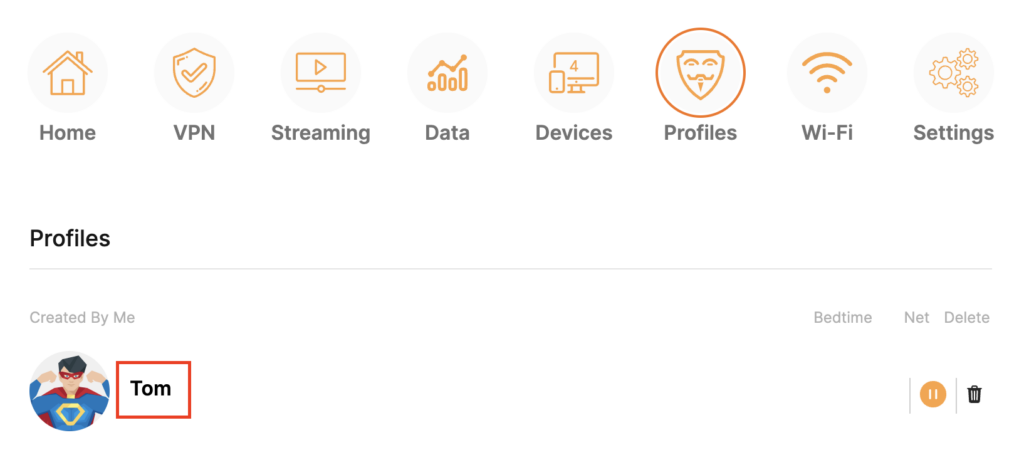
3. Click the Profiles symbol.

Privacy Hero Profiles

4. Click the name of the User Profile.

Privacy Hero Select Profile

5. Click Schoolnights or Weekends depending on which you need to set rules for.

Privacy Hero Bedtime School Nights Weekends

6. Select the time that you want the Internet to turn off and the days you want this rule to apply to. Click Save.

Privacy Hero Set Bedtime

7. Set the Bedtime toggle to On.

Privacy Hero Enable Bedtime

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark AsusWRT WireGuard Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for Surfshark AsusWRT Setup

Copy your Surfshark Private Key

If you are not already a Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

Surfshark Account Login

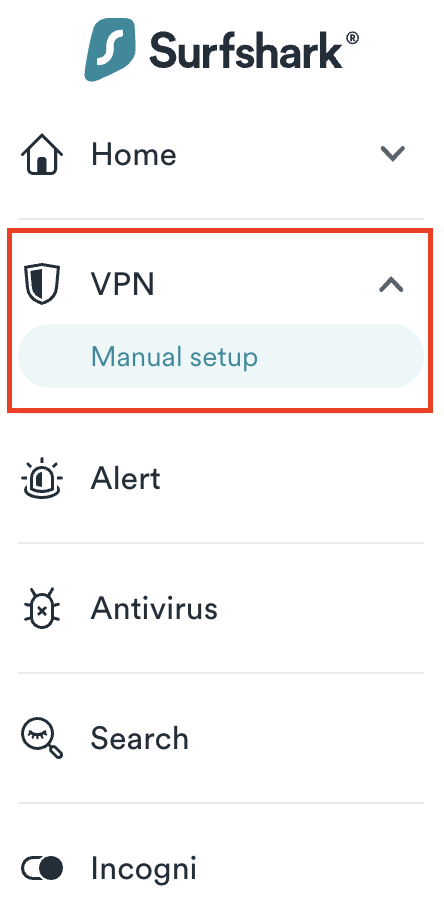
2. Click VPN Manual Setup.

Surfshark VPN Manual Setup

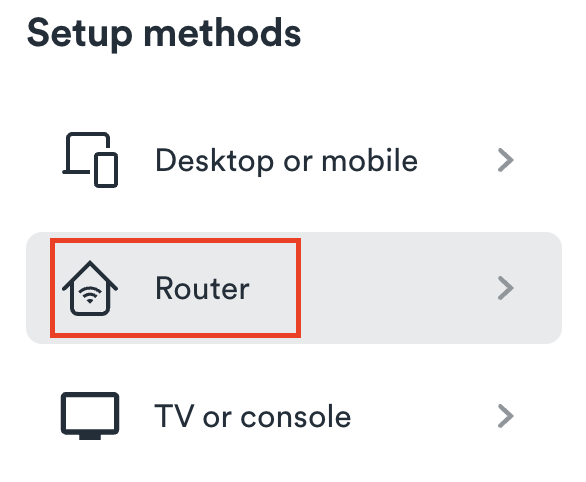
3. Select Router as the Setup method.

Surfshark setup method Router

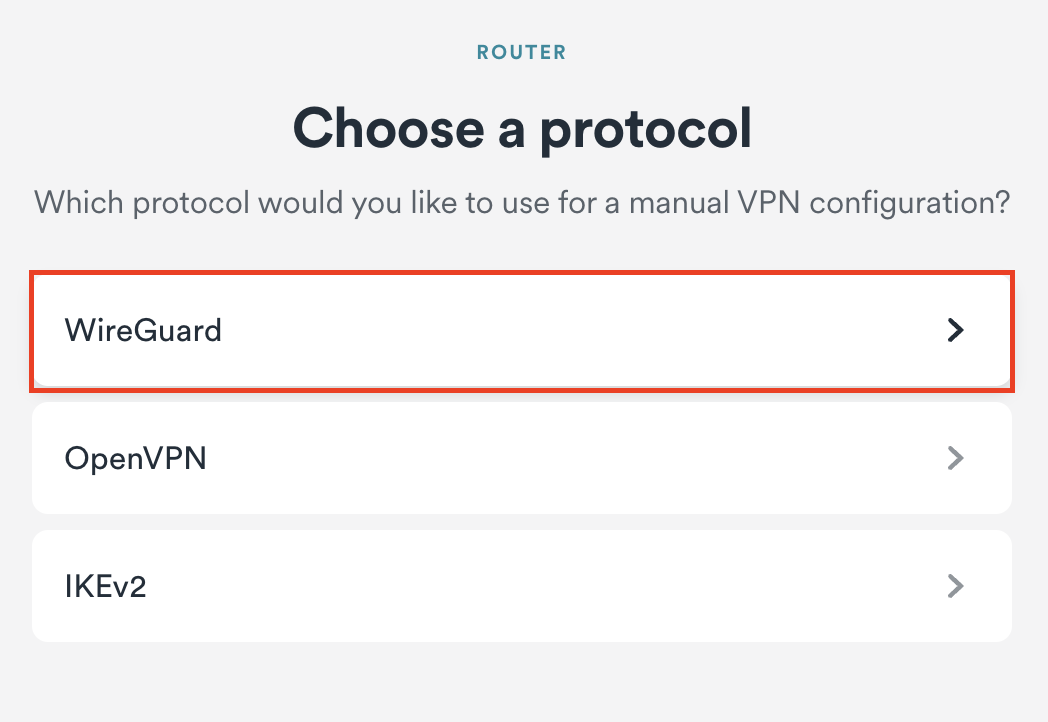
4. Select WireGuard as the Protocol.

Surfshark select WireGuard

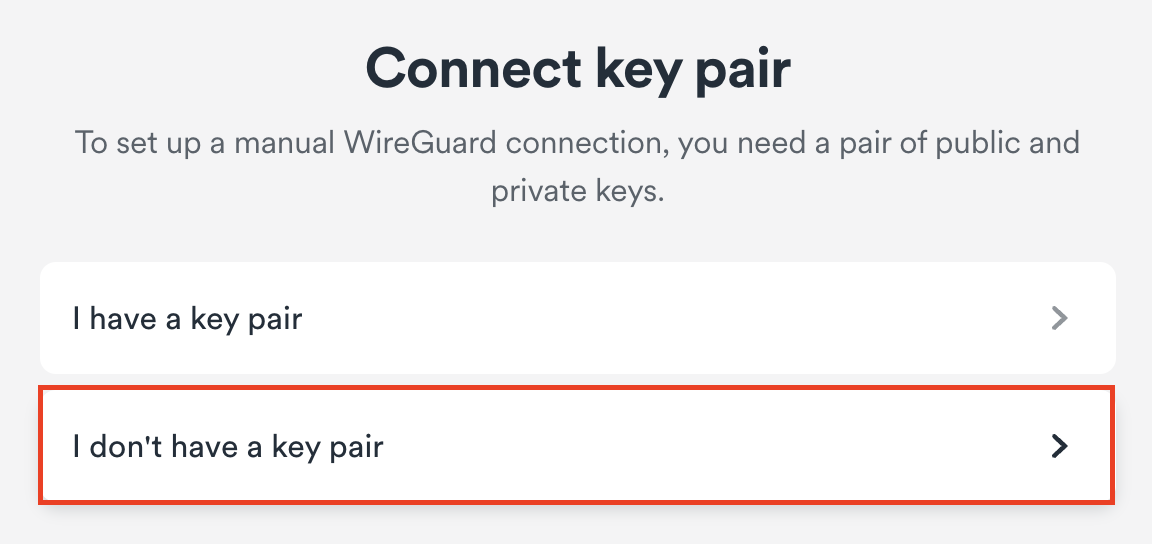
5. Select I don’t have a key pair.

Surfshark No Key Pair

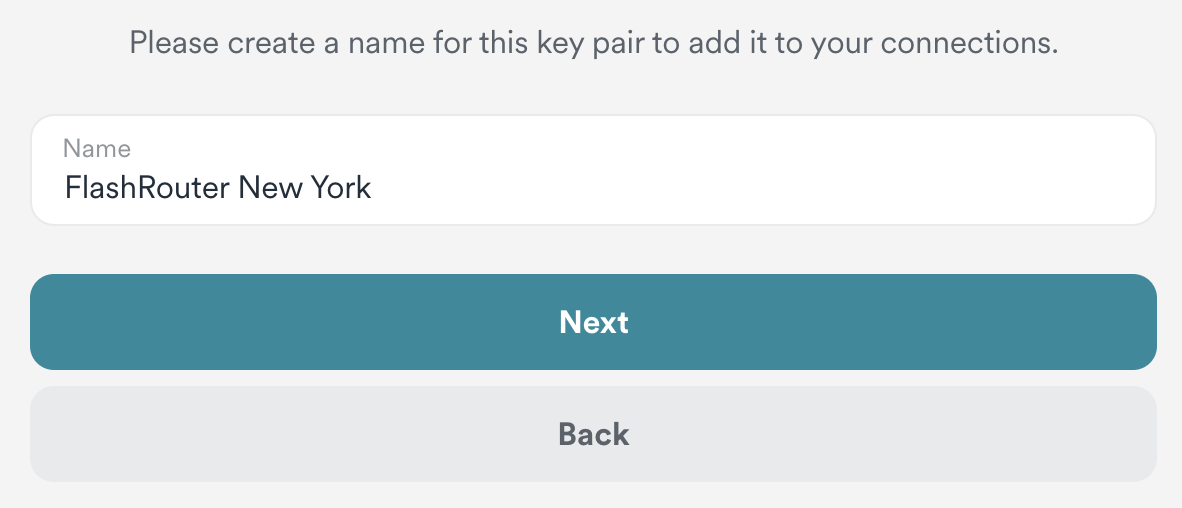
6. Enter FlashRouter as the name of the connection and click Next.

Surfshark Connection Name

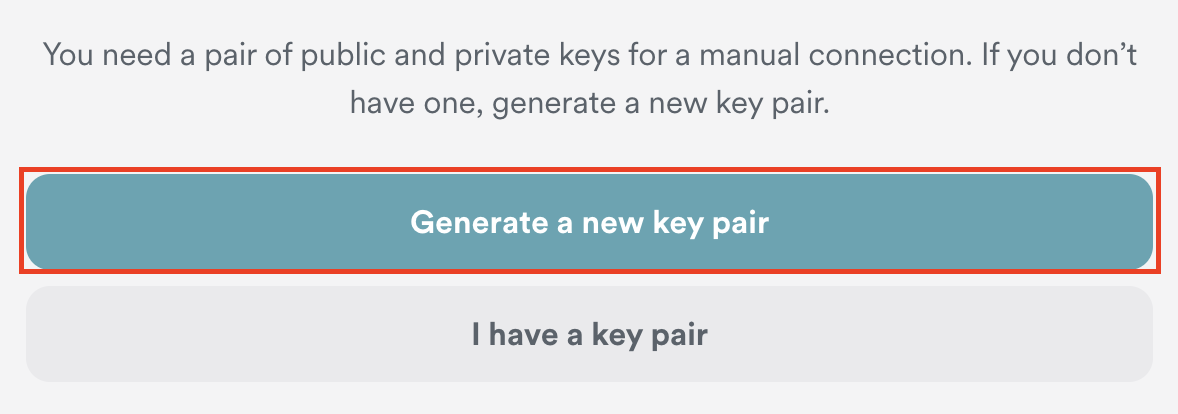
7. Click Generate a new key pair.

Surfshark Generate new Key Pair

8. A Public Key and Private Key will then appear. Use the copy box to copy the Private Key. You will not need the public key.

Surfshark Private Key

AsusWRT Router Setup for Surfshark

Login to AsusWRT firmware settings in a browser on any computer or smart device connected to the AsusWRT FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

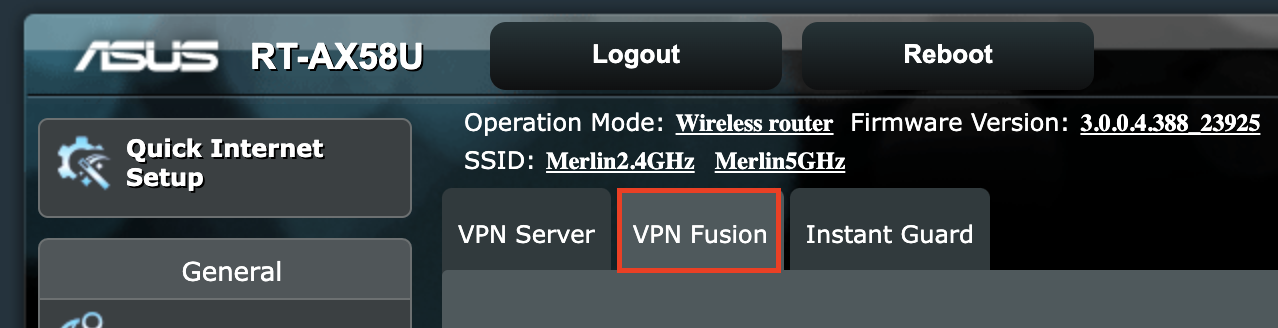
2. Navigate to the VPN Fusion tab.

Asus VPN Fusion

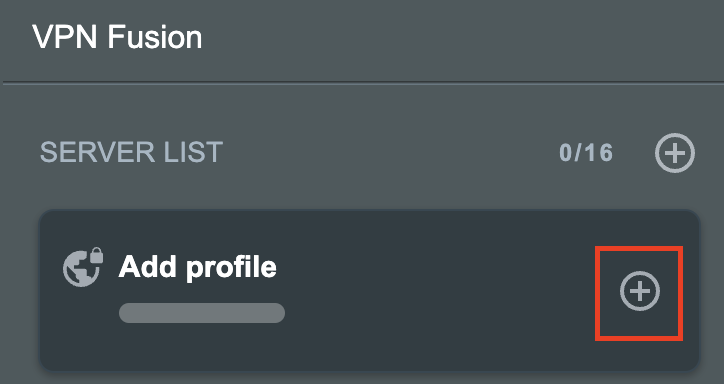
3. Click Add profile.

Asus Add profile

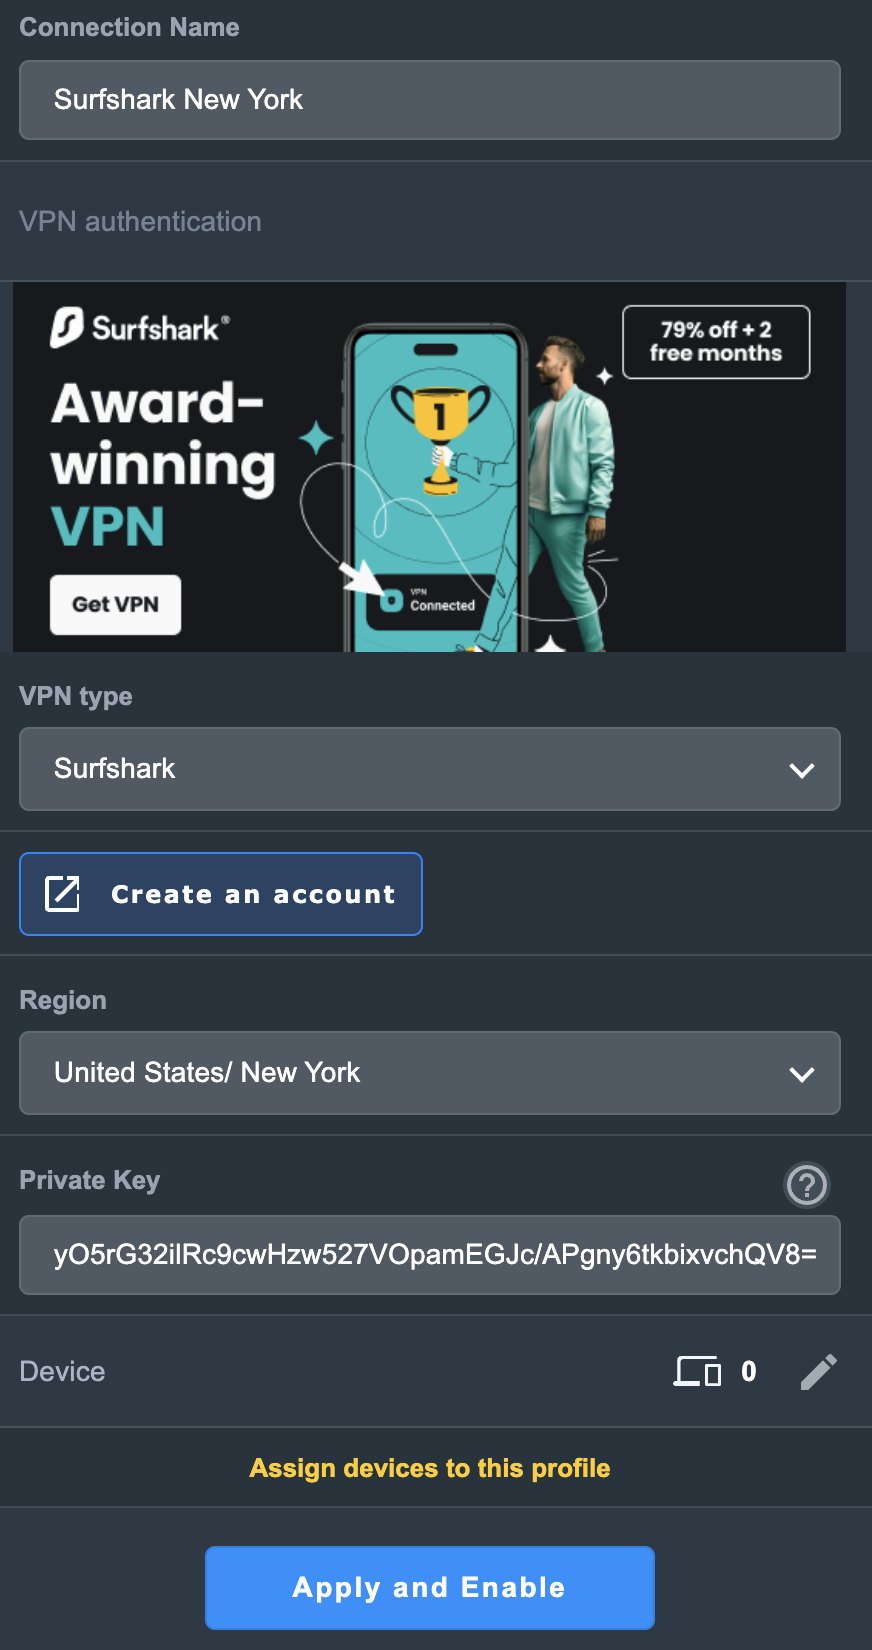
4. In the Connection Name field enter in Surfshark.

5. In the VPN Type dropdown select Surfshark.

6. In the Region dropdown select the Surfshark location you want to connect to.

7. In the Private Key field paste in the Surfshark Private Key obtained earlier.

8. Click Apply and Enable at the bottom of the page.

Asus Surfshark profile

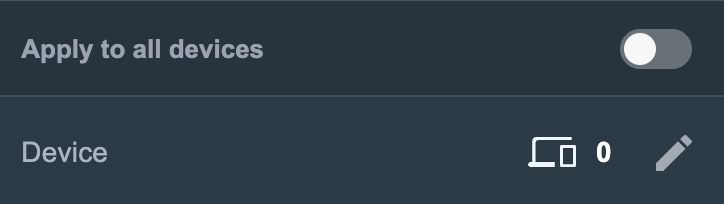
If you only want certain devices to connect to the Surfshark profile you are setting up instead of all the devices connected to the FlashRouter’s network click into the profile and disable Apply to all devices. Then click Devices and select the devices that you want to connect to VPN.
Asus VPN devices
Asus VPN select devices

9. At the top of the page set the Service State toggle to ON to activate the VPN connection.
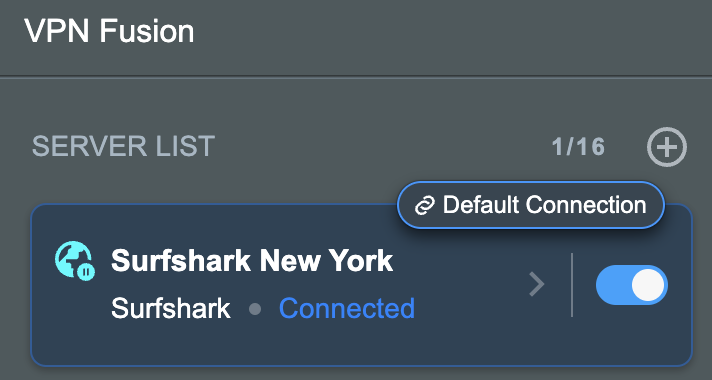
Asus Surfshark Connected

Verify a successful Surfshark connection

  1. You should now see a CONNECTED message.
  2. Visit Surfshark’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark.

How to change the Surfshark server

  1. Use the profile service state toggle to disconnect the currently connected location.
  2. Then click into the Surfshark profile in the router’s settings.
  3. Then adjust the Region dropdown to a new location.
  4. Click Apply all settings.
  5. Use the profile service state toggle to connect the new location.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark TP-Link OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for Surfshark TP-Link Setup

Download your Surfshark .ovpn file

If you are not already a Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

Surfshark Account Login

2. Click VPN Manual Setup.

Surfshark VPN Manual Setup

3. Select Router as the Setup method.

Surfshark setup method Router

4. Select OpenVPN as the Protocol.

Surfshark OpenVPN Protocol

5. Copy and paste your Surfshark manual username and password to a secure location. This is the username and password you will enter into the router settings to connect to Surfshark.

Surfshark OpenVPN credentials

6. Click Location and select the server location you want to connect to. Unless you need a specific location we recommend using Surfshark’s recommended Fastest server. Click Download to download the UDP .ovpn file for this Surfshark server location.

Surfshark download .ovpn file

TP-Link Router Setup for Surfshark

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location. Our example server was New York so I have entered in Surfshark New York.

Set the VPN Type to OpenVPN.

In the Username and Password fields paste in the Surfshark username and password we obtained earlier.

Click Browse and select the .ovpn file you downloaded earlier. Then click Save.

TP-Link Surfshark OpenVPN

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.
6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.
TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link Surfshark OpenVPN connected

Verify a successful Surfshark connection

  1. You should now see a CONNECTED message.
  2. Visit Surfshark’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark.

How to change the Surfshark server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

CyberGhost AsusWRT OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for CyberGhost Setup

Obtain your CyberGhost OpenVPN information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

2. Select VPN.
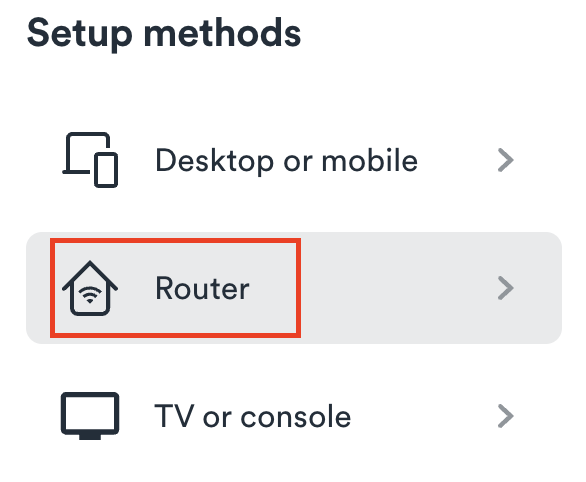
CyberGhost VPN

3. Click Configure New Device.

CyberGhost Configure Device

4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.
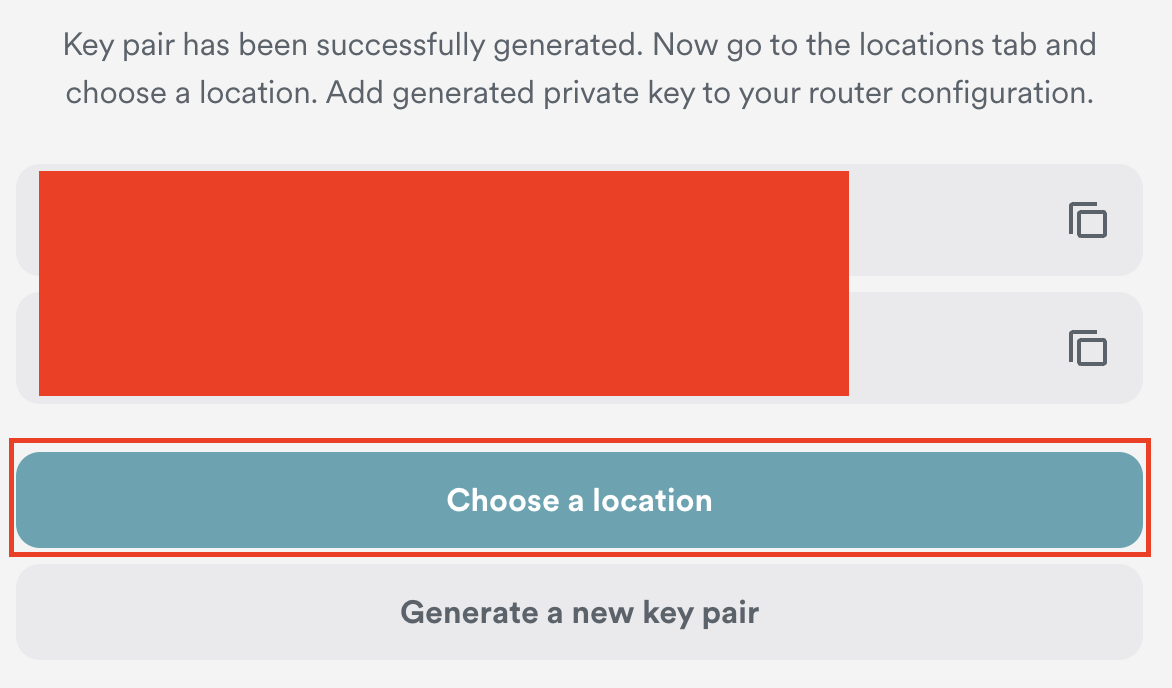
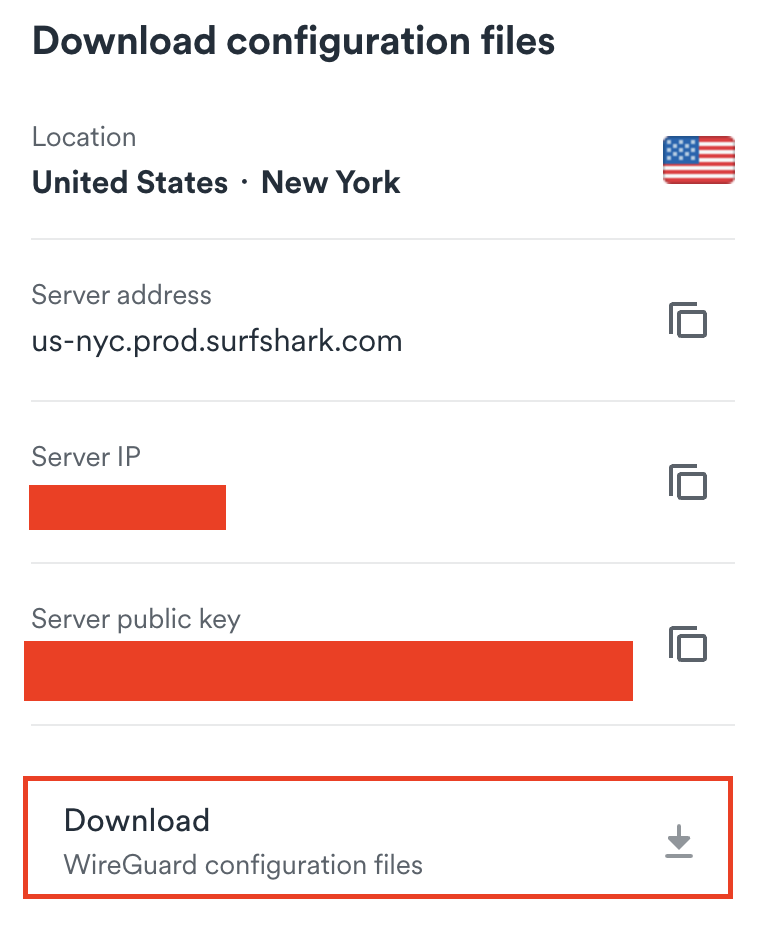
CyberGhost protocol and location

5. Press View configuration.

CyberGhost view configuration

6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the folder that was downloaded. Then open the ca.crt the client.crt, and client.key files with NotePad++ for Windows or TextEdit for Apple. All CyberGhost servers have different keys and certificates.

AsusWRT Router Setup for CyberGhost

Login to AsusWRT firmware settings in a browser on any computer or smart device connected to the AsusWRT FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Fusion tab.

Asus VPN Fusion

3. Click Add profile.

Asus Add profile

4. In the Connection Name field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was in USA so I have entered in CyberGhost USA.

5. In the VPN Type dropdown select OpenVPN.

6. Click Import .ovpn file and select the openvpn.ovpn file from the folder you downloaded earlier. Then click Upload.

7. In the Username and Password fields enter in the CyberGhost assigned username and password that you obtained earlier.

8. After uploading the openvpn.ovpn file you will get a message that says “Complete, Lack of Client Key!, Lack of Client Certificate, Lack of Certificate Authority”. For CyberGhost you need to enter in these details manually. Click Import the CA file or edit the .ovpn file manually and then click the edit icon next to Content modification of Keys and Certificate.

Asus CyberGhost import certs and keys

9. In the Certificate Authority field paste in the entire content of the ca.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

10. In the Client Certificate field paste in the entire content of the client.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

11. In the Client Key field paste in the entire content of the client.key file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Then click OK.

Asus CyberGhost enter certs and keys

8. Click Apply and Enable at the bottom of the page.

Asus CyberGhost profile

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network click into the profile and disable Apply to all devices. Then click Devices and select the devices that you want to connect to VPN.

Asus VPN devices
Asus VPN select devices

9. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Asus CyberGhost connected

Verify a successful CyberGhost connection

  1. You should now see a CONNECTED message.
  2. Visit What is my IP Address from a private/incognito browser to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to CyberGhost.

How to change the CyberGhost server

  1. Follow the steps at the top of the page to create a new CyberGhost location profile in your account.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ExpressVPN Merlin OpenVPN Setup

TeamFlashRouters · Jan 11, 2023 ·

Preparing for ExpressVPN Merlin Setup

Obtain your ExpressVPN OpenVPN Information

If you are not already an ExpressVPN user Sign Up Now.

1. Log in to your account on the ExpressVPN website.

ExpressVPN login page

2. Successfully log in with your account information. Select More.

3. Select Manual Configuration and copy the Username and Password that are displayed on the right hand side of the screen.

ExpressVPN Manual Configuration
ExpressVPN username and password

4. Click the Server Location that you want to connect to. This will download a .ovpn file to your computer that we will use later on. There is no need to open the file. For this example I have selected New York but feel free to select any server listed there.

ExpressVPN Download .ovpn file

Merlin Router Setup for ExpressVPN

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Click Choose file and select the .ovpn file you downloaded earlier. Then click Upload.

Merlin Choose File Upload

4. Set Automatic Start at boot time to Yes if you want the VPN connection to begin automatically when the router is powered off and back on.

Merlin Automatic Start at boot time

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was in New York so I have entered in ExpressVPN New York.

Merlin ExpressVPN Description

6. Set Accept DNS Configuration to Strict. Set Redirect Internet traffic through tunnel to Yes (all). Set Kill Switch to Yes or No depending on if you want the Internet to be killed if the VPN connection drops.

Merlin Accept DNS configuration Redirect Internet and Kill Switch

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network please set the Redirect Internet traffic through tunnel to VPN Director. Then complete the instructions on this page and then view our VPN Director guide.

7. Enter your ExpressVPN username and password that you obtained earlier in the Username and Password. Note that these are different from your ExpressVPN email login and password.

Merlin VPN Username and Password

8. Click Apply at the bottom of the page.

9. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Merlin Service State

Verify a successful ExpressVPN connection

  1. You should now see a CONNECTED message.
  2. Visit ExpressVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ExpressVPN.

How to change the ExpressVPN server

  1. Copy the new ExpressVPN server address from the below server list.
  2. Paste the server into the Server Address field.
  3. Click Apply at the bottom of the page.

ExpressVPN Server Addresses

Americas

usa-atlanta-ca-version-2.expressnetw.com
usa-boston-ca-version-2.expressnetw.com
usa-chicago-ca-version-2.expressnetw.com
usa-dallas-ca-version-2.expressnetw.com
usa-dallas-2-ca-version-2.expressnetw.com
usa-denver-ca-version-2.expressnetw.com
usa-kansascity-ca-version-2.expressnetw.com
usa-losangeles-ca-version-2.expressnetw.com
usa-losangeles-1-ca-version-2.expressnetw.com
usa-losangeles-2-ca-version-2.expressnetw.com
usa-losangeles-3-ca-version-2.expressnetw.com
usa-los-angeles-4-ca-version-2.expressnetw.com
usa-miami-ca-version-2.expressnetw.com
usa-miami-2-ca-version-2.expressnetw.com
usa-minneapolis-ca-version-2.expressnetw.com
usa-newjersey-1-ca-version-2.expressnetw.com
usa-newjersey-3-ca-version-2.expressnetw.com
usa-newyork-ca-version-2.expressnetw.com
us-new-york-2-ca-version-2.expressnetw.com
usa-phoenix-ca-version-2.expressnetw.com
usa-saltlakecity-ca-version-2.expressnetw.com
usa-sanfrancisco-ca-version-2.expressnetw.com
usa-sanjose-ca-version-2.expressnetw.com
usa-seattle-ca-version-2.expressnetw.com
usa-tampa-1-ca-version-2.expressnetw.com
usa-virginia-ca-version-2.expressnetw.com
usa-washingtondc-ca-version-2.expressnetw.com
usa-washingtondc-2-ca-version-2.expressnetw.com
canada-montreal-ca-version-2.expressnetw.com
canada-toronto-ca-version-2.expressnetw.com
canada-toronto-2-ca-version-2.expressnetw.com
canada-vancouver-ca-version-2.expressnetw.com
mexico-ca-version-2.expressnetw.com
argentina-ca-version-2.expressnetw.com
brazil-ca-version-2.expressnetw.com
brazil-2-ca-version-2.expressnetw.com
chile-ca-version-2.expressnetw.com
colombia-ca-version-2.expressnetw.com
costarica-ca-version-2.expressnetw.com
ecuador-ca-version-2.expressnetw.com
guatemala-ca-version-2.expressnetw.com
panama-ca-version-2.expressnetw.com
peru-ca-version-2.expressnetw.com
uruguay-ca-version-2.expressnetw.com
venezuela-ca-version-2.expressnetw.com

Europe

uk-berkshire-ca-version-2.expressnetw.com
uk-berkshire-2-ca-version-2.expressnetw.com
uk-docklands-ca-version-2.expressnetw.com
uk-east-london-ca-version-2.expressnetw.com
uk-kent-ca-version-2.expressnetw.com
uk-london-ca-version-2.expressnetw.com
france-paris-1-ca-version-2.expressnetw.com
france-paris-2-ca-version-2.expressnetw.com
france-strasbourg-ca-version-2.expressnetw.com
germany-darmstadt-ca-version-2.expressnetw.com
germany-frankfurt-1-ca-version-2.expressnetw.com
germany-frankfurt-2-ca-version-2.expressnetw.com
germany-nuremberg-ca-version-2.expressnetw.com
italy-cosenza-ca-version-2.expressnetw.com
italy-milan-ca-version-2.expressnetw.com
netherlands-amsterdam-ca-version-2.expressnetw.com
netherlands-rotterdam-ca-version-2.expressnetw.com
netherlands-thehague-ca-version-2.expressnetw.com
spain-barcelona-ca-version-2.expressnetw.com
spain-ca-version-2.expressnetw.com
sweden-ca-version-2.expressnetw.com
sweden-2-ca-version-2.expressnetw.com
switzerland-ca-version-2.expressnetw.com
switzerland-2-ca-version-2.expressnetw.com
albania-ca-version-2.expressnetw.com
andorra-ca-version-2.expressnetw.com
armenia-ca-version-2.expressnetw.com
austria-ca-version-2.expressnetw.com
azerbaijan-ca-version-2.expressnetw.com
belarus-ca-version-2.expressnetw.com
belgium-ca-version-2.expressnetw.com
bosniaandherzegovina-ca-version-2.expressnetw.com
bulgaria-ca-version-2.expressnetw.com
croatia-ca-version-2.expressnetw.com
cyprus-ca-version-2.expressnetw.com
czechrepublic-ca-version-2.expressnetw.com
denmark-ca-version-2.expressnetw.com
estonia-ca-version-2.expressnetw.com
finland-ca-version-2.expressnetw.com
georgia-ca-version-2.expressnetw.com
greece-ca-version-2.expressnetw.com
hungary-ca-version-2.expressnetw.com
iceland-ca-version-2.expressnetw.com
ireland-ca-version-2.expressnetw.com
isleofman-ca-version-2.expressnetw.com
jersey-ca-version-2.expressnetw.com
latvia-ca-version-2.expressnetw.com
liechtenstein-ca-version-2.expressnetw.com
lithuania-ca-version-2.expressnetw.com
luxembourg-ca-version-2.expressnetw.com
macedonia-ca-version-2.expressnetw.com
malta-ca-version-2.expressnetw.com
moldova-ca-version-2.expressnetw.com
monaco-ca-version-2.expressnetw.com
montenegro-ca-version-2.expressnetw.com
norway-ca-version-2.expressnetw.com
poland-ca-version-2.expressnetw.com
portugal-ca-version-2.expressnetw.com
romania-ca-version-2.expressnetw.com
serbia-ca-version-2.expressnetw.com
slovakia-ca-version-2.expressnetw.com
slovenia-ca-version-2.expressnetw.com
ukraine-ca-version-2.expressnetw.com

Asia Pacific

australia-brisbane-ca-version-2.expressnetw.com
australia-melbourne-ca-version-2.expressnetw.com
australia-perth-ca-version-2.expressnetw.com
australia-sydney-ca-version-2.expressnetw.com
australia-sydney-2-ca-version-2.expressnetw.com
australia-sydney-3-ca-version-2.expressnetw.com
hongkong-2-ca-version-2.expressnetw.com
hongkong4-ca-version-2.expressnetw.com
hongkong-1-ca-version-2.expressnetw.com
japan-tokyo-1-ca-version-2.expressnetw.com
japan-tokyo-2-ca-version-2.expressnetw.com
india-chennai-ca-version-2.expressnetw.com
india-mumbai-1-ca-version-2.expressnetw.com
singapore-cbd-ca-version-2.expressnetw.com
singapore-jurong-ca-version-2.expressnetw.com
southkorea-ca-version-2.expressnetw.com
southkorea2-ca-version-2.expressnetw.com
bangladesh-ca-version-2.expressnetw.com
bhutan-ca-version-2.expressnetw.com
brunei-ca-version-2.expressnetw.com
cambodia-ca-version-2.expressnetw.com
indonesia-ca-version-2.expressnetw.com
kazakhstan-ca-version-2.expressnetw.com
kyrgyzstan-ca-version-2.expressnetw.com
laos-ca-version-2.expressnetw.com
macau-ca-version-2.expressnetw.com
malaysia-ca-version-2.expressnetw.com
mongolia-ca-version-2.expressnetw.com
myanmar-ca-version-2.expressnetw.com
nepal-ca-version-2.expressnetw.com
newzealand-ca-version-2.expressnetw.com
pakistan-ca-version-2.expressnetw.com
ph-via-sing-ca-version-2.expressnetw.com
srilanka-ca-version-2.expressnetw.com
taiwan-3-ca-version-2.expressnetw.com
thailand-ca-version-2.expressnetw.com
vietnam-ca-version-2.expressnetw.com

Middle East and Africa

algeria-ca-version-2.expressnetw.com
israel-ca-version-2.expressnetw.com
kenya-ca-version-2.expressnetw.com
southafrica-ca-version-2.expressnetw.com

Merlin ExpressVPN change server location

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

SaferVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 15, 2019 ·

Preparing for Manual SaferVPN Setup

Verify your SaferVPN login information

If you are not already an SaferVPN user Sign Up Now.

Log in to your account on the SaferVPN website.

FlashRouters Privacy App - SaferVPN Login

SaferVPN Server Addresses

View a full list of SaferVPN servers.

America

East Coast:
us1.safervpn.net

West Coast:
us2.safervpn.net

United Kingdom

uk1.safervpn.net

DD-WRT Router Setup for SaferVPN

Navigate to Services > VPN

Enter SaferVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change SaferVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your SaferVPN account with.

Password

Enter the Password you successfully logged in to your SaferVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Additional Config

persist-key
persist-tun
tun-mtu-extra 32
mssfix 1450

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIE1jCCA76gAwIBAgIJAOnRq4FWsZgYMA0GCSqGSIb3DQEBCwUAMIGiMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExFTATBgNVBAcTDFNhbkZyYW5jaXNjbzERMA8G
A1UEChMIU2FmZXJWUE4xETAPBgNVBAsTCFNhZmVyVlBOMREwDwYDVQQDEwhTYWZl
clZQTjERMA8GA1UEKRMIU2FmZXJWUE4xIzAhBgkqhkiG9w0BCQEWFHN1cHBvcnRA
c2FmZXJ2cG4uY29tMB4XDTE3MDgzMTA5NDEyM1oXDTI3MDgyOTA5NDEyM1owgaIx
CzAJBgNVBAYTAlVTMQswCQYDVQQIEwJDQTEVMBMGA1UEBxMMU2FuRnJhbmNpc2Nv
MREwDwYDVQQKEwhTYWZlclZQTjERMA8GA1UECxMIU2FmZXJWUE4xETAPBgNVBAMT
CFNhZmVyVlBOMREwDwYDVQQpEwhTYWZlclZQTjEjMCEGCSqGSIb3DQEJARYUc3Vw
cG9ydEBzYWZlcnZwbi5jb20wggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIB
AQCqNV7oJZrUqD/mBSWlKi/sGRE2y3Yphs5m/vmmS4GPrc8lyaI1idhv44MGZ0i1
XCkJFZmaVQk7NUz5npz9hcnxN3MiZd/5Kv8Vo4aQkL0xQ7euto71LIgTqbJvTJjW
kowsVVgartGK2ewfCd+KV6k5oBImlDdSnLW1pq82Kg+YcnXxdaFc8RpNWdBbdxBe
tb4k6JcoZHuk9Zq5gi5Nnhtjc6lheCRzTGZ2hslDfJ58yMpR0jTMC3Rd+G+sM0q3
/gEEEW34ckUgCb5j6Kq35LUlnuonnViBnEzFR/MTizMARFj7VYkzOpxSsxJ6Epan
JP8Zgbz81z4A822hosakl7kTAgMBAAGjggELMIIBBzAdBgNVHQ4EFgQUKSnUrJLQ
omrGvdncxKkKT7Rxrj8wgdcGA1UdIwSBzzCBzIAUKSnUrJLQomrGvdncxKkKT7Rx
rj+hgaikgaUwgaIxCzAJBgNVBAYTAlVTMQswCQYDVQQIEwJDQTEVMBMGA1UEBxMM
U2FuRnJhbmNpc2NvMREwDwYDVQQKEwhTYWZlclZQTjERMA8GA1UECxMIU2FmZXJW
UE4xETAPBgNVBAMTCFNhZmVyVlBOMREwDwYDVQQpEwhTYWZlclZQTjEjMCEGCSqG
SIb3DQEJARYUc3VwcG9ydEBzYWZlcnZwbi5jb22CCQDp0auBVrGYGDAMBgNVHRME
BTADAQH/MA0GCSqGSIb3DQEBCwUAA4IBAQB704c0nixfDuJ7OiFBUmkhmDUFEIhl
D35wxlthKYRs8tBzetZEipFGdyUOwuWiuwG/BuOwuP7fPS9uP4u4EPKjA5kL/Z/V
E743q50PS4L/kT3ZFyUrcisUKajAr5Gu+o6rzA6F4+QYu26iBbKewNrrb+riF1wR
GKthc6W++Awt+oVyKtVNyS2QokuBFcSu5IiVsfGqJ8TmffvFBqKUUjWopmP+qiYR
8+0qwHing/S/C9S72ZxhM9DF3et1dXFuHf/69YL8/u36tyKMqy/JVhByAlc87cRI
tcRGaviUttBeSw4j1Y6XrycVkhn4LzizWrqrmfCikhx26MrIeWK5JxYL
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful SaferVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit SaferVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to SaferVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the SaferVPN server

  1. Copy the new SaferVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

OverPlay Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual OverPlay Setup

Verify your OverPlay login information

Log in to your account on the OverPlay website.

OverPlay Server Addresses

View a full list of OverPlay servers.

United States

Ashburn:
iad-a01.wlvpn.com

Atlanta:
atl-a01.wlvpn.com

Chicago
:
chi-a01.wlvpn.com

Dallas
:
dal-a02.wlvpn.com

Las Vegas
:
las-c11.wlvpn.com

Los Angeles
:
lax-a01.wlvpn.com

Miami
:
mia-a01.wlvpn.com

New York
:
nyc-a01.wlvpn.com

Phoenix
:
phx-a01.wlvpn.com

Salt Lake City
:
slc-c01.wlvpn.com

San Jose
:
sjc-a01.wlvpn.com

Seattle
:
sea-a01.wlvpn.com

DD-WRT Router Setup for OverPlay

Navigate to Services > VPN

Enter OverPlay settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change OverPlay connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194 for UDP
443 for TCP

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the username that you use to login to the OverPlay website.  Make sure to add @overplay after your username.

Hint:  For example, if your OverPlay username is “flashrouters” enter “flashrouters@overplay” as your username.

Password

Enter the Password you successfully logged in to your OverPlay account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIESDCCAzCgAwIBAgIJAKSqvk2CSdJGMA0GCSqGSIb3DQEBBQUAMHUxCzAJBgNV
BAYTAlVTMQwwCgYDVQQIEwNWUE4xDDAKBgNVBAcTA1ZQTjEMMAoGA1UEChMDVlBO
MQwwCgYDVQQLEwNWUE4xDDAKBgNVBAMTA1ZQTjEMMAoGA1UEKRMDVlBOMRIwEAYJ
KoZIhvcNAQkBFgNWUE4wHhcNMTMwNDI1MDIzMjQ3WhcNMjMwNDI3MDIzMjQ3WjB1
MQswCQYDVQQGEwJVUzEMMAoGA1UECBMDVlBOMQwwCgYDVQQHEwNWUE4xDDAKBgNV
BAoTA1ZQTjEMMAoGA1UECxMDVlBOMQwwCgYDVQQDEwNWUE4xDDAKBgNVBCkTA1ZQ
TjESMBAGCSqGSIb3DQEJARYDVlBOMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIB
CgKCAQEAyUr2BAz2gHGaXri6rWMpKqcvVTX3IOSLEfBWf1fb2zCwx0+GFMG258Yk
OCiQho/YOX58bJpssGI42OzZitSisTVpXNIBelzGUPdKgx0qURGgDW+7eOySJYCn
1EUncElJCHt1so0SbfdQpxA88VZMH9fFOKtLY5qHHi0drXm/wZy+zW7TfV5Lce04
6vv2M9I5/Ko4zZ5Vh6jTo2VrCQRw8goXB5NAdU5D76lVhWK4Zzt4woI8nRW5Ev3A
WEw5oX85j5B0TY9nEi5j0vNYBuMxf/GiLO8M8LCHPX0HYBiLDjZesJCvuG3vfwnA
Y5CJQqNjufpmnF3ivsaF0dGeo54kWQIDAQABo4HaMIHXMB0GA1UdDgQWBBQXnwHk
vpHSf/lMacKoKshAcGM2qTCBpwYDVR0jBIGfMIGcgBQXnwHkvpHSf/lMacKoKshA
cGM2qaF5pHcwdTELMAkGA1UEBhMCVVMxDDAKBgNVBAgTA1ZQTjEMMAoGA1UEBxMD
VlBOMQwwCgYDVQQKEwNWUE4xDDAKBgNVBAsTA1ZQTjEMMAoGA1UEAxMDVlBOMQww
CgYDVQQpEwNWUE4xEjAQBgkqhkiG9w0BCQEWA1ZQToIJAKSqvk2CSdJGMAwGA1Ud
EwQFMAMBAf8wDQYJKoZIhvcNAQEFBQADggEBADAbNIIHF5vtCA+69/oipQ6niZit
Q+mnCNX5bxiF4xtw9qOQ90vLDc/ocbAGGP4Sub3hEkOoQlv9DHH56HVq1g9+L/Y7
RoneRykZ+GSPj2NlkobrPA7ZxAsLdFwM9Y+Fkql7cAHHLUCKh7H1IKidhTDHPCUj
hs4ZstNRckPd6wxlGGOP/Yf5sVse3pJwa0HyMYhI8pdTVJIHnFSy9vTPjVf3oWiz
Trci0+SkYKQE//5pE5wsYe0uB5wvQJslq/eEWfczg0l9biwJxG/qwxsVBkRgw5q6
defHWGj1eucVyy9fxKMcX89gjstQZDmsINNtG1C78/+nYS65rqaBaq+rqpA=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit OverPlay’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to OverPlay.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the OverPlay server

  1. Copy the new OverPlay server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark Manual OpenVPN Setup

TeamFlashRouters · Apr 24, 2019 ·

Preparing for Manual Surfshark Setup

Obtain your Surfshark OpenVPN information

If you are not already an Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

2. Successfully log in with your account information and Navigate to the Manual Connection Guide. Here you will find the OpenVPN Specific Username and Password required for manual configuration.

FlashRouters Privacy App - SurfShark OpenVPN Specific Username and Password

Surfshark Server Addresses

View a full list of Surfshark servers.

United States

Atlanta:
us-atl.prod.surfshark.com
Buffalo:
us-buf.prod.surfshark.com
Chicago:
us-chi.prod.surfshark.com
Dallas:
us-dal.prod.surfshark.com
Las Vegas:
us-las.prod.surfshark.com
Los Angeles:
us-lax.prod.surfshark.com
Miami:
us-mia.prod.surfshark.com
New York City:
us-nyc.prod.surfshark.com
Phoenix:
us-phx.prod.surfshark.com
San Fransisco:
us-sfo.prod.surfshark.com
Seattle:
us-sea.prod.surfshark.com

DD-WRT Router Setup for Surfshark

Navigate to Services > VPN

Enter Surfshark settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Surfshark connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

None

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
b02cb1d7c6fee5d4f89b8de72b51a8d0
c7b282631d6fc19be1df6ebae9e2779e
6d9f097058a31c97f57f0c35526a44ae
09a01d1284b50b954d9246725a1ead1f
f224a102ed9ab3da0152a15525643b2e
ee226c37041dc55539d475183b889a10
e18bb94f079a4a49888da566b9978346
0ece01daaf93548beea6c827d9674897
e7279ff1a19cb092659e8c1860fbad0d
b4ad0ad5732f1af4655dbd66214e552f
04ed8fd0104e1d4bf99c249ac229ce16
9d9ba22068c6c0ab742424760911d463
6aafb4b85f0c952a9ce4275bc821391a
a65fcd0d2394f006e3fba0fd34c4bc4a
b260f4b45dec3285875589c97d3087c9
134d3a3aa2f904512e85aa2dc2202498
-----END OpenVPN Static key V1-----

Additional Config

remote-cert-tls server
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping-timer-rem
reneg-sec 0
cipher AES-256-GCM
log /tmp/vpn.log

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFTTCCAzWgAwIBAgIJAMs9S3fqwv+mMA0GCSqGSIb3DQEBCwUAMD0xCzAJBgNV
BAYTAlZHMRIwEAYDVQQKDAlTdXJmc2hhcmsxGjAYBgNVBAMMEVN1cmZzaGFyayBS
b290IENBMB4XDTE4MDMxNDA4NTkyM1oXDTI4MDMxMTA4NTkyM1owPTELMAkGA1UE
BhMCVkcxEjAQBgNVBAoMCVN1cmZzaGFyazEaMBgGA1UEAwwRU3VyZnNoYXJrIFJv
b3QgQ0EwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDEGMNj0aisM63o
SkmVJyZPaYX7aPsZtzsxo6m6p5Wta3MGASoryRsBuRaH6VVa0fwbI1nw5ubyxkua
Na4v3zHVwuSq6F1p8S811+1YP1av+jqDcMyojH0ujZSHIcb/i5LtaHNXBQ3qN48C
c7sqBnTIIFpmb5HthQ/4pW+a82b1guM5dZHsh7q+LKQDIGmvtMtO1+NEnmj81BAp
FayiaD1ggvwDI4x7o/Y3ksfWSCHnqXGyqzSFLh8QuQrTmWUm84YHGFxoI1/8AKdI
yVoB6BjcaMKtKs/pbctk6vkzmYf0XmGovDKPQF6MwUekchLjB5gSBNnptSQ9kNgn
TLqi0OpSwI6ixX52Ksva6UM8P01ZIhWZ6ua/T/tArgODy5JZMW+pQ1A6L0b7egIe
ghpwKnPRG+5CzgO0J5UE6gv000mqbmC3CbiS8xi2xuNgruAyY2hUOoV9/BuBev8t
tE5ZCsJH3YlG6NtbZ9hPc61GiBSx8NJnX5QHyCnfic/X87eST/amZsZCAOJ5v4EP
SaKrItt+HrEFWZQIq4fJmHJNNbYvWzCE08AL+5/6Z+lxb/Bm3dapx2zdit3x2e+m
iGHekuiE8lQWD0rXD4+T+nDRi3X+kyt8Ex/8qRiUfrisrSHFzVMRungIMGdO9O/z
CINFrb7wahm4PqU2f12Z9TRCOTXciQIDAQABo1AwTjAdBgNVHQ4EFgQUYRpbQwyD
ahLMN3F2ony3+UqOYOgwHwYDVR0jBBgwFoAUYRpbQwyDahLMN3F2ony3+UqOYOgw
DAYDVR0TBAUwAwEB/zANBgkqhkiG9w0BAQsFAAOCAgEAn9zV7F/XVnFNZhHFrt0Z
S1Yqz+qM9CojLmiyblMFh0p7t+Hh+VKVgMwrz0LwDH4UsOosXA28eJPmech6/bjf
ymkoXISy/NUSTFpUChGO9RabGGxJsT4dugOw9MPaIVZffny4qYOc/rXDXDSfF2b+
303lLPI43y9qoe0oyZ1vtk/UKG75FkWfFUogGNbpOkuz+et5Y0aIEiyg0yh6/l5Q
5h8+yom0HZnREHhqieGbkaGKLkyu7zQ4D4tRK/mBhd8nv+09GtPEG+D5LPbabFVx
KjBMP4Vp24WuSUOqcGSsURHevawPVBfgmsxf1UCjelaIwngdh6WfNCRXa5QQPQTK
ubQvkvXONCDdhmdXQccnRX1nJWhPYi0onffvjsWUfztRypsKzX4dvM9k7xnIcGSG
EnCC4RCgt1UiZIj7frcCMssbA6vJ9naM0s7JF7N3VKeHJtqe1OCRHMYnWUZt9vrq
X6IoIHlZCoLlv39wFW9QNxelcAOCVbD+19MZ0ZXt7LitjIqe7yF5WxDQN4xru087
FzQ4Hfj7eH1SNLLyKZkA1eecjmRoi/OoqAt7afSnwtQLtMUc2bQDg6rHt5C0e4dC
LqP/9PGZTSJiwmtRHJ/N5qYWIh9ju83APvLm/AGBTR2pXmj9G3KdVOkpIC7L35dI
623cSEC3Q3UZutsEm/UplsM=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Surfshark connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Surfshark server

  1. Visit the Surfshark Manual setup page and scroll down to Section 3.
  2. Copy and paste one of the server IP Address into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Windscribe Manual OpenVPN Setup

TeamFlashRouters · Apr 25, 2019 ·

Preparing for Manual Windscribe Setup

Verify your Windscribe login information

If you are not already an Windscribe user Sign Up Now.

1. Log in to your account on the Windscribe website.

2. Click on the Download link at the top of the page.

3. Scroll down to the Config Generators section and Click on the OpenVPN link.

Windscribe Website - Generate OpenVPN Configuration Files

4. Click on Get Credentials and copy the Username and Password. This information will be used later on in the configuration.

Windscribe Website OpenVPN Specific Username and Password

Windscribe Server Addresses

United States

US East:
us-east.windscribe.com
US West:
us-west.windscribe.com
US Windflix:
wf-us.windscribe.com

Canada

Canada:
ca.windscribe.com
Canada West:
ca-west.windscribe.com

Additional Servers

Australia:
au.windscribe.com
Austria:
at.windscribe.com
Belgium:
be.windscribe.com
Brazil:
br.windscribe.com
Bulgaria:
bg.windscribe.com
Czech Republic:
cz.windscribe.com
Denmark:
dk.windscribe.com
Egypt:
eg.windscribe.com
Finland:
fi.windscribe.com
France:
fr.windscribe.com
Germany:
de.windscribe.com
Hong Kong:
hk.windscribe.com
Hungary:
hu.windscribe.com
India:
in.windscribe.com
Ireland:
ie.windscribe.com
Italy:
it.windscribe.com
Japan:
jp.windscribe.com
Latvia:
lv.windscribe.com
Luxemburg:
lu.windscribe.com
Malaysia:
my.windscribe.com
Mexico:
mx.windscribe.com
Netherlands:
nl.windscribe.com
Norway:
no.windscribe.com
Poland:
pl.windscribe.com
Romania:
ro.windscribe.com
Russia:
ru.windscribe.com
Singapore:
ch.windscribe.com
South Africa:
za.windscribe.com
South Korea:
kr.windscribe.com
Spain:
es.windscribe.com
Sweden:
se.windscribe.com
Switzerland:
ch.windscribe.com
Taiwan:
tw.windscribe.com
Turkey:
tr.windscribe.com
Ukraine:
ua.windscribe.com
United Kingdom:
uk.windscribe.com

DD-WRT Router Setup for Windscribe

Navigate to Services > VPN

Enter Windscribe settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and Paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Windscribe connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

User Pass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
5801926a57ac2ce27e3dfd1dd6ef8204
2d82bd4f3f0021296f57734f6f1ea714
a6623845541c4b0c3dea0a050fe6746c
b66dfab14cda27e5ae09d7c155aa554f
399fa4a863f0e8c1af787e5c602a801d
3a2ec41e395a978d56729457fe6102d7
d9e9119aa83643210b33c678f9d4109e
3154ac9c759e490cb309b319cf708cae
83ddadc3060a7a26564d1a24411cd552
fe6620ea16b755697a4fc5e6e9d0cfc0
c5c4a1874685429046a424c026db672e
4c2c492898052ba59128d46200b40f88
0027a8b6610a4d559bdc9346d33a0a6b
08e75c7fd43192b162bfd0aef0c716b3
1584827693f676f9a5047123466f0654
eade34972586b31c6ce7e395f4b478cb
-----END OpenVPN Static key V1-----

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFozCCA4ugAwIBAgIBATANBgkqhkiG9w0BAQ0FADBAMQswCQYDVQQGEwJDSDEV
MBMGA1UEChMMUHJvdG9uVlBOIEFHMRowGAYDVQQDExFQcm90b25WUE4gUm9vdCBD
QTAeFw0xNzAyMTUxNDM4MDBaFw0yNzAyMTUxNDM4MDBaMEAxCzAJBgNVBAYTAkNI
MRUwEwYDVQQKEwxQcm90b25WUE4gQUcxGjAYBgNVBAMTEVByb3RvblZQTiBSb290
IENBMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAt+BsSsZg7+AuqTq7
vDbPzfygtl9f8fLJqO4amsyOXlI7pquL5IsEZhpWyJIIvYybqS4s1/T7BbvHPLVE
wlrq8A5DBIXcfuXrBbKoYkmpICGc2u1KYVGOZ9A+PH9z4Tr6OXFfXRnsbZToie8t
2Xjv/dZDdUDAqeW89I/mXg3k5x08m2nfGCQDm4gCanN1r5MT7ge56z0MkY3FFGCO
qRwspIEUzu1ZqGSTkG1eQiOYIrdOF5cc7n2APyvBIcfvp/W3cpTOEmEBJ7/14RnX
nHo0fcx61Inx/6ZxzKkW8BMdGGQF3tF6u2M0FjVN0lLH9S0ul1TgoOS56yEJ34hr
JSRTqHuar3t/xdCbKFZjyXFZFNsXVvgJu34CNLrHHTGJj9jiUfFnxWQYMo9UNUd4
a3PPG1HnbG7LAjlvj5JlJ5aqO5gshdnqb9uIQeR2CdzcCJgklwRGCyDT1pm7eoiv
WV19YBd81vKulLzgPavu3kRRe83yl29It2hwQ9FMs5w6ZV/X6ciTKo3etkX9nBD9
ZzJPsGQsBUy7CzO1jK4W01+u3ItmQS+1s4xtcFxdFY8o/q1zoqBlxpe5MQIWN6Qa
lryiET74gMHE/S5WrPlsq/gehxsdgc6GDUXG4dk8vn6OUMa6wb5wRO3VXGEc67IY
m4mDFTYiPvLaFOxtndlUWuCruKcCAwEAAaOBpzCBpDAMBgNVHRMEBTADAQH/MB0G
A1UdDgQWBBSDkIaYhLVZTwyLNTetNB2qV0gkVDBoBgNVHSMEYTBfgBSDkIaYhLVZ
TwyLNTetNB2qV0gkVKFEpEIwQDELMAkGA1UEBhMCQ0gxFTATBgNVBAoTDFByb3Rv
blZQTiBBRzEaMBgGA1UEAxMRUHJvdG9uVlBOIFJvb3QgQ0GCAQEwCwYDVR0PBAQD
AgEGMA0GCSqGSIb3DQEBDQUAA4ICAQCYr7LpvnfZXBCxVIVc2ea1fjxQ6vkTj0zM
htFs3qfeXpMRf+g1NAh4vv1UIwLsczilMt87SjpJ25pZPyS3O+/VlI9ceZMvtGXd
MGfXhTDp//zRoL1cbzSHee9tQlmEm1tKFxB0wfWd/inGRjZxpJCTQh8oc7CTziHZ
ufS+Jkfpc4Rasr31fl7mHhJahF1j/ka/OOWmFbiHBNjzmNWPQInJm+0ygFqij5qs
51OEvubR8yh5Mdq4TNuWhFuTxpqoJ87VKaSOx/Aefca44Etwcj4gHb7LThidw/ky
zysZiWjyrbfX/31RX7QanKiMk2RDtgZaWi/lMfsl5O+6E2lJ1vo4xv9pW8225B5X
eAeXHCfjV/vrrCFqeCprNF6a3Tn/LX6VNy3jbeC+167QagBOaoDA01XPOx7Odhsb
Gd7cJ5VkgyycZgLnT9zrChgwjx59JQosFEG1DsaAgHfpEl/N3YPJh68N7fwN41Cj
zsk39v6iZdfuet/sP7oiP5/gLmA/CIPNhdIYxaojbLjFPkftVjVPn49RqwqzJJPR
N8BOyb94yhQ7KO4F3IcLT/y/dsWitY0ZH4lCnAVV/v2YjWAWS3OWyC8BFx/Jmc3W
DK/yPwECUcPgHIeXiRjHnJt0Zcm23O2Q3RphpU+1SO3XixsXpOVOYP6rJIXW9bMZ
A1gTTlpi7A==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Windscribe VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Windscribe server

  1. Copy and paste the server IP Address from the server list above into the Server IP/Name field.
  2. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

IPVanish Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual IPVanish Setup

Verify your IPVanish login information

If you are not already an IPVanish user Sign Up Now.

Log in to your account on the IPVanish website.

IPVanish Server Addresses

View a full list of IPVanish servers.

America

Ashburn:
iad-a01.ipvanish.com
through
iad-a78.ipvanish.com

Atlanta:
atl-a01.ipvanish.com
through
atl-a88.ipvanish.com

Boston:
bos-c01.ipvanish.com
through
bos-c27.ipvanish.com

Chicago:
chi-a01.ipvanish.com
through
chi-a58.ivpanish.com

Cleveland:
cle-c01.ipvanish.com
through
cle-c20.ipvanish.com

Dallas:
dal-a01.ipvanish.com
through
dal-a79.ipvanish.com

Denver:
den-c01.ipvanish.com
through
den-c13.ipvanish.com

Jackson:
jan-c01.ipvanish.com
through
jan-c15.ipvanish.com

Las Vegas:
las-c11.ipvanish.com
through
las-c20.ipvanish.com

Los Angeles:
lax-a01.ipvanish.com
through
lax-a60.ipvanish.com

Miami:
mia-a01.ipvanish.com
through
mia-a34.ipvanish.com

Milwaukee:
mke-c01.ipvanish.com
through
mke-c19.ipvanish.com

New York:
nyc-a01.ipvanish.com
through
nyc-a51.ipvanish.com

Phoenix:
phx-a01.ipvanish.com
through
phx-a24.ipvanish.com

Salt Lake City:
slc-c01.ipvanish.com
through
slc-c12.ipvanish.com

San Jose:
sjc-a01.ipvanish.com
through
sjc-a27.ipvanish.com

Seattle:
sea-a01-ipvanish.com
through
sea-a41.ipvanish.com

St. Louis:
stl-c01.ipvanish.com
through
stl-c18.ipvanish.com

United Kingdom

London:
lon-a01.ipvanish.com
through
lon-a69.ipvanish.com

lon-c01.ipvanish.com
through
lon-c58.ipvanish.com

Manchester:
man-c01.ipvanish.com
through
man-c09.ipvanish.com

DD-WRT Router Setup for IPVanish

Navigate to Services > VPN

Enter IPVanish settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change IPVanish connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your IPVanish account with.

Password

Enter the Password you successfully logged in to your IPVanish account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun
persist-remote-ip
keysize 256

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIErTCCA5WgAwIBAgIJAMYKzSS8uPKDMA0GCSqGSIb3DQEBDQUAMIGVMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCRkwxFDASBgNVBAcTC1dpbnRlciBQYXJrMREwDwYD
VQQKEwhJUFZhbmlzaDEVMBMGA1UECxMMSVBWYW5pc2ggVlBOMRQwEgYDVQQDEwtJ
UFZhbmlzaCBDQTEjMCEGCSqGSIb3DQEJARYUc3VwcG9ydEBpcHZhbmlzaC5jb20w
HhcNMTIwMTExMTkzMjIwWhcNMjgxMTAyMTkzMjIwWjCBlTELMAkGA1UEBhMCVVMx
CzAJBgNVBAgTAkZMMRQwEgYDVQQHEwtXaW50ZXIgUGFyazERMA8GA1UEChMISVBW
YW5pc2gxFTATBgNVBAsTDElQVmFuaXNoIFZQTjEUMBIGA1UEAxMLSVBWYW5pc2gg
Q0ExIzAhBgkqhkiG9w0BCQEWFHN1cHBvcnRAaXB2YW5pc2guY29tMIIBIjANBgkq
hkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAt9DBWNr/IKOuY3TmDP5x7vYZR0DGxLbX
U8TyAzBbjUtFFMbhxlHiXVQrZHmgzih94x7BgXM7tWpmMKYVb+gNaqMdWE680Qm3
nOwmhy/dulXDkEHAwD05i/iTx4ZaUdtV2vsKBxRg1vdC4AEiwD7bqV4HOi13xcG9
71aQ55Mj1KeCdA0aNvpat1LWx2jjWxsfI8s2Lv5Fkoi1HO1+vTnnaEsJZrBgAkLX
pItqP29Lik3/OBIvkBIxlKrhiVPixE5qNiD+eSPirsmROvsyIonoJtuY4Dw5K6pc
NlKyYiwo1IOFYU3YxffwFJk+bSW4WVBhsdf5dGxq/uOHmuz5gdwxCwIDAQABo4H9
MIH6MAwGA1UdEwQFMAMBAf8wHQYDVR0OBBYEFEv9FCWJHefBcIPX9p8RHCVOGe6u
MIHKBgNVHSMEgcIwgb+AFEv9FCWJHefBcIPX9p8RHCVOGe6uoYGbpIGYMIGVMQsw
CQYDVQQGEwJVUzELMAkGA1UECBMCRkwxFDASBgNVBAcTC1dpbnRlciBQYXJrMREw
DwYDVQQKEwhJUFZhbmlzaDEVMBMGA1UECxMMSVBWYW5pc2ggVlBOMRQwEgYDVQQD
EwtJUFZhbmlzaCBDQTEjMCEGCSqGSIb3DQEJARYUc3VwcG9ydEBpcHZhbmlzaC5j
b22CCQDGCs0kvLjygzANBgkqhkiG9w0BAQ0FAAOCAQEAI2dkh/43ksV2fdYpVGhY
aFZPVqCJoToCez0IvOmLeLGzow+EOSrY508oyjYeNP4VJEjApqo0NrMbKl8g/8bp
LBcotOCF1c1HZ+y9v7648uumh01SMjsbBeHOuQcLb+7gX6c0pEmxWv8qj5JiW3/1
L1bktnjW5Yp5oFkFSMXjOnIoYKHyKLjN2jtwH6XowUNYpg4qVtKU0CXPdOznWcd9
/zSfa393HwJPeeVLbKYaFMC4IEbIUmKYtWyoJ9pJ58smU3pWsHZUg9Zc0LZZNjkN
lBdQSLmUHAJ33Bd7pJS0JQeiWviC+4UTmzEWRKa7pDGnYRYNu2cUo0/voStphv8E
VA==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful IPVanish connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit IPVanish’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to IPVanish.

Back up your settings

Navigate to Administration > Backup.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the IPVanish server

  1. Copy the new IPVanish server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark Merlin WireGuard Setup

TeamFlashRouters · Mar 30, 2023 ·

Preparing for Surfshark Merlin Setup

Download your Surfshark .conf file

If you are not already a Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

Surfshark Account Login

2. Click VPN Manual Setup.

Surfshark VPN Manual Setup

3. Select Router as the Setup Method.

Surfshark setup method Router

4. Select WireGuard as the Protocol.

Surfshark select WireGuard

5. Select I don’t have a key pair.

Surfshark No Key Pair

6. Enter FlashRouter as the name of the connection and click Next.

Surfshark Connection Name

7. Click Generate a new key pair.

Surfshark Generate new Key Pair

8. Click Choose a location.

Surfshark Choose a Location

9. Select the server location you want to connect to. Unless you need a specific location we recommend using Surfshark’s recommended Fastest server. Click Download to download the .conf file for this Surfshark server location.

Surfshark download conf file

Merlin Router Setup for Surfshark

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Select WireGuard as the VPN Protocol.

Merlin VPN Client WireGuard

4. Click Choose file and select the .conf file you downloaded earlier. Then click Upload.

Merlin WireGuard Choose File Upload

5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location here. Our example server was in New York so I have entered in Surfshark New York.

Merlin WireGuard ProtonVPN Description

6. Set Enable WireGuard to Yes.

Merlin Enable WireGuard

7. Click Apply at the bottom of the page and you should then see a Connected message appear.

Merlin WireGuard Connected

8. By default no devices are assigned to the new active WireGuard connection profile. Click the VPN Director tab to assign specific devices to the new WireGuard profile. Your IP will not be changed on your devices yet.

WireGuard select VPN Director

9. On the VPN Director page click the + symbol next to Add new rule.

WireGuard VPN Director Add new rule

10. Select the new WireGuard profile in the Interface dropdown.

WireGuard VPN Director select Interface

11. In the Local IP field enter in 192.168.50.0/24 if you want ALL devices connected to the FlashRouter’s network to use the WireGuard VPN connection. Click OK.

If you only want certain devices to connect to the WireGuard Client profile you have setting up instead of all the devices connected to the FlashRouter’s network please complete the instructions on our VPN Director guide.

12. Then click Apply at the bottom of the page.

Verify a successful Surfshark connection

Visit Surfshark’s IP Check from a private/incognito browsing window to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark.

How to change the Surfshark server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 8, 2019 ·

Preparing for Manual NordVPN Setup

Verify your NordVPN login information

If you are not already an NordVPN user Sign Up Now.

Log in to your account on the NordVPN website.

NordVPN Server Addresses

For a NordVPN server recommendation visit their Recommend Server page.

Once you have selected the server you want to connect to, download the UDP .ovpn file containing the Server IP Address, TLS Auth Key, and CA Cert referenced below.

Open the .ovpn file that is downloaded to your computer with NotePad++ for Windows or TextEdit for Apple. You will only need the Server IP Address, TLS Auth Key, and CA Cert from this file. All NordVPN servers and .ovpn files have different IP Addresses, keys, and certificates.

DD-WRT Router Setup for NordVPN

Navigate to Services > VPN

Enter NordVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote 206.226.72.27 1194
206.226.72.27 is your NordVPN server IP address. Enter the IP Address in this field.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your NordVPN account with.

Password

Enter the Password you successfully logged in to your NordVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

In the .ovpn file copy and paste all contents in between the <tls-auth> and </tls-auth> lines from your .ovpn file starting and ending with:
—–BEGIN OpenVPN Static key V1—–
…
—–END OpenVPN Static key V1—–

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

In the .ovpn file Copy and Paste all contents in between the <ca> and </ca> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful NordVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit NordVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the NordVPN server

  1. Download and open a new .ovpn file from NordVPN.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the TLS Auth Key into the TLS Auth Key field.
  4. Copy and paste the CA Cert into the CA Cert field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark TP-Link WireGuard Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for Surfshark TP-Link Setup

Download your Surfshark .conf file

If you are not already a Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

Surfshark Account Login

2. Click VPN Manual Setup.

Surfshark VPN Manual Setup

3. Select Router as the Setup method.

Surfshark setup method Router

4. Select WireGuard as the Protocol.

Surfshark select WireGuard

5. Select I don’t have a key pair.

Surfshark No Key Pair

6. Enter FlashRouter as the name of the connection and click Next.

Surfshark Connection Name

7. Click Generate a new key pair.

Surfshark Generate new Key Pair

8. Click Choose a location.

Surfshark Choose a Location

9. Select the server location you want to connect to. Unless you need a specific location we recommend using Surfshark’s recommended Fastest server. Click Download to download the .conf file for this Surfshark server location.

Surfshark download conf file

TP-Link Router Setup for Surfshark

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location. Our example server was New York so I have entered in Surfshark New York.

Set the VPN Type to WireGuard.

Click Browse and select the .conf file you downloaded earlier. Then click Save.

TP-Link Surfshark WireGuard

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link Surfshark WireGuard Connected

Verify a successful Surfshark connection

  1. You should now see a CONNECTED message.
  2. Visit Surfshark’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark.

How to change the Surfshark server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

IVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual IVPN Setup

Verify your IVPN login information

If you are not already an IVPN user Sign Up Now.

Log in to your account on the IVPN website.

FlashRouter Privacy App - IVPN Login

Locate and Copy the Username displayed on the VPN Accounts page.

FlashRouters DD-WRT Privacy APP IVPN OpenVPN Specific Username and Password

IVPN Server Addresses

View a full list of IVPN servers.

United States

Atlanta:
us-ga.gw.ivpn.net

Dallas:
us-tx.gw.ivpn.net

Los Angeles
:
us-ca.gw.ivpn.net

Miami
:
us-fl.gw.ivpn.net

New Jersey
:
us-nj.gw.ivpn.net

Salt Lake City
:
us-ut.gw.ivpn.net

DD-WRT Router Setup for IVPN

Navigate to Services > VPN

Enter IVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PureVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443 for TCP
2049 for UDP

Tunnel Device

TUN

Tunnel Protocol

TCP or UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you noted from the Home page above.
eg. ivpn1234567

Password

Enter the Password you successfully logged in to your IVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
ac470c93ff9f5602a8aab37dee84a528
14d10f20490ad23c47d5d82120c1bf85
9e93d0696b455d4a1b8d55d40c2685c4
1ca1d0aef29a3efd27274c4ef09020a3
978fe45784b335da6df2d12db97bbb83
8416515f2a96f04715fd28949c6fe296
a925cfada3f8b8928ed7fc963c156327
2f5cf46e5e1d9c845d7703ca881497b7
e6564a9d1dea9358adffd435295479f4
7d5298fabf5359613ff5992cb57ff081
a04dfb81a26513a6b44a9b5490ad265f
8a02384832a59cc3e075ad545461060b
7bcab49bac815163cb80983dd51d5b1f
d76170ffd904d8291071e96efc3fb777
856c717b148d08a510f5687b8a8285dc
ffe737b98916dd15ef6235dee4266d3b
-----END OpenVPN Static key V1-----

Additional Config

tls-client
tls-cipher TLS-DHE-RSA-WITH-AES-256-CBC-SHA
resolv-retry infinite
keepalive 10 60
nobind
persist-key
persist-tun
persist-remote-ip
verb 3

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGoDCCBIigAwIBAgIJAJjvUclXmxtnMA0GCSqGSIb3DQEBCwUAMIGMMQswCQYD
VQQGEwJDSDEPMA0GA1UECAwGWnVyaWNoMQ8wDQYDVQQHDAZadXJpY2gxETAPBgNV
BAoMCElWUE4ubmV0MQ0wCwYDVQQLDARJVlBOMRgwFgYDVQQDDA9JVlBOIFJvb3Qg
Q0EgdjIxHzAdBgkqhkiG9w0BCQEWEHN1cHBvcnRAaXZwbi5uZXQwHhcNMjAwMjI2
MTA1MjI5WhcNNDAwMjIxMTA1MjI5WjCBjDELMAkGA1UEBhMCQ0gxDzANBgNVBAgM
Blp1cmljaDEPMA0GA1UEBwwGWnVyaWNoMREwDwYDVQQKDAhJVlBOLm5ldDENMAsG
A1UECwwESVZQTjEYMBYGA1UEAwwPSVZQTiBSb290IENBIHYyMR8wHQYJKoZIhvcN
AQkBFhBzdXBwb3J0QGl2cG4ubmV0MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIIC
CgKCAgEAxHVeaQN3nYCLnGoEg6cY44AExbQ3W6XGKYwC9vI+HJbb1o0tAv56ryvc
6eS6BdG5q9M8fHaHEE/jw9rtznioiXPwIEmqMqFPA9k1oRIQTGX73m+zHGtRpt9P
4tGYhkvbqnN0OGI0H+j9R6cwKi7KpWIoTVibtyI7uuwgzC2nvDzVkLi63uvnCKRX
cGy3VWC06uWFbqI9+QDrHHgdJA1F0wRfg0Iac7TE75yXItBMvNLbdZpge9SmplYW
FQ2rVPG+n75KepJ+KW7PYfTP4Mh3R8A7h3/WRm03o3spf2aYw71t44voZ6agvslv
wqGyczDytsLUny0U2zR7/mfEAyVbL8jqcWr2Df0m3TA0WxwdWvA51/RflVk9G96L
ncUkoxuBT56QSMtdjbMSqRgLfz1iPsglQEaCzUSqHfQExvONhXtNgy+Pr2+wGrEu
SlLMee7aUEMTFEX/vHPZanCrUVYf5Vs8vDOirZjQSHJfgZfwj3nL5VLtIq6ekDhS
AdrqCTILP3V2HbgdZGWPVQxl4YmQPKo0IJpse5Kb6TF2o0i90KhORcKg7qZA40sE
bYLEwqTM7VBs1FahTXsOPAoMa7xZWV1TnigF5pdVS1l51dy5S8L4ErHFEnAp242B
DuTClSLVnWDdofW0EZ0OkK7V9zKyVl75dlBgxMIS0y5MsK7IWicCAwEAAaOCAQEw
gf4wHQYDVR0OBBYEFHUDcMOMo35yg2A/v0uYfkDE11CXMIHBBgNVHSMEgbkwgbaA
FHUDcMOMo35yg2A/v0uYfkDE11CXoYGSpIGPMIGMMQswCQYDVQQGEwJDSDEPMA0G
A1UECAwGWnVyaWNoMQ8wDQYDVQQHDAZadXJpY2gxETAPBgNVBAoMCElWUE4ubmV0
MQ0wCwYDVQQLDARJVlBOMRgwFgYDVQQDDA9JVlBOIFJvb3QgQ0EgdjIxHzAdBgkq
hkiG9w0BCQEWEHN1cHBvcnRAaXZwbi5uZXSCCQCY71HJV5sbZzAMBgNVHRMEBTAD
AQH/MAsGA1UdDwQEAwIBBjANBgkqhkiG9w0BAQsFAAOCAgEAABAjRMJy+mXFLezA
Z8iUgxOjNtSqkCv1aU78K1XkYUzbwNNrSIVGKfP9cqOEiComXY6nniws7QEV2IWi
lcdPKm0x57recrr9TExGGOTVGB/WdmsFfn0g/HgmxNvXypzG3qulBk4qQTymICds
l9vIPb1l9FSjKw1KgUVuCPaYq7xiXbZ/kZdZX49xeKtoDBrXKKhXVYoWus/S+k2I
S8iCxvcp599y7LQJg5DOGlbaxFhsW4R+kfGOaegyhPvpaznguv02i7NLd99XqJhp
v2jTUF5F3T23Z4KkL/wTo4zxz09DKOlELrE4ai++ilCt/mXWECXNOSNXzgszpe6W
As0h9R++sH+AzJyhBfIGgPUTxHHHvxBVLj3k6VCgF7mRP2Y+rTWa6d8AGI2+Raey
V9DVVH9UeSoU0Hv2JHiZL6dRERnyg8dyzKeTCke8poLIjXF+gyvI+22/xsL8jcNH
i9Kji3Vpc3i0Mxzx3gu2N+PL71CwJilgqBgxj0firr3k8sFcWVSGos6RJ3IvFvTh
xYx0p255WrWM01fR9TktPYEfjDT9qpIJ8OrGlNOhWhYj+a45qibXDpaDdb/uBEmf
2sSXNifjSeUyqu6cKfZvMqB7pS3l/AhuAOTT80E4sXLEoDxkFD4C78swZ8wyWRKw
sWGIGABGAHwXEAoDiZ/jjFrEZT0=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful IVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to IVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the IVPN server

  1. Copy the new IVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

How do I connect a Wireless Extender to my FlashRouter network?

Dave · Apr 29, 2019 ·

The settings of your FlashRouter do not need to change to connect an extender to the FlashRouter’s network. Simply access the settings of the extender device and enter the FlashRouter’s wireless network name and the correct wireless password.

The extender will then connect via wireless to the FlashRouter and add wireless range to your network.

To use a DD-WRT router as an extender follow our Advanced Wireless Setup Guides.

It is also easy to setup a Mesh system like Orbi or Velop and send your entire Mesh network through the FlashRouter VPN Network, for a VPN connected Mesh Network.

Simply connect from an open LAN port on your FlashRouter to the WAN port on your Mesh base station and then use your Mesh smart apps to complete the setup from there.

ExpressVPN Asus AX1800S OpenVPN Setup

TeamFlashRouters · Feb 26, 2024 ·

Preparing for ExpressVPN Asus AX1800S Setup

Obtain your ExpressVPN OpenVPN Information

If you are not already an ExpressVPN user Sign Up Now.

1. Log in to your account on the ExpressVPN website.

ExpressVPN login page

2. Successfully log in with your account information. Select More.

3. Select Manual Configuration and copy the Username and Password that are displayed on the right hand side of the screen.

ExpressVPN Manual Configuration
ExpressVPN username and password

4. Click the Server Location that you want to connect to. This will download a .ovpn file to your computer that we will use later on. There is no need to open the file. For this example I have selected New York but feel free to select any server listed there.

ExpressVPN Download .ovpn file

Asus AX1800S Router Setup for ExpressVPN

Login to Asus firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

Asus AX1800S VPN Settings

3. Click Add Profile.

Asus AX1800S VPN Settings

4. Click Choose file and select the .ovpn file you downloaded earlier. Then click Upload.

Asus AX1800S OpenVPN upload

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here.

6. Enter your ExpressVPN username and password that you obtained earlier in the Username and Password. Note that these are different from your ExpressVPN email login and password.

7. Click the Activate button.

Verify a successful ExpressVPN connection

  1. You should now see a check mark in the Connection Status area.
  2. Visit ExpressVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ExpressVPN.

How to change the ExpressVPN server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.
  3. Be sure to deactivate a previously active connection before activating the new one. You do not want to connect to two at the same time.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Flint/Slate GL.iNet ExpressVPN OpenVPN Setup

TeamFlashRouters · May 29, 2023 ·

Preparing for ExpressVPN GL.iNet Setup

Obtain your ExpressVPN OpenVPN Information

If you are not already an ExpressVPN user Sign Up Now.

1. Log in to your account on the ExpressVPN website.

ExpressVPN login page

2. Successfully log in with your account information. Select More.

3. Select Manual Configuration and copy the Username and Password that are displayed on the right hand side of the screen.

ExpressVPN Manual Configuration
ExpressVPN username and password

4. Click the Server Location(s) that you want to connect to. This will download a .ovpn file to your computer that we will use later on. There is no need to open the file. For this example I have selected New York but feel free to select any server listed there or multiple servers.

ExpressVPN Download .ovpn file

GL.iNet Router Setup for ExpressVPN

Login to GL.iNet firmware settings in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network. For more instructions on how to access the firmware settings view our guide here.

1. Navigate to the VPN tab and select OpenVPN Client.

GL.iNet VPN OpenVPN Client

2. Click New Group.

GL.iNet New OpenVPN Client Group

3. Enter ExpressVPN and click the check mark.

GL.iNet ExpressVPN

4. Select the .ovpn file(s) you downloaded earlier and upload them here.

GL.iNet VPN select file

5. Enter in the ExpressVPN username and password that you obtained earlier. Do NOT enter your ExpressVPN account email and password login. Click Apply.

GL.iNet VPN username and password

6. Select VPN Dashboard.

GL.iNet VPN Dashboard

7. Set the Enable toggle to On to begin the ExpressVPN connection.

GL.iNet ExpressVPN enable switch

Verify a successful ExpressVPN connection

  1. You should now see information appear in the Server Address, Server Listen Port, Traffic Statistics, and Client Virtual IP areas.
  2. Visit ExpressVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ExpressVPN.

How to change the ExpressVPN server

  1. Download a new .ovpn file location as detailed above.
  2. In the ExpressVPN Group on the OpenVPN Client area click Upload Configuration File and select the new .ovpn file.
  3. Click VPN Dashboard and then click the Configuration File area and select the new location that you added.
  4. Click Apply.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

CyberGhost Merlin OpenVPN Setup

TeamFlashRouters · Mar 30, 2023 ·

Preparing for CyberGhost Setup

Obtain your CyberGhost OpenVPN information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

2. Select VPN.

CyberGhost VPN

3. Click Configure New Device.

CyberGhost Configure Device

4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost protocol and location

5. Press View configuration.

CyberGhost view configuration

6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the folder that was downloaded. Then open the ca.crt the client.crt, and client.key files with NotePad++ for Windows or TextEdit for Apple. All CyberGhost servers have different keys and certificates.

Merlin Router Setup for CyberGhost

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Click Choose file and select the .ovpn file from the folder you downloaded earlier. Then click Upload.

Merlin Choose File Upload

4. Set Automatic Start at boot time to Yes if you want the VPN connection to begin automatically when the router is powered off and back on.

Merlin Automatic Start at boot time

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location here. Our example server was in USA so I have entered in CyberGhost USA.

Merlin CyberGhost Description field

6. Set Accept DNS Configuration to Strict. Set Redirect Internet traffic through tunnel to Yes (all). Set Kill Switch to Yes or No depending on if you want the Internet to be killed if the VPN connection drops.

Merlin Accept DNS configuration Redirect Internet and Kill Switch

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network please set the Redirect Internet traffic through tunnel to VPN Director. Then complete the instructions on this page and then view our VPN Director guide.

7. Enter your CyberGhost OpenVPN username and password that you obtained earlier. Do not enter your account login.

Merlin VPN Username and Password

8. Click the Edit button in the Keys and Certificates area.

Merlin Keys and Certificates Edit button

9. In the Certificate Authority field paste in the entire content of the ca.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Merlin Certificate Authority

10. In the Client Certificate field paste in the entire content of the client.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Merlin Client Certificate

11. In the Client Key field paste in the entire content of the client.key file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Merlin Client Key

12. Click Save at the bottom of that window.

13. Click Apply at the bottom of the page.

14. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Merlin Service State All Providers

Verify a successful CyberGhost connection

  1. You should now see a CONNECTED message.
  2. Visit What is my IP Address from a private/incognito browser to verify your new IP address and virtual location.

TROUBLESHOOTING

Still having issues? Visit the FR Privacy App Troubleshooting section.

Troubleshoot Here

ExpressVPN Cudy OpenVPN Setup

TeamFlashRouters · Feb 29, 2024 ·

Preparing for ExpressVPN Cudy Setup

Obtain your ExpressVPN OpenVPN Information

If you are not already an ExpressVPN user Sign Up Now.

1. Log in to your account on the ExpressVPN website.

ExpressVPN login page

2. Successfully log in with your account information. Select More.

3. Select Manual Configuration and copy the Username and Password that are displayed on the right hand side of the screen.

ExpressVPN Manual Configuration
ExpressVPN username and password

4. Click the Server Location that you want to connect to. This will download a .ovpn file to your computer that we will use later on. There is no need to open the file. For this example I have selected New York but feel free to select any server listed there.

ExpressVPN Download .ovpn file

Cudy Router Setup for ExpressVPN

Login to Cudy firmware settings in a browser on any computer or smart device connected to the Cudy FlashRouter’s network.

1. Click General Settings.

Cudy General Settings

2. Click VPN.

Cudy VPN Tab

3. Toggle the Enable switch to On.

Cudy enable VPN

4. Select OpenVPN Client from the Protocol dropdown.

Cudy select OpenVPN Client

5. Click Browse and select the .ovpn file you downloaded earlier. You should see the server file name listed next to Current Config File after doing so.

Cudy OpenVPN Browse button

6. Enter your ExpressVPN username and password that you obtained earlier in the Username and Password. Note that these are different from your ExpressVPN email login and password.

Cudy ExpressVPN enter username and password

7. Click Save & Apply at the bottom of the page.

Verify a successful ExpressVPN connection

  1. You should now see a CONNECTED message.
  2. Visit ExpressVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ExpressVPN.

How to change the ExpressVPN server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here
« Previous Page
Next Page »

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer