• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: icons to use on

Sales FAQs

admin · Jan 29, 2019 ·

Sales FAQs

Can My Router Be Preconfigured With My VPN Information?

Plug and Play VPN Support

Yes you can!

To receive a plug and play with VPN device, you will need to provide our team with the credentials from your VPN provider subscription.

IMPORTANT NOTE: This is not required but recommended for users who wish to have the simplest, most seamless experience when the FlashRouter arrives. You can always change the password when the device arrives if you wish as well.


To have your router VPN preconfigured:

  1. Check the “Connect To VPN For Me” box under VPN – Preconfiguration on the Product Page during check out.
  2. Select your VPN provider. If you don’t see your VPN listed select “Other” and you will see an additional field to input who your provider is.
  3. You’ll receive an email after purchase with detailed instructions. If you have any questions our team is happy to help!
Please note:  If you do give a server location, we will automatically start the device with the closest/optimal server for the location we are shipping the device by default. A location has to be added to the initial configuration for plug and play encryption security to occur on the device.


Privacy Hero 2 Only:

While our team isn’t able to pre-configure the Privacy Hero 2 VPN Router before shipping it out since you’ll have to make a Privacy Hero user account and register your router, we can assist you with the VPN set up process once you receive the router and create your Privacy Hero user account via 1-on-1 remote session, email, or live chat on our site.

You can also use our step-by-step Privacy Hero VPN Router Setup Guide to complete the process.

Can I Use My Dedicated IP Address With A FlashRouter?

Dedicated IP Addresses from NordVPN, SurfShark, & TorGuard are supported on almost all of our FlashRouter options.

Check out our Dedicated IP Addresses Blog Post for more details!

Can I Use A FlashRouter With My Current Mesh System?

Yes!

You will be able to connect the FlashRouter of your choosing to your current mesh router via ethernet port as shown below:

ISP Modem/Router —- FlashRouter (VPN) —- Main Mesh Router (VPN from FlashRouter) 

This setup will allow you to keep your mesh network with added VPN protection, as well as add the FlashRouter wireless network for your devices.

You can disable the wifi on the FlashRouter also if you only wanted to use the mesh network for wifi.

Can You Flash My Router and Connect me to VPN?

At FlashRouters, we offer expert router flashing and VPN configuration services through our Flash My Router plans. Whether your router needs custom firmware flashing or just a VPN configuration, we ensure it’s set up for maximum security, privacy, and streaming performance with your chosen VPN provider.

The appointment will take place via remote software. During the appointment, our team will also answer any questions you may have about using the VPN on the router. Flashing is done out of the East Coast of the United States – we will do our best to accommodate your time zone difference if you are located in another part of the United States or another country.

👉 Explore our Flash My Router plans:
🔗 Flash My Router Plans


🔹 How It Works

✅ Flashing vs. Configuration: Some routers require custom firmware (flashing) to enable VPN, while others can be configured without flashing.
✅ Fully Optimized: Our team ensures your router is ready to securely connect to your VPN, block ISP tracking, and enhance your streaming experience.
✅ Remote Assistance Available: Get expert help setting up your VPN connection remotely if needed.


Flashing vs. Configuration: Router Compatibility

At FlashRouters, we handle VPN setup differently based on your router brand and model. Some routers require flashing custom firmware (like DD-WRT or AsusWRT-Merlin), while others can be configured without flashing.

🛠 Router Setup Types by Brand

🔹 Flashing Required (Custom Firmware Installation)

These routers require firmware flashing (DD-WRT or AsusWRT-Merlin) to enable VPN compatibility.

  • Asus – Flashed with AsusWRT-Merlin or updated to the latest AsusWRT build. Some models only require configuration.
  • Linksys – Flashed with DD-WRT firmware.
  • Netgear – Flashed with DD-WRT firmware.

🔹 Configuration Only (No Flashing Required)

These routers have built-in VPN support and only require proper setup.

  • TP-Link – Configured without flashing.
  • GL.iNet – Configured without flashing.
  • Cudy – Configured without flashing.

📌 Other brands are not supported at this time. If you have a different router, we recommend checking out our pre-flashed router options.


✅ Supported VPN Providers

We work with a wide range of VPN providers, including:

  • NordVPN
  • ExpressVPN
  • Surfshark
  • CyberGhost
  • IPVanish
  • Private Internet Access (PIA)
  • VyprVPN
  • ProtonVPN
  • PureVPN
  • Windscribe
  • IVPN
  • Mullvad
  • StrongVPN
  • AzireVPN
  • AstrillVPN
  • HotspotShield VPN

(If your provider isn’t listed, reach out – we may still be able to support it!)


🔗 Get Started Today!

👉 Explore our Flash My Router plans:
🔗 Flash My Router Plans

🔹 Need help selecting the right option? Contact our support team! We’re happy to assist.

How Can I Add The 1 Year NordVPN Service From My FlashRouters.com Order To My Current NordVPN Account?

You can easily combine the free 1 year of NordVPN included with your FlashRouter purchase once you receive the NordVPN Activation Code Email from FlashRouters.com. The email is typically received within 24 hours of order completion and will contain a link as well as an activation code.

This code can be entered at nordvpn.com/activate with the email address associated with your current NordVPN account to add the 1 year of free service to your existing service.


Privacy Hero 2 Only:

You can easily combine the free 1 year of NordVPN included with the Privacy Hero 2 VPN Router during the router activation process.

After activating the router, you’ll receive a NordVPN activation code within your privacy hero account dashboard. This code can be entered at nordvpn.com/activate with the email address associated with your current NordVPN account to add the 1 year of free service to your existing service.

What Are the Differences Between New, Recertified, And Open Box FlashRouters?

New

  • Direct from manufacturer, in new box.
  • Custom flashed on demand at time of the order.
  • 30 Day Satisfaction Guarantee / 1 Year Warranty.

Recertified (RM)

  • Direct from manufacturer/reseller, may be reboxed.
  • Custom flashed on demand at time of the order.
  • Specialists tested to guarantee same functionality as NEW routers.
  • 30 Day Satisfaction Guarantee / 1 Year Warranty.

Open Box

  • Limited quantity, discount items reboxed that may have cosmetic imperfections.
  • Same testing and functionality level and New and RM.
  • 30 Day Satisfaction Guarantee / No Warranty.

Will a FlashRouter Work With My Internet Service Provider?

US Customers (Single Router Solution):

Almost all Internet Service Providers(ISPs) require a modem in place to establish a connection to their service, however a modem by itself doesn’t provide the wifi connectivity needed in the home or office. A FlashRouter can connect directly to all known modems provided by major ISPs to create a wireless network so long as there is an Ethernet port on the modem to connect to the FlashRouter Internet port. 

US Customers (Dual Router Solution): 

Yes, FlashRouters are compatible with your ISP in what is called a Dual Router Set Up.

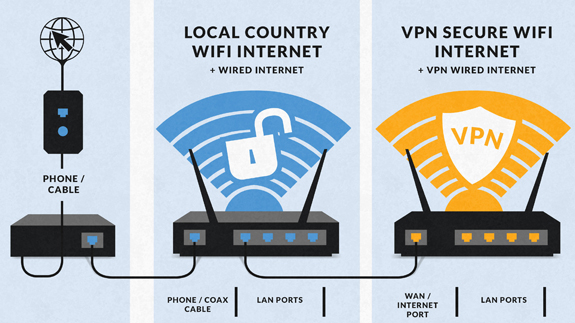
For this type of setup, you would use your current router or modem router to connect to your local ISP while using a FlashRouter to connect to your VPN. This is recommended as you will not overhaul your network with a new router, and you will be able to use your selected VPN service on the devices you wish to use it with.

This set up would result in the creation of two networks, which can be seen as the “Local Network” and the “FlashRouter Network”. All devices connected to the FlashRouter Network will go through the VPN service. 

For any device you would prefer to use without a VPN, you can connect to the local network. The chain of devices would be connected from LAN ton your modem or modem/router to WAN on the FlashRouter, with your current router connected to the FlashRouter via Ethernet cable. 


International Customers (Single Router Solution):

Almost all Internet Service Providers (ISPs) require a modem in place to establish a connection to their service, however a modem by itself doesn’t provide the wifi connectivity needed in the home or office. A FlashRouter can connect directly to all known modems provided by major ISPs to create a wireless network so long as there is an Ethernet port on the modem to connect to the FlashRouter Internet port. 

International Customers (Dual Router Solution):

ISPs should all be compatible. Some providers require VLAN tagging/VID settings when wiring directly from modem to FlashRouter. 

For this type of setup, you would use your current router or modem router to connect to your local ISP while using a FlashRouter to connect to your VPN. This is recommended as you will not overhaul your network with a new router, and you will be able to use your selected VPN service on the devices you wish to use it with.

This set up would result in the creation of two networks, which can be seen as the “Local Network” and the “FlashRouter Network”. All devices connected to the FlashRouter Network will go through the VPN service. 

For any device you would prefer to use without a VPN, you can connect to the local network. The chain of devices would be connected from LAN ton your modem or modem/router to WAN on the FlashRouter, with your current router connected to the FlashRouter via Ethernet cable. 

What Stock Firmware Features Will I Lose If I Flash My Router

Open Source firmware like DD-WRT or Assu Merlin has many features equivalent to what stock firmware has, in addition to adding new features to a router. However, some features are lost from the stock firmware when a router is flashed.

These are typically features that are put into the stock firmware by the manufacturers themselves. Things like the Linksys App and the NetGear Genie are examples of what would not be available or compatible on the router after flashing.

Most routers also have a WPS button. By default, the WPS button’s functionality is disabled when a router is flashed as it can be vulnerable and a security risk. It can be re-enabled by following this guide but we do not recommend it.

Does a FlashRouter or Service Plan Purchase Include a VPN Subscription?

A subscription to a VPN does not come with a FlashRouter or Service plan. If you are planning to use a VPN, you would need to sign up for one separately, directly from a provider.

Need assistance in finding a VPN Provider? Please visit our recent VPN Provider Best Seller List.

Plug and Play VPN Support

Unlike other VPN Router providers, FlashRouters is proud to offer free VPN service integration with any purchase.

To receive a plug and play with VPN device, you will need to provide our team with the credentials from your VPN provider subscription.

IMPORTANT NOTE: This is not required but recommended for users who wish to have the simplest, most seamless experience when the FlashRouter arrives. You can always change the password when the device arrives if you wish as well.

Shows what to look for when you want to preconfigure your router.

To have your router VPN pre-configured:

  1. Select Yes from the “Want Your Router Preconfigured?” on the Payment Page during checkout.
  2. Select your VPN provider. If you don’t see your VPN listed select “Other” and you will see an additional field to input who your provider is.
  3. Enter your your VPN username and password
  4. For ExpressVPN Firmware Routers there will be an additional box for your activation code.

Please note:  If you do not enter a server location request in “Order Comments”, we will automatically start the device with the closest/optimal server for the location we are shipping the device by default. A location has to be added to the initial configuration for plug and play encryption security to occur on the device.

Can I Use A FlashRouter To Work From Home?

Yes! A large number of our customers use their FlashRouters to “work from home” no matter where your travels take you. Check out our Working Remotely Blog Post for more details.

What is the Difference Between Business VPNs and VPN Services?

Location: VPN Services offer many server locations to encrypt your traffic through. They are located in several countries worldwide for creating a private VPN tunnel for your online activities. A business VPN connects to specific central servers for data or directly to your office, creating a direct tunnel for accessing sensitive work documents and information.

Logging: Most VPN services offer log-free connections for total anonymity and security when connected (it is important to check out their terms of service and privacy policy for full details). A business VPN is monitored and maintained by employers such as corporations, hospitals or universities.

Protection: VPN services secure your family’s personal data while using computers, SmartTVs and various Internet of Things devices. Business VPNs protect the data of the company while you are tunneling into work.

Are There VPN Service Providers That Offer VPN for Business?

There are in fact several trusted VPN providers that have services specially tailored for business use. NordVPN Teams and VyprVPN for Business offer a full suite of solutions like user management tools, dedicated IPs, personal product managers, global server access, business pricing, and more.

These solutions allow you to quickly deploy a safe and secure corporate network without building and maintaining your own servers. If you are a small business looking to quickly secure remote workers as they shift to work from home, and you do not have an in-house IT expert, then you should consider NordVPN Teams or VyprVPN for Business.

Even better, when choosing a business VPN provider like NordVPN or VyprVPN, employees can use routers with direct NordVPN and VyprVPN integration already included through the FR Privacy App. Meaning that a full network kill switch, routing by device, automatic connections, and more are all included as features with your business VPN connection.

Can I use a VPN on a FlashRouter With My Work/Corporate VPN?

Many of our customers have found that they can connect to both their corporate and personal VPN, however due to the variables beyond our control, we cannot guarantee this for every unique situation.

Using two VPNs at once can lead to unpredictable results. Bouncing your network traffic to multiple servers before finally arriving at it’s intended destination can sometimes introduce speed and connection issues.

Please consider that some employers and agencies are more vigilant regarding third party VPN use than others. There are tools readily available that detect the use of VPN services.

While these tools cannot decrypt and view your network traffic, they can tell your employer that you are potentially using a VPN, which can be against company policy.

If your corporate and personal VPN do not work together, then you can always set the computer using your work VPN to bypass the FlashRouter’s VPN tunnel by accessing the router admin panel for your device.

This way, your computer would only use the work VPN. Keep in mind however, your location would appear as your actual location to your work.

Every FlashRouter also comes with a 30 Day Satisfaction Guarantee.

If in the event you determine the FlashRouter is not working out for you, you can return the device within the first 30 Days. A $25 restocking fee does apply.

Can I Use a FlashRouter to Connect to a Dedicated Business VPN Network?

Of course! If you have an OpenVPN server running on a local machine or hosted on a cloud provider like Amazon Web Services (AWS), FlashRouters can create a custom router client configuration to connect the entire router and all connected devices to your OpenVPN server. Instead of employees connecting device-by-device, a router-based VPN connection allows for always-on secure VPN tunneling.

Our service team is here to work with you to test and ensure compatibility before purchasing. Interested in a router based custom client VPN solution for your remote workers? Please do not hesitate to contact us.

And, if you’re looking for a specific router, take a look at some of our most popular options!

How can I Reset the Password for My FlashRouters.com Customer Account?

To reset your password, you’ll want to click the “Account” icon in the upper right hand corner on our main website (Flashrouters.com). Once clicked, a menu will open where you can enter your login information, or select the “Forgot Password” button to trigger a reset email.

If you’re still having issues accessing your FlashRouters.com customer account after attempting a password reset, please reach out to us at support@flashrouters.com for further assistance.

What Payment Methods does FlashRouters Accept?

We accept Apple Pay, Google Pay, and all major cred/debit card providers on our payment method options page during checkout.


If you’d like to complete a purchase using PayPal as a payment method, please contact our team at support@flashrouters.com to request an invoice.

Can I Make Change/Update/Cancel My Order?

We strive to process and ship all orders within one business day. If you wish to make changes or cancellations, please contact us within 24 hours of placing your order at support@flashrouters.com with your order number and the changes you’d like to make.

While we will do our best to accommodate your request, please note that we cannot guarantee changes or cancellations.

Please note that if you need to update the shipping address, the order will require reapproval through our fraud prevention system with the new address.

Trouble Checking Out

Some customers have found that trying the methods below have helped solve any checkout errors they may have encountered:

⚡️Clearing cache
⚡️Refreshing web page
⚡️Switching web browsers
⚡️Using an incognito/private window
⚡️Confirming all billing information is accurate
⚡️Disable VPN if one is enabled
⚡️Disable Ad & Script Blockers if enabled
⚡️If you’re using a mobile device, switching to a computer or laptop would be ideal.
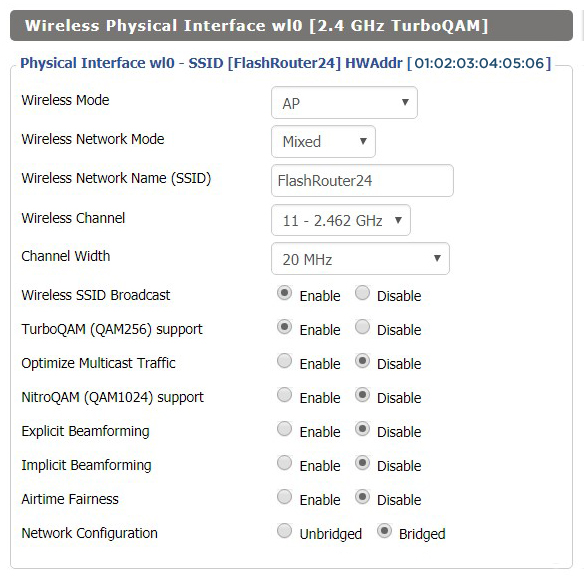
Which DD-WRT wireless extender setup should I be using?

TeamFlashRouters · Jun 11, 2019 ·

FlashRouters supports four unique DD-WRT wireless extender setups – options similar to an open source Mesh network. Each different wireless extender configuration serves a different purpose. Read below to see which guide fits your configuration requirements!

Wireless Repeater

Why should I choose Wireless Repeater Setup?

  1. If you have a MiFi wireless only internet connection or other type of WiFi internet where there is no access to any ethernet port for a wired internet connection, then you can setup a wireless repeater network to both extend WiFi and add wired connection capabilities.
  2. If you have a large home or office area that requires additional WiFi coverage can use a wireless repeater setup to extend the existing network.
  3. If you want to create a separate VPN WiFi network in your home without placing the FlashRouter in the same room as your primary router you can use wireless repeater to establish a WiFi internet connection and then connect to VPN on your WiFi repeater network.
  4. If you want a wireless Dual Router setup option where you can have local ISP IP address through your main router WiFi network and your VPN IP address through your FlashRouter Wireless Repeater WiFi network, both available for you to connect at all times. Each network is on a unique subnet.

View the FlashRouter Wireless Repeater Setup Guide.

Wireless Repeater Bridge

Use Cases

Wireless Repeater Bridge Setup

  1. Anyone that needs all their devices connected to the same local network.
  2. Anyone with a MiFi internet connection that does not have an ethernet port and has no need for VPN.
  3. Anyone with a large wireless area that requires additional coverage.

Wireless Client Bridge

Use Cases

Wireless Client Bridge Setup

  1. Anyone with a MiFi internet connection that needs wired access.
  2. Anyone that needs additional wired ports instead of using a switch.
  3. Anyone with wired only devices in their home that are too far from your main router.

Wireless Access Point DHCP Forwarder

Use Cases

Wireless Access Point DHCP Forwarder Setup

  1. Anyone that needs their devices connected to the same local network and wants lossless LAN to LAN speeds via wireless and ethernet connection.
  2. Anyone that wants to use their main router to provide DHCP to their router instead of having an additional DHCP server.

How to Use ASUS VPN Fusion: Assign Devices and Multiple VPNs

Dave · Oct 26, 2026 ·

ASUS VPN Fusion lets supported AsusWRT routers run VPN client profiles and decide which connected devices use each VPN connection. You can send the entire network through one VPN, use separate VPN profiles for selected devices, or leave certain devices on the regular ISP connection.

This guide covers how to use ASUS VPN Fusion to assign devices to specific VPN connections, manage multiple VPN profiles simultaneously, and choose which devices use a VPN or connect directly through your ISP. These features work with supported VPN providers and protocols, including WireGuard and OpenVPN.

In This Guide

Before You Start →Connect and open VPN FusionApply VPN to All Devices →Default VPN routeAssign Selected Devices →Per-device VPN or ISPMultiple VPN Profiles →WireGuard and OpenVPNVerify & Troubleshoot →Check each device’s public IPGuest Network Routing →VPN WiFi and ISP WiFi

Open VPN Fusion

  1. Connect your computer or phone to your ASUS FlashRouter’s WiFi or LAN.
  2. Open http://www.asusrouter.com or the router’s LAN IP (often 192.168.50.1) and log in. See How to Access Your AsusWRT FlashRouter Settings.
  3. Go to VPN > VPN Fusion. Add and configure at least one working VPN client profile before assigning devices.
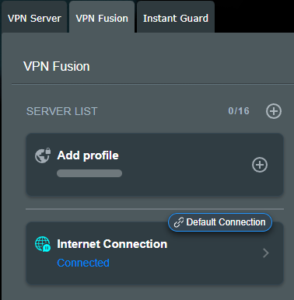
ASUS VPN Fusion page with Add Profile and Internet Connection
VPN Fusion displays your saved VPN profiles and the Add Profile option.

The exact menu names, profile limits, and available VPN types depend on your ASUS model and firmware. Some older ASUS routers use a different VPN Client interface and do not have the full VPN Fusion controls.

Method 1: Apply One VPN to All Devices

Use this option when you want the selected VPN profile to be your router’s default connection.

  1. In VPN Fusion, open the VPN profile that should provide the default internet route.
  2. Enable Apply to all devices (or Default Connection in firmware that uses that label).
  3. Click Apply all settings, then enable the VPN profile.
  4. Connect a test device to the router and check its IP. If you use per-device overrides, verify those rules separately.
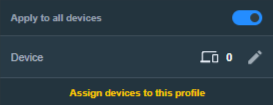
ASUS VPN Fusion Apply to all devices setting and device count
Enable Apply to all devices to use the selected VPN as the default connection.

Do not assume every active VPN profile applies to every device. The default route and any device-specific policies determine which connection a device uses.

Method 2: Send Only Selected Devices Through a VPN

  1. In VPN Fusion, turn off Apply to all devices for a profile when you do not want that VPN used network-wide.
  2. Open the profile’s Device area using the pencil/edit icon or the firmware’s device-assignment control.
  3. Select the intended devices (for example, a TV and streaming box), confirm with OK, then click Apply all settings.
  4. Enable the VPN profile and verify the selected devices’ public IPs.
  5. For devices that should use the normal ISP internet, leave them on the Internet Connection route or explicitly set the Internet/bypass rule available in your firmware. Remove any conflicting VPN assignments.

Important: A device being connected to ASUS WiFi does not guarantee that it is assigned to the desired VPN. Check the assigned profile and the actual public IP.

How Multiple VPN Connections Work

On supported models, VPN Fusion can keep several VPN connections active and route different devices through different providers at the same time. For example:

TVNordVPN — WireGuard
LaptopProton VPN — OpenVPN
Streaming deviceSurfshark — OpenVPN
Work computerRegular ISP connection

You may be able to run one WireGuard profile and multiple OpenVPN profiles concurrently, but connection limits and supported combinations vary by ASUS router model and firmware. Adding many saved OpenVPN profiles is not the same as having all of them connected at once.

  1. Create separate profiles with clear names, such as Nord-US-WG, Proton-US-OVPN, and Surfshark-UK-OVPN.
  2. Enable only the profiles you need and confirm each shows connected.
  3. Assign each client device to the appropriate active profile; avoid applying conflicting default routes.
  4. Verify each device’s observed IP and server country. If one tunnel fails, test it individually with the other profiles temporarily disabled.

ASUS reference: How VPN Fusion handles multiple tunnels and devices.

Confirm a Device Is Actually Using the VPN

  1. In VPN Fusion, confirm the target profile’s connection status is active.
  2. Check the device’s assignment in the ASUS VPN Fusion interface.
  3. On that same device, visit IPLeak.net or another public-IP checker.
  4. Compare the reported public IP and location with the VPN server assigned to that device.
  5. If the device still shows your ISP IP, test with its own VPN app and iCloud Private Relay / Private DNS / browser proxy disabled. Use Device Settings That Can Interfere With Your Router VPN.

Quick isolation test

  1. Turn off VPN Fusion routing for a test device and confirm ISP internet works.
  2. Turn on just one known-working VPN profile for that device.
  3. Recheck public IP. If it now works, reintroduce other profiles/assignments individually.

Want a Separate WiFi Network With or Without VPN?

Rather than selecting devices one at a time, supported ASUS routers offer Guest Network Pro or Network > VPN Network features that can associate a WiFi SSID with VPN routing. See ASUS Guest WiFi With or Without VPN: Setup Guide.

On routers with only the traditional Guest Network feature, available VPN-by-SSID behavior may differ; do not assume the standard guest SSID bypasses a network-wide VPN default.

Related AsusWRT Guides

  • NordVPN Setup for AsusWRT: Token, WireGuard & OpenVPN
  • ASUS Guest WiFi With or Without VPN: Setup Guide
  • Device Settings That Can Interfere With Your Router VPN
  • How to Access Your AsusWRT FlashRouter Settings

Upgrade your ASUS router

Explore the Latest WiFi 7 ASUS FlashRouters

Looking for a newer ASUS router? Browse WiFi 7 models available from FlashRouters and compare features to find the right fit for your home or office. VPN Fusion and other features vary by router model and firmware.

Shop ASUS WiFi 7 Routers →

Wireless Repeater Bridge Setup

TeamFlashRouters · Apr 22, 2019 ·

If you need to extend your connection capabilities and you are not able to wire directly into your main router, you can setup a FlashRouter as a Wireless Repeater Bridge. In Wireless Repeater Bridge mode the FlashRouter connects to your main router on the same subnet via WiFi, and then transmits your internet signal via the FlashRouter for internet access anywhere in your home or office.

Preparing for Wireless Repeater Bridge Setup

Verify your wireless information

In order to setup your FlashRouter as a Wireless Repeater Bridge, you will need the exact SSID and password of your existing wireless network. Make sure you have this information before proceeding.

We recommend using a 2.4GHz network to repeat as this network will have more range. Be sure to click Add under the 2.4GHz settings and not the 5GHz settings.

Locate the Local IP Address of the existing wireless network

Locate the Local IP Address of the existing router that the FlashRouter will be bridged to.

DD-WRT Router Setup for Wireless Repeater Bridge

Disable Firewall

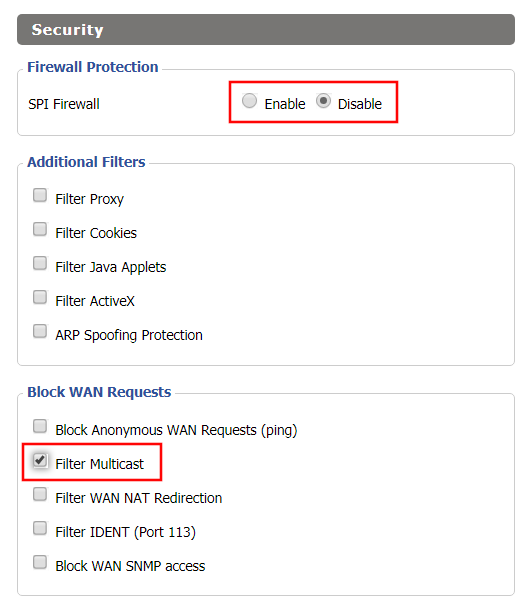
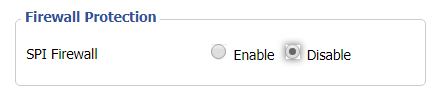
Navigate to Security > Firewall

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable Firewall and Enable Filter Multicast
  1. Set SPI Firewall to Disable.
  2. Uncheck all boxes except for Filter Multicast.
  3. Click Save.

Disable DNSmasq

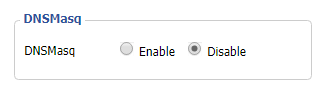
Navigate to Services > Services

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable DNSMasqButton
  1. Set DNSmasq to Disable.
  2. Click Save.

Enter Wireless settings

Navigate to Wireless > Basic Settings

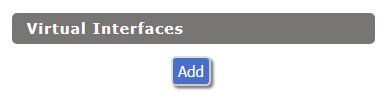
Select Add in the Virtual Interface area.

Wireless Repeater Setup on DD-WRT FlashRouter - Add Virtual Interface

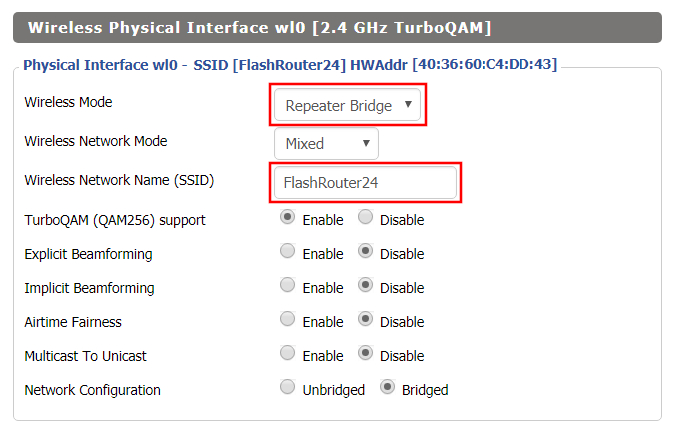
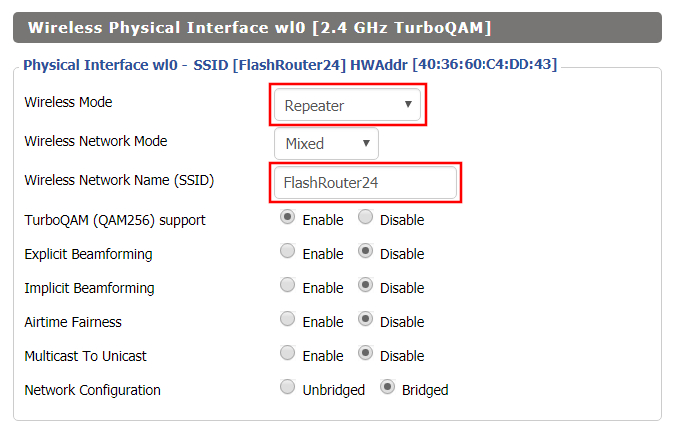
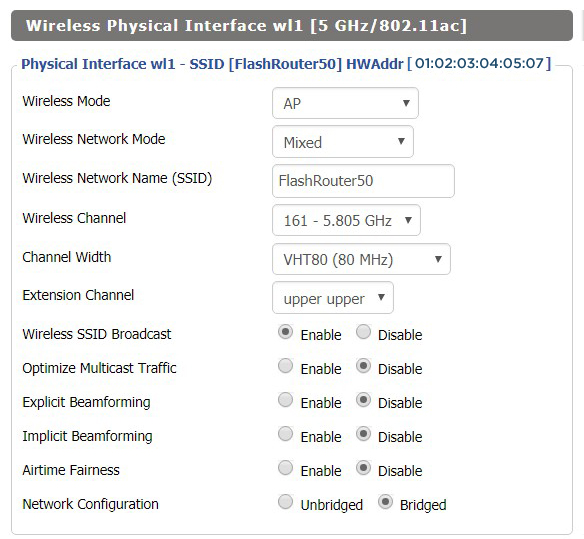
In the Wireless Physical Interface settings for the 2.4GHz network set the Wireless Mode to Repeater Bridge.

Change the Wireless Network Name (SSID) to match exactly with the Wireless Network Name of the network that you will bridge to.

Set Wireless Mode to Repeater Bridge in FlashRouter DD-WRT Basic Wireless Settings Page

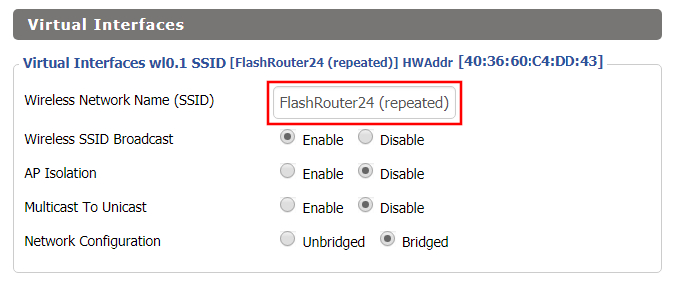
In the Virtual Interfaces settings change the Wireless Network Name (SSID) to FlashRouter24 or any other unique SSID.

Wireless Repeater Setup on DD-WRT FlashRouter - Set SSID for Repeated Band

CLICK SAVE

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

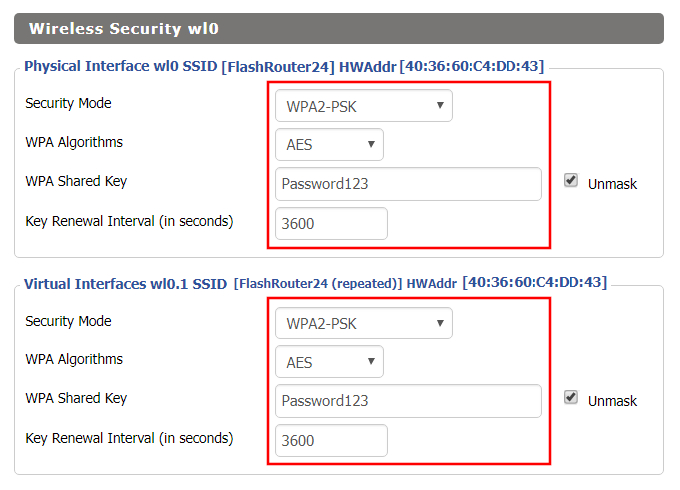
Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Password
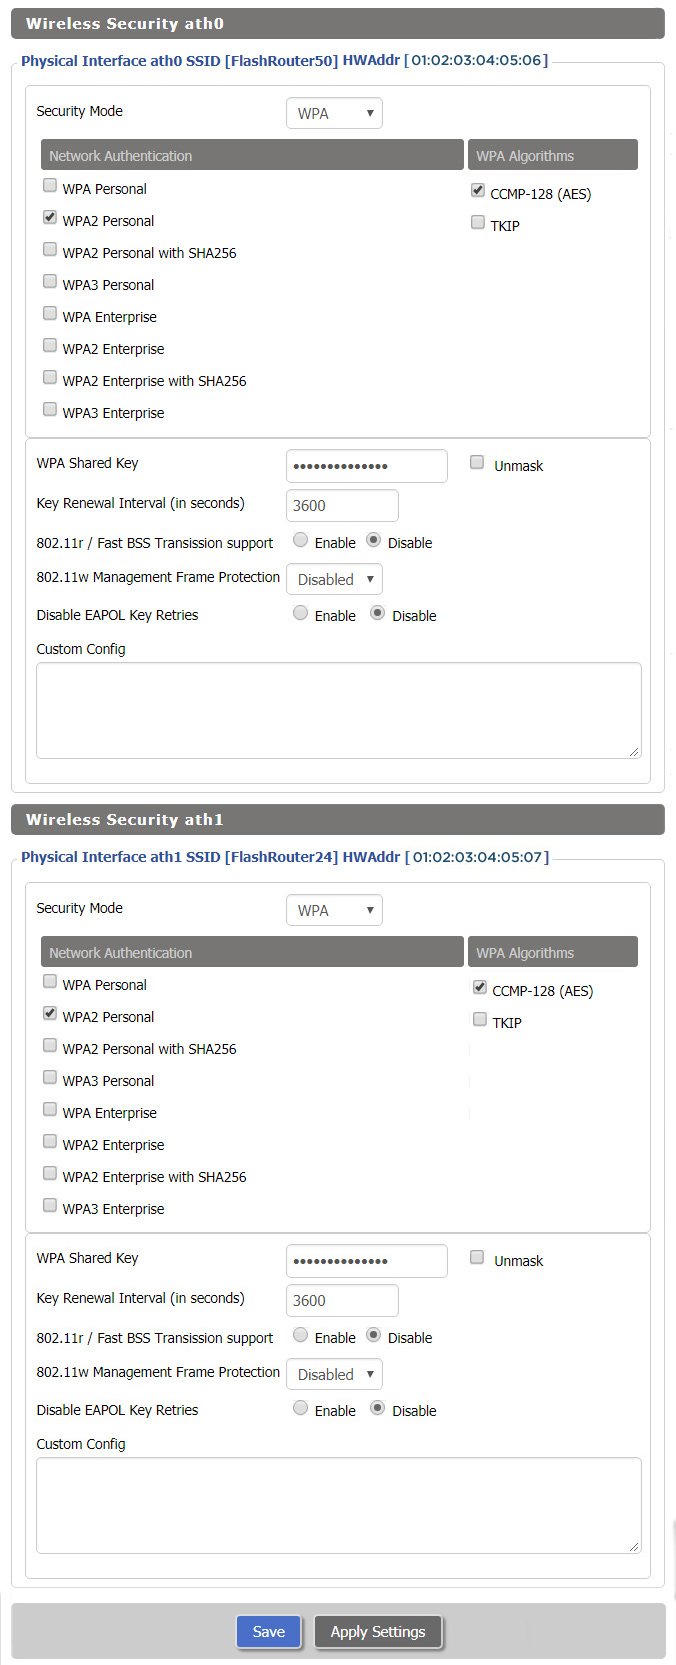
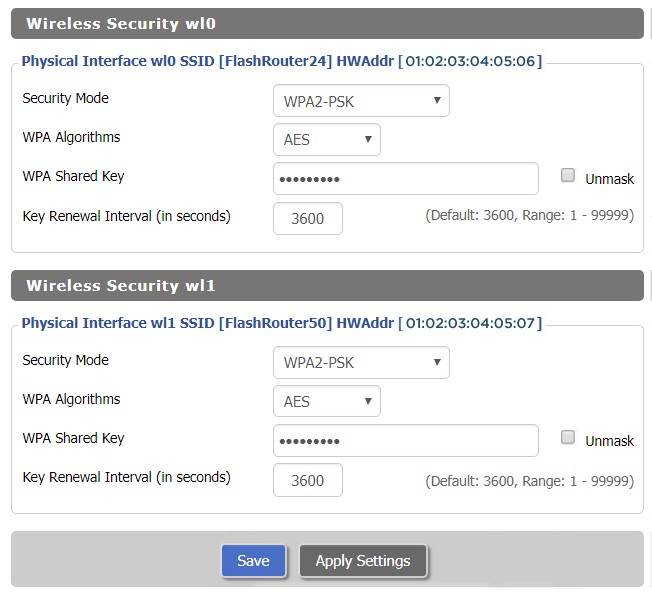
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Change the WPA Shared Key to match exactly with the Wireless Password of the network that you will bridge to.
  3. Click Save.

Change the FlashRouter's Local IP Address

Navigate to Setup > Basic Setup

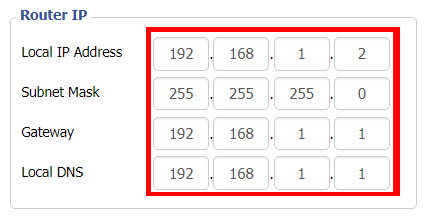
Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Set Local Router IP, Gateway, Local DNS
  1. Set the Local IP Address to a different address on the same subnet as the existing network that you noted early. (example: if the existing network is 192.168.1.1 then set the Local IP Address to 192.168.1.2)
  2. Set the Gateway to the Local IP Address of the existing network. (example: 192.168.1.1)
  3. Set the Local DNS to the Local IP Address of the existing network. (example: 192.168.1.1)
  4. Click Save.

Change the FlashRouter's Operating Mode

Navigate to Setup > Advanced Routing

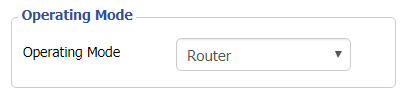
Set Operating Mode to Router in FlashRouter DD-WRT Basic Wireless Settings Page
  1. Set the Operating Mode to Router.
  2. Click Apply Settings.

Reboot your FlashRouter

Power off the FlashRouter for 30 seconds and then power it back on. When it boots back up you will be able to access the FlashRouter’s settings at the new Local IP Address that you set. Your existing network and the FlashRouter’s network will now be bridged wirelessly.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

How to Reset a Failed VPN Connection on Privacy Hero

Dave · Oct 24, 2026 ·

If your Privacy Hero VPN connection shows Failed, you can use the new Reset button to clear the saved third-party VPN settings and return the router to its available default connection. This is useful when a VPN setup is stuck or you want to start again without manually removing the existing third-party VPN configuration.

Important: A VPN reset removes all saved third-party VPN settings from Privacy Hero. You will need to configure that provider again if you want to use it later. The connection Privacy Hero uses after resetting depends on your subscription plan.

Reset a Failed VPN Connection

Follow the reset instructions, then check which connection your plan restores.

When to Use Reset →Know when a VPN reset is appropriate
Reset the Failed VPN →Clear third-party VPN settings in the dashboard
Premium vs. Core →Understand which connection returns afterward
What Gets Removed →Know what you will need to set up again
Verify Your Connection →Check the dashboard and public IP address
Still No Internet? →Check Kill Switch, WAN, and WiFi separately

When Should You Use the VPN Reset Button?

Use Reset when the current VPN connection is in a Failed state and you want to remove the third-party VPN setup and restore a working default connection. It is a more complete action than simply retrying the same VPN server.

  • Use it if the third-party VPN settings are no longer working and you want to start over.
  • Use it if you no longer want the saved third-party VPN configuration.
  • Do not use it if you need to preserve the existing VPN configuration. First try reconnecting or choosing a different VPN server or protocol.

The Reset action addresses the VPN configuration. It does not repair a disconnected WAN cable, an ISP outage, or a router that cannot reach the Privacy Hero cloud.


How to Reset a Failed VPN Connection

  1. Open app.privacyhero.com in a browser and sign in to your Privacy Hero account.
  2. Select your Privacy Hero router, then open its VPN settings.
  3. Confirm the existing VPN connection is showing Failed.
  4. Find the new Reset button in the failed VPN connection area. Before clicking, be aware that this action will remove all third-party VPN settings saved on the router.
  5. Click Reset. If a confirmation message appears, review it before confirming. Allow the dashboard to apply the reset and update the VPN connection status.
  6. Check the resulting connection using the subscription comparison below, then verify internet access from a device connected to Privacy Hero.

Dashboard access during a Kill Switch block: Privacy Hero permits access to app.privacyhero.com over its WiFi or LAN even when the VPN Kill Switch blocks ordinary internet traffic, as long as the router maintains its upstream/cloud connection. You can also manage the router from cellular data or another working internet connection.


What Happens After Reset? Privacy Premium vs. Privacy Core

VPN Reset: Side-by-Side Plan Comparison
Privacy Premium Active subscription Privacy Core
Third-party VPN settingsRemoved Third-party VPN settingsRemoved
Connection after resetBuilt-in Privacy Hero VPN Connection after resetNormal ISP internet
VPN protection afterwardYes, when the built-in VPN is connected VPN protection afterwardNo router VPN is active

Privacy Core users: After resetting, your normal internet access is not VPN-protected by Privacy Hero. If you want a third-party VPN again, you must configure it again in Privacy Hero.

Privacy Premium users: Check that the built-in Privacy Hero VPN shows Connected before assuming your traffic is going through the VPN. A working upstream internet connection and active Premium subscription are still required.


What Information Does the Reset Remove?

The VPN Reset button clears the third-party VPN configuration stored in Privacy Hero. This means any saved third-party provider details will need to be entered or imported again before that provider can be used.

Depending on the provider and protocol you had configured, this may include the saved VPN provider selection, server details, credentials or tokens, and custom OpenVPN or WireGuard settings. Have your provider login or configuration materials available if you plan to set up that VPN again.

This is a VPN configuration reset, not a request to cancel your third-party VPN subscription. It should not be confused with a full router factory reset.


How to Verify Internet and VPN Status After Reset

  1. Refresh the Privacy Hero dashboard and reopen VPN.
  2. If you have Privacy Premium, verify that the built-in Privacy Hero VPN is selected and shows Connected.
  3. If you have Privacy Core, verify that the third-party VPN configuration is gone and ordinary internet access is available through your ISP connection.
  4. Connect a computer or phone to the Privacy Hero WiFi or LAN. To test the router by itself, turn off any VPN application running directly on that device.
  5. Load a regular website, then check your public IP address using ipleak.net. Premium should show a VPN IP if its built-in VPN is connected; Core will normally show your ISP public IP.

If you have Streaming Relocation enabled, some streaming services may use their separately selected location; that is not necessarily the same location shown by a general public IP check.


Reset Complete but Still No Internet?

  1. Check the VPN Kill Switch. If it is still enabled while there is no working VPN connection, it may block ordinary internet traffic. Review the Kill Switch setting before assuming the router has lost WiFi.
  2. Check the connection status. A router listed as Offline may have a WAN, ISP, or cloud-communication problem. The VPN reset cannot fix an upstream internet outage.
  3. Check the network wiring. Confirm your main router or ISP gateway has internet access and the cable is connected to the Privacy Hero WAN/Internet port.
  4. Check a device on Privacy Hero WiFi or LAN. Make sure you are testing the Privacy Hero network rather than another WiFi or cellular connection.
  5. Check your subscription. An active Privacy Premium subscription is required for the built-in Privacy Hero VPN fallback described above. Privacy Core returns to ordinary ISP internet access.

For Kill Switch behavior and restoring internet, see Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting. To learn when to enable the feature, see Privacy Hero VPN Kill Switch Setup.

Related Privacy Hero Articles

  • VPN Kill Switch: No Internet or WiFi Troubleshooting
  • How to Enable the Privacy Hero VPN Kill Switch
  • Privacy Hero VPN Setup Guides

Connect FlashRouter to Internet

TeamFlashRouters · Mar 21, 2019 ·

All FlashRouters are compatible with all ISP service types such as fiber, cable, DSL, and satellite. As long as you have a modem, modem/router, or router capable of an ethernet connection your FlashRouter will have no problems connecting to the internet.

Internet Service Providers (ISP) include a modem or modem/router combo to connect your network devices to the internet. In some instances your ISP will provide a separate router as well as the modem. You can replace this router with a FlashRouter or use both in a dual router setup.

Single router setup

If you would like to replace your outdated router or avoid paying to rent a router from your ISP then you should use a FlashRouter as the only WiFi device in your network.

In a single router setup the FlashRouter will be wired directly to your modem via ethernet cable and will be the only router in the setup.

Connect to your ISP modem

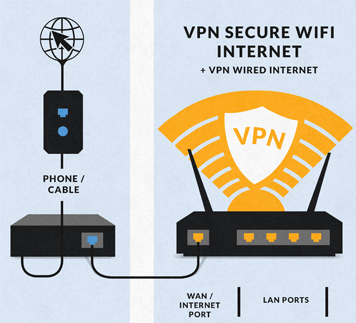
Wire an ethernet cable from an open ethernet port on your modem to the WAN/internet port of the FlashRouter.

FlashRouters Single Router Setup

On Asus FlashRouters the WAN/internet port will be blue.

Asus Wifi Setup - back panel

On Linksys FlashRouters the WAN/internet port will be yellow.

Linksys Wifi Setup - back panel

On Netgear FlashRouters the WAN/internet port will be yellow.

Netgear Wifi Setup - back panel

Power cycle modem and router

Once you have properly connected an ethernet cable from your modem into the FlashRouter internet port you must power cycle your network devices to establish an internet connection.

  1. Power off your ISP modem and the FlashRouter.
  2. Power on the ISP modem and wait for it to fully boot up.
  3. Power on the FlashRouter.

Dual router setup

If you would like to keep your existing WiFi network in place, and simply want to add in a VPN WiFi network with a FlashRouter then you can do so using a dual router setup. No settings in your existing network router need to change to add a FlashRouter in a dual router setup. Since we preset all FlashRouters to a unique Local IP Address, there won’t be a conflict with your existing router.

In a dual router setup the FlashRouter is wired to your existing router via ethernet cable and you will have two completely segmented WiFi networks available.

Connect to your existing router

Remember if your existing router is connecting to the internet without issue already, make sure to keep the ethernet cable between your modem and existing router internet port in place.

Now connect another ethernet cable from a LAN/numbered port on your existing router to the WAN/internet port of the FlashRouter.

Reference the images above to see your WAN/internet port color.

FlashRouters Dual Router Setup

Power cycle all network devices

Once you have properly connected an ethernet cable from your existing router into the FlashRouter internet port you must power cycle your network devices to establish an internet connection.

  1. Power off your ISP modem, existing router, and the FlashRouter.
  2. Power on the ISP modem and wait for it to fully boot up.
  3. Power on the existing router and wait for it to fully boot up.
  4. Power on the FlashRouter.

Verify a successful internet connection

Once the power cycling steps are complete and the FlashRouter is powered up, start connecting your internet capable devices via ethernet or WiFi. Visit any website and make sure the page fully loads.

If you want to check your internet IP address that is visible to websites and services that you visit over the internet check out WhatIsMyIPAddress.com.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

OverPlay Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual OverPlay Setup

Verify your OverPlay login information

Log in to your account on the OverPlay website.

OverPlay Server Addresses

View a full list of OverPlay servers.

United States

Ashburn:
iad-a01.wlvpn.com

Atlanta:
atl-a01.wlvpn.com

Chicago
:
chi-a01.wlvpn.com

Dallas
:
dal-a02.wlvpn.com

Las Vegas
:
las-c11.wlvpn.com

Los Angeles
:
lax-a01.wlvpn.com

Miami
:
mia-a01.wlvpn.com

New York
:
nyc-a01.wlvpn.com

Phoenix
:
phx-a01.wlvpn.com

Salt Lake City
:
slc-c01.wlvpn.com

San Jose
:
sjc-a01.wlvpn.com

Seattle
:
sea-a01.wlvpn.com

DD-WRT Router Setup for OverPlay

Navigate to Services > VPN

Enter OverPlay settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change OverPlay connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194 for UDP
443 for TCP

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the username that you use to login to the OverPlay website.  Make sure to add @overplay after your username.

Hint:  For example, if your OverPlay username is “flashrouters” enter “flashrouters@overplay” as your username.

Password

Enter the Password you successfully logged in to your OverPlay account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIESDCCAzCgAwIBAgIJAKSqvk2CSdJGMA0GCSqGSIb3DQEBBQUAMHUxCzAJBgNV
BAYTAlVTMQwwCgYDVQQIEwNWUE4xDDAKBgNVBAcTA1ZQTjEMMAoGA1UEChMDVlBO
MQwwCgYDVQQLEwNWUE4xDDAKBgNVBAMTA1ZQTjEMMAoGA1UEKRMDVlBOMRIwEAYJ
KoZIhvcNAQkBFgNWUE4wHhcNMTMwNDI1MDIzMjQ3WhcNMjMwNDI3MDIzMjQ3WjB1
MQswCQYDVQQGEwJVUzEMMAoGA1UECBMDVlBOMQwwCgYDVQQHEwNWUE4xDDAKBgNV
BAoTA1ZQTjEMMAoGA1UECxMDVlBOMQwwCgYDVQQDEwNWUE4xDDAKBgNVBCkTA1ZQ
TjESMBAGCSqGSIb3DQEJARYDVlBOMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIB
CgKCAQEAyUr2BAz2gHGaXri6rWMpKqcvVTX3IOSLEfBWf1fb2zCwx0+GFMG258Yk
OCiQho/YOX58bJpssGI42OzZitSisTVpXNIBelzGUPdKgx0qURGgDW+7eOySJYCn
1EUncElJCHt1so0SbfdQpxA88VZMH9fFOKtLY5qHHi0drXm/wZy+zW7TfV5Lce04
6vv2M9I5/Ko4zZ5Vh6jTo2VrCQRw8goXB5NAdU5D76lVhWK4Zzt4woI8nRW5Ev3A
WEw5oX85j5B0TY9nEi5j0vNYBuMxf/GiLO8M8LCHPX0HYBiLDjZesJCvuG3vfwnA
Y5CJQqNjufpmnF3ivsaF0dGeo54kWQIDAQABo4HaMIHXMB0GA1UdDgQWBBQXnwHk
vpHSf/lMacKoKshAcGM2qTCBpwYDVR0jBIGfMIGcgBQXnwHkvpHSf/lMacKoKshA
cGM2qaF5pHcwdTELMAkGA1UEBhMCVVMxDDAKBgNVBAgTA1ZQTjEMMAoGA1UEBxMD
VlBOMQwwCgYDVQQKEwNWUE4xDDAKBgNVBAsTA1ZQTjEMMAoGA1UEAxMDVlBOMQww
CgYDVQQpEwNWUE4xEjAQBgkqhkiG9w0BCQEWA1ZQToIJAKSqvk2CSdJGMAwGA1Ud
EwQFMAMBAf8wDQYJKoZIhvcNAQEFBQADggEBADAbNIIHF5vtCA+69/oipQ6niZit
Q+mnCNX5bxiF4xtw9qOQ90vLDc/ocbAGGP4Sub3hEkOoQlv9DHH56HVq1g9+L/Y7
RoneRykZ+GSPj2NlkobrPA7ZxAsLdFwM9Y+Fkql7cAHHLUCKh7H1IKidhTDHPCUj
hs4ZstNRckPd6wxlGGOP/Yf5sVse3pJwa0HyMYhI8pdTVJIHnFSy9vTPjVf3oWiz
Trci0+SkYKQE//5pE5wsYe0uB5wvQJslq/eEWfczg0l9biwJxG/qwxsVBkRgw5q6
defHWGj1eucVyy9fxKMcX89gjstQZDmsINNtG1C78/+nYS65rqaBaq+rqpA=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit OverPlay’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to OverPlay.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the OverPlay server

  1. Copy the new OverPlay server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

VyprVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual VyprVPN Setup

Verify your VyprVPN login information

If you are not already a VyprVPN user Sign Up Now.

Log in to your account on the VyprVPN website.

VyprVPN - Website Login

VyprVPN Server Addresses

United States

Los Angeles, CA us1.vpn.goldenfrog.com
Washington, DC us2.vpn.goldenfrog.com
Austin, TX us3.vpn.goldenfrog.com
Miami, FL us4.vpn.goldenfrog.com
New York City, NY us5.vpn.goldenfrog.com
Chicago, IL us6.vpn.goldenfrog.com
San Francisco, CA us7.vpn.goldenfrog.com
Seattle, WA us8.vpn.goldenfrog.com

United Kingdom

 London uk1.vpn.goldenfrog.com

Canada

Toronto ca1.vpn.goldenfrog.com

Australia

Sydney au1.vpn.goldenfrog.com
Melbourne au2.vpn.goldenfrog.com
Perth au3.vpn.goldenfrog.com

Germany

Frankfurt de1.vpn.goldenfrog.com

Rest of the World

UAE – Dubai ae1.vpn.goldenfrog.com
Argentina – Buenos Aires ar1.vpn.goldenfrog.com
Austria – Vienna at1.vpn.goldenfrog.com
Belgium – Brussels be1.vpn.goldenfrog.com
Bulgaria – Sofia bg1.vpn.goldenfrog.com
Bahrain – Manama bh1.vpn.goldenfrog.com
Brazil – São Paulo br1.vpn.goldenfrog.com
Switzerland – Zurich ch1.vpn.goldenfrog.com
Colombia – Bogotá co1.vpn.goldenfrog.com
Costa Rica – San José cr1.vpn.goldenfrog.com
Czech Republic – Prague cz1.vpn.goldenfrog.com
Germany – Frankfurt de1.vpn.goldenfrog.com
Denmark – Copenhagen dk1.vpn.goldenfrog.com
Algeria – Algiers dz1.vpn.goldenfrog.com
Egypt – Cairo eg1.vpn.goldenfrog.com
Spain – Madrid es1.vpn.goldenfrog.com
Netherlands – Amsterdam eu1.vpn.goldenfrog.com
Finland – Helsinki fi1.vpn.goldenfrog.com
France – Paris fr1.vpn.goldenfrog.com
Greece – Athens gr1.vpn.goldenfrog.com
Hong Kong – Hong Kong hk1.vpn.goldenfrog.com
Indonesia – Jakarta id1.vpn.goldenfrog.com
Ireland – Dublin ie1.vpn.goldenfrog.com
Israel – Tel Aviv il1.vpn.goldenfrog.com
India – Mumbai in1.vpn.goldenfrog.com
Iceland – Reykjavík is1.vpn.goldenfrog.com
Italy – Rome it1.vpn.goldenfrog.com
Japan – Tokyo jp1.vpn.goldenfrog.com
South Korea – Seoul kr1.vpn.goldenfrog.com
Liechtenstein – Schaan li1.vpn.goldenfrog.com
Lithuania – Vilnius lt1.vpn.goldenfrog.com
Luxembourg – Luxembourg City lu1.vpn.goldenfrog.com
Latvia – Riga lv1.vpn.goldenfrog.com
Marshall Islands – Majuro mh1.vpn.goldenfrog.com
Macao – Macao mo1.vpn.goldenfrog.com
Maldives – Malé mv1.vpn.goldenfrog.com
Mexico – Mexico City mx1.vpn.goldenfrog.com
Malaysia – Kuala Lumpur my1.vpn.goldenfrog.com
Norway – Oslo no1.vpn.goldenfrog.com
New Zealand – Auckland nz1.vpn.goldenfrog.com
Panama – Panama City pa1.vpn.goldenfrog.com
Philippines – Manila ph1.vpn.goldenfrog.com
Pakistan – Karachi pk1.vpn.goldenfrog.com
Poland – Warsaw pl1.vpn.goldenfrog.com
Portugal – Lisbon pt1.vpn.goldenfrog.com
Qatar – Doha qa1.vpn.goldenfrog.com
Romania – Bucharest ro1.vpn.goldenfrog.com
Russia – Moscow ru1.vpn.goldenfrog.com
Saudi Arabia – Riyadh sa1.vpn.goldenfrog.com
Sweden – Stockholm se1.vpn.goldenfrog.com
Singapore – Singapore sg1.vpn.goldenfrog.com
Slovenia – Ljubljana si1.vpn.goldenfrog.com
Slovakia – Bratislava sk1.vpn.goldenfrog.com
El Salvador – San Salvador sv1.vpn.goldenfrog.com
Thailand – Bangkok th1.vpn.goldenfrog.com
Turkey – Istanbul tr1.vpn.goldenfrog.com
Taiwan – Taipei tw1.vpn.goldenfrog.com
Ukraine – Kiev ua1.vpn.goldenfrog.com
Uruguay – Montevideo uy1.vpn.goldenfrog.com
Vietnam – Hanoi vn1.vpn.goldenfrog.com

DD-WRT Router Setup for VyprVPN

Navigate to Services > VPN

VyprVPN offers two different Encryption levels:

Default Encryption (Blowfish-CBC)
typically provides faster speeds.

Strong Encryption (AES-256) provides stronger encryption.

Follow the table below of the one that fits your needs.

Enter VyprVPN settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change VyprVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

Blowfish-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your VyprVPN account with.

Password

Enter the Password you successfully logged in to your VyprVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
keepalive 10 60
persist-key
persist-tun
persist-remote-ip
nobind

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter VyprVPN settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change VyprVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your VyprVPN account with.

Password

Enter the Password you successfully logged in to your VyprVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
keepalive 10 60
persist-key
persist-tun
persist-remote-ip
nobind
tls-cipher TLS-DHE-RSA-WITH-AES-256-CBC-SHA

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing. Learn more here.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VyprVPN connection

Navigate to the Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit to WhatIsMyIPAddress to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to VyprVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the VyprVPN server

  1. Copy the new VyprVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field and Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN Setup for AsusWRT: Token, WireGuard & OpenVPN

TeamFlashRouters · Oct 15, 2025 ·

Set up NordVPN on an ASUS router using AsusWRT VPN Fusion. Supported ASUS firmware offers three different VPN types: NordVPN (access-token integration), WireGuard (downloadable .conf file), and OpenVPN (manual service credentials plus an .ovpn file). Choose the method that matches your needs and your router’s available options.

All configuration is completed directly through your ASUS router’s administration interface using VPN Fusion. Before starting, make sure your router is connected to the internet, your firmware supports VPN Fusion, and you have an active NordVPN subscription.

Before starting, join the ASUS router WiFi or LAN and sign in to http://www.asusrouter.com or your router’s LAN IP (commonly 192.168.50.1). Open VPN > VPN Fusion > Add profile. Router model, firmware, and region affect which VPN types appear. See Access Your AsusWRT Settings.

In This Guide

Choose a VPN Type →NordVPN, WireGuard, or OpenVPNNordVPN Token Setup →Built-in NordLynx integrationWireGuard File Setup →Download and import a .confOpenVPN Setup →Manual credentials and .ovpnDedicated IP Setup →OpenVPN onlyDevices & Troubleshooting →Route devices and verify IP

Which NordVPN Option Should You Choose?

1. NordVPN

NordVPN access token and a country/region dropdown. The built-in ASUS/NordVPN integration is the simplest approach if you only need a country, not an exact server file.

Follow token setup →

2. WireGuard

Import a NordVPN .conf configuration file for a server selected in Nord Account. Useful when you want a downloaded profile for a particular server.

Follow WireGuard setup →

3. OpenVPN

Import a NordVPN .ovpn server file and enter your separate manual service username and password. Also used for NordVPN Dedicated IP.

Follow OpenVPN setup →

Dedicated IP uses OpenVPN only in this guide. Select OpenVPN in VPN Fusion and import your Dedicated IP .ovpn file. Do not use the standard NordVPN token/region dropdown for a Dedicated IP.

Option 1: NordVPN Dropdown — Token-Based NordLynx

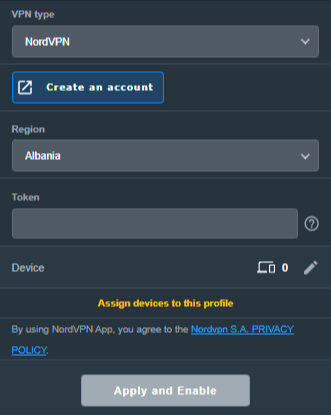
Select the NordVPN type inside VPN Fusion. This is the integrated token-based setup and offers a country/region selection, rather than a manually imported server file.

  1. In Nord Account, open NordVPN Access Tokens and complete email/account verification if requested.
  2. Generate an access token, choose an expiry period if NordVPN offers that setting, and copy the token immediately (it may only be displayed once).
  3. On your ASUS router, open VPN > VPN Fusion > Add profile.
  4. Set VPN Type to NordVPN. Name the profile, select your preferred Region, and paste the token.
  5. Choose Apply to all devices if you want it as the default route, or assign only selected devices (see the VPN Fusion guide below).
  6. Click Apply and Enable / Apply all settings, as shown in your firmware, and verify the profile connects.
ASUS VPN Fusion NordVPN VPN type with Region and Token fields
Keep: existing ASUS NordVPN region/token form (remove any private token before publishing).

Need a specific server? Use the separate WireGuard file method below or the OpenVPN configuration-file method. Do not expect the token-based country dropdown to accept a .conf or .ovpn file.

Option 2: WireGuard Dropdown — Import a NordVPN .conf File

NordVPN now provides downloadable WireGuard configuration files through its manual server recommendation page. This is different from the built-in NordVPN token option in VPN Fusion.

  1. Sign in to Nord Account and open NordVPN Server Recommendation.
  2. Choose your preferred country and server; use the available filters if you need to narrow the list. Select a currently available server.
  3. Choose Get setup configuration, select WireGuard from the protocol menu, and click Download config. Save the downloaded .conf file.
  4. In your ASUS router settings open VPN > VPN Fusion > Add profile, then set VPN Type to WireGuard (not NordVPN).
  5. Use the ASUS Import configuration / file-import control to select the NordVPN .conf file. Confirm the imported parameters and save the profile.
  6. Choose the target devices or enable the default/all-devices route. Click Apply and Enable, then check the VPN status and your public IP.


WireGuard configuration files may contain a private key. Do not share an actual customer .conf file or publish a screenshot exposing its key material. When changing servers, download/import a different file and choose the desired active profile.
NordVPN’s official instructions: How to download WireGuard and OpenVPN configuration files.

Option 3: OpenVPN Dropdown — Credentials + .ovpn File

OpenVPN requires two separate items: the configuration file for your desired server and NordVPN’s manual service credentials. Your normal Nord Account email/password is not the correct credential pair for this method.

  1. Open NordVPN Manual Service Credentials and copy the service username and service password after any required verification.
  2. Open NordVPN OpenVPN Configuration Files and choose a server/location. Download its UDP .ovpn file, or TCP .ovpn if UDP does not work on your network.
  3. On ASUS, go to VPN > VPN Fusion > Add profile and set VPN Type to OpenVPN.
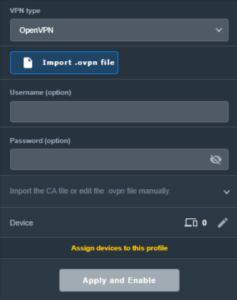
  4. Enter a connection name, Import .ovpn file, and paste the NordVPN manual service username and password in the corresponding fields.
  5. Choose devices or Apply to all devices, then click Apply and Enable. Confirm VPN Fusion shows a successful connection.
ASUS VPN Fusion OpenVPN VPN type with OVPN import and username password fields
Keep: existing ASUS OpenVPN profile form. New screenshots should use a larger clean capture if available.

Server selection: The location is controlled by the server named in the imported .ovpn file. To switch locations, import another server file or use a separate OpenVPN profile.

NordVPN Dedicated IP — OpenVPN Only

If you have purchased and activated the NordVPN Dedicated IP add-on, use your specific Dedicated IP OpenVPN configuration file. Do not select the ordinary NordVPN token integration or a regular shared server.

  1. In your Nord Account, open the Dedicated IP details and download the assigned server’s OpenVPN UDP or TCP configuration file, following NordVPN Dedicated IP manual configuration instructions.
  2. Open NordVPN Manual Service Credentials and copy the manual username and password.
  3. In ASUS VPN Fusion > Add profile, choose OpenVPN.
  4. Import the Dedicated IP .ovpn file, enter manual service credentials, save, enable, and verify the public IP matches your assigned Dedicated IP.

The Dedicated IP add-on must be active on the NordVPN account. A regular shared-server .ovpn file will not give you the Dedicated IP.

Assign Devices, Verify the VPN, and Troubleshoot

One VPN for everyone, or different VPNs for different devices?

VPN Fusion lets you use a VPN profile as the default connection for all devices or assign specific client devices to different profiles. Some supported ASUS models can maintain one WireGuard tunnel alongside multiple OpenVPN profiles, but the number of simultaneous tunnels is model/firmware dependent; creating multiple profiles does not mean all can be active simultaneously.

For step-by-step device assignments, default routing, profile conflicts, and bypassing the VPN, see How to Use ASUS VPN Fusion and Assign Devices to VPN Profiles. For a dedicated WiFi network with VPN or ISP routing, see ASUS Guest Network VPN / No-VPN Setup.

Verify the IP of the actual device

  1. Confirm your chosen profile shows Connected in VPN Fusion.
  2. Join the ASUS WiFi or LAN using a device that is actually assigned to that VPN profile.
  3. Open NordVPN IP Address Check and compare the public IP/location with the intended server or Dedicated IP.
  4. If the device shows an ISP IP, first check Apply to all devices and the per-device assignments in VPN Fusion.
  5. Disconnect a NordVPN app, Apple iCloud Private Relay, browser VPN/proxy, or other device-level network service during testing. Follow Router VPN Shows Wrong IP? Check Device Settings.

If VPN Fusion will not connect

  1. Temporarily disable the failing profile and confirm the ASUS router works using its normal ISP internet connection.
  2. For NordVPN type, check that the access token is valid and hasn’t expired; regenerate if needed.
  3. For WireGuard, import a fresh .conf from the Nord server recommendation page and make sure the profile is enabled.
  4. For OpenVPN, double-check manual service credentials (not website credentials) and try a different server file or TCP instead of UDP.
  5. Check that device-assignment rules point to the intended active profile, then retest with one clean device.

NordVPN Routers & Offers

Shop NordVPN-Ready FlashRouters

Compare ASUS and Privacy Hero router options and choose the hardware that fits your VPN and network requirements.

Browse NordVPN Routers →

NordVPN Partner Offer

Need NordVPN service? See the current FlashRouters NordVPN promotional offer. Subscription pricing and terms are shown on the offer page.

See NordVPN Offer →

Related AsusWRT Guides

  • ASUS VPN Fusion: Assign Devices and Manage Multiple Profiles
  • ASUS Guest Network: WiFi With or Without a VPN
  • AsusWRT Router Login Guide
  • Router VPN Shows Wrong IP? Device Settings

Upgrade your ASUS router

Explore the Latest WiFi 7 ASUS FlashRouters

Looking for a newer ASUS router? Browse WiFi 7 models available from FlashRouters and compare features to find the right fit for your home or office. VPN Fusion and other features vary by router model and firmware.

Shop ASUS WiFi 7 Routers →

SaferVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 15, 2019 ·

Preparing for Manual SaferVPN Setup

Verify your SaferVPN login information

If you are not already an SaferVPN user Sign Up Now.

Log in to your account on the SaferVPN website.

FlashRouters Privacy App - SaferVPN Login

SaferVPN Server Addresses

View a full list of SaferVPN servers.

America

East Coast:
us1.safervpn.net

West Coast:
us2.safervpn.net

United Kingdom

uk1.safervpn.net

DD-WRT Router Setup for SaferVPN

Navigate to Services > VPN

Enter SaferVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change SaferVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your SaferVPN account with.

Password

Enter the Password you successfully logged in to your SaferVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Additional Config

persist-key
persist-tun
tun-mtu-extra 32
mssfix 1450

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIE1jCCA76gAwIBAgIJAOnRq4FWsZgYMA0GCSqGSIb3DQEBCwUAMIGiMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExFTATBgNVBAcTDFNhbkZyYW5jaXNjbzERMA8G
A1UEChMIU2FmZXJWUE4xETAPBgNVBAsTCFNhZmVyVlBOMREwDwYDVQQDEwhTYWZl
clZQTjERMA8GA1UEKRMIU2FmZXJWUE4xIzAhBgkqhkiG9w0BCQEWFHN1cHBvcnRA
c2FmZXJ2cG4uY29tMB4XDTE3MDgzMTA5NDEyM1oXDTI3MDgyOTA5NDEyM1owgaIx
CzAJBgNVBAYTAlVTMQswCQYDVQQIEwJDQTEVMBMGA1UEBxMMU2FuRnJhbmNpc2Nv
MREwDwYDVQQKEwhTYWZlclZQTjERMA8GA1UECxMIU2FmZXJWUE4xETAPBgNVBAMT
CFNhZmVyVlBOMREwDwYDVQQpEwhTYWZlclZQTjEjMCEGCSqGSIb3DQEJARYUc3Vw
cG9ydEBzYWZlcnZwbi5jb20wggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIB
AQCqNV7oJZrUqD/mBSWlKi/sGRE2y3Yphs5m/vmmS4GPrc8lyaI1idhv44MGZ0i1
XCkJFZmaVQk7NUz5npz9hcnxN3MiZd/5Kv8Vo4aQkL0xQ7euto71LIgTqbJvTJjW
kowsVVgartGK2ewfCd+KV6k5oBImlDdSnLW1pq82Kg+YcnXxdaFc8RpNWdBbdxBe
tb4k6JcoZHuk9Zq5gi5Nnhtjc6lheCRzTGZ2hslDfJ58yMpR0jTMC3Rd+G+sM0q3
/gEEEW34ckUgCb5j6Kq35LUlnuonnViBnEzFR/MTizMARFj7VYkzOpxSsxJ6Epan
JP8Zgbz81z4A822hosakl7kTAgMBAAGjggELMIIBBzAdBgNVHQ4EFgQUKSnUrJLQ
omrGvdncxKkKT7Rxrj8wgdcGA1UdIwSBzzCBzIAUKSnUrJLQomrGvdncxKkKT7Rx
rj+hgaikgaUwgaIxCzAJBgNVBAYTAlVTMQswCQYDVQQIEwJDQTEVMBMGA1UEBxMM
U2FuRnJhbmNpc2NvMREwDwYDVQQKEwhTYWZlclZQTjERMA8GA1UECxMIU2FmZXJW
UE4xETAPBgNVBAMTCFNhZmVyVlBOMREwDwYDVQQpEwhTYWZlclZQTjEjMCEGCSqG
SIb3DQEJARYUc3VwcG9ydEBzYWZlcnZwbi5jb22CCQDp0auBVrGYGDAMBgNVHRME
BTADAQH/MA0GCSqGSIb3DQEBCwUAA4IBAQB704c0nixfDuJ7OiFBUmkhmDUFEIhl
D35wxlthKYRs8tBzetZEipFGdyUOwuWiuwG/BuOwuP7fPS9uP4u4EPKjA5kL/Z/V
E743q50PS4L/kT3ZFyUrcisUKajAr5Gu+o6rzA6F4+QYu26iBbKewNrrb+riF1wR
GKthc6W++Awt+oVyKtVNyS2QokuBFcSu5IiVsfGqJ8TmffvFBqKUUjWopmP+qiYR
8+0qwHing/S/C9S72ZxhM9DF3et1dXFuHf/69YL8/u36tyKMqy/JVhByAlc87cRI
tcRGaviUttBeSw4j1Y6XrycVkhn4LzizWrqrmfCikhx26MrIeWK5JxYL
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful SaferVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit SaferVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to SaferVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the SaferVPN server

  1. Copy the new SaferVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

VPN Unlimited Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual VPN Unlimited Setup

Verify your VPN Unlimited login information

If you are not already a VPN Unlimited user Sign Up Now.

Log in to your account on the VPN Unlimited website.

VPN Unlimited Website Login

Generate your VPN Unlimited OVPN Configuration Files

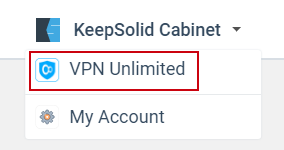
1. Navigate to the VPN Unlimited section in the dropdown on the top left.

VPN Unlimited Website Login

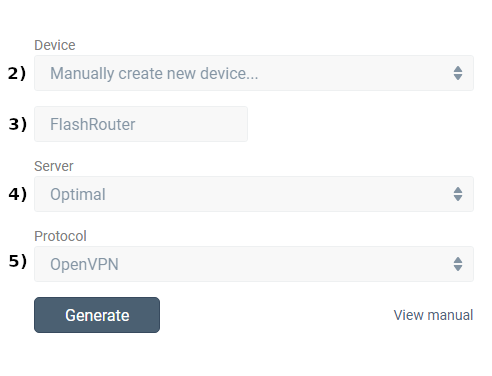
2. Set Device to “Manually create new device…”

3. Name your device.

4. Select Server.

5. Set Protocol to OpenVPN.

FlashRouters DD-WRT Privacy App - Create Open VPN Configuration files

6. Open the ‘.OVPN’ file in a word processing program.

NOTE: We highly recommend using Notepad++ for Windows or TextEdit for Apple to open these files in order to preserve text format.

DD-WRT Router Setup for VPN Unlimited

Navigate to the Services > VPN

Enter VPN Unlimited settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the bottom of the .ovpn file you downloaded above, you can find your server address, it should look something like us-la.vpnunlimitedapp.com

Port

1194 for Tunnel Protocol UDP
80 for Tunnel Protocol TCP

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

Blowfish-CBC

Hash Algorithm

SHA1

User Pass Authentication

Disabled

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIEjjCCA/egAwIBAgIJAKsVbHBdakXuMA0GCSqGSIb3DQEBBQUAMIHgMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCTlkxETAPBgNVBAcTCE5ldyBZb3JrMR8wHQYDVQQK
ExZTaW1wbGV4IFNvbHV0aW9ucyBJbmMuMRYwFAYDVQQLEw1WcG4gVW5saW1pdGVk
MSMwIQYDVQQDExpzZXJ2ZXIudnBudW5saW1pdGVkYXBwLmNvbTEjMCEGA1UEKRMa
c2VydmVyLnZwbnVubGltaXRlZGFwcC5jb20xLjAsBgkqhkiG9w0BCQEWH3N1cHBv
cnRAc2ltcGxleHNvbHV0aW9uc2luYy5jb20wHhcNMTMxMjE2MTM1OTQ0WhcNMjMx
MjE0MTM1OTQ0WjCB4DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAk5ZMREwDwYDVQQH
EwhOZXcgWW9yazEfMB0GA1UEChMWU2ltcGxleCBTb2x1dGlvbnMgSW5jLjEWMBQG
A1UECxMNVnBuIFVubGltaXRlZDEjMCEGA1UEAxMac2VydmVyLnZwbnVubGltaXRl
ZGFwcC5jb20xIzAhBgNVBCkTGnNlcnZlci52cG51bmxpbWl0ZWRhcHAuY29tMS4w
LAYJKoZIhvcNAQkBFh9zdXBwb3J0QHNpbXBsZXhzb2x1dGlvbnNpbmMuY29tMIGf
MA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQDADUzS8QWGvdhLFKsEzAiq5+b0ukKj
Bza0k6/dmCeYTvCVqGKg/h1IAtQdVVLAkmEp0zvGH7PuOhXm7zZrCouBr/RiG4tE
coRHwc6AJmowkYERlY7+xGx3OuNrD00QceNTsan0bn78jwt0zhFNmHdoTtFjgK3o
qmQYSAtbEVWYgwIDAQABo4IBTDCCAUgwHQYDVR0OBBYEFKClmYP+tMNgWagUJCCH
jtaui2k+MIIBFwYDVR0jBIIBDjCCAQqAFKClmYP+tMNgWagUJCCHjtaui2k+oYHm
pIHjMIHgMQswCQYDVQQGEwJVUzELMAkGA1UECBMCTlkxETAPBgNVBAcTCE5ldyBZ
b3JrMR8wHQYDVQQKExZTaW1wbGV4IFNvbHV0aW9ucyBJbmMuMRYwFAYDVQQLEw1W
cG4gVW5saW1pdGVkMSMwIQYDVQQDExpzZXJ2ZXIudnBudW5saW1pdGVkYXBwLmNv
bTEjMCEGA1UEKRMac2VydmVyLnZwbnVubGltaXRlZGFwcC5jb20xLjAsBgkqhkiG
9w0BCQEWH3N1cHBvcnRAc2ltcGxleHNvbHV0aW9uc2luYy5jb22CCQCrFWxwXWpF
7jAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBBQUAA4GBALkWhfw7SSV7it+ZYZmT
+cQbExjlYgQ40zae2J2CqIYACRcfsDHvh7Q+fiwSocevv2NE0dWi6WB2H6SiudYj
vDvubAX/QbzfBxtbxCCoAIlfPCm8xOnWFN7TUJAzWwHJkKgEnu29GZHu2x8J+7Ve
DbKH5RTMHHe8FkSxh6Zz/BMN
—–END CERTIFICATE—–

Public Client Cert

Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN RSA PRIVATE KEY—–
…
—–END RSA PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN Unlimited connection

Navigate to the Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit to WhatIsMyIPAddress to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to VPN Unlimited.

Back up your settings

Navigate to the Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the VPN Unlimited server

  1. Follow Steps 1-6 to Generate an .OVPN file for the server you wish to connect to and open it a word processing program.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the <cert> into the Public Client Cert field.
  4. Copy and paste the <key> into the Private Client Key field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PureVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual PureVPN Setup

Verify your PureVPN login information

If you are not already an PureVPN user Sign Up Now.

Log in to your account on the PureVPN website.

PureVPN Website Login

Navigate to the Home page and note the VPN username on this page. You will need this specific username later on in the configuration process.
Ex: purevpn0s1234567

PureVPN Server Addresses

View a full list of PureVPN servers.

United States

Miami:
usfl1-ovpn-udp.pointtoserver.com

Seattle:
ussa-ovpn-udp.pointtoserver.com

Houston
:
ustx1-ovpn-tcp.pointtoserver.com

Georgia
:
usga1-ovpn-udp.pointtoserver.com

New Jersey
:
usnj1-ovpn-udp.pointtoserver.com

Washington
:
uswdc1-ovpn-udp.pointtoserver.com

Chicago
:
usil1-ovpn-udp.pointtoserver.com

Phoenix
:
usphx1-ovpn-udp.pointtoserver.com

Los Angeles
:
usla1-ovpn-udp.pointtoserver.com

Virginia
:
vlbr-usvc1-ovpn-udp.pointtoserver.com

San Francisco
:
vlsa-ussf1-ovpn-udp.pointtoserver.com

New York
:
usny1-ovpn-udp.pointtoserver.com

Ohio
:
vleu-usoh1-ovpn-udp.pointtoserver.com

United Kingdom

London:
ukl1-ovpn-udp.pointtoserver.com

Gosport:
ukg1-ovpn-udp.pointtoserver.com

Maidenhead:
ukm1-ovpn-udp.pointtoserver.com

Manchester
:
vlus-uk-man1-ovpn-udp.pointtoserver.com

Leicester
:
vlap-ukle1-ovpn-udp.pointtoserver.com

DD-WRT Router Setup for PureVPN

Navigate to Services > VPN

Enter PureVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PureVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

53

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

Userpass Authentication

Enable

Username

Enter the Username you noted from the Home page above.
Ex: purevpn0s1234567

Password

Enter the Password you successfully logged in to your PureVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
e30af995f56d07426d9ba1f824730521
d4283db4b4d0cdda9c6e8759a3799dcb
7939b6a5989160c9660de0f6125cbb1f
585b41c074b2fe88ecfcf17eab9a33be
1352379cdf74952b588fb161a93e13df
9135b2b29038231e02d657a6225705e6
868ccb0c384ed11614690a1894bfbeb2
74cebf1fe9c2329bdd5c8a40fe882062
4d2ea7540cd79ab76892db51fc371a3a
c5fc9573afecb3fffe3281e61d72e915
79d9b03d8cbf7909b3aebf4d90850321
ee6b7d0a7846d15c27d8290e031e951e
19438a4654663cad975e138f5bc5af89
c737ad822f27e19057731f41e1e254cc
9c95b7175c622422cde9f1f2cfd3510a
dd94498b4d7133d3729dd214a16b27fb
-----END OpenVPN Static key V1-----

Additional Config

tls-cipher “DEFAULT:@SECLEVEL=0”

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIEoTCCA4mgAwIBAgIJANysBdFD6U2oMA0GCSqGSIb3DQEBBQUAMIGRMQswCQYD
VQQGEwJISzELMAkGA1UECBMCSEsxETAPBgNVBAcTCEhvbmdLb25nMRAwDgYDVQQK
EwdQdXJlVlBOMQswCQYDVQQLEwJJVDEQMA4GA1UEAxMHUHVyZVZQTjEQMA4GA1UE
KRMHUHVyZVZQTjEfMB0GCSqGSIb3DQEJARYQbWFpbEBob3N0LmRvbWFpbjAeFw0x
NDA0MTAwNzI5NDlaFw0yNDA0MDcwNzI5NDlaMIGRMQswCQYDVQQGEwJISzELMAkG
A1UECBMCSEsxETAPBgNVBAcTCEhvbmdLb25nMRAwDgYDVQQKEwdQdXJlVlBOMQsw
CQYDVQQLEwJJVDEQMA4GA1UEAxMHUHVyZVZQTjEQMA4GA1UEKRMHUHVyZVZQTjEf
MB0GCSqGSIb3DQEJARYQbWFpbEBob3N0LmRvbWFpbjCCASIwDQYJKoZIhvcNAQEB
BQADggEPADCCAQoCggEBAJYqtUkQTlf/pHcGXuuII8S3pfI0fwFbs7l/1RP3nX3n
v1vyuvLi7h0jWsgJU0XM7LJywiRFJ8zsMLH7KZnIg7bscb50GY75WIq7C2NnWnnS
7zzyCCm2XD/2xZPym2lVRytpnWJbpemSS6Hdz7xI3q2FmixuBa1t5FeKsXfeaGGg
+ohwLvamnGHJYUYu3Nu0EWVzzy5wgT0c2C5jleGxl3kxRimD8FpnlAVdqyt0ib/f
f9XanaotSopIHUZmpYjT+udRC2+harlNKvOXYgDRl1mpimCvlzEWpZAo8dyBCxWl
xlBIT8OA8rimGi1XviknuOlWu2cGi13Ug8mCG0MjOQ0CAwEAAaOB+TCB9jAdBgNV
HQ4EFgQUt+1vJ2X2ho12PUDhdo2CsSHYXbYwgcYGA1UdIwSBvjCBu4AUt+1vJ2X2
ho12PUDhdo2CsSHYXbahgZekgZQwgZExCzAJBgNVBAYTAkhLMQswCQYDVQQIEwJI
SzERMA8GA1UEBxMISG9uZ0tvbmcxEDAOBgNVBAoTB1B1cmVWUE4xCzAJBgNVBAsT
AklUMRAwDgYDVQQDEwdQdXJlVlBOMRAwDgYDVQQpEwdQdXJlVlBOMR8wHQYJKoZI
hvcNAQkBFhBtYWlsQGhvc3QuZG9tYWluggkA3KwF0UPpTagwDAYDVR0TBAUwAwEB
/zANBgkqhkiG9w0BAQUFAAOCAQEAAhLQQmkKWJdyGqgMSKOWXSKN2WXTDjIdb9bK
Q8uHeq0LYCcPoRh8VYJg2X4UWR/KO9pKaG+iZJw4Jqz4GQJjjJLKHfsWwj790ay0
7U5KT08qmxFaxZUYn663H9b0+Zud1spTsTJjVe1eoRk6IDbbB4OMUzN9zyWEn6er
xi6llIAjQX1qtlBQasmTAbRtbSsCsZAxL2kXysULIdLrQP0iTgMQqqkv5zvpdEKN
3ciKCd8OHEhHOlAwA0/DNy3dg3Et0F2hNMDJhqMpxXsbKtGJ/rzGXQF2geEVzLZA
o42I1wBOSZLTX1fO1gl3gAGS9aYg5o31rrpBKzQewitJgIuc+Q==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PureVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PureVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PureVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the PureVPN server

  1. Copy the new PureVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Wireless Repeater Setup

TeamFlashRouters · Apr 16, 2019 ·

If you need to extend your wireless and wired connection capabilities, you can setup a FlashRouter as a Wireless Repeater. In Wireless Repeater mode the FlashRouter connects to your main router via WiFi and then creates a completely separate network segment for you. This new “repeater” network then transmits your internet signal via FlashRouter LAN ports for wired internet access while also creating a new Wireless Extender network that will expand your wireless network range throughout your home or office just like a mesh network.

Preparing for Wireless Repeater Setup

Verify your wireless information

To connect your FlashRouter wirelessly to your existing wireless network you will need the Wireless Network Name (SSID) and Wireless Password of the existing wireless network that you will repeat. Verify and note this information.

We recommend using a 2.4GHz network to repeat as this network will have more range. Be sure to click Add under the 2.4GHz settings and not the 5GHz settings.

DD-WRT Router Setup for Wireless Repeater

Disable Firewall

Navigate to Security > Firewall

Wireless Repeater Setup on DD-WRT FlashRouter - Disable SPI Firewall
  1. Set SPI Firewall to Disable.
  2. Click Save.

Enter Wireless settings

Navigate to Wireless > Basic Settings

Select Add in the Virtual Interface area.

Wireless Repeater Setup on DD-WRT FlashRouter - Add Virtual Interface

In the Wireless Physical Interface settings for the 2.4GHz network set the Wireless Mode to Repeater.

FlashRouters with a Broadcom chipset will have Repeater as an option in the dropdown but FlashRouters with an Atheroes chipset will not. Select Client or Client (Routed) if Repeater is not listed for your FlashRouter.

Change the Wireless Network Name (SSID) to match exactly with the Wireless Network Name of the network that you will repeat.

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Mode to Repeater

In the Virtual Interfaces settings change the Wireless Network Name (SSID) to FlashRouter24 or any other unique SSID.

Wireless Repeater Setup on DD-WRT FlashRouter - Set SSID for Repeated Band

CLICK SAVE

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Password
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Change the WPA Shared Key to match exactly with the Wireless Password of the network that you will repeat.
  3. Click Apply Settings.

Verify the Internet Connection

In the top right hand corner of the DD-WRT you should see the WAN IP change from 0.0.0.0 to an actual IP Address. Once this changes navigate to any website to test your Internet connection.

Wireless Repeater Setup on DD-WRT FlashRouter - Verify WAN Connection

Back up your settings

Navigate to the Administration > Backup page.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

DNS Setup for DD-WRT FlashRouters

TeamFlashRouters · Apr 3, 2019 ·

The Domain Name System (DNS) is the phonebook of the Internet. DNS resolves website domain names (www.website.com) to IP Addresses so you don’t have to remember the IP Address of every site you visit.

We setup each FlashRouter with Google DNS (8.8.8.8 , 8.8.4.4) and/or OpenDNS (208.67.220.220 , 208.67.222.222) to prevent your ISP DNS from leaking when connected to the FlashRouter.

By using a trusted DNS server like those listed below, or from your trusted VPN service provider, you can prevent ISP’S from compiling your browsing data and selling it to third parties without your consent.

Recommended DNS servers

GoogleDNS

Primary DNS: 8.8.8.8

Secondary DNS: 8.8.4.4

OpenDNS

Primary DNS: 208.67.220.220

Secondary DNS: 208.67.222.222

Cloudfare

Primary DNS: 1.1.1.1

Secondary DNS: 1.0.0.1

Level 3

Primary DNS: 209.244.0.3

Secondary DNS: 209.244.0.4

How to change the DNS on your FlashRouter

We preset each FlashRouter with GoogleDNS and OpenDNS so there is no need to change the DNS servers unless you have reset the FlashRouter or want to use different DNS servers.

Navigate to Setup > Basic Setup

DNS Setup on DD-WRT FlashRouters
  1. Scroll down to Network Address Server Settings (DHCP).
  2. Enter in any combination of valid DNS servers into Statict DNS fields 1, 2, and 3.
  3. Click Apply Settings at the bottom of the page.
  4. Power cycle your FlashRouter off and back on.

DNS Leak Test

We recommend checking to see if your DNS is leaking when using VPN.

ProtonVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual ProtonVPN Setup

Verify your ProtonVPN login information

If you are not already an ProtonVPN user Sign Up Now.

1. Log in to your account on the ProtonVPN website.

2. Navigate to the Account tab and note your OpenVPN specific Username and Password.

FlashRouters DD-WRT Privacy APP ProtonVPN OpenVPN Specific Username and Password

ProtonVPN Server Addresses

Click on the following link to Download the .ovpn file containing the Server IP Address you wish to connect to.

Open the .ovpn file that is downloaded to your computer with NotePad++ for Windows or TextEdit for Apple.

DD-WRT Router Setup for ProtonVPN

Navigate to Services > VPN

Enter ProtonVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote 206.226.72.27 1194
206.226.72.27 is your ProtonVPN server IP address. Enter that IP Address in this field.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
6acef03f62675b4b1bbd03e53b187727
423cea742242106cb2916a8a4c829756
3d22c7e5cef430b1103c6f66eb1fc5b3
75a672f158e2e2e936c3faa48b035a6d
e17beaac23b5f03b10b868d53d03521d
8ba115059da777a60cbfd7b2c9c57472
78a15b8f6e68a3ef7fd583ec9f398c8b
d4735dab40cbd1e3c62a822e97489186
c30a0b48c7c38ea32ceb056d3fa5a710
e10ccc7a0ddb363b08c3d2777a3395e1
0c0b6080f56309192ab5aacd4b45f55d
a61fc77af39bd81a19218a79762c3386
2df55785075f37d8c71dc8a42097ee43
344739a0dd48d03025b0450cf1fb5e8c
aeb893d9a96d1f15519bb3c4dcb40ee3
16672ea16c012664f8a9f11255518deb
-----END OpenVPN Static key V1-----

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFozCCA4ugAwIBAgIBATANBgkqhkiG9w0BAQ0FADBAMQswCQYDVQQGEwJDSDEV
MBMGA1UEChMMUHJvdG9uVlBOIEFHMRowGAYDVQQDExFQcm90b25WUE4gUm9vdCBD
QTAeFw0xNzAyMTUxNDM4MDBaFw0yNzAyMTUxNDM4MDBaMEAxCzAJBgNVBAYTAkNI
MRUwEwYDVQQKEwxQcm90b25WUE4gQUcxGjAYBgNVBAMTEVByb3RvblZQTiBSb290
IENBMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAt+BsSsZg7+AuqTq7
vDbPzfygtl9f8fLJqO4amsyOXlI7pquL5IsEZhpWyJIIvYybqS4s1/T7BbvHPLVE
wlrq8A5DBIXcfuXrBbKoYkmpICGc2u1KYVGOZ9A+PH9z4Tr6OXFfXRnsbZToie8t
2Xjv/dZDdUDAqeW89I/mXg3k5x08m2nfGCQDm4gCanN1r5MT7ge56z0MkY3FFGCO
qRwspIEUzu1ZqGSTkG1eQiOYIrdOF5cc7n2APyvBIcfvp/W3cpTOEmEBJ7/14RnX
nHo0fcx61Inx/6ZxzKkW8BMdGGQF3tF6u2M0FjVN0lLH9S0ul1TgoOS56yEJ34hr
JSRTqHuar3t/xdCbKFZjyXFZFNsXVvgJu34CNLrHHTGJj9jiUfFnxWQYMo9UNUd4
a3PPG1HnbG7LAjlvj5JlJ5aqO5gshdnqb9uIQeR2CdzcCJgklwRGCyDT1pm7eoiv
WV19YBd81vKulLzgPavu3kRRe83yl29It2hwQ9FMs5w6ZV/X6ciTKo3etkX9nBD9
ZzJPsGQsBUy7CzO1jK4W01+u3ItmQS+1s4xtcFxdFY8o/q1zoqBlxpe5MQIWN6Qa
lryiET74gMHE/S5WrPlsq/gehxsdgc6GDUXG4dk8vn6OUMa6wb5wRO3VXGEc67IY
m4mDFTYiPvLaFOxtndlUWuCruKcCAwEAAaOBpzCBpDAMBgNVHRMEBTADAQH/MB0G
A1UdDgQWBBSDkIaYhLVZTwyLNTetNB2qV0gkVDBoBgNVHSMEYTBfgBSDkIaYhLVZ
TwyLNTetNB2qV0gkVKFEpEIwQDELMAkGA1UEBhMCQ0gxFTATBgNVBAoTDFByb3Rv
blZQTiBBRzEaMBgGA1UEAxMRUHJvdG9uVlBOIFJvb3QgQ0GCAQEwCwYDVR0PBAQD
AgEGMA0GCSqGSIb3DQEBDQUAA4ICAQCYr7LpvnfZXBCxVIVc2ea1fjxQ6vkTj0zM
htFs3qfeXpMRf+g1NAh4vv1UIwLsczilMt87SjpJ25pZPyS3O+/VlI9ceZMvtGXd
MGfXhTDp//zRoL1cbzSHee9tQlmEm1tKFxB0wfWd/inGRjZxpJCTQh8oc7CTziHZ
ufS+Jkfpc4Rasr31fl7mHhJahF1j/ka/OOWmFbiHBNjzmNWPQInJm+0ygFqij5qs
51OEvubR8yh5Mdq4TNuWhFuTxpqoJ87VKaSOx/Aefca44Etwcj4gHb7LThidw/ky
zysZiWjyrbfX/31RX7QanKiMk2RDtgZaWi/lMfsl5O+6E2lJ1vo4xv9pW8225B5X
eAeXHCfjV/vrrCFqeCprNF6a3Tn/LX6VNy3jbeC+167QagBOaoDA01XPOx7Odhsb
Gd7cJ5VkgyycZgLnT9zrChgwjx59JQosFEG1DsaAgHfpEl/N3YPJh68N7fwN41Cj
zsk39v6iZdfuet/sP7oiP5/gLmA/CIPNhdIYxaojbLjFPkftVjVPn49RqwqzJJPR
N8BOyb94yhQ7KO4F3IcLT/y/dsWitY0ZH4lCnAVV/v2YjWAWS3OWyC8BFx/Jmc3W
DK/yPwECUcPgHIeXiRjHnJt0Zcm23O2Q3RphpU+1SO3XixsXpOVOYP6rJIXW9bMZ
A1gTTlpi7A==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful ProtonVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the ProtonVPN server

  1. Download and open a new .ovpn file from ProtonVPN.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark Manual OpenVPN Setup

TeamFlashRouters · Apr 24, 2019 ·

Preparing for Manual Surfshark Setup

Obtain your Surfshark OpenVPN information

If you are not already an Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

2. Successfully log in with your account information and Navigate to the Manual Connection Guide. Here you will find the OpenVPN Specific Username and Password required for manual configuration.

FlashRouters Privacy App - SurfShark OpenVPN Specific Username and Password

Surfshark Server Addresses

View a full list of Surfshark servers.

United States

Atlanta:
us-atl.prod.surfshark.com
Buffalo:
us-buf.prod.surfshark.com
Chicago:
us-chi.prod.surfshark.com
Dallas:
us-dal.prod.surfshark.com
Las Vegas:
us-las.prod.surfshark.com
Los Angeles:
us-lax.prod.surfshark.com
Miami:
us-mia.prod.surfshark.com
New York City:
us-nyc.prod.surfshark.com
Phoenix:
us-phx.prod.surfshark.com
San Fransisco:
us-sfo.prod.surfshark.com
Seattle:
us-sea.prod.surfshark.com

DD-WRT Router Setup for Surfshark

Navigate to Services > VPN

Enter Surfshark settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Surfshark connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

None

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
b02cb1d7c6fee5d4f89b8de72b51a8d0
c7b282631d6fc19be1df6ebae9e2779e
6d9f097058a31c97f57f0c35526a44ae
09a01d1284b50b954d9246725a1ead1f
f224a102ed9ab3da0152a15525643b2e
ee226c37041dc55539d475183b889a10
e18bb94f079a4a49888da566b9978346
0ece01daaf93548beea6c827d9674897
e7279ff1a19cb092659e8c1860fbad0d
b4ad0ad5732f1af4655dbd66214e552f
04ed8fd0104e1d4bf99c249ac229ce16
9d9ba22068c6c0ab742424760911d463
6aafb4b85f0c952a9ce4275bc821391a
a65fcd0d2394f006e3fba0fd34c4bc4a
b260f4b45dec3285875589c97d3087c9
134d3a3aa2f904512e85aa2dc2202498
-----END OpenVPN Static key V1-----

Additional Config

remote-cert-tls server
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping-timer-rem
reneg-sec 0
cipher AES-256-GCM
log /tmp/vpn.log

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFTTCCAzWgAwIBAgIJAMs9S3fqwv+mMA0GCSqGSIb3DQEBCwUAMD0xCzAJBgNV
BAYTAlZHMRIwEAYDVQQKDAlTdXJmc2hhcmsxGjAYBgNVBAMMEVN1cmZzaGFyayBS
b290IENBMB4XDTE4MDMxNDA4NTkyM1oXDTI4MDMxMTA4NTkyM1owPTELMAkGA1UE
BhMCVkcxEjAQBgNVBAoMCVN1cmZzaGFyazEaMBgGA1UEAwwRU3VyZnNoYXJrIFJv
b3QgQ0EwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDEGMNj0aisM63o
SkmVJyZPaYX7aPsZtzsxo6m6p5Wta3MGASoryRsBuRaH6VVa0fwbI1nw5ubyxkua
Na4v3zHVwuSq6F1p8S811+1YP1av+jqDcMyojH0ujZSHIcb/i5LtaHNXBQ3qN48C
c7sqBnTIIFpmb5HthQ/4pW+a82b1guM5dZHsh7q+LKQDIGmvtMtO1+NEnmj81BAp
FayiaD1ggvwDI4x7o/Y3ksfWSCHnqXGyqzSFLh8QuQrTmWUm84YHGFxoI1/8AKdI
yVoB6BjcaMKtKs/pbctk6vkzmYf0XmGovDKPQF6MwUekchLjB5gSBNnptSQ9kNgn
TLqi0OpSwI6ixX52Ksva6UM8P01ZIhWZ6ua/T/tArgODy5JZMW+pQ1A6L0b7egIe
ghpwKnPRG+5CzgO0J5UE6gv000mqbmC3CbiS8xi2xuNgruAyY2hUOoV9/BuBev8t
tE5ZCsJH3YlG6NtbZ9hPc61GiBSx8NJnX5QHyCnfic/X87eST/amZsZCAOJ5v4EP
SaKrItt+HrEFWZQIq4fJmHJNNbYvWzCE08AL+5/6Z+lxb/Bm3dapx2zdit3x2e+m
iGHekuiE8lQWD0rXD4+T+nDRi3X+kyt8Ex/8qRiUfrisrSHFzVMRungIMGdO9O/z
CINFrb7wahm4PqU2f12Z9TRCOTXciQIDAQABo1AwTjAdBgNVHQ4EFgQUYRpbQwyD
ahLMN3F2ony3+UqOYOgwHwYDVR0jBBgwFoAUYRpbQwyDahLMN3F2ony3+UqOYOgw
DAYDVR0TBAUwAwEB/zANBgkqhkiG9w0BAQsFAAOCAgEAn9zV7F/XVnFNZhHFrt0Z
S1Yqz+qM9CojLmiyblMFh0p7t+Hh+VKVgMwrz0LwDH4UsOosXA28eJPmech6/bjf
ymkoXISy/NUSTFpUChGO9RabGGxJsT4dugOw9MPaIVZffny4qYOc/rXDXDSfF2b+
303lLPI43y9qoe0oyZ1vtk/UKG75FkWfFUogGNbpOkuz+et5Y0aIEiyg0yh6/l5Q
5h8+yom0HZnREHhqieGbkaGKLkyu7zQ4D4tRK/mBhd8nv+09GtPEG+D5LPbabFVx
KjBMP4Vp24WuSUOqcGSsURHevawPVBfgmsxf1UCjelaIwngdh6WfNCRXa5QQPQTK
ubQvkvXONCDdhmdXQccnRX1nJWhPYi0onffvjsWUfztRypsKzX4dvM9k7xnIcGSG
EnCC4RCgt1UiZIj7frcCMssbA6vJ9naM0s7JF7N3VKeHJtqe1OCRHMYnWUZt9vrq
X6IoIHlZCoLlv39wFW9QNxelcAOCVbD+19MZ0ZXt7LitjIqe7yF5WxDQN4xru087
FzQ4Hfj7eH1SNLLyKZkA1eecjmRoi/OoqAt7afSnwtQLtMUc2bQDg6rHt5C0e4dC
LqP/9PGZTSJiwmtRHJ/N5qYWIh9ju83APvLm/AGBTR2pXmj9G3KdVOkpIC7L35dI
623cSEC3Q3UZutsEm/UplsM=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Surfshark connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Surfshark server

  1. Visit the Surfshark Manual setup page and scroll down to Section 3.
  2. Copy and paste one of the server IP Address into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Windscribe Manual OpenVPN Setup

TeamFlashRouters · Apr 25, 2019 ·

Preparing for Manual Windscribe Setup

Verify your Windscribe login information

If you are not already an Windscribe user Sign Up Now.

1. Log in to your account on the Windscribe website.

2. Click on the Download link at the top of the page.

3. Scroll down to the Config Generators section and Click on the OpenVPN link.

Windscribe Website - Generate OpenVPN Configuration Files

4. Click on Get Credentials and copy the Username and Password. This information will be used later on in the configuration.

Windscribe Website OpenVPN Specific Username and Password

Windscribe Server Addresses

United States

US East:
us-east.windscribe.com
US West:
us-west.windscribe.com
US Windflix:
wf-us.windscribe.com

Canada

Canada:
ca.windscribe.com
Canada West:
ca-west.windscribe.com

Additional Servers

Australia:
au.windscribe.com
Austria:
at.windscribe.com
Belgium:
be.windscribe.com
Brazil:
br.windscribe.com
Bulgaria:
bg.windscribe.com
Czech Republic:
cz.windscribe.com
Denmark:
dk.windscribe.com
Egypt:
eg.windscribe.com
Finland:
fi.windscribe.com
France:
fr.windscribe.com
Germany:
de.windscribe.com
Hong Kong:
hk.windscribe.com
Hungary:
hu.windscribe.com
India:
in.windscribe.com
Ireland:
ie.windscribe.com
Italy:
it.windscribe.com
Japan:
jp.windscribe.com
Latvia:
lv.windscribe.com
Luxemburg:
lu.windscribe.com
Malaysia:
my.windscribe.com
Mexico:
mx.windscribe.com
Netherlands:
nl.windscribe.com
Norway:
no.windscribe.com
Poland:
pl.windscribe.com
Romania:
ro.windscribe.com
Russia:
ru.windscribe.com
Singapore:
ch.windscribe.com
South Africa:
za.windscribe.com
South Korea:
kr.windscribe.com
Spain:
es.windscribe.com
Sweden:
se.windscribe.com
Switzerland:
ch.windscribe.com
Taiwan:
tw.windscribe.com
Turkey:
tr.windscribe.com
Ukraine:
ua.windscribe.com
United Kingdom:
uk.windscribe.com

DD-WRT Router Setup for Windscribe

Navigate to Services > VPN

Enter Windscribe settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and Paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Windscribe connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

User Pass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
5801926a57ac2ce27e3dfd1dd6ef8204
2d82bd4f3f0021296f57734f6f1ea714
a6623845541c4b0c3dea0a050fe6746c
b66dfab14cda27e5ae09d7c155aa554f
399fa4a863f0e8c1af787e5c602a801d
3a2ec41e395a978d56729457fe6102d7
d9e9119aa83643210b33c678f9d4109e
3154ac9c759e490cb309b319cf708cae
83ddadc3060a7a26564d1a24411cd552
fe6620ea16b755697a4fc5e6e9d0cfc0
c5c4a1874685429046a424c026db672e
4c2c492898052ba59128d46200b40f88
0027a8b6610a4d559bdc9346d33a0a6b
08e75c7fd43192b162bfd0aef0c716b3
1584827693f676f9a5047123466f0654
eade34972586b31c6ce7e395f4b478cb
-----END OpenVPN Static key V1-----

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFozCCA4ugAwIBAgIBATANBgkqhkiG9w0BAQ0FADBAMQswCQYDVQQGEwJDSDEV
MBMGA1UEChMMUHJvdG9uVlBOIEFHMRowGAYDVQQDExFQcm90b25WUE4gUm9vdCBD
QTAeFw0xNzAyMTUxNDM4MDBaFw0yNzAyMTUxNDM4MDBaMEAxCzAJBgNVBAYTAkNI
MRUwEwYDVQQKEwxQcm90b25WUE4gQUcxGjAYBgNVBAMTEVByb3RvblZQTiBSb290
IENBMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAt+BsSsZg7+AuqTq7
vDbPzfygtl9f8fLJqO4amsyOXlI7pquL5IsEZhpWyJIIvYybqS4s1/T7BbvHPLVE
wlrq8A5DBIXcfuXrBbKoYkmpICGc2u1KYVGOZ9A+PH9z4Tr6OXFfXRnsbZToie8t
2Xjv/dZDdUDAqeW89I/mXg3k5x08m2nfGCQDm4gCanN1r5MT7ge56z0MkY3FFGCO
qRwspIEUzu1ZqGSTkG1eQiOYIrdOF5cc7n2APyvBIcfvp/W3cpTOEmEBJ7/14RnX
nHo0fcx61Inx/6ZxzKkW8BMdGGQF3tF6u2M0FjVN0lLH9S0ul1TgoOS56yEJ34hr
JSRTqHuar3t/xdCbKFZjyXFZFNsXVvgJu34CNLrHHTGJj9jiUfFnxWQYMo9UNUd4
a3PPG1HnbG7LAjlvj5JlJ5aqO5gshdnqb9uIQeR2CdzcCJgklwRGCyDT1pm7eoiv
WV19YBd81vKulLzgPavu3kRRe83yl29It2hwQ9FMs5w6ZV/X6ciTKo3etkX9nBD9
ZzJPsGQsBUy7CzO1jK4W01+u3ItmQS+1s4xtcFxdFY8o/q1zoqBlxpe5MQIWN6Qa
lryiET74gMHE/S5WrPlsq/gehxsdgc6GDUXG4dk8vn6OUMa6wb5wRO3VXGEc67IY
m4mDFTYiPvLaFOxtndlUWuCruKcCAwEAAaOBpzCBpDAMBgNVHRMEBTADAQH/MB0G
A1UdDgQWBBSDkIaYhLVZTwyLNTetNB2qV0gkVDBoBgNVHSMEYTBfgBSDkIaYhLVZ
TwyLNTetNB2qV0gkVKFEpEIwQDELMAkGA1UEBhMCQ0gxFTATBgNVBAoTDFByb3Rv
blZQTiBBRzEaMBgGA1UEAxMRUHJvdG9uVlBOIFJvb3QgQ0GCAQEwCwYDVR0PBAQD
AgEGMA0GCSqGSIb3DQEBDQUAA4ICAQCYr7LpvnfZXBCxVIVc2ea1fjxQ6vkTj0zM
htFs3qfeXpMRf+g1NAh4vv1UIwLsczilMt87SjpJ25pZPyS3O+/VlI9ceZMvtGXd
MGfXhTDp//zRoL1cbzSHee9tQlmEm1tKFxB0wfWd/inGRjZxpJCTQh8oc7CTziHZ
ufS+Jkfpc4Rasr31fl7mHhJahF1j/ka/OOWmFbiHBNjzmNWPQInJm+0ygFqij5qs
51OEvubR8yh5Mdq4TNuWhFuTxpqoJ87VKaSOx/Aefca44Etwcj4gHb7LThidw/ky
zysZiWjyrbfX/31RX7QanKiMk2RDtgZaWi/lMfsl5O+6E2lJ1vo4xv9pW8225B5X
eAeXHCfjV/vrrCFqeCprNF6a3Tn/LX6VNy3jbeC+167QagBOaoDA01XPOx7Odhsb
Gd7cJ5VkgyycZgLnT9zrChgwjx59JQosFEG1DsaAgHfpEl/N3YPJh68N7fwN41Cj
zsk39v6iZdfuet/sP7oiP5/gLmA/CIPNhdIYxaojbLjFPkftVjVPn49RqwqzJJPR
N8BOyb94yhQ7KO4F3IcLT/y/dsWitY0ZH4lCnAVV/v2YjWAWS3OWyC8BFx/Jmc3W
DK/yPwECUcPgHIeXiRjHnJt0Zcm23O2Q3RphpU+1SO3XixsXpOVOYP6rJIXW9bMZ
A1gTTlpi7A==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Windscribe VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Windscribe server

  1. Copy and paste the server IP Address from the server list above into the Server IP/Name field.
  2. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

IPVanish Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual IPVanish Setup

Verify your IPVanish login information

If you are not already an IPVanish user Sign Up Now.

Log in to your account on the IPVanish website.

IPVanish Server Addresses

View a full list of IPVanish servers.

America

Ashburn:
iad-a01.ipvanish.com
through
iad-a78.ipvanish.com

Atlanta:
atl-a01.ipvanish.com
through
atl-a88.ipvanish.com

Boston:
bos-c01.ipvanish.com
through
bos-c27.ipvanish.com

Chicago:
chi-a01.ipvanish.com
through
chi-a58.ivpanish.com

Cleveland:
cle-c01.ipvanish.com
through
cle-c20.ipvanish.com

Dallas:
dal-a01.ipvanish.com
through
dal-a79.ipvanish.com

Denver:
den-c01.ipvanish.com
through
den-c13.ipvanish.com

Jackson:
jan-c01.ipvanish.com
through
jan-c15.ipvanish.com

Las Vegas:
las-c11.ipvanish.com
through
las-c20.ipvanish.com

Los Angeles:
lax-a01.ipvanish.com
through
lax-a60.ipvanish.com

Miami:
mia-a01.ipvanish.com
through
mia-a34.ipvanish.com

Milwaukee:
mke-c01.ipvanish.com
through
mke-c19.ipvanish.com

New York:
nyc-a01.ipvanish.com
through
nyc-a51.ipvanish.com

Phoenix:
phx-a01.ipvanish.com
through
phx-a24.ipvanish.com

Salt Lake City:
slc-c01.ipvanish.com
through
slc-c12.ipvanish.com

San Jose:
sjc-a01.ipvanish.com
through
sjc-a27.ipvanish.com

Seattle:
sea-a01-ipvanish.com
through
sea-a41.ipvanish.com

St. Louis:
stl-c01.ipvanish.com
through
stl-c18.ipvanish.com

United Kingdom

London:
lon-a01.ipvanish.com
through
lon-a69.ipvanish.com

lon-c01.ipvanish.com
through
lon-c58.ipvanish.com

Manchester:
man-c01.ipvanish.com
through
man-c09.ipvanish.com

DD-WRT Router Setup for IPVanish

Navigate to Services > VPN

Enter IPVanish settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change IPVanish connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your IPVanish account with.

Password

Enter the Password you successfully logged in to your IPVanish account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun
persist-remote-ip
keysize 256

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIErTCCA5WgAwIBAgIJAMYKzSS8uPKDMA0GCSqGSIb3DQEBDQUAMIGVMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCRkwxFDASBgNVBAcTC1dpbnRlciBQYXJrMREwDwYD
VQQKEwhJUFZhbmlzaDEVMBMGA1UECxMMSVBWYW5pc2ggVlBOMRQwEgYDVQQDEwtJ
UFZhbmlzaCBDQTEjMCEGCSqGSIb3DQEJARYUc3VwcG9ydEBpcHZhbmlzaC5jb20w
HhcNMTIwMTExMTkzMjIwWhcNMjgxMTAyMTkzMjIwWjCBlTELMAkGA1UEBhMCVVMx
CzAJBgNVBAgTAkZMMRQwEgYDVQQHEwtXaW50ZXIgUGFyazERMA8GA1UEChMISVBW
YW5pc2gxFTATBgNVBAsTDElQVmFuaXNoIFZQTjEUMBIGA1UEAxMLSVBWYW5pc2gg
Q0ExIzAhBgkqhkiG9w0BCQEWFHN1cHBvcnRAaXB2YW5pc2guY29tMIIBIjANBgkq
hkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAt9DBWNr/IKOuY3TmDP5x7vYZR0DGxLbX
U8TyAzBbjUtFFMbhxlHiXVQrZHmgzih94x7BgXM7tWpmMKYVb+gNaqMdWE680Qm3
nOwmhy/dulXDkEHAwD05i/iTx4ZaUdtV2vsKBxRg1vdC4AEiwD7bqV4HOi13xcG9
71aQ55Mj1KeCdA0aNvpat1LWx2jjWxsfI8s2Lv5Fkoi1HO1+vTnnaEsJZrBgAkLX
pItqP29Lik3/OBIvkBIxlKrhiVPixE5qNiD+eSPirsmROvsyIonoJtuY4Dw5K6pc
NlKyYiwo1IOFYU3YxffwFJk+bSW4WVBhsdf5dGxq/uOHmuz5gdwxCwIDAQABo4H9
MIH6MAwGA1UdEwQFMAMBAf8wHQYDVR0OBBYEFEv9FCWJHefBcIPX9p8RHCVOGe6u
MIHKBgNVHSMEgcIwgb+AFEv9FCWJHefBcIPX9p8RHCVOGe6uoYGbpIGYMIGVMQsw
CQYDVQQGEwJVUzELMAkGA1UECBMCRkwxFDASBgNVBAcTC1dpbnRlciBQYXJrMREw
DwYDVQQKEwhJUFZhbmlzaDEVMBMGA1UECxMMSVBWYW5pc2ggVlBOMRQwEgYDVQQD
EwtJUFZhbmlzaCBDQTEjMCEGCSqGSIb3DQEJARYUc3VwcG9ydEBpcHZhbmlzaC5j
b22CCQDGCs0kvLjygzANBgkqhkiG9w0BAQ0FAAOCAQEAI2dkh/43ksV2fdYpVGhY
aFZPVqCJoToCez0IvOmLeLGzow+EOSrY508oyjYeNP4VJEjApqo0NrMbKl8g/8bp
LBcotOCF1c1HZ+y9v7648uumh01SMjsbBeHOuQcLb+7gX6c0pEmxWv8qj5JiW3/1
L1bktnjW5Yp5oFkFSMXjOnIoYKHyKLjN2jtwH6XowUNYpg4qVtKU0CXPdOznWcd9
/zSfa393HwJPeeVLbKYaFMC4IEbIUmKYtWyoJ9pJ58smU3pWsHZUg9Zc0LZZNjkN
lBdQSLmUHAJ33Bd7pJS0JQeiWviC+4UTmzEWRKa7pDGnYRYNu2cUo0/voStphv8E
VA==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful IPVanish connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit IPVanish’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to IPVanish.

Back up your settings

Navigate to Administration > Backup.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the IPVanish server

  1. Copy the new IPVanish server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 8, 2019 ·

Preparing for Manual NordVPN Setup

Verify your NordVPN login information

If you are not already an NordVPN user Sign Up Now.

Log in to your account on the NordVPN website.

NordVPN Server Addresses

For a NordVPN server recommendation visit their Recommend Server page.

Once you have selected the server you want to connect to, download the UDP .ovpn file containing the Server IP Address, TLS Auth Key, and CA Cert referenced below.

Open the .ovpn file that is downloaded to your computer with NotePad++ for Windows or TextEdit for Apple. You will only need the Server IP Address, TLS Auth Key, and CA Cert from this file. All NordVPN servers and .ovpn files have different IP Addresses, keys, and certificates.

DD-WRT Router Setup for NordVPN

Navigate to Services > VPN

Enter NordVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote 206.226.72.27 1194
206.226.72.27 is your NordVPN server IP address. Enter the IP Address in this field.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your NordVPN account with.

Password

Enter the Password you successfully logged in to your NordVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

In the .ovpn file copy and paste all contents in between the <tls-auth> and </tls-auth> lines from your .ovpn file starting and ending with:
—–BEGIN OpenVPN Static key V1—–
…
—–END OpenVPN Static key V1—–

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

In the .ovpn file Copy and Paste all contents in between the <ca> and </ca> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful NordVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit NordVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the NordVPN server

  1. Download and open a new .ovpn file from NordVPN.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the TLS Auth Key into the TLS Auth Key field.
  4. Copy and paste the CA Cert into the CA Cert field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Private Internet Access (PIA) Setup for Privacy Hero

TeamFlashRouters · Apr 3, 2023 ·

Privacy Hero supports Private Internet Access (PIA) with WireGuard (recommended) and OpenVPN. You need an active PIA subscription and your PIA VPN username and password.

Important difference: PIA WireGuard has a built-in provider integration in Privacy Hero. Choose Private Internet Access from the VPN provider list—not Custom WireGuard. No WireGuard configuration file or key generation is needed.

By default, Privacy Hero can automatically select an optimal available PIA server based on your location and server conditions. Alternatively, use Advanced Options to enter a specific PIA server hostname from the regional list below.

Privacy Hero is cloud-managed. You can configure your router from any device with an internet connection, whether or not you are on the Privacy Hero WiFi network.

PIA VPN Setup Guide

Choose your setup method or jump to a particular step.

PIA WireGuard →Use the built-in Privacy Hero PIA providerAutomatic or Manual Server →Select an optimal server or enter a hostnamePIA Server Hostnames →Browse the full list organized by regionOpenVPN Setup →Generate and upload an OpenVPN configurationVerify Connection →Confirm your device is using the PIA VPNTroubleshooting →Connection errors, wrong region, no internet

Set Up PIA WireGuard in Privacy Hero (Recommended)

Unlike most other providers, PIA WireGuard does not use Custom VPN file uploads in Privacy Hero. The built-in PIA integration connects using your PIA account credentials and handles the WireGuard configuration for you.

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section. Select Change beside your current VPN provider.
  3. Choose Private Internet Access from the provider list. Do not select Custom for this WireGuard setup.
  4. Enter your PIA VPN account username and password (not your Privacy Hero dashboard credentials). You can check your account at PIA Client Control Panel.
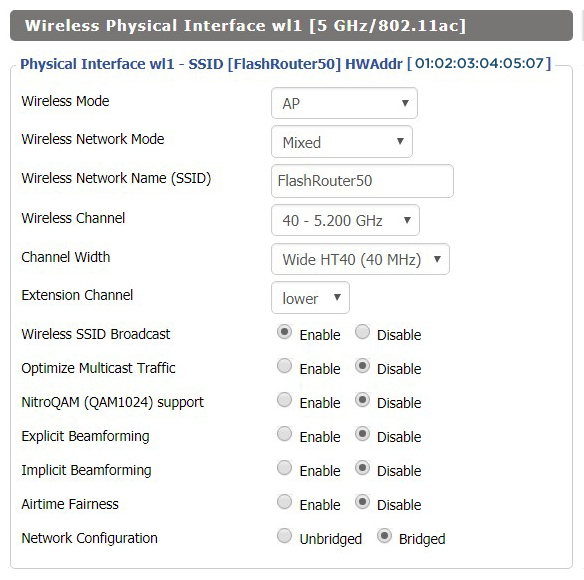
  5. For automatic server selection, leave the optional server hostname unset, then click Save to connect. Wait until Privacy Hero displays Connected.
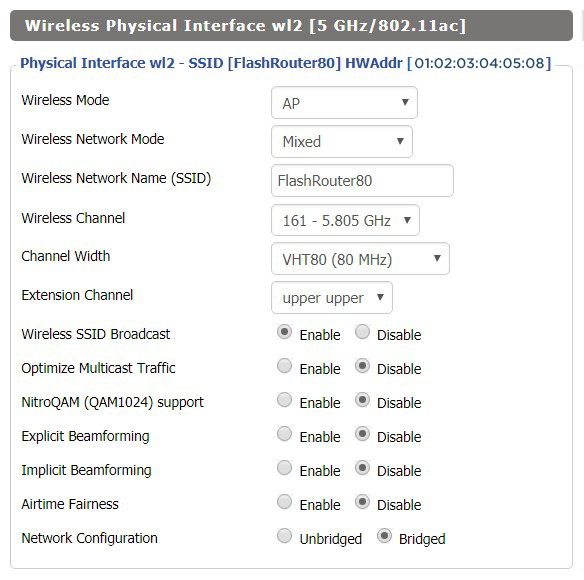
Privacy Hero built-in Private Internet Access provider login settings

Choose the Automatic Server or a Specific PIA Location

Privacy Hero offers two ways to select the PIA WireGuard server:

  • Automatic (recommended for most users): Leave the server hostname field blank. Privacy Hero selects an optimal available PIA location, generally favoring nearby servers and server conditions such as load. You do not need to manually maintain a server address.
  • Specific location: Enter a PIA region hostname under Advanced Options. This is useful when you need an IP address from a particular country or city.
  1. To use a specific location, open the existing Private Internet Access connection and select Advanced Options.
  2. Enter a complete PIA server hostname from the list below, for example us-newyorkcity.privacy.network or uk-london.privacy.network.
  3. Click Save, wait for Connected, then verify your new public IP address. If the selected location becomes unavailable, try another hostname or remove the hostname to return to automatic selection.
Privacy Hero Private Internet Access Advanced Options field for entering a VPN server hostname

PIA Server Hostname List by Region

Use these hostnames in PIA > Advanced Options when you prefer a specific location. Expand a region below and copy the complete hostname, including .privacy.network. This list is retained from the existing FlashRouters guide.

Server availability can change. Some hostnames, particularly those ending in -pf or marked for streaming, are specialized locations and may not be available for every connection. If a hostname no longer works, use automatic selection or check PIA’s current location list for available locations. PIA’s location list names regions; it does not necessarily provide matching hostnames.

North America (65 locations)
bahamas.privacy.networkca-ontario.privacy.networkca-toronto.privacy.networkca-vancouver.privacy.networkca-montreal.privacy.networkgreenland.privacy.networkgt-guatemala-pf.privacy.networkmexico.privacy.networkpanama.privacy.networksanjose.privacy.networkus-alabama-pf.privacy.networkus-alaska-pf.privacy.networkus-arkansas-pf.privacy.networkus-atlanta.privacy.networkus-california.privacy.networkus-chicago.privacy.networkus-connecticut-pf.privacy.networkus-denver.privacy.networkus-florida.privacy.networkus-houston.privacy.networkus-idaho-pf.privacy.networkus-indiana-pf.privacy.networkus-iowa-pf.privacy.networkus-kansas-pf.privacy.networkus-kentucky-pf.privacy.networkus-lasvegas.privacy.networkus-louisiana-pf.privacy.networkus-maine-pf.privacy.networkus-massachusetts-pf.privacy.networkus-michigan-pf.privacy.networkus-minnesota-pf.privacy.networkus-mississippi-pf.privacy.networkus-missouri-pf.privacy.networkus-montana-pf.privacy.networkus-nebraska-pf.privacy.networkus-new-hampshire-pf.privacy.networkus-new-mexico-pf.privacy.networkus-newyorkcity.privacy.networkus-north-carolina-pf.privacy.networkus-north-dakota-pf.privacy.networkus-ohio-pf.privacy.networkus-oklahoma-pf.privacy.networkus-oregon-pf.privacy.networkus-pennsylvania-pf.privacy.networkus-rhode-island-pf.privacy.networkus-seattle.privacy.networkus-siliconvalley.privacy.networkus-south-carolina-pf.privacy.networkus-south-dakota-pf.privacy.networkus-texas.privacy.networkus-tennessee-pf.privacy.networkus-vermont-pf.privacy.networkus-virginia-pf.privacy.networkus-washingtondc.privacy.networkus-west-virginia-pf.privacy.networkus-wisconsin-pf.privacy.networkus-wyoming-pf.privacy.networkus3.privacy.networkus-baltimore.privacy.networkus-honolulu.privacy.networkus-newjersey.privacy.networkus-saltlakecity.privacy.networkus-streaming-2.privacy.networkus-streaming.privacy.networkus-wilmington.privacy.network
South America (9 locations)
ar.privacy.networkbo-bolivia-pf.privacy.networkbogota.privacy.networkbr.privacy.networkec-ecuador-pf.privacy.networkpe-peru-pf.privacy.networksantiago.privacy.networkuy-uruguay-pf.privacy.networkvenezuela.privacy.network
Europe (51 locations)
al.privacy.networkad.privacy.networkaustria.privacy.networkbrussels.privacy.networkba.privacy.networksofia.privacy.networkzagreb.privacy.networkczech.privacy.networkde-berlin.privacy.networkde-frankfurt.privacy.networkdenmark.privacy.networkdenmark-2.privacy.networkspain.privacy.networkes-valencia.privacy.networkee.privacy.networkfi.privacy.networkfi-2.privacy.networkfrance.privacy.networkgr.privacy.networkhungary.privacy.networkitaly.privacy.networkitaly-2.privacy.networkis.privacy.networkireland.privacy.networkman.privacy.networklv.privacy.networkliechtenstein.privacy.networklt.privacy.networklu.privacy.networkmalta.privacy.networkmd.privacy.networkmonaco.privacy.networkmontenegro.privacy.networknl-amsterdam.privacy.networkmk.privacy.networkno.privacy.networkpoland.privacy.networkpt.privacy.networkro.privacy.networksweden.privacy.networksweden-2.privacy.networkrs.privacy.networksk.privacy.networkslovenia.privacy.networkswiss.privacy.networktr.privacy.networkuk-london.privacy.networkuk-manchester.privacy.networkuk-southampton.privacy.networkuk-2.privacy.networkua.privacy.network
Asia (26 locations)
ae.privacy.networkbangladesh.privacy.networkcambodia.privacy.networkchina.privacy.networkcyprus.privacy.networkgeorgia.privacy.networkhk.privacy.networkin.privacy.networkisrael.privacy.networkjakarta.privacy.networkjapan.privacy.networkjapan-2.privacy.networkkazakhstan.privacy.networkkr-south-korea-pf.privacy.networkkualalumpur.privacy.networkmacau.privacy.networkmongolia.privacy.networknp-nepal-pf.privacy.networkphilippines.privacy.networkqatar.privacy.networksaudiarabia.privacy.networksg.privacy.networksrilanka.privacy.networktaiwan.privacy.networkvietnam.privacy.networkyerevan.privacy.network
Oceania (7 locations)
au-adelaide-pf.privacy.networkau-australia-so.privacy.networkau-brisbane-pf.privacy.networkaus-melbourne.privacy.networkaus-perth.privacy.networkau-sydney.privacy.networknz.privacy.network
Africa (5 locations)
dz.privacy.networkegypt.privacy.networkmorocco.privacy.networknigeria.privacy.networkza.privacy.network

Set Up PIA OpenVPN in Privacy Hero

OpenVPN is the alternative when you need a manually uploaded connection or if the built-in PIA WireGuard method does not work on your network. OpenVPN uses Custom in Privacy Hero, unlike the built-in PIA WireGuard setup.

Download a PIA OpenVPN Configuration File

  1. Sign in to the PIA Client Control Panel using your PIA VPN account.
  2. Open Downloads and scroll to OpenVPN Configuration Generator or OpenVPN Configurations.
  3. If using the generator, choose OpenVPN 2.4 or newer and Linux when these options are offered, then choose an available server location.
  4. Select your preferred configuration. UDP / 1198 (AES-128-CBC) is a standard default. UDP / 1197 (AES-256-CBC) is an alternative. Use a PIA-provided TCP configuration if UDP does not work on your network.
  5. Click Generate or download a suitable pre-made configuration and save the resulting .ovpn file. Each server file is tied to its selected location/settings.

PIA also provides pre-made OpenVPN configuration bundles; see PIA’s OpenVPN file instructions.

Add PIA OpenVPN as a Custom VPN

  1. Open Privacy Hero, go to VPN, click Change, and select Custom.
  2. Choose OpenVPN and upload the PIA .ovpn file downloaded in the previous section.
  3. Enter your PIA VPN username and password in the Custom OpenVPN authentication fields.
  4. Click Save and confirm Privacy Hero shows Connected.
Privacy Hero Custom OpenVPN configuration with file upload and username password fields

Note: If OpenVPN UDP cannot connect, try a TCP profile from PIA or another server. When switching protocols, make sure you upload a matching PIA configuration file.


Verify Your Private Internet Access Connection

  1. Connect a device to the Privacy Hero WiFi or LAN network.
  2. Disconnect any PIA app or other VPN running directly on the device so the router VPN can be tested independently.
  3. Open a private/incognito browser window and visit PIA What Is My IP.
  4. Confirm that your public IP address reflects the VPN connection, and that the approximate location is consistent with either the selected hostname or Privacy Hero’s automatic server selection.

Privacy Hero VPN settings can be changed remotely, but the device used to verify the VPN IP must be connected to the Privacy Hero network.

Streaming Relocation and Your PIA Location

If Streaming Relocation is enabled for a supported service, that service may use the Streaming Relocation location instead of your PIA VPN server location. See Privacy Hero Streaming Relocation.


PIA VPN Not Connecting?

If Privacy Hero reports Failed, stays on Connecting, or connected devices lose internet access, try these checks:

  1. Confirm your PIA subscription is active and enter your PIA VPN login, not your Privacy Hero email/password.
  2. For built-in PIA WireGuard, verify the provider is Private Internet Access—not Custom. No downloaded WireGuard file is required.
  3. Remove any specific server hostname to test automatic server selection. If that connects, the previous hostname may be unavailable.
  4. For Custom OpenVPN, upload a fresh PIA .ovpn file, re-enter the PIA credentials, and try a different server or a TCP configuration.
  5. Turn off the router VPN temporarily to check that normal internet access works. If the VPN Kill Switch is blocking internet traffic, temporarily disable it for testing, then restore your preferred setting.
  6. Check whether a separate VPN app, iCloud Private Relay, Private DNS, proxy, or security software on the testing device is affecting your VPN IP results.

No Internet When the VPN Disconnects?

The Privacy Hero VPN Kill Switch may intentionally block internet access if the VPN goes down. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

If other devices show the expected VPN address, review device VPN apps, iCloud Private Relay, Private DNS, and security settings.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

Asus RT-AC5300 DD-WRT WiFi Settings

Dave · Mar 4, 2019 ·

Recommended DD-WRT WiFi settings for the Asus RT-AC5300 are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Asus RT-AC5300 with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

2.4 GHz - Wireless-N

View AC5300 DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC #1

View AC5300 DD-WRT FlashRouter 5GHz #1 Settings

5.0 GHz - Wireless-AC #2

View AC5300 DD-WRT FlashRouter 5GHz #2 Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

RT-AC5300 DD-WRT Wireless Security

The preset Asus RT-AC5300 FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

View RT-AC5300 DD-WRT FlashRouter WiFi Seucirty Settings

TROUBLESHOOTING

Trouble with your Asus RT-AC5300 WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Netgear R9000 Nighthawk X10 DD-WRT WiFi Settings

Dave · Mar 5, 2019 ·

Recommended DD-WRT WiFi settings for the Netgear R9000 are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Netgear R9000 with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

5.0 GHz - Wireless-AC

View R9000 DD-WRT FlashRouter 5GHz Settings

2.4 GHz - Wireless-N

View R9000 DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AD

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

R9000 DD-WRT Wireless Security

The preset R9000 FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

TROUBLESHOOTING

Trouble with your Netgear R9000 WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Netgear R8500 Nighthawk X8 DD-WRT WiFi Settings

Dave · Mar 5, 2019 ·

Recommended DD-WRT WiFi settings for the Netgear R8500 are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Netgear R8500 with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

5.0 GHz - Wireless-AC #1

View R8500 DD-WRT FlashRouter 5GHz #1 Settings

2.4 GHz - Wireless-N

View R8500 DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC #2

View R8500 DD-WRT FlashRouter 5GHz #2 Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

R8500 DD-WRT Wireless Security

The preset Netgear R8500 FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

TROUBLESHOOTING

Trouble with your Netgear R8500 WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

ASUS Guest WiFi With or Without VPN: Setup Guide

Dave · Oct 26, 2026 ·

On supported ASUS routers, you can create a separate WiFi network (SSID) that routes connected devices through a VPN profile, while another network uses the regular ISP connection. This is useful for streaming TVs, guests, work devices, and family members who need different VPN behavior.

The available controls depend on your ASUS model and firmware. Newer routers may call the feature Guest Network Pro or simply Network; older routers may only have Guest Network, which does not offer the same VPN-by-SSID options.

In This Guide

Check Your ASUS Model →Guest Network Pro vs. legacyCreate a VPN WiFi →SSID associated with VPNCreate an ISP WiFi →Network without VPNTest Both Networks →Verify VPN and ISP IPsCommon Mistakes →Default routes, DNS and firmwareRelated Guides →VPN setup and device routing

What You Need Before Starting

  1. Connect to your ASUS router and open http://www.asusrouter.com or its LAN IP. For login details, see AsusWRT Router Access Guide.
  2. For a VPN WiFi network, first set up and verify at least one connected VPN profile under VPN > VPN Fusion. Choose a supported VPN provider from the AsusWRT VPN Setup Guides, then review How to Use ASUS VPN Fusion: Assign Devices and Multiple VPNs for routing options.
  3. Look for Guest Network Pro, Network, or VPN Network in your ASUS firmware. If you only see the traditional Guest Network screen, read the legacy note below before proceeding.

Firmware compatibility: ASUS documents VPN Network functionality on eligible models with firmware 3.0.0.6.102_34312 or later, with the Guest Network Pro section renamed Network from 3.0.0.6.102_35404. Not all models, regions, or firmware builds offer the same features.

Create a Dedicated WiFi Network That Uses the VPN

Preferred route for supported ASUS models: create a VPN Network SSID so all devices joining that SSID use the chosen VPN without individual device assignments.

  1. Open Guest Network Pro > VPN Network, or the equivalent Network > Add Network > VPN Network menu in newer firmware.
  2. Choose a recognizable WiFi name such as Home-VPN and a strong WiFi password.
  3. Select the configured, connected VPN Fusion client/profile and enable VPN routing for that network.
  4. Review any options for local-network access, guest isolation, and bands, then click Apply.
  5. Connect a test device to the new Home-VPN WiFi SSID and check its public IP.

ASUS official walkthrough: Guest Network Pro / VPN Network Setup.

Alternative: Assign a VPN to an Existing Guest Network Pro SSID

  1. In Guest Network Pro / Network, open the existing Guest Network profile.
  2. Select the VPN tab, enable VPN routing, and choose your existing VPN Fusion client.
  3. Click Apply, reconnect a device to the guest SSID, and verify the VPN IP.

ASUS also documents this path: Assign a VPN to Guest Network Pro.

Create a Separate WiFi Network Without a VPN

Use a guest/secondary network routed through the regular ISP internet connection for devices that should not use the VPN.

  1. Under Guest Network Pro / Network, add a normal Guest Network or other suitable network profile (not the VPN Network preset).
  2. Set a clear name such as Home-ISP and secure it with a strong password.
  3. In that network profile’s VPN tab, leave the VPN assignment disabled or choose the Internet/ISP path if your firmware offers it.
  4. Check your VPN Fusion default connection and device policies. If a VPN is set to Apply to all devices, simply turning off the Guest Network’s VPN toggle may not guarantee an ISP bypass on every firmware. Configure an explicit ISP/bypass route where supported.
  5. Save, join the Home-ISP network with a test device, and confirm the public IP matches the ISP connection.

Always test the actual public IP. Different ASUS firmwares apply VPN Fusion defaults and network-profile overrides differently. A WiFi name that says “ISP” or “No VPN” does not itself enforce a VPN bypass.

Confirm Each WiFi Network Uses the Intended Internet Route

  1. Connect a phone or laptop to the VPN WiFi SSID. Disable any VPN app or iCloud Private Relay on the device for this test.
  2. Visit WhatIsMyIPAddress.com and note the public IP and location. This should reflect your selected VPN endpoint.
  3. Disconnect and join the ISP WiFi SSID. Repeat the IP check; it should now show the ISP’s public internet route.
  4. If both SSIDs show the same IP, review the VPN Fusion default profile, guest-network VPN assignment, and any device-specific rules.

Common Issues and What to Check

I only see “Guest Network,” not “Guest Network Pro” or “VPN Network”

Your router may use older firmware or lack this feature. Traditional Guest Network creates a separate WiFi SSID, but the VPN routing option may not exist. Use VPN Fusion device assignments as an alternative rather than assuming the guest network automatically bypasses or uses the VPN.

Every network still uses the VPN

Check whether Apply to all devices is enabled in VPN Fusion. If it is, verify that the guest profile actually overrides the default route on your firmware. You may need an explicit per-network or per-device ISP rule.

A phone reports the wrong IP although the guest VPN profile is correct

Temporarily disable device-level VPN apps, iCloud Private Relay / Limit IP Address Tracking, browser proxy, or Private DNS settings, then reconnect. See Device Settings That Interfere With Router VPN.

Guest devices cannot reach local printers or other LAN devices

Check the guest network’s intranet access / network isolation settings. Changing isolation affects LAN access, not necessarily VPN selection. Keep guests isolated unless LAN access is actually needed.

Related AsusWRT Guides

  • AsusWRT VPN Setup Guides
  • How to Use ASUS VPN Fusion: Assign Devices and Multiple VPNs
  • Device Settings That Interfere With Router VPN
  • ASUS Guest Network Pro Instructions (official)

Upgrade your ASUS router

Explore the Latest WiFi 7 ASUS FlashRouters

Looking for a newer ASUS router? Browse WiFi 7 models available from FlashRouters and compare features to find the right fit for your home or office. VPN Fusion and other features vary by router model and firmware.

Shop ASUS WiFi 7 Routers →

Asus RT-AC68U B1 / C1 / AC1900 DD-WRT WiFi Settings

Dave · Feb 25, 2019 ·

Recommended DD-WRT WiFi settings for the Asus RT-AC68U are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Asus RT-AC68U with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

2.4 GHz - Wireless-N

View AC68U DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC

View AC68U DD-WRT FlashRouter 5GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

RT-AC68U DD-WRT Wireless Security

The preset RT-AC68U FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

View AC68U DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Asus RT-AC68U WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Asus RT-AC66U DD-WRT WiFi Settings

Dave · Feb 25, 2019 ·

Recommended DD-WRT WiFi settings for the Asus RT-AC66U are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Asus RT-AC66U with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

2.4 GHz - Wireless-N

View AC66U DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC

View AC66U DD-WRT FlashRouter 5GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

RT-AC66U DD-WRT Wireless Security

The preset RT-AC66U FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

View AC66U DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Asus RT-AC66U WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Asus RT-AC56U DD-WRT WiFi Settings

Dave · Mar 5, 2019 ·

Recommended DD-WRT WiFi settings for the Asus RT-AC56U are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Asus RT-AC56U with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

2.4 GHz - Wireless-N

View AC56U DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC

View AC56U DD-WRT FlashRouter 5GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

RT-AC56U DD-WRT Wireless Security

The preset RT-AC56U FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

ViewAC56U DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Asus RT-AC56U WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Linksys WRT1200AC DD-WRT WiFi Settings

Dave · Mar 4, 2019 ·

Recommended DD-WRT WiFi settings for the Linksys WRT1200AC are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Linksys WRT1200AC with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

5.0 GHz - Wireless-AC

View WRT1200AC DD-WRT FlashRouter 5GHz Settings

2.4 GHz - Wireless-N

View WRT1900AC DD-WRT FlashRouter 2.4GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

WRT1200AC DD-WRT Wireless Security

The preset WRT1200AC FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

View WRT1200AC DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Linksys WRT1200AC WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Netgear R6400V2 DD-WRT WiFi Settings

Dave · Feb 21, 2019 ·

Recommended DD-WRT WiFi settings for the Linksys R6400V2 are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

Screenshots below provide a visual display of WiFi settings exactly as they appear in the Linksys R6400V2 with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

2.4 GHz - Wireless-N

View R6400 DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC

View R6400 DD-WRT FlashRouter 5GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

R6400V2 DD-WRT Wireless Security

The preset WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

View R6400 DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Netgear R6400 V2 WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

CyberGhost Manual OpenVPN Setup

TeamFlashRouters · Apr 9, 2019 ·

Preparing for Manual CyberGhost Setup

Obtain your CyberGhost OpenVPN Information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

2. Select My Devices.

3. Select Other and then Configure New Device.

CyberGhost Website OpenVPN Configuration Files Generator Cyberghost - Website Screen CyberGhost Website OpenVPN Configuration Files Generator

4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 3

5. Press View configuration.

CyberGhost Website OpenVPN Configuration Files Generator 2

6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the ca.crt, client.crt, and client.key files. All CyberGhost servers have different keys and certificates.

DD-WRT Router Setup for CyberGhost

Navigate to Services > VPN

Enter CyberGhost settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you selected in your account. Be sure there are no extra spaces or characters.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your CyberGhost account.

Password

Enter the Password you obtained in your CyberGhost account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

tun-mtu 1500
fragment 1300
mssfix 1300

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
—–END CERTIFICATE—–

Public Client Cert

Copy and paste all contents of the client.crt file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and paste all contents of the client.key file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful CyberGhost connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit CyberGhost’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to CyberGhost.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the CyberGhost server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new ca.crt, client.crt, and client.key
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here
Next Page »

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer