• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: name server fai

Wireless Guest Network Setup – Bridged (Advanced)

TeamFlashRouters · Jun 12, 2019 ·

If you would like to prevent visitors from connecting to your main WiFi network then you can create a Bridged Guest Network that will prevent access to the main router. This setup also allows you to create different rules for different WiFi SSID’s in your home ranging from QoS controls, access restrictions, VPN network segmentation, and more.

Preparing for Wireless Guest Network Setup

If you have a Dual-band or Tri-Band router you can setup a WiFi Guest Network, creating a separate VLAN (virtual local area network) for your visitors, or in order to segment your VPN networks on any band you like. We recommend using the 2.4GHz network for your DD-WRT Guest Wireless Network so it is compatible with the most possible WiFi devices. Setting up a guest network for visitors in your home allows you to keep them off of your main WiFi network.

We recommend performing this setup while connected to the FlashRouter via ethernet cable. If your computer does not have an ethernet port and you must proceed via wireless connection to the FlashRouter pay attention to the wireless connection as you may need to rejoin the FlashRouter’s network after making changes.

DD-WRT Router Setup for Wireless Guest Network

Enter Wireless settings

Navigate to Wireless > Basic Settings
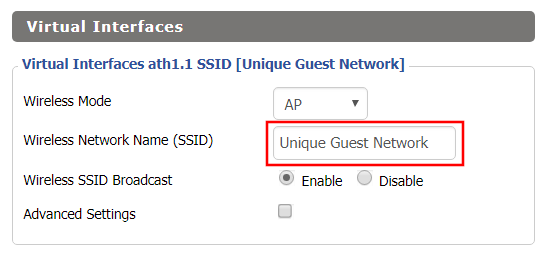
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Setting SSID for Guest Network
  1. Under the 2.4GHz or 5GHz Interface click the Add button.
  2. In the Wireless Network Name (SSID) field enter the unique network name of the guest network.
  3. Click Save.

Enter Wireless Security settings

Navigate to Wireless > Wireless Security
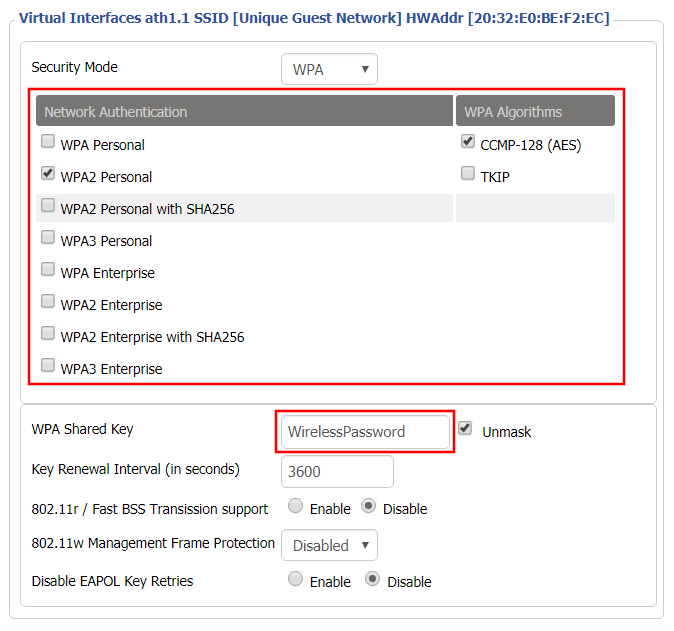
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Setting Guest Network Wireless Password
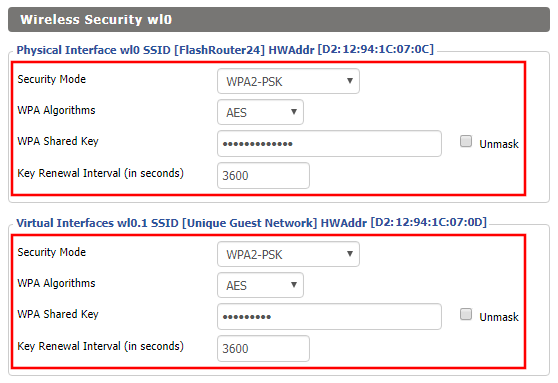
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Click Apply Settings.
  3. Reboot your router.

Create Bridge

Navigate to Setup > Networking
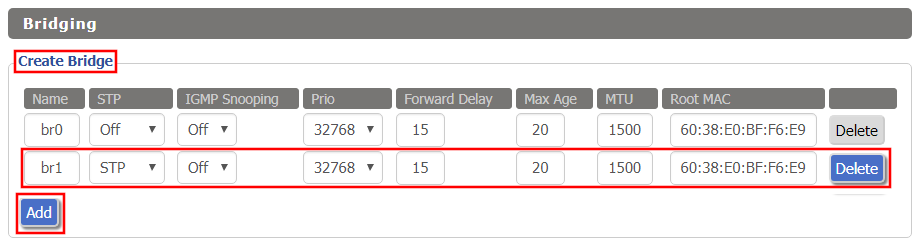
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Create Bridge
  1. Under Create Bridge click Add. Name the newly created bridge br1.
  2. Click Apply Settings

Assign to Bridge

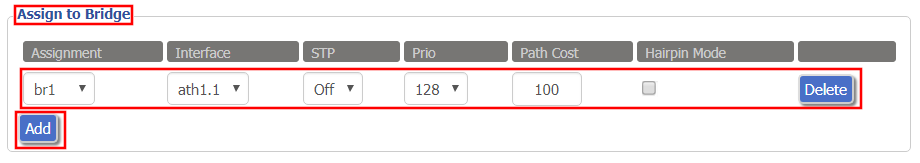
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Assign Bridge
  1. Under Assign to Bridge select br1 from the Assignment dropdown. Select wl1.1 or ath1.1 depending on your router model.
  2. Click Apply Settings.

Depending on the router model and WiFi band you are using, the wireless interfaces will be labelled differently.

This setting can be labelled wl1.1, ath0.1, wl2.1, and so on. Make sure when you get up to the bridge assignment section that you are using the correct guest network Virtual Interface.

Network Configuration br1
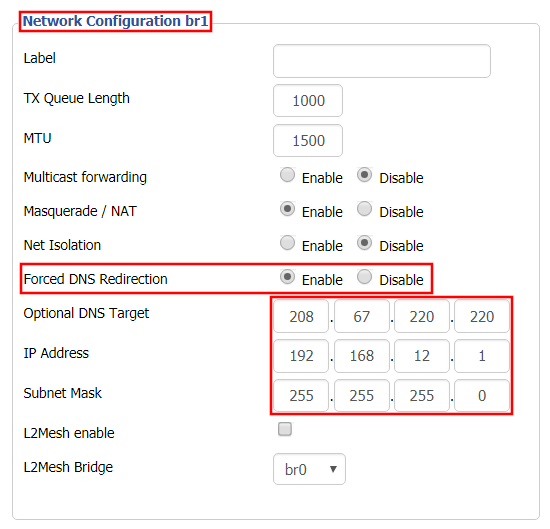
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Configure Bridge DNS Redirection
  1. Under Network Configuration br1 select Enable for Forced DNS Redirection.
  2. Set Optional DNS Target to 208.67.220.220
  3. Set IP Address to 192.168.12.1
  4. Set Subnet Mask to 255.255.255.0
  5. Click Apply Settings.

Multiple DHCP Server
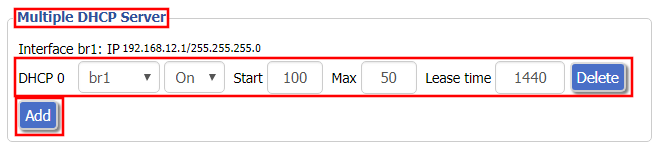
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Configure DHCP Server Settings
  1. Under Multiple DHCP Server click Add.
  2. Set the first dropdown to br1.
  3. Click Apply Settings.
  4. Reboot your router.

Firewall Rules

Navigate to Administration > Commands

  1. Copy the fire script from below and paste into the empty Commands shell
  2. Click Save Firewall.
  3. Wait one minute and then reboot your router.

iptables -I FORWARD -i br1 -o br0 -m state –state NEW -j DROP
iptables -I FORWARD -i br0 -o br1 -m state –state NEW -j DROP
iptables -I INPUT -i br1 -p tcp –dport telnet -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport ssh -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport www -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport https -j REJECT –reject-with tcp-reset

You will now have a working Bridged Guest Network on the FlashRouter. By inputting the firewall rules, this will also prevent any guests on your network from gaining access to your router settings.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Wireless Client Bridge Setup

TeamFlashRouters · Apr 22, 2019 ·

If you need to extend your wired connection capabilities and you are not able to wire directly into your main router, you can setup a FlashRouter as a Wireless Client Bridge. In Wireless Client Bridge mode the FlashRouter connects to your main router via WiFi, and then transmits your internet signal via the FlashRouter LAN ports for wired internet access anywhere in your home or office.

Preparing for Wireless Client Bridge Setup

Verify your wireless information

In order to setup your FlashRouter as a Wireless Client Bridge, you will need the exact SSID and password of your existing wireless network. Make sure you have this information before proceeding.

We recommend using a 2.4GHz network to repeat as this network will have more range.

Locate the Local IP Address of the existing wireless network

Locate the Local IP Address of the existing router that the FlashRouter will be bridged to.

DD-WRT Router Setup for Wireless Client Bridge

Disable Firewall

Navigate to Security > Firewall

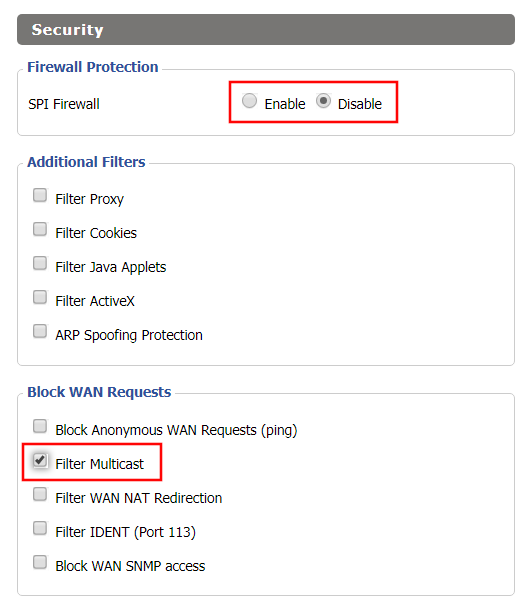
Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable Firewall and Enable Filter Multicast
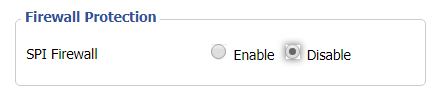
  1. Set SPI Firewall to Disable.
  2. Uncheck all boxes except for Filter Multicast.
  3. Click Save.

Disable DNSmasq

Navigate to Services > Services

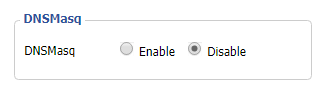
Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable DNSMasqButton
  1. Set DNSmasq to Disable.
  2. Click Save.

Enter Wireless settings

Navigate to Wireless > Basic Settings

Wireless Client Bridge Setup on FlashRouter DD-WRT - Set Wireless Mode to Client Bridge
  1. In the Wireless Physical Interface settings for the 2.4GHz network set the Wireless Mode to Client Bridge.
  2. Change the Wireless Network Name (SSID) to match exactly with the Wireless Network Name of the network that you will bridge to.
  3. Click Save.

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Wireless Client Bridge Setup on FlashRouter DD-WRT - Set Wireless Password
  1. Change the WPA Shared Key to match exactly with the Wireless Password of the network that you will bridge to.
  2. Click Save.

Change the FlashRouter's Local IP Address

Navigate to Setup > Basic Setup

  1. Set the Local IP Address to a different address on the same subnet as the existing network that you noted early. (example: if the existing network is 192.168.1.1 then set the Local IP Address to 192.168.1.2)
  2. Set the Gateway to the Local IP Address of the existing network. (example: 192.168.1.1)
  3. Set the Local DNS to the Local IP Address of the existing network. (example: 192.168.1.1)
  4. Click Apply Settings.

Reboot your FlashRouter

Power off the FlashRouter for 30 seconds and then power it back on. When it boots back up you will be able to access the FlashRouter’s settings at the new Local IP Address that you set. Your existing network and the FlashRouter’s network will now be bridged wirelessly.

Your FlashRouter is now providing wired connection access to your main router network. Wireless connections to the FlashRouter are disabled in this setup.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Wireless Guest Network Setup – Unbridged (Recommended)

TeamFlashRouters · Jun 12, 2019 ·

If you would like to prevent visitors from connecting to your main WiFi network then you can create a separate Guest Network that will prevent access to the main router. This setup also allows you to create different rules for different WiFi SSID’s in your home ranging from QoS controls, access restrictions, VPN network segmentation, and more.

Preparing for Wireless Guest Network Setup

If you have a Dual-band or Tri-Band router you can setup a WiFi Guest Network, creating a separate VLAN (virtual local area network) for your visitors, or in order to segment your VPN networks on any band you like. We recommend using the 2.4GHz network for your DD-WRT Guest Wireless Network so it is compatible with the most possible WiFi devices. Setting up a guest network for visitors in your home allows you to keep them off of your main WiFi network.

We recommend performing this setup while connected to the FlashRouter via ethernet cable. If your computer does not have an ethernet port and you must proceed via wireless connection to the FlashRouter. Be sure to pay attention to the wireless connection as you may need to rejoin the FlashRouter’s network after making changes.

DD-WRT Router Setup for Wireless Guest Network

Enter Wireless settings

Navigate to Wireless > Basic Settings

FlashRouter DD-WRT Wireless Guest Network Settings Unbridged

Under the 2.4GHz or 5GHz Interface click the Add button.

Wireless Network Name (SSID)

Enter the a unique network name for the guest network.

Network Configuration

Unbridged

Force DNS Redirection

Enable

Optional DNS Target

208.67.220.220

IP Address

192.168.12.1

Subnet Mask

255.255.255.0

CLICK SAVE

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Wireless Guest Network Setup on DD-WRT FlashRouter Unbridged
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Click Apply Settings.
  3. Reboot your router.

Enable DHCP for Guest Network

Navigate to Setup > Networking

Wireless Guest Network Setup on DD-WRT FlashRouter Unbridged Setting DHCP Server
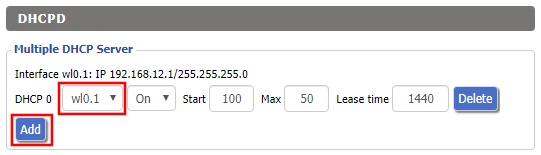
  1. Scroll to the very bottom of the page and under DHCPD click Add.
  2. Select wl0.1 or ath1.1 depending on your router model.
  3. Click Apply Settings.
  4. Reboot your router.

Depending on the router model and WiFi band you are using, the wireless interfaces will be labelled differently.

This setting can be labelled wl1.1, ath0.1, wl2.1, and so on. Make sure when you get up to the bridge assignment section that you are using the correct guest network Virtual Interface.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Wireless Access Point Setup

TeamFlashRouters · Apr 23, 2019 ·

A Wireless Access Point is a setup that has the FlashRouter using an existing network’s DHCP instead of assigning its own. The FlashRouter’s WAN/Internet port should be not be connected to your modem or other router while performing this setup.

Preparing for Wireless Access Point Setup

Locate the Local IP Address of the existing wireless network

Locate the Local IP Address of the existing router that the FlashRouter will be bridged to.

DD-WRT Router Setup for Wireless Access Point

Disable Firewall

Navigate to Security > Firewall

Wireless Client Bridge Setup on FlashRouter DD-WRT - Disable Firewall
  1. Set SPI Firewall to Disable.
  2. Click Save.

Disable DNSmasq

Navigate to Services > Services

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable DNSMasqButton
  1. Set DNSmasq to Disable.
  2. Click Save.

Change the FlashRouter's Local IP Address

Navigate to Setup > Basic Setup

Wireless Client Bridge Setup on FlashRouter DD-WRT - Set Local IP
  1. Set the Local IP Address to a different address on the same subnet as the existing network that you noted early. (example: if the existing network is 192.168.1.1 then set the Local IP Address to 192.168.1.2)
  2. Set the Gateway to the Local IP Address of the existing network. (example: 192.168.1.1)
  3. Set the Local DNS to the Local IP Address of the existing network. (example: 192.168.1.1)
  4. Click Save.

Change the FlashRouter's DHCP settings

DHCP Forwarder Setup for DD-WRT
  1. Set the DHCP Type to DHCP Forwarder.
  2. Click Save.

Change the FlashRouter's Operating Mode

Navigate to Setup > Advanced Routing

DHCP Forwarder Setup for DD-WRT
  1. Set the Operating Mode to Router.
  2. Click Apply Settings.

Reboot your FlashRouter

  • Power off the FlashRouter for 30 seconds and connect from the other router’s LAN port to one of the FlashRouter’s LAN port then power it back on.  When it boots back up you will be able to access the FlashRouter’s settings at the new Local IP Address that you set.

Back up your settings

Navigate to the Administration > Backup page.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Wireless Repeater Bridge Setup

TeamFlashRouters · Apr 22, 2019 ·

If you need to extend your connection capabilities and you are not able to wire directly into your main router, you can setup a FlashRouter as a Wireless Repeater Bridge. In Wireless Repeater Bridge mode the FlashRouter connects to your main router on the same subnet via WiFi, and then transmits your internet signal via the FlashRouter for internet access anywhere in your home or office.

Preparing for Wireless Repeater Bridge Setup

Verify your wireless information

In order to setup your FlashRouter as a Wireless Repeater Bridge, you will need the exact SSID and password of your existing wireless network. Make sure you have this information before proceeding.

We recommend using a 2.4GHz network to repeat as this network will have more range. Be sure to click Add under the 2.4GHz settings and not the 5GHz settings.

Locate the Local IP Address of the existing wireless network

Locate the Local IP Address of the existing router that the FlashRouter will be bridged to.

DD-WRT Router Setup for Wireless Repeater Bridge

Disable Firewall

Navigate to Security > Firewall

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable Firewall and Enable Filter Multicast
  1. Set SPI Firewall to Disable.
  2. Uncheck all boxes except for Filter Multicast.
  3. Click Save.

Disable DNSmasq

Navigate to Services > Services

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Disable DNSMasqButton
  1. Set DNSmasq to Disable.
  2. Click Save.

Enter Wireless settings

Navigate to Wireless > Basic Settings

Select Add in the Virtual Interface area.

Wireless Repeater Setup on DD-WRT FlashRouter - Add Virtual Interface

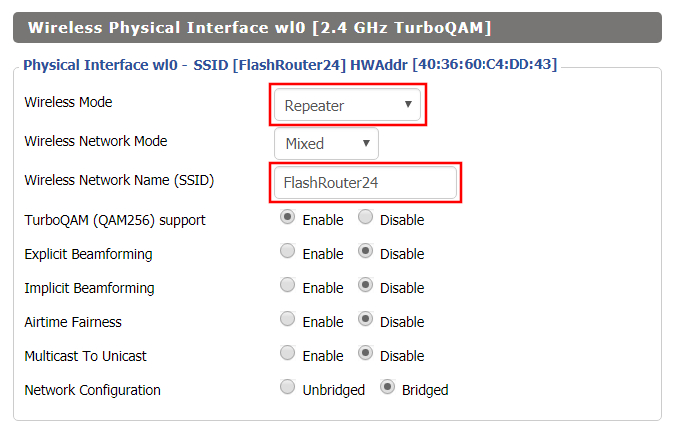
In the Wireless Physical Interface settings for the 2.4GHz network set the Wireless Mode to Repeater Bridge.

Change the Wireless Network Name (SSID) to match exactly with the Wireless Network Name of the network that you will bridge to.

Set Wireless Mode to Repeater Bridge in FlashRouter DD-WRT Basic Wireless Settings Page

In the Virtual Interfaces settings change the Wireless Network Name (SSID) to FlashRouter24 or any other unique SSID.

Wireless Repeater Setup on DD-WRT FlashRouter - Set SSID for Repeated Band

CLICK SAVE

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Password
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Change the WPA Shared Key to match exactly with the Wireless Password of the network that you will bridge to.
  3. Click Save.

Change the FlashRouter's Local IP Address

Navigate to Setup > Basic Setup

Wireless Repeater Bridge Setup on FlashRouter DD-WRT - Set Local Router IP, Gateway, Local DNS
  1. Set the Local IP Address to a different address on the same subnet as the existing network that you noted early. (example: if the existing network is 192.168.1.1 then set the Local IP Address to 192.168.1.2)
  2. Set the Gateway to the Local IP Address of the existing network. (example: 192.168.1.1)
  3. Set the Local DNS to the Local IP Address of the existing network. (example: 192.168.1.1)
  4. Click Save.

Change the FlashRouter's Operating Mode

Navigate to Setup > Advanced Routing

Set Operating Mode to Router in FlashRouter DD-WRT Basic Wireless Settings Page
  1. Set the Operating Mode to Router.
  2. Click Apply Settings.

Reboot your FlashRouter

Power off the FlashRouter for 30 seconds and then power it back on. When it boots back up you will be able to access the FlashRouter’s settings at the new Local IP Address that you set. Your existing network and the FlashRouter’s network will now be bridged wirelessly.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Private Internet Access (PIA) Setup for Privacy Hero

TeamFlashRouters · Apr 3, 2023 ·

Privacy Hero supports Private Internet Access (PIA) with WireGuard (recommended) and OpenVPN. You need an active PIA subscription and your PIA VPN username and password.

Important difference: PIA WireGuard has a built-in provider integration in Privacy Hero. Choose Private Internet Access from the VPN provider list—not Custom WireGuard. No WireGuard configuration file or key generation is needed.

By default, Privacy Hero can automatically select an optimal available PIA server based on your location and server conditions. Alternatively, use Advanced Options to enter a specific PIA server hostname from the regional list below.

Privacy Hero is cloud-managed. You can configure your router from any device with an internet connection, whether or not you are on the Privacy Hero WiFi network.

PIA VPN Setup Guide

Choose your setup method or jump to a particular step.

PIA WireGuard →Use the built-in Privacy Hero PIA providerAutomatic or Manual Server →Select an optimal server or enter a hostnamePIA Server Hostnames →Browse the full list organized by regionOpenVPN Setup →Generate and upload an OpenVPN configurationVerify Connection →Confirm your device is using the PIA VPNTroubleshooting →Connection errors, wrong region, no internet

Set Up PIA WireGuard in Privacy Hero (Recommended)

Unlike most other providers, PIA WireGuard does not use Custom VPN file uploads in Privacy Hero. The built-in PIA integration connects using your PIA account credentials and handles the WireGuard configuration for you.

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section. Select Change beside your current VPN provider.
  3. Choose Private Internet Access from the provider list. Do not select Custom for this WireGuard setup.
  4. Enter your PIA VPN account username and password (not your Privacy Hero dashboard credentials). You can check your account at PIA Client Control Panel.
  5. For automatic server selection, leave the optional server hostname unset, then click Save to connect. Wait until Privacy Hero displays Connected.
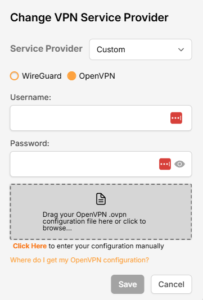
Privacy Hero built-in Private Internet Access provider login settings

Choose the Automatic Server or a Specific PIA Location

Privacy Hero offers two ways to select the PIA WireGuard server:

  • Automatic (recommended for most users): Leave the server hostname field blank. Privacy Hero selects an optimal available PIA location, generally favoring nearby servers and server conditions such as load. You do not need to manually maintain a server address.
  • Specific location: Enter a PIA region hostname under Advanced Options. This is useful when you need an IP address from a particular country or city.
  1. To use a specific location, open the existing Private Internet Access connection and select Advanced Options.
  2. Enter a complete PIA server hostname from the list below, for example us-newyorkcity.privacy.network or uk-london.privacy.network.
  3. Click Save, wait for Connected, then verify your new public IP address. If the selected location becomes unavailable, try another hostname or remove the hostname to return to automatic selection.
Privacy Hero Private Internet Access Advanced Options field for entering a VPN server hostname

PIA Server Hostname List by Region

Use these hostnames in PIA > Advanced Options when you prefer a specific location. Expand a region below and copy the complete hostname, including .privacy.network. This list is retained from the existing FlashRouters guide.

Server availability can change. Some hostnames, particularly those ending in -pf or marked for streaming, are specialized locations and may not be available for every connection. If a hostname no longer works, use automatic selection or check PIA’s current location list for available locations. PIA’s location list names regions; it does not necessarily provide matching hostnames.

North America (65 locations)
bahamas.privacy.networkca-ontario.privacy.networkca-toronto.privacy.networkca-vancouver.privacy.networkca-montreal.privacy.networkgreenland.privacy.networkgt-guatemala-pf.privacy.networkmexico.privacy.networkpanama.privacy.networksanjose.privacy.networkus-alabama-pf.privacy.networkus-alaska-pf.privacy.networkus-arkansas-pf.privacy.networkus-atlanta.privacy.networkus-california.privacy.networkus-chicago.privacy.networkus-connecticut-pf.privacy.networkus-denver.privacy.networkus-florida.privacy.networkus-houston.privacy.networkus-idaho-pf.privacy.networkus-indiana-pf.privacy.networkus-iowa-pf.privacy.networkus-kansas-pf.privacy.networkus-kentucky-pf.privacy.networkus-lasvegas.privacy.networkus-louisiana-pf.privacy.networkus-maine-pf.privacy.networkus-massachusetts-pf.privacy.networkus-michigan-pf.privacy.networkus-minnesota-pf.privacy.networkus-mississippi-pf.privacy.networkus-missouri-pf.privacy.networkus-montana-pf.privacy.networkus-nebraska-pf.privacy.networkus-new-hampshire-pf.privacy.networkus-new-mexico-pf.privacy.networkus-newyorkcity.privacy.networkus-north-carolina-pf.privacy.networkus-north-dakota-pf.privacy.networkus-ohio-pf.privacy.networkus-oklahoma-pf.privacy.networkus-oregon-pf.privacy.networkus-pennsylvania-pf.privacy.networkus-rhode-island-pf.privacy.networkus-seattle.privacy.networkus-siliconvalley.privacy.networkus-south-carolina-pf.privacy.networkus-south-dakota-pf.privacy.networkus-texas.privacy.networkus-tennessee-pf.privacy.networkus-vermont-pf.privacy.networkus-virginia-pf.privacy.networkus-washingtondc.privacy.networkus-west-virginia-pf.privacy.networkus-wisconsin-pf.privacy.networkus-wyoming-pf.privacy.networkus3.privacy.networkus-baltimore.privacy.networkus-honolulu.privacy.networkus-newjersey.privacy.networkus-saltlakecity.privacy.networkus-streaming-2.privacy.networkus-streaming.privacy.networkus-wilmington.privacy.network
South America (9 locations)
ar.privacy.networkbo-bolivia-pf.privacy.networkbogota.privacy.networkbr.privacy.networkec-ecuador-pf.privacy.networkpe-peru-pf.privacy.networksantiago.privacy.networkuy-uruguay-pf.privacy.networkvenezuela.privacy.network
Europe (51 locations)
al.privacy.networkad.privacy.networkaustria.privacy.networkbrussels.privacy.networkba.privacy.networksofia.privacy.networkzagreb.privacy.networkczech.privacy.networkde-berlin.privacy.networkde-frankfurt.privacy.networkdenmark.privacy.networkdenmark-2.privacy.networkspain.privacy.networkes-valencia.privacy.networkee.privacy.networkfi.privacy.networkfi-2.privacy.networkfrance.privacy.networkgr.privacy.networkhungary.privacy.networkitaly.privacy.networkitaly-2.privacy.networkis.privacy.networkireland.privacy.networkman.privacy.networklv.privacy.networkliechtenstein.privacy.networklt.privacy.networklu.privacy.networkmalta.privacy.networkmd.privacy.networkmonaco.privacy.networkmontenegro.privacy.networknl-amsterdam.privacy.networkmk.privacy.networkno.privacy.networkpoland.privacy.networkpt.privacy.networkro.privacy.networksweden.privacy.networksweden-2.privacy.networkrs.privacy.networksk.privacy.networkslovenia.privacy.networkswiss.privacy.networktr.privacy.networkuk-london.privacy.networkuk-manchester.privacy.networkuk-southampton.privacy.networkuk-2.privacy.networkua.privacy.network
Asia (26 locations)
ae.privacy.networkbangladesh.privacy.networkcambodia.privacy.networkchina.privacy.networkcyprus.privacy.networkgeorgia.privacy.networkhk.privacy.networkin.privacy.networkisrael.privacy.networkjakarta.privacy.networkjapan.privacy.networkjapan-2.privacy.networkkazakhstan.privacy.networkkr-south-korea-pf.privacy.networkkualalumpur.privacy.networkmacau.privacy.networkmongolia.privacy.networknp-nepal-pf.privacy.networkphilippines.privacy.networkqatar.privacy.networksaudiarabia.privacy.networksg.privacy.networksrilanka.privacy.networktaiwan.privacy.networkvietnam.privacy.networkyerevan.privacy.network
Oceania (7 locations)
au-adelaide-pf.privacy.networkau-australia-so.privacy.networkau-brisbane-pf.privacy.networkaus-melbourne.privacy.networkaus-perth.privacy.networkau-sydney.privacy.networknz.privacy.network
Africa (5 locations)
dz.privacy.networkegypt.privacy.networkmorocco.privacy.networknigeria.privacy.networkza.privacy.network

Set Up PIA OpenVPN in Privacy Hero

OpenVPN is the alternative when you need a manually uploaded connection or if the built-in PIA WireGuard method does not work on your network. OpenVPN uses Custom in Privacy Hero, unlike the built-in PIA WireGuard setup.

Download a PIA OpenVPN Configuration File

  1. Sign in to the PIA Client Control Panel using your PIA VPN account.
  2. Open Downloads and scroll to OpenVPN Configuration Generator or OpenVPN Configurations.
  3. If using the generator, choose OpenVPN 2.4 or newer and Linux when these options are offered, then choose an available server location.
  4. Select your preferred configuration. UDP / 1198 (AES-128-CBC) is a standard default. UDP / 1197 (AES-256-CBC) is an alternative. Use a PIA-provided TCP configuration if UDP does not work on your network.
  5. Click Generate or download a suitable pre-made configuration and save the resulting .ovpn file. Each server file is tied to its selected location/settings.

PIA also provides pre-made OpenVPN configuration bundles; see PIA’s OpenVPN file instructions.

Add PIA OpenVPN as a Custom VPN

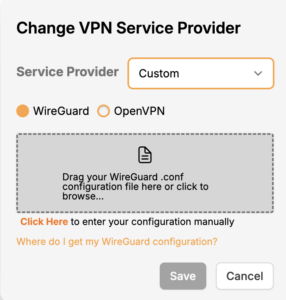
  1. Open Privacy Hero, go to VPN, click Change, and select Custom.
  2. Choose OpenVPN and upload the PIA .ovpn file downloaded in the previous section.
  3. Enter your PIA VPN username and password in the Custom OpenVPN authentication fields.
  4. Click Save and confirm Privacy Hero shows Connected.
Privacy Hero Custom OpenVPN configuration with file upload and username password fields

Note: If OpenVPN UDP cannot connect, try a TCP profile from PIA or another server. When switching protocols, make sure you upload a matching PIA configuration file.


Verify Your Private Internet Access Connection

  1. Connect a device to the Privacy Hero WiFi or LAN network.
  2. Disconnect any PIA app or other VPN running directly on the device so the router VPN can be tested independently.
  3. Open a private/incognito browser window and visit PIA What Is My IP.
  4. Confirm that your public IP address reflects the VPN connection, and that the approximate location is consistent with either the selected hostname or Privacy Hero’s automatic server selection.

Privacy Hero VPN settings can be changed remotely, but the device used to verify the VPN IP must be connected to the Privacy Hero network.

Streaming Relocation and Your PIA Location

If Streaming Relocation is enabled for a supported service, that service may use the Streaming Relocation location instead of your PIA VPN server location. See Privacy Hero Streaming Relocation.


PIA VPN Not Connecting?

If Privacy Hero reports Failed, stays on Connecting, or connected devices lose internet access, try these checks:

  1. Confirm your PIA subscription is active and enter your PIA VPN login, not your Privacy Hero email/password.
  2. For built-in PIA WireGuard, verify the provider is Private Internet Access—not Custom. No downloaded WireGuard file is required.
  3. Remove any specific server hostname to test automatic server selection. If that connects, the previous hostname may be unavailable.
  4. For Custom OpenVPN, upload a fresh PIA .ovpn file, re-enter the PIA credentials, and try a different server or a TCP configuration.
  5. Turn off the router VPN temporarily to check that normal internet access works. If the VPN Kill Switch is blocking internet traffic, temporarily disable it for testing, then restore your preferred setting.
  6. Check whether a separate VPN app, iCloud Private Relay, Private DNS, proxy, or security software on the testing device is affecting your VPN IP results.

No Internet When the VPN Disconnects?

The Privacy Hero VPN Kill Switch may intentionally block internet access if the VPN goes down. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

If other devices show the expected VPN address, review device VPN apps, iCloud Private Relay, Private DNS, and security settings.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

NordVPN Setup for AsusWRT: Token, WireGuard & OpenVPN

TeamFlashRouters · Oct 15, 2025 ·

Set up NordVPN on an ASUS router using AsusWRT VPN Fusion. Supported ASUS firmware offers three different VPN types: NordVPN (access-token integration), WireGuard (downloadable .conf file), and OpenVPN (manual service credentials plus an .ovpn file). Choose the method that matches your needs and your router’s available options.

All configuration is completed directly through your ASUS router’s administration interface using VPN Fusion. Before starting, make sure your router is connected to the internet, your firmware supports VPN Fusion, and you have an active NordVPN subscription.

Before starting, join the ASUS router WiFi or LAN and sign in to http://www.asusrouter.com or your router’s LAN IP (commonly 192.168.50.1). Open VPN > VPN Fusion > Add profile. Router model, firmware, and region affect which VPN types appear. See Access Your AsusWRT Settings.

In This Guide

Choose a VPN Type →NordVPN, WireGuard, or OpenVPNNordVPN Token Setup →Built-in NordLynx integrationWireGuard File Setup →Download and import a .confOpenVPN Setup →Manual credentials and .ovpnDedicated IP Setup →OpenVPN onlyDevices & Troubleshooting →Route devices and verify IP

Which NordVPN Option Should You Choose?

1. NordVPN

NordVPN access token and a country/region dropdown. The built-in ASUS/NordVPN integration is the simplest approach if you only need a country, not an exact server file.

Follow token setup →

2. WireGuard

Import a NordVPN .conf configuration file for a server selected in Nord Account. Useful when you want a downloaded profile for a particular server.

Follow WireGuard setup →

3. OpenVPN

Import a NordVPN .ovpn server file and enter your separate manual service username and password. Also used for NordVPN Dedicated IP.

Follow OpenVPN setup →

Dedicated IP uses OpenVPN only in this guide. Select OpenVPN in VPN Fusion and import your Dedicated IP .ovpn file. Do not use the standard NordVPN token/region dropdown for a Dedicated IP.

Option 1: NordVPN Dropdown — Token-Based NordLynx

Select the NordVPN type inside VPN Fusion. This is the integrated token-based setup and offers a country/region selection, rather than a manually imported server file.

  1. In Nord Account, open NordVPN Access Tokens and complete email/account verification if requested.
  2. Generate an access token, choose an expiry period if NordVPN offers that setting, and copy the token immediately (it may only be displayed once).
  3. On your ASUS router, open VPN > VPN Fusion > Add profile.
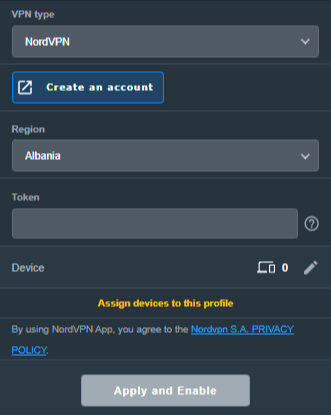
  4. Set VPN Type to NordVPN. Name the profile, select your preferred Region, and paste the token.
  5. Choose Apply to all devices if you want it as the default route, or assign only selected devices (see the VPN Fusion guide below).
  6. Click Apply and Enable / Apply all settings, as shown in your firmware, and verify the profile connects.
ASUS VPN Fusion NordVPN VPN type with Region and Token fields
Keep: existing ASUS NordVPN region/token form (remove any private token before publishing).

Need a specific server? Use the separate WireGuard file method below or the OpenVPN configuration-file method. Do not expect the token-based country dropdown to accept a .conf or .ovpn file.

Option 2: WireGuard Dropdown — Import a NordVPN .conf File

NordVPN now provides downloadable WireGuard configuration files through its manual server recommendation page. This is different from the built-in NordVPN token option in VPN Fusion.

  1. Sign in to Nord Account and open NordVPN Server Recommendation.
  2. Choose your preferred country and server; use the available filters if you need to narrow the list. Select a currently available server.
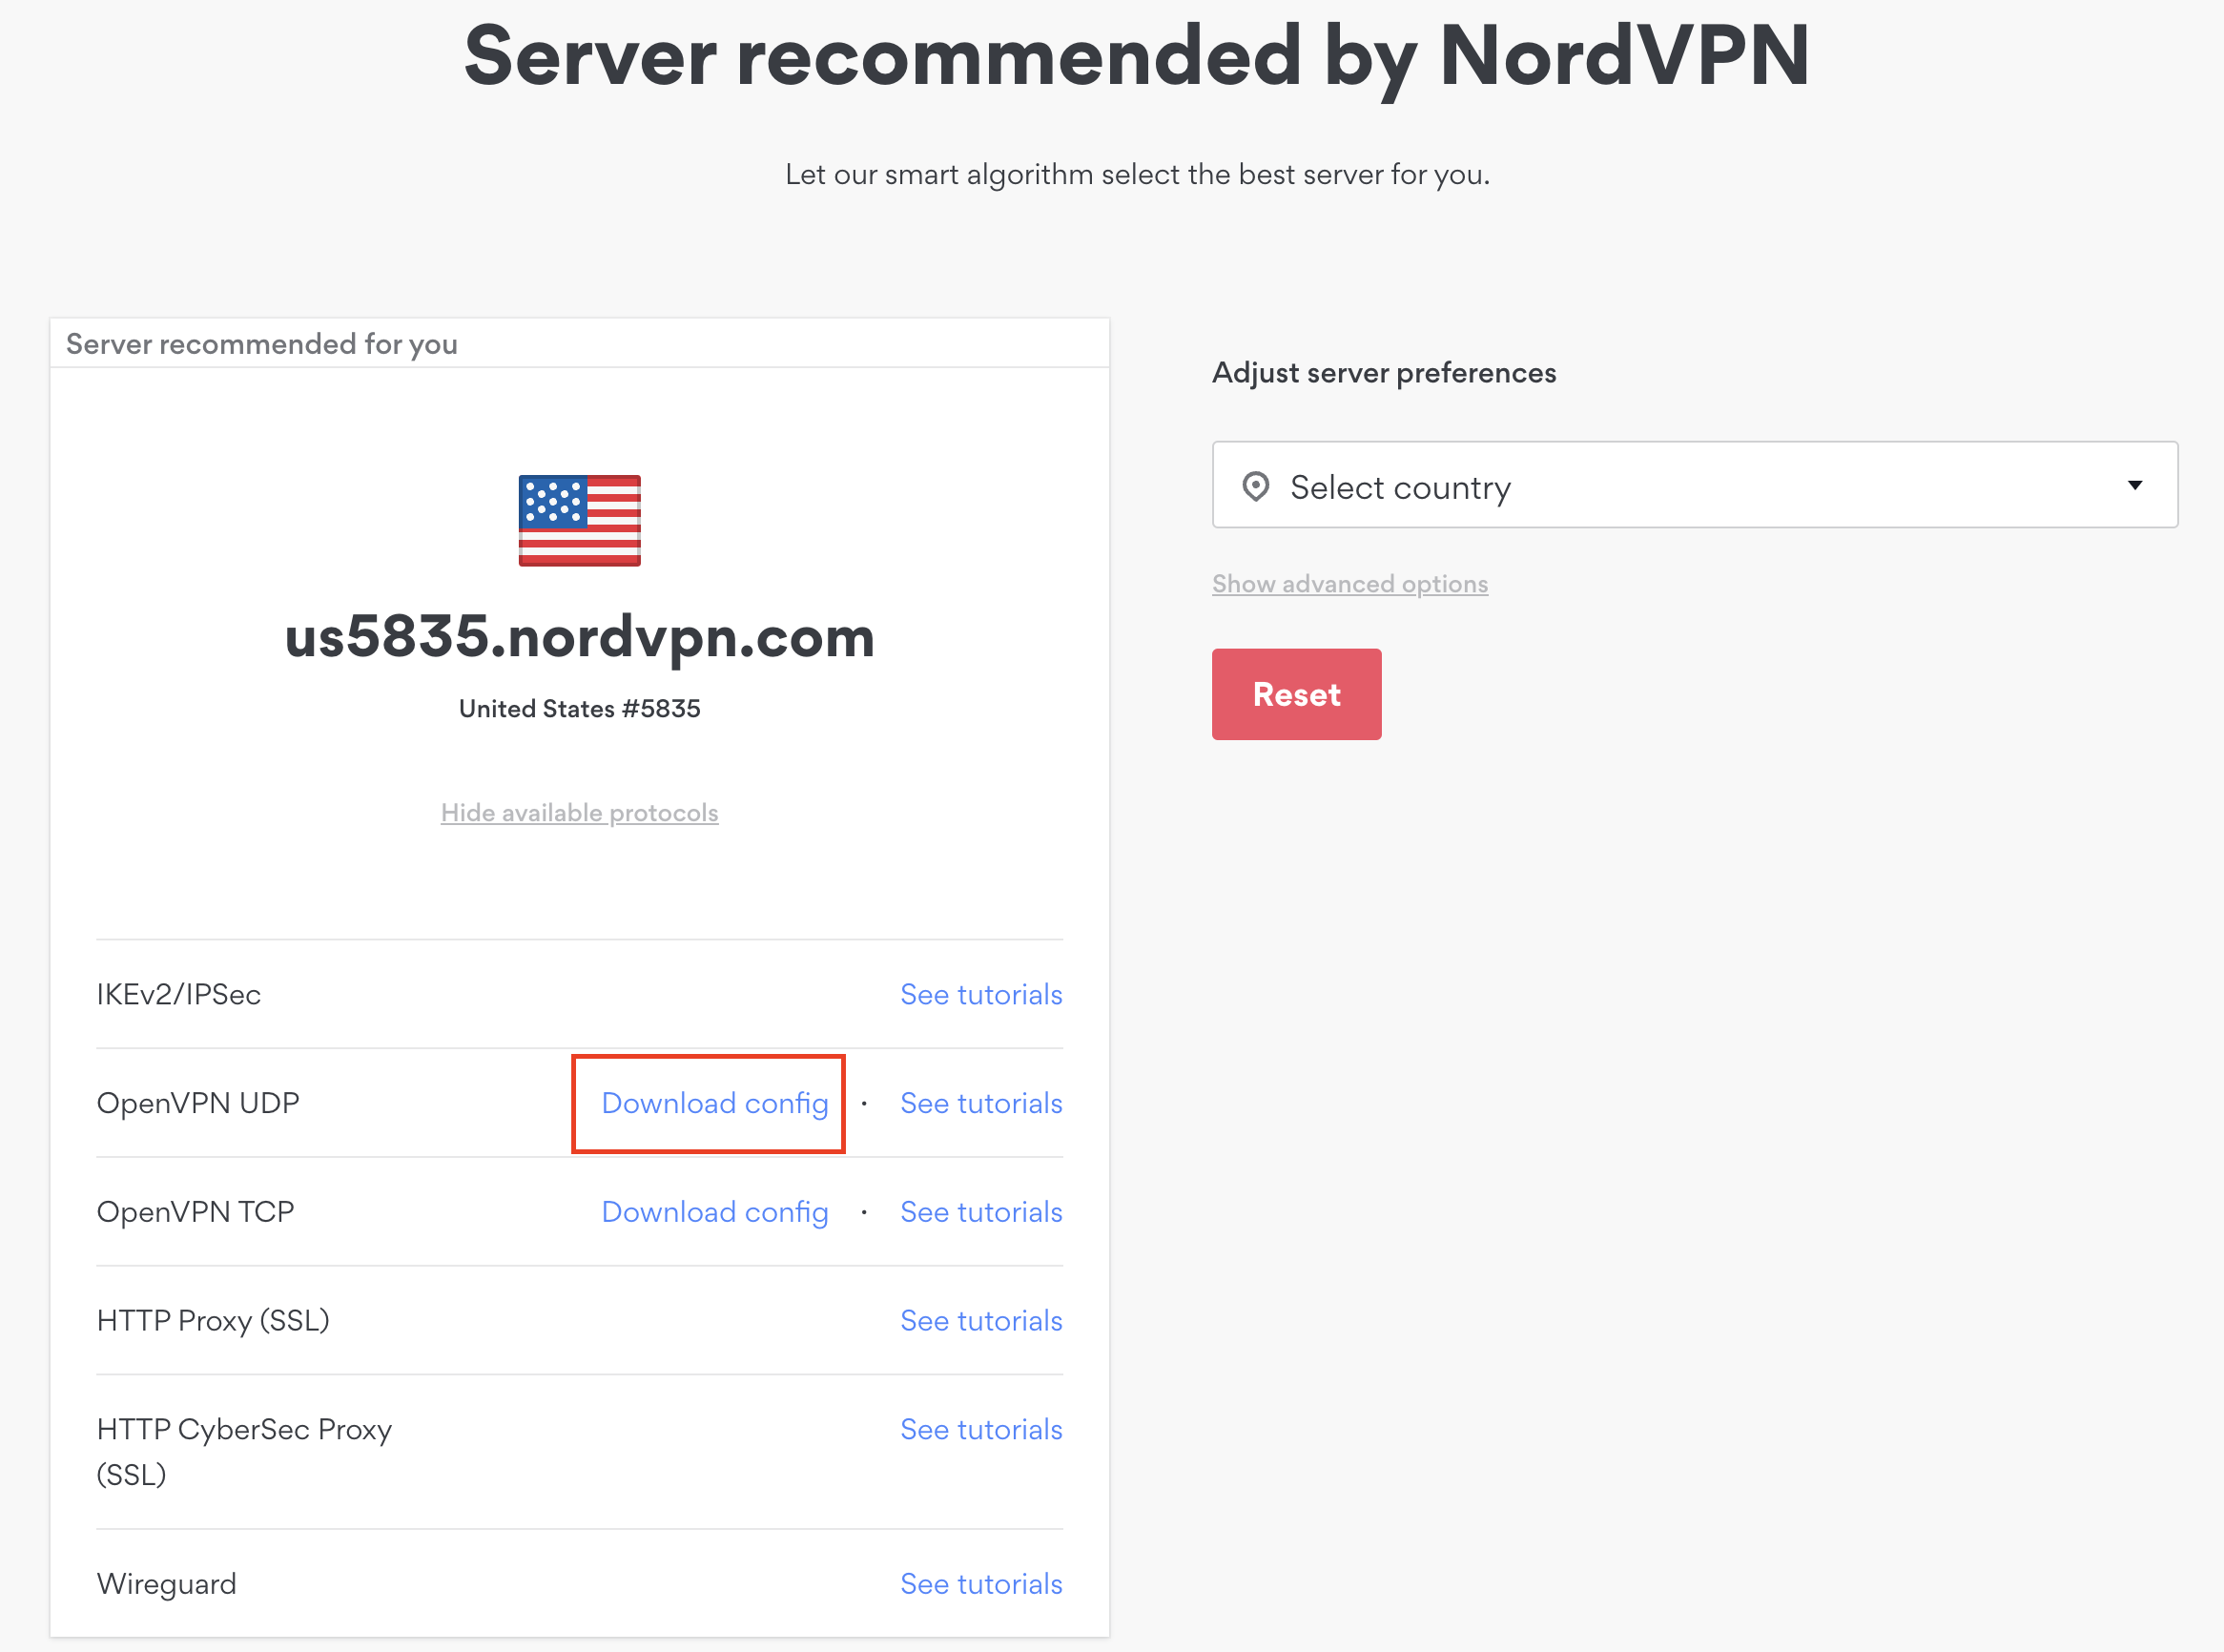
  3. Choose Get setup configuration, select WireGuard from the protocol menu, and click Download config. Save the downloaded .conf file.
  4. In your ASUS router settings open VPN > VPN Fusion > Add profile, then set VPN Type to WireGuard (not NordVPN).
  5. Use the ASUS Import configuration / file-import control to select the NordVPN .conf file. Confirm the imported parameters and save the profile.
  6. Choose the target devices or enable the default/all-devices route. Click Apply and Enable, then check the VPN status and your public IP.


WireGuard configuration files may contain a private key. Do not share an actual customer .conf file or publish a screenshot exposing its key material. When changing servers, download/import a different file and choose the desired active profile.

NordVPN’s official instructions: How to download WireGuard and OpenVPN configuration files.

Option 3: OpenVPN Dropdown — Credentials + .ovpn File

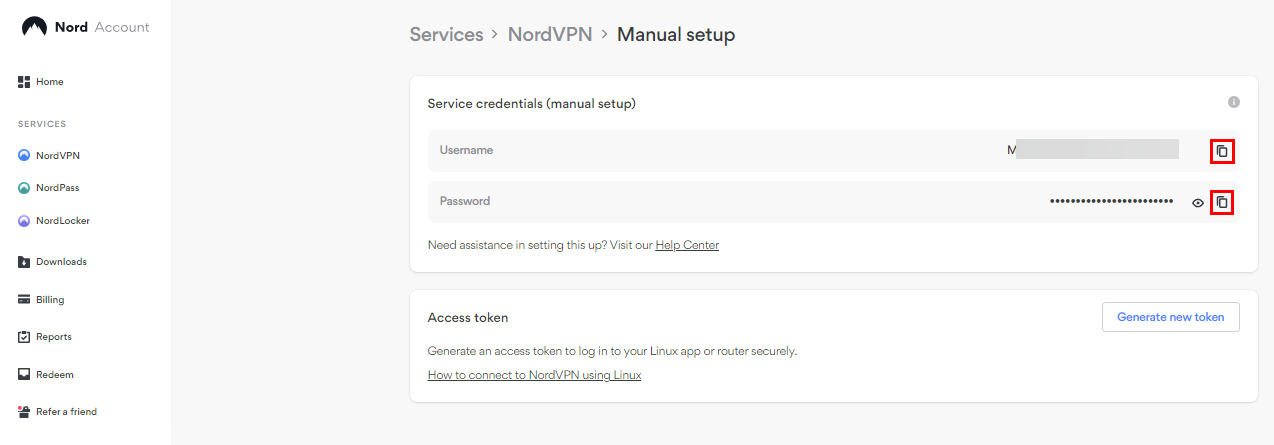
OpenVPN requires two separate items: the configuration file for your desired server and NordVPN’s manual service credentials. Your normal Nord Account email/password is not the correct credential pair for this method.

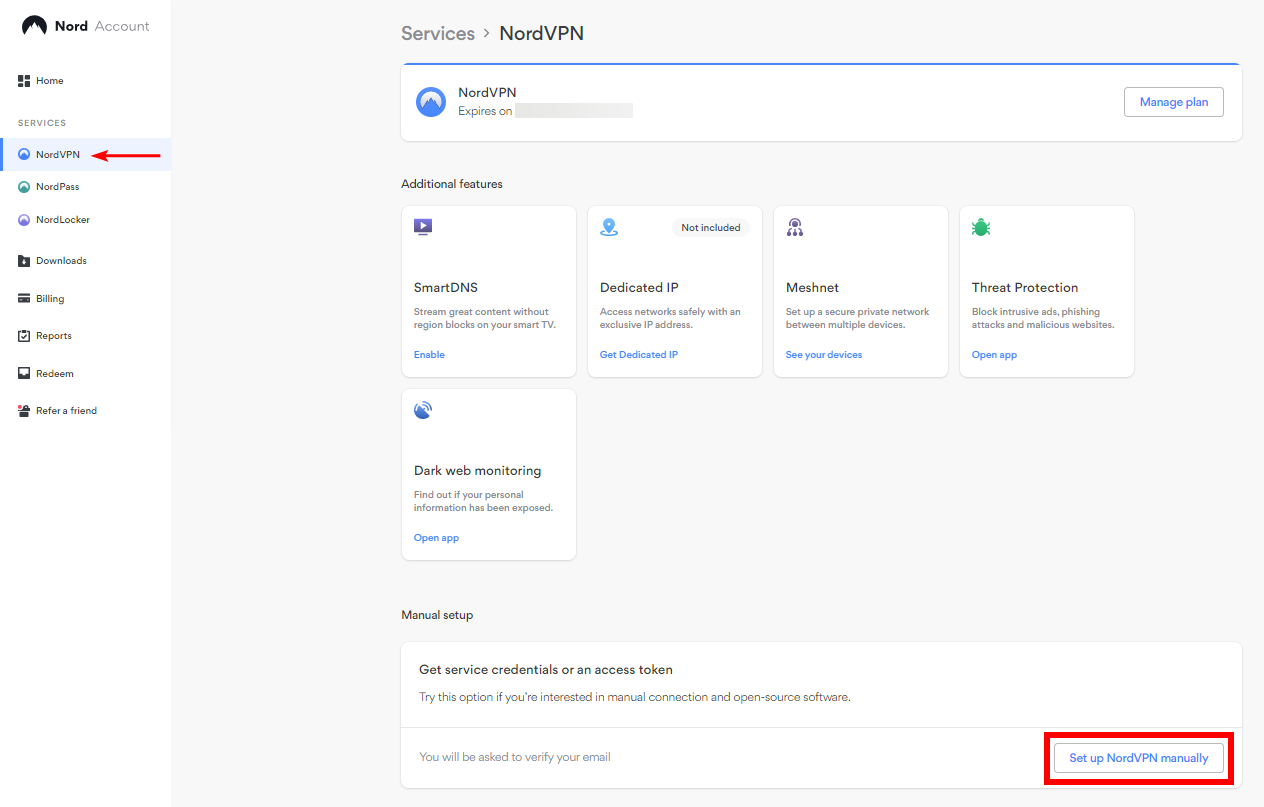
  1. Open NordVPN Manual Service Credentials and copy the service username and service password after any required verification.
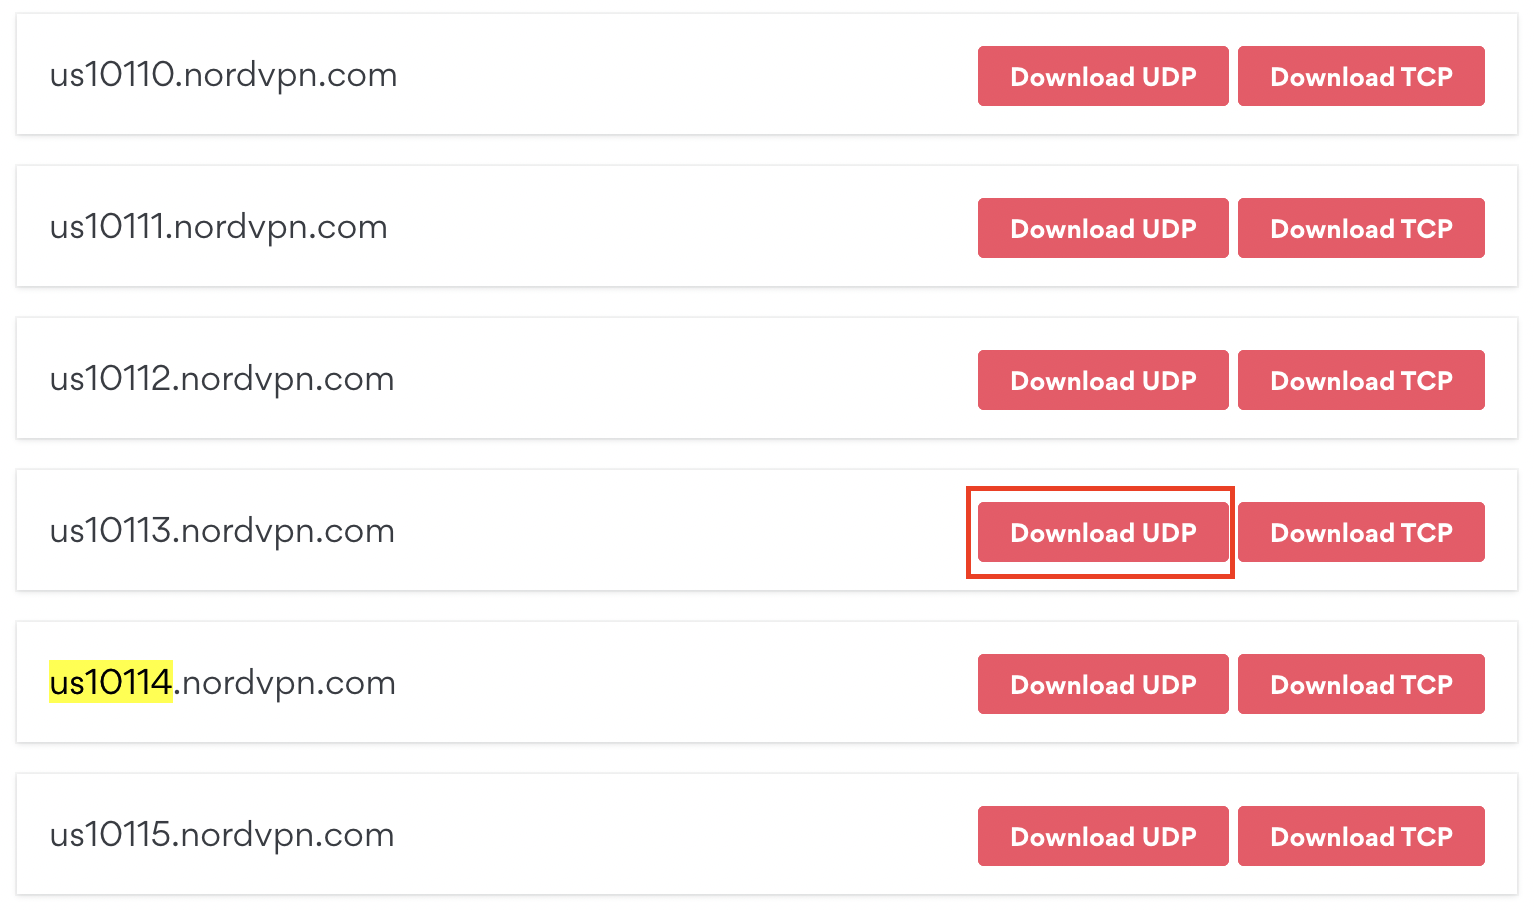
  2. Open NordVPN OpenVPN Configuration Files and choose a server/location. Download its UDP .ovpn file, or TCP .ovpn if UDP does not work on your network.
  3. On ASUS, go to VPN > VPN Fusion > Add profile and set VPN Type to OpenVPN.
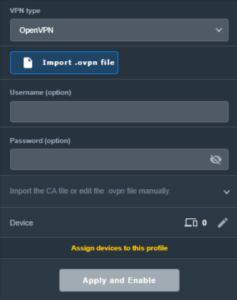
  4. Enter a connection name, Import .ovpn file, and paste the NordVPN manual service username and password in the corresponding fields.
  5. Choose devices or Apply to all devices, then click Apply and Enable. Confirm VPN Fusion shows a successful connection.
ASUS VPN Fusion OpenVPN VPN type with OVPN import and username password fields
Keep: existing ASUS OpenVPN profile form. New screenshots should use a larger clean capture if available.

Server selection: The location is controlled by the server named in the imported .ovpn file. To switch locations, import another server file or use a separate OpenVPN profile.

NordVPN Dedicated IP — OpenVPN Only

If you have purchased and activated the NordVPN Dedicated IP add-on, use your specific Dedicated IP OpenVPN configuration file. Do not select the ordinary NordVPN token integration or a regular shared server.

  1. In your Nord Account, open the Dedicated IP details and download the assigned server’s OpenVPN UDP or TCP configuration file, following NordVPN Dedicated IP manual configuration instructions.
  2. Open NordVPN Manual Service Credentials and copy the manual username and password.
  3. In ASUS VPN Fusion > Add profile, choose OpenVPN.
  4. Import the Dedicated IP .ovpn file, enter manual service credentials, save, enable, and verify the public IP matches your assigned Dedicated IP.

The Dedicated IP add-on must be active on the NordVPN account. A regular shared-server .ovpn file will not give you the Dedicated IP.

Assign Devices, Verify the VPN, and Troubleshoot

One VPN for everyone, or different VPNs for different devices?

VPN Fusion lets you use a VPN profile as the default connection for all devices or assign specific client devices to different profiles. Some supported ASUS models can maintain one WireGuard tunnel alongside multiple OpenVPN profiles, but the number of simultaneous tunnels is model/firmware dependent; creating multiple profiles does not mean all can be active simultaneously.

For step-by-step device assignments, default routing, profile conflicts, and bypassing the VPN, see How to Use ASUS VPN Fusion and Assign Devices to VPN Profiles. For a dedicated WiFi network with VPN or ISP routing, see ASUS Guest Network VPN / No-VPN Setup.

Verify the IP of the actual device

  1. Confirm your chosen profile shows Connected in VPN Fusion.
  2. Join the ASUS WiFi or LAN using a device that is actually assigned to that VPN profile.
  3. Open NordVPN IP Address Check and compare the public IP/location with the intended server or Dedicated IP.
  4. If the device shows an ISP IP, first check Apply to all devices and the per-device assignments in VPN Fusion.
  5. Disconnect a NordVPN app, Apple iCloud Private Relay, browser VPN/proxy, or other device-level network service during testing. Follow Router VPN Shows Wrong IP? Check Device Settings.

If VPN Fusion will not connect

  1. Temporarily disable the failing profile and confirm the ASUS router works using its normal ISP internet connection.
  2. For NordVPN type, check that the access token is valid and hasn’t expired; regenerate if needed.
  3. For WireGuard, import a fresh .conf from the Nord server recommendation page and make sure the profile is enabled.
  4. For OpenVPN, double-check manual service credentials (not website credentials) and try a different server file or TCP instead of UDP.
  5. Check that device-assignment rules point to the intended active profile, then retest with one clean device.

NordVPN Routers & Offers

Shop NordVPN-Ready FlashRouters

Compare ASUS and Privacy Hero router options and choose the hardware that fits your VPN and network requirements.

Browse NordVPN Routers →

NordVPN Partner Offer

Need NordVPN service? See the current FlashRouters NordVPN promotional offer. Subscription pricing and terms are shown on the offer page.

See NordVPN Offer →

Related AsusWRT Guides

  • ASUS VPN Fusion: Assign Devices and Manage Multiple Profiles
  • ASUS Guest Network: WiFi With or Without a VPN
  • AsusWRT Router Login Guide
  • Router VPN Shows Wrong IP? Device Settings

Upgrade your ASUS router

Explore the Latest WiFi 7 ASUS FlashRouters

Looking for a newer ASUS router? Browse WiFi 7 models available from FlashRouters and compare features to find the right fit for your home or office. VPN Fusion and other features vary by router model and firmware.

Shop ASUS WiFi 7 Routers →

NordVPN Setup for Privacy Hero

TeamFlashRouters · Apr 3, 2023 ·

Privacy Hero supports NordVPN using both NordLynx and OpenVPN.

NordLynx is recommended for most users. OpenVPN is also available and may be required for NordVPN Dedicated IP connections. Some Dedicated IP configurations require a private OpenVPN file imported as a Custom VPN.

Privacy Hero is cloud-managed, so you can complete the setup from any device with an internet connection. You do not need to be connected to Privacy Hero WiFi to change these settings.

Choose Your NordVPN Setup

Jump straight to the setup or troubleshooting instructions you need.

NordLynx Setup →Recommended · Access token
OpenVPN Setup →Manual service credentials
Country & Server →Select a location or server hostname
Dedicated IP →Advanced Options or Custom .ovpn
Verify Connection →Confirm your VPN IP and location
Troubleshooting →Connection errors and next steps

NordVPN NordLynx Setup

NordLynx uses a NordVPN access token, not your regular NordVPN website email and password.

Open Privacy Hero and Select NordLynx

  1. From a computer, smartphone, or tablet, open app.privacyhero.com.
  2. Sign in with your Privacy Hero account email and password.
  3. Open the VPN section.
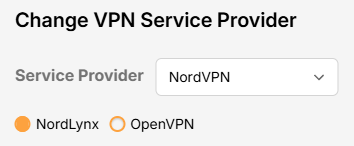
  4. Click Change and select NordVPN.
  5. Choose NordLynx.
NordVPN Protocol Privacy Hero

Generate Your NordVPN Access Token

  1. In another browser tab, open NordVPN Access Tokens and sign in to your NordVPN account.
  2. Complete any account or email verification requested by NordVPN.
  3. Select Generate new token; choose Doesn’t expire if available, then copy the token.

Important: Treat your NordVPN token as a password. Do not share it publicly.

Connect Privacy Hero to NordVPN

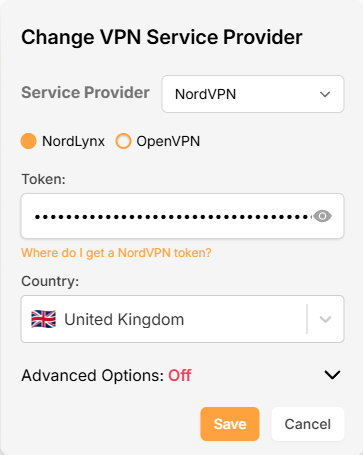
  1. Return to Privacy Hero, paste the token into the NordLynx token field, and click Save. The default country selection automatically chooses an available NordVPN server for that location.
  2. Wait for the VPN status to show Connected.
NordVPN Protocols Privacy Hero

NordVPN OpenVPN Setup

Use OpenVPN if you prefer the OpenVPN protocol or if your configuration requires it. OpenVPN requires NordVPN Manual Service Credentials, which are different from your website login email and password.

Select OpenVPN in Privacy Hero

  1. Open app.privacyhero.com and sign in.
  2. Open the VPN section.
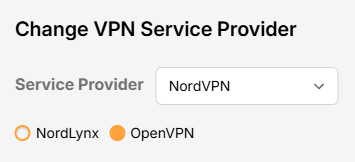
  3. Click Change and select NordVPN.
  4. Select OpenVPN.
NordVPN Protocol Privacy Hero

Get Your Manual Service Credentials

  1. Open NordVPN Manual Service Credentials and sign in.
  2. Complete NordVPN’s verification if prompted, then copy the current Service Username and Service Password.

Important: Do not enter your normal NordVPN website email and password into Privacy Hero’s OpenVPN fields.

Save Your OpenVPN Connection

  1. Return to Privacy Hero and enter the manual service username and password in the OpenVPN credential fields. Click Save.
  2. Confirm Privacy Hero shows the connection as Connected.

Choose a NordVPN Country or Specific Server

Privacy Hero can select a NordVPN server automatically, or you can choose a country or specify a server hostname.

Choose a Country

  1. Open your NordVPN connection in Privacy Hero.
  2. Open the Country dropdown.
  3. Search for and select your preferred country.
  4. Click Save. Privacy Hero will use an available NordVPN server for the selected country.

Use a Specific NordVPN Server

  1. Open your NordVPN connection in Privacy Hero.
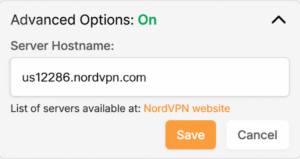
  2. Open Advanced Options.
  3. Enter the NordVPN server hostname, for example us12286.nordvpn.com.
  4. Click Save.

Use NordVPN’s server recommendation tool if you need a hostname. NordVPN servers can be retired or taken offline for maintenance; if your specific server stops working, choose another server or return to country selection.


NordVPN Dedicated IP Setup

NordVPN Dedicated IP can require either the regular NordVPN OpenVPN connection or a private .ovpn file imported as a Custom VPN.

Method 1: OpenVPN Advanced Options

Try this first if your Dedicated IP works with the standard NordVPN OpenVPN setup.

  1. Set up NordVPN → OpenVPN using your NordVPN Manual Service Credentials as described above.
  2. Open Advanced Options.
  3. Enter the Dedicated IP server hostname assigned to your account.
  4. Click Save and check whether the VPN connects.
  5. Verify that your public IP matches your assigned Dedicated IP.
Nord US Dedicated OpenVPN

If connected and the public IP matches, no additional configuration is needed.

Method 2: Custom VPN With a Private OpenVPN File

Some Dedicated IP servers require a private OpenVPN configuration file. If Method 1 does not connect, follow NordVPN’s Manual Dedicated IP Server Setup instructions.

Download Your Dedicated IP Configuration

  1. Sign in to the NordVPN account associated with the Dedicated IP.
  2. Locate your assigned Dedicated IP server using NordVPN’s manual setup instructions.
  3. Download its OpenVPN UDP configuration file.
  4. Save the .ovpn file to your computer or device.

Important: Use the private configuration file for your actual Dedicated IP, not a public NordVPN server file.

Upload the File as a Custom VPN

  1. Open app.privacyhero.com and select VPN → Change.
  2. Select Custom from the VPN provider dropdown, not NordVPN.
  3. Upload your Dedicated IP UDP .ovpn file.
  4. Enter your NordVPN Manual Service Username and Password.
  5. Save the configuration, enable the VPN, and wait for Connected.
  6. Verify the public IP matches your NordVPN Dedicated IP.

These are NordVPN’s separate manual service credentials, not your regular website login.


Verify Your NordVPN Connection

  1. Connect your testing device to the Privacy Hero WiFi.
  2. Disconnect any NordVPN or other VPN app running directly on that device.
  3. Open a fresh private/incognito browser window.
  4. Visit NordVPN What Is My IP.
  5. Confirm the public IP and location match your selected NordVPN server (or assigned Dedicated IP).

Running a VPN application directly on the device at the same time as the router VPN can produce double-VPN conflicts and unexpected IP or location results.

Streaming Relocation and VPN Location

If Streaming Relocation is enabled for a supported service, that service may use the Streaming Relocation region instead of your VPN server region. See Privacy Hero Streaming Relocation.


NordVPN Not Connecting?

If the VPN displays Failed, Connecting, or a timeout error, check for:

  • A server undergoing maintenance or no longer available.
  • An expired, revoked, or outdated NordLynx access token.
  • Incorrect or changed OpenVPN Manual Service Credentials.
  • Recent account changes or an inactive NordVPN subscription.
  • A protocol-specific issue.
  • A Dedicated IP that requires a private .ovpn file and Custom provider selection.

Follow Privacy Hero NordVPN Not Connecting or Showing Timeout Errors for troubleshooting.

No Internet After NordVPN Disconnects?

If internet access stops when the VPN disconnects, the VPN Kill Switch may be blocking normal traffic as intended. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected, but One Device Shows the Wrong IP?

If other devices show the correct VPN IP, check the affected device’s VPN apps, Private Relay, Private DNS, antivirus, and browser settings. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • NordVPN Not Connecting / Timeout
  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN

IPVanish Setup for Privacy Hero

TeamFlashRouters · Sep 23, 2025 ·

Privacy Hero supports IPVanish VPN through WireGuard (recommended) and OpenVPN. Both are configured in Privacy Hero using the Custom VPN provider option. You will need an active IPVanish VPN subscription and the configuration file for the protocol and server location you select.

Choose your method: WireGuard uses a generated .conf file and generally provides better performance. OpenVPN uses a downloaded .ovpn file plus your IPVanish VPN username and password.

Privacy Hero is cloud-managed. You can sign in and adjust VPN settings from a computer, phone, or tablet connected to any internet connection. You do not need to be on the Privacy Hero WiFi network to configure the router.

IPVanish Setup Guide

Jump to the instructions you need.

WireGuard File →Generate a WireGuard server configurationWireGuard Setup →Upload your .conf file to Privacy HeroOpenVPN File →Download an IPVanish .ovpn server fileOpenVPN Setup →Enter credentials and upload the configurationVerify Connection →Check your public VPN IP addressTroubleshooting →Fix connection errors and IP issues

Download an IPVanish WireGuard Configuration (Recommended)

Use the WireGuard configuration generator in your IPVanish account to create a server file for your router. A generated WireGuard file contains the connection keys and server details, so keep it private.

  1. Open the IPVanish account sign-in page and log in.
  2. Open WireGuard in the account navigation to access the WireGuard Configuration Generator.
  3. Select your preferred IPVanish server location and choose Generate to download the WireGuard configuration file. Save the downloaded .conf file to the device you are using for setup.

Important: Do not publicly share your WireGuard configuration file. To switch server locations later, generate and upload a new configuration.

Add IPVanish WireGuard to Privacy Hero

  1. Sign in to the Privacy Hero dashboard at app.privacyhero.com.
  2. Open the VPN section, select Change beside the provider, and choose Custom.
  3. Choose WireGuard and upload the IPVanish .conf file you just generated.
  4. Click Save to apply the settings. Wait for Privacy Hero to report Connected.
Privacy Hero Custom WireGuard configuration with WireGuard file upload

WireGuard authentication is contained in the generated configuration file; there is no separate OpenVPN username/password step in this method.


Download an IPVanish OpenVPN Configuration File

OpenVPN is a good alternative if WireGuard is unavailable or fails to connect on your network. It requires an IPVanish .ovpn configuration file and VPN login credentials.

  1. Open the IPVanish OpenVPN server configuration list.
  2. Download an .ovpn file for your preferred available server location. If IPVanish provides both UDP and TCP files, start with UDP and keep a TCP file as a fallback.
  3. Have your IPVanish account username and password available for the OpenVPN setup. Use the credentials accepted by your IPVanish VPN account; these are not Privacy Hero login credentials.

If the linked server directory has changed, check the latest manual OpenVPN configuration downloads offered by IPVanish before selecting a file.

Add IPVanish OpenVPN to Privacy Hero

  1. Sign in at app.privacyhero.com and open VPN.
  2. Select Change, choose Custom, and select OpenVPN.
  3. Upload the IPVanish .ovpn file you downloaded.
  4. Enter your IPVanish username and password in the Custom OpenVPN fields. Do not enter the Privacy Hero account login.
  5. Click Save and wait for the connection status to show Connected.
Privacy Hero Custom OpenVPN configuration showing server file upload and username and password fields

Tip: If OpenVPN UDP times out or cannot connect, try an available IPVanish OpenVPN TCP configuration or another server location.


Verify Your IPVanish VPN Connection

After Privacy Hero displays Connected, verify that a device on the router is actually using IPVanish.

  1. Connect the device you want to test to the Privacy Hero WiFi or LAN network.
  2. Temporarily disconnect any IPVanish app, other VPN app, or device-level VPN connection on that device so you test the router VPN alone.
  3. Open a new private/incognito browser window and visit IPVanish What Is My IP Address.
  4. Confirm that your public IP address and approximate location correspond to the VPN server you selected.

Note: Privacy Hero settings can be managed remotely, but the device used for this IP test must be on the Privacy Hero network.

Streaming Relocation and Your VPN Location

If Streaming Relocation is enabled for a supported streaming service, that service may use the configured Streaming Relocation location instead of the IPVanish server location. See Privacy Hero Streaming Relocation.


IPVanish Not Connecting?

If Privacy Hero remains on Connecting, displays Failed, or reports a timeout, check the following:

  1. Make sure your IPVanish subscription is active and that Custom is selected as the VPN provider in Privacy Hero.
  2. For WireGuard, generate a fresh configuration from your IPVanish account and upload that .conf file again.
  3. For OpenVPN, confirm your IPVanish username/password and upload a fresh .ovpn file for a different server.
  4. Try a different server location. With OpenVPN, also try switching between available UDP and TCP files.
  5. Temporarily disable the Privacy Hero VPN connection and test normal internet access. If enabled, temporarily turn off the VPN Kill Switch for this test, then restore your preferred Kill Switch setting.
  6. Check whether a device-level VPN app, private DNS, proxy, or security software is interfering with the router VPN connection.

VPN Disconnected and No Internet?

The VPN Kill Switch can intentionally block internet access when the VPN disconnects. Review Privacy Hero VPN Kill Switch Setup.

VPN Connected but One Device Shows the Wrong IP?

If only one device shows an unexpected IP address, look for another VPN app, iCloud Private Relay, Private DNS, browser proxy/DNS settings, or security software on that device. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

VyprVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual VyprVPN Setup

Verify your VyprVPN login information

If you are not already a VyprVPN user Sign Up Now.

Log in to your account on the VyprVPN website.

VyprVPN - Website Login

VyprVPN Server Addresses

United States

Los Angeles, CA us1.vpn.goldenfrog.com
Washington, DC us2.vpn.goldenfrog.com
Austin, TX us3.vpn.goldenfrog.com
Miami, FL us4.vpn.goldenfrog.com
New York City, NY us5.vpn.goldenfrog.com
Chicago, IL us6.vpn.goldenfrog.com
San Francisco, CA us7.vpn.goldenfrog.com
Seattle, WA us8.vpn.goldenfrog.com

United Kingdom

 London uk1.vpn.goldenfrog.com

Canada

Toronto ca1.vpn.goldenfrog.com

Australia

Sydney au1.vpn.goldenfrog.com
Melbourne au2.vpn.goldenfrog.com
Perth au3.vpn.goldenfrog.com

Germany

Frankfurt de1.vpn.goldenfrog.com

Rest of the World

UAE – Dubai ae1.vpn.goldenfrog.com
Argentina – Buenos Aires ar1.vpn.goldenfrog.com
Austria – Vienna at1.vpn.goldenfrog.com
Belgium – Brussels be1.vpn.goldenfrog.com
Bulgaria – Sofia bg1.vpn.goldenfrog.com
Bahrain – Manama bh1.vpn.goldenfrog.com
Brazil – São Paulo br1.vpn.goldenfrog.com
Switzerland – Zurich ch1.vpn.goldenfrog.com
Colombia – Bogotá co1.vpn.goldenfrog.com
Costa Rica – San José cr1.vpn.goldenfrog.com
Czech Republic – Prague cz1.vpn.goldenfrog.com
Germany – Frankfurt de1.vpn.goldenfrog.com
Denmark – Copenhagen dk1.vpn.goldenfrog.com
Algeria – Algiers dz1.vpn.goldenfrog.com
Egypt – Cairo eg1.vpn.goldenfrog.com
Spain – Madrid es1.vpn.goldenfrog.com
Netherlands – Amsterdam eu1.vpn.goldenfrog.com
Finland – Helsinki fi1.vpn.goldenfrog.com
France – Paris fr1.vpn.goldenfrog.com
Greece – Athens gr1.vpn.goldenfrog.com
Hong Kong – Hong Kong hk1.vpn.goldenfrog.com
Indonesia – Jakarta id1.vpn.goldenfrog.com
Ireland – Dublin ie1.vpn.goldenfrog.com
Israel – Tel Aviv il1.vpn.goldenfrog.com
India – Mumbai in1.vpn.goldenfrog.com
Iceland – Reykjavík is1.vpn.goldenfrog.com
Italy – Rome it1.vpn.goldenfrog.com
Japan – Tokyo jp1.vpn.goldenfrog.com
South Korea – Seoul kr1.vpn.goldenfrog.com
Liechtenstein – Schaan li1.vpn.goldenfrog.com
Lithuania – Vilnius lt1.vpn.goldenfrog.com
Luxembourg – Luxembourg City lu1.vpn.goldenfrog.com
Latvia – Riga lv1.vpn.goldenfrog.com
Marshall Islands – Majuro mh1.vpn.goldenfrog.com
Macao – Macao mo1.vpn.goldenfrog.com
Maldives – Malé mv1.vpn.goldenfrog.com
Mexico – Mexico City mx1.vpn.goldenfrog.com
Malaysia – Kuala Lumpur my1.vpn.goldenfrog.com
Norway – Oslo no1.vpn.goldenfrog.com
New Zealand – Auckland nz1.vpn.goldenfrog.com
Panama – Panama City pa1.vpn.goldenfrog.com
Philippines – Manila ph1.vpn.goldenfrog.com
Pakistan – Karachi pk1.vpn.goldenfrog.com
Poland – Warsaw pl1.vpn.goldenfrog.com
Portugal – Lisbon pt1.vpn.goldenfrog.com
Qatar – Doha qa1.vpn.goldenfrog.com
Romania – Bucharest ro1.vpn.goldenfrog.com
Russia – Moscow ru1.vpn.goldenfrog.com
Saudi Arabia – Riyadh sa1.vpn.goldenfrog.com
Sweden – Stockholm se1.vpn.goldenfrog.com
Singapore – Singapore sg1.vpn.goldenfrog.com
Slovenia – Ljubljana si1.vpn.goldenfrog.com
Slovakia – Bratislava sk1.vpn.goldenfrog.com
El Salvador – San Salvador sv1.vpn.goldenfrog.com
Thailand – Bangkok th1.vpn.goldenfrog.com
Turkey – Istanbul tr1.vpn.goldenfrog.com
Taiwan – Taipei tw1.vpn.goldenfrog.com
Ukraine – Kiev ua1.vpn.goldenfrog.com
Uruguay – Montevideo uy1.vpn.goldenfrog.com
Vietnam – Hanoi vn1.vpn.goldenfrog.com

DD-WRT Router Setup for VyprVPN

Navigate to Services > VPN

VyprVPN offers two different Encryption levels:

Default Encryption (Blowfish-CBC)
typically provides faster speeds.

Strong Encryption (AES-256) provides stronger encryption.

Follow the table below of the one that fits your needs.

Enter VyprVPN settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change VyprVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

Blowfish-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your VyprVPN account with.

Password

Enter the Password you successfully logged in to your VyprVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
keepalive 10 60
persist-key
persist-tun
persist-remote-ip
nobind

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter VyprVPN settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change VyprVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your VyprVPN account with.

Password

Enter the Password you successfully logged in to your VyprVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
keepalive 10 60
persist-key
persist-tun
persist-remote-ip
nobind
tls-cipher TLS-DHE-RSA-WITH-AES-256-CBC-SHA

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing. Learn more here.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VyprVPN connection

Navigate to the Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit to WhatIsMyIPAddress to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to VyprVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
How to change the VyprVPN server

  1. Copy the new VyprVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field and Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

OverPlay Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual OverPlay Setup

Verify your OverPlay login information

Log in to your account on the OverPlay website.

OverPlay Server Addresses

View a full list of OverPlay servers.

United States

Ashburn:
iad-a01.wlvpn.com

Atlanta:
atl-a01.wlvpn.com

Chicago
:
chi-a01.wlvpn.com

Dallas
:
dal-a02.wlvpn.com

Las Vegas
:
las-c11.wlvpn.com

Los Angeles
:
lax-a01.wlvpn.com

Miami
:
mia-a01.wlvpn.com

New York
:
nyc-a01.wlvpn.com

Phoenix
:
phx-a01.wlvpn.com

Salt Lake City
:
slc-c01.wlvpn.com

San Jose
:
sjc-a01.wlvpn.com

Seattle
:
sea-a01.wlvpn.com

DD-WRT Router Setup for OverPlay

Navigate to Services > VPN

Enter OverPlay settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change OverPlay connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194 for UDP
443 for TCP

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the username that you use to login to the OverPlay website.  Make sure to add @overplay after your username.

Hint:  For example, if your OverPlay username is “flashrouters” enter “flashrouters@overplay” as your username.

Password

Enter the Password you successfully logged in to your OverPlay account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIESDCCAzCgAwIBAgIJAKSqvk2CSdJGMA0GCSqGSIb3DQEBBQUAMHUxCzAJBgNV
BAYTAlVTMQwwCgYDVQQIEwNWUE4xDDAKBgNVBAcTA1ZQTjEMMAoGA1UEChMDVlBO
MQwwCgYDVQQLEwNWUE4xDDAKBgNVBAMTA1ZQTjEMMAoGA1UEKRMDVlBOMRIwEAYJ
KoZIhvcNAQkBFgNWUE4wHhcNMTMwNDI1MDIzMjQ3WhcNMjMwNDI3MDIzMjQ3WjB1
MQswCQYDVQQGEwJVUzEMMAoGA1UECBMDVlBOMQwwCgYDVQQHEwNWUE4xDDAKBgNV
BAoTA1ZQTjEMMAoGA1UECxMDVlBOMQwwCgYDVQQDEwNWUE4xDDAKBgNVBCkTA1ZQ
TjESMBAGCSqGSIb3DQEJARYDVlBOMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIB
CgKCAQEAyUr2BAz2gHGaXri6rWMpKqcvVTX3IOSLEfBWf1fb2zCwx0+GFMG258Yk
OCiQho/YOX58bJpssGI42OzZitSisTVpXNIBelzGUPdKgx0qURGgDW+7eOySJYCn
1EUncElJCHt1so0SbfdQpxA88VZMH9fFOKtLY5qHHi0drXm/wZy+zW7TfV5Lce04
6vv2M9I5/Ko4zZ5Vh6jTo2VrCQRw8goXB5NAdU5D76lVhWK4Zzt4woI8nRW5Ev3A
WEw5oX85j5B0TY9nEi5j0vNYBuMxf/GiLO8M8LCHPX0HYBiLDjZesJCvuG3vfwnA
Y5CJQqNjufpmnF3ivsaF0dGeo54kWQIDAQABo4HaMIHXMB0GA1UdDgQWBBQXnwHk
vpHSf/lMacKoKshAcGM2qTCBpwYDVR0jBIGfMIGcgBQXnwHkvpHSf/lMacKoKshA
cGM2qaF5pHcwdTELMAkGA1UEBhMCVVMxDDAKBgNVBAgTA1ZQTjEMMAoGA1UEBxMD
VlBOMQwwCgYDVQQKEwNWUE4xDDAKBgNVBAsTA1ZQTjEMMAoGA1UEAxMDVlBOMQww
CgYDVQQpEwNWUE4xEjAQBgkqhkiG9w0BCQEWA1ZQToIJAKSqvk2CSdJGMAwGA1Ud
EwQFMAMBAf8wDQYJKoZIhvcNAQEFBQADggEBADAbNIIHF5vtCA+69/oipQ6niZit
Q+mnCNX5bxiF4xtw9qOQ90vLDc/ocbAGGP4Sub3hEkOoQlv9DHH56HVq1g9+L/Y7
RoneRykZ+GSPj2NlkobrPA7ZxAsLdFwM9Y+Fkql7cAHHLUCKh7H1IKidhTDHPCUj
hs4ZstNRckPd6wxlGGOP/Yf5sVse3pJwa0HyMYhI8pdTVJIHnFSy9vTPjVf3oWiz
Trci0+SkYKQE//5pE5wsYe0uB5wvQJslq/eEWfczg0l9biwJxG/qwxsVBkRgw5q6
defHWGj1eucVyy9fxKMcX89gjstQZDmsINNtG1C78/+nYS65rqaBaq+rqpA=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit OverPlay’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to OverPlay.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
How to change the OverPlay server

  1. Copy the new OverPlay server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

IVPN WireGuard Setup

TeamFlashRouters · Oct 13, 2021 ·

Preparing for IVPN WireGuard Setup

Verify your IVPN login information

If you are not already a IVPN user Sign Up Now.

Log in to your account on the IVPN website.

IVPN website login

DD-WRT Router Setup for IVPN WireGuard

Navigate to Setup > Tunnels 

Enter IVPN WireGuard settings

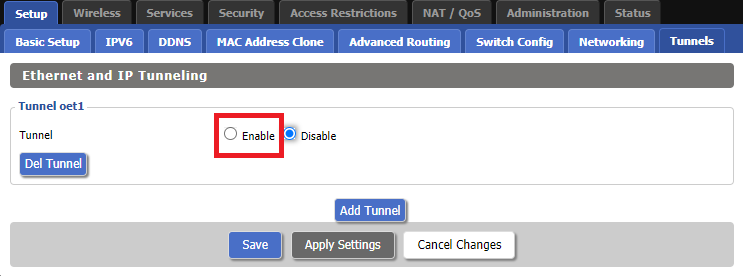
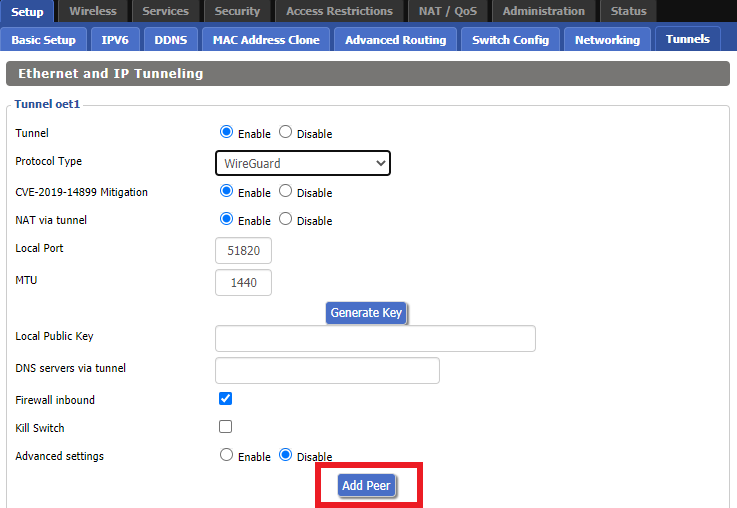
1. Click Add Tunnel.

2. Set Tunnel to Enable.

Setup - Tunnel - Enable Tunnel

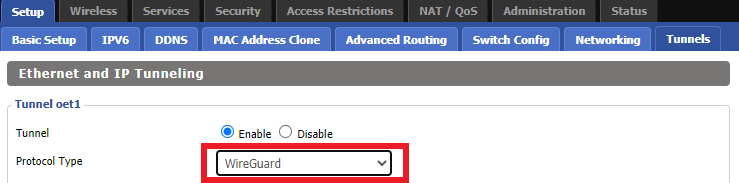
3. Select Wireguard from the dropdown.

Setup - Tunnel - Select Wireguard

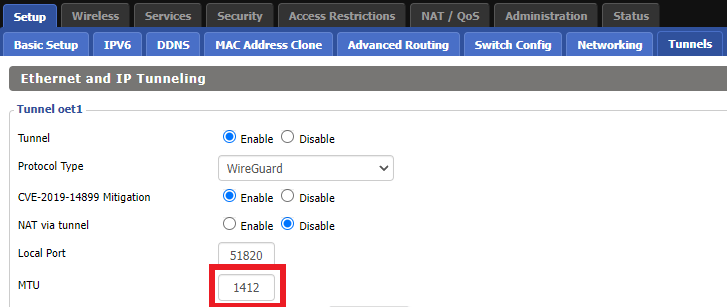
3. Set MTU to 1412.

IVPN Wireguard MTU setting

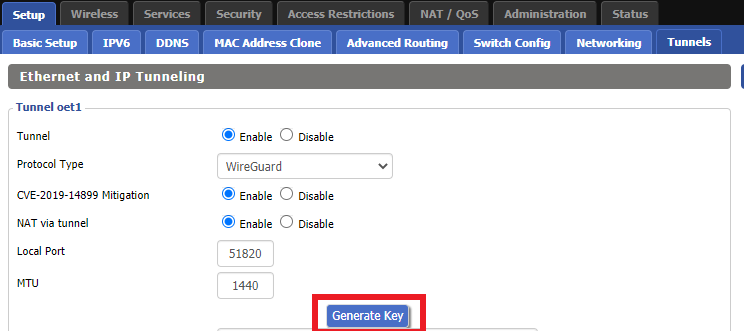
4. Click Generate Key.

Setup - Tunnel - Generate Key

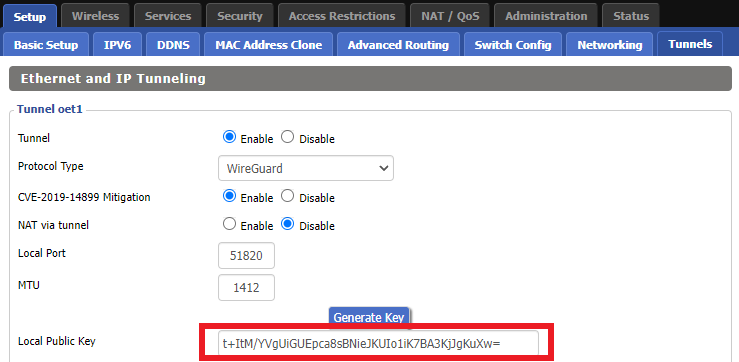
9. Copy the Local Public Key.

IVPN Wireguard Local Public Key

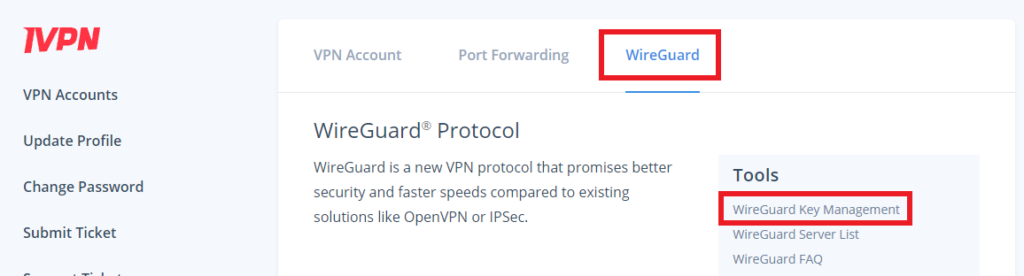
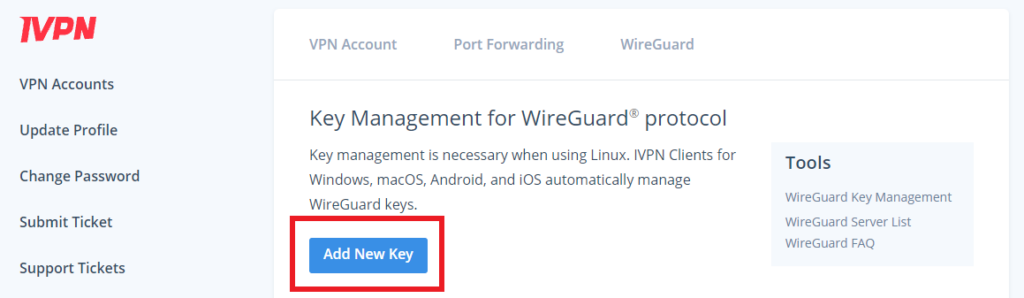
10. In a new tab (leave the DD-WRT settings opened), go to your IVPN Account and click WireGuard and then click WireGuard Key Management.

IVPN Wireguard Key Management

11. Click Add New Key.

IVPN Wireguard Add New Key

12. Paste the copied Local Public key to the Public Key field and click Add Key.

IVPN Wireguard Paste Public Key

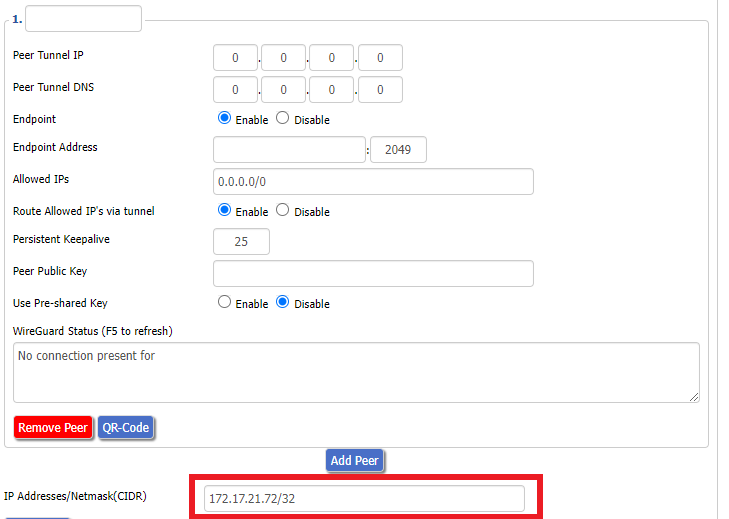
13.Copy the IP Address assigned to your public key and add it to the IP Addresses/Netmask(CIDR) field followed by a /32 subnet mask.

IVPN Wireguard copy IP Address
IVPN Wireguard paste IP Address

Certain DD-WRT builds will show two separate fields here: IP Address and Subnet Mask. If that is the case set the IP Address field to the Address without the /32 added and set the Subnet Mask to 255.255.255.255

14. Click Add Peer.

Setup - Tunnel - Add Peer

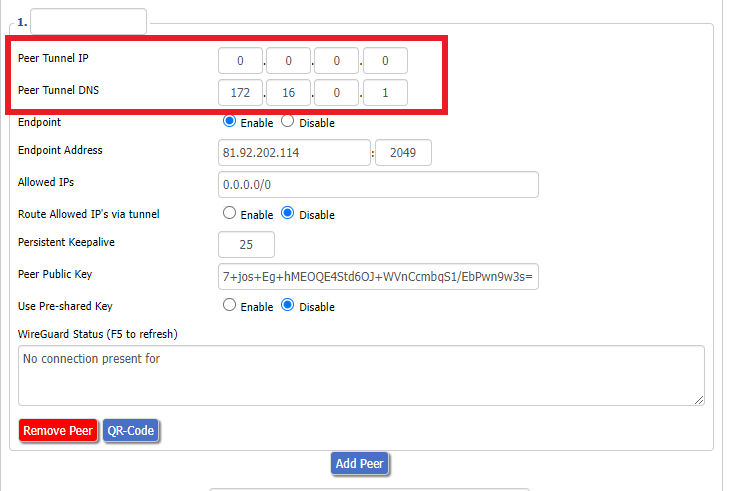
15. Set the Peer Tunnel IP to 0.0.0.0. Set Peer Tunnel DNS to 172.16.0.1

IVPN Wireguard Peer Tunnel IP and DNS

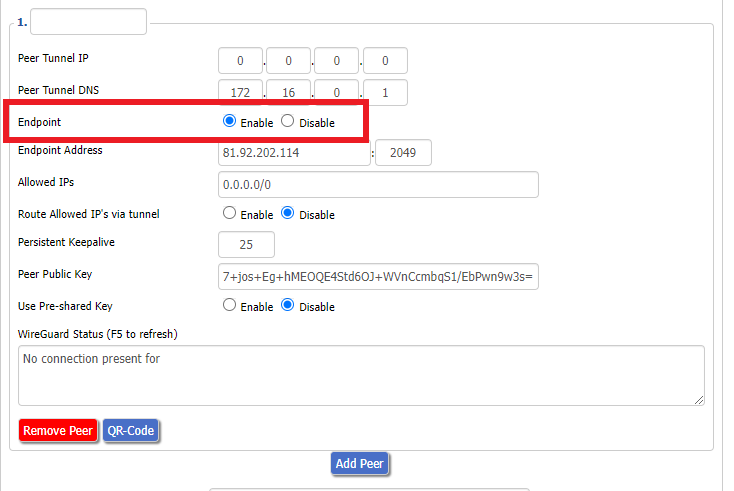
16. Set Endpoint to Enable.

IVPN Wireguard Enable Endpoint

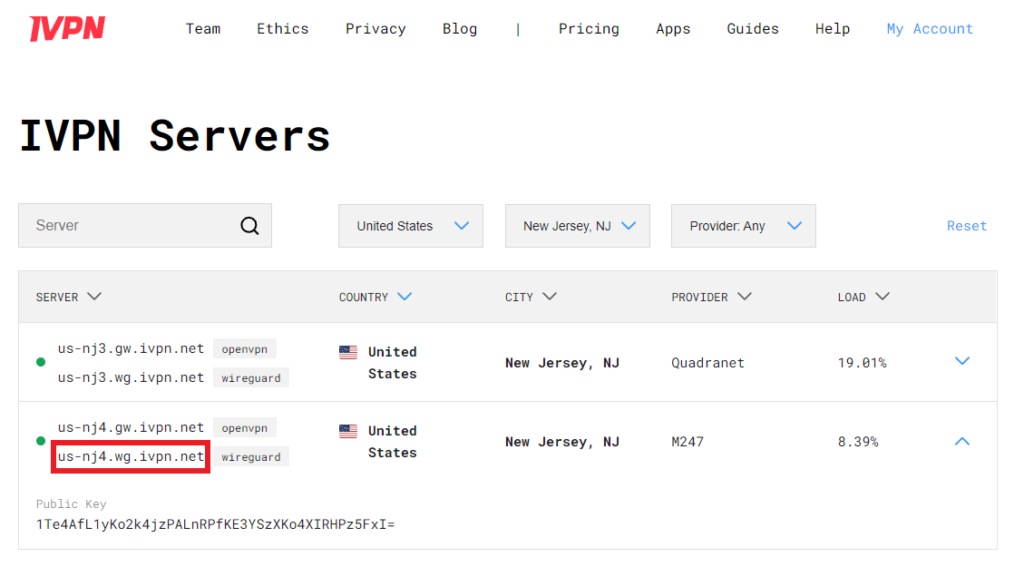
17. Go to the IVPN Server Status page and copy the server name for the WireGuard server location you want to connect to.

IVPN Wireguard Endpoint server

Be sure to copy the WireGuard server address and not the OpenVPN server address.

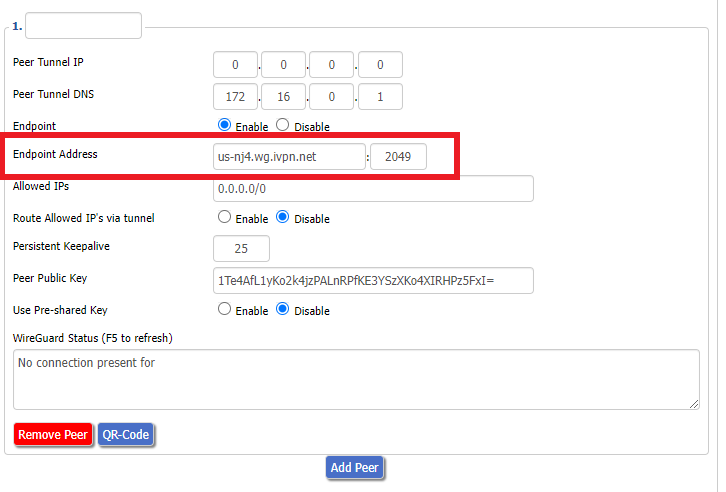
18. Paste the server name you copied into the Endpoint Address field and set the Port to 2049.

IVPN Wireguard Endpoint Address

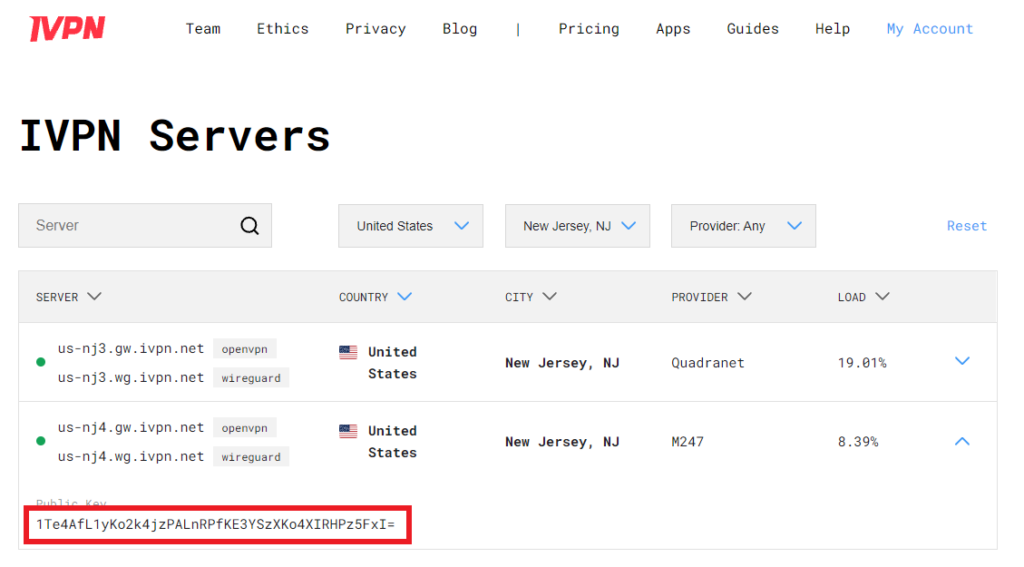
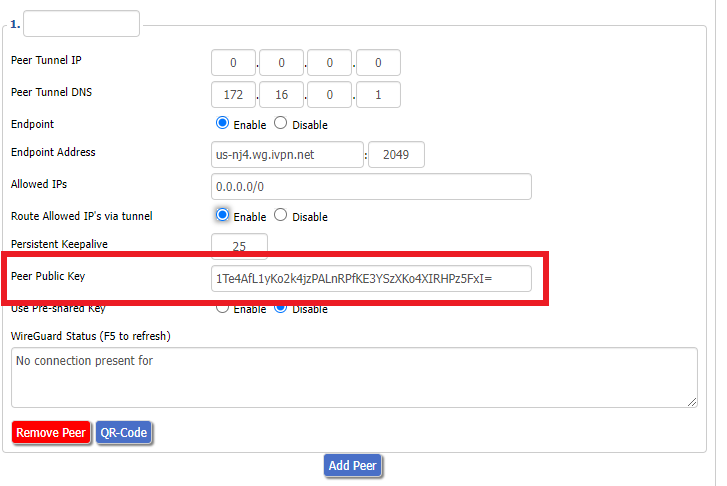
19. On the IVPN Server Status page copy the Public Key of the server location you entered. Paste the Public Key into the Peer Public Key field.

IVPN Wireguard copy server Public Key
IVPN Wireguard enter Peer Public Key

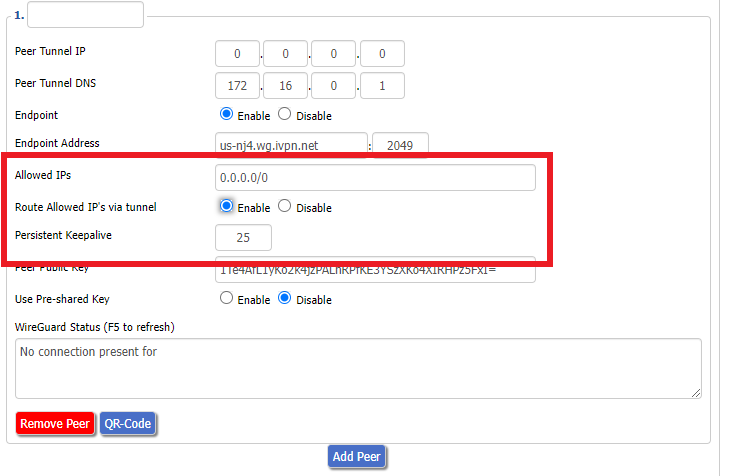
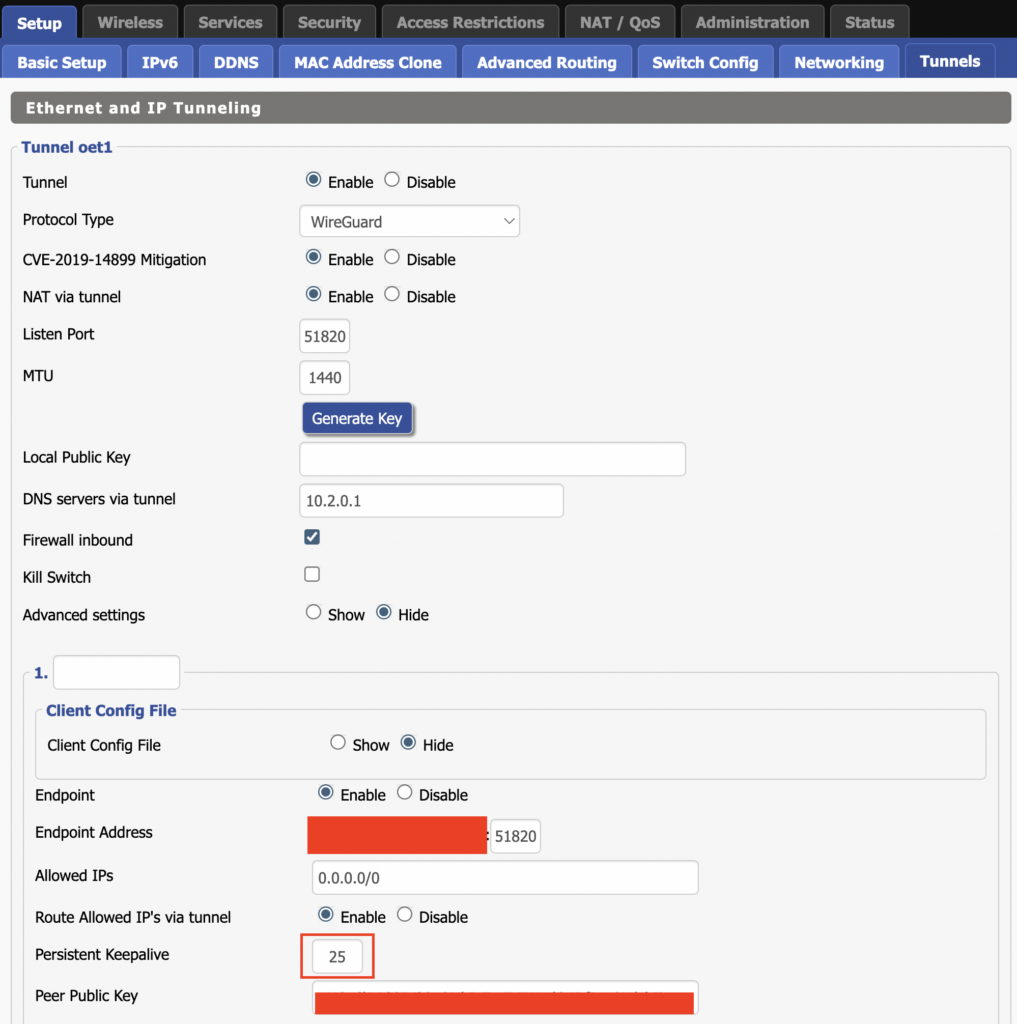
20. Leave Allowed IPs as 0.0.0.0/0. Set Router Allowed IP’s via tunnel to Enable. Set Persistent Keep Alive to 25.

IVPN Wireguard Peer settings

21. At the bottom of the page click Save and then click Apply Settings.

Set IVPN DNS servers

Navigate to Setup > Basic Setup

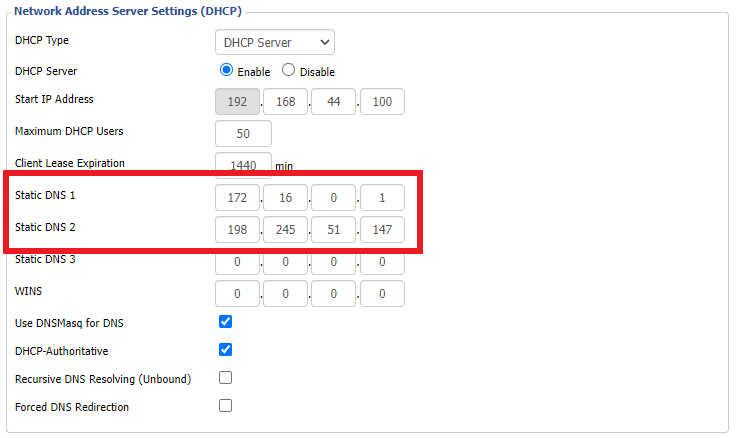
Set Static DNS 1 to 172.16.0.1

Set Static DNS 2 to 198.245.51.147

IVPN Wireguard Static DNS

Click Apply Settings.

Reboot the FlashRouter

Navigate to Administration > Management

Scroll to the bottom of the page and click the red Reboot Router button. Wait for the FlashRouter to reboot and then reconnect.

Verify a successful IVPN connection

Navigate to Setup > Tunnels

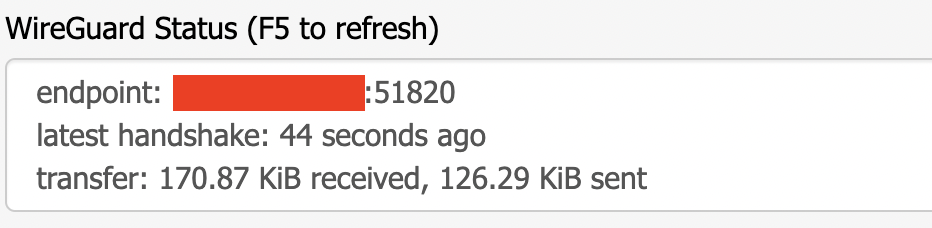
  1. You should Endpoint, Latest handshake, and Transfer in the WireGuard status area.
  2. Visit IVPN’s website to verify your status as using IVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Wireless Repeater Setup

TeamFlashRouters · Apr 16, 2019 ·

If you need to extend your wireless and wired connection capabilities, you can setup a FlashRouter as a Wireless Repeater. In Wireless Repeater mode the FlashRouter connects to your main router via WiFi and then creates a completely separate network segment for you. This new “repeater” network then transmits your internet signal via FlashRouter LAN ports for wired internet access while also creating a new Wireless Extender network that will expand your wireless network range throughout your home or office just like a mesh network.

Preparing for Wireless Repeater Setup

Verify your wireless information

To connect your FlashRouter wirelessly to your existing wireless network you will need the Wireless Network Name (SSID) and Wireless Password of the existing wireless network that you will repeat. Verify and note this information.

We recommend using a 2.4GHz network to repeat as this network will have more range. Be sure to click Add under the 2.4GHz settings and not the 5GHz settings.

DD-WRT Router Setup for Wireless Repeater

Disable Firewall

Navigate to Security > Firewall

Wireless Repeater Setup on DD-WRT FlashRouter - Disable SPI Firewall
  1. Set SPI Firewall to Disable.
  2. Click Save.

Enter Wireless settings

Navigate to Wireless > Basic Settings

Select Add in the Virtual Interface area.

Wireless Repeater Setup on DD-WRT FlashRouter - Add Virtual Interface

In the Wireless Physical Interface settings for the 2.4GHz network set the Wireless Mode to Repeater.

FlashRouters with a Broadcom chipset will have Repeater as an option in the dropdown but FlashRouters with an Atheroes chipset will not. Select Client or Client (Routed) if Repeater is not listed for your FlashRouter.

Change the Wireless Network Name (SSID) to match exactly with the Wireless Network Name of the network that you will repeat.

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Mode to Repeater

In the Virtual Interfaces settings change the Wireless Network Name (SSID) to FlashRouter24 or any other unique SSID.

Wireless Repeater Setup on DD-WRT FlashRouter - Set SSID for Repeated Band

CLICK SAVE

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

Wireless Repeater Setup on DD-WRT FlashRouter - Set Wireless Password
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Change the WPA Shared Key to match exactly with the Wireless Password of the network that you will repeat.
  3. Click Apply Settings.

Verify the Internet Connection

In the top right hand corner of the DD-WRT you should see the WAN IP change from 0.0.0.0 to an actual IP Address. Once this changes navigate to any website to test your Internet connection.

Wireless Repeater Setup on DD-WRT FlashRouter - Verify WAN Connection

Back up your settings

Navigate to the Administration > Backup page.

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
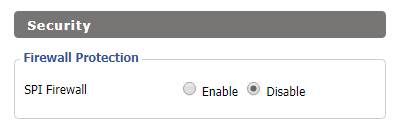
TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

Surfshark Manual OpenVPN Setup

TeamFlashRouters · Apr 24, 2019 ·

Preparing for Manual Surfshark Setup

Obtain your Surfshark OpenVPN information

If you are not already an Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

2. Successfully log in with your account information and Navigate to the Manual Connection Guide. Here you will find the OpenVPN Specific Username and Password required for manual configuration.

FlashRouters Privacy App - SurfShark OpenVPN Specific Username and Password

Surfshark Server Addresses

View a full list of Surfshark servers.

United States

Atlanta:
us-atl.prod.surfshark.com
Buffalo:
us-buf.prod.surfshark.com
Chicago:
us-chi.prod.surfshark.com
Dallas:
us-dal.prod.surfshark.com
Las Vegas:
us-las.prod.surfshark.com
Los Angeles:
us-lax.prod.surfshark.com
Miami:
us-mia.prod.surfshark.com
New York City:
us-nyc.prod.surfshark.com
Phoenix:
us-phx.prod.surfshark.com
San Fransisco:
us-sfo.prod.surfshark.com
Seattle:
us-sea.prod.surfshark.com

DD-WRT Router Setup for Surfshark

Navigate to Services > VPN

Enter Surfshark settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Surfshark connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

None

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
b02cb1d7c6fee5d4f89b8de72b51a8d0
c7b282631d6fc19be1df6ebae9e2779e
6d9f097058a31c97f57f0c35526a44ae
09a01d1284b50b954d9246725a1ead1f
f224a102ed9ab3da0152a15525643b2e
ee226c37041dc55539d475183b889a10
e18bb94f079a4a49888da566b9978346
0ece01daaf93548beea6c827d9674897
e7279ff1a19cb092659e8c1860fbad0d
b4ad0ad5732f1af4655dbd66214e552f
04ed8fd0104e1d4bf99c249ac229ce16
9d9ba22068c6c0ab742424760911d463
6aafb4b85f0c952a9ce4275bc821391a
a65fcd0d2394f006e3fba0fd34c4bc4a
b260f4b45dec3285875589c97d3087c9
134d3a3aa2f904512e85aa2dc2202498
-----END OpenVPN Static key V1-----

Additional Config

remote-cert-tls server
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping-timer-rem
reneg-sec 0
cipher AES-256-GCM
log /tmp/vpn.log

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFTTCCAzWgAwIBAgIJAMs9S3fqwv+mMA0GCSqGSIb3DQEBCwUAMD0xCzAJBgNV
BAYTAlZHMRIwEAYDVQQKDAlTdXJmc2hhcmsxGjAYBgNVBAMMEVN1cmZzaGFyayBS
b290IENBMB4XDTE4MDMxNDA4NTkyM1oXDTI4MDMxMTA4NTkyM1owPTELMAkGA1UE
BhMCVkcxEjAQBgNVBAoMCVN1cmZzaGFyazEaMBgGA1UEAwwRU3VyZnNoYXJrIFJv
b3QgQ0EwggIiMA0GCSqGSIb3DQEBAQUAA4ICDwAwggIKAoICAQDEGMNj0aisM63o
SkmVJyZPaYX7aPsZtzsxo6m6p5Wta3MGASoryRsBuRaH6VVa0fwbI1nw5ubyxkua
Na4v3zHVwuSq6F1p8S811+1YP1av+jqDcMyojH0ujZSHIcb/i5LtaHNXBQ3qN48C
c7sqBnTIIFpmb5HthQ/4pW+a82b1guM5dZHsh7q+LKQDIGmvtMtO1+NEnmj81BAp
FayiaD1ggvwDI4x7o/Y3ksfWSCHnqXGyqzSFLh8QuQrTmWUm84YHGFxoI1/8AKdI
yVoB6BjcaMKtKs/pbctk6vkzmYf0XmGovDKPQF6MwUekchLjB5gSBNnptSQ9kNgn
TLqi0OpSwI6ixX52Ksva6UM8P01ZIhWZ6ua/T/tArgODy5JZMW+pQ1A6L0b7egIe
ghpwKnPRG+5CzgO0J5UE6gv000mqbmC3CbiS8xi2xuNgruAyY2hUOoV9/BuBev8t
tE5ZCsJH3YlG6NtbZ9hPc61GiBSx8NJnX5QHyCnfic/X87eST/amZsZCAOJ5v4EP
SaKrItt+HrEFWZQIq4fJmHJNNbYvWzCE08AL+5/6Z+lxb/Bm3dapx2zdit3x2e+m
iGHekuiE8lQWD0rXD4+T+nDRi3X+kyt8Ex/8qRiUfrisrSHFzVMRungIMGdO9O/z
CINFrb7wahm4PqU2f12Z9TRCOTXciQIDAQABo1AwTjAdBgNVHQ4EFgQUYRpbQwyD
ahLMN3F2ony3+UqOYOgwHwYDVR0jBBgwFoAUYRpbQwyDahLMN3F2ony3+UqOYOgw
DAYDVR0TBAUwAwEB/zANBgkqhkiG9w0BAQsFAAOCAgEAn9zV7F/XVnFNZhHFrt0Z
S1Yqz+qM9CojLmiyblMFh0p7t+Hh+VKVgMwrz0LwDH4UsOosXA28eJPmech6/bjf
ymkoXISy/NUSTFpUChGO9RabGGxJsT4dugOw9MPaIVZffny4qYOc/rXDXDSfF2b+
303lLPI43y9qoe0oyZ1vtk/UKG75FkWfFUogGNbpOkuz+et5Y0aIEiyg0yh6/l5Q
5h8+yom0HZnREHhqieGbkaGKLkyu7zQ4D4tRK/mBhd8nv+09GtPEG+D5LPbabFVx
KjBMP4Vp24WuSUOqcGSsURHevawPVBfgmsxf1UCjelaIwngdh6WfNCRXa5QQPQTK
ubQvkvXONCDdhmdXQccnRX1nJWhPYi0onffvjsWUfztRypsKzX4dvM9k7xnIcGSG
EnCC4RCgt1UiZIj7frcCMssbA6vJ9naM0s7JF7N3VKeHJtqe1OCRHMYnWUZt9vrq
X6IoIHlZCoLlv39wFW9QNxelcAOCVbD+19MZ0ZXt7LitjIqe7yF5WxDQN4xru087
FzQ4Hfj7eH1SNLLyKZkA1eecjmRoi/OoqAt7afSnwtQLtMUc2bQDg6rHt5C0e4dC
LqP/9PGZTSJiwmtRHJ/N5qYWIh9ju83APvLm/AGBTR2pXmj9G3KdVOkpIC7L35dI
623cSEC3Q3UZutsEm/UplsM=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Surfshark connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
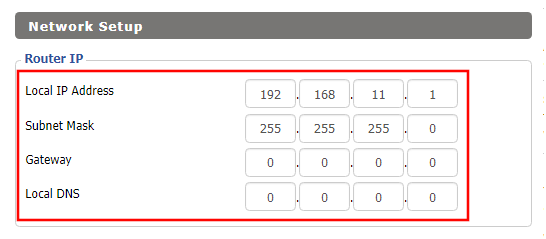
How to change the Surfshark server

  1. Visit the Surfshark Manual setup page and scroll down to Section 3.
  2. Copy and paste one of the server IP Address into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Windscribe Manual OpenVPN Setup

TeamFlashRouters · Apr 25, 2019 ·

Preparing for Manual Windscribe Setup

Verify your Windscribe login information

If you are not already an Windscribe user Sign Up Now.

1. Log in to your account on the Windscribe website.

2. Click on the Download link at the top of the page.

3. Scroll down to the Config Generators section and Click on the OpenVPN link.

Windscribe Website - Generate OpenVPN Configuration Files

4. Click on Get Credentials and copy the Username and Password. This information will be used later on in the configuration.

Windscribe Website OpenVPN Specific Username and Password

Windscribe Server Addresses

United States

US East:
us-east.windscribe.com
US West:
us-west.windscribe.com
US Windflix:
wf-us.windscribe.com

Canada

Canada:
ca.windscribe.com
Canada West:
ca-west.windscribe.com

Additional Servers

Australia:
au.windscribe.com
Austria:
at.windscribe.com
Belgium:
be.windscribe.com
Brazil:
br.windscribe.com
Bulgaria:
bg.windscribe.com
Czech Republic:
cz.windscribe.com
Denmark:
dk.windscribe.com
Egypt:
eg.windscribe.com
Finland:
fi.windscribe.com
France:
fr.windscribe.com
Germany:
de.windscribe.com
Hong Kong:
hk.windscribe.com
Hungary:
hu.windscribe.com
India:
in.windscribe.com
Ireland:
ie.windscribe.com
Italy:
it.windscribe.com
Japan:
jp.windscribe.com
Latvia:
lv.windscribe.com
Luxemburg:
lu.windscribe.com
Malaysia:
my.windscribe.com
Mexico:
mx.windscribe.com
Netherlands:
nl.windscribe.com
Norway:
no.windscribe.com
Poland:
pl.windscribe.com
Romania:
ro.windscribe.com
Russia:
ru.windscribe.com
Singapore:
ch.windscribe.com
South Africa:
za.windscribe.com
South Korea:
kr.windscribe.com
Spain:
es.windscribe.com
Sweden:
se.windscribe.com
Switzerland:
ch.windscribe.com
Taiwan:
tw.windscribe.com
Turkey:
tr.windscribe.com
Ukraine:
ua.windscribe.com
United Kingdom:
uk.windscribe.com

DD-WRT Router Setup for Windscribe

Navigate to Services > VPN

Enter Windscribe settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and Paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change Windscribe connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

User Pass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
5801926a57ac2ce27e3dfd1dd6ef8204
2d82bd4f3f0021296f57734f6f1ea714
a6623845541c4b0c3dea0a050fe6746c
b66dfab14cda27e5ae09d7c155aa554f
399fa4a863f0e8c1af787e5c602a801d
3a2ec41e395a978d56729457fe6102d7
d9e9119aa83643210b33c678f9d4109e
3154ac9c759e490cb309b319cf708cae
83ddadc3060a7a26564d1a24411cd552
fe6620ea16b755697a4fc5e6e9d0cfc0
c5c4a1874685429046a424c026db672e
4c2c492898052ba59128d46200b40f88
0027a8b6610a4d559bdc9346d33a0a6b
08e75c7fd43192b162bfd0aef0c716b3
1584827693f676f9a5047123466f0654
eade34972586b31c6ce7e395f4b478cb
-----END OpenVPN Static key V1-----

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFozCCA4ugAwIBAgIBATANBgkqhkiG9w0BAQ0FADBAMQswCQYDVQQGEwJDSDEV
MBMGA1UEChMMUHJvdG9uVlBOIEFHMRowGAYDVQQDExFQcm90b25WUE4gUm9vdCBD
QTAeFw0xNzAyMTUxNDM4MDBaFw0yNzAyMTUxNDM4MDBaMEAxCzAJBgNVBAYTAkNI
MRUwEwYDVQQKEwxQcm90b25WUE4gQUcxGjAYBgNVBAMTEVByb3RvblZQTiBSb290
IENBMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAt+BsSsZg7+AuqTq7
vDbPzfygtl9f8fLJqO4amsyOXlI7pquL5IsEZhpWyJIIvYybqS4s1/T7BbvHPLVE
wlrq8A5DBIXcfuXrBbKoYkmpICGc2u1KYVGOZ9A+PH9z4Tr6OXFfXRnsbZToie8t
2Xjv/dZDdUDAqeW89I/mXg3k5x08m2nfGCQDm4gCanN1r5MT7ge56z0MkY3FFGCO
qRwspIEUzu1ZqGSTkG1eQiOYIrdOF5cc7n2APyvBIcfvp/W3cpTOEmEBJ7/14RnX
nHo0fcx61Inx/6ZxzKkW8BMdGGQF3tF6u2M0FjVN0lLH9S0ul1TgoOS56yEJ34hr
JSRTqHuar3t/xdCbKFZjyXFZFNsXVvgJu34CNLrHHTGJj9jiUfFnxWQYMo9UNUd4
a3PPG1HnbG7LAjlvj5JlJ5aqO5gshdnqb9uIQeR2CdzcCJgklwRGCyDT1pm7eoiv
WV19YBd81vKulLzgPavu3kRRe83yl29It2hwQ9FMs5w6ZV/X6ciTKo3etkX9nBD9
ZzJPsGQsBUy7CzO1jK4W01+u3ItmQS+1s4xtcFxdFY8o/q1zoqBlxpe5MQIWN6Qa
lryiET74gMHE/S5WrPlsq/gehxsdgc6GDUXG4dk8vn6OUMa6wb5wRO3VXGEc67IY
m4mDFTYiPvLaFOxtndlUWuCruKcCAwEAAaOBpzCBpDAMBgNVHRMEBTADAQH/MB0G
A1UdDgQWBBSDkIaYhLVZTwyLNTetNB2qV0gkVDBoBgNVHSMEYTBfgBSDkIaYhLVZ
TwyLNTetNB2qV0gkVKFEpEIwQDELMAkGA1UEBhMCQ0gxFTATBgNVBAoTDFByb3Rv
blZQTiBBRzEaMBgGA1UEAxMRUHJvdG9uVlBOIFJvb3QgQ0GCAQEwCwYDVR0PBAQD
AgEGMA0GCSqGSIb3DQEBDQUAA4ICAQCYr7LpvnfZXBCxVIVc2ea1fjxQ6vkTj0zM
htFs3qfeXpMRf+g1NAh4vv1UIwLsczilMt87SjpJ25pZPyS3O+/VlI9ceZMvtGXd
MGfXhTDp//zRoL1cbzSHee9tQlmEm1tKFxB0wfWd/inGRjZxpJCTQh8oc7CTziHZ
ufS+Jkfpc4Rasr31fl7mHhJahF1j/ka/OOWmFbiHBNjzmNWPQInJm+0ygFqij5qs
51OEvubR8yh5Mdq4TNuWhFuTxpqoJ87VKaSOx/Aefca44Etwcj4gHb7LThidw/ky
zysZiWjyrbfX/31RX7QanKiMk2RDtgZaWi/lMfsl5O+6E2lJ1vo4xv9pW8225B5X
eAeXHCfjV/vrrCFqeCprNF6a3Tn/LX6VNy3jbeC+167QagBOaoDA01XPOx7Odhsb
Gd7cJ5VkgyycZgLnT9zrChgwjx59JQosFEG1DsaAgHfpEl/N3YPJh68N7fwN41Cj
zsk39v6iZdfuet/sP7oiP5/gLmA/CIPNhdIYxaojbLjFPkftVjVPn49RqwqzJJPR
N8BOyb94yhQ7KO4F3IcLT/y/dsWitY0ZH4lCnAVV/v2YjWAWS3OWyC8BFx/Jmc3W
DK/yPwECUcPgHIeXiRjHnJt0Zcm23O2Q3RphpU+1SO3XixsXpOVOYP6rJIXW9bMZ
A1gTTlpi7A==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Windscribe VPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
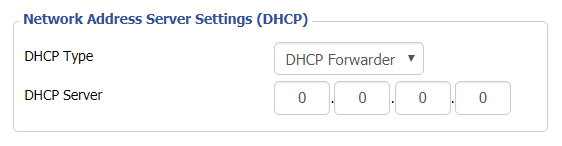
How to change the Windscribe server

  1. Copy and paste the server IP Address from the server list above into the Server IP/Name field.
  2. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark Setup for Privacy Hero

TeamFlashRouters · Sep 23, 2025 ·

Privacy Hero supports Surfshark through WireGuard and OpenVPN using the Custom VPN provider option.

WireGuard is recommended for most users. It requires a Surfshark WireGuard key pair and a downloaded server configuration file. OpenVPN uses a downloaded .ovpn file and Surfshark’s separate Manual Setup credentials, not your usual Surfshark login email and password.

Privacy Hero is cloud-managed. You can change these settings from any computer, smartphone, or tablet with an internet connection; you do not need to be on the Privacy Hero WiFi to configure the VPN.

Choose Your Surfshark Setup

Select the connection method or instructions you need.

WireGuard Setup →Recommended · Key pair and server fileOpenVPN Setup →Manual credentials and UDP .ovpn fileUpload WireGuard →Import your configuration into Privacy HeroUpload OpenVPN →Add the file and service credentialsVerify Connection →Check your VPN IP and locationTroubleshooting →Fix connection failures and no internet

Surfshark WireGuard Setup (Recommended)

WireGuard uses a key pair for authentication. A separate Surfshark username and password is not needed for the WireGuard configuration.

Create or Select Your Surfshark WireGuard Key Pair

  1. Sign in to your Surfshark account.
  2. Open VPN → Manual Setup, choose the Router setup option, and select WireGuard.
  3. If you already registered a key pair with Surfshark, select I have a key pair and follow the prompts to register your public key. Otherwise, select I don’t have a key pair.
  4. If generating a new key pair, enter a name and choose Generate a new key pair. Save the generated keys securely when prompted.

Important: Your WireGuard private key is sensitive. Do not publish or send it in a support ticket. Surfshark notes that you may not be able to view the generated keys again after leaving that screen.

Download a Surfshark WireGuard Server File

  1. After setting up the key pair, select Choose a location or open the Locations section.
  2. Choose an available Surfshark server and download its WireGuard configuration file to your device.

Do not download the WireGuard configuration before setting up the key pair. Surfshark warns that a file downloaded too early can be missing the required key information. For more detail, see Surfshark’s manual WireGuard router instructions.

Upload WireGuard to Privacy Hero

  1. Open app.privacyhero.com and log in to your Privacy Hero account.
  2. Open the VPN section, click Change, and choose Custom as the VPN provider.
  3. Select WireGuard and upload the Surfshark WireGuard configuration file you downloaded.
  4. Click Save and allow Privacy Hero to establish the connection. Confirm the VPN status shows Connected.
Privacy Hero Custom WireGuard configuration and file upload panel

Surfshark OpenVPN Setup

OpenVPN is an alternative to WireGuard. It requires a Surfshark Manual Setup username and password and a downloaded OpenVPN configuration (.ovpn) file.

Get Your Surfshark OpenVPN Credentials

  1. Sign in to your Surfshark account.
  2. Open VPN → Manual Setup, choose Router, and select OpenVPN.
  3. Open the Credentials tab. If credentials are not yet available, select Generate credentials.
  4. Copy the Manual Setup username and password, or keep the tab open to enter them into Privacy Hero later.

Important: These are not your regular Surfshark website email and password. Keep the service credentials private.

Download a Surfshark OpenVPN Server File

  1. In Surfshark’s OpenVPN Manual Setup area, open the Locations tab.
  2. Select a country or server and download its UDP .ovpn configuration file. UDP is the recommended starting option; a TCP configuration may be worth trying later if needed.

Download a new .ovpn file whenever you want to switch to a different Surfshark server location. See Surfshark’s manual server selection instructions.

Upload OpenVPN to Privacy Hero

  1. Open app.privacyhero.com, sign in, and select the VPN section.
  2. Click Change, select Custom, and choose OpenVPN.
  3. Upload the Surfshark UDP .ovpn file you downloaded.
  4. Enter the Surfshark Manual Setup username and password into the Custom OpenVPN fields.
  5. Click Save, then confirm the VPN status shows Connected.
Privacy Hero Custom OpenVPN screen with configuration file upload and username and password fields

Verify Your Surfshark Connection

Privacy Hero showing Connected confirms the router connection status. Test a device on the Privacy Hero network to confirm it is using Surfshark.

  1. Connect your device to the Privacy Hero WiFi or LAN.
  2. Disconnect the Surfshark app or any other VPN app running directly on the testing device.
  3. Open a fresh private/incognito browser window.
  4. Visit Surfshark’s IP address checker.
  5. Confirm the displayed public IP and approximate location correspond to your selected Surfshark server.

You can change Privacy Hero settings while using another WiFi network or cellular data, but the device performing this VPN IP test must be connected to Privacy Hero. Avoid running a separate VPN app on the same testing device, as that creates a double-VPN connection.

Streaming Relocation and Your VPN Location

When Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation region instead of the Surfshark VPN server region. See Privacy Hero Streaming Relocation.


Surfshark Not Connecting?

If Privacy Hero displays Failed, remains on Connecting, or reports a timeout, try these steps:

  1. Confirm your Surfshark subscription is active and that Custom is selected as the VPN provider in Privacy Hero.
  2. If using WireGuard, confirm that the key pair was created or registered before downloading the server file. If necessary, generate a new key pair, download a fresh configuration, and upload it again.
  3. If using OpenVPN, double-check your separate Surfshark Manual Setup username and password, not your regular website login.
  4. Download a fresh server configuration for another available Surfshark location and try again.
  5. If OpenVPN UDP continues to fail, try a Surfshark TCP .ovpn configuration file to check for a protocol-specific issue.
  6. Temporarily disable the VPN Kill Switch while checking whether internet access works without the VPN, then restore your preferred Kill Switch setting.

No Internet After Surfshark Disconnects?

The VPN Kill Switch may intentionally block normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

If other Privacy Hero devices display the expected Surfshark VPN IP, review the affected device for VPN apps, iCloud Private Relay, Private DNS, proxy settings, antivirus filtering, or other security software. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

IVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual IVPN Setup

Verify your IVPN login information

If you are not already an IVPN user Sign Up Now.

Log in to your account on the IVPN website.

FlashRouter Privacy App - IVPN Login

Locate and Copy the Username displayed on the VPN Accounts page.

FlashRouters DD-WRT Privacy APP IVPN OpenVPN Specific Username and Password

IVPN Server Addresses

View a full list of IVPN servers.

United States

Atlanta:
us-ga.gw.ivpn.net

Dallas:
us-tx.gw.ivpn.net

Los Angeles
:
us-ca.gw.ivpn.net

Miami
:
us-fl.gw.ivpn.net

New Jersey
:
us-nj.gw.ivpn.net

Salt Lake City
:
us-ut.gw.ivpn.net

DD-WRT Router Setup for IVPN

Navigate to Services > VPN

Enter IVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PureVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443 for TCP
2049 for UDP

Tunnel Device

TUN

Tunnel Protocol

TCP or UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you noted from the Home page above.
eg. ivpn1234567

Password

Enter the Password you successfully logged in to your IVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
ac470c93ff9f5602a8aab37dee84a528
14d10f20490ad23c47d5d82120c1bf85
9e93d0696b455d4a1b8d55d40c2685c4
1ca1d0aef29a3efd27274c4ef09020a3
978fe45784b335da6df2d12db97bbb83
8416515f2a96f04715fd28949c6fe296
a925cfada3f8b8928ed7fc963c156327
2f5cf46e5e1d9c845d7703ca881497b7
e6564a9d1dea9358adffd435295479f4
7d5298fabf5359613ff5992cb57ff081
a04dfb81a26513a6b44a9b5490ad265f
8a02384832a59cc3e075ad545461060b
7bcab49bac815163cb80983dd51d5b1f
d76170ffd904d8291071e96efc3fb777
856c717b148d08a510f5687b8a8285dc
ffe737b98916dd15ef6235dee4266d3b
-----END OpenVPN Static key V1-----

Additional Config

tls-client
tls-cipher TLS-DHE-RSA-WITH-AES-256-CBC-SHA
resolv-retry infinite
keepalive 10 60
nobind
persist-key
persist-tun
persist-remote-ip
verb 3

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGoDCCBIigAwIBAgIJAJjvUclXmxtnMA0GCSqGSIb3DQEBCwUAMIGMMQswCQYD
VQQGEwJDSDEPMA0GA1UECAwGWnVyaWNoMQ8wDQYDVQQHDAZadXJpY2gxETAPBgNV
BAoMCElWUE4ubmV0MQ0wCwYDVQQLDARJVlBOMRgwFgYDVQQDDA9JVlBOIFJvb3Qg
Q0EgdjIxHzAdBgkqhkiG9w0BCQEWEHN1cHBvcnRAaXZwbi5uZXQwHhcNMjAwMjI2
MTA1MjI5WhcNNDAwMjIxMTA1MjI5WjCBjDELMAkGA1UEBhMCQ0gxDzANBgNVBAgM
Blp1cmljaDEPMA0GA1UEBwwGWnVyaWNoMREwDwYDVQQKDAhJVlBOLm5ldDENMAsG
A1UECwwESVZQTjEYMBYGA1UEAwwPSVZQTiBSb290IENBIHYyMR8wHQYJKoZIhvcN
AQkBFhBzdXBwb3J0QGl2cG4ubmV0MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIIC
CgKCAgEAxHVeaQN3nYCLnGoEg6cY44AExbQ3W6XGKYwC9vI+HJbb1o0tAv56ryvc
6eS6BdG5q9M8fHaHEE/jw9rtznioiXPwIEmqMqFPA9k1oRIQTGX73m+zHGtRpt9P
4tGYhkvbqnN0OGI0H+j9R6cwKi7KpWIoTVibtyI7uuwgzC2nvDzVkLi63uvnCKRX
cGy3VWC06uWFbqI9+QDrHHgdJA1F0wRfg0Iac7TE75yXItBMvNLbdZpge9SmplYW
FQ2rVPG+n75KepJ+KW7PYfTP4Mh3R8A7h3/WRm03o3spf2aYw71t44voZ6agvslv
wqGyczDytsLUny0U2zR7/mfEAyVbL8jqcWr2Df0m3TA0WxwdWvA51/RflVk9G96L
ncUkoxuBT56QSMtdjbMSqRgLfz1iPsglQEaCzUSqHfQExvONhXtNgy+Pr2+wGrEu
SlLMee7aUEMTFEX/vHPZanCrUVYf5Vs8vDOirZjQSHJfgZfwj3nL5VLtIq6ekDhS
AdrqCTILP3V2HbgdZGWPVQxl4YmQPKo0IJpse5Kb6TF2o0i90KhORcKg7qZA40sE
bYLEwqTM7VBs1FahTXsOPAoMa7xZWV1TnigF5pdVS1l51dy5S8L4ErHFEnAp242B
DuTClSLVnWDdofW0EZ0OkK7V9zKyVl75dlBgxMIS0y5MsK7IWicCAwEAAaOCAQEw
gf4wHQYDVR0OBBYEFHUDcMOMo35yg2A/v0uYfkDE11CXMIHBBgNVHSMEgbkwgbaA
FHUDcMOMo35yg2A/v0uYfkDE11CXoYGSpIGPMIGMMQswCQYDVQQGEwJDSDEPMA0G
A1UECAwGWnVyaWNoMQ8wDQYDVQQHDAZadXJpY2gxETAPBgNVBAoMCElWUE4ubmV0
MQ0wCwYDVQQLDARJVlBOMRgwFgYDVQQDDA9JVlBOIFJvb3QgQ0EgdjIxHzAdBgkq
hkiG9w0BCQEWEHN1cHBvcnRAaXZwbi5uZXSCCQCY71HJV5sbZzAMBgNVHRMEBTAD
AQH/MAsGA1UdDwQEAwIBBjANBgkqhkiG9w0BAQsFAAOCAgEAABAjRMJy+mXFLezA
Z8iUgxOjNtSqkCv1aU78K1XkYUzbwNNrSIVGKfP9cqOEiComXY6nniws7QEV2IWi
lcdPKm0x57recrr9TExGGOTVGB/WdmsFfn0g/HgmxNvXypzG3qulBk4qQTymICds
l9vIPb1l9FSjKw1KgUVuCPaYq7xiXbZ/kZdZX49xeKtoDBrXKKhXVYoWus/S+k2I
S8iCxvcp599y7LQJg5DOGlbaxFhsW4R+kfGOaegyhPvpaznguv02i7NLd99XqJhp
v2jTUF5F3T23Z4KkL/wTo4zxz09DKOlELrE4ai++ilCt/mXWECXNOSNXzgszpe6W
As0h9R++sH+AzJyhBfIGgPUTxHHHvxBVLj3k6VCgF7mRP2Y+rTWa6d8AGI2+Raey
V9DVVH9UeSoU0Hv2JHiZL6dRERnyg8dyzKeTCke8poLIjXF+gyvI+22/xsL8jcNH
i9Kji3Vpc3i0Mxzx3gu2N+PL71CwJilgqBgxj0firr3k8sFcWVSGos6RJ3IvFvTh
xYx0p255WrWM01fR9TktPYEfjDT9qpIJ8OrGlNOhWhYj+a45qibXDpaDdb/uBEmf
2sSXNifjSeUyqu6cKfZvMqB7pS3l/AhuAOTT80E4sXLEoDxkFD4C78swZ8wyWRKw
sWGIGABGAHwXEAoDiZ/jjFrEZT0=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful IVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to IVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
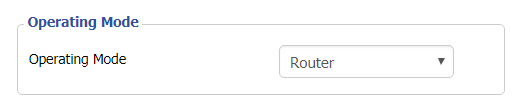
How to change the IVPN server

  1. Copy the new IVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 8, 2019 ·

Preparing for Manual NordVPN Setup

Verify your NordVPN login information

If you are not already an NordVPN user Sign Up Now.

Log in to your account on the NordVPN website.

NordVPN Server Addresses

For a NordVPN server recommendation visit their Recommend Server page.

Once you have selected the server you want to connect to, download the UDP .ovpn file containing the Server IP Address, TLS Auth Key, and CA Cert referenced below.

Open the .ovpn file that is downloaded to your computer with NotePad++ for Windows or TextEdit for Apple. You will only need the Server IP Address, TLS Auth Key, and CA Cert from this file. All NordVPN servers and .ovpn files have different IP Addresses, keys, and certificates.

DD-WRT Router Setup for NordVPN

Navigate to Services > VPN

Enter NordVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote 206.226.72.27 1194
206.226.72.27 is your NordVPN server IP address. Enter the IP Address in this field.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your NordVPN account with.

Password

Enter the Password you successfully logged in to your NordVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

In the .ovpn file copy and paste all contents in between the <tls-auth> and </tls-auth> lines from your .ovpn file starting and ending with:
—–BEGIN OpenVPN Static key V1—–
…
—–END OpenVPN Static key V1—–

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

In the .ovpn file Copy and Paste all contents in between the <ca> and </ca> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful NordVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit NordVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
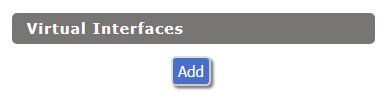
How to change the NordVPN server

  1. Download and open a new .ovpn file from NordVPN.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the TLS Auth Key into the TLS Auth Key field.
  4. Copy and paste the CA Cert into the CA Cert field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN Setup Guide for GL.iNet Routers

Dave · Mar 23, 2026 ·

You can connect to ProtonVPN on your GL.iNet router using Wireguard or OpenVPN.

Quick Options

  • Wireguard: Download your preferred server .conf configuration file from the ProtonVPN website.

  • OpenVPN: Download your preferred server .ovpn configuration file from the ProtonVPN website.

:point_right: If you are not already a ProtonVPN user Sign Up Now.

ProtonVPN Wireguard Setup for GLiNet (Recommended)

1. Login to your ProtonVPN account and go to the Downloads section of your ProtonVPN account page

2. Scroll down to find the WireGuard configuration section. Name your configuration and then select Router as the platform, and select Standard server configs.

3. Click Create button to choose the recommended server or scroll down to choose and Download any of the available server files from the list.

4.  Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

5. Navigate to the VPN tab and select WireGuard Client then click + New Group and name your connection and click the check to save.

6. Upload the configuration file and click Apply.

7. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

8. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

ProtonVPN OpenVPN Setup for GLiNet

1. Log in to your ProtonVPN account and navigate to the Account tab. Scroll down to find your OpenVPN specific Username and Password.

2. Go to the Downloads section of your ProtonVPN account page

ProtonVPN Downloads

3. Scroll down to find the OpenVPN configuration Files. Select Router as the platform, UDP as the protocol, and select Standard server configs. Choose your preferred country and download the configuration file.

4. Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

5. Navigate to the VPN tab and select OpenVPN Client.

GL.iNet VPN OpenVPN Client

6. Select Add Manually then click + New Group and name your connection and click the check to save.

7. Upload the configuration file and input your username and password, click Apply.

8. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

9. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

  1. You should now see information appear in the Server Address, Server Listen Port, Traffic Statistics, and Client Virtual IP areas.
  2. Visit ProtonVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

🚫📱Do not run ProtonVPN apps on devices connected to your ProtonVPN router. Using the app at the same time as the router VPN may cause conflicts and connection issues.

Still having issues?

Feel free to submit a ticket and we will get back to you as soon as possible.

PrivateInternetAccess (PIA) Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual PIA Setup

Verify your PIA login information

If you are not already a PIA user Sign Up Now.

Log in to your account on the PIA website.

FlashRouters Privacy App - PIA Login

PIA Server Addresses

The below servers are the only servers compatible with PIA router connections. Dedicated IP Addresses are not able to connect via routers.

United States

us-california.privacy.network
us-newjersey.privacy.network
us-chicago.privacy.network
us-texas.privacy.network
us-florida.privacy.network
us-seattle.privacy.network
us3.privacy.network
us-siliconvalley.privacy.network
us-newyorkcity.privacy.network
us-washingtondc.privacy.network
us-atlanta.privacy.network
us-houston.privacy.network
us-denver.privacy.network

United Kingdom

uk-london.privacy.network
uk-manchester.privacy.network

Canada

ca-toronto.privacy.network
ca-montreal.privacy.network

Australia

au-sydney.privacy.network
aus-melbourne.privacy.network
aus-perth.privacy.network

Germany

de-berlin.privacy.network
de-frankfurt.privacy.network

Rest of the World

ae.privacy.network
austria.privacy.network
dz.privacy.network
ad.privacy.network
ar.privacy.network
yerevan.privacy.network
bahamas.privacy.network
bangladesh.privacy.network
brussels.privacy.network
sofia.privacy.network
cambodia.privacy.network
china.privacy.network
cyprus.privacy.network
czech.privacy.network
denmark.privacy.network
egypt.privacy.network
fi.privacy.network
france.privacy.network
georgia.privacy.network
greenland.privacy.network
hungary.privacy.network
is.privacy.network
in.privacy.network
iran.privacy.network
ireland.privacy.network
man.privacy.network
israel.privacy.network
italy.privacy.network
japan.privacy.network
kazakhstan.privacy.network
liechtenstein.privacy.network
lu.privacy.network
macau.privacy.network
malta.privacy.network
mexico.privacy.network
md.privacy.network
monaco.privacy.network
mongolia.privacy.network
montenegro.privacy.network
morocco.privacy.network
nl-amsterdam.privacy.network
nz.privacy.network
nigeria.privacy.network
no.privacy.network
panama.privacy.network
philippines.privacy.network
poland.privacy.network
qatar.privacy.network
ro.privacy.network
rs.privacy.network
saudiarabia.privacy.network
spain.privacy.network
srilanka.privacy.network
sweden.privacy.network
swiss.privacy.network
sg.privacy.network
tr.privacy.network
taiwan.privacy.network
ua.privacy.network
venezuela.privacy.network
vietnam.privacy.network
za.privacy.network

DD-WRT Router Setup for PIA

Navigate to Services > VPN

PIA offers two different Encryption levels.
Default Encryption (AES-128) typically provides faster speeds.
Strong Encryption (AES-256) provides stronger encryption.
Follow the table below of the one that fits your needs.

Enter PIA settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1198

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA1

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFqzCCBJOgAwIBAgIJAKZ7D5Yv87qDMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzM1
MThaFw0zNDA0MTIxNzM1MThaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAPXD
L1L9tX6DGf36liA7UBTy5I869z0UVo3lImfOs/GSiFKPtInlesP65577nd7UNzzX
lH/P/CnFPdBWlLp5ze3HRBCc/Avgr5CdMRkEsySL5GHBZsx6w2cayQ2EcRhVTwWp
cdldeNO+pPr9rIgPrtXqT4SWViTQRBeGM8CDxAyTopTsobjSiYZCF9Ta1gunl0G/
8Vfp+SXfYCC+ZzWvP+L1pFhPRqzQQ8k+wMZIovObK1s+nlwPaLyayzw9a8sUnvWB
/5rGPdIYnQWPgoNlLN9HpSmsAcw2z8DXI9pIxbr74cb3/HSfuYGOLkRqrOk6h4RC
OfuWoTrZup1uEOn+fw8CAwEAAaOCAVQwggFQMB0GA1UdDgQWBBQv63nQ/pJAt5tL
y8VJcbHe22ZOsjCCAR8GA1UdIwSCARYwggESgBQv63nQ/pJAt5tLy8VJcbHe22ZO
sqGB7qSB6zCB6DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAkNBMRMwEQYDVQQHEwpM
b3NBbmdlbGVzMSAwHgYDVQQKExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4G
A1UECxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBAMTF1ByaXZhdGUg
SW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQpExdQcml2YXRlIEludGVybmV0IEFjY2Vz
czEvMC0GCSqGSIb3DQEJARYgc2VjdXJlQHByaXZhdGVpbnRlcm5ldGFjY2Vzcy5j
b22CCQCmew+WL/O6gzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBDQUAA4IBAQAn
a5PgrtxfwTumD4+3/SYvwoD66cB8IcK//h1mCzAduU8KgUXocLx7QgJWo9lnZ8xU
ryXvWab2usg4fqk7FPi00bED4f4qVQFVfGfPZIH9QQ7/48bPM9RyfzImZWUCenK3
7pdw4Bvgoys2rHLHbGen7f28knT2j/cbMxd78tQc20TIObGjo8+ISTRclSTRBtyC
GohseKYpTS9himFERpUgNtefvYHbn70mIOzfOJFTVqfrptf9jXa9N8Mpy3ayfodz
1wiqdteqFXkTYoSDctgKMiZ6GdocK9nMroQipIQtpnwd4yBDWIyC6Bvlkrq5TQUt
YDQ8z9v+DMO6iwyIDRiU
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter PIA settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1197

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIHqzCCBZOgAwIBAgIJAJ0u+vODZJntMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzQw
MzNaFw0zNDA0MTIxNzQwMzNaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBALVk
hjumaqBbL8aSgj6xbX1QPTfTd1qHsAZd2B97m8Vw31c/2yQgZNf5qZY0+jOIHULN
De4R9TIvyBEbvnAg/OkPw8n/+ScgYOeH876VUXzjLDBnDb8DLr/+w9oVsuDeFJ9K
V2UFM1OYX0SnkHnrYAN2QLF98ESK4NCSU01h5zkcgmQ+qKSfA9Ny0/UpsKPBFqsQ
25NvjDWFhCpeqCHKUJ4Be27CDbSl7lAkBuHMPHJs8f8xPgAbHRXZOxVCpayZ2SND
fCwsnGWpWFoMGvdMbygngCn6jA/W1VSFOlRlfLuuGe7QFfDwA0jaLCxuWt/BgZyl
p7tAzYKR8lnWmtUCPm4+BtjyVDYtDCiGBD9Z4P13RFWvJHw5aapx/5W/CuvVyI7p
Kwvc2IT+KPxCUhH1XI8ca5RN3C9NoPJJf6qpg4g0rJH3aaWkoMRrYvQ+5PXXYUzj
tRHImghRGd/ydERYoAZXuGSbPkm9Y/p2X8unLcW+F0xpJD98+ZI+tzSsI99Zs5wi
jSUGYr9/j18KHFTMQ8n+1jauc5bCCegN27dPeKXNSZ5riXFL2XX6BkY68y58UaNz
meGMiUL9BOV1iV+PMb7B7PYs7oFLjAhh0EdyvfHkrh/ZV9BEhtFa7yXp8XR0J6vz
1YV9R6DYJmLjOEbhU8N0gc3tZm4Qz39lIIG6w3FDAgMBAAGjggFUMIIBUDAdBgNV
HQ4EFgQUrsRtyWJftjpdRM0+925Y6Cl08SUwggEfBgNVHSMEggEWMIIBEoAUrsRt
yWJftjpdRM0+925Y6Cl08SWhge6kgeswgegxCzAJBgNVBAYTAlVTMQswCQYDVQQI
EwJDQTETMBEGA1UEBxMKTG9zQW5nZWxlczEgMB4GA1UEChMXUHJpdmF0ZSBJbnRl
cm5ldCBBY2Nlc3MxIDAeBgNVBAsTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAw
HgYDVQQDExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UEKRMXUHJpdmF0
ZSBJbnRlcm5ldCBBY2Nlc3MxLzAtBgkqhkiG9w0BCQEWIHNlY3VyZUBwcml2YXRl
aW50ZXJuZXRhY2Nlc3MuY29tggkAnS7684Nkme0wDAYDVR0TBAUwAwEB/zANBgkq
hkiG9w0BAQ0FAAOCAgEAJsfhsPk3r8kLXLxY+v+vHzbr4ufNtqnL9/1Uuf8NrsCt
pXAoyZ0YqfbkWx3NHTZ7OE9ZRhdMP/RqHQE1p4N4Sa1nZKhTKasV6KhHDqSCt/dv
Em89xWm2MVA7nyzQxVlHa9AkcBaemcXEiyT19XdpiXOP4Vhs+J1R5m8zQOxZlV1G
tF9vsXmJqWZpOVPmZ8f35BCsYPvv4yMewnrtAC8PFEK/bOPeYcKN50bol22QYaZu
LfpkHfNiFTnfMh8sl/ablPyNY7DUNiP5DRcMdIwmfGQxR5WEQoHL3yPJ42LkB5zs
6jIm26DGNXfwura/mi105+ENH1CaROtRYwkiHb08U6qLXXJz80mWJkT90nr8Asj3
5xN2cUppg74nG3YVav/38P48T56hG1NHbYF5uOCske19F6wi9maUoto/3vEr0rnX
JUp2KODmKdvBI7co245lHBABWikk8VfejQSlCtDBXn644ZMtAdoxKNfR2WTFVEwJ
iyd1Fzx0yujuiXDROLhISLQDRjVVAvawrAtLZWYK31bY7KlezPlQnl/D9Asxe85l
8jO5+0LdJ6VyOs/Hd4w52alDW/MFySDZSfQHMTIc30hLBJ8OnCEIvluVQQ2UQvoW
+no177N9L2Y+M9TcTA62ZyMXShHQGeh20rb4kK8f+iFX8NxtdHVSkxMEFSfDDyQ=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PIA connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
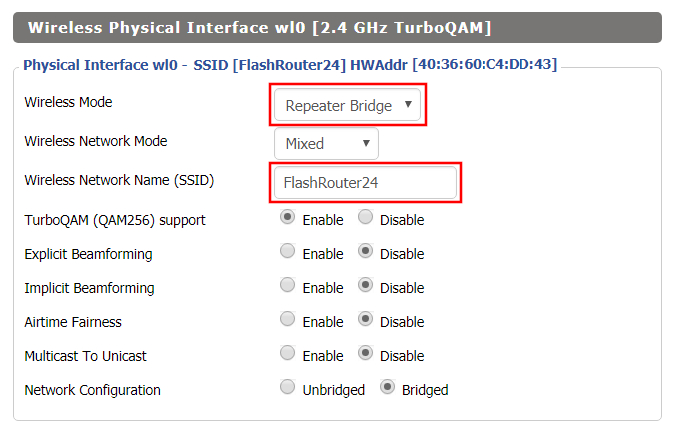
How to change the PIA server

  1. Copy the new PIA server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PureVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual PureVPN Setup

Verify your PureVPN login information

If you are not already an PureVPN user Sign Up Now.

Log in to your account on the PureVPN website.

PureVPN Website Login

Navigate to the Home page and note the VPN username on this page. You will need this specific username later on in the configuration process.
Ex: purevpn0s1234567

PureVPN Server Addresses

View a full list of PureVPN servers.

United States

Miami:
usfl1-ovpn-udp.pointtoserver.com

Seattle:
ussa-ovpn-udp.pointtoserver.com

Houston
:
ustx1-ovpn-tcp.pointtoserver.com

Georgia
:
usga1-ovpn-udp.pointtoserver.com

New Jersey
:
usnj1-ovpn-udp.pointtoserver.com

Washington
:
uswdc1-ovpn-udp.pointtoserver.com

Chicago
:
usil1-ovpn-udp.pointtoserver.com

Phoenix
:
usphx1-ovpn-udp.pointtoserver.com

Los Angeles
:
usla1-ovpn-udp.pointtoserver.com

Virginia
:
vlbr-usvc1-ovpn-udp.pointtoserver.com

San Francisco
:
vlsa-ussf1-ovpn-udp.pointtoserver.com

New York
:
usny1-ovpn-udp.pointtoserver.com

Ohio
:
vleu-usoh1-ovpn-udp.pointtoserver.com

United Kingdom

London:
ukl1-ovpn-udp.pointtoserver.com

Gosport:
ukg1-ovpn-udp.pointtoserver.com

Maidenhead:
ukm1-ovpn-udp.pointtoserver.com

Manchester
:
vlus-uk-man1-ovpn-udp.pointtoserver.com

Leicester
:
vlap-ukle1-ovpn-udp.pointtoserver.com

DD-WRT Router Setup for PureVPN

Navigate to Services > VPN

Enter PureVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PureVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

53

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

Userpass Authentication

Enable

Username

Enter the Username you noted from the Home page above.
Ex: purevpn0s1234567

Password

Enter the Password you successfully logged in to your PureVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
e30af995f56d07426d9ba1f824730521
d4283db4b4d0cdda9c6e8759a3799dcb
7939b6a5989160c9660de0f6125cbb1f
585b41c074b2fe88ecfcf17eab9a33be
1352379cdf74952b588fb161a93e13df
9135b2b29038231e02d657a6225705e6
868ccb0c384ed11614690a1894bfbeb2
74cebf1fe9c2329bdd5c8a40fe882062
4d2ea7540cd79ab76892db51fc371a3a
c5fc9573afecb3fffe3281e61d72e915
79d9b03d8cbf7909b3aebf4d90850321
ee6b7d0a7846d15c27d8290e031e951e
19438a4654663cad975e138f5bc5af89
c737ad822f27e19057731f41e1e254cc
9c95b7175c622422cde9f1f2cfd3510a
dd94498b4d7133d3729dd214a16b27fb
-----END OpenVPN Static key V1-----

Additional Config

tls-cipher “DEFAULT:@SECLEVEL=0”

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIEoTCCA4mgAwIBAgIJANysBdFD6U2oMA0GCSqGSIb3DQEBBQUAMIGRMQswCQYD
VQQGEwJISzELMAkGA1UECBMCSEsxETAPBgNVBAcTCEhvbmdLb25nMRAwDgYDVQQK
EwdQdXJlVlBOMQswCQYDVQQLEwJJVDEQMA4GA1UEAxMHUHVyZVZQTjEQMA4GA1UE
KRMHUHVyZVZQTjEfMB0GCSqGSIb3DQEJARYQbWFpbEBob3N0LmRvbWFpbjAeFw0x
NDA0MTAwNzI5NDlaFw0yNDA0MDcwNzI5NDlaMIGRMQswCQYDVQQGEwJISzELMAkG
A1UECBMCSEsxETAPBgNVBAcTCEhvbmdLb25nMRAwDgYDVQQKEwdQdXJlVlBOMQsw
CQYDVQQLEwJJVDEQMA4GA1UEAxMHUHVyZVZQTjEQMA4GA1UEKRMHUHVyZVZQTjEf
MB0GCSqGSIb3DQEJARYQbWFpbEBob3N0LmRvbWFpbjCCASIwDQYJKoZIhvcNAQEB
BQADggEPADCCAQoCggEBAJYqtUkQTlf/pHcGXuuII8S3pfI0fwFbs7l/1RP3nX3n
v1vyuvLi7h0jWsgJU0XM7LJywiRFJ8zsMLH7KZnIg7bscb50GY75WIq7C2NnWnnS
7zzyCCm2XD/2xZPym2lVRytpnWJbpemSS6Hdz7xI3q2FmixuBa1t5FeKsXfeaGGg
+ohwLvamnGHJYUYu3Nu0EWVzzy5wgT0c2C5jleGxl3kxRimD8FpnlAVdqyt0ib/f
f9XanaotSopIHUZmpYjT+udRC2+harlNKvOXYgDRl1mpimCvlzEWpZAo8dyBCxWl
xlBIT8OA8rimGi1XviknuOlWu2cGi13Ug8mCG0MjOQ0CAwEAAaOB+TCB9jAdBgNV
HQ4EFgQUt+1vJ2X2ho12PUDhdo2CsSHYXbYwgcYGA1UdIwSBvjCBu4AUt+1vJ2X2
ho12PUDhdo2CsSHYXbahgZekgZQwgZExCzAJBgNVBAYTAkhLMQswCQYDVQQIEwJI
SzERMA8GA1UEBxMISG9uZ0tvbmcxEDAOBgNVBAoTB1B1cmVWUE4xCzAJBgNVBAsT
AklUMRAwDgYDVQQDEwdQdXJlVlBOMRAwDgYDVQQpEwdQdXJlVlBOMR8wHQYJKoZI
hvcNAQkBFhBtYWlsQGhvc3QuZG9tYWluggkA3KwF0UPpTagwDAYDVR0TBAUwAwEB
/zANBgkqhkiG9w0BAQUFAAOCAQEAAhLQQmkKWJdyGqgMSKOWXSKN2WXTDjIdb9bK
Q8uHeq0LYCcPoRh8VYJg2X4UWR/KO9pKaG+iZJw4Jqz4GQJjjJLKHfsWwj790ay0
7U5KT08qmxFaxZUYn663H9b0+Zud1spTsTJjVe1eoRk6IDbbB4OMUzN9zyWEn6er
xi6llIAjQX1qtlBQasmTAbRtbSsCsZAxL2kXysULIdLrQP0iTgMQqqkv5zvpdEKN
3ciKCd8OHEhHOlAwA0/DNy3dg3Et0F2hNMDJhqMpxXsbKtGJ/rzGXQF2geEVzLZA
o42I1wBOSZLTX1fO1gl3gAGS9aYg5o31rrpBKzQewitJgIuc+Q==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PureVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PureVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PureVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
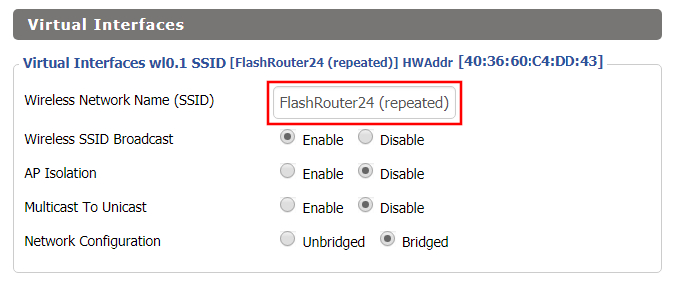
How to change the PureVPN server

  1. Copy the new PureVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN WireGuard Setup

TeamFlashRouters · Jun 15, 2022 ·

Preparing for ProtonVPN WireGuard Setup

Verify your ProtonVPN login information

If you are not already a ProtonVPN user Sign Up Now.

Log in to your account on the ProtonVPN website.

ProtonVPN Account login

1. On the left hand side select Downloads.

ProtonVPN Downloads

2. Then select WireGuard Configuration.

ProtonVPN WireGuard Configuration

3. Enter the Device Name to assign the FlashRouter to identify it among your ProtonVPN connections.

ProtonVPN WireGuard Desired Name

4. Set the Device platform as Router.

ProtonVPN WireGuard select Router

5. Select the VPN Options that you would like to connect with.

ProtonVPN WireGuard VPN Options

6. ProtonVPN will recommend the ideal server for you to connect to based on your location. Click Create or scroll down and select the server you wish to connect to and click Create next to the server number.

ProtonVPN WireGuard select server
ProtonVPN WireGuard select servers

7. Click Download to download the .conf file of the server you selected.

ProtonVPN WireGuard download configuration

DD-WRT Router Setup for ProtonVPN WireGuard

Navigate to Setup > Tunnels 

ProtonVPN WireGuard DD-WRT Tunnels

Enter ProtonVPN WireGuard settings

1. Click Import Config and then select Choose file. Select the .conf file that was downloaded earlier.

ProtonVPN WireGuard Import Config and Choose File

2. All settings will be loaded into the DD-WRT firmware the only field that needs to be adjusted is setting Persistent Keepalive to 25.

ProtonVPN WireGuard Persistent Keep Alive

3. Click Apply Settings at the bottom of the page.

4. After 30 seconds or so refresh the page until you see the WireGuard Status on the page is populated as seen below.

ProtonVPN WireGuard Status

Verify a successful ProtonVPN connection

Navigate to Setup > Tunnels

  1. You should Endpoint, Latest handshake, and Transfer in the WireGuard status area.
  2. Visit whatismyipaddress.com to verify your status as using ProtonVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
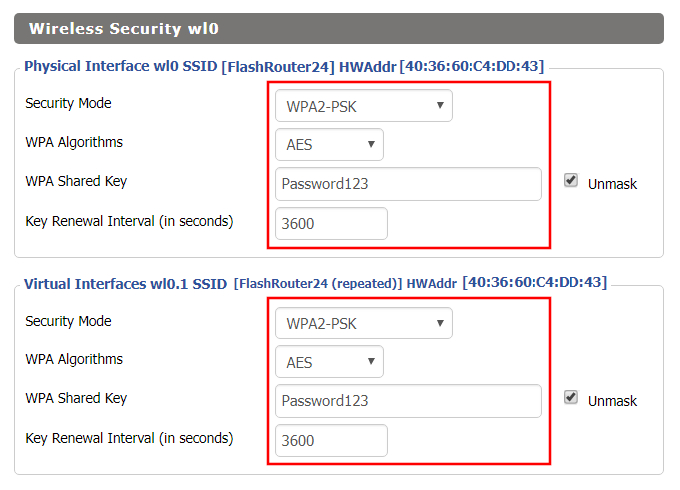
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN TP-Link OpenVPN Setup

TeamFlashRouters · Apr 16, 2024 ·

Preparing for NordVPN TP-Link Setup

Obtain your NordVPN manual Username and Password

If you are not already an NordVPN user Sign Up Now.

1. Log in to your account on the NordVPN website.

NordVPN login

2. Click NordVPN on the left hand side and then click Setup NordVPN manually.

NordVPN setup manually

3. Enter in the verification code that was sent to your email.

NordVPN verify code

4. Copy and paste your NordVPN manual username and password to a secure location. This is the username and password you will enter into the router settings to connect to NordVPN.

NordVPN credentials

Download your NordVPN .ovpn file

1. There are two options for obtaining the .ovpn file. The first and recommended is to navigate to NordVPN’s server recommendation page. Click Recommended Server to display the fastest server based on your actual location. You can adjust the country if you don’t want to connect to the recommended country.

Then click Show Available Protocols. Click Download Config next to OpenVPN UDP. This will download the .ovpn file to your computer for this server. Do not open this file.

NordVPN Recommended Server

The second method to obtain a server is for connecting to a specific server number that you know you want to use. This applies to NordVPN Dedicated IP servers if you are signed up for that service. Go to NordVPN’s .ovpn file page. Then search for the server number that you want to use and click Download UDP.

NordVPN Download Specific Server

TP-Link Router Setup for NordVPN

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was us6821 so I have entered in NordVPN us6821.

Set the VPN Type to OpenVPN.

In the Username and Password fields paste in the NordVPN username and password we obtained earlier.

Click Browse and select the .ovpn file you downloaded earlier. Then click Save.

TP-Link NordVPN

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link NordVPN connected

Verify a successful NordVPN connection

  1. You should now see a CONNECTED message.
  2. Visit NordVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

How to change the NordVPN server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

VPN Unlimited Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual VPN Unlimited Setup

Verify your VPN Unlimited login information

If you are not already a VPN Unlimited user Sign Up Now.

Log in to your account on the VPN Unlimited website.

VPN Unlimited Website Login

Generate your VPN Unlimited OVPN Configuration Files

1. Navigate to the VPN Unlimited section in the dropdown on the top left.

VPN Unlimited Website Login

2. Set Device to “Manually create new device…”

3. Name your device.

4. Select Server.

5. Set Protocol to OpenVPN.

FlashRouters DD-WRT Privacy App - Create Open VPN Configuration files

6. Open the ‘.OVPN’ file in a word processing program.

NOTE: We highly recommend using Notepad++ for Windows or TextEdit for Apple to open these files in order to preserve text format.

DD-WRT Router Setup for VPN Unlimited

Navigate to the Services > VPN

Enter VPN Unlimited settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the bottom of the .ovpn file you downloaded above, you can find your server address, it should look something like us-la.vpnunlimitedapp.com

Port

1194 for Tunnel Protocol UDP
80 for Tunnel Protocol TCP

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

Blowfish-CBC

Hash Algorithm

SHA1

User Pass Authentication

Disabled

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIEjjCCA/egAwIBAgIJAKsVbHBdakXuMA0GCSqGSIb3DQEBBQUAMIHgMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCTlkxETAPBgNVBAcTCE5ldyBZb3JrMR8wHQYDVQQK
ExZTaW1wbGV4IFNvbHV0aW9ucyBJbmMuMRYwFAYDVQQLEw1WcG4gVW5saW1pdGVk
MSMwIQYDVQQDExpzZXJ2ZXIudnBudW5saW1pdGVkYXBwLmNvbTEjMCEGA1UEKRMa
c2VydmVyLnZwbnVubGltaXRlZGFwcC5jb20xLjAsBgkqhkiG9w0BCQEWH3N1cHBv
cnRAc2ltcGxleHNvbHV0aW9uc2luYy5jb20wHhcNMTMxMjE2MTM1OTQ0WhcNMjMx
MjE0MTM1OTQ0WjCB4DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAk5ZMREwDwYDVQQH
EwhOZXcgWW9yazEfMB0GA1UEChMWU2ltcGxleCBTb2x1dGlvbnMgSW5jLjEWMBQG
A1UECxMNVnBuIFVubGltaXRlZDEjMCEGA1UEAxMac2VydmVyLnZwbnVubGltaXRl
ZGFwcC5jb20xIzAhBgNVBCkTGnNlcnZlci52cG51bmxpbWl0ZWRhcHAuY29tMS4w
LAYJKoZIhvcNAQkBFh9zdXBwb3J0QHNpbXBsZXhzb2x1dGlvbnNpbmMuY29tMIGf
MA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQDADUzS8QWGvdhLFKsEzAiq5+b0ukKj
Bza0k6/dmCeYTvCVqGKg/h1IAtQdVVLAkmEp0zvGH7PuOhXm7zZrCouBr/RiG4tE
coRHwc6AJmowkYERlY7+xGx3OuNrD00QceNTsan0bn78jwt0zhFNmHdoTtFjgK3o
qmQYSAtbEVWYgwIDAQABo4IBTDCCAUgwHQYDVR0OBBYEFKClmYP+tMNgWagUJCCH
jtaui2k+MIIBFwYDVR0jBIIBDjCCAQqAFKClmYP+tMNgWagUJCCHjtaui2k+oYHm
pIHjMIHgMQswCQYDVQQGEwJVUzELMAkGA1UECBMCTlkxETAPBgNVBAcTCE5ldyBZ
b3JrMR8wHQYDVQQKExZTaW1wbGV4IFNvbHV0aW9ucyBJbmMuMRYwFAYDVQQLEw1W
cG4gVW5saW1pdGVkMSMwIQYDVQQDExpzZXJ2ZXIudnBudW5saW1pdGVkYXBwLmNv
bTEjMCEGA1UEKRMac2VydmVyLnZwbnVubGltaXRlZGFwcC5jb20xLjAsBgkqhkiG
9w0BCQEWH3N1cHBvcnRAc2ltcGxleHNvbHV0aW9uc2luYy5jb22CCQCrFWxwXWpF
7jAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBBQUAA4GBALkWhfw7SSV7it+ZYZmT
+cQbExjlYgQ40zae2J2CqIYACRcfsDHvh7Q+fiwSocevv2NE0dWi6WB2H6SiudYj
vDvubAX/QbzfBxtbxCCoAIlfPCm8xOnWFN7TUJAzWwHJkKgEnu29GZHu2x8J+7Ve
DbKH5RTMHHe8FkSxh6Zz/BMN
—–END CERTIFICATE—–

Public Client Cert

Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN RSA PRIVATE KEY—–
…
—–END RSA PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN Unlimited connection

Navigate to the Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit to WhatIsMyIPAddress to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to VPN Unlimited.

Back up your settings

Navigate to the Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
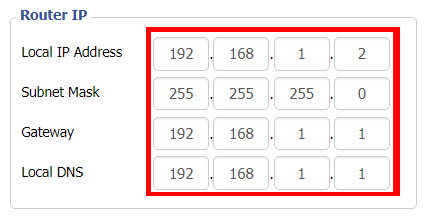
How to change the VPN Unlimited server

  1. Follow Steps 1-6 to Generate an .OVPN file for the server you wish to connect to and open it a word processing program.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the <cert> into the Public Client Cert field.
  4. Copy and paste the <key> into the Private Client Key field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero NordVPN Not Connecting or Showing Timeout Errors

Dave · Sep 22, 2026 ·

If NordVPN will not connect on Privacy Hero, shows a timeout error, remains stuck on Connecting, or displays Failed, the Privacy Hero router itself may still be working normally.

NordVPN connections can occasionally stop working when servers are placed into maintenance, removed or cycled out of service, account credentials change, or a previously saved NordVPN access token or manual service credential is no longer valid.

Start by confirming that Privacy Hero has normal internet access, then troubleshoot the NordVPN connection.


Jump to a Section

  • Confirm Privacy Hero Has Internet
  • Reconnect NordVPN
  • Try Another NordVPN Server
  • Update Your NordLynx Token
  • Update OpenVPN Credentials
  • Recent NordVPN Account Changes
  • Verify the VPN Connection

First: Confirm Privacy Hero Has Internet

Before changing your NordVPN settings, confirm that Privacy Hero itself has normal internet access.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. If the VPN Kill Switch is enabled, temporarily turn it Off.
  4. Turn the failed NordVPN connection off.
  5. Connect a device to the Privacy Hero network.
  6. Test normal internet access.

If internet access works normally with NordVPN and the Kill Switch disabled, the underlying Privacy Hero internet connection is working. Continue troubleshooting the NordVPN connection.

If your internet stopped working because NordVPN failed while the VPN Kill Switch was enabled, follow our Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting guide.

Reconnect NordVPN

A temporary NordVPN server or connection issue may resolve without changing your account information.

  1. Open the VPN section at app.privacyhero.com.
  2. Turn the NordVPN connection off.
  3. Wait a few seconds.
  4. Turn NordVPN back on.
  5. Allow the connection time to establish.
  6. Check whether the VPN status changes to Connected.

If NordVPN still shows Failed, Connecting, or a timeout error, continue with the steps below.

Try Another NordVPN Server

NordVPN regularly maintains, replaces, and cycles servers in its network. A specific NordVPN server that worked previously may eventually be taken offline, removed, or temporarily unavailable.

If your Privacy Hero NordVPN connection is configured to use a specific server and suddenly stops working, try another server or return to the normal country selection.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. Select your NordVPN connection.
  4. If you previously entered a specific NordVPN server under Advanced Options, remove or replace that server.
  5. Select the country or location you want to use.
  6. Save the settings.
  7. Reconnect NordVPN.
  8. Check whether the status changes to Connected.

If you specifically need to use an individual NordVPN server, make sure that server is still active before continuing to use it.

Important: A previously working specific server should not be assumed to remain available indefinitely. NordVPN may change its server network over time.

Update Your NordVPN Token for NordLynx

Privacy Hero uses a NordVPN access token to authenticate NordLynx connections.

If the saved token is expired, revoked, replaced, or otherwise no longer valid, NordLynx may show Failed, Connecting, or a timeout error.

Generating a new token is a good troubleshooting step if your NordVPN account information has changed or the existing token is no longer working.

  1. Sign in to your NordVPN account.
  2. Open the NordVPN Access Tokens page.
  3. Generate a new access token.
  4. Select Doesn’t expire if NordVPN provides that option.
  5. Copy the new token.
  6. Open app.privacyhero.com.
  7. Open the NordVPN settings.
  8. Confirm that NordLynx is the selected protocol.
  9. Replace the existing token with the newly generated token.
  10. Save the settings.
  11. Reconnect NordVPN.

Important: NordVPN access tokens are sensitive account credentials. Do not post or share your token publicly.

For complete setup instructions, see Privacy Hero NordVPN / NordLynx Setup.

Update NordVPN Manual Service Credentials for OpenVPN

If you are using OpenVPN instead of NordLynx, Privacy Hero uses NordVPN’s Manual Service Credentials.

These are different from the email address and password you normally use to sign in to the NordVPN website or application.

If the saved credentials are no longer valid, update them:

  1. Sign in to your NordVPN account.
  2. Open NordVPN Manual Service Credentials.
  3. Copy the current service username and password.
  4. Open app.privacyhero.com.
  5. Open your NordVPN settings.
  6. Confirm that OpenVPN is the selected protocol.
  7. Replace the existing manual service credentials with the current credentials from NordVPN.
  8. Save the settings.
  9. Reconnect NordVPN.

Do not enter your regular NordVPN website email address and password in place of the manual service credentials.

Did You Recently Change Your NordVPN Account Information?

If NordVPN stopped connecting after an account change, update the authentication information stored in Privacy Hero.

This is especially important after changes such as:

  • Changing your NordVPN account password.
  • Changing or updating NordVPN account security settings.
  • Generating or replacing NordVPN access tokens.
  • Changes to NordVPN manual service credentials.
  • Renewing, changing, or restoring your NordVPN subscription.

The credentials used by Privacy Hero depend on the VPN protocol:

  • NordLynx: Uses a NordVPN access token.
  • OpenVPN: Uses NordVPN manual service credentials.

Your regular NordVPN website login should not be entered as the router’s OpenVPN credentials.

If you are unsure whether the existing authentication information is still valid, retrieve current credentials directly from your NordVPN account and update Privacy Hero.

Confirm Your NordVPN Subscription Is Active

Privacy Hero cannot establish a NordVPN connection if the NordVPN account being used no longer has active VPN service.

Sign in to your NordVPN account and confirm that your subscription is active before continuing with server, token, or credential troubleshooting.

Try Another VPN Protocol

If your NordVPN account, credentials, and server selection are correct but the connection still fails, try another NordVPN protocol available in Privacy Hero.

For example, if NordLynx is not connecting, testing OpenVPN can help determine whether the issue is specific to the protocol or authentication method.

Remember that changing protocols also changes the required NordVPN authentication:

  • NordLynx requires a NordVPN access token.
  • OpenVPN requires NordVPN manual service credentials.

Important: Do Not Run Two VPNs at Once

Do not leave the NordVPN application connected directly on your phone or computer while testing the Privacy Hero VPN.

Running a VPN application on the device while also routing that device through the Privacy Hero VPN creates a double-VPN connection and can cause routing, connectivity, or IP-location problems.

Disconnect the device-level NordVPN app before testing the router VPN.

Verify the NordVPN Connection

Once Privacy Hero displays NordVPN as Connected:

  1. Connect your device to the Privacy Hero WiFi.
  2. Make sure the NordVPN app on the device is disconnected.
  3. Open a fresh private/incognito browser window.
  4. Visit NordVPN What Is My IP.
  5. Confirm that the public IP address and location correspond to your selected NordVPN location.
  6. Test several websites or applications.

If you use the Privacy Hero VPN Kill Switch, enable it only after confirming that NordVPN is connected and working.

NordVPN Is Connected but One Device Shows the Wrong IP

If Privacy Hero shows NordVPN as Connected and other devices display the correct VPN IP, the NordVPN connection itself is likely working.

Check the affected device’s Privacy Hero VPN assignment and review any VPN, privacy, DNS, browser, antivirus, firewall, or security settings running directly on that device.

See Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero NordVPN / NordLynx Setup
  • Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN

ProtonVPN Setup for Privacy Hero

TeamFlashRouters · Sep 17, 2025 ·

Privacy Hero supports Proton VPN through WireGuard and OpenVPN using the Custom VPN provider option.

WireGuard is recommended for most users. It uses a downloadable .conf configuration file. OpenVPN uses a downloadable .ovpn file and a separate Proton VPN OpenVPN username and password (not your regular Proton Account login).

Privacy Hero is cloud-managed. You can configure the VPN from a computer, smartphone, or tablet connected to any internet network; you do not need to be on the Privacy Hero WiFi to change settings.

Choose Your Proton VPN Setup

Jump directly to the connection method or instructions you need.

WireGuard Setup →Recommended · Generate your .conf fileOpenVPN Setup →Manual credentials and .ovpn fileUpload WireGuard →Add a Custom WireGuard connectionUpload OpenVPN →Add the file and service credentialsVerify Connection →Confirm VPN IP address and locationTroubleshooting →Fix connection failures and no internet

Proton VPN WireGuard Setup (Recommended)

WireGuard uses a configuration file generated by Proton VPN. You do not need an OpenVPN username and password for this method.

Generate Your Proton VPN WireGuard Configuration

  1. Open your Proton VPN account and sign in.
  2. Go to Downloads → WireGuard configuration.
  3. Enter a recognizable configuration name and select Router as the platform.
  4. Choose your preferred VPN options and an available server or country. For a straightforward setup, select a standard server configuration.
  5. Click Create, then Download to save the generated WireGuard .conf file to your device.

Important: A WireGuard configuration contains a private key. Keep the downloaded file private; do not paste its contents into public posts or unprotected support messages. For detailed Proton account instructions, see Proton VPN: Download WireGuard Configuration Files.

Upload WireGuard to Privacy Hero

  1. Open app.privacyhero.com and log in to your Privacy Hero account.
  2. Open the VPN section, click Change beside the VPN provider, and choose Custom.
  3. Select WireGuard and upload the Proton VPN .conf file you downloaded.
  4. Click Save to apply the configuration and connect. Confirm that Privacy Hero reports Connected.
Privacy Hero Custom WireGuard configuration screen showing the configuration file upload

Proton VPN OpenVPN Setup

OpenVPN is an alternative to WireGuard. You need a Proton VPN OpenVPN-specific username and password and a server .ovpn configuration file.

Get Your Proton VPN OpenVPN Credentials

  1. Sign in to your Proton VPN account.
  2. Open Account → OpenVPN username to find your separate OpenVPN username and password.
  3. Copy these credentials or keep the page open. Do not use your usual Proton Account email and password for the manual OpenVPN connection.

For help locating these credentials, see Proton VPN: How to Sign In / OpenVPN Credentials.

Download Your Proton VPN OpenVPN Server File

  1. In your Proton VPN account, go to Downloads → OpenVPN configuration files.
  2. Select Router as the platform and UDP as the protocol (recommended starting point). If UDP does not work on your network, you can try a TCP configuration later.
  3. Select an available country or individual server from the standard configuration list, then click Download to save its .ovpn file.

For additional details about the file download options, see Proton VPN: Download OpenVPN Configuration Files.

Upload OpenVPN to Privacy Hero

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section, click Change, and select Custom as the VPN provider.
  3. Choose OpenVPN and upload the Proton VPN .ovpn file you downloaded.
  4. Enter your separate Proton VPN OpenVPN username and password into the Custom VPN fields.
  5. Click Save, then confirm Privacy Hero displays Connected.
Privacy Hero Custom OpenVPN setup with configuration file upload and separate VPN username and password fields

Verify Your Proton VPN Connection

After Privacy Hero reports Connected, confirm that a device on the router network is using your Proton VPN connection.

  1. Connect your testing device to the Privacy Hero WiFi or LAN network.
  2. Disable any Proton VPN app or other VPN application running directly on that device, so it does not create a second VPN connection.
  3. Open a private/incognito browser window.
  4. Visit Proton VPN’s IP Address Checker.
  5. Verify that the public IP address and approximate location correspond to the Proton VPN server configured in Privacy Hero.

Important: You can manage Privacy Hero from another WiFi network or cellular data. However, the device performing the VPN IP test must be connected to the Privacy Hero network.

Streaming Relocation and VPN Location

If Privacy Hero Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation location rather than the country selected in your Proton VPN configuration. See Privacy Hero Streaming Relocation.


Proton VPN Not Connecting?

If Privacy Hero displays Failed, remains on Connecting, or reports a timeout, work through these checks:

  1. Confirm that you selected Custom as the VPN provider in Privacy Hero and chose the protocol that matches your configuration file.
  2. For WireGuard, create and download a fresh Proton VPN .conf file for an available server, then upload it again. Do not use an OpenVPN .ovpn file in the WireGuard section.
  3. For OpenVPN, verify that you entered Proton VPN’s separate OpenVPN username and password, not your regular Proton Account login.
  4. Download a fresh configuration for a different Proton VPN server and reconnect. Proton VPN occasionally changes server configurations.
  5. If using OpenVPN UDP and the connection still fails, download and try a TCP .ovpn configuration file to test for a protocol-related issue.
  6. Temporarily disable the VPN Kill Switch while checking whether internet works without the VPN. Re-enable your preferred Kill Switch setting once testing is complete.

VPN Disconnects and Devices Have No Internet?

The VPN Kill Switch may be intentionally blocking normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

Check the affected device for a second VPN app, iCloud Private Relay, Private DNS, browser proxy settings, or filtering software. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

SaferVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 15, 2019 ·

Preparing for Manual SaferVPN Setup

Verify your SaferVPN login information

If you are not already an SaferVPN user Sign Up Now.

Log in to your account on the SaferVPN website.

FlashRouters Privacy App - SaferVPN Login

SaferVPN Server Addresses

View a full list of SaferVPN servers.

America

East Coast:
us1.safervpn.net

West Coast:
us2.safervpn.net

United Kingdom

uk1.safervpn.net

DD-WRT Router Setup for SaferVPN

Navigate to Services > VPN

Enter SaferVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change SaferVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you successfully logged in to your SaferVPN account with.

Password

Enter the Password you successfully logged in to your SaferVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Additional Config

persist-key
persist-tun
tun-mtu-extra 32
mssfix 1450

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIE1jCCA76gAwIBAgIJAOnRq4FWsZgYMA0GCSqGSIb3DQEBCwUAMIGiMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExFTATBgNVBAcTDFNhbkZyYW5jaXNjbzERMA8G
A1UEChMIU2FmZXJWUE4xETAPBgNVBAsTCFNhZmVyVlBOMREwDwYDVQQDEwhTYWZl
clZQTjERMA8GA1UEKRMIU2FmZXJWUE4xIzAhBgkqhkiG9w0BCQEWFHN1cHBvcnRA
c2FmZXJ2cG4uY29tMB4XDTE3MDgzMTA5NDEyM1oXDTI3MDgyOTA5NDEyM1owgaIx
CzAJBgNVBAYTAlVTMQswCQYDVQQIEwJDQTEVMBMGA1UEBxMMU2FuRnJhbmNpc2Nv
MREwDwYDVQQKEwhTYWZlclZQTjERMA8GA1UECxMIU2FmZXJWUE4xETAPBgNVBAMT
CFNhZmVyVlBOMREwDwYDVQQpEwhTYWZlclZQTjEjMCEGCSqGSIb3DQEJARYUc3Vw
cG9ydEBzYWZlcnZwbi5jb20wggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIB
AQCqNV7oJZrUqD/mBSWlKi/sGRE2y3Yphs5m/vmmS4GPrc8lyaI1idhv44MGZ0i1
XCkJFZmaVQk7NUz5npz9hcnxN3MiZd/5Kv8Vo4aQkL0xQ7euto71LIgTqbJvTJjW
kowsVVgartGK2ewfCd+KV6k5oBImlDdSnLW1pq82Kg+YcnXxdaFc8RpNWdBbdxBe
tb4k6JcoZHuk9Zq5gi5Nnhtjc6lheCRzTGZ2hslDfJ58yMpR0jTMC3Rd+G+sM0q3
/gEEEW34ckUgCb5j6Kq35LUlnuonnViBnEzFR/MTizMARFj7VYkzOpxSsxJ6Epan
JP8Zgbz81z4A822hosakl7kTAgMBAAGjggELMIIBBzAdBgNVHQ4EFgQUKSnUrJLQ
omrGvdncxKkKT7Rxrj8wgdcGA1UdIwSBzzCBzIAUKSnUrJLQomrGvdncxKkKT7Rx
rj+hgaikgaUwgaIxCzAJBgNVBAYTAlVTMQswCQYDVQQIEwJDQTEVMBMGA1UEBxMM
U2FuRnJhbmNpc2NvMREwDwYDVQQKEwhTYWZlclZQTjERMA8GA1UECxMIU2FmZXJW
UE4xETAPBgNVBAMTCFNhZmVyVlBOMREwDwYDVQQpEwhTYWZlclZQTjEjMCEGCSqG
SIb3DQEJARYUc3VwcG9ydEBzYWZlcnZwbi5jb22CCQDp0auBVrGYGDAMBgNVHRME
BTADAQH/MA0GCSqGSIb3DQEBCwUAA4IBAQB704c0nixfDuJ7OiFBUmkhmDUFEIhl
D35wxlthKYRs8tBzetZEipFGdyUOwuWiuwG/BuOwuP7fPS9uP4u4EPKjA5kL/Z/V
E743q50PS4L/kT3ZFyUrcisUKajAr5Gu+o6rzA6F4+QYu26iBbKewNrrb+riF1wR
GKthc6W++Awt+oVyKtVNyS2QokuBFcSu5IiVsfGqJ8TmffvFBqKUUjWopmP+qiYR
8+0qwHing/S/C9S72ZxhM9DF3et1dXFuHf/69YL8/u36tyKMqy/JVhByAlc87cRI
tcRGaviUttBeSw4j1Y6XrycVkhn4LzizWrqrmfCikhx26MrIeWK5JxYL
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful SaferVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit SaferVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to SaferVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.
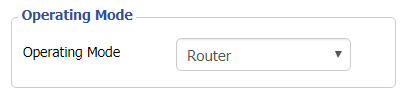
How to change the SaferVPN server

  1. Copy the new SaferVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ExpressVPN Setup for Privacy Hero

TeamFlashRouters · Aug 14, 2025 ·

Privacy Hero supports ExpressVPN using OpenVPN. To connect, you need your ExpressVPN Manual Configuration username and password and an OpenVPN (.ovpn) configuration file for your preferred server location.

Important: In Privacy Hero, choose Custom as the VPN provider. Upload the ExpressVPN .ovpn file and enter your separate Manual Configuration credentials, not your regular ExpressVPN website login.

Privacy Hero is cloud-managed, so you can complete setup from any computer, smartphone, or tablet with an internet connection. You do not need to be connected to Privacy Hero WiFi while changing the settings.

Choose Your ExpressVPN Setup Step

Jump directly to the instructions you need.

Manual Credentials →Find your ExpressVPN OpenVPN username and passwordDownload .ovpn File →Choose a server location and download its UDP fileCustom VPN Setup →Upload the file and enter credentials in Privacy HeroUDP Configuration →Check the OpenVPN protocol and save your connectionVerify Connection →Confirm your VPN IP address and server locationTroubleshooting →Connection errors, timeouts, and no internet

Get Your ExpressVPN Manual Configuration Credentials

ExpressVPN provides separate credentials for manual OpenVPN connections. These are different from your normal ExpressVPN website email and password.

  1. Open ExpressVPN Set Up Devices and sign in to your ExpressVPN account.
  2. In the left navigation, select Set Up Devices.
  3. Under Applications, expand Advanced setup and choose Manual Configuration.
  4. Find your unique Username and Password under Manual Configuration. Keep this tab open so you can copy them into Privacy Hero.

Important: Do not use your regular ExpressVPN account password, and do not share your manual configuration credentials publicly.


Download Your ExpressVPN OpenVPN Server File

Each available ExpressVPN location has its own OpenVPN configuration file. The file determines the server location used by Privacy Hero.

  1. On the same Manual Configuration page, locate the server regions, such as Americas, Europe, Asia Pacific, or Middle East & Africa.
  2. Expand your preferred region and download the UDP .ovpn file for an available location. Save it to the device you are using to configure Privacy Hero.

Only locations offered on your ExpressVPN Manual Configuration page can be used for this setup. To change locations later, download the corresponding .ovpn file and upload it to Privacy Hero.


Add ExpressVPN to Privacy Hero as a Custom VPN

ExpressVPN uses Privacy Hero’s Custom VPN configuration rather than a dedicated ExpressVPN provider option.

Upload the OpenVPN File and Enter Credentials

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section.
  3. Click Change beside the VPN provider and choose Custom.
  4. Choose OpenVPN if prompted, then upload the UDP .ovpn file downloaded from ExpressVPN.
  5. Copy the separate ExpressVPN Manual Configuration Username and Password into the corresponding Privacy Hero fields.
Privacy Hero Custom OpenVPN configuration showing file upload and manual username and password fields

Check the UDP Configuration and Connect

  1. If Privacy Hero displays the OpenVPN configuration in an editor, confirm that the downloaded UDP configuration specifies proto udp. If the directive is missing, add proto udp at the beginning of the configuration. Do not add a conflicting second protocol directive.
  2. Click Save to apply the configuration and establish the VPN connection.
  3. Confirm Privacy Hero displays Connected for the Custom OpenVPN connection.
Privacy Hero Custom OpenVPN configuration editor with proto udp directive

Verify Your ExpressVPN Connection

After Privacy Hero reports Connected, check that devices on the Privacy Hero network are actually using the VPN.

  1. Connect the testing device to the Privacy Hero WiFi or LAN network.
  2. Disconnect the ExpressVPN app or any other VPN application running directly on that device.
  3. Open a fresh private/incognito browser window.
  4. Visit ExpressVPN What Is My IP.
  5. Confirm the public IP address and approximate location correspond to the ExpressVPN server selected in your .ovpn file.

Important: You can manage Privacy Hero’s VPN settings from another network or cellular data. However, to verify the router’s VPN IP, the testing device must be connected to the Privacy Hero network. Running another VPN app on the device can produce double-VPN results.

Streaming Relocation and VPN Location

If Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation region instead of the location defined in the ExpressVPN configuration file. See Privacy Hero Streaming Relocation.


ExpressVPN Not Connecting?

If Privacy Hero shows Failed, stays on Connecting, or displays a timeout error, try these checks:

  1. Confirm your ExpressVPN subscription is active and you entered the separate Manual Configuration username and password.
  2. Check that you selected Custom in Privacy Hero, rather than another VPN provider.
  3. Download a fresh UDP .ovpn file for an available ExpressVPN server location and upload it again.
  4. Check that the OpenVPN configuration uses proto udp without conflicting protocol directives.
  5. Temporarily disable the VPN Kill Switch while testing whether normal internet access works without the VPN, then restore your preferred Kill Switch setting.
  6. Try another ExpressVPN server location or reconnect the VPN.

No Internet After the VPN Disconnects?

The Privacy Hero VPN Kill Switch may intentionally block normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected, but One Device Shows the Wrong IP?

If other devices show the correct VPN IP, check the affected device’s VPN apps, iCloud Private Relay, Private DNS, antivirus filtering, browser proxy/DNS settings, or other security software. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

ProtonVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual ProtonVPN Setup

Verify your ProtonVPN login information

If you are not already an ProtonVPN user Sign Up Now.

1. Log in to your account on the ProtonVPN website.

2. Navigate to the Account tab and note your OpenVPN specific Username and Password.

FlashRouters DD-WRT Privacy APP ProtonVPN OpenVPN Specific Username and Password

ProtonVPN Server Addresses

Click on the following link to Download the .ovpn file containing the Server IP Address you wish to connect to.

Open the .ovpn file that is downloaded to your computer with NotePad++ for Windows or TextEdit for Apple.

DD-WRT Router Setup for ProtonVPN

Navigate to Services > VPN

Enter ProtonVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote 206.226.72.27 1194
206.226.72.27 is your ProtonVPN server IP address. Enter that IP Address in this field.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter your OpenVPN specific Username.

Password

Enter your OpenVPN specific Password.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
6acef03f62675b4b1bbd03e53b187727
423cea742242106cb2916a8a4c829756
3d22c7e5cef430b1103c6f66eb1fc5b3
75a672f158e2e2e936c3faa48b035a6d
e17beaac23b5f03b10b868d53d03521d
8ba115059da777a60cbfd7b2c9c57472
78a15b8f6e68a3ef7fd583ec9f398c8b
d4735dab40cbd1e3c62a822e97489186
c30a0b48c7c38ea32ceb056d3fa5a710
e10ccc7a0ddb363b08c3d2777a3395e1
0c0b6080f56309192ab5aacd4b45f55d
a61fc77af39bd81a19218a79762c3386
2df55785075f37d8c71dc8a42097ee43
344739a0dd48d03025b0450cf1fb5e8c
aeb893d9a96d1f15519bb3c4dcb40ee3
16672ea16c012664f8a9f11255518deb
-----END OpenVPN Static key V1-----

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFozCCA4ugAwIBAgIBATANBgkqhkiG9w0BAQ0FADBAMQswCQYDVQQGEwJDSDEV
MBMGA1UEChMMUHJvdG9uVlBOIEFHMRowGAYDVQQDExFQcm90b25WUE4gUm9vdCBD
QTAeFw0xNzAyMTUxNDM4MDBaFw0yNzAyMTUxNDM4MDBaMEAxCzAJBgNVBAYTAkNI
MRUwEwYDVQQKEwxQcm90b25WUE4gQUcxGjAYBgNVBAMTEVByb3RvblZQTiBSb290
IENBMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAt+BsSsZg7+AuqTq7
vDbPzfygtl9f8fLJqO4amsyOXlI7pquL5IsEZhpWyJIIvYybqS4s1/T7BbvHPLVE
wlrq8A5DBIXcfuXrBbKoYkmpICGc2u1KYVGOZ9A+PH9z4Tr6OXFfXRnsbZToie8t
2Xjv/dZDdUDAqeW89I/mXg3k5x08m2nfGCQDm4gCanN1r5MT7ge56z0MkY3FFGCO
qRwspIEUzu1ZqGSTkG1eQiOYIrdOF5cc7n2APyvBIcfvp/W3cpTOEmEBJ7/14RnX
nHo0fcx61Inx/6ZxzKkW8BMdGGQF3tF6u2M0FjVN0lLH9S0ul1TgoOS56yEJ34hr
JSRTqHuar3t/xdCbKFZjyXFZFNsXVvgJu34CNLrHHTGJj9jiUfFnxWQYMo9UNUd4
a3PPG1HnbG7LAjlvj5JlJ5aqO5gshdnqb9uIQeR2CdzcCJgklwRGCyDT1pm7eoiv
WV19YBd81vKulLzgPavu3kRRe83yl29It2hwQ9FMs5w6ZV/X6ciTKo3etkX9nBD9
ZzJPsGQsBUy7CzO1jK4W01+u3ItmQS+1s4xtcFxdFY8o/q1zoqBlxpe5MQIWN6Qa
lryiET74gMHE/S5WrPlsq/gehxsdgc6GDUXG4dk8vn6OUMa6wb5wRO3VXGEc67IY
m4mDFTYiPvLaFOxtndlUWuCruKcCAwEAAaOBpzCBpDAMBgNVHRMEBTADAQH/MB0G
A1UdDgQWBBSDkIaYhLVZTwyLNTetNB2qV0gkVDBoBgNVHSMEYTBfgBSDkIaYhLVZ
TwyLNTetNB2qV0gkVKFEpEIwQDELMAkGA1UEBhMCQ0gxFTATBgNVBAoTDFByb3Rv
blZQTiBBRzEaMBgGA1UEAxMRUHJvdG9uVlBOIFJvb3QgQ0GCAQEwCwYDVR0PBAQD
AgEGMA0GCSqGSIb3DQEBDQUAA4ICAQCYr7LpvnfZXBCxVIVc2ea1fjxQ6vkTj0zM
htFs3qfeXpMRf+g1NAh4vv1UIwLsczilMt87SjpJ25pZPyS3O+/VlI9ceZMvtGXd
MGfXhTDp//zRoL1cbzSHee9tQlmEm1tKFxB0wfWd/inGRjZxpJCTQh8oc7CTziHZ
ufS+Jkfpc4Rasr31fl7mHhJahF1j/ka/OOWmFbiHBNjzmNWPQInJm+0ygFqij5qs
51OEvubR8yh5Mdq4TNuWhFuTxpqoJ87VKaSOx/Aefca44Etwcj4gHb7LThidw/ky
zysZiWjyrbfX/31RX7QanKiMk2RDtgZaWi/lMfsl5O+6E2lJ1vo4xv9pW8225B5X
eAeXHCfjV/vrrCFqeCprNF6a3Tn/LX6VNy3jbeC+167QagBOaoDA01XPOx7Odhsb
Gd7cJ5VkgyycZgLnT9zrChgwjx59JQosFEG1DsaAgHfpEl/N3YPJh68N7fwN41Cj
zsk39v6iZdfuet/sP7oiP5/gLmA/CIPNhdIYxaojbLjFPkftVjVPn49RqwqzJJPR
N8BOyb94yhQ7KO4F3IcLT/y/dsWitY0ZH4lCnAVV/v2YjWAWS3OWyC8BFx/Jmc3W
DK/yPwECUcPgHIeXiRjHnJt0Zcm23O2Q3RphpU+1SO3XixsXpOVOYP6rJIXW9bMZ
A1gTTlpi7A==
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful ProtonVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the ProtonVPN server

  1. Download and open a new .ovpn file from ProtonVPN.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN Merlin OpenVPN Setup

TeamFlashRouters · Jan 11, 2023 ·

Preparing for NordVPN Merlin Setup

Obtain your NordVPN manual Username and Password

If you are not already an NordVPN user Sign Up Now.

1. Log in to your account on the NordVPN website.

NordVPN login

2. Click NordVPN on the left hand side and then click Setup NordVPN manually.

NordVPN setup manually

3. Enter in the verification code that was sent to your email.

NordVPN verify code

4. Copy and paste your NordVPN manual username and password to a secure location. This is the username and password you will enter into the router settings to connect to NordVPN.

NordVPN credentials

Download your NordVPN .ovpn file

1. There are two options for obtaining the .ovpn file. The first and recommended is to navigate to NordVPN’s server recommendation page. Click Recommended Server to display the fastest server based on your actual location. You can adjust the country if you don’t want to connect to the recommended country.

Then click Show Available Protocols. Click Download Config next to OpenVPN UDP. This will download the .ovpn file to your computer for this server. Do not open this file.

NordVPN Recommended Server

The second method to obtain a server is for connecting to a specific server number that you know you want to use. This applies to NordVPN Dedicated IP servers if you are signed up for that service. Go to NordVPN’s .ovpn file page. Then search for the server number that you want to use and click Download UDP.

NordVPN Download Specific Server

Merlin Router Setup for NordVPN

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Click Choose file and select the .ovpn file you downloaded earlier. Then click Upload.

Merlin Choose File Upload

4. Set Automatic Start at boot time to Yes if you want the VPN connection to begin automatically when the router is powered off and back on.

Merlin Automatic Start at boot time

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was in us5835.nordvpn.com so I have entered in NordVPN us5835.

Merlin NordVPN Description

6. Set Accept DNS Configuration to Strict. Set Redirect Internet traffic through tunnel to Yes (all). Set Kill Switch to Yes or No depending on if you want the Internet to be killed if the VPN connection drops.
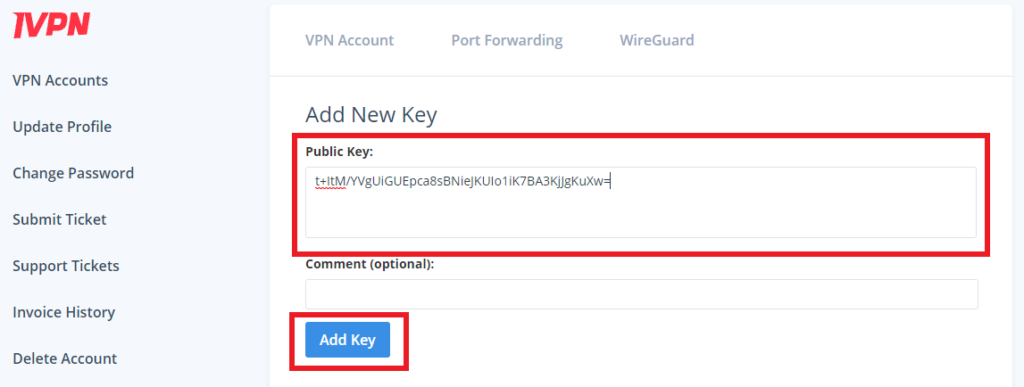
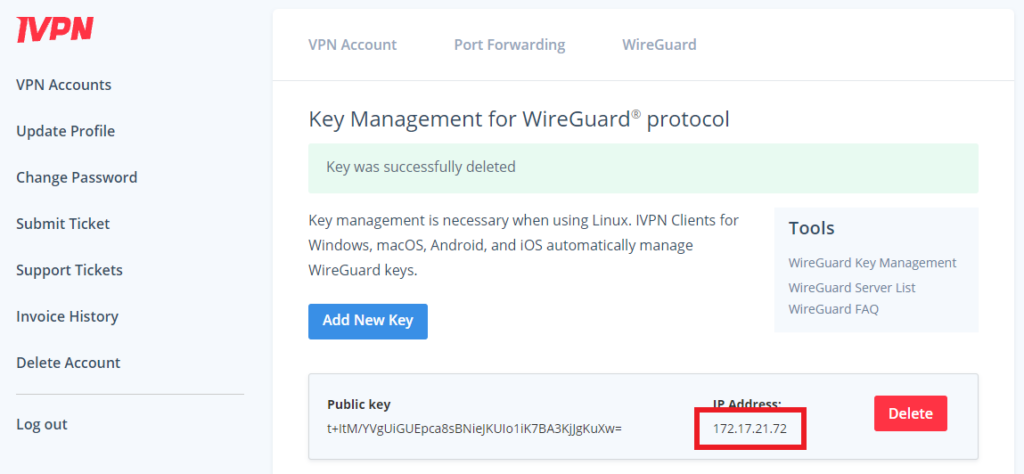
Merlin Accept DNS configuration Redirect Internet and Kill Switch

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network please set the Redirect Internet traffic through tunnel to VPN Director. Then complete the instructions on this page and then view our VPN Director guide.

7. Enter your NordVPN username and password that you obtained earlier in the Username and Password. Note that these are different from your NordVPN email login and password.

Merlin VPN Username and Password

8. Click Apply at the bottom of the page.

9. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Merlin Service State All Providers

Verify a successful NordVPN connection

  1. You should now see a CONNECTED message.
  2. Visit NordVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

How to change the NordVPN server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here
Next Page »

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer