• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: files of downlo

NordVPN Setup for AsusWRT: Token, WireGuard & OpenVPN

TeamFlashRouters · Oct 15, 2025 ·

Set up NordVPN on an ASUS router using AsusWRT VPN Fusion. Supported ASUS firmware offers three different VPN types: NordVPN (access-token integration), WireGuard (downloadable .conf file), and OpenVPN (manual service credentials plus an .ovpn file). Choose the method that matches your needs and your router’s available options.

All configuration is completed directly through your ASUS router’s administration interface using VPN Fusion. Before starting, make sure your router is connected to the internet, your firmware supports VPN Fusion, and you have an active NordVPN subscription.

Before starting, join the ASUS router WiFi or LAN and sign in to http://www.asusrouter.com or your router’s LAN IP (commonly 192.168.50.1). Open VPN > VPN Fusion > Add profile. Router model, firmware, and region affect which VPN types appear. See Access Your AsusWRT Settings.

In This Guide

Choose a VPN Type →NordVPN, WireGuard, or OpenVPNNordVPN Token Setup →Built-in NordLynx integrationWireGuard File Setup →Download and import a .confOpenVPN Setup →Manual credentials and .ovpnDedicated IP Setup →OpenVPN onlyDevices & Troubleshooting →Route devices and verify IP

Which NordVPN Option Should You Choose?

1. NordVPN

NordVPN access token and a country/region dropdown. The built-in ASUS/NordVPN integration is the simplest approach if you only need a country, not an exact server file.

Follow token setup →

2. WireGuard

Import a NordVPN .conf configuration file for a server selected in Nord Account. Useful when you want a downloaded profile for a particular server.

Follow WireGuard setup →

3. OpenVPN

Import a NordVPN .ovpn server file and enter your separate manual service username and password. Also used for NordVPN Dedicated IP.

Follow OpenVPN setup →

Dedicated IP uses OpenVPN only in this guide. Select OpenVPN in VPN Fusion and import your Dedicated IP .ovpn file. Do not use the standard NordVPN token/region dropdown for a Dedicated IP.

Option 1: NordVPN Dropdown — Token-Based NordLynx

Select the NordVPN type inside VPN Fusion. This is the integrated token-based setup and offers a country/region selection, rather than a manually imported server file.

  1. In Nord Account, open NordVPN Access Tokens and complete email/account verification if requested.
  2. Generate an access token, choose an expiry period if NordVPN offers that setting, and copy the token immediately (it may only be displayed once).
  3. On your ASUS router, open VPN > VPN Fusion > Add profile.
  4. Set VPN Type to NordVPN. Name the profile, select your preferred Region, and paste the token.
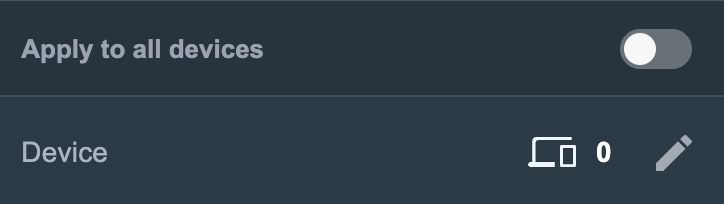
  5. Choose Apply to all devices if you want it as the default route, or assign only selected devices (see the VPN Fusion guide below).
  6. Click Apply and Enable / Apply all settings, as shown in your firmware, and verify the profile connects.
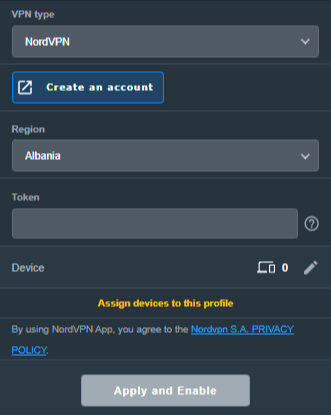
ASUS VPN Fusion NordVPN VPN type with Region and Token fields
Keep: existing ASUS NordVPN region/token form (remove any private token before publishing).

Need a specific server? Use the separate WireGuard file method below or the OpenVPN configuration-file method. Do not expect the token-based country dropdown to accept a .conf or .ovpn file.

Option 2: WireGuard Dropdown — Import a NordVPN .conf File

NordVPN now provides downloadable WireGuard configuration files through its manual server recommendation page. This is different from the built-in NordVPN token option in VPN Fusion.

  1. Sign in to Nord Account and open NordVPN Server Recommendation.
  2. Choose your preferred country and server; use the available filters if you need to narrow the list. Select a currently available server.
  3. Choose Get setup configuration, select WireGuard from the protocol menu, and click Download config. Save the downloaded .conf file.
  4. In your ASUS router settings open VPN > VPN Fusion > Add profile, then set VPN Type to WireGuard (not NordVPN).
  5. Use the ASUS Import configuration / file-import control to select the NordVPN .conf file. Confirm the imported parameters and save the profile.
  6. Choose the target devices or enable the default/all-devices route. Click Apply and Enable, then check the VPN status and your public IP.


WireGuard configuration files may contain a private key. Do not share an actual customer .conf file or publish a screenshot exposing its key material. When changing servers, download/import a different file and choose the desired active profile.

NordVPN’s official instructions: How to download WireGuard and OpenVPN configuration files.

Option 3: OpenVPN Dropdown — Credentials + .ovpn File

OpenVPN requires two separate items: the configuration file for your desired server and NordVPN’s manual service credentials. Your normal Nord Account email/password is not the correct credential pair for this method.

  1. Open NordVPN Manual Service Credentials and copy the service username and service password after any required verification.
  2. Open NordVPN OpenVPN Configuration Files and choose a server/location. Download its UDP .ovpn file, or TCP .ovpn if UDP does not work on your network.
  3. On ASUS, go to VPN > VPN Fusion > Add profile and set VPN Type to OpenVPN.
  4. Enter a connection name, Import .ovpn file, and paste the NordVPN manual service username and password in the corresponding fields.
  5. Choose devices or Apply to all devices, then click Apply and Enable. Confirm VPN Fusion shows a successful connection.
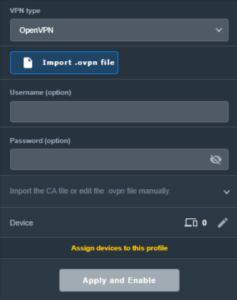
ASUS VPN Fusion OpenVPN VPN type with OVPN import and username password fields
Keep: existing ASUS OpenVPN profile form. New screenshots should use a larger clean capture if available.

Server selection: The location is controlled by the server named in the imported .ovpn file. To switch locations, import another server file or use a separate OpenVPN profile.

NordVPN Dedicated IP — OpenVPN Only

If you have purchased and activated the NordVPN Dedicated IP add-on, use your specific Dedicated IP OpenVPN configuration file. Do not select the ordinary NordVPN token integration or a regular shared server.

  1. In your Nord Account, open the Dedicated IP details and download the assigned server’s OpenVPN UDP or TCP configuration file, following NordVPN Dedicated IP manual configuration instructions.
  2. Open NordVPN Manual Service Credentials and copy the manual username and password.
  3. In ASUS VPN Fusion > Add profile, choose OpenVPN.
  4. Import the Dedicated IP .ovpn file, enter manual service credentials, save, enable, and verify the public IP matches your assigned Dedicated IP.

The Dedicated IP add-on must be active on the NordVPN account. A regular shared-server .ovpn file will not give you the Dedicated IP.

Assign Devices, Verify the VPN, and Troubleshoot

One VPN for everyone, or different VPNs for different devices?

VPN Fusion lets you use a VPN profile as the default connection for all devices or assign specific client devices to different profiles. Some supported ASUS models can maintain one WireGuard tunnel alongside multiple OpenVPN profiles, but the number of simultaneous tunnels is model/firmware dependent; creating multiple profiles does not mean all can be active simultaneously.

For step-by-step device assignments, default routing, profile conflicts, and bypassing the VPN, see How to Use ASUS VPN Fusion and Assign Devices to VPN Profiles. For a dedicated WiFi network with VPN or ISP routing, see ASUS Guest Network VPN / No-VPN Setup.

Verify the IP of the actual device

  1. Confirm your chosen profile shows Connected in VPN Fusion.
  2. Join the ASUS WiFi or LAN using a device that is actually assigned to that VPN profile.
  3. Open NordVPN IP Address Check and compare the public IP/location with the intended server or Dedicated IP.
  4. If the device shows an ISP IP, first check Apply to all devices and the per-device assignments in VPN Fusion.
  5. Disconnect a NordVPN app, Apple iCloud Private Relay, browser VPN/proxy, or other device-level network service during testing. Follow Router VPN Shows Wrong IP? Check Device Settings.

If VPN Fusion will not connect

  1. Temporarily disable the failing profile and confirm the ASUS router works using its normal ISP internet connection.
  2. For NordVPN type, check that the access token is valid and hasn’t expired; regenerate if needed.
  3. For WireGuard, import a fresh .conf from the Nord server recommendation page and make sure the profile is enabled.
  4. For OpenVPN, double-check manual service credentials (not website credentials) and try a different server file or TCP instead of UDP.
  5. Check that device-assignment rules point to the intended active profile, then retest with one clean device.

NordVPN Routers & Offers

Shop NordVPN-Ready FlashRouters

Compare ASUS and Privacy Hero router options and choose the hardware that fits your VPN and network requirements.

Browse NordVPN Routers →

NordVPN Partner Offer

Need NordVPN service? See the current FlashRouters NordVPN promotional offer. Subscription pricing and terms are shown on the offer page.

See NordVPN Offer →

Related AsusWRT Guides

  • ASUS VPN Fusion: Assign Devices and Manage Multiple Profiles
  • ASUS Guest Network: WiFi With or Without a VPN
  • AsusWRT Router Login Guide
  • Router VPN Shows Wrong IP? Device Settings

Upgrade your ASUS router

Explore the Latest WiFi 7 ASUS FlashRouters

Looking for a newer ASUS router? Browse WiFi 7 models available from FlashRouters and compare features to find the right fit for your home or office. VPN Fusion and other features vary by router model and firmware.
Shop ASUS WiFi 7 Routers →

ProtonVPN Setup for Privacy Hero

TeamFlashRouters · Sep 17, 2025 ·

Privacy Hero supports Proton VPN through WireGuard and OpenVPN using the Custom VPN provider option.

WireGuard is recommended for most users. It uses a downloadable .conf configuration file. OpenVPN uses a downloadable .ovpn file and a separate Proton VPN OpenVPN username and password (not your regular Proton Account login).

Privacy Hero is cloud-managed. You can configure the VPN from a computer, smartphone, or tablet connected to any internet network; you do not need to be on the Privacy Hero WiFi to change settings.

Choose Your Proton VPN Setup

Jump directly to the connection method or instructions you need.

WireGuard Setup →Recommended · Generate your .conf fileOpenVPN Setup →Manual credentials and .ovpn fileUpload WireGuard →Add a Custom WireGuard connectionUpload OpenVPN →Add the file and service credentialsVerify Connection →Confirm VPN IP address and locationTroubleshooting →Fix connection failures and no internet

Proton VPN WireGuard Setup (Recommended)

WireGuard uses a configuration file generated by Proton VPN. You do not need an OpenVPN username and password for this method.

Generate Your Proton VPN WireGuard Configuration

  1. Open your Proton VPN account and sign in.
  2. Go to Downloads → WireGuard configuration.
  3. Enter a recognizable configuration name and select Router as the platform.
  4. Choose your preferred VPN options and an available server or country. For a straightforward setup, select a standard server configuration.
  5. Click Create, then Download to save the generated WireGuard .conf file to your device.

Important: A WireGuard configuration contains a private key. Keep the downloaded file private; do not paste its contents into public posts or unprotected support messages. For detailed Proton account instructions, see Proton VPN: Download WireGuard Configuration Files.

Upload WireGuard to Privacy Hero

  1. Open app.privacyhero.com and log in to your Privacy Hero account.
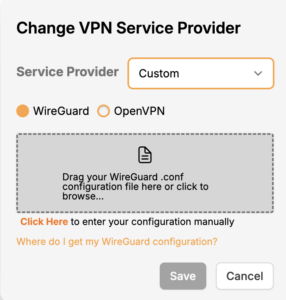
  2. Open the VPN section, click Change beside the VPN provider, and choose Custom.
  3. Select WireGuard and upload the Proton VPN .conf file you downloaded.
  4. Click Save to apply the configuration and connect. Confirm that Privacy Hero reports Connected.
Privacy Hero Custom WireGuard configuration screen showing the configuration file upload

Proton VPN OpenVPN Setup

OpenVPN is an alternative to WireGuard. You need a Proton VPN OpenVPN-specific username and password and a server .ovpn configuration file.

Get Your Proton VPN OpenVPN Credentials

  1. Sign in to your Proton VPN account.
  2. Open Account → OpenVPN username to find your separate OpenVPN username and password.
  3. Copy these credentials or keep the page open. Do not use your usual Proton Account email and password for the manual OpenVPN connection.

For help locating these credentials, see Proton VPN: How to Sign In / OpenVPN Credentials.

Download Your Proton VPN OpenVPN Server File

  1. In your Proton VPN account, go to Downloads → OpenVPN configuration files.
  2. Select Router as the platform and UDP as the protocol (recommended starting point). If UDP does not work on your network, you can try a TCP configuration later.
  3. Select an available country or individual server from the standard configuration list, then click Download to save its .ovpn file.

For additional details about the file download options, see Proton VPN: Download OpenVPN Configuration Files.

Upload OpenVPN to Privacy Hero

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
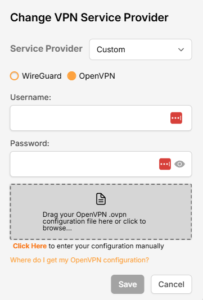
  2. Open the VPN section, click Change, and select Custom as the VPN provider.
  3. Choose OpenVPN and upload the Proton VPN .ovpn file you downloaded.
  4. Enter your separate Proton VPN OpenVPN username and password into the Custom VPN fields.
  5. Click Save, then confirm Privacy Hero displays Connected.
Privacy Hero Custom OpenVPN setup with configuration file upload and separate VPN username and password fields

Verify Your Proton VPN Connection

After Privacy Hero reports Connected, confirm that a device on the router network is using your Proton VPN connection.

  1. Connect your testing device to the Privacy Hero WiFi or LAN network.
  2. Disable any Proton VPN app or other VPN application running directly on that device, so it does not create a second VPN connection.
  3. Open a private/incognito browser window.
  4. Visit Proton VPN’s IP Address Checker.
  5. Verify that the public IP address and approximate location correspond to the Proton VPN server configured in Privacy Hero.

Important: You can manage Privacy Hero from another WiFi network or cellular data. However, the device performing the VPN IP test must be connected to the Privacy Hero network.

Streaming Relocation and VPN Location

If Privacy Hero Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation location rather than the country selected in your Proton VPN configuration. See Privacy Hero Streaming Relocation.


Proton VPN Not Connecting?

If Privacy Hero displays Failed, remains on Connecting, or reports a timeout, work through these checks:

  1. Confirm that you selected Custom as the VPN provider in Privacy Hero and chose the protocol that matches your configuration file.
  2. For WireGuard, create and download a fresh Proton VPN .conf file for an available server, then upload it again. Do not use an OpenVPN .ovpn file in the WireGuard section.
  3. For OpenVPN, verify that you entered Proton VPN’s separate OpenVPN username and password, not your regular Proton Account login.
  4. Download a fresh configuration for a different Proton VPN server and reconnect. Proton VPN occasionally changes server configurations.
  5. If using OpenVPN UDP and the connection still fails, download and try a TCP .ovpn configuration file to test for a protocol-related issue.
  6. Temporarily disable the VPN Kill Switch while checking whether internet works without the VPN. Re-enable your preferred Kill Switch setting once testing is complete.

VPN Disconnects and Devices Have No Internet?

The VPN Kill Switch may be intentionally blocking normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

Check the affected device for a second VPN app, iCloud Private Relay, Private DNS, browser proxy settings, or filtering software. See Device Settings That Can Interfere With Your Router VPN.
Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

IPVanish Setup for Privacy Hero

TeamFlashRouters · Sep 23, 2025 ·

Privacy Hero supports IPVanish VPN through WireGuard (recommended) and OpenVPN. Both are configured in Privacy Hero using the Custom VPN provider option. You will need an active IPVanish VPN subscription and the configuration file for the protocol and server location you select.

Choose your method: WireGuard uses a generated .conf file and generally provides better performance. OpenVPN uses a downloaded .ovpn file plus your IPVanish VPN username and password.

Privacy Hero is cloud-managed. You can sign in and adjust VPN settings from a computer, phone, or tablet connected to any internet connection. You do not need to be on the Privacy Hero WiFi network to configure the router.

IPVanish Setup Guide

Jump to the instructions you need.

WireGuard File →Generate a WireGuard server configurationWireGuard Setup →Upload your .conf file to Privacy HeroOpenVPN File →Download an IPVanish .ovpn server fileOpenVPN Setup →Enter credentials and upload the configurationVerify Connection →Check your public VPN IP addressTroubleshooting →Fix connection errors and IP issues

Download an IPVanish WireGuard Configuration (Recommended)

Use the WireGuard configuration generator in your IPVanish account to create a server file for your router. A generated WireGuard file contains the connection keys and server details, so keep it private.

  1. Open the IPVanish account sign-in page and log in.
  2. Open WireGuard in the account navigation to access the WireGuard Configuration Generator.
  3. Select your preferred IPVanish server location and choose Generate to download the WireGuard configuration file. Save the downloaded .conf file to the device you are using for setup.

Important: Do not publicly share your WireGuard configuration file. To switch server locations later, generate and upload a new configuration.

Add IPVanish WireGuard to Privacy Hero

  1. Sign in to the Privacy Hero dashboard at app.privacyhero.com.
  2. Open the VPN section, select Change beside the provider, and choose Custom.
  3. Choose WireGuard and upload the IPVanish .conf file you just generated.
  4. Click Save to apply the settings. Wait for Privacy Hero to report Connected.
Privacy Hero Custom WireGuard configuration with WireGuard file upload

WireGuard authentication is contained in the generated configuration file; there is no separate OpenVPN username/password step in this method.


Download an IPVanish OpenVPN Configuration File

OpenVPN is a good alternative if WireGuard is unavailable or fails to connect on your network. It requires an IPVanish .ovpn configuration file and VPN login credentials.

  1. Open the IPVanish OpenVPN server configuration list.
  2. Download an .ovpn file for your preferred available server location. If IPVanish provides both UDP and TCP files, start with UDP and keep a TCP file as a fallback.
  3. Have your IPVanish account username and password available for the OpenVPN setup. Use the credentials accepted by your IPVanish VPN account; these are not Privacy Hero login credentials.

If the linked server directory has changed, check the latest manual OpenVPN configuration downloads offered by IPVanish before selecting a file.

Add IPVanish OpenVPN to Privacy Hero

  1. Sign in at app.privacyhero.com and open VPN.
  2. Select Change, choose Custom, and select OpenVPN.
  3. Upload the IPVanish .ovpn file you downloaded.
  4. Enter your IPVanish username and password in the Custom OpenVPN fields. Do not enter the Privacy Hero account login.
  5. Click Save and wait for the connection status to show Connected.
Privacy Hero Custom OpenVPN configuration showing server file upload and username and password fields

Tip: If OpenVPN UDP times out or cannot connect, try an available IPVanish OpenVPN TCP configuration or another server location.


Verify Your IPVanish VPN Connection

After Privacy Hero displays Connected, verify that a device on the router is actually using IPVanish.

  1. Connect the device you want to test to the Privacy Hero WiFi or LAN network.
  2. Temporarily disconnect any IPVanish app, other VPN app, or device-level VPN connection on that device so you test the router VPN alone.
  3. Open a new private/incognito browser window and visit IPVanish What Is My IP Address.
  4. Confirm that your public IP address and approximate location correspond to the VPN server you selected.

Note: Privacy Hero settings can be managed remotely, but the device used for this IP test must be on the Privacy Hero network.

Streaming Relocation and Your VPN Location

If Streaming Relocation is enabled for a supported streaming service, that service may use the configured Streaming Relocation location instead of the IPVanish server location. See Privacy Hero Streaming Relocation.


IPVanish Not Connecting?

If Privacy Hero remains on Connecting, displays Failed, or reports a timeout, check the following:

  1. Make sure your IPVanish subscription is active and that Custom is selected as the VPN provider in Privacy Hero.
  2. For WireGuard, generate a fresh configuration from your IPVanish account and upload that .conf file again.
  3. For OpenVPN, confirm your IPVanish username/password and upload a fresh .ovpn file for a different server.
  4. Try a different server location. With OpenVPN, also try switching between available UDP and TCP files.
  5. Temporarily disable the Privacy Hero VPN connection and test normal internet access. If enabled, temporarily turn off the VPN Kill Switch for this test, then restore your preferred Kill Switch setting.
  6. Check whether a device-level VPN app, private DNS, proxy, or security software is interfering with the router VPN connection.

VPN Disconnected and No Internet?

The VPN Kill Switch can intentionally block internet access when the VPN disconnects. Review Privacy Hero VPN Kill Switch Setup.

VPN Connected but One Device Shows the Wrong IP?

If only one device shows an unexpected IP address, look for another VPN app, iCloud Private Relay, Private DNS, browser proxy/DNS settings, or security software on that device. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

VPN Unlimited Manual OpenVPN Setup

TeamFlashRouters · Apr 19, 2019 ·

Preparing for Manual VPN Unlimited Setup

Verify your VPN Unlimited login information

If you are not already a VPN Unlimited user Sign Up Now.

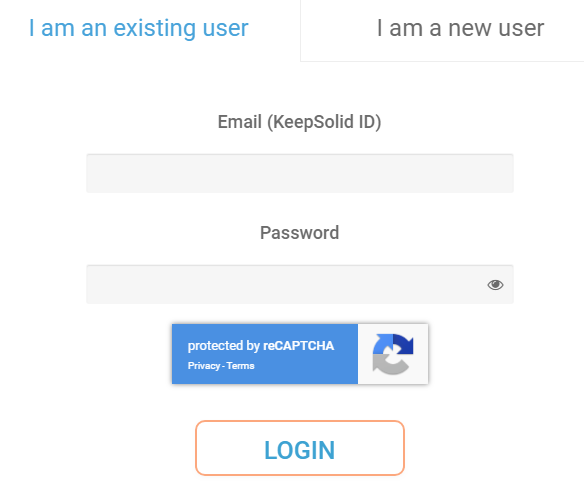
Log in to your account on the VPN Unlimited website.

VPN Unlimited Website Login

Generate your VPN Unlimited OVPN Configuration Files

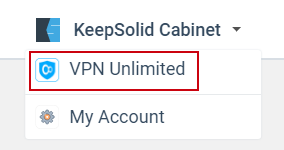
1. Navigate to the VPN Unlimited section in the dropdown on the top left.

VPN Unlimited Website Login

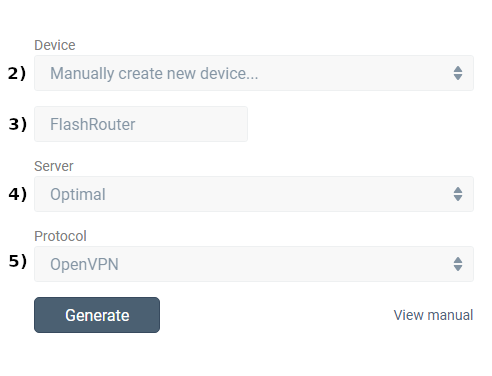
2. Set Device to “Manually create new device…”

3. Name your device.

4. Select Server.

5. Set Protocol to OpenVPN.

FlashRouters DD-WRT Privacy App - Create Open VPN Configuration files

6. Open the ‘.OVPN’ file in a word processing program.

NOTE: We highly recommend using Notepad++ for Windows or TextEdit for Apple to open these files in order to preserve text format.

DD-WRT Router Setup for VPN Unlimited

Navigate to the Services > VPN

Enter VPN Unlimited settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the bottom of the .ovpn file you downloaded above, you can find your server address, it should look something like us-la.vpnunlimitedapp.com

Port

1194 for Tunnel Protocol UDP
80 for Tunnel Protocol TCP

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

Blowfish-CBC

Hash Algorithm

SHA1

User Pass Authentication

Disabled

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIEjjCCA/egAwIBAgIJAKsVbHBdakXuMA0GCSqGSIb3DQEBBQUAMIHgMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCTlkxETAPBgNVBAcTCE5ldyBZb3JrMR8wHQYDVQQK
ExZTaW1wbGV4IFNvbHV0aW9ucyBJbmMuMRYwFAYDVQQLEw1WcG4gVW5saW1pdGVk
MSMwIQYDVQQDExpzZXJ2ZXIudnBudW5saW1pdGVkYXBwLmNvbTEjMCEGA1UEKRMa
c2VydmVyLnZwbnVubGltaXRlZGFwcC5jb20xLjAsBgkqhkiG9w0BCQEWH3N1cHBv
cnRAc2ltcGxleHNvbHV0aW9uc2luYy5jb20wHhcNMTMxMjE2MTM1OTQ0WhcNMjMx
MjE0MTM1OTQ0WjCB4DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAk5ZMREwDwYDVQQH
EwhOZXcgWW9yazEfMB0GA1UEChMWU2ltcGxleCBTb2x1dGlvbnMgSW5jLjEWMBQG
A1UECxMNVnBuIFVubGltaXRlZDEjMCEGA1UEAxMac2VydmVyLnZwbnVubGltaXRl
ZGFwcC5jb20xIzAhBgNVBCkTGnNlcnZlci52cG51bmxpbWl0ZWRhcHAuY29tMS4w
LAYJKoZIhvcNAQkBFh9zdXBwb3J0QHNpbXBsZXhzb2x1dGlvbnNpbmMuY29tMIGf
MA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQDADUzS8QWGvdhLFKsEzAiq5+b0ukKj
Bza0k6/dmCeYTvCVqGKg/h1IAtQdVVLAkmEp0zvGH7PuOhXm7zZrCouBr/RiG4tE
coRHwc6AJmowkYERlY7+xGx3OuNrD00QceNTsan0bn78jwt0zhFNmHdoTtFjgK3o
qmQYSAtbEVWYgwIDAQABo4IBTDCCAUgwHQYDVR0OBBYEFKClmYP+tMNgWagUJCCH
jtaui2k+MIIBFwYDVR0jBIIBDjCCAQqAFKClmYP+tMNgWagUJCCHjtaui2k+oYHm
pIHjMIHgMQswCQYDVQQGEwJVUzELMAkGA1UECBMCTlkxETAPBgNVBAcTCE5ldyBZ
b3JrMR8wHQYDVQQKExZTaW1wbGV4IFNvbHV0aW9ucyBJbmMuMRYwFAYDVQQLEw1W
cG4gVW5saW1pdGVkMSMwIQYDVQQDExpzZXJ2ZXIudnBudW5saW1pdGVkYXBwLmNv
bTEjMCEGA1UEKRMac2VydmVyLnZwbnVubGltaXRlZGFwcC5jb20xLjAsBgkqhkiG
9w0BCQEWH3N1cHBvcnRAc2ltcGxleHNvbHV0aW9uc2luYy5jb22CCQCrFWxwXWpF
7jAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBBQUAA4GBALkWhfw7SSV7it+ZYZmT
+cQbExjlYgQ40zae2J2CqIYACRcfsDHvh7Q+fiwSocevv2NE0dWi6WB2H6SiudYj
vDvubAX/QbzfBxtbxCCoAIlfPCm8xOnWFN7TUJAzWwHJkKgEnu29GZHu2x8J+7Ve
DbKH5RTMHHe8FkSxh6Zz/BMN
—–END CERTIFICATE—–

Public Client Cert

Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN RSA PRIVATE KEY—–
…
—–END RSA PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful VPN Unlimited connection

Navigate to the Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit to WhatIsMyIPAddress to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to VPN Unlimited.

Back up your settings

Navigate to the Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the VPN Unlimited server

  1. Follow Steps 1-6 to Generate an .OVPN file for the server you wish to connect to and open it a word processing program.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the <cert> into the Public Client Cert field.
  4. Copy and paste the <key> into the Private Client Key field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN Setup Guide for GL.iNet Routers

Dave · Mar 23, 2026 ·

You can connect to ProtonVPN on your GL.iNet router using Wireguard or OpenVPN.

Quick Options

  • Wireguard: Download your preferred server .conf configuration file from the ProtonVPN website.

  • OpenVPN: Download your preferred server .ovpn configuration file from the ProtonVPN website.

:point_right: If you are not already a ProtonVPN user Sign Up Now.

ProtonVPN Wireguard Setup for GLiNet (Recommended)

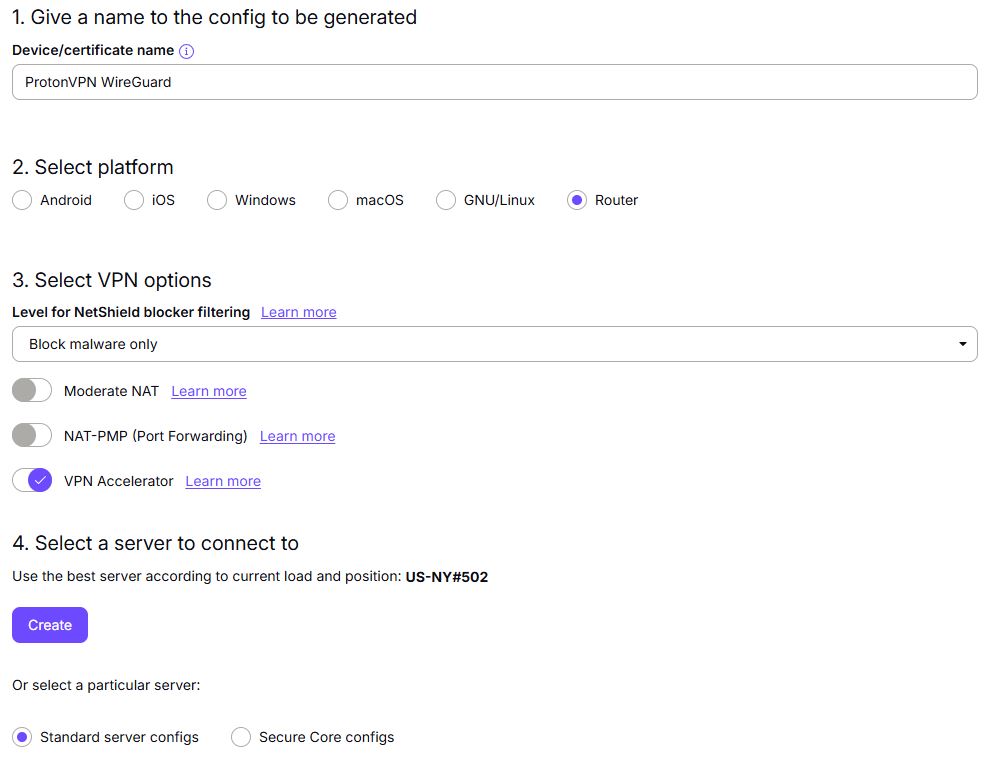
1. Login to your ProtonVPN account and go to the Downloads section of your ProtonVPN account page

2. Scroll down to find the WireGuard configuration section. Name your configuration and then select Router as the platform, and select Standard server configs.

3. Click Create button to choose the recommended server or scroll down to choose and Download any of the available server files from the list.

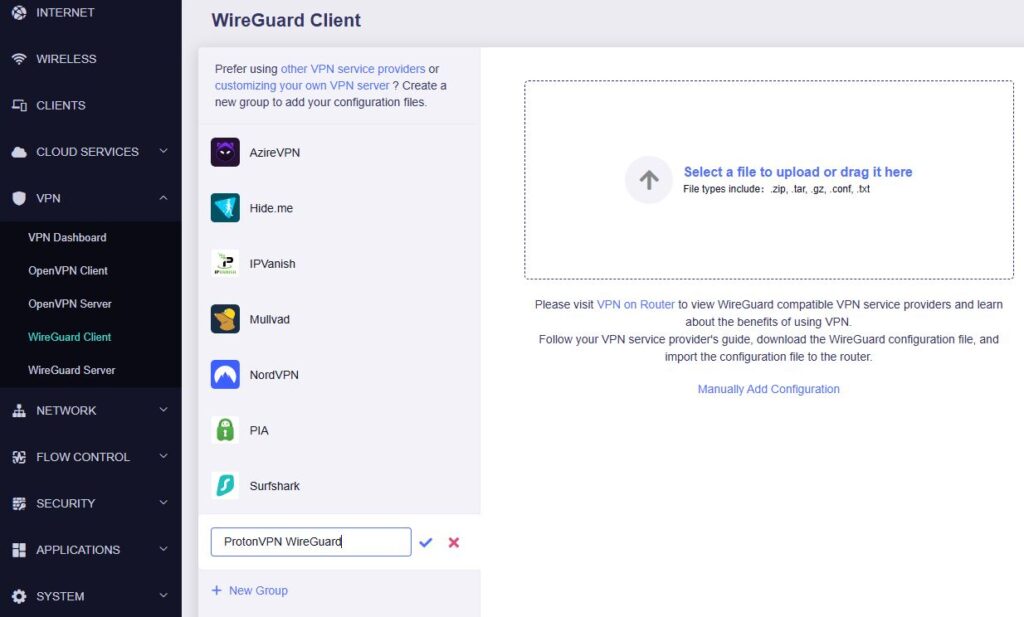
4.  Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

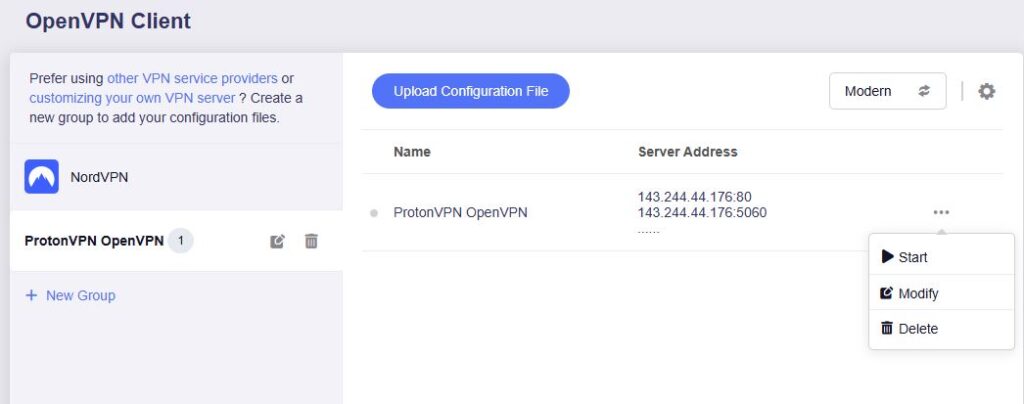
5. Navigate to the VPN tab and select WireGuard Client then click + New Group and name your connection and click the check to save.

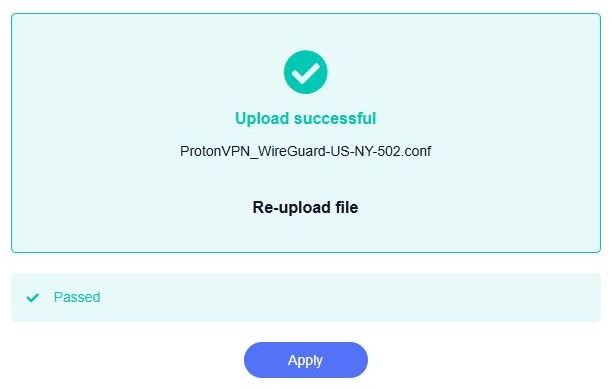
6. Upload the configuration file and click Apply.

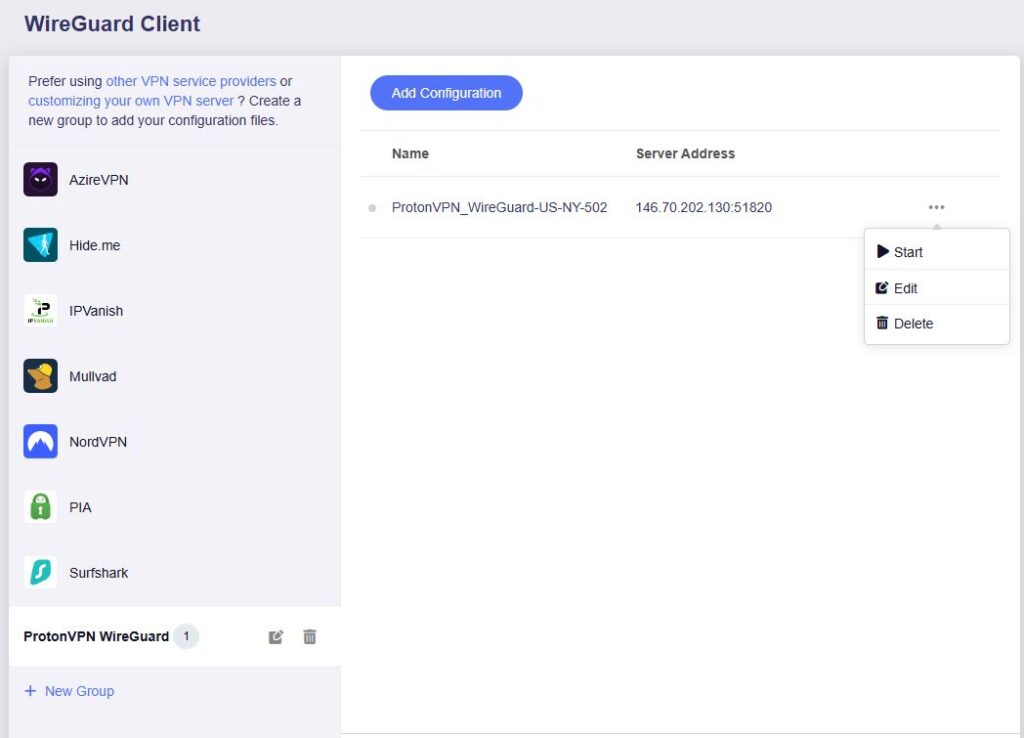
7. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

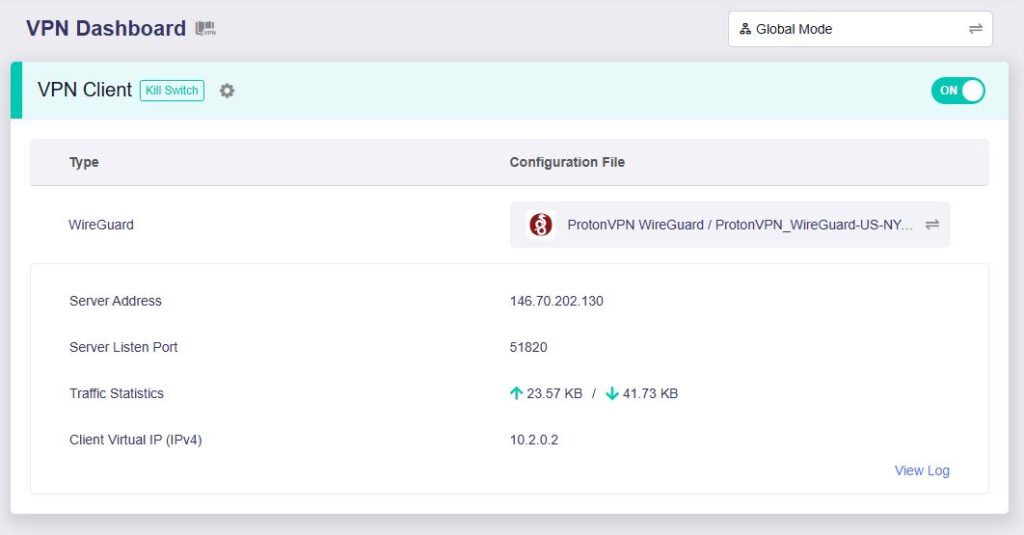
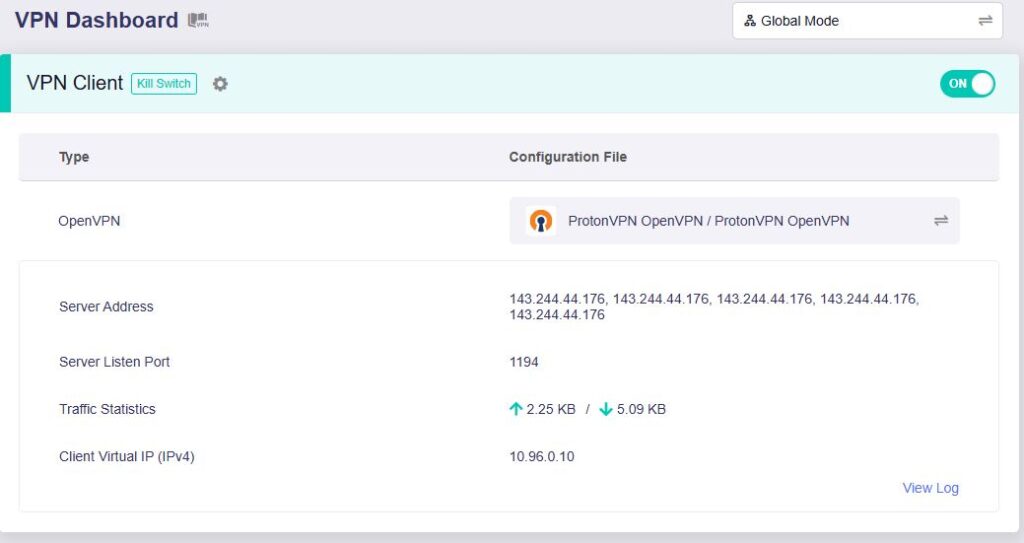
8. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

ProtonVPN OpenVPN Setup for GLiNet

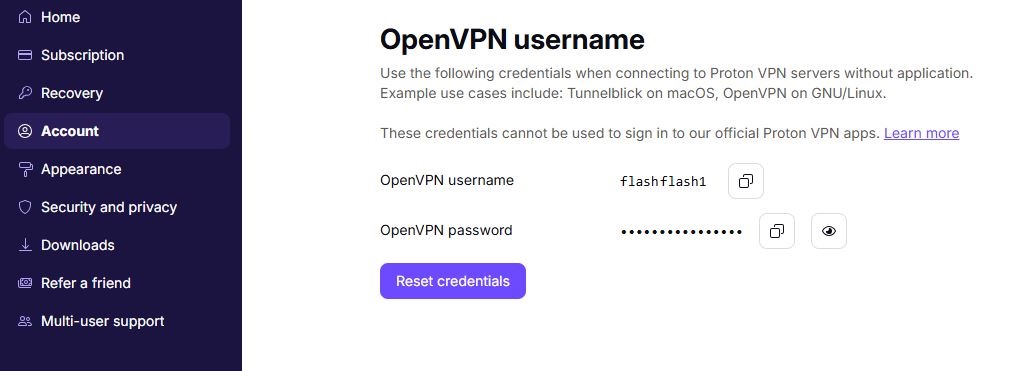
1. Log in to your ProtonVPN account and navigate to the Account tab. Scroll down to find your OpenVPN specific Username and Password.

2. Go to the Downloads section of your ProtonVPN account page

ProtonVPN Downloads

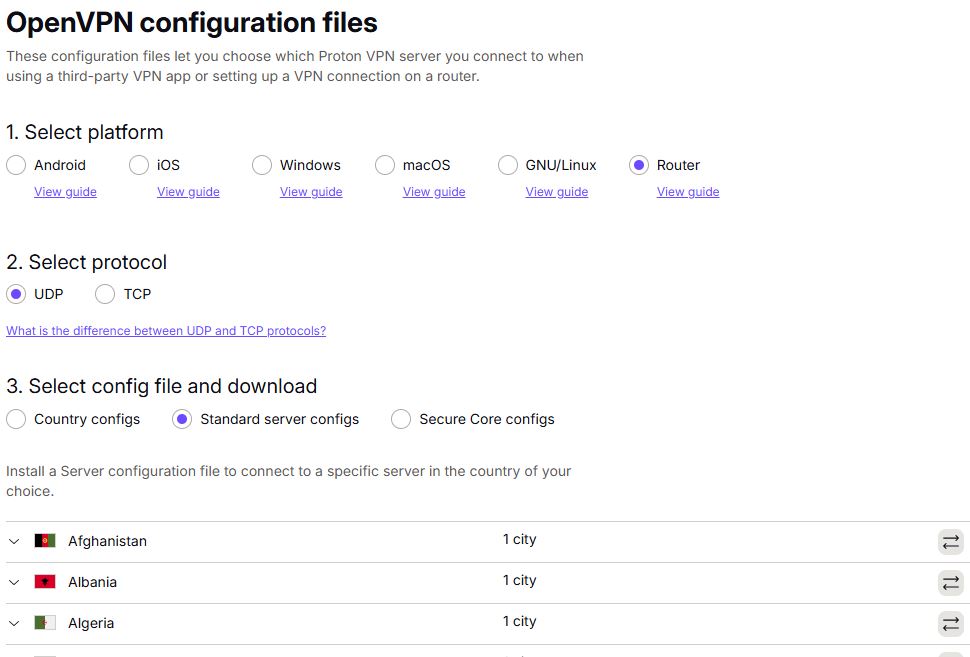
3. Scroll down to find the OpenVPN configuration Files. Select Router as the platform, UDP as the protocol, and select Standard server configs. Choose your preferred country and download the configuration file.

4. Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

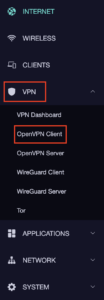
5. Navigate to the VPN tab and select OpenVPN Client.

GL.iNet VPN OpenVPN Client

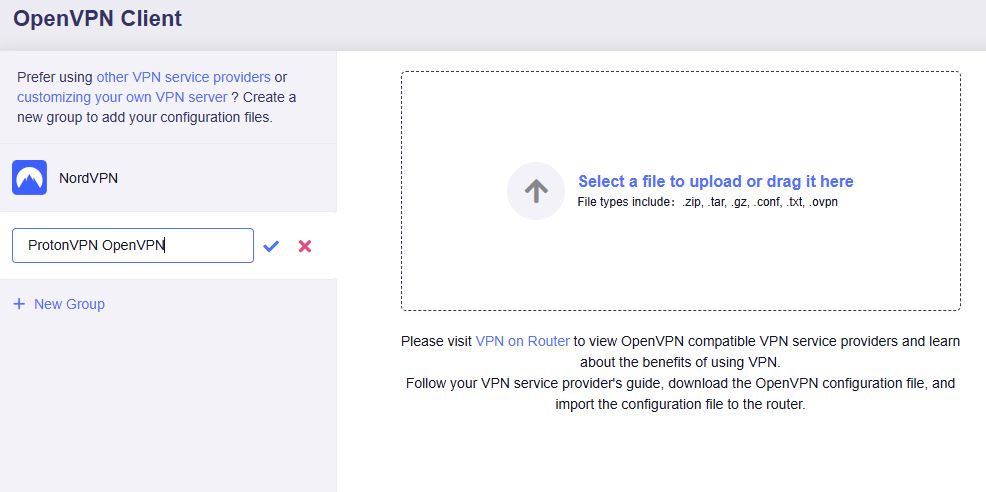
6. Select Add Manually then click + New Group and name your connection and click the check to save.

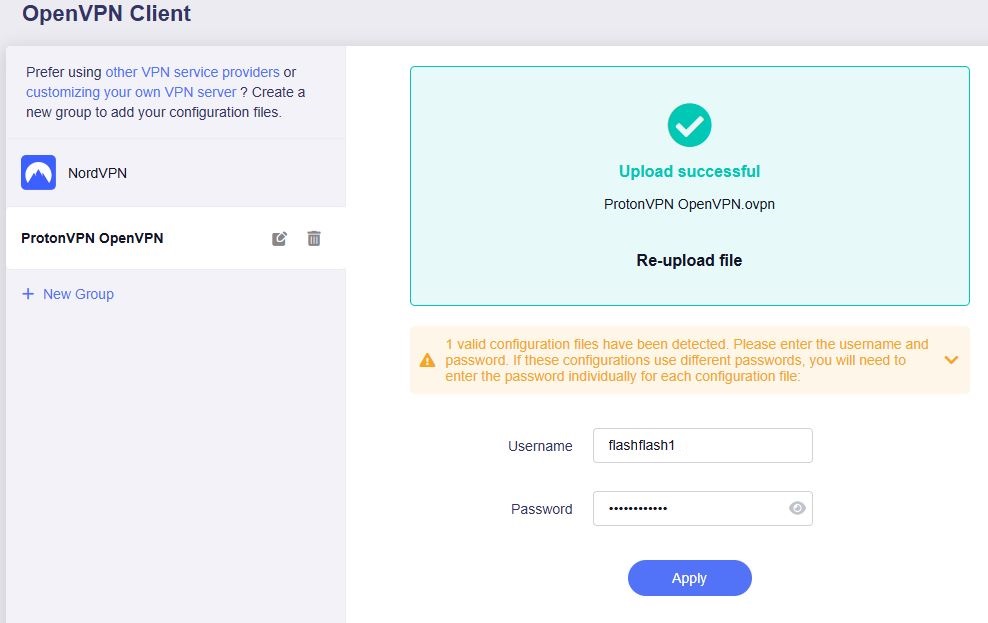
7. Upload the configuration file and input your username and password, click Apply.

8. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

9. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

  1. You should now see information appear in the Server Address, Server Listen Port, Traffic Statistics, and Client Virtual IP areas.
  2. Visit ProtonVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

🚫📱Do not run ProtonVPN apps on devices connected to your ProtonVPN router. Using the app at the same time as the router VPN may cause conflicts and connection issues.

Still having issues?

Feel free to submit a ticket and we will get back to you as soon as possible.

CyberGhost AsusWRT OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for CyberGhost Setup

Obtain your CyberGhost OpenVPN information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

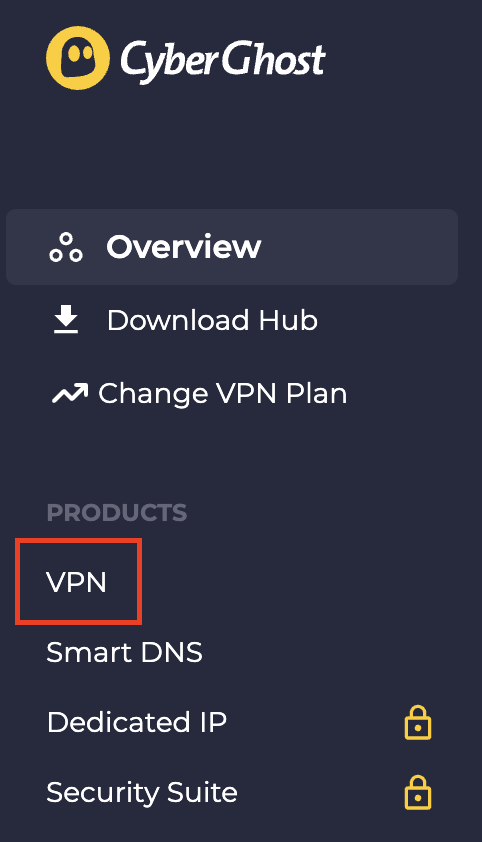
2. Select VPN.

CyberGhost VPN

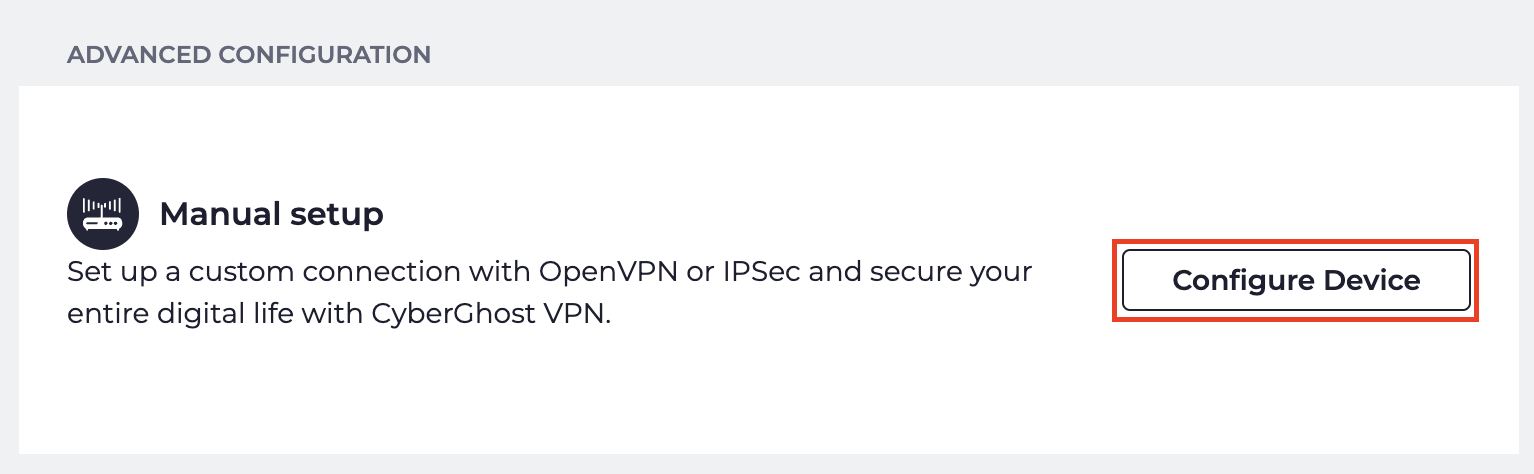
3. Click Configure New Device.

CyberGhost Configure Device

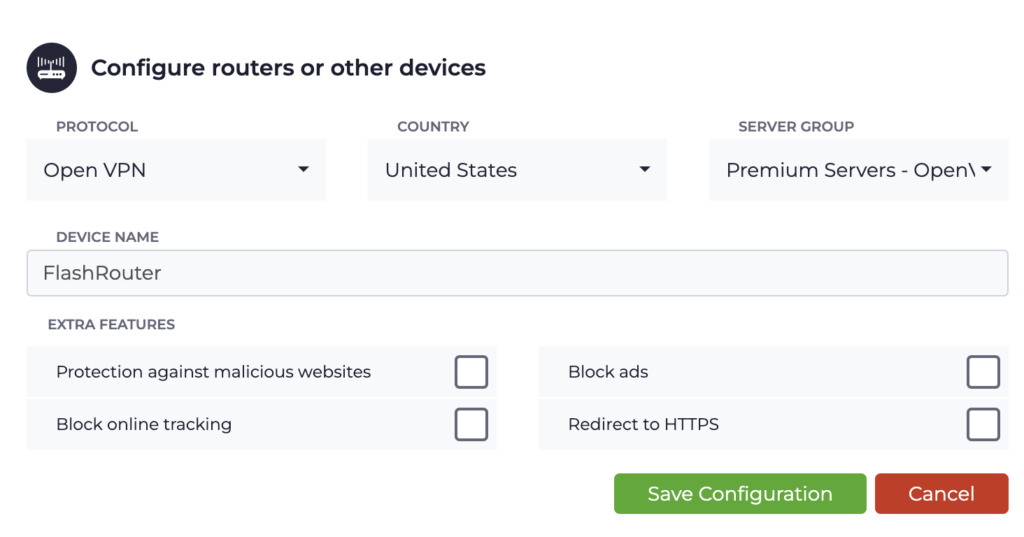
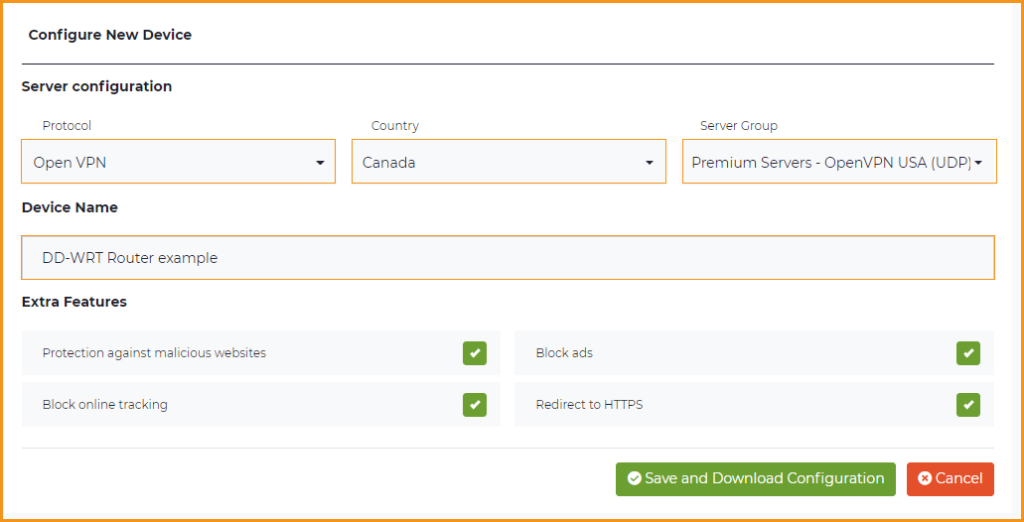
4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost protocol and location

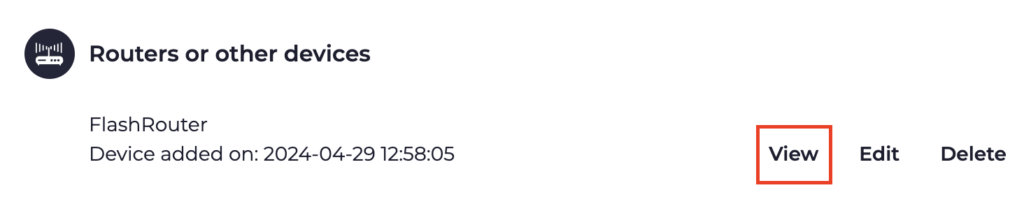
5. Press View configuration.

CyberGhost view configuration

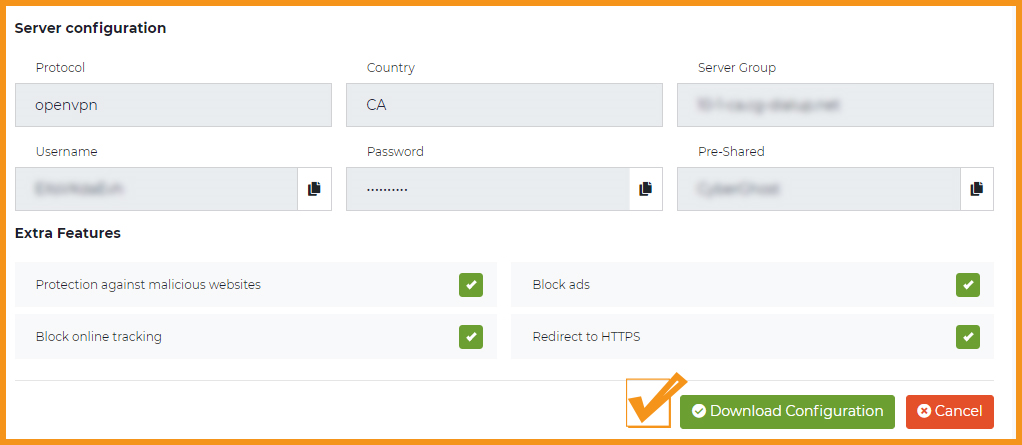
6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the folder that was downloaded. Then open the ca.crt the client.crt, and client.key files with NotePad++ for Windows or TextEdit for Apple. All CyberGhost servers have different keys and certificates.

AsusWRT Router Setup for CyberGhost

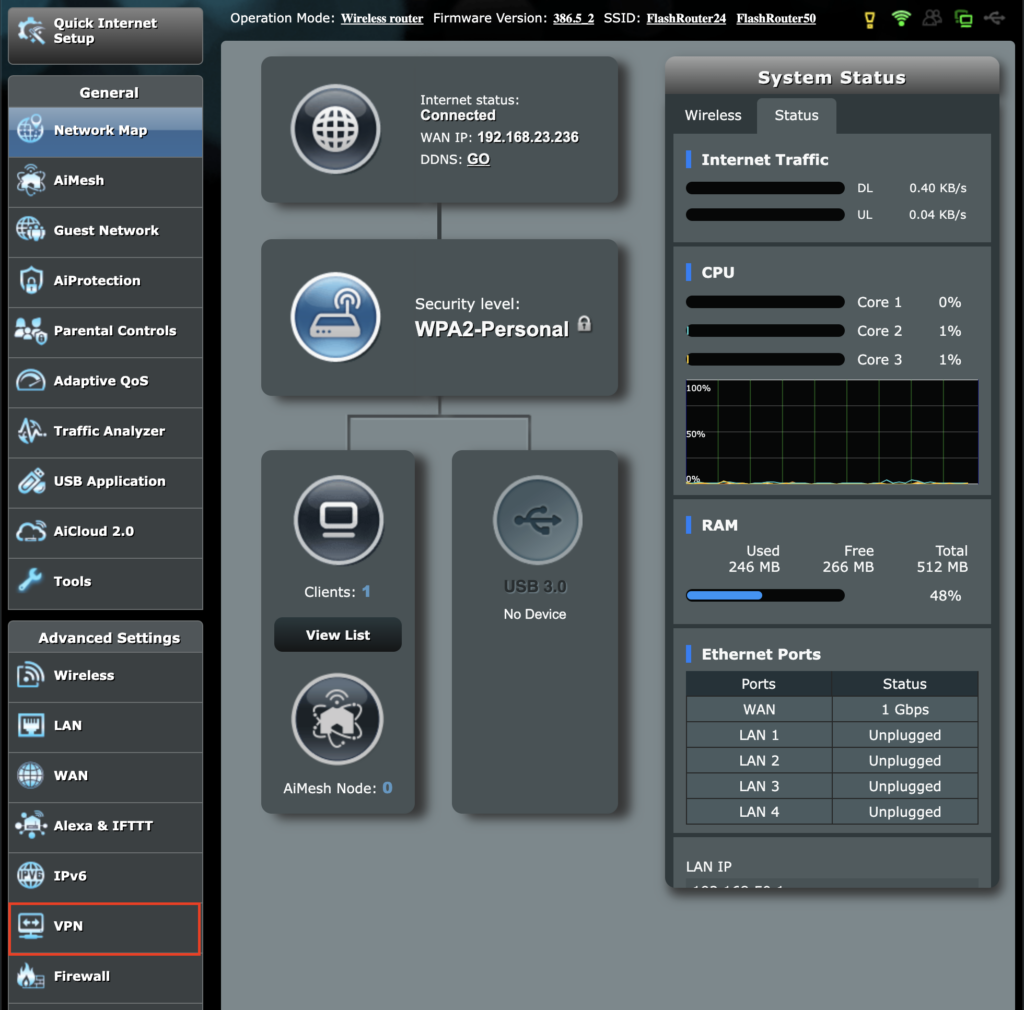
Login to AsusWRT firmware settings in a browser on any computer or smart device connected to the AsusWRT FlashRouter’s network.

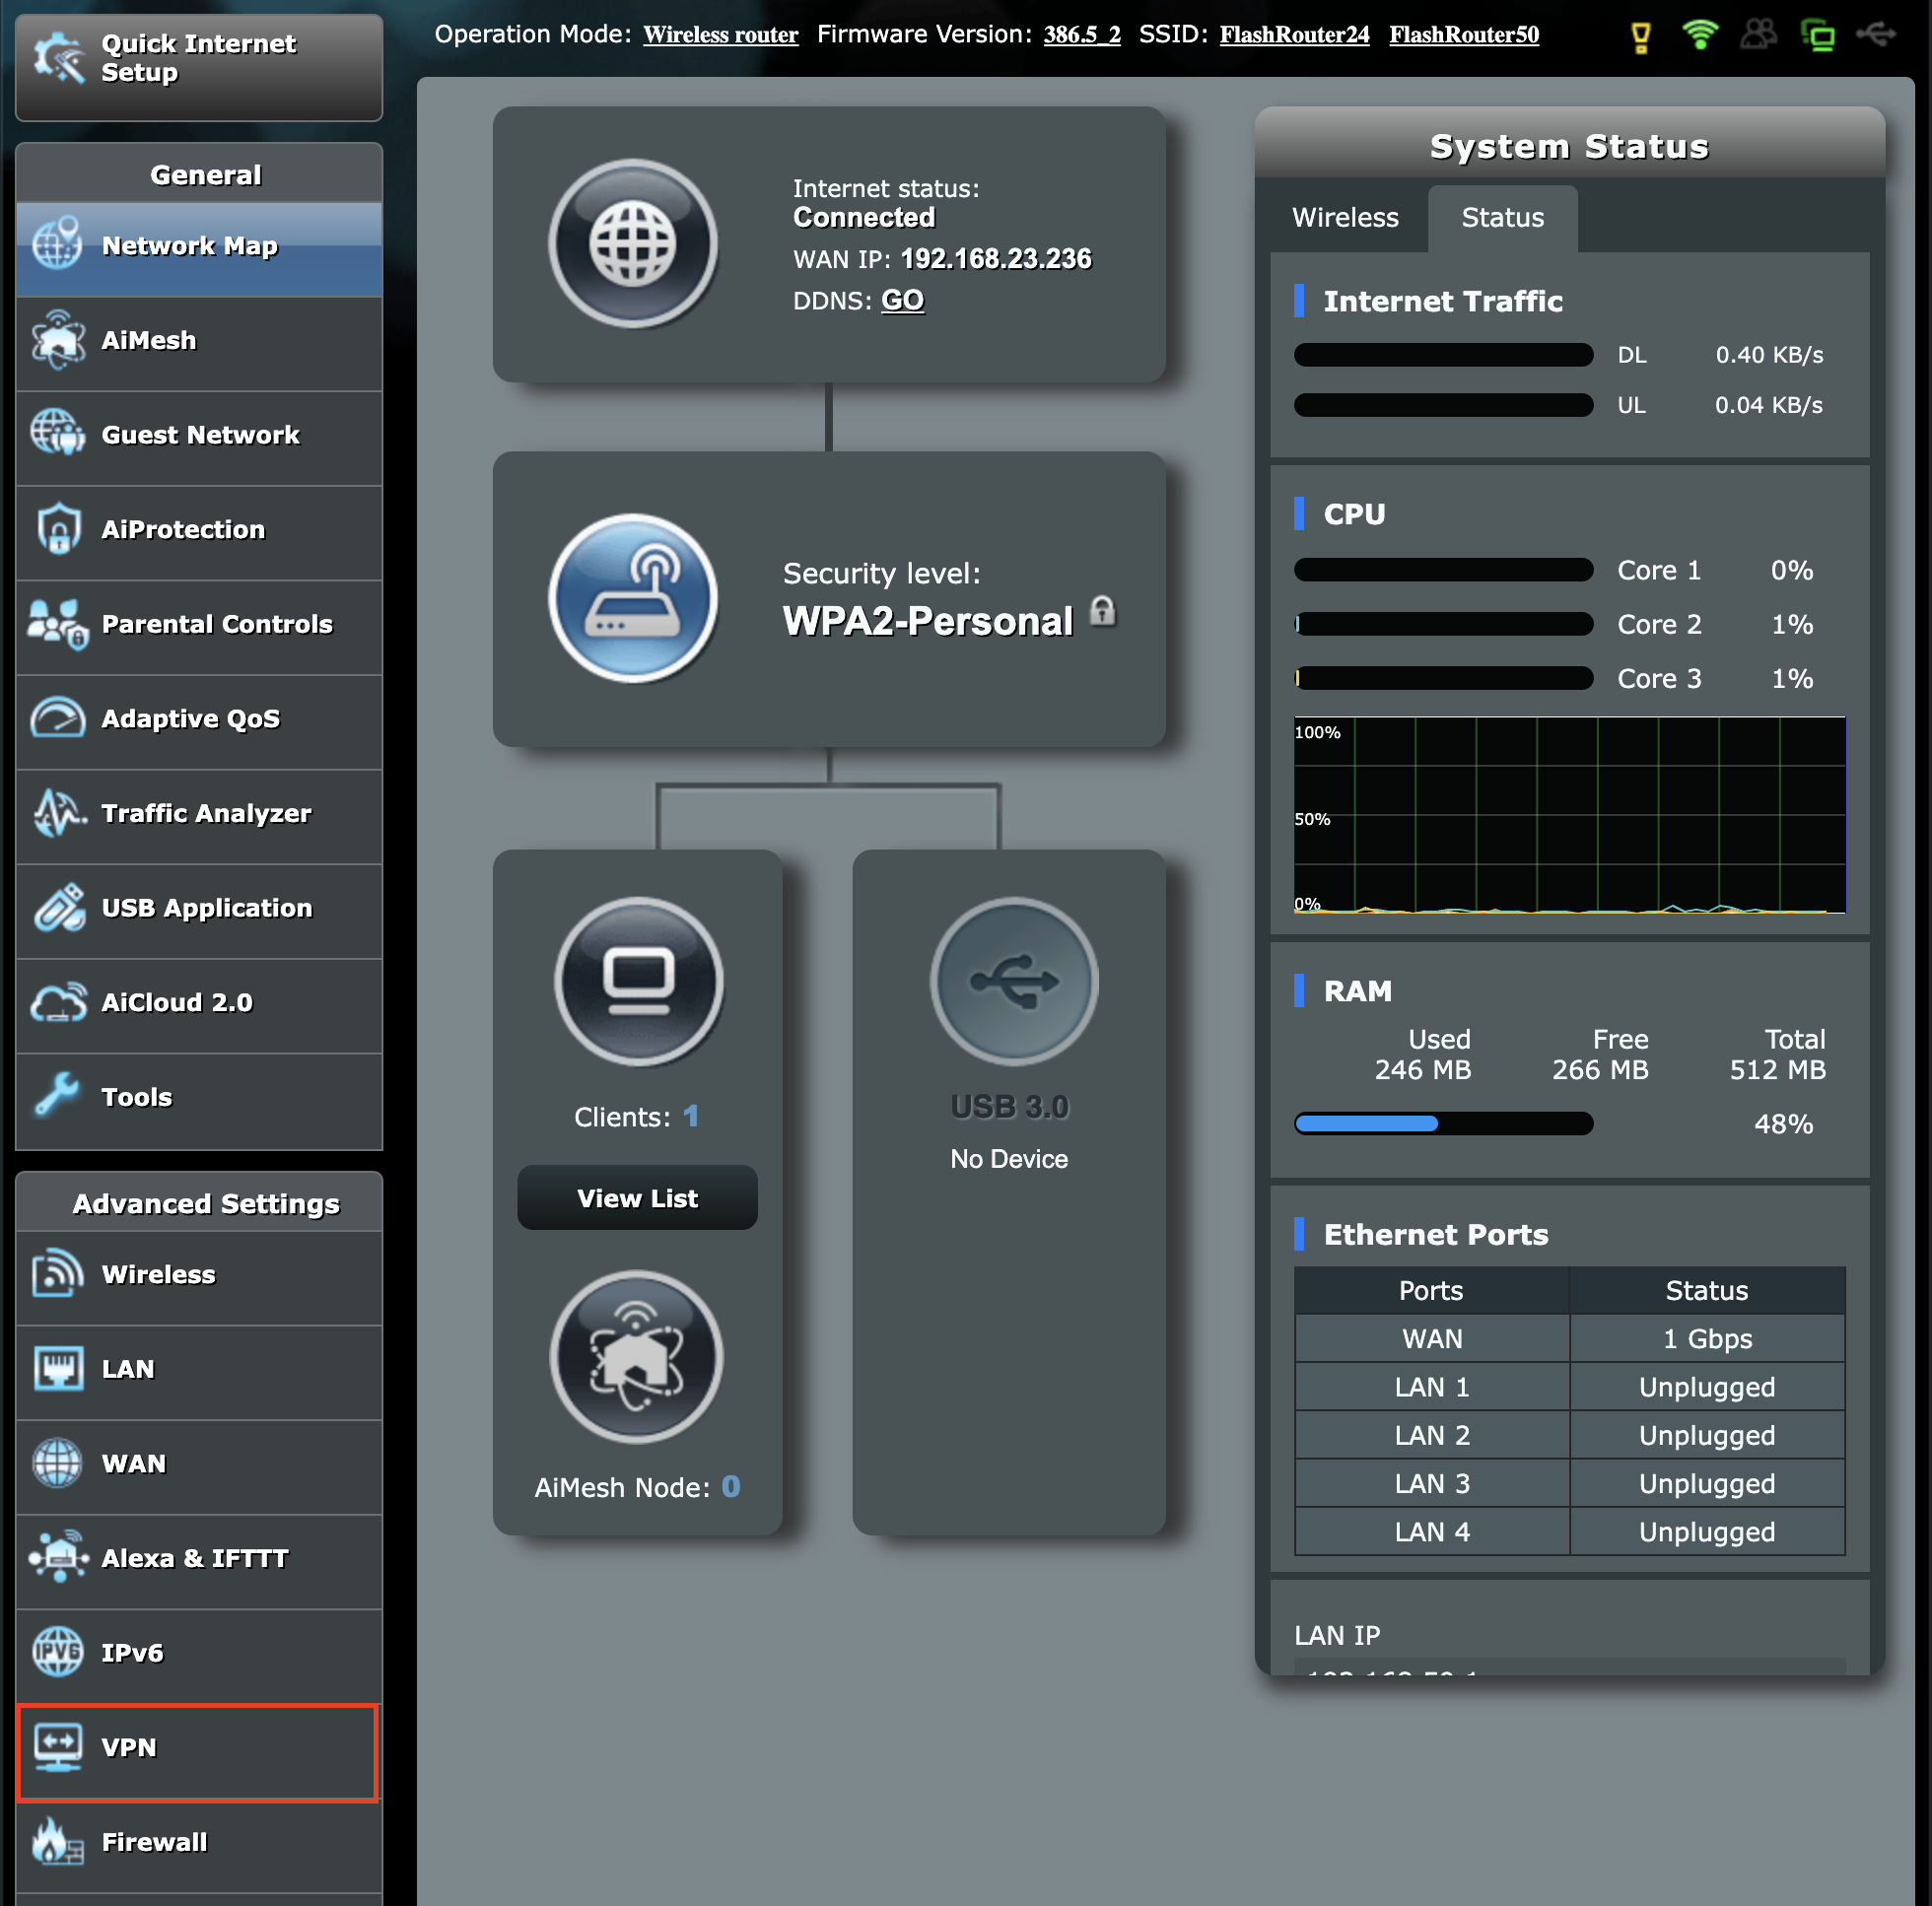
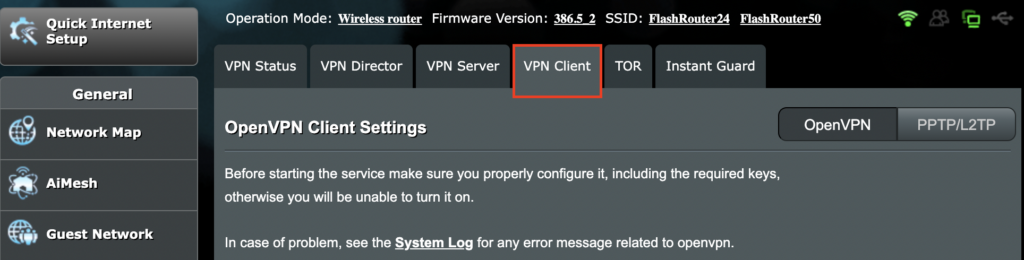
1. Navigate to the VPN tab.

Merlin VPN Tab

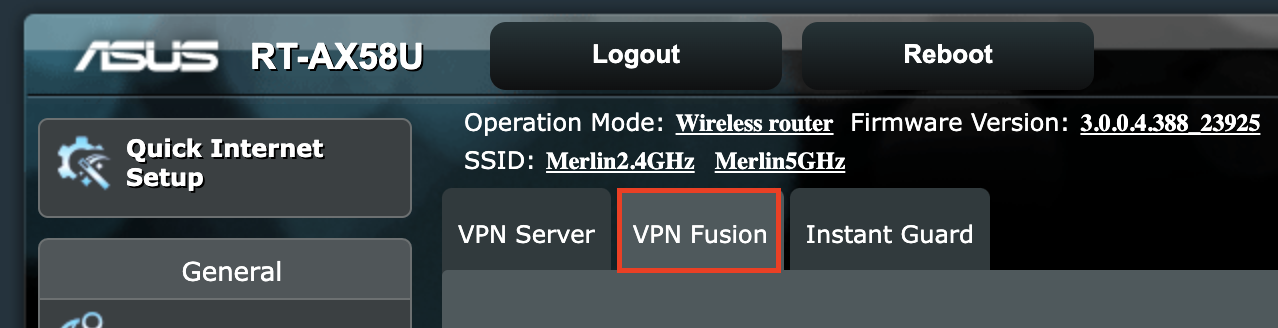
2. Navigate to the VPN Fusion tab.

Asus VPN Fusion

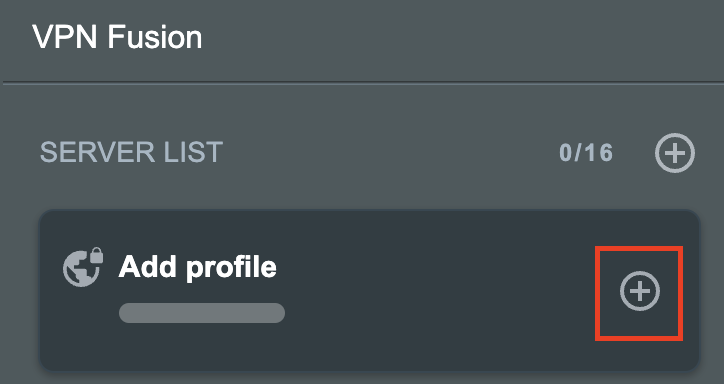
3. Click Add profile.

Asus Add profile

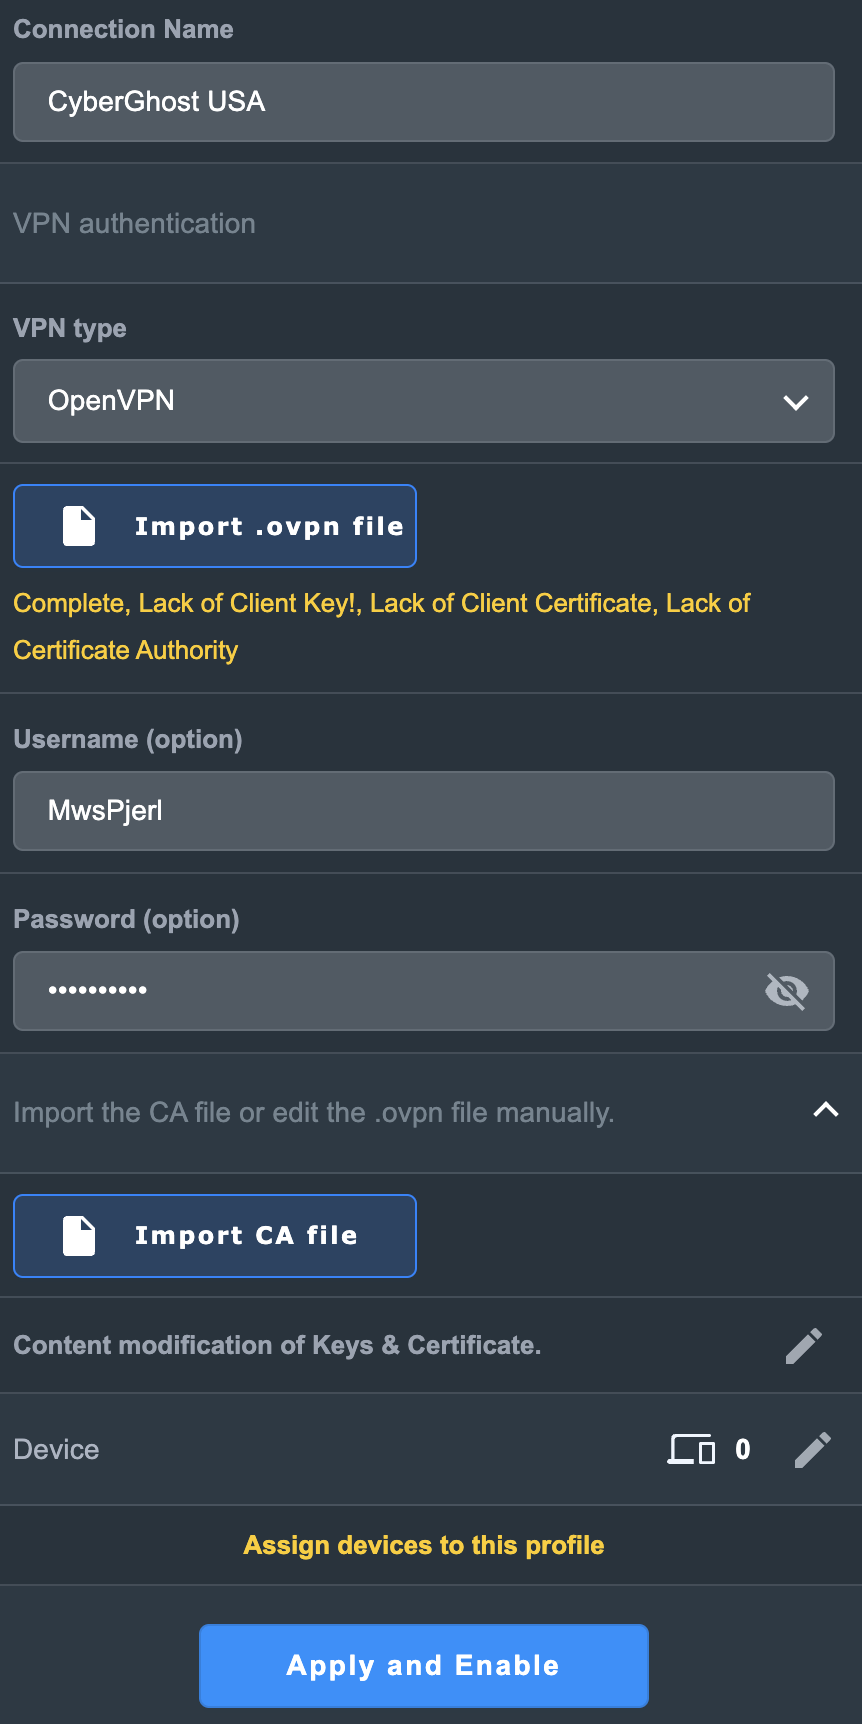
4. In the Connection Name field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was in USA so I have entered in CyberGhost USA.

5. In the VPN Type dropdown select OpenVPN.

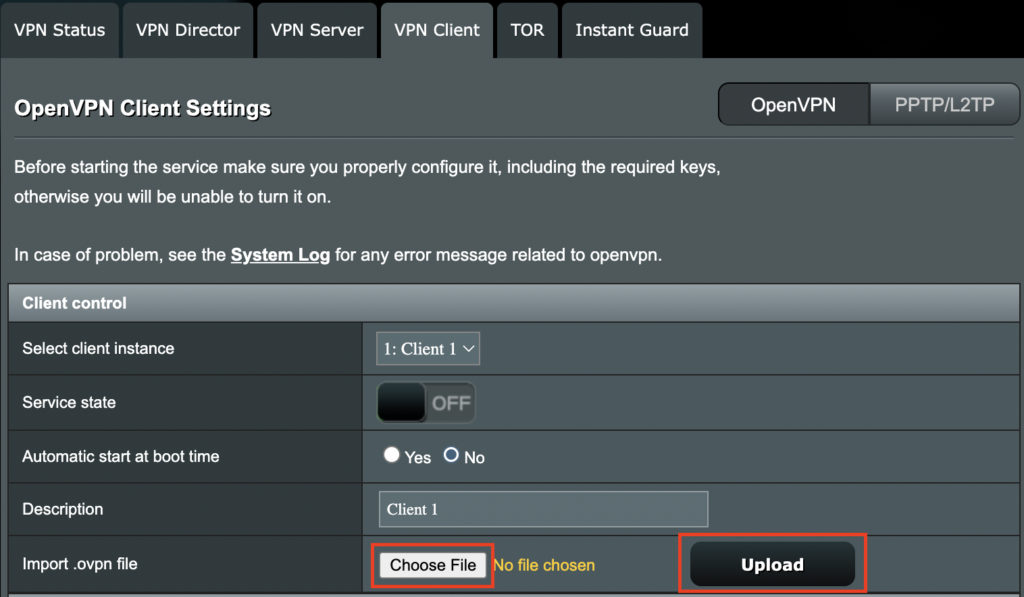
6. Click Import .ovpn file and select the openvpn.ovpn file from the folder you downloaded earlier. Then click Upload.

7. In the Username and Password fields enter in the CyberGhost assigned username and password that you obtained earlier.

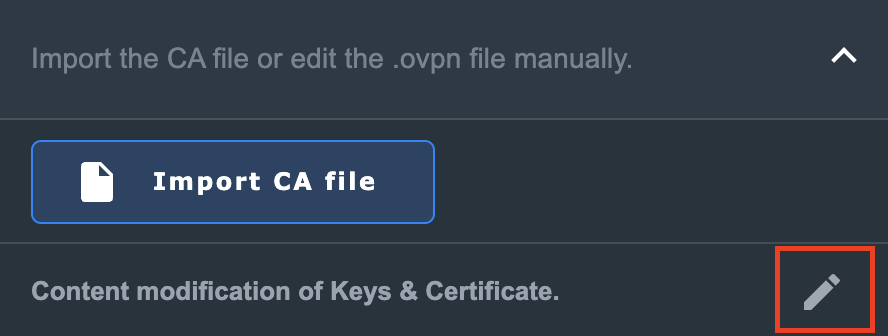
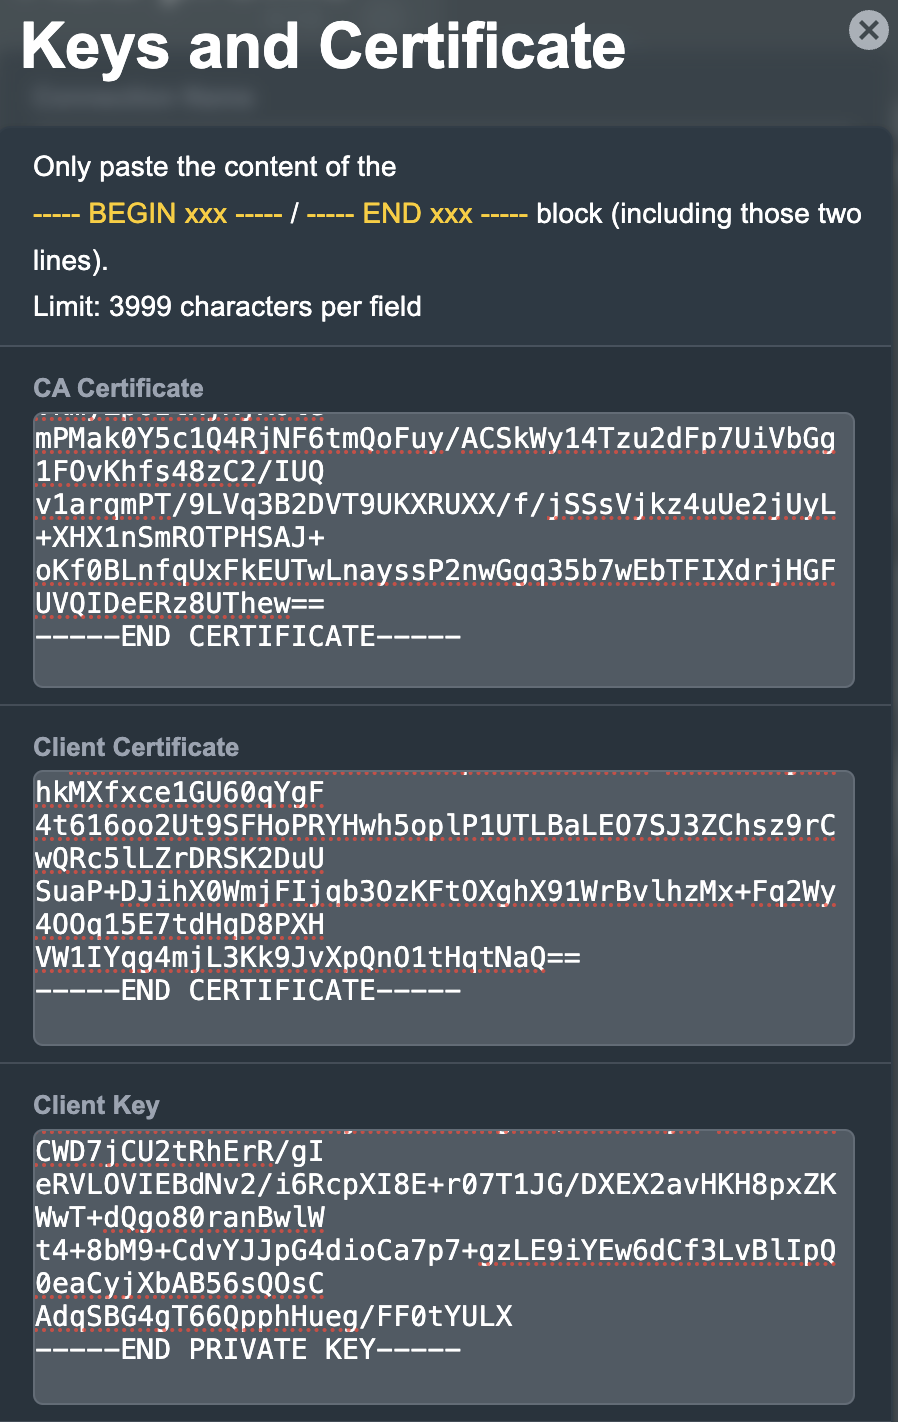
8. After uploading the openvpn.ovpn file you will get a message that says “Complete, Lack of Client Key!, Lack of Client Certificate, Lack of Certificate Authority”. For CyberGhost you need to enter in these details manually. Click Import the CA file or edit the .ovpn file manually and then click the edit icon next to Content modification of Keys and Certificate.

Asus CyberGhost import certs and keys

9. In the Certificate Authority field paste in the entire content of the ca.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

10. In the Client Certificate field paste in the entire content of the client.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

11. In the Client Key field paste in the entire content of the client.key file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Then click OK.

Asus CyberGhost enter certs and keys

8. Click Apply and Enable at the bottom of the page.

Asus CyberGhost profile

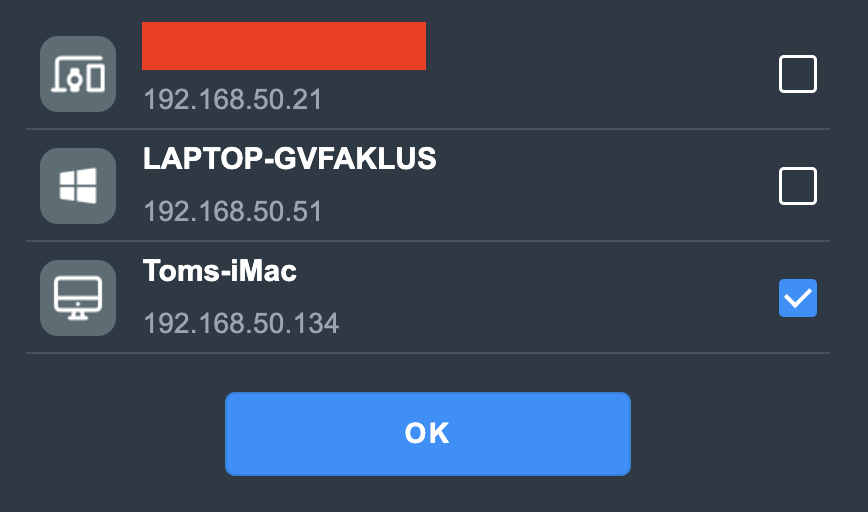
If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network click into the profile and disable Apply to all devices. Then click Devices and select the devices that you want to connect to VPN.

Asus VPN devices
Asus VPN select devices

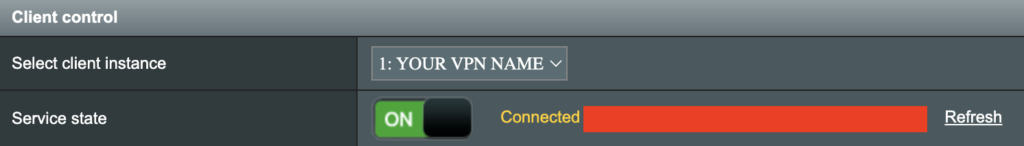
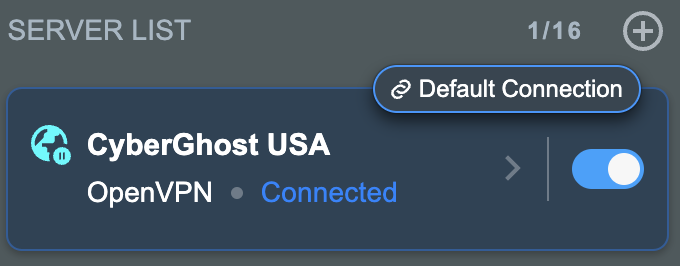
9. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Asus CyberGhost connected

Verify a successful CyberGhost connection

  1. You should now see a CONNECTED message.
  2. Visit What is my IP Address from a private/incognito browser to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to CyberGhost.

How to change the CyberGhost server

  1. Follow the steps at the top of the page to create a new CyberGhost location profile in your account.
  2. Then proceed with the settings same as initial setup.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

CyberGhost Merlin OpenVPN Setup

TeamFlashRouters · Mar 30, 2023 ·

Preparing for CyberGhost Setup

Obtain your CyberGhost OpenVPN information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

2. Select VPN.

CyberGhost VPN

3. Click Configure New Device.

CyberGhost Configure Device

4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost protocol and location

5. Press View configuration.

CyberGhost view configuration

6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the folder that was downloaded. Then open the ca.crt the client.crt, and client.key files with NotePad++ for Windows or TextEdit for Apple. All CyberGhost servers have different keys and certificates.

Merlin Router Setup for CyberGhost

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Click Choose file and select the .ovpn file from the folder you downloaded earlier. Then click Upload.

Merlin Choose File Upload

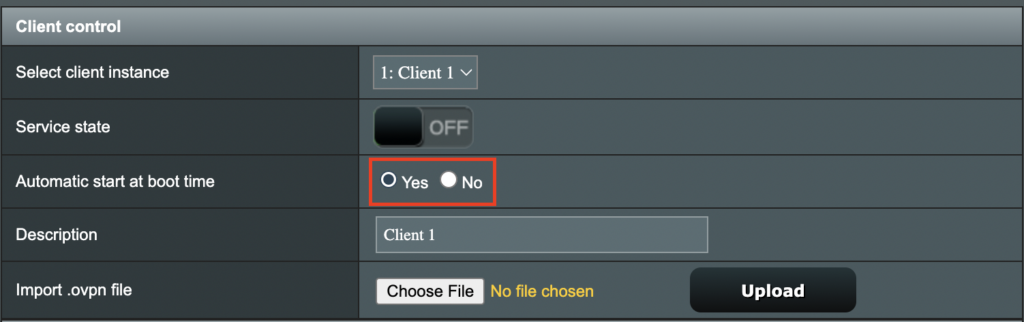
4. Set Automatic Start at boot time to Yes if you want the VPN connection to begin automatically when the router is powered off and back on.

Merlin Automatic Start at boot time

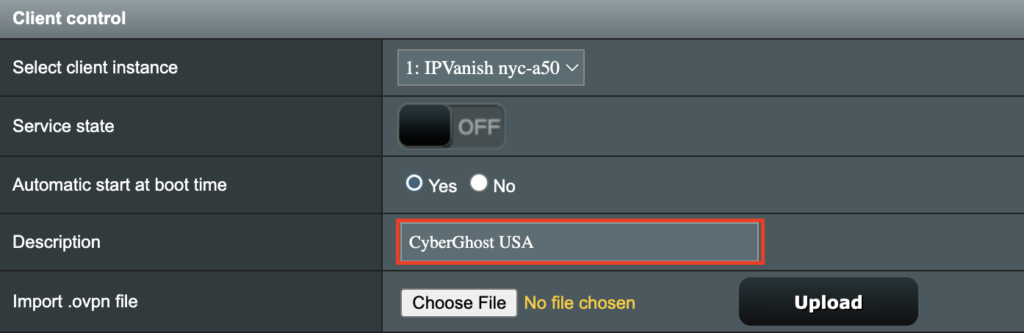
5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location here. Our example server was in USA so I have entered in CyberGhost USA.

Merlin CyberGhost Description field

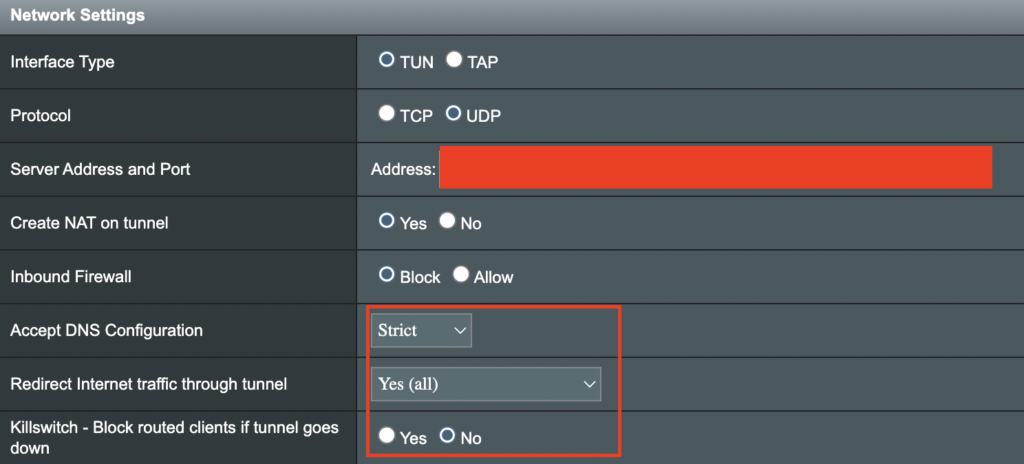
6. Set Accept DNS Configuration to Strict. Set Redirect Internet traffic through tunnel to Yes (all). Set Kill Switch to Yes or No depending on if you want the Internet to be killed if the VPN connection drops.

Merlin Accept DNS configuration Redirect Internet and Kill Switch

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network please set the Redirect Internet traffic through tunnel to VPN Director. Then complete the instructions on this page and then view our VPN Director guide.

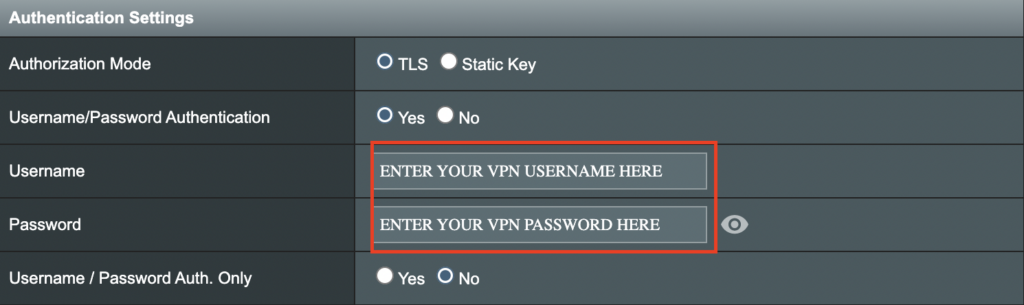
7. Enter your CyberGhost OpenVPN username and password that you obtained earlier. Do not enter your account login.

Merlin VPN Username and Password

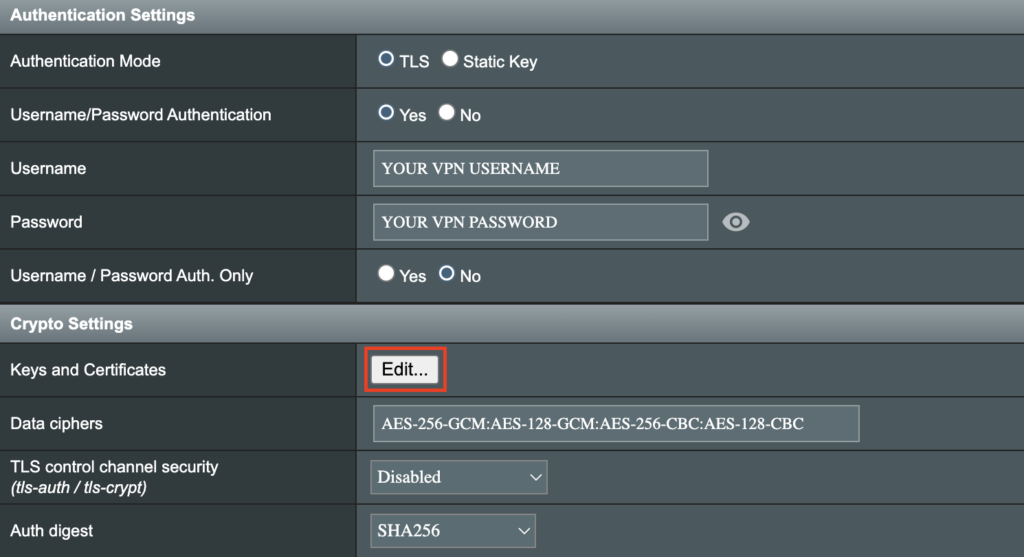
8. Click the Edit button in the Keys and Certificates area.

Merlin Keys and Certificates Edit button

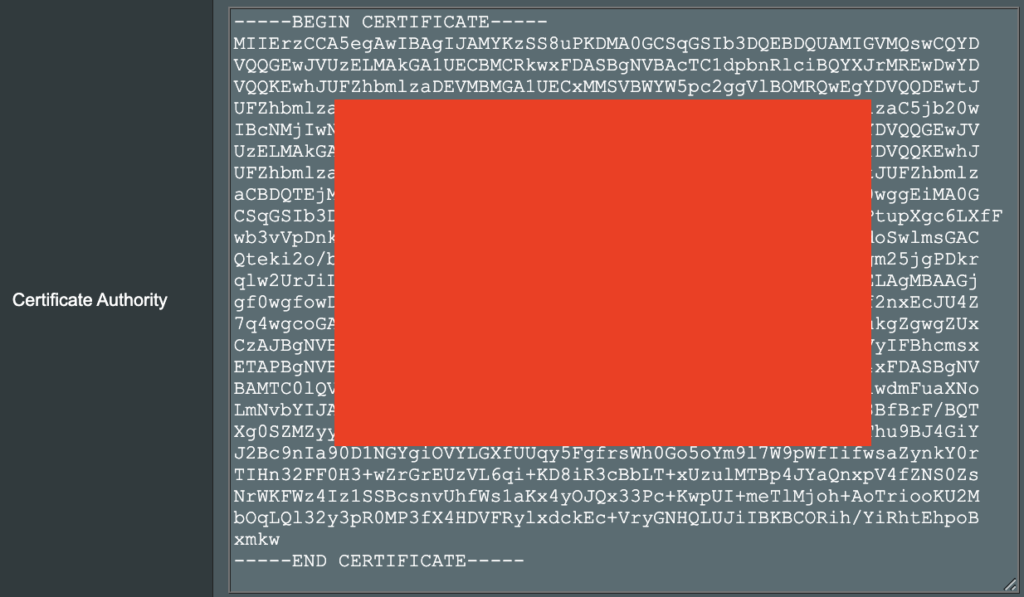
9. In the Certificate Authority field paste in the entire content of the ca.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Merlin Certificate Authority

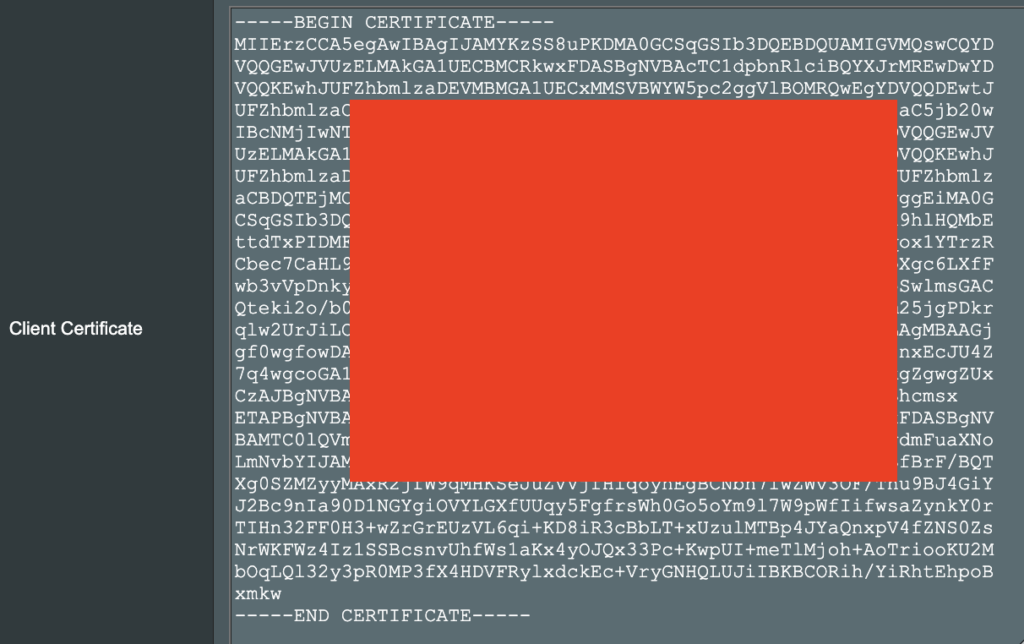
10. In the Client Certificate field paste in the entire content of the client.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Merlin Client Certificate

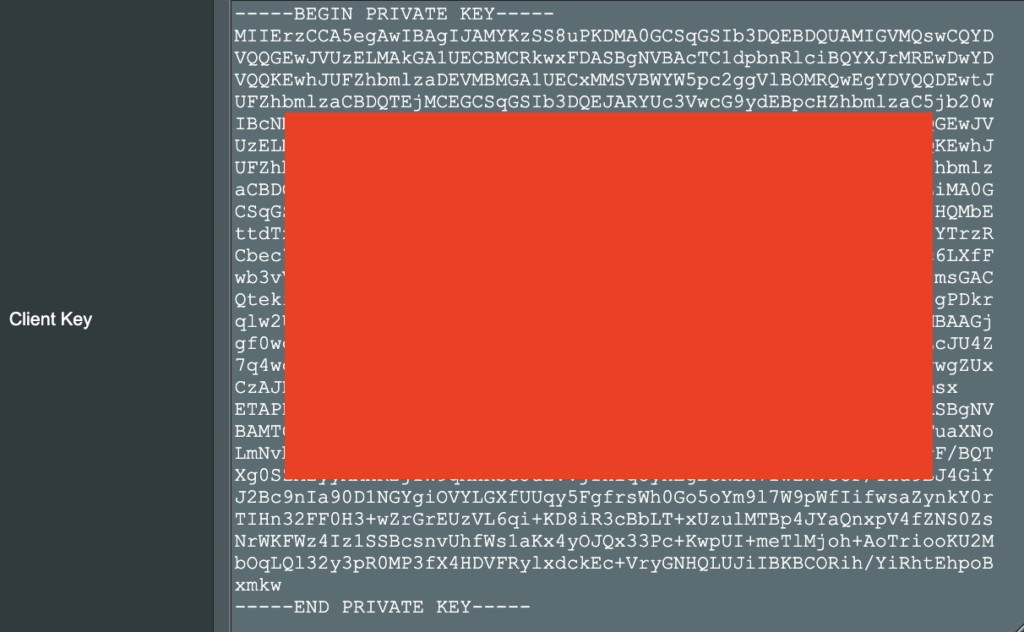
11. In the Client Key field paste in the entire content of the client.key file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).

Merlin Client Key

12. Click Save at the bottom of that window.

13. Click Apply at the bottom of the page.

14. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Merlin Service State All Providers

Verify a successful CyberGhost connection

  1. You should now see a CONNECTED message.
  2. Visit What is my IP Address from a private/incognito browser to verify your new IP address and virtual location.

TROUBLESHOOTING

Still having issues? Visit the FR Privacy App Troubleshooting section.

Troubleshoot Here

NordVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 8, 2019 ·

Preparing for Manual NordVPN Setup

Verify your NordVPN login information

If you are not already an NordVPN user Sign Up Now.

Log in to your account on the NordVPN website.

NordVPN Server Addresses

For a NordVPN server recommendation visit their Recommend Server page.

Once you have selected the server you want to connect to, download the UDP .ovpn file containing the Server IP Address, TLS Auth Key, and CA Cert referenced below.

Open the .ovpn file that is downloaded to your computer with NotePad++ for Windows or TextEdit for Apple. You will only need the Server IP Address, TLS Auth Key, and CA Cert from this file. All NordVPN servers and .ovpn files have different IP Addresses, keys, and certificates.

DD-WRT Router Setup for NordVPN

Navigate to Services > VPN

Enter NordVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote 206.226.72.27 1194
206.226.72.27 is your NordVPN server IP address. Enter the IP Address in this field.

Port

1194

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your NordVPN account with.

Password

Enter the Password you successfully logged in to your NordVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

In the .ovpn file copy and paste all contents in between the <tls-auth> and </tls-auth> lines from your .ovpn file starting and ending with:
—–BEGIN OpenVPN Static key V1—–
…
—–END OpenVPN Static key V1—–

Additional Config

tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

In the .ovpn file Copy and Paste all contents in between the <ca> and </ca> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful NordVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit NordVPN’s website to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the NordVPN server

  1. Download and open a new .ovpn file from NordVPN.
  2. Copy and paste the server IP Address into the Server IP/Name field.
  3. Copy and paste the TLS Auth Key into the TLS Auth Key field.
  4. Copy and paste the CA Cert into the CA Cert field.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Router FAQs

admin · Jan 29, 2019 ·

Router FAQs

What is an IP Address?

An IP (Internet Protocol) Address is a numerical assignment for each device (cell phone, iPad, laptop computer, printer etc) inside a network that uses the Internet Protocol for communication. Internet Protocol is responsible for routing information packets across network boundaries. It is the main protocol establishing the Internet.

An IP address serves two predominant functions. First is to host or network interface identification. Second, it provides location addressing. To put it bluntly, an IP address tells wherever you are connecting, to whom you are visiting, and where you are located.

What is DNS?

DNS (Domain Name System) is a protocol within the TCP/IP protocol that uses a set of standards for how computers exchange data on the Internet and on many private networks.

The basic job of DNS is to convert a user-friendly domain name into an IP address that computers use to identify one another. Think of DNS like your cellphone contact list; you tap the name and the phone contacts to a phone number.

It is easier to remember flashrouters.com, rather than its IP address. Imagine if you had to remember all of the IP addresses of your favorite websites!

What is DNSMasq?

DNSMasq is a local DNS server that speeds up host-name searches from your computer/Internet connection after pressing enter.

Basically, DNSMasq gives the router some advanced enterprise functionality – caching DNS records locally so you have a faster browsing experience. Your computer only has to go to the router instead of repeatedly scouring the web for a commonly visited site.

What is Throughput and How Do I Improve it?

Throughput is the average rate of successful delivery of messages through a network. Simply put, throughput measures the speed of message delivery inside a network. If you think about it in relationship to networks and Internet connections, throughput defines the user experience. The key to a pleasing user experience is uninterrupted service and smooth data transfer.

In order to improve throughput,  you should get a router with more memory. If you notice that your network is running slowly due to congestion, you could probably benefit by upgrading your router to one with more memory. FlashMemory and RAM on a router add more room to prevent network congestion and improve throughput.

Most of FlashRouters‘ high-end units come with at least 8 MB of Flash memory and 64 MB of RAM which should be more than capable for providing for the average home users’ or small business will need in the future.

What is PPPoE?

PPPoE stands for Point-to-Point Protocol over Ethernet, a network protocol for encapsulating Point-to-Point Protocol (PPP) frames inside Ethernet frames. It is used mainly with DSL services where individual users connect to a DSL modem over Ethernet.

With PPPoE, users virtually “dial” from one machine to another over an Ethernet network, establish a point-to-point connection and then data packets are securely transported through the connection.

PPPoE offers an Internet service provider (ISP) an easier way to track exactly how much bandwidth you are using in case they want to charge for it in the future.

What is the Difference Between VPN Encryption and Wireless Network Security?

VPN Encryption: If you are connected to the VPN on your home network, then any data that flows over the Internet is entirely encrypted whether you are connected to the Internet either wired or wirelessly. This means that if your Local ISP was trying to see what you are browsing or downloading, they would not be able to see your data.

Wireless Network Security: If you leave your wireless network open or insecure, it does not matter whether Internet traffic is encrypted, because someone can directly see what you are doing on your network, or even worse, can go in and put a wireless password on your network, locking you out. They may also be able to access folders and files on your computer without your control.

Best thing to do is protect your wireless network with a WPA secured password along with your VPN connection.

Are FlashRouters Affected By the Shellshock Bug?

No.

According to our in-house testing and multiple DD-WRT community reports, we have found that the Shellshock vulnerability will not work on with DD-WRT or TomatoUSB installed router. The vulnerability is based on a shell called BASH (Bourne Again Shell) but DD-WRT & Tomato firmware use BusyBox which is confirmed to not have this issue.

Please be advised that if you are using Optware on your DD-WRT router there is a chance that implementation is BASH based. Only used trusted optware on your router.

CyberGhost Manual OpenVPN Setup

TeamFlashRouters · Apr 9, 2019 ·

Preparing for Manual CyberGhost Setup

Obtain your CyberGhost OpenVPN Information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

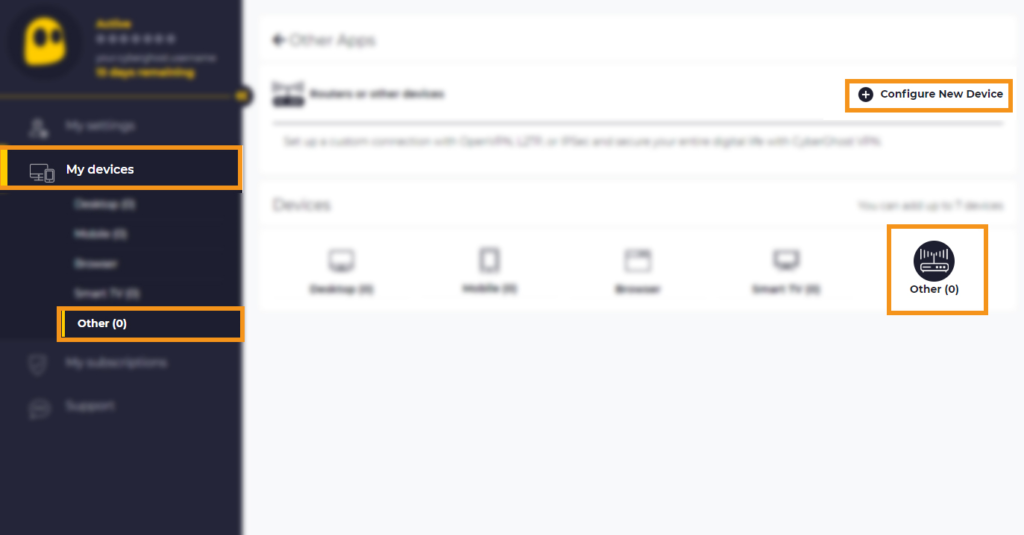
2. Select My Devices.

3. Select Other and then Configure New Device.

CyberGhost Website OpenVPN Configuration Files Generator Cyberghost - Website Screen CyberGhost Website OpenVPN Configuration Files Generator

4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 3

5. Press View configuration.

CyberGhost Website OpenVPN Configuration Files Generator 2

6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the ca.crt, client.crt, and client.key files. All CyberGhost servers have different keys and certificates.

DD-WRT Router Setup for CyberGhost

Navigate to Services > VPN

Enter CyberGhost settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you selected in your account. Be sure there are no extra spaces or characters.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your CyberGhost account.

Password

Enter the Password you obtained in your CyberGhost account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

tun-mtu 1500
fragment 1300
mssfix 1300

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
—–END CERTIFICATE—–

Public Client Cert

Copy and paste all contents of the client.crt file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and paste all contents of the client.key file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful CyberGhost connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit CyberGhost’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to CyberGhost.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the CyberGhost server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new ca.crt, client.crt, and client.key
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero Dashboard Not Updating or Showing Old Information

Dave · Oct 8, 2026 ·

If the Privacy Hero dashboard is showing old information, a VPN status does not appear to update, settings you changed are not displaying correctly, or the dashboard behaves unexpectedly, your browser may be displaying cached Privacy Hero website data.

Before changing your router or VPN configuration again, open a fresh browser session and confirm that the dashboard is displaying the current information.

Start With a Private or Incognito Browser Window

The fastest test is to open the Privacy Hero dashboard in a new private or incognito browser window.

  1. Close any existing Privacy Hero dashboard tabs.
  2. Open a new private or incognito browser window.
  3. Visit app.privacyhero.com.
  4. Sign in to your Privacy Hero account.
  5. Check the router, VPN, device, or setting again.

If the correct information appears in the private browser window, the original browser session was likely displaying cached or stale website information.

Refresh the Privacy Hero Dashboard

If the dashboard has been open while you are changing VPN or router settings, refresh the page before assuming that a change failed.

  1. Refresh the Privacy Hero dashboard.
  2. Allow the page to finish loading.
  3. Return to the section you were changing.
  4. Check the current status again.

If the information still appears incorrect, sign out of Privacy Hero, close the browser tab, and sign back in through a fresh browser session.

Clear Cached Privacy Hero Site Data

If Privacy Hero works correctly in a private/incognito window but not in your normal browser window, clear the cached website data for Privacy Hero.

Browser menus vary, but look for settings related to:

  • Cached files and images.
  • Cookies and site data.
  • Website data.
  • Privacy and browsing data.

If your browser allows you to remove data for an individual website, clear the stored data for app.privacyhero.com rather than clearing your entire browser history.

Then reopen app.privacyhero.com, sign in again, and check the dashboard.

Try Another Browser or Device

If the dashboard still behaves unexpectedly, test it from another browser or device.

  1. Open app.privacyhero.com in another browser.
  2. Sign in using the same Privacy Hero account.
  3. Check whether the same router and settings appear correctly.

You can also test from another computer, phone, or tablet.

Privacy Hero is cloud-managed, so you do not need to be connected to the Privacy Hero WiFi to access the dashboard. You can use cellular data, another WiFi network, or another internet connection.

Disable Browser Extensions While Testing

Browser extensions can sometimes interfere with website login, scripts, or dashboard functions.

If the problem occurs only in one browser, temporarily test without extensions such as:

  • Ad blockers.
  • Privacy extensions.
  • Script blockers.
  • VPN or proxy extensions.
  • Security or filtering extensions.

A private/incognito window may disable some extensions automatically, depending on your browser configuration.

VPN Status Still Shows Failed or Connecting?

If a fresh browser session confirms that Privacy Hero is actually reporting the VPN as Failed, Connecting, Disconnected, or showing a timeout error, the problem is no longer just a browser display issue.

NordVPN users should continue with Privacy Hero NordVPN Not Connecting or Showing Timeout Errors.

No Internet After the VPN Failed?

If the dashboard confirms that the VPN has failed and your Privacy Hero network also has no internet access, check whether the VPN Kill Switch is enabled.

See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

One Device Shows the Wrong VPN IP?

If Privacy Hero shows the VPN as connected and working but only one device shows an unexpected IP address or location, the browser cache is probably not the main issue.

Check the device for its own VPN application, Private Relay, Private DNS, browser Secure DNS, antivirus, firewall, or other network settings.

See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero NordVPN Not Connecting or Showing Timeout Errors
  • Privacy Hero VPN Kill Switch Setup
  • Device Settings That Can Interfere With Your Router VPN

Surfshark Setup for Privacy Hero

TeamFlashRouters · Sep 23, 2025 ·

Privacy Hero supports Surfshark through WireGuard and OpenVPN using the Custom VPN provider option.

WireGuard is recommended for most users. It requires a Surfshark WireGuard key pair and a downloaded server configuration file. OpenVPN uses a downloaded .ovpn file and Surfshark’s separate Manual Setup credentials, not your usual Surfshark login email and password.

Privacy Hero is cloud-managed. You can change these settings from any computer, smartphone, or tablet with an internet connection; you do not need to be on the Privacy Hero WiFi to configure the VPN.

Choose Your Surfshark Setup

Select the connection method or instructions you need.

WireGuard Setup →Recommended · Key pair and server fileOpenVPN Setup →Manual credentials and UDP .ovpn fileUpload WireGuard →Import your configuration into Privacy HeroUpload OpenVPN →Add the file and service credentialsVerify Connection →Check your VPN IP and locationTroubleshooting →Fix connection failures and no internet

Surfshark WireGuard Setup (Recommended)

WireGuard uses a key pair for authentication. A separate Surfshark username and password is not needed for the WireGuard configuration.

Create or Select Your Surfshark WireGuard Key Pair

  1. Sign in to your Surfshark account.
  2. Open VPN → Manual Setup, choose the Router setup option, and select WireGuard.
  3. If you already registered a key pair with Surfshark, select I have a key pair and follow the prompts to register your public key. Otherwise, select I don’t have a key pair.
  4. If generating a new key pair, enter a name and choose Generate a new key pair. Save the generated keys securely when prompted.

Important: Your WireGuard private key is sensitive. Do not publish or send it in a support ticket. Surfshark notes that you may not be able to view the generated keys again after leaving that screen.

Download a Surfshark WireGuard Server File

  1. After setting up the key pair, select Choose a location or open the Locations section.
  2. Choose an available Surfshark server and download its WireGuard configuration file to your device.

Do not download the WireGuard configuration before setting up the key pair. Surfshark warns that a file downloaded too early can be missing the required key information. For more detail, see Surfshark’s manual WireGuard router instructions.

Upload WireGuard to Privacy Hero

  1. Open app.privacyhero.com and log in to your Privacy Hero account.
  2. Open the VPN section, click Change, and choose Custom as the VPN provider.
  3. Select WireGuard and upload the Surfshark WireGuard configuration file you downloaded.
  4. Click Save and allow Privacy Hero to establish the connection. Confirm the VPN status shows Connected.
Privacy Hero Custom WireGuard configuration and file upload panel

Surfshark OpenVPN Setup

OpenVPN is an alternative to WireGuard. It requires a Surfshark Manual Setup username and password and a downloaded OpenVPN configuration (.ovpn) file.

Get Your Surfshark OpenVPN Credentials

  1. Sign in to your Surfshark account.
  2. Open VPN → Manual Setup, choose Router, and select OpenVPN.
  3. Open the Credentials tab. If credentials are not yet available, select Generate credentials.
  4. Copy the Manual Setup username and password, or keep the tab open to enter them into Privacy Hero later.

Important: These are not your regular Surfshark website email and password. Keep the service credentials private.

Download a Surfshark OpenVPN Server File

  1. In Surfshark’s OpenVPN Manual Setup area, open the Locations tab.
  2. Select a country or server and download its UDP .ovpn configuration file. UDP is the recommended starting option; a TCP configuration may be worth trying later if needed.

Download a new .ovpn file whenever you want to switch to a different Surfshark server location. See Surfshark’s manual server selection instructions.

Upload OpenVPN to Privacy Hero

  1. Open app.privacyhero.com, sign in, and select the VPN section.
  2. Click Change, select Custom, and choose OpenVPN.
  3. Upload the Surfshark UDP .ovpn file you downloaded.
  4. Enter the Surfshark Manual Setup username and password into the Custom OpenVPN fields.
  5. Click Save, then confirm the VPN status shows Connected.
Privacy Hero Custom OpenVPN screen with configuration file upload and username and password fields

Verify Your Surfshark Connection

Privacy Hero showing Connected confirms the router connection status. Test a device on the Privacy Hero network to confirm it is using Surfshark.

  1. Connect your device to the Privacy Hero WiFi or LAN.
  2. Disconnect the Surfshark app or any other VPN app running directly on the testing device.
  3. Open a fresh private/incognito browser window.
  4. Visit Surfshark’s IP address checker.
  5. Confirm the displayed public IP and approximate location correspond to your selected Surfshark server.

You can change Privacy Hero settings while using another WiFi network or cellular data, but the device performing this VPN IP test must be connected to Privacy Hero. Avoid running a separate VPN app on the same testing device, as that creates a double-VPN connection.

Streaming Relocation and Your VPN Location

When Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation region instead of the Surfshark VPN server region. See Privacy Hero Streaming Relocation.


Surfshark Not Connecting?

If Privacy Hero displays Failed, remains on Connecting, or reports a timeout, try these steps:

  1. Confirm your Surfshark subscription is active and that Custom is selected as the VPN provider in Privacy Hero.
  2. If using WireGuard, confirm that the key pair was created or registered before downloading the server file. If necessary, generate a new key pair, download a fresh configuration, and upload it again.
  3. If using OpenVPN, double-check your separate Surfshark Manual Setup username and password, not your regular website login.
  4. Download a fresh server configuration for another available Surfshark location and try again.
  5. If OpenVPN UDP continues to fail, try a Surfshark TCP .ovpn configuration file to check for a protocol-specific issue.
  6. Temporarily disable the VPN Kill Switch while checking whether internet access works without the VPN, then restore your preferred Kill Switch setting.

No Internet After Surfshark Disconnects?

The VPN Kill Switch may intentionally block normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

If other Privacy Hero devices display the expected Surfshark VPN IP, review the affected device for VPN apps, iCloud Private Relay, Private DNS, proxy settings, antivirus filtering, or other security software. See Device Settings That Can Interfere With Your Router VPN.
Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

ExpressVPN Setup for Privacy Hero

TeamFlashRouters · Aug 14, 2025 ·

Privacy Hero supports ExpressVPN using OpenVPN. To connect, you need your ExpressVPN Manual Configuration username and password and an OpenVPN (.ovpn) configuration file for your preferred server location.

Important: In Privacy Hero, choose Custom as the VPN provider. Upload the ExpressVPN .ovpn file and enter your separate Manual Configuration credentials, not your regular ExpressVPN website login.

Privacy Hero is cloud-managed, so you can complete setup from any computer, smartphone, or tablet with an internet connection. You do not need to be connected to Privacy Hero WiFi while changing the settings.

Choose Your ExpressVPN Setup Step

Jump directly to the instructions you need.

Manual Credentials →Find your ExpressVPN OpenVPN username and passwordDownload .ovpn File →Choose a server location and download its UDP fileCustom VPN Setup →Upload the file and enter credentials in Privacy HeroUDP Configuration →Check the OpenVPN protocol and save your connectionVerify Connection →Confirm your VPN IP address and server locationTroubleshooting →Connection errors, timeouts, and no internet

Get Your ExpressVPN Manual Configuration Credentials

ExpressVPN provides separate credentials for manual OpenVPN connections. These are different from your normal ExpressVPN website email and password.

  1. Open ExpressVPN Set Up Devices and sign in to your ExpressVPN account.
  2. In the left navigation, select Set Up Devices.
  3. Under Applications, expand Advanced setup and choose Manual Configuration.
  4. Find your unique Username and Password under Manual Configuration. Keep this tab open so you can copy them into Privacy Hero.

Important: Do not use your regular ExpressVPN account password, and do not share your manual configuration credentials publicly.


Download Your ExpressVPN OpenVPN Server File

Each available ExpressVPN location has its own OpenVPN configuration file. The file determines the server location used by Privacy Hero.

  1. On the same Manual Configuration page, locate the server regions, such as Americas, Europe, Asia Pacific, or Middle East & Africa.
  2. Expand your preferred region and download the UDP .ovpn file for an available location. Save it to the device you are using to configure Privacy Hero.

Only locations offered on your ExpressVPN Manual Configuration page can be used for this setup. To change locations later, download the corresponding .ovpn file and upload it to Privacy Hero.


Add ExpressVPN to Privacy Hero as a Custom VPN

ExpressVPN uses Privacy Hero’s Custom VPN configuration rather than a dedicated ExpressVPN provider option.

Upload the OpenVPN File and Enter Credentials

  1. Open app.privacyhero.com and sign in to your Privacy Hero account.
  2. Open the VPN section.
  3. Click Change beside the VPN provider and choose Custom.
  4. Choose OpenVPN if prompted, then upload the UDP .ovpn file downloaded from ExpressVPN.
  5. Copy the separate ExpressVPN Manual Configuration Username and Password into the corresponding Privacy Hero fields.
Privacy Hero Custom OpenVPN configuration showing file upload and manual username and password fields

Check the UDP Configuration and Connect

  1. If Privacy Hero displays the OpenVPN configuration in an editor, confirm that the downloaded UDP configuration specifies proto udp. If the directive is missing, add proto udp at the beginning of the configuration. Do not add a conflicting second protocol directive.
  2. Click Save to apply the configuration and establish the VPN connection.
  3. Confirm Privacy Hero displays Connected for the Custom OpenVPN connection.
Privacy Hero Custom OpenVPN configuration editor with proto udp directive

Verify Your ExpressVPN Connection

After Privacy Hero reports Connected, check that devices on the Privacy Hero network are actually using the VPN.

  1. Connect the testing device to the Privacy Hero WiFi or LAN network.
  2. Disconnect the ExpressVPN app or any other VPN application running directly on that device.
  3. Open a fresh private/incognito browser window.
  4. Visit ExpressVPN What Is My IP.
  5. Confirm the public IP address and approximate location correspond to the ExpressVPN server selected in your .ovpn file.

Important: You can manage Privacy Hero’s VPN settings from another network or cellular data. However, to verify the router’s VPN IP, the testing device must be connected to the Privacy Hero network. Running another VPN app on the device can produce double-VPN results.

Streaming Relocation and VPN Location

If Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation region instead of the location defined in the ExpressVPN configuration file. See Privacy Hero Streaming Relocation.


ExpressVPN Not Connecting?

If Privacy Hero shows Failed, stays on Connecting, or displays a timeout error, try these checks:

  1. Confirm your ExpressVPN subscription is active and you entered the separate Manual Configuration username and password.
  2. Check that you selected Custom in Privacy Hero, rather than another VPN provider.
  3. Download a fresh UDP .ovpn file for an available ExpressVPN server location and upload it again.
  4. Check that the OpenVPN configuration uses proto udp without conflicting protocol directives.
  5. Temporarily disable the VPN Kill Switch while testing whether normal internet access works without the VPN, then restore your preferred Kill Switch setting.
  6. Try another ExpressVPN server location or reconnect the VPN.

No Internet After the VPN Disconnects?

The Privacy Hero VPN Kill Switch may intentionally block normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected, but One Device Shows the Wrong IP?

If other devices show the correct VPN IP, check the affected device’s VPN apps, iCloud Private Relay, Private DNS, antivirus filtering, browser proxy/DNS settings, or other security software. See Device Settings That Can Interfere With Your Router VPN.
Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer