• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: settings to mak

Netgear R6700V3 Nighthawk DD-WRT WiFi Settings

Dave · Jun 5, 2020 ·

Recommended DD-WRT WiFi settings for the Netgear R6700V3 are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

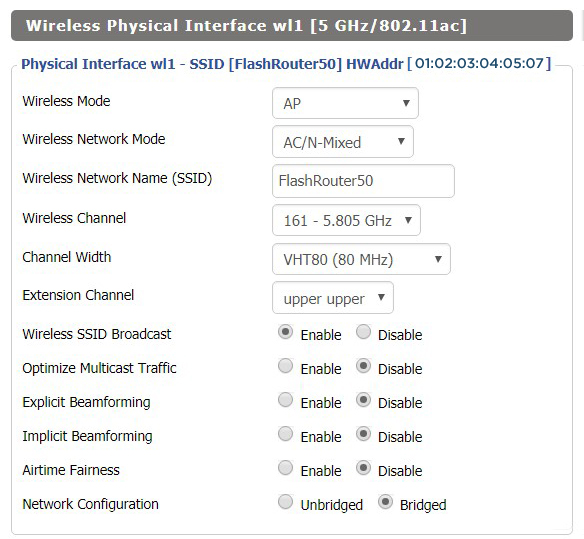
Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Netgear R6700V3 with DD-WRT firmware.

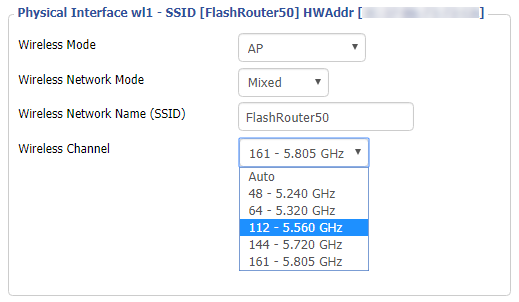
Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

2.4 GHz - Wireless-N

View R6700V3 DD-WRT FlashRouter 2.4GHz Settings

5.0 GHz - Wireless-AC

View R6700V3 DD-WRT FlashRouter 5GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

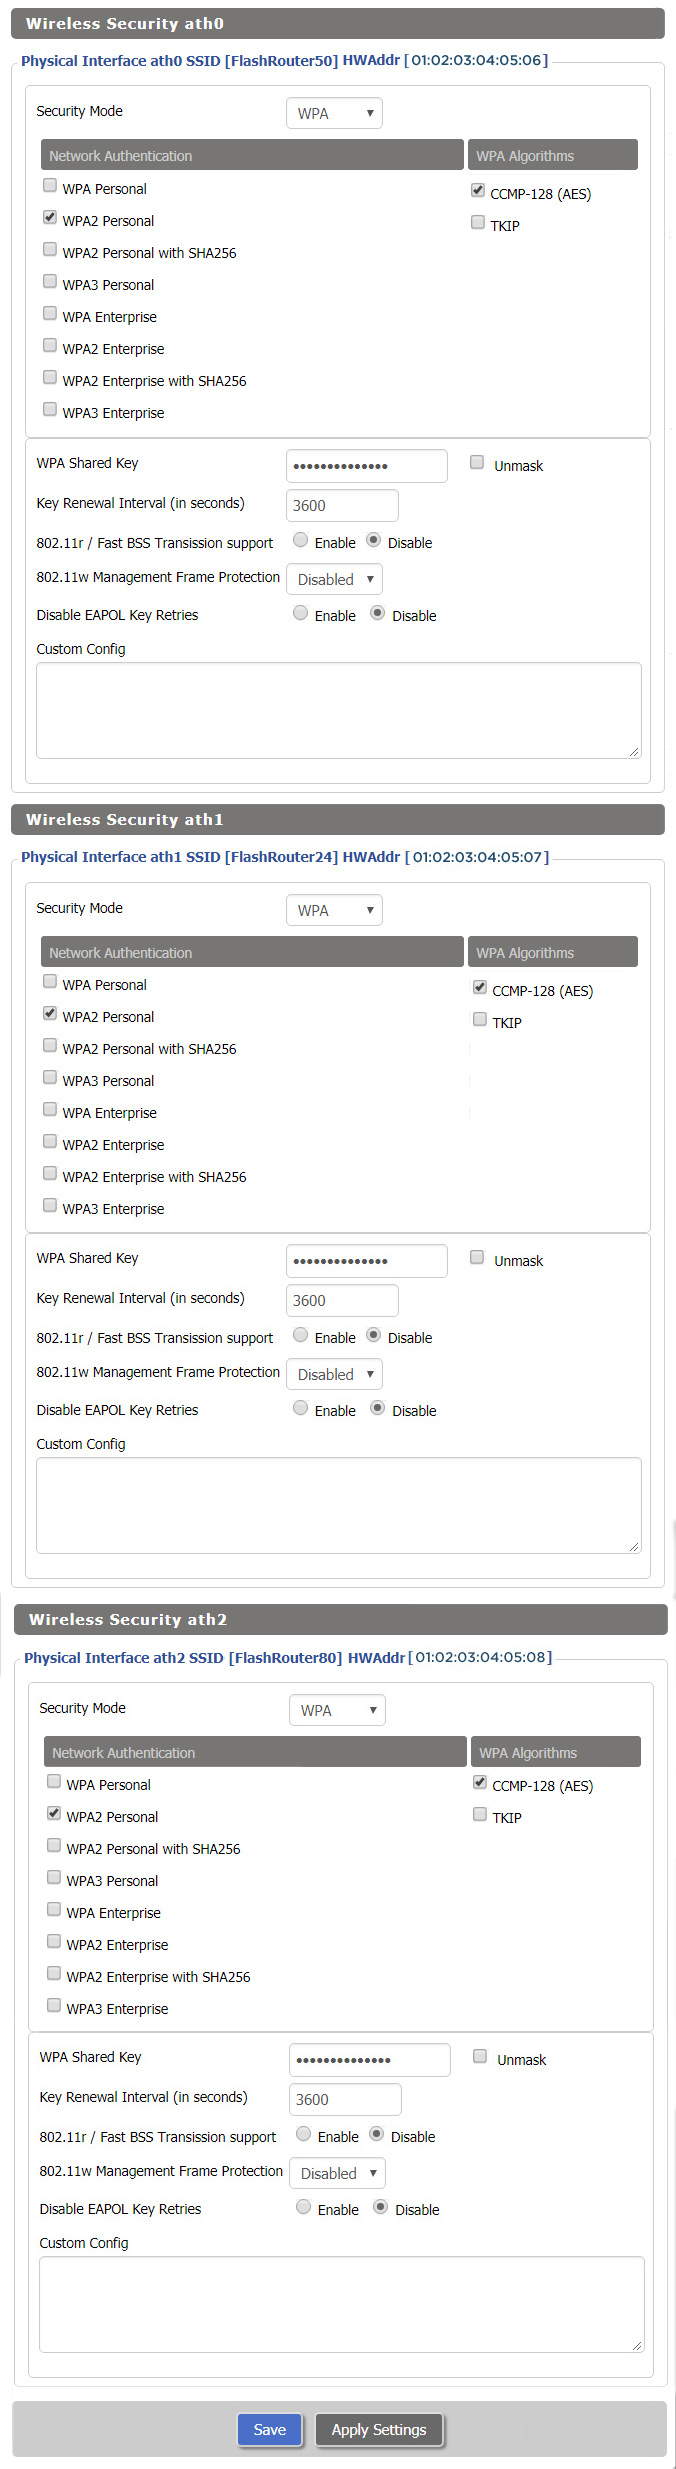
R6700V3 DD-WRT Wireless Security

The preset R6700V3 FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.

View R6700V3 DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Netgear R6700V3 WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Linksys WRT32X DD-WRT WiFi Settings

admin · Feb 19, 2019 ·

Recommended DD-WRT WiFi settings for the Linksys WRT32X are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

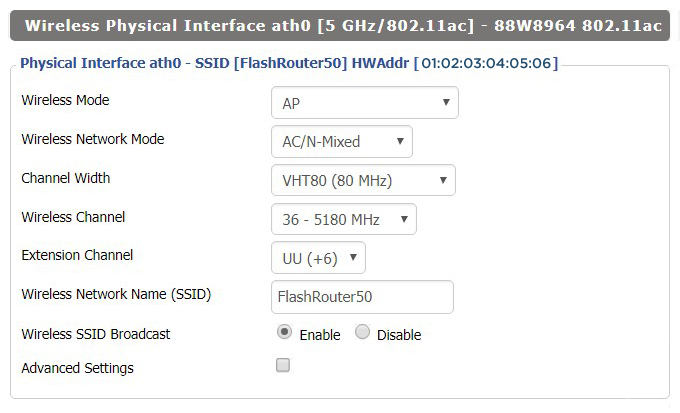
Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Linksys WRT32X with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

5.0 GHz - Wireless-AC

View WRT32X DD-WRT FlashRouter 5GHz #1 Settings

2.4 GHz - Wireless-N

View WRT32X DD-WRT FlashRouter 2.4GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

WRT32X DD-WRT Wireless Security

The preset WRT32X FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.
View WRT32X DD-WRT FlashRouter WiFi Security Settings

TROUBLESHOOTING

Trouble with your Linksys WRT32X WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

Privacy Hero NordVPN Not Connecting or Showing Timeout Errors

Dave · Sep 22, 2026 ·

If NordVPN will not connect on Privacy Hero, shows a timeout error, remains stuck on Connecting, or displays Failed, the Privacy Hero router itself may still be working normally.

NordVPN connections can occasionally stop working when servers are placed into maintenance, removed or cycled out of service, account credentials change, or a previously saved NordVPN access token or manual service credential is no longer valid.

Start by confirming that Privacy Hero has normal internet access, then troubleshoot the NordVPN connection.


Jump to a Section

  • Confirm Privacy Hero Has Internet
  • Reconnect NordVPN
  • Try Another NordVPN Server
  • Update Your NordLynx Token
  • Update OpenVPN Credentials
  • Recent NordVPN Account Changes
  • Verify the VPN Connection

First: Confirm Privacy Hero Has Internet

Before changing your NordVPN settings, confirm that Privacy Hero itself has normal internet access.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. If the VPN Kill Switch is enabled, temporarily turn it Off.
  4. Turn the failed NordVPN connection off.
  5. Connect a device to the Privacy Hero network.
  6. Test normal internet access.

If internet access works normally with NordVPN and the Kill Switch disabled, the underlying Privacy Hero internet connection is working. Continue troubleshooting the NordVPN connection.

If your internet stopped working because NordVPN failed while the VPN Kill Switch was enabled, follow our Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting guide.

Reconnect NordVPN

A temporary NordVPN server or connection issue may resolve without changing your account information.

  1. Open the VPN section at app.privacyhero.com.
  2. Turn the NordVPN connection off.
  3. Wait a few seconds.
  4. Turn NordVPN back on.
  5. Allow the connection time to establish.
  6. Check whether the VPN status changes to Connected.

If NordVPN still shows Failed, Connecting, or a timeout error, continue with the steps below.

Try Another NordVPN Server

NordVPN regularly maintains, replaces, and cycles servers in its network. A specific NordVPN server that worked previously may eventually be taken offline, removed, or temporarily unavailable.

If your Privacy Hero NordVPN connection is configured to use a specific server and suddenly stops working, try another server or return to the normal country selection.

  1. Open app.privacyhero.com.
  2. Open the VPN section.
  3. Select your NordVPN connection.
  4. If you previously entered a specific NordVPN server under Advanced Options, remove or replace that server.
  5. Select the country or location you want to use.
  6. Save the settings.
  7. Reconnect NordVPN.
  8. Check whether the status changes to Connected.

If you specifically need to use an individual NordVPN server, make sure that server is still active before continuing to use it.

Important: A previously working specific server should not be assumed to remain available indefinitely. NordVPN may change its server network over time.

Update Your NordVPN Token for NordLynx

Privacy Hero uses a NordVPN access token to authenticate NordLynx connections.

If the saved token is expired, revoked, replaced, or otherwise no longer valid, NordLynx may show Failed, Connecting, or a timeout error.

Generating a new token is a good troubleshooting step if your NordVPN account information has changed or the existing token is no longer working.

  1. Sign in to your NordVPN account.
  2. Open the NordVPN Access Tokens page.
  3. Generate a new access token.
  4. Select Doesn’t expire if NordVPN provides that option.
  5. Copy the new token.
  6. Open app.privacyhero.com.
  7. Open the NordVPN settings.
  8. Confirm that NordLynx is the selected protocol.
  9. Replace the existing token with the newly generated token.
  10. Save the settings.
  11. Reconnect NordVPN.

Important: NordVPN access tokens are sensitive account credentials. Do not post or share your token publicly.

For complete setup instructions, see Privacy Hero NordVPN / NordLynx Setup.

Update NordVPN Manual Service Credentials for OpenVPN

If you are using OpenVPN instead of NordLynx, Privacy Hero uses NordVPN’s Manual Service Credentials.

These are different from the email address and password you normally use to sign in to the NordVPN website or application.

If the saved credentials are no longer valid, update them:

  1. Sign in to your NordVPN account.
  2. Open NordVPN Manual Service Credentials.
  3. Copy the current service username and password.
  4. Open app.privacyhero.com.
  5. Open your NordVPN settings.
  6. Confirm that OpenVPN is the selected protocol.
  7. Replace the existing manual service credentials with the current credentials from NordVPN.
  8. Save the settings.
  9. Reconnect NordVPN.

Do not enter your regular NordVPN website email address and password in place of the manual service credentials.

Did You Recently Change Your NordVPN Account Information?

If NordVPN stopped connecting after an account change, update the authentication information stored in Privacy Hero.

This is especially important after changes such as:

  • Changing your NordVPN account password.
  • Changing or updating NordVPN account security settings.
  • Generating or replacing NordVPN access tokens.
  • Changes to NordVPN manual service credentials.
  • Renewing, changing, or restoring your NordVPN subscription.

The credentials used by Privacy Hero depend on the VPN protocol:

  • NordLynx: Uses a NordVPN access token.
  • OpenVPN: Uses NordVPN manual service credentials.

Your regular NordVPN website login should not be entered as the router’s OpenVPN credentials.

If you are unsure whether the existing authentication information is still valid, retrieve current credentials directly from your NordVPN account and update Privacy Hero.

Confirm Your NordVPN Subscription Is Active

Privacy Hero cannot establish a NordVPN connection if the NordVPN account being used no longer has active VPN service.

Sign in to your NordVPN account and confirm that your subscription is active before continuing with server, token, or credential troubleshooting.

Try Another VPN Protocol

If your NordVPN account, credentials, and server selection are correct but the connection still fails, try another NordVPN protocol available in Privacy Hero.

For example, if NordLynx is not connecting, testing OpenVPN can help determine whether the issue is specific to the protocol or authentication method.

Remember that changing protocols also changes the required NordVPN authentication:

  • NordLynx requires a NordVPN access token.
  • OpenVPN requires NordVPN manual service credentials.

Important: Do Not Run Two VPNs at Once

Do not leave the NordVPN application connected directly on your phone or computer while testing the Privacy Hero VPN.

Running a VPN application on the device while also routing that device through the Privacy Hero VPN creates a double-VPN connection and can cause routing, connectivity, or IP-location problems.

Disconnect the device-level NordVPN app before testing the router VPN.

Verify the NordVPN Connection

Once Privacy Hero displays NordVPN as Connected:

  1. Connect your device to the Privacy Hero WiFi.
  2. Make sure the NordVPN app on the device is disconnected.
  3. Open a fresh private/incognito browser window.
  4. Visit NordVPN What Is My IP.
  5. Confirm that the public IP address and location correspond to your selected NordVPN location.
  6. Test several websites or applications.

If you use the Privacy Hero VPN Kill Switch, enable it only after confirming that NordVPN is connected and working.

NordVPN Is Connected but One Device Shows the Wrong IP

If Privacy Hero shows NordVPN as Connected and other devices display the correct VPN IP, the NordVPN connection itself is likely working.

Check the affected device’s Privacy Hero VPN assignment and review any VPN, privacy, DNS, browser, antivirus, firewall, or security settings running directly on that device.

See Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero NordVPN / NordLynx Setup
  • Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN

Linksys WRT3200ACM DD-WRT WiFi Settings

Dave · Feb 25, 2019 ·

Recommended DD-WRT WiFi settings for the Linksys WRT3200ACM are based on extensive testing by FlashRouters. Please note that optimal settings may vary depending on external factors such as home size, interference, and the types of WiFi devices you are connecting in your network.

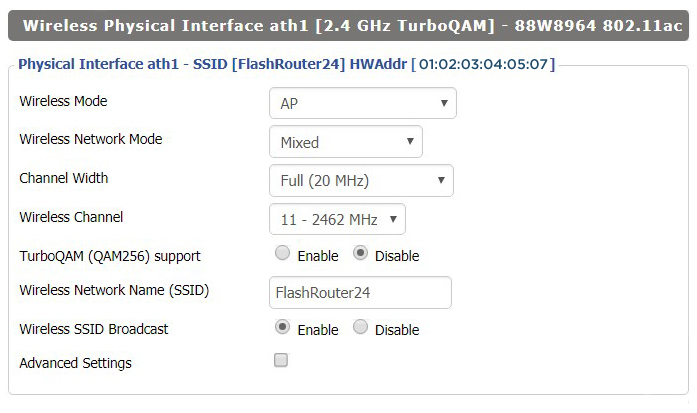
Screenshots below provide a visual display of recommended WiFi and encryption settings exactly as they appear in the Linksys WRT3200ACM with DD-WRT firmware.

Navigate to the Wireless > Basic Settings to view or edit WiFi network settings.

5.0 GHz - Wireless-AC

View WRT3200ACM DD-WRT FlashRouter 5GHz #1 Settings

2.4 GHz - Wireless-N

View WRT3200ACM DD-WRT FlashRouter 2.4GHz Settings

Additional DD-WRT WiFi Information

Intimidated by all the available WiFi settings? The DD-WRT website provides extensive information about all of the available configuration options in the firmware. Learn about everything from Wireless channels to channel widths and more in the Basic Wireless Settings – DD-WRT Wiki.

WRT3200ACM DD-WRT Wireless Security

The preset WRT3200ACM FlashRouter WiFi password is Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Navigate to the Wireless > Wireless Security to view or edit WiFi passwords.
TROUBLESHOOTING

Trouble with your Linksys WRT3200ACM WiFi? Visit the Wireless troubleshooting section.

Troubleshoot Here

How to Reset a Failed VPN Connection on Privacy Hero

Dave · Oct 24, 2026 ·

If your Privacy Hero VPN connection shows Failed, you can use the new Reset button to clear the saved third-party VPN settings and return the router to its available default connection. This is useful when a VPN setup is stuck or you want to start again without manually removing the existing third-party VPN configuration.

Important: A VPN reset removes all saved third-party VPN settings from Privacy Hero. You will need to configure that provider again if you want to use it later. The connection Privacy Hero uses after resetting depends on your subscription plan.

Reset a Failed VPN Connection

Follow the reset instructions, then check which connection your plan restores.

When to Use Reset →Know when a VPN reset is appropriate
Reset the Failed VPN →Clear third-party VPN settings in the dashboard
Premium vs. Core →Understand which connection returns afterward
What Gets Removed →Know what you will need to set up again
Verify Your Connection →Check the dashboard and public IP address
Still No Internet? →Check Kill Switch, WAN, and WiFi separately

When Should You Use the VPN Reset Button?

Use Reset when the current VPN connection is in a Failed state and you want to remove the third-party VPN setup and restore a working default connection. It is a more complete action than simply retrying the same VPN server.

  • Use it if the third-party VPN settings are no longer working and you want to start over.
  • Use it if you no longer want the saved third-party VPN configuration.
  • Do not use it if you need to preserve the existing VPN configuration. First try reconnecting or choosing a different VPN server or protocol.

The Reset action addresses the VPN configuration. It does not repair a disconnected WAN cable, an ISP outage, or a router that cannot reach the Privacy Hero cloud.


How to Reset a Failed VPN Connection

  1. Open app.privacyhero.com in a browser and sign in to your Privacy Hero account.
  2. Select your Privacy Hero router, then open its VPN settings.
  3. Confirm the existing VPN connection is showing Failed.
  4. Find the new Reset button in the failed VPN connection area. Before clicking, be aware that this action will remove all third-party VPN settings saved on the router.
  5. Click Reset. If a confirmation message appears, review it before confirming. Allow the dashboard to apply the reset and update the VPN connection status.
  6. Check the resulting connection using the subscription comparison below, then verify internet access from a device connected to Privacy Hero.

Dashboard access during a Kill Switch block: Privacy Hero permits access to app.privacyhero.com over its WiFi or LAN even when the VPN Kill Switch blocks ordinary internet traffic, as long as the router maintains its upstream/cloud connection. You can also manage the router from cellular data or another working internet connection.


What Happens After Reset? Privacy Premium vs. Privacy Core

VPN Reset: Side-by-Side Plan Comparison
Privacy Premium Active subscription Privacy Core
Third-party VPN settingsRemoved Third-party VPN settingsRemoved
Connection after resetBuilt-in Privacy Hero VPN Connection after resetNormal ISP internet
VPN protection afterwardYes, when the built-in VPN is connected VPN protection afterwardNo router VPN is active

Privacy Core users: After resetting, your normal internet access is not VPN-protected by Privacy Hero. If you want a third-party VPN again, you must configure it again in Privacy Hero.

Privacy Premium users: Check that the built-in Privacy Hero VPN shows Connected before assuming your traffic is going through the VPN. A working upstream internet connection and active Premium subscription are still required.


What Information Does the Reset Remove?

The VPN Reset button clears the third-party VPN configuration stored in Privacy Hero. This means any saved third-party provider details will need to be entered or imported again before that provider can be used.

Depending on the provider and protocol you had configured, this may include the saved VPN provider selection, server details, credentials or tokens, and custom OpenVPN or WireGuard settings. Have your provider login or configuration materials available if you plan to set up that VPN again.

This is a VPN configuration reset, not a request to cancel your third-party VPN subscription. It should not be confused with a full router factory reset.


How to Verify Internet and VPN Status After Reset

  1. Refresh the Privacy Hero dashboard and reopen VPN.
  2. If you have Privacy Premium, verify that the built-in Privacy Hero VPN is selected and shows Connected.
  3. If you have Privacy Core, verify that the third-party VPN configuration is gone and ordinary internet access is available through your ISP connection.
  4. Connect a computer or phone to the Privacy Hero WiFi or LAN. To test the router by itself, turn off any VPN application running directly on that device.
  5. Load a regular website, then check your public IP address using ipleak.net. Premium should show a VPN IP if its built-in VPN is connected; Core will normally show your ISP public IP.

If you have Streaming Relocation enabled, some streaming services may use their separately selected location; that is not necessarily the same location shown by a general public IP check.


Reset Complete but Still No Internet?

  1. Check the VPN Kill Switch. If it is still enabled while there is no working VPN connection, it may block ordinary internet traffic. Review the Kill Switch setting before assuming the router has lost WiFi.
  2. Check the connection status. A router listed as Offline may have a WAN, ISP, or cloud-communication problem. The VPN reset cannot fix an upstream internet outage.
  3. Check the network wiring. Confirm your main router or ISP gateway has internet access and the cable is connected to the Privacy Hero WAN/Internet port.
  4. Check a device on Privacy Hero WiFi or LAN. Make sure you are testing the Privacy Hero network rather than another WiFi or cellular connection.
  5. Check your subscription. An active Privacy Premium subscription is required for the built-in Privacy Hero VPN fallback described above. Privacy Core returns to ordinary ISP internet access.

For Kill Switch behavior and restoring internet, see Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting. To learn when to enable the feature, see Privacy Hero VPN Kill Switch Setup.

Related Privacy Hero Articles

  • VPN Kill Switch: No Internet or WiFi Troubleshooting
  • How to Enable the Privacy Hero VPN Kill Switch
  • Privacy Hero VPN Setup Guides

PrivateInternetAccess (PIA) Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual PIA Setup

Verify your PIA login information

If you are not already a PIA user Sign Up Now.

Log in to your account on the PIA website.

FlashRouters Privacy App - PIA Login

PIA Server Addresses

The below servers are the only servers compatible with PIA router connections. Dedicated IP Addresses are not able to connect via routers.

United States

us-california.privacy.network
us-newjersey.privacy.network
us-chicago.privacy.network
us-texas.privacy.network
us-florida.privacy.network
us-seattle.privacy.network
us3.privacy.network
us-siliconvalley.privacy.network
us-newyorkcity.privacy.network
us-washingtondc.privacy.network
us-atlanta.privacy.network
us-houston.privacy.network
us-denver.privacy.network

United Kingdom

uk-london.privacy.network
uk-manchester.privacy.network

Canada

ca-toronto.privacy.network
ca-montreal.privacy.network

Australia

au-sydney.privacy.network
aus-melbourne.privacy.network
aus-perth.privacy.network

Germany

de-berlin.privacy.network
de-frankfurt.privacy.network

Rest of the World

ae.privacy.network
austria.privacy.network
dz.privacy.network
ad.privacy.network
ar.privacy.network
yerevan.privacy.network
bahamas.privacy.network
bangladesh.privacy.network
brussels.privacy.network
sofia.privacy.network
cambodia.privacy.network
china.privacy.network
cyprus.privacy.network
czech.privacy.network
denmark.privacy.network
egypt.privacy.network
fi.privacy.network
france.privacy.network
georgia.privacy.network
greenland.privacy.network
hungary.privacy.network
is.privacy.network
in.privacy.network
iran.privacy.network
ireland.privacy.network
man.privacy.network
israel.privacy.network
italy.privacy.network
japan.privacy.network
kazakhstan.privacy.network
liechtenstein.privacy.network
lu.privacy.network
macau.privacy.network
malta.privacy.network
mexico.privacy.network
md.privacy.network
monaco.privacy.network
mongolia.privacy.network
montenegro.privacy.network
morocco.privacy.network
nl-amsterdam.privacy.network
nz.privacy.network
nigeria.privacy.network
no.privacy.network
panama.privacy.network
philippines.privacy.network
poland.privacy.network
qatar.privacy.network
ro.privacy.network
rs.privacy.network
saudiarabia.privacy.network
spain.privacy.network
srilanka.privacy.network
sweden.privacy.network
swiss.privacy.network
sg.privacy.network
tr.privacy.network
taiwan.privacy.network
ua.privacy.network
venezuela.privacy.network
vietnam.privacy.network
za.privacy.network

DD-WRT Router Setup for PIA

Navigate to Services > VPN

PIA offers two different Encryption levels.
Default Encryption (AES-128) typically provides faster speeds.
Strong Encryption (AES-256) provides stronger encryption.
Follow the table below of the one that fits your needs.
Enter PIA settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.
Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1198

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA1

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFqzCCBJOgAwIBAgIJAKZ7D5Yv87qDMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzM1
MThaFw0zNDA0MTIxNzM1MThaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAPXD
L1L9tX6DGf36liA7UBTy5I869z0UVo3lImfOs/GSiFKPtInlesP65577nd7UNzzX
lH/P/CnFPdBWlLp5ze3HRBCc/Avgr5CdMRkEsySL5GHBZsx6w2cayQ2EcRhVTwWp
cdldeNO+pPr9rIgPrtXqT4SWViTQRBeGM8CDxAyTopTsobjSiYZCF9Ta1gunl0G/
8Vfp+SXfYCC+ZzWvP+L1pFhPRqzQQ8k+wMZIovObK1s+nlwPaLyayzw9a8sUnvWB
/5rGPdIYnQWPgoNlLN9HpSmsAcw2z8DXI9pIxbr74cb3/HSfuYGOLkRqrOk6h4RC
OfuWoTrZup1uEOn+fw8CAwEAAaOCAVQwggFQMB0GA1UdDgQWBBQv63nQ/pJAt5tL
y8VJcbHe22ZOsjCCAR8GA1UdIwSCARYwggESgBQv63nQ/pJAt5tLy8VJcbHe22ZO
sqGB7qSB6zCB6DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAkNBMRMwEQYDVQQHEwpM
b3NBbmdlbGVzMSAwHgYDVQQKExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4G
A1UECxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBAMTF1ByaXZhdGUg
SW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQpExdQcml2YXRlIEludGVybmV0IEFjY2Vz
czEvMC0GCSqGSIb3DQEJARYgc2VjdXJlQHByaXZhdGVpbnRlcm5ldGFjY2Vzcy5j
b22CCQCmew+WL/O6gzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBDQUAA4IBAQAn
a5PgrtxfwTumD4+3/SYvwoD66cB8IcK//h1mCzAduU8KgUXocLx7QgJWo9lnZ8xU
ryXvWab2usg4fqk7FPi00bED4f4qVQFVfGfPZIH9QQ7/48bPM9RyfzImZWUCenK3
7pdw4Bvgoys2rHLHbGen7f28knT2j/cbMxd78tQc20TIObGjo8+ISTRclSTRBtyC
GohseKYpTS9himFERpUgNtefvYHbn70mIOzfOJFTVqfrptf9jXa9N8Mpy3ayfodz
1wiqdteqFXkTYoSDctgKMiZ6GdocK9nMroQipIQtpnwd4yBDWIyC6Bvlkrq5TQUt
YDQ8z9v+DMO6iwyIDRiU
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter PIA settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1197

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIHqzCCBZOgAwIBAgIJAJ0u+vODZJntMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzQw
MzNaFw0zNDA0MTIxNzQwMzNaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBALVk
hjumaqBbL8aSgj6xbX1QPTfTd1qHsAZd2B97m8Vw31c/2yQgZNf5qZY0+jOIHULN
De4R9TIvyBEbvnAg/OkPw8n/+ScgYOeH876VUXzjLDBnDb8DLr/+w9oVsuDeFJ9K
V2UFM1OYX0SnkHnrYAN2QLF98ESK4NCSU01h5zkcgmQ+qKSfA9Ny0/UpsKPBFqsQ
25NvjDWFhCpeqCHKUJ4Be27CDbSl7lAkBuHMPHJs8f8xPgAbHRXZOxVCpayZ2SND
fCwsnGWpWFoMGvdMbygngCn6jA/W1VSFOlRlfLuuGe7QFfDwA0jaLCxuWt/BgZyl
p7tAzYKR8lnWmtUCPm4+BtjyVDYtDCiGBD9Z4P13RFWvJHw5aapx/5W/CuvVyI7p
Kwvc2IT+KPxCUhH1XI8ca5RN3C9NoPJJf6qpg4g0rJH3aaWkoMRrYvQ+5PXXYUzj
tRHImghRGd/ydERYoAZXuGSbPkm9Y/p2X8unLcW+F0xpJD98+ZI+tzSsI99Zs5wi
jSUGYr9/j18KHFTMQ8n+1jauc5bCCegN27dPeKXNSZ5riXFL2XX6BkY68y58UaNz
meGMiUL9BOV1iV+PMb7B7PYs7oFLjAhh0EdyvfHkrh/ZV9BEhtFa7yXp8XR0J6vz
1YV9R6DYJmLjOEbhU8N0gc3tZm4Qz39lIIG6w3FDAgMBAAGjggFUMIIBUDAdBgNV
HQ4EFgQUrsRtyWJftjpdRM0+925Y6Cl08SUwggEfBgNVHSMEggEWMIIBEoAUrsRt
yWJftjpdRM0+925Y6Cl08SWhge6kgeswgegxCzAJBgNVBAYTAlVTMQswCQYDVQQI
EwJDQTETMBEGA1UEBxMKTG9zQW5nZWxlczEgMB4GA1UEChMXUHJpdmF0ZSBJbnRl
cm5ldCBBY2Nlc3MxIDAeBgNVBAsTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAw
HgYDVQQDExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UEKRMXUHJpdmF0
ZSBJbnRlcm5ldCBBY2Nlc3MxLzAtBgkqhkiG9w0BCQEWIHNlY3VyZUBwcml2YXRl
aW50ZXJuZXRhY2Nlc3MuY29tggkAnS7684Nkme0wDAYDVR0TBAUwAwEB/zANBgkq
hkiG9w0BAQ0FAAOCAgEAJsfhsPk3r8kLXLxY+v+vHzbr4ufNtqnL9/1Uuf8NrsCt
pXAoyZ0YqfbkWx3NHTZ7OE9ZRhdMP/RqHQE1p4N4Sa1nZKhTKasV6KhHDqSCt/dv
Em89xWm2MVA7nyzQxVlHa9AkcBaemcXEiyT19XdpiXOP4Vhs+J1R5m8zQOxZlV1G
tF9vsXmJqWZpOVPmZ8f35BCsYPvv4yMewnrtAC8PFEK/bOPeYcKN50bol22QYaZu
LfpkHfNiFTnfMh8sl/ablPyNY7DUNiP5DRcMdIwmfGQxR5WEQoHL3yPJ42LkB5zs
6jIm26DGNXfwura/mi105+ENH1CaROtRYwkiHb08U6qLXXJz80mWJkT90nr8Asj3
5xN2cUppg74nG3YVav/38P48T56hG1NHbYF5uOCske19F6wi9maUoto/3vEr0rnX
JUp2KODmKdvBI7co245lHBABWikk8VfejQSlCtDBXn644ZMtAdoxKNfR2WTFVEwJ
iyd1Fzx0yujuiXDROLhISLQDRjVVAvawrAtLZWYK31bY7KlezPlQnl/D9Asxe85l
8jO5+0LdJ6VyOs/Hd4w52alDW/MFySDZSfQHMTIc30hLBJ8OnCEIvluVQQ2UQvoW
+no177N9L2Y+M9TcTA62ZyMXShHQGeh20rb4kK8f+iFX8NxtdHVSkxMEFSfDDyQ=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PIA connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the PIA server

  1. Copy the new PIA server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

NordVPN Setup for AsusWRT Firmware Routers

TeamFlashRouters · Oct 15, 2025 ·

You can connect to NordVPN on your AsusWRT router using NordLynx, OpenVPN, or a Dedicated IP.

Quick Options

  • NordLynx: Choose your preferred country from NordVPN’s server list

  • OpenVPN: Choose your preferred city or country from NordVPN’s server list.

  • Dedicated IP (optional): Enter your unique configuration file if you’ve been assigned a static NordVPN IP.

:point_right: If you are not already a NordVPN user Sign Up Now.

NordVPN NordLynx Setup for AsusWRT

1. Get your NordVPN Access Token for NordLynx connections. Log in to your NordVPN account and select NordVPN from your list of Services.

NordVPN Services Section

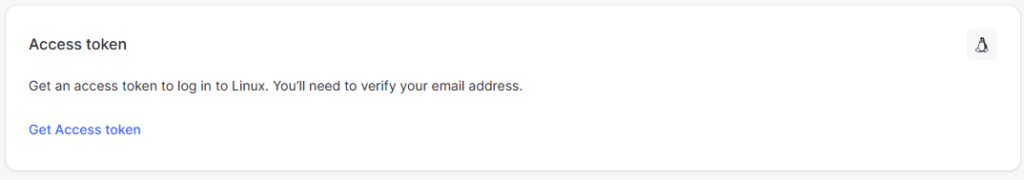
2. At the bottom of the page click Get Access token and you will receive a code via email. Enter this code to proceed.

NordVPN Access Token

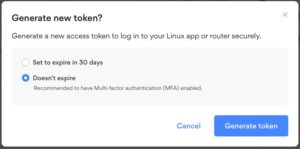
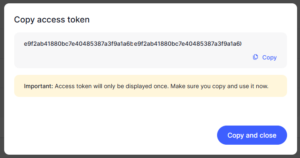
3. After you enter the email code select Generate new token and set it to Doesn’t expire. Copy this token.

NordVPN Generate new token
NordVPN Copy Token

4. Log in to the Asus settings page by connecting to the Asus router’s WiFi (or wired LAN) on your computer. Then, enter 192.168.50.1 or asusrouter.com in the browser.

View our guide for more instructions on how to access AsusWRT firmware settings.

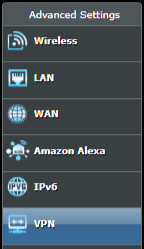
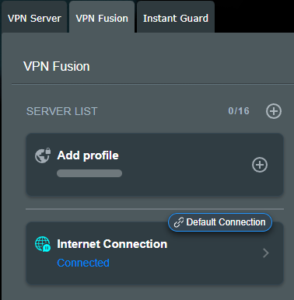
5. Navigate to the VPN tab and then select the VPN Fusion tab, then click Add profile.

Click the VPN Button
VPN Fusion Add Profile

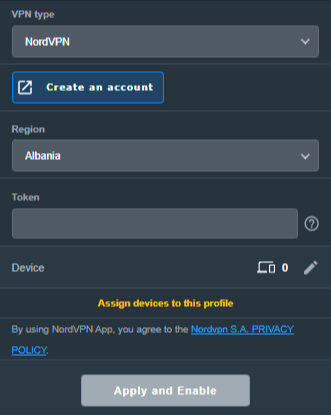
6. Fill in your NordVPN information, then click Apply and Enable.

  • Connection Name: Choose a name for your NordLynx connection.
  • VPN Type: Select NordVPN
  • Region: Choose your VPN server location
  • Token: Copy and paste your NordVPN token.
Apply NordLynx Settings

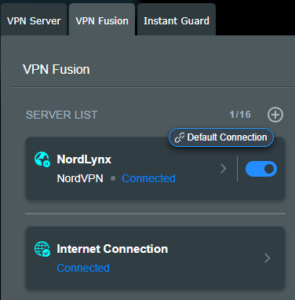
6. You should now see the Profile say Connected, indicating that the NordVPN server is successfully connected to your router!

VPN Fusion NordLynx Connected

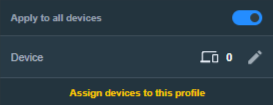
7. The VPN connection is automatically set to Apply to all devices.

If you only want certain devices to connect to the VPN, then turn off the VPN connection and switch off Apply to all devices.

Now click the pencil next to the Device section and select the devices (computer, phone, etc.) that you want to connect to VPN. Click OK and then click Apply all settings.

Apply VPN by Device

NordVPN OpenVPN Setup for AsusWRT

1. Get your NordVPN manual service credentials for OpenVPN connections. Log in to your NordVPN account and select NordVPN from your list of Services.

NordVPN Services Section

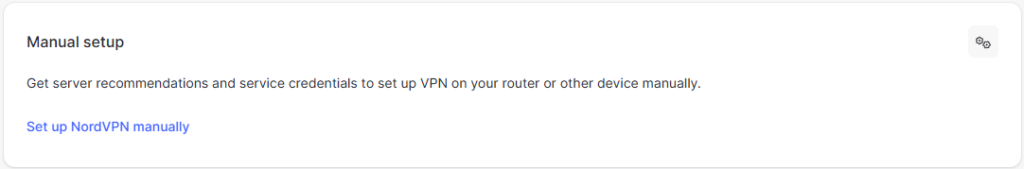
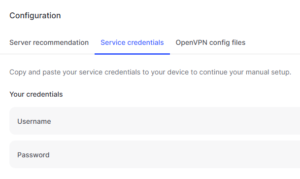
2. At the bottom of the page in the Manual Setup section click Setup NordVPN manually then under the Configuration section go to Service credentials. Click Verify email to receive a code via email and enter the code to view and copy your credentials.

NordVPN Manual OpenVPN
NordVPN Service Credentials

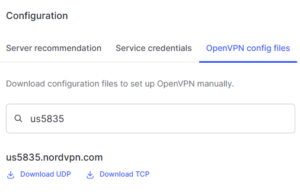
3. Click on OpenVPN config files. Search and download the server file for your preferred NordVPN location, UDP is recommended.

NordVPN OpenVPN Config Files

4. Log in to the Asus settings page by connecting to the Asus router’s WiFi (or wired LAN) on your computer. Then, enter 192.168.50.1 or asusrouter.com in the browser.

View our guide for more instructions on how to access AsusWRT firmware settings.

5. Navigate to the VPN tab and then click on the VPN Fusion tab, then click Add Profile.

Click the VPN Button
VPN Fusion Add Profile

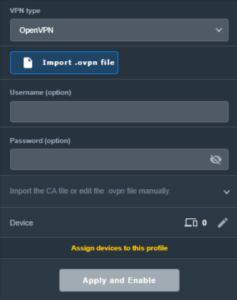
6. Fill in your NordVPN information then click Apply and Enable.

  • Connection Name: Choose a name for your NordVPN OpenVPN connection.
  • VPN Type: Select OpenVPN
  • Import .ovpn File: Upload the OpenVPN file that you downloaded.
  • Username and Password: Copy and paste your NordVPN manual service credentials.
AsusWRT OpenVPN Connection File Load

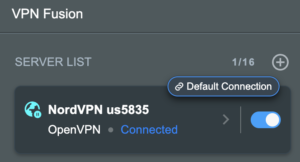
6. You should now see the Profile say Connected, indicating that the NordVPN server is successfully connected to your router!

Asus NordVPN Connected

7. The VPN connection is automatically set to Apply to all devices.

If you only want certain devices to connect to the VPN, then turn off the VPN connection and switch off Apply to all devices.

Now click the pencil next to the Device section and select the devices (computer, phone, etc.) that you want to connect to VPN. Click OK and then click Apply all settings.

Apply VPN by Device

NordVPN Dedicated IP Setup for AsusWRT

1. Get your NordVPN manual service credentials for OpenVPN connections. Log in to your NordVPN account and select NordVPN from your list of Services.

NordVPN Services Section

2. At the bottom of the page in the Manual Setup section click Setup NordVPN manually then under the Configuration section go to Service credentials. Click Verify email to receive a code via email and enter the code to view and copy your credentials.

NordVPN Manual OpenVPN
NordVPN Service Credentials

3. Now download your Dedicated IP configuration file from the NordVPN website.

4. Log in to the Asus settings page by connecting to the Asus router’s WiFi (or wired LAN) on your computer. Then, enter 192.168.50.1 or asusrouter.com in the browser.

View our guide for more instructions on how to access AsusWRT firmware settings.

5. Navigate to the VPN tab then click on the VPN Fusion tab, then click Add Profile.

Click the VPN Button
VPN Fusion Add Profile

6. Fill in your NordVPN information then click Apply and Enable.

  • Connection Name: Choose a name for your NordVPN Dedicated IP connection.
  • VPN Type: Select OpenVPN
  • Import .ovpn File: Upload the Dedicated IP OpenVPN file that you downloaded.
  • Username and Password: Copy and paste your NordVPN manual service credentials.
AsusWRT OpenVPN Connection File Load

6. You should now see the Profile say Connected, indicating that the NordVPN server is successfully connected to your router!

Asus NordVPN Connected

7. The VPN connection is automatically set to Apply to all devices.

If you only want certain devices to connect to the VPN, then turn off the VPN connection and switch off Apply to all devices.

Now click the pencil next to the Device section and select the devices (computer, phone, etc.) that you want to connect to VPN. Click OK and then click Apply all settings.

Apply VPN by Device
  1. Connect your devices to the Asus router network and visit the NordVPN website, at the top it should display Your Status: Protected.
  2. Visit NordVPN’s IP Check to verify your new IP address and virtual location.

🚫📱Do not run NordVPN apps on devices connected to your NordVPN router. Using the app at the same time as the router VPN may cause conflicts and connection issues.

Still having issues?

Feel free to submit a ticket and we will get back to you as soon as possible.

Wireless Guest Network Setup – Bridged (Advanced)

TeamFlashRouters · Jun 12, 2019 ·

If you would like to prevent visitors from connecting to your main WiFi network then you can create a Bridged Guest Network that will prevent access to the main router. This setup also allows you to create different rules for different WiFi SSID’s in your home ranging from QoS controls, access restrictions, VPN network segmentation, and more.

Preparing for Wireless Guest Network Setup

If you have a Dual-band or Tri-Band router you can setup a WiFi Guest Network, creating a separate VLAN (virtual local area network) for your visitors, or in order to segment your VPN networks on any band you like. We recommend using the 2.4GHz network for your DD-WRT Guest Wireless Network so it is compatible with the most possible WiFi devices. Setting up a guest network for visitors in your home allows you to keep them off of your main WiFi network.

We recommend performing this setup while connected to the FlashRouter via ethernet cable. If your computer does not have an ethernet port and you must proceed via wireless connection to the FlashRouter pay attention to the wireless connection as you may need to rejoin the FlashRouter’s network after making changes.

DD-WRT Router Setup for Wireless Guest Network

Enter Wireless settings

Navigate to Wireless > Basic Settings

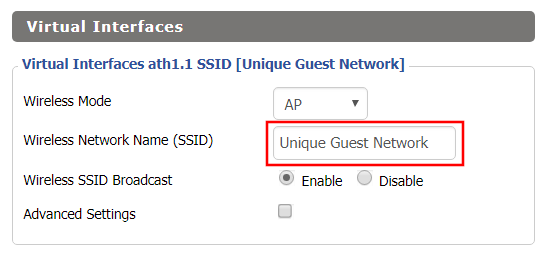
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Setting SSID for Guest Network
  1. Under the 2.4GHz or 5GHz Interface click the Add button.
  2. In the Wireless Network Name (SSID) field enter the unique network name of the guest network.
  3. Click Save.

Enter Wireless Security settings

Navigate to Wireless > Wireless Security

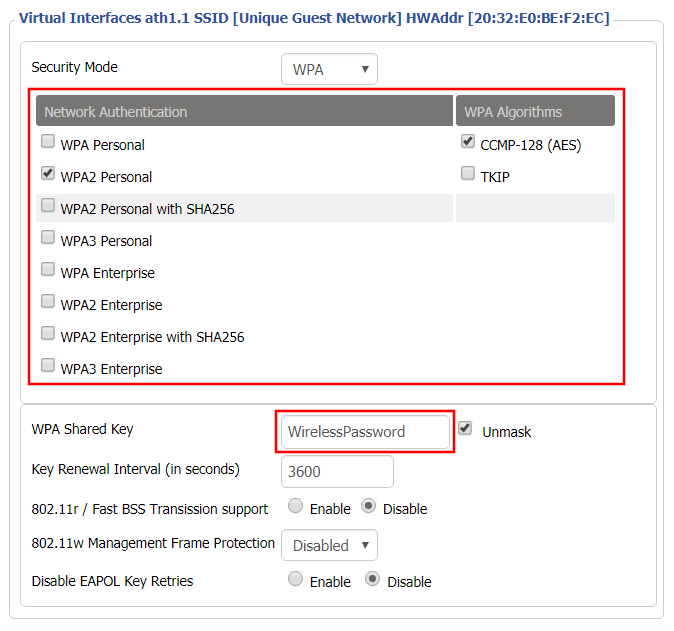
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Setting Guest Network Wireless Password
  1. Duplicate the wireless security settings that are set for the other bands for the newly created virtual interface.
  2. Click Apply Settings.
  3. Reboot your router.

Create Bridge

Navigate to Setup > Networking

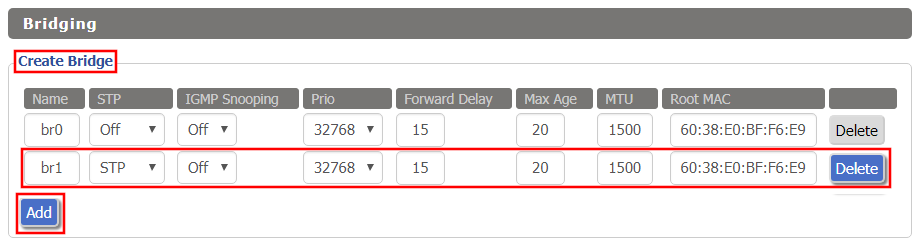
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Create Bridge
  1. Under Create Bridge click Add. Name the newly created bridge br1.
  2. Click Apply Settings

Assign to Bridge

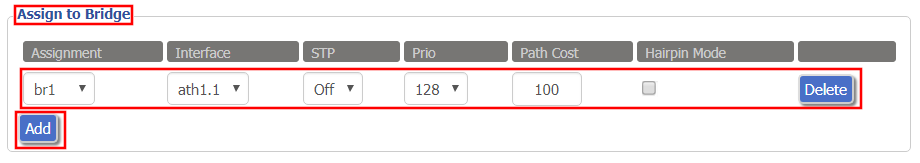
Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Assign Bridge
  1. Under Assign to Bridge select br1 from the Assignment dropdown. Select wl1.1 or ath1.1 depending on your router model.
  2. Click Apply Settings.

Depending on the router model and WiFi band you are using, the wireless interfaces will be labelled differently.

This setting can be labelled wl1.1, ath0.1, wl2.1, and so on. Make sure when you get up to the bridge assignment section that you are using the correct guest network Virtual Interface.

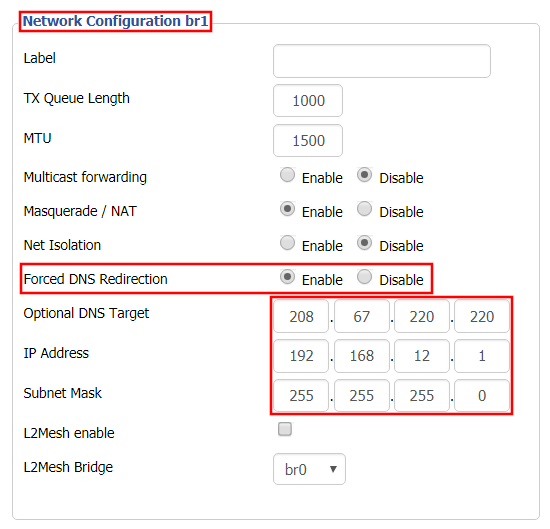
Network Configuration br1

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Configure Bridge DNS Redirection
  1. Under Network Configuration br1 select Enable for Forced DNS Redirection.
  2. Set Optional DNS Target to 208.67.220.220
  3. Set IP Address to 192.168.12.1
  4. Set Subnet Mask to 255.255.255.0
  5. Click Apply Settings.

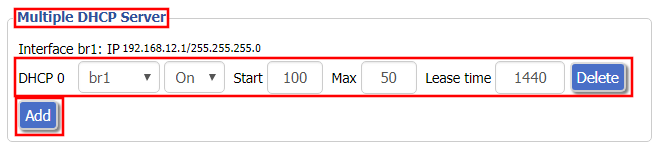
Multiple DHCP Server

Bridged Wireless Guest Network Setup on DD-WRT FlashRouter – Configure DHCP Server Settings
  1. Under Multiple DHCP Server click Add.
  2. Set the first dropdown to br1.
  3. Click Apply Settings.
  4. Reboot your router.

Firewall Rules

Navigate to Administration > Commands

  1. Copy the fire script from below and paste into the empty Commands shell
  2. Click Save Firewall.
  3. Wait one minute and then reboot your router.

iptables -I FORWARD -i br1 -o br0 -m state –state NEW -j DROP
iptables -I FORWARD -i br0 -o br1 -m state –state NEW -j DROP
iptables -I INPUT -i br1 -p tcp –dport telnet -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport ssh -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport www -j REJECT –reject-with tcp-reset
iptables -I INPUT -i br1 -p tcp –dport https -j REJECT –reject-with tcp-reset

You will now have a working Bridged Guest Network on the FlashRouter. By inputting the firewall rules, this will also prevent any guests on your network from gaining access to your router settings.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit our Troubleshooting section to diagnose common problems here.

Troubleshoot Here

How do I reset and reconfigure my FlashRouter?

Dave · May 3, 2019 ·

When is a router reset needed?

A reset of the FlashRouter should only be performed in the following instances:

  • You have exhausted all other troubleshooting methods and cannot access your router settings.
  • A backup file was saved of your previously working settings.
  • Username and password to access the FlashRouter’s settings are not working.
  • Power light on the router is blinking steadily.
  • Firmware upgrade was performed with Reset to Default settings selected.

Reset Router

Asus FlashRouters:

  1. While the router is powered off press and hold the WPS button on the back or side of the router. Power up the router while continuing to hold the WPS. Continue to hold for 15 seconds as the router powers on (note this could be up to 45 seconds on some models before lights flash).
  2. You will see the lights on the router flashing steadily and this is how you know you have reset the router.
  3. Let the router sit for about a minute and then reboot the router.

Linksys and Netgear FlashRouters:

  1. While the router is plugged in, find the reset button located on the back of the router. You will need a pin or pencil to hold down the button for 15 seconds.
  2. You will see the lights on the back of the router flash simultaneously and this is how you know you have reset the router.
  3. Let the router sit for about a minute and then reboot the router.

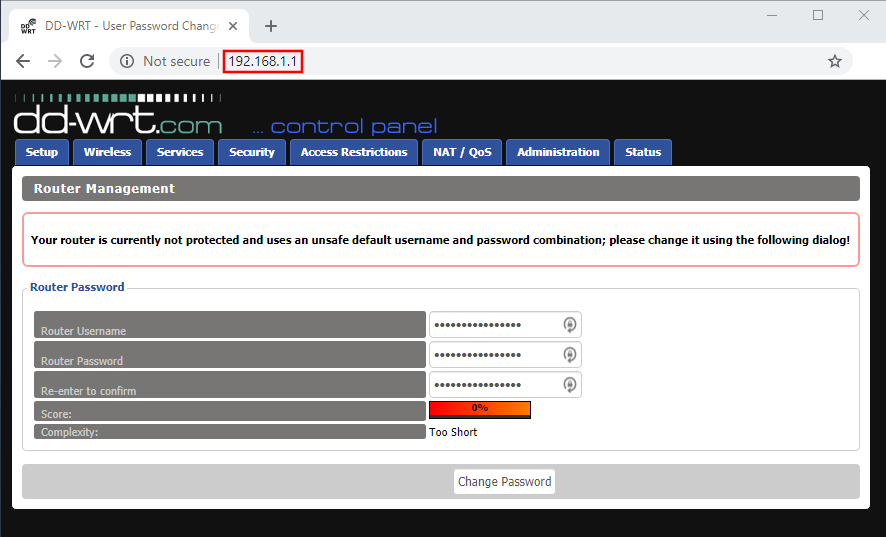
Access Router Settings

1. Connect to the FlashRouter’s network via ethernet cable or wireless.
The wireless network will appear as “dd-wrt” and will likely not require a password to join. If it does require a password to join the password will be the default wireless password found on the bottom of the router.
2. Open your web browser and enter 192.168.1.1 in the URL.

Reset FlashRouters DD-WRT Settings Back to Default Settings

3. Delete the dots and enter the new administration login in the Router Username, Router Password, and Re-enter to confirm fields.

TYPE CAREFULLY when setting the administration login as a typo will result in needing to reset the router again.

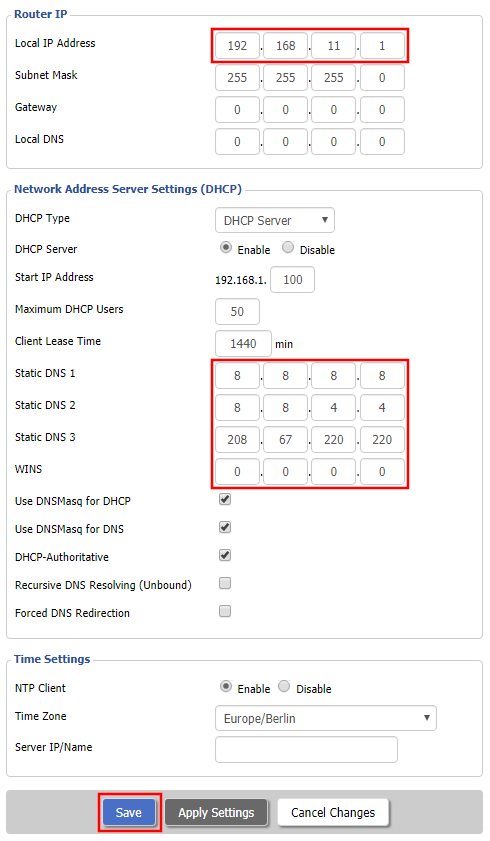
Change Local IP Address and DNS

Navigate to Setup > Basic Setup

1. Set the Local IP Address to 192.168.11.1

2. Set the Static DNS 1 to 8.8.8.8

3. Set the Static DNS 2 to 8.8.4.4

4. Set the Static DNS 3 to 208.67.220.220

Enter New Local IP Address and DNS Servers After FlashRouter DD-WRT Reset

CLICK SAVE

Setup WiFi

Navigate to Wireless > Basic Settings

Find your FlashRouter model in the WiFi Setup section and replicate the wireless settings on this page.

CLICK APPLY SETTINGS

REBOOT ROUTER

Connect to the FlashRouter's network

You will be able to connect to the newly setup wireless network using the details you set. The router will now be accessible at 192.168.11.1

Back up your settings

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to Access Your GL.iNet FlashRouter Settings

TeamFlashRouters · Feb 26, 2024 ·

This quick guide walk you through connecting to your GL.iNet FlashRouter (Flint, Slate, Beryl, or Marble) and logging into the admin settings page. You’ll use either WiFi or an Ethernet cable, then access the router dashboard through your browser.

Step 1. Connect Your Device to the Router

You can connect by WiFi or Ethernet:

  • WiFi: Look for a network name like FlashRouter24 or FlashRouter50
    • The WiFi password has been set to: Wireless#9483C
    • ⚠️ Be sure to capitalize the “W” in
  • Ethernet: Plug an Ethernet cable from your computer into one of the router’s LAN ports (usually marked or color-coded differently from the WAN port).

👉 Pro tip: Disconnect from any other WiFi networks during setup.

Step 2. Open the Router Login Page

  1. Open a web browser (Chrome, Safari, Firefox, Edge).
  2. In the address bar, type: 192.168.8.1
  3. Press Enter.
GL.iNet router access

This is the local router dashboard address (not a public website). If the page doesn’t load:

  • Try a different browser.
  • Clear your cache.
  • Ensure your device is connected to the FlashRouter network.

Step 3. Log In to the Router Settings

  • Default password: glopenwrt1 or openwrt
  • This is the factory default for all GL.iNet routers shipped by FlashRouters.
GL.iNet admin password enter

💡 Once you’re in, you can update your admin password in the settings for extra security.

Next Steps

Now that you’ve accessed your GL.iNet FlashRouter, you can:

  • Set up your VPN service
  • Customize your WiFi name and password
  • Adjust device controls and security settings

Check our support library for your specific VPN setup guide.

How to Access Your AsusWRT FlashRouter Settings

TeamFlashRouters · Oct 16, 2025 ·

This quick guide will walk you through connecting to your AsusWRT FlashRouter and logging into the admin settings page. You’ll use either WiFi or an Ethernet cable, then access the router dashboard through your browser.

Step 1. Connect Your Device to the Router

You can connect by WiFi or Ethernet:

  • WiFi: Look for a network name like FlashRouter24 or FlashRouter50.
    • The WiFi password is set to: Wireless#[First 5 characters of your router’s MAC]
    • Example: If your MAC is CC28A07E70A8, your WiFi password is Wireless#CC28A.
    • ⚠️ Be sure to capitalize the “W” in Wireless.
  • Ethernet: Plug an Ethernet cable from your computer into one of the router’s LAN ports (usually marked or color-coded differently from the WAN port).

👉 Pro tip: Disconnect from any other WiFi networks during setup.

Step 2. Open the Router Login Page

  1. Open a web browser (Chrome, Safari, Firefox, Edge).
  2. In the address bar, type: 192.168.50.1 or go to asusrouter.com
  3. Press Enter.
Access Asus Router

This is the local router dashboard address (not a public website). If the page doesn’t load:

  • Try a different browser.
  • Clear your cache.
  • Ensure your device is connected to the FlashRouter network.

Step 3. Log In to the Router Settings

  • Default username: flashrouter
  • Default password: asuswrt-admin1
  • Some older devices may use: asuswrt1 or asuswrt
  • This is the factory default for AsusWRT routers shipped by FlashRouters.
Asus Router Login

💡 Once you’re in, you can update your admin password in the settings for extra security.

Next Steps

Now that you’ve accessed your AsusWRT FlashRouter, you can:

  • Set up your VPN service
  • Customize your WiFi name and password
  • Adjust device controls and security settings

Check our support library for your specific VPN setup guide.

Mullvad WireGuard Setup

TeamFlashRouters · Aug 19, 2021 ·

Preparing for Mullvad WireGuard Setup

Verify your Mullvad login information

If you are not already a Mullvad user Sign Up Now.

Log in to your account on the Mullvad website.

Mullvad Login

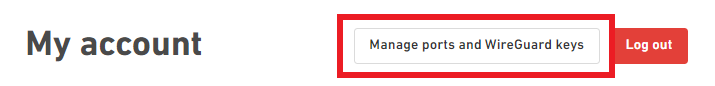
Select Manage ports and WireGuard Keys displayed on the account page.

Mullvad Manage ports and WireGuard Keys

DD-WRT Router Setup for Mullvad WireGuard

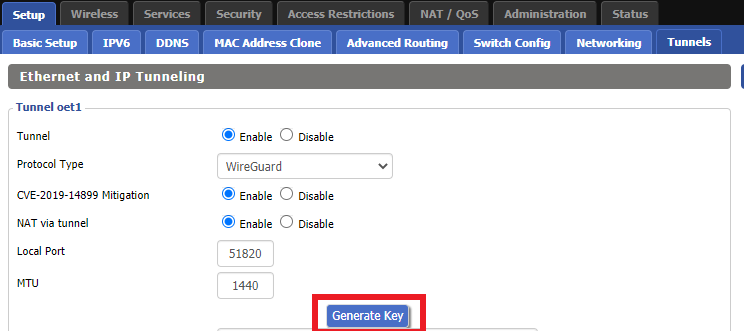
Navigate to Setup > Tunnels 

Enter Mullvad WireGuard settings

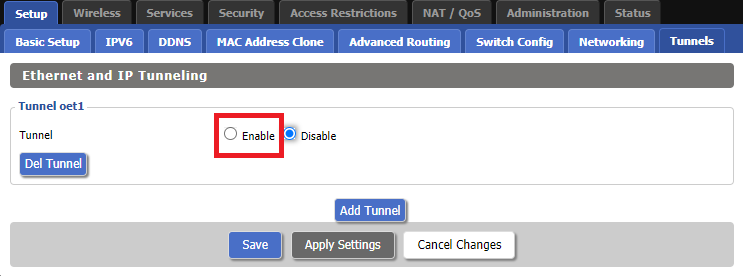
1. Click Add Tunnel.

2. Set Tunnel to Enable.

Setup - Tunnel - Enable Tunnel

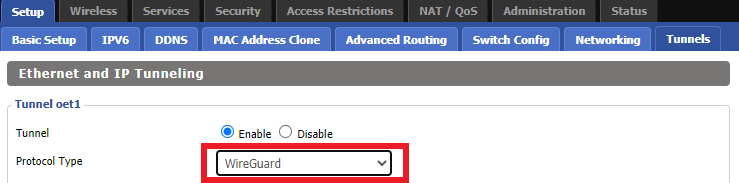
3. Select Wireguard from the dropdown.

Setup - Tunnel - Select Wireguard

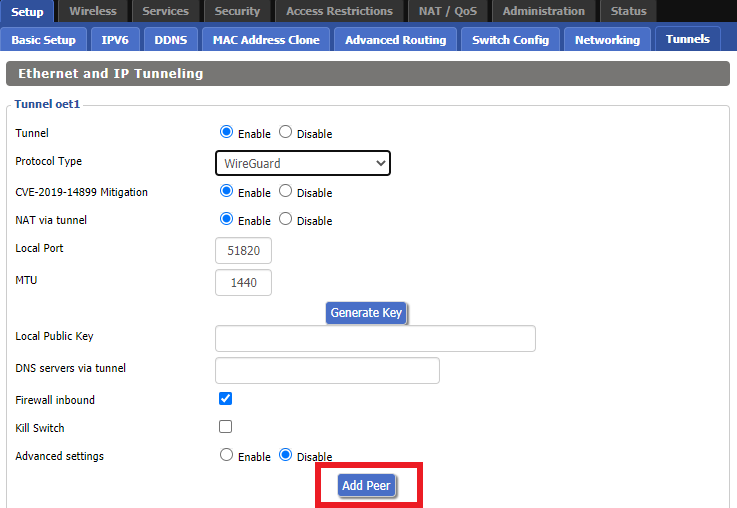
4. Click Add Peer.

Setup - Tunnel - Add Peer

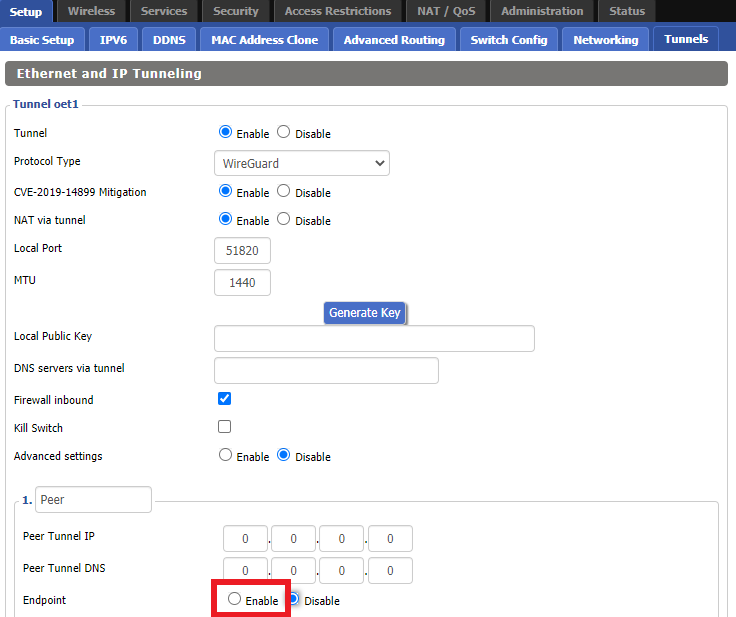
5. Set Endpoint to Enable.

Setup - Tunnel - Enable Endpoint

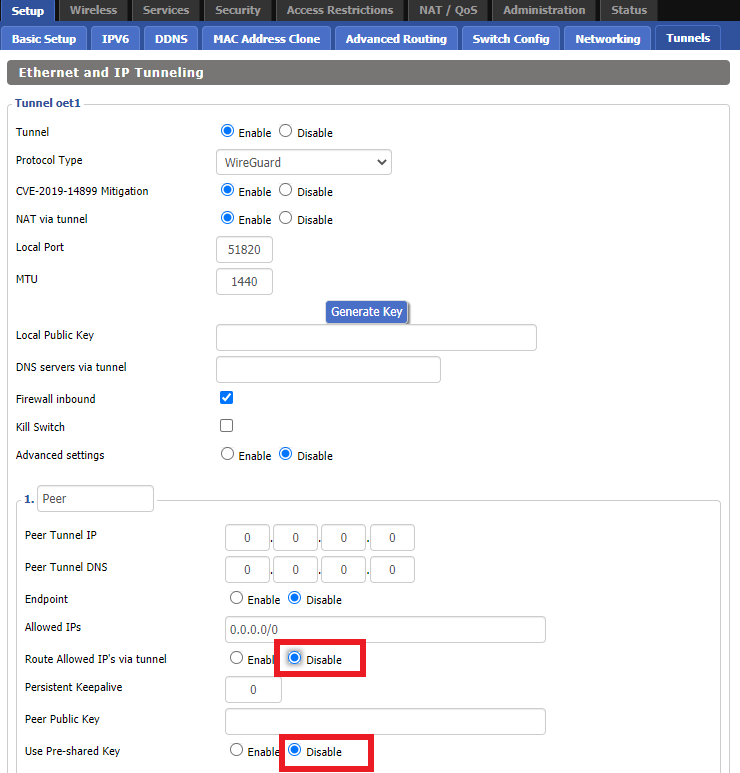
6. Set Router Allowed IP’s via tunnel and Use Pre-shared Key to Disable.

Setup - Tunnel - Disable Preshare Key and Allow IP

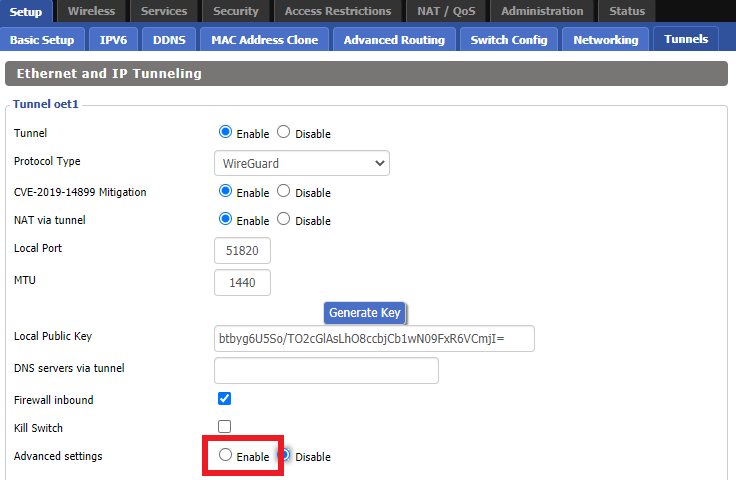
7. Click Generate Key.

Setup - Tunnel - Generate Key

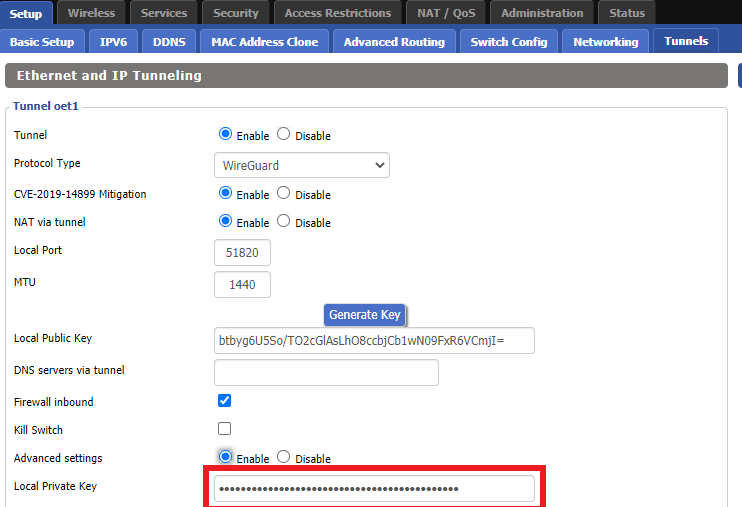
8. Set Advanced Settings to Enable.

Setup - Tunnel - Enable Advanced Settings

9. Copy the Local Private Key.

Setup - Tunnel - Copy Local Private Key

10. In a new tab (leave the DD-WRT settings opened), go to your Mullvad Account and click Manage Ports and WireGuard Keys.

Mullvad Account - Manage ports and Wireguard Keys

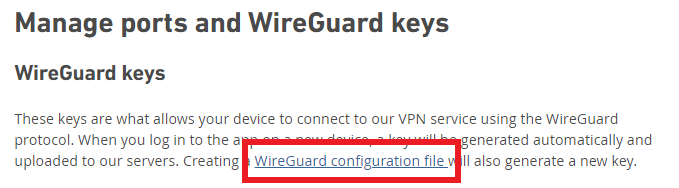
11. Click WireGuard configuration file.

Mullvad - Wireguard configuration file

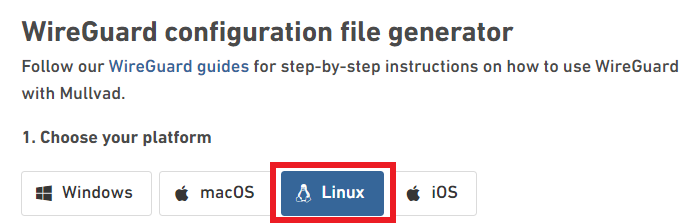
12. Select Linux as your Platform.

Mullvad - Select Linux

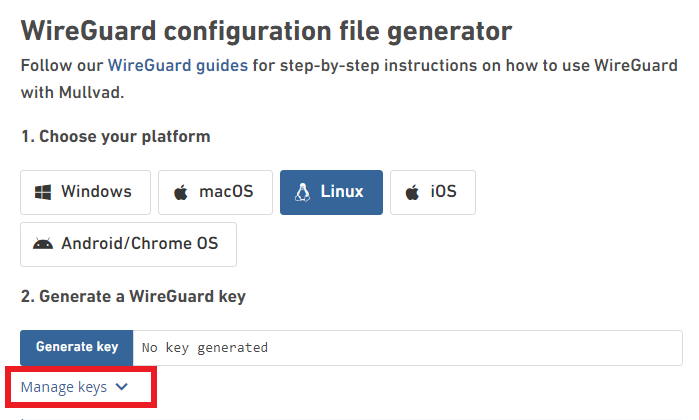
13. Click Manage Keys.

Mullvad - Manage Keys

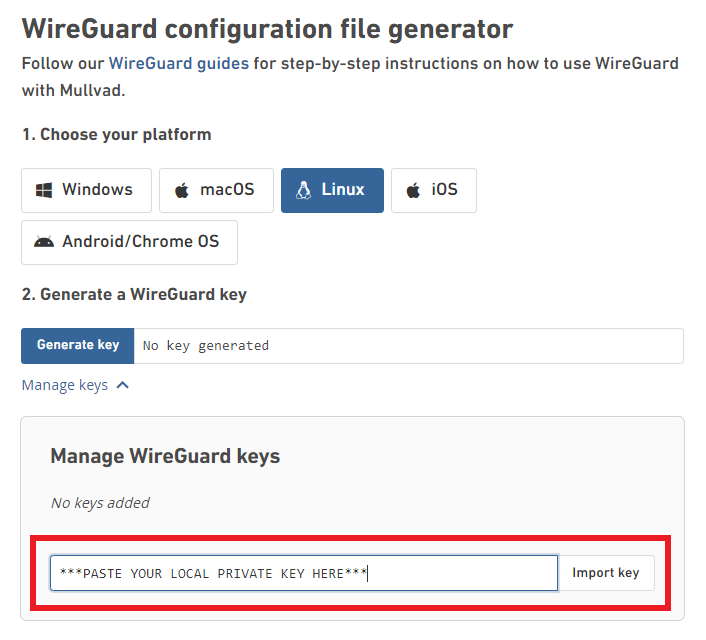
14. Paste the copied Local Private key to the Manage WireGuard Keys field and click Import Keys.

Mullvad - Import Key

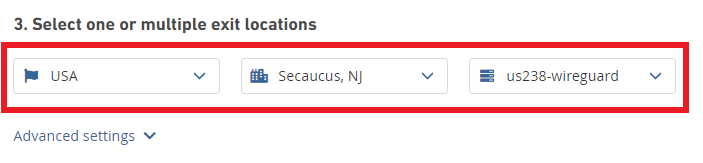
15. Select your Country, City, and Server number that you want to connect to.

Mullvad - Select Location

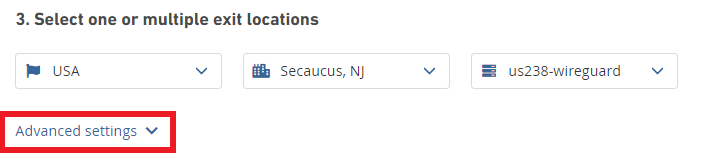
16. Click Advanced Settings.

Mullvad - Advanced Settings

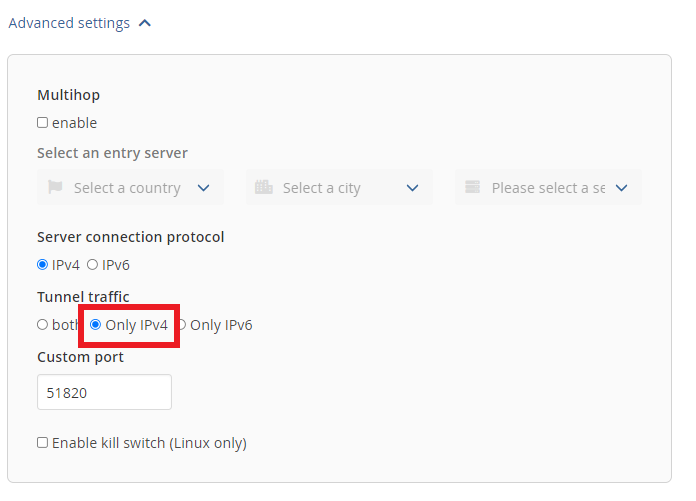
17. Set the Tunnel Traffic to Only IPv4.

Mullvad - Only IPv4

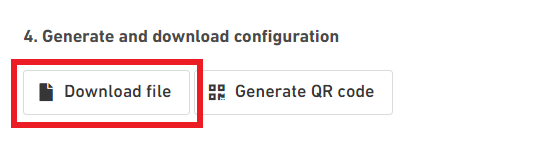
18. Click Download File.

Mullvad - Download Config

19. Open the config file that was downloaded to your computer with NotePad or Notepad++ for Windows or TextEdit for Mac.

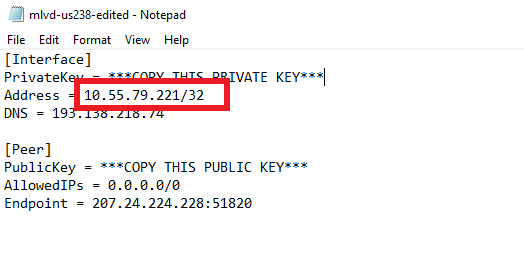
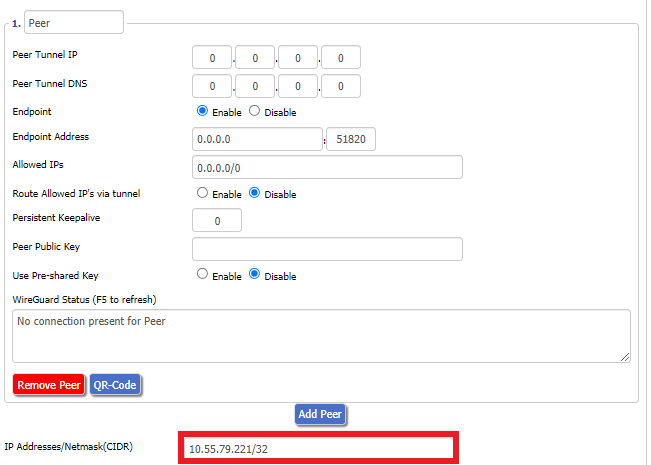
20. In the downloaded config file under [Interface] enter the Address into the IP Addresses/Netmask(CIDR) field in the DD-WRT settings.

Config File - Copy IP Address
Setup - Tunnel - IP Address Netmask Note

Certain DD-WRT builds will show two separate fields here: IP Address and Subnet Mask. If that is the case set the IP Address field to the Address without the /32 added and set the Subnet Mask to 255.255.255.255

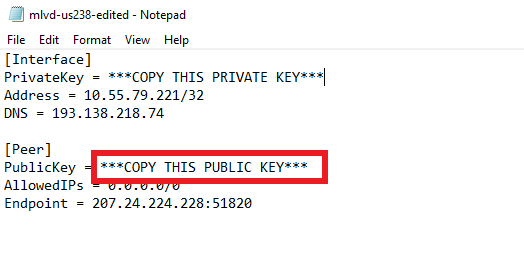
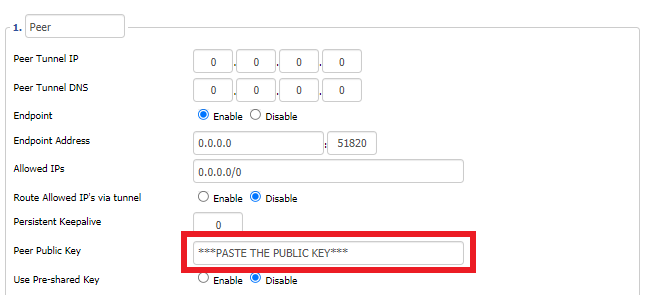
21. In the config file under [Peer] copy the PublicKey and paste it into the Peer Public Key field in the DD-WRT Settings.

Config File - Copy PublicKey
Setup - Tunnel - Paste Public Key

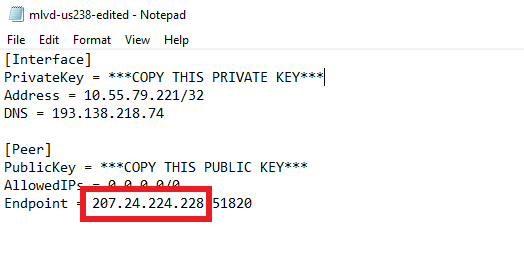
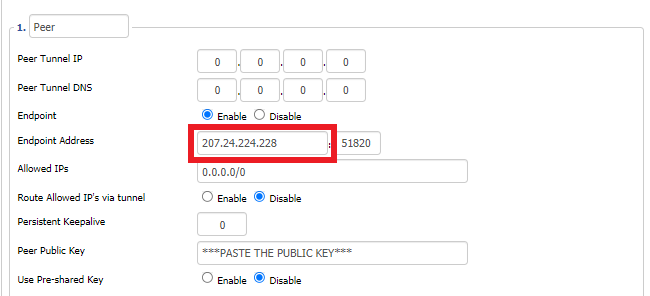
22. In the config file under [Peer] copy the Endpoint and paste it into the Endpoint Address field.

Config File - Endpoint
Setup - Tunnel - Endpoint Address

23. At the bottom of the page click Save and then click Apply Settings.

Enter Mullvad WireGuard Commands

Navigate to Administration > Commands

1. Copy and paste the text below and click Save Startup.

sleep 30
echo "Update route table on startup..."
WGSERVER=$(/usr/sbin/nvram get oet1_rem0)
WANGW=$(/usr/sbin/nvram get wan_gateway)
WANIF=$(/usr/sbin/nvram get wan_iface)
route add -host $WGSERVER gw $WANGW dev $WANIF
route del default
route add default dev oet1
ip route flush cache
mkdir -p /tmp/etc/config
ln -s /tmp/custom.sh /tmp/etc/config/wg-route-fix.wanup
echo "... Done route table update."

2. Copy and paste the text below and click Save Custom.

#!/bin/sh
sleep 5
echo "Update route table on wanup ..."
WGSERVER=$(/usr/sbin/nvram get oet1_rem0)
WANGW=$(/usr/sbin/nvram get wan_gateway)
WANIF=$(/usr/sbin/nvram get wan_iface)
route add -host $WGSERVER gw $WANGW dev $WANIF
route del default
route add default dev oet1
ip route flush cache
echo "... Done route table update."

3. Copy and paste the text below and click Save Firewall.

WANIF=$(/usr/sbin/nvram get wan_iface)
iptables -t nat -I POSTROUTING -o oet1 -j MASQUERADE
iptables -I FORWARD -i br0 -o $WANIF -m state –state NEW -j REJECT –reject-with icmp-host-prohibited
iptables -I FORWARD -i br0 -p tcp -o $WANIF -m state –state NEW -j REJECT –reject-with tcp-reset

Set Mullvad DNS servers

Navigate to Setup > Basic Setup

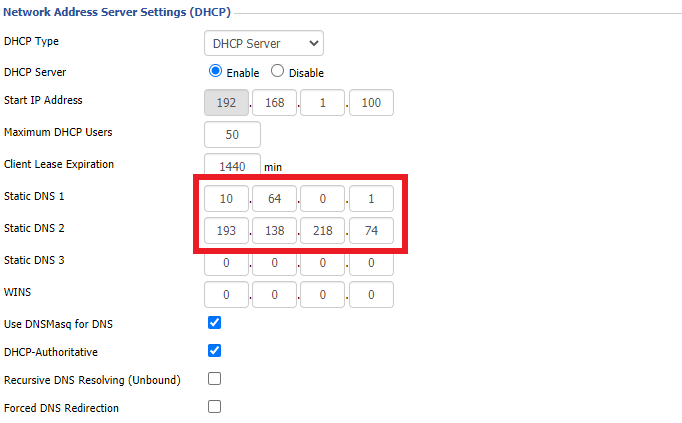
Set Static DNS 1 to 10.64.0.1

Set Static DNS 2 to 193.138.218.74

Setup - Basic Setup - Mullvad DNS

Click Apply Settings.

Reboot the FlashRouter

Navigate to Administration > Management

Scroll to the bottom of the page and click the red Reboot Router button. Wait for the FlashRouter to reboot and then reconnect.

Verify a successful Mullvad connection

Navigate to Setup > Tunnels

  1. You should see Endpoint, Latest handshake, and Transfer in the WireGuard status area.
  2. Visit Mullvad’s IP Check to verify your status as using Mullvad.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero VPN Kill Switch Troubleshooting: No Internet or WiFi

Dave · Oct 8, 2026 ·

If your Privacy Hero router suddenly loses internet access, devices report that WiFi has no internet, or devices will not stay connected after a VPN failure, the VPN Kill Switch may be blocking normal internet traffic.

The VPN Kill Switch is designed to prevent traffic from passing through Privacy Hero without VPN protection. If the VPN disconnects or fails while the Kill Switch is enabled, normal internet access is intentionally blocked.

Important: You can still access app.privacyhero.com to manage Privacy Hero, turn off the Kill Switch, or repair the VPN connection.

Privacy Hero is cloud-managed, so you do not need to be connected to the Privacy Hero WiFi to change these settings. You can also access the dashboard using cellular data, your main router’s WiFi, or another internet connection as long as Privacy Hero remains connected to the internet and Privacy Hero cloud.


Jump to a Section

  • Common Kill Switch Symptoms
  • Restore Internet Access
  • VPN Still Fails to Connect
  • Privacy Hero Appears Offline
  • Kill Switch, WiFi, or WAN Problem?
  • Frequently Asked Questions

Common Privacy Hero Kill Switch Symptoms

A failed VPN connection combined with an enabled Kill Switch can make the Privacy Hero network appear unavailable even though the router itself may still be functioning.

Common symptoms include:

  1. Your device connects to Privacy Hero WiFi but websites and apps will not load.
  2. Your phone, computer, television, or streaming device reports that WiFi has no internet.
  3. A device refuses to remain connected because it detects that the WiFi network does not currently provide normal internet access.
  4. Your phone automatically switches from Privacy Hero WiFi to cellular data or another saved WiFi network.
  5. Your computer displays “No Internet” or “Connected without Internet.”
  6. The VPN displays Failed, Disconnected, Connecting, or a timeout error.
  7. Privacy Hero was working normally and suddenly stopped providing internet access.

If the Privacy Hero WiFi network itself is completely missing and cannot be detected by any device, that is different from normal Kill Switch behavior. Continue with WiFi or router connectivity troubleshooting instead.

Restore Internet Access

The fastest way to determine whether the Kill Switch is responsible is to temporarily disable it and test Privacy Hero without VPN.

  1. Open app.privacyhero.com.
  2. Sign in to your Privacy Hero account.
  3. Open the VPN section.
  4. Check the current VPN status.
  5. If the VPN shows Failed or Disconnected, turn the VPN Kill Switch Off.
  6. Turn the failed VPN connection off.
  7. Connect a device to the Privacy Hero network.
  8. Test normal internet access.

If internet access returns with the VPN and Kill Switch disabled, Privacy Hero’s basic internet connection is working and the problem is isolated to the VPN connection.

Important: Disabling the Kill Switch allows normal non-VPN internet traffic through Privacy Hero. Leave it disabled only while troubleshooting if continuous VPN protection is required.

VPN Still Fails to Connect

Do not turn the Kill Switch back on until the VPN is connected and working.

If you are using NordVPN and the VPN shows Failed, Connecting, or a timeout error, continue with our dedicated Privacy Hero NordVPN Not Connecting or Showing Timeout Errors guide.

That guide covers:

  • Selecting a different NordVPN server.
  • Replacing a failed Auto Country connection with a specific NordVPN server.
  • Generating a new NordVPN NordLynx access token.
  • Verifying NordVPN OpenVPN manual service credentials.
  • Avoiding double-VPN conflicts while testing.

If you use another VPN provider, try another available VPN server or protocol and verify that your VPN account and credentials remain active.

Verify the VPN Before Re-Enabling the Kill Switch

Once the VPN reconnects:

  1. Confirm Privacy Hero displays the VPN as Connected.
  2. Connect a device to the Privacy Hero WiFi.
  3. Make sure a separate VPN application is not connected directly on the testing device.
  4. Check your public IP address.
  5. Confirm the IP address and location reflect the VPN server you selected.
  6. Test normal websites and applications.
  7. Return to Privacy Hero and enable the VPN Kill Switch.

If you enable the Kill Switch while the VPN is still failing, normal internet access will be blocked again.

What If Privacy Hero Appears Offline?

If Privacy Hero shows Offline in the dashboard, the router may not currently be communicating with the Privacy Hero cloud.

  1. Confirm Privacy Hero is powered on.
  2. Confirm the Ethernet cable from your ISP gateway or primary router is connected to the Privacy Hero WAN/Internet port.
  3. Confirm your ISP gateway or primary router has working internet access.
  4. Restart Privacy Hero and allow it to finish booting.
  5. Using another internet connection, open app.privacyhero.com.
  6. Check whether Privacy Hero returns online.

If the router returns online, check the VPN and Kill Switch status before enabling the VPN again.

Privacy Hero Has a WAN IP but Devices Have No Internet

Privacy Hero can receive an IP address from your ISP gateway while the Kill Switch is still blocking normal internet traffic.

Before changing IP Passthrough, bridge mode, firewall settings, or other ISP gateway settings:

  1. Check the VPN status.
  2. Check whether the Kill Switch is enabled.
  3. Disable the VPN and Kill Switch temporarily.
  4. Test internet access again.

If internet access returns, troubleshoot the VPN connection rather than changing the ISP gateway configuration.

Kill Switch, WiFi, or WAN Problem?

WiFi Connects but There Is No Internet

If the VPN shows Failed or Disconnected and the Kill Switch is enabled, the Kill Switch is likely blocking normal internet traffic.

Device Will Not Stay Connected to Privacy Hero WiFi

Some devices automatically leave a WiFi network when they detect that it does not provide internet access. Use cellular data or another internet connection to access app.privacyhero.com and check the VPN and Kill Switch.

Privacy Hero WiFi Is Completely Missing

The Kill Switch does not normally cause the WiFi network itself to stop broadcasting. If no devices can detect the Privacy Hero WiFi network, troubleshoot the WiFi or router connection separately.

Privacy Hero Is Not Receiving a WAN IP Address

Check the Ethernet connection between Privacy Hero and your ISP gateway or primary router and confirm the upstream internet connection is working.

VPN Shows Connected but One Device Has the Wrong IP

If the VPN works correctly on other devices, the Kill Switch is probably not the issue. Check that device’s Privacy Hero VPN assignment and its own VPN, privacy, DNS, or security settings.

See Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN.

Frequently Asked Questions

Why does Privacy Hero WiFi say no internet?

If the VPN has failed while the Kill Switch is enabled, normal internet traffic is intentionally blocked. Your device may therefore report that Privacy Hero WiFi has no internet.

Can I access Privacy Hero settings while the Kill Switch is blocking internet?

Yes. Open app.privacyhero.com. You can use the Privacy Hero network, cellular data, your main router’s WiFi, or another internet connection.

Do I have to be connected to Privacy Hero WiFi to change the settings?

No. Privacy Hero is cloud-managed and can be managed remotely while the router remains connected to the Privacy Hero cloud.

Why does my phone keep leaving the Privacy Hero WiFi?

Some phones automatically switch to cellular data or another saved WiFi network when the current WiFi connection does not provide normal internet access.

Should I turn the Kill Switch back on immediately?

Only after the VPN is connected and you have confirmed that your internet traffic is using the VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero NordVPN Not Connecting or Showing Timeout Errors
  • Privacy Hero NordVPN / NordLynx Setup
  • Device Privacy, DNS, VPN, and Security Settings That Can Interfere With Your Router VPN
  • Privacy Hero Router Setup Guide

How do I check for static network settings on my devices?

TeamFlashRouters · May 8, 2019 ·

Static network settings set on a device from a previous connection will interfere with the FlashRouter’s network. Typically the FlashRouter’s network performs best when connected devices are set to automatically use the FlashRouter’s IP Address and DNS.

Make sure you are connected to the FlashRouter’s network via ethernet or WiFi. Keep in mind these instructions may vary based on your current software version.

Check for Static IP Address in Windows

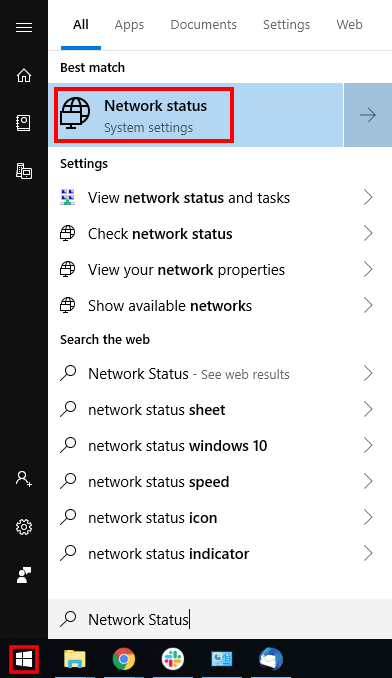
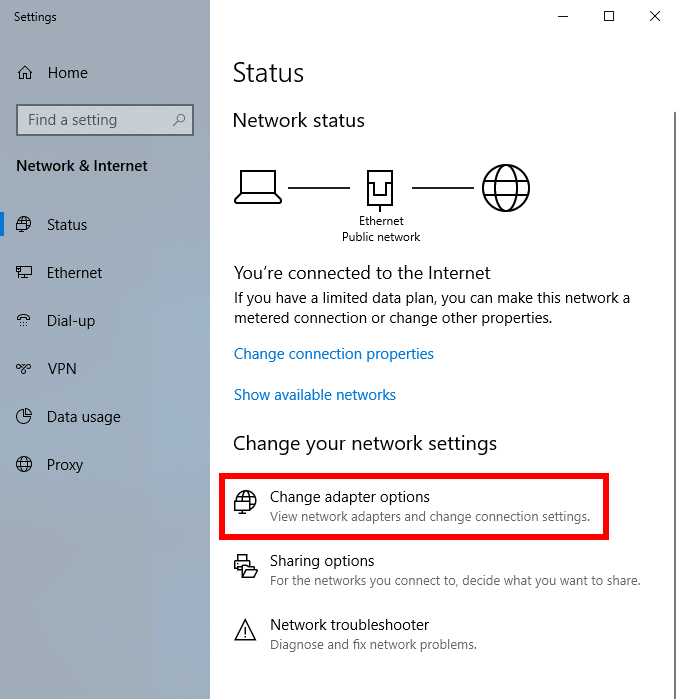
1.  Open the Window search box, and search “Network Status”

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer

2. Select “Change adapter optons”

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer 2

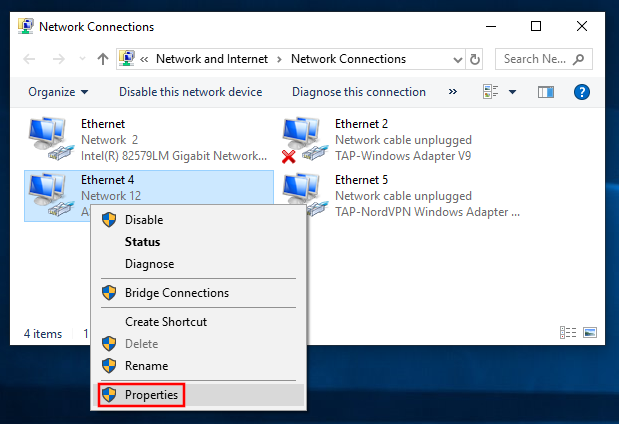
3. Right click on the WiFi and/or ethernet adapter and select Properties.

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer 3

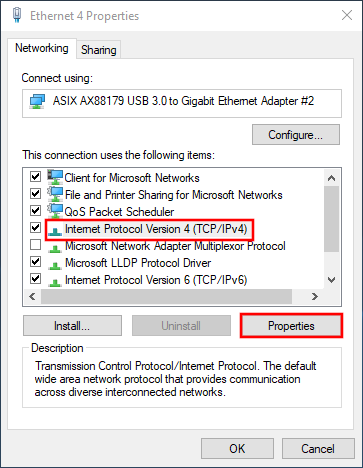
4. Highlight Internet Protocol Version 4 (TCP/IPv4) and click Properties.

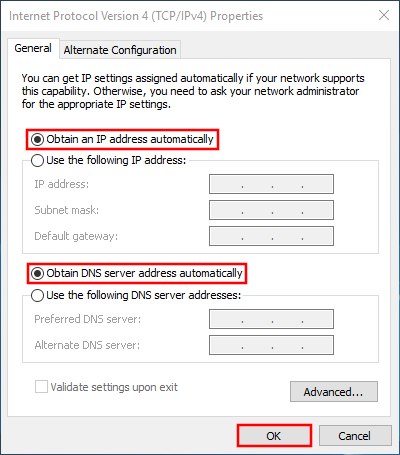
5. Delete the values entered for IP address, Subnet mask, Default gateway, Preferred DNS server, and Alternate DNS server.

6. Select Obtain an IP address automatically and Obtain DNS server address automatically.

7. Click OK.

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer 4

Check for Static IP Address in Apple / Mac

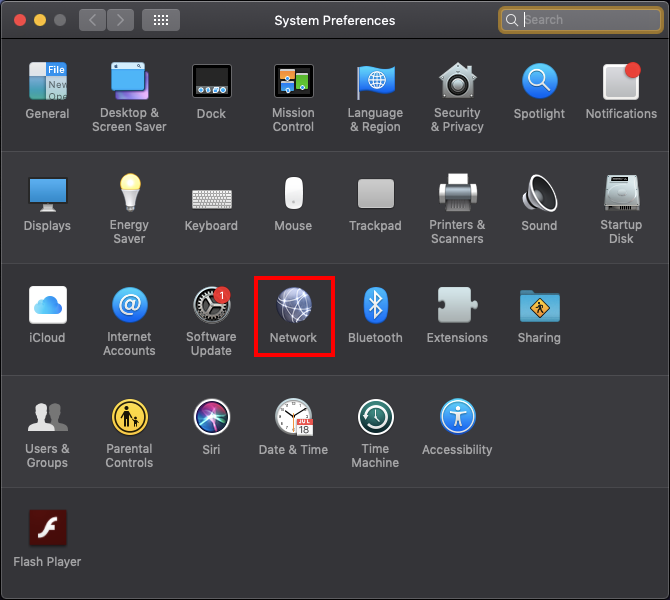
1. Open System Preferences, and select Network.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer

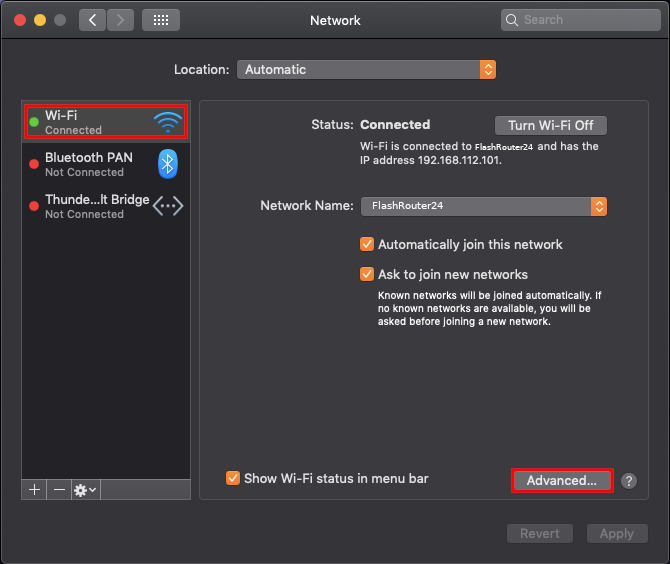
2. Select the adapter that is connected via ethernet or wireless. This will vary based on your current connection.

3. Select Advanced.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer 2

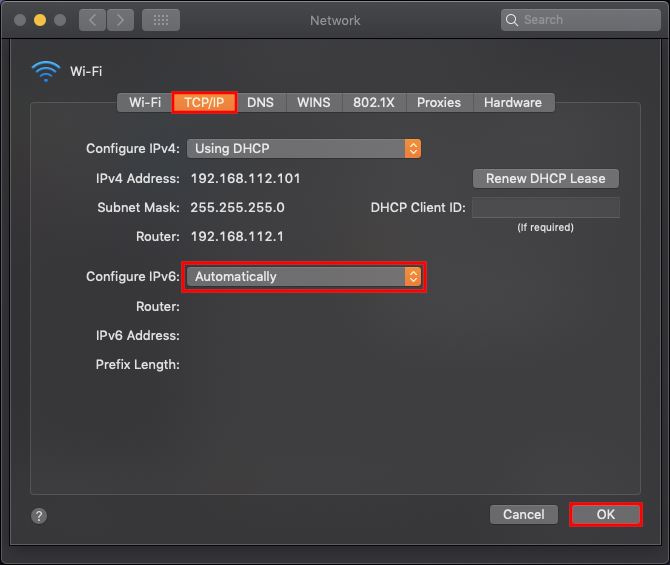
4. Select the TCP/IP tab.

5. Set Configure IPv4 to Automatically.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer 4

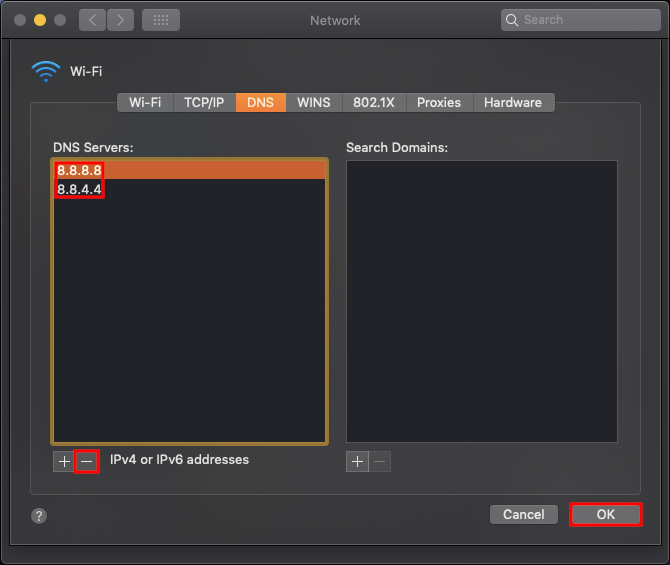
6. Select the DNS field and highlight any DNS servers you see there. If they can be removed you should click the minus symbol below.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer 5

7. Click OK.

8. Click Apply.

Check for Static IP Address in iOS

1.  Open Settings

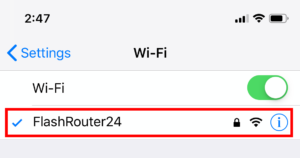
2. Select WiFi, and select the blue icon next to your current connection.

Select FlashRouters DD-WRT Wireless Network in order to Check Static IP Network Settings on iOS Mobile Device

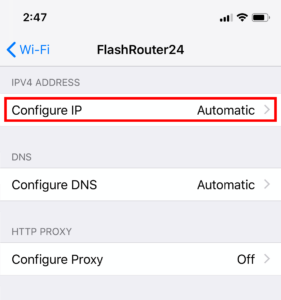
3. Make sure Configure IP is set to Automatically.

Check Static IP Network Settings on iOS Mobile Device and set Configure IP to Automatic

Check for Static IP Address in Android

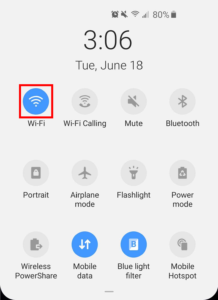
1. From the top of the screen, swipe down to display settings.

2. Select WiFi.

WiFi Icon and Settings in Android Mobile Device

3. Select your current network.

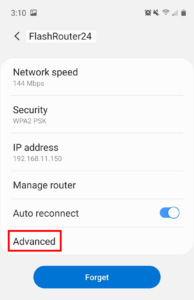
4. Select Advanced.

Advanced Settings Button in Android Mobile Device

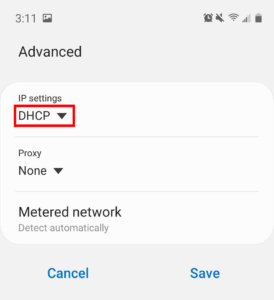
5. Make sure that IP settings is set to DHCP.

Check Static IP DHCP Network Settings in Android Mobile Device

Privacy Hero Dashboard Not Updating or Showing Old Information

Dave · Oct 8, 2026 ·

If the Privacy Hero dashboard is showing old information, a VPN status does not appear to update, settings you changed are not displaying correctly, or the dashboard behaves unexpectedly, your browser may be displaying cached Privacy Hero website data.

Before changing your router or VPN configuration again, open a fresh browser session and confirm that the dashboard is displaying the current information.

Start With a Private or Incognito Browser Window

The fastest test is to open the Privacy Hero dashboard in a new private or incognito browser window.

  1. Close any existing Privacy Hero dashboard tabs.
  2. Open a new private or incognito browser window.
  3. Visit app.privacyhero.com.
  4. Sign in to your Privacy Hero account.
  5. Check the router, VPN, device, or setting again.

If the correct information appears in the private browser window, the original browser session was likely displaying cached or stale website information.

Refresh the Privacy Hero Dashboard

If the dashboard has been open while you are changing VPN or router settings, refresh the page before assuming that a change failed.

  1. Refresh the Privacy Hero dashboard.
  2. Allow the page to finish loading.
  3. Return to the section you were changing.
  4. Check the current status again.

If the information still appears incorrect, sign out of Privacy Hero, close the browser tab, and sign back in through a fresh browser session.

Clear Cached Privacy Hero Site Data

If Privacy Hero works correctly in a private/incognito window but not in your normal browser window, clear the cached website data for Privacy Hero.

Browser menus vary, but look for settings related to:

  • Cached files and images.
  • Cookies and site data.
  • Website data.
  • Privacy and browsing data.

If your browser allows you to remove data for an individual website, clear the stored data for app.privacyhero.com rather than clearing your entire browser history.

Then reopen app.privacyhero.com, sign in again, and check the dashboard.

Try Another Browser or Device

If the dashboard still behaves unexpectedly, test it from another browser or device.

  1. Open app.privacyhero.com in another browser.
  2. Sign in using the same Privacy Hero account.
  3. Check whether the same router and settings appear correctly.

You can also test from another computer, phone, or tablet.

Privacy Hero is cloud-managed, so you do not need to be connected to the Privacy Hero WiFi to access the dashboard. You can use cellular data, another WiFi network, or another internet connection.

Disable Browser Extensions While Testing

Browser extensions can sometimes interfere with website login, scripts, or dashboard functions.

If the problem occurs only in one browser, temporarily test without extensions such as:

  • Ad blockers.
  • Privacy extensions.
  • Script blockers.
  • VPN or proxy extensions.
  • Security or filtering extensions.

A private/incognito window may disable some extensions automatically, depending on your browser configuration.

VPN Status Still Shows Failed or Connecting?

If a fresh browser session confirms that Privacy Hero is actually reporting the VPN as Failed, Connecting, Disconnected, or showing a timeout error, the problem is no longer just a browser display issue.

NordVPN users should continue with Privacy Hero NordVPN Not Connecting or Showing Timeout Errors.

No Internet After the VPN Failed?

If the dashboard confirms that the VPN has failed and your Privacy Hero network also has no internet access, check whether the VPN Kill Switch is enabled.

See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

One Device Shows the Wrong VPN IP?

If Privacy Hero shows the VPN as connected and working but only one device shows an unexpected IP address or location, the browser cache is probably not the main issue.

Check the device for its own VPN application, Private Relay, Private DNS, browser Secure DNS, antivirus, firewall, or other network settings.

See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero NordVPN Not Connecting or Showing Timeout Errors
  • Privacy Hero VPN Kill Switch Setup
  • Device Settings That Can Interfere With Your Router VPN

NordVPN Setup for GL.iNet Routers

TeamFlashRouters · May 29, 2023 ·

You can connect to NordVPN on your GL.iNet router using NordLynx, OpenVPN, or a Dedicated IP.

Quick Options

  • NordLynx: Choose your preferred city or country from NordVPN’s server list

  • OpenVPN: Choose your preferred city or country from NordVPN’s server list.

  • Dedicated IP (optional): Enter your unique configuration file if you’ve been assigned a static NordVPN IP.

:point_right: If you are not already a NordVPN user Sign Up Now.

NordVPN NordLynx Setup for GLiNet

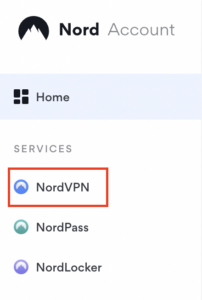
1. Get your NordVPN Access Token for NordLynx connections. Log in to your NordVPN account and select NordVPN from your list of Services.

NordVPN Services Section

2. At the bottom of the page click Get Access token and you will receive a code via email. Enter this code to proceed.

NordVPN Access Token

3. After you enter the email code select Generate new token and set it to Doesn’t expire. Copy this token.

NordVPN Generate new token
NordVPN Copy Token

4. Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

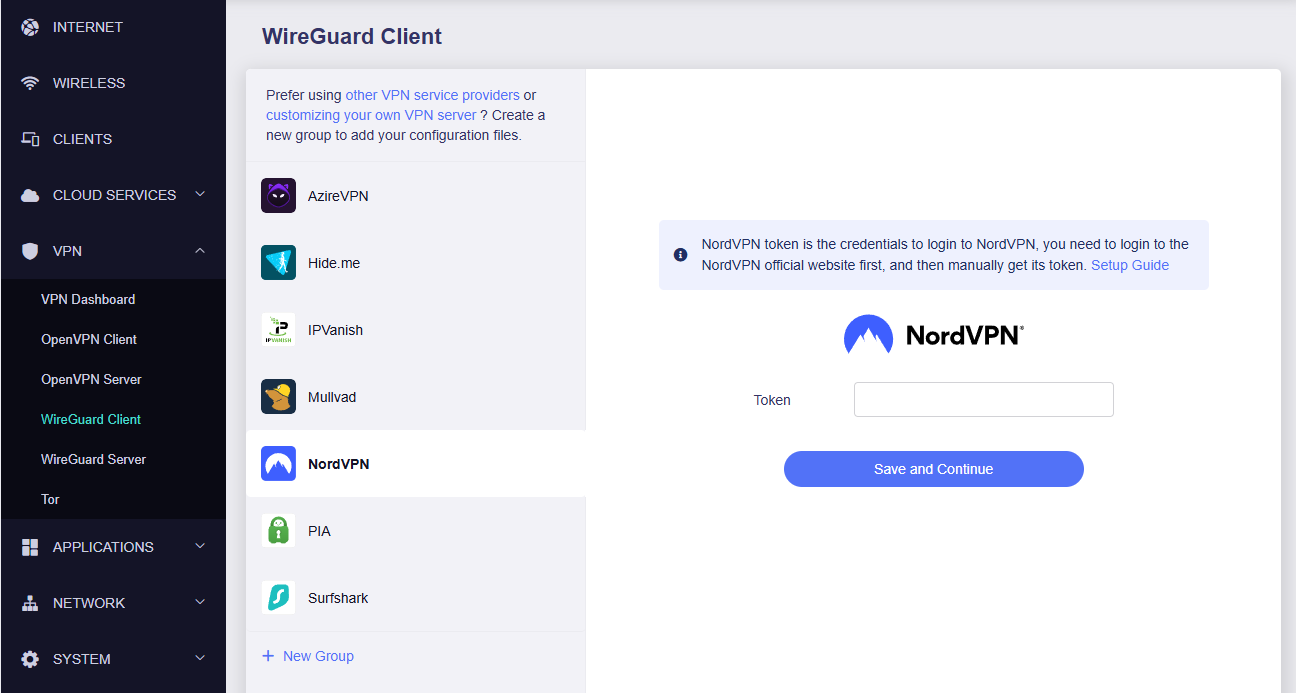
5. Navigate to the VPN tab and select Wireguard Client then choose NordVPN. Enter your Token then click Save and Continue

GLiNet NordVPN Wireguard

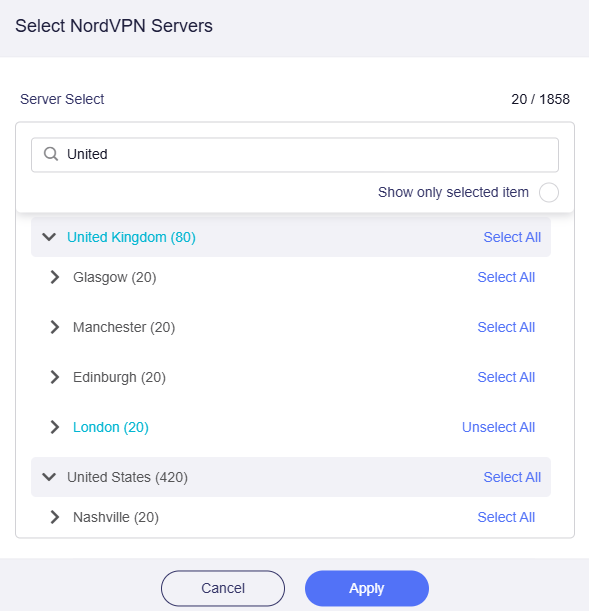
6. Select your preferred server locations, and click Apply.

GLiNet Select NordLynx Servers

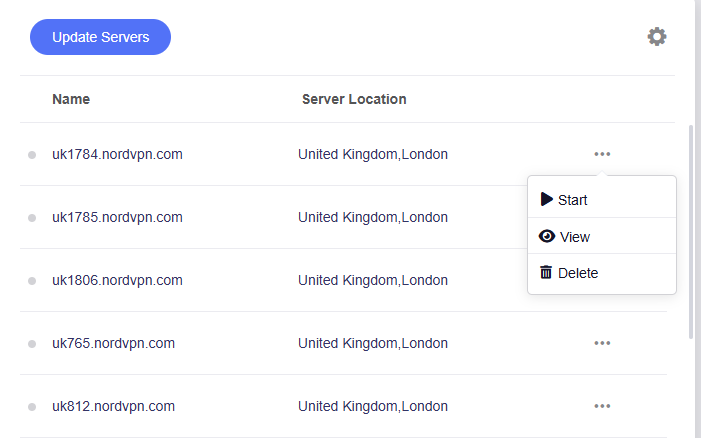
7. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

GLiNet NordLynx Start

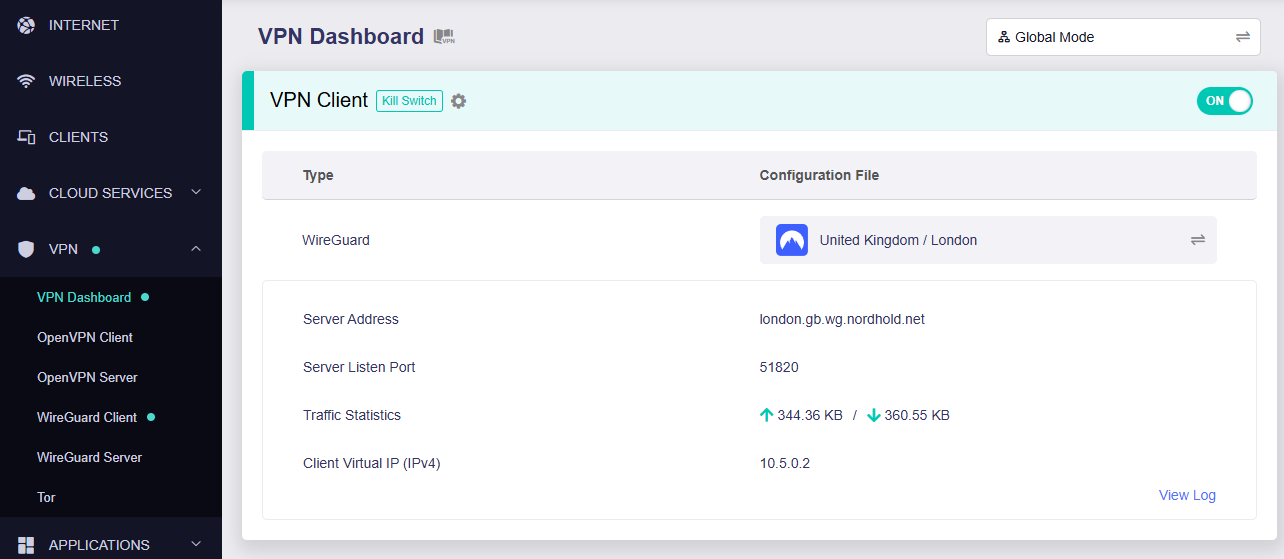
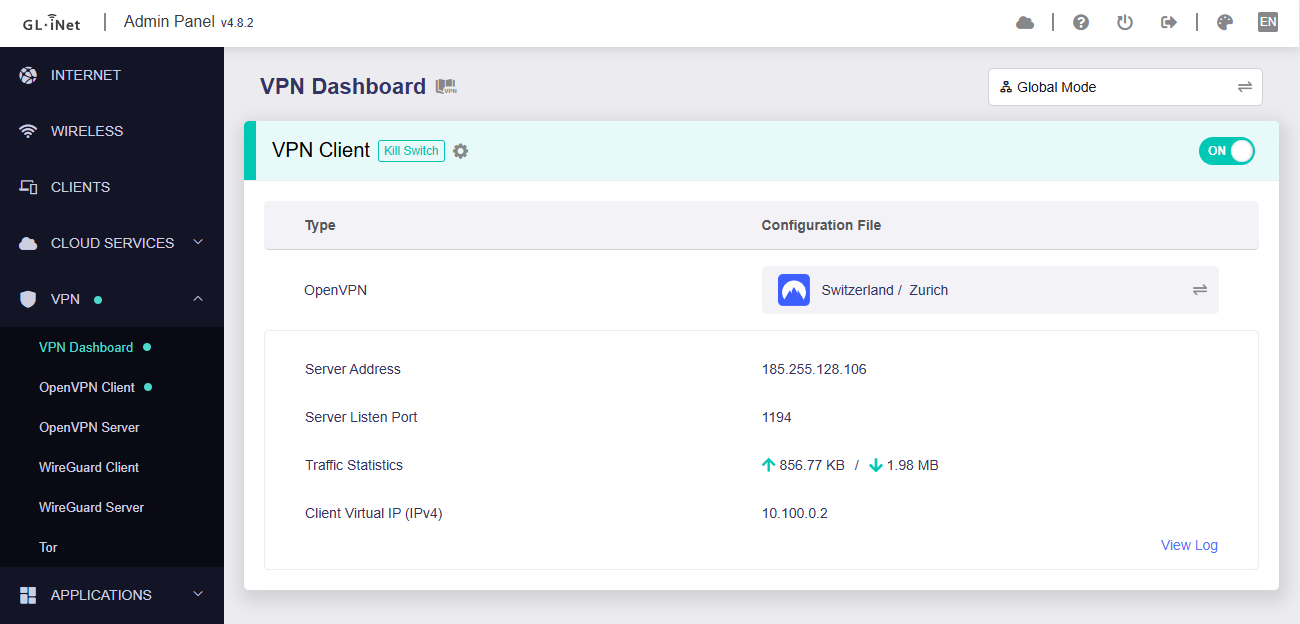
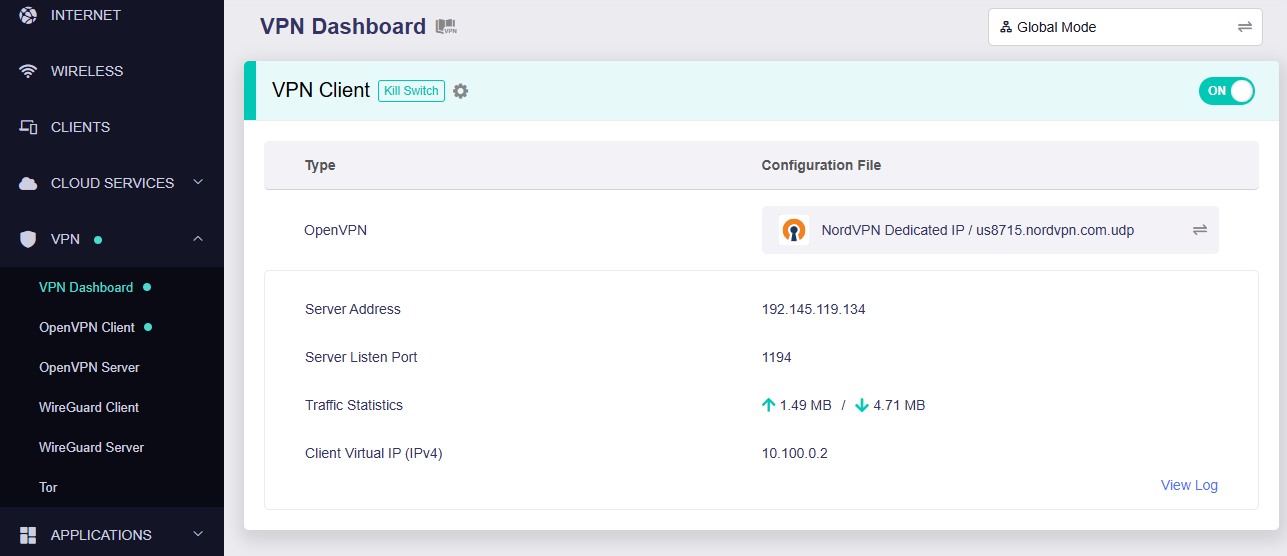
8. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

GLiNet NordLynx Connected

NordVPN OpenVPN Setup for GLiNet

1. Get your NordVPN manual service credentials for OpenVPN connections. Log in to your NordVPN account and select NordVPN from your list of Services.

NordVPN Service

2. At the bottom of the page in the Manual Setup section click Setup NordVPN manually then under the Configuration section go to Service credentials. Click Verify email to receive a code via email and enter the code to view and copy your credentials.

NordVPN Manual OpenVPN
NordVPN Service Credentials

3. Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

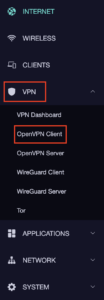
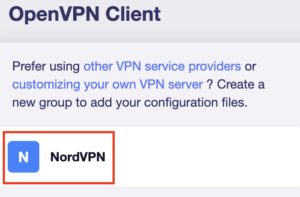
4. Navigate to the VPN tab and select OpenVPN Client.

GL.iNet VPN OpenVPN Client

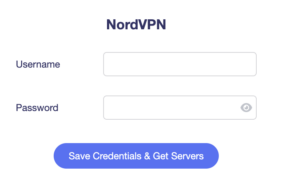
5. Select the NordVPN group, enter your manual credentials, then click Save Credentials & Get Servers.

GL.iNet NordVPN Group
GL.iNet NordVPN Login

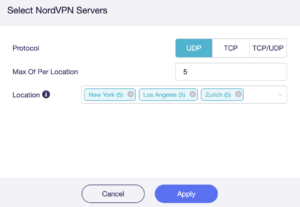
6. Choose UDP (recommended), select your preferred server locations, and click Apply.

GL.iNet NordVPN select servers

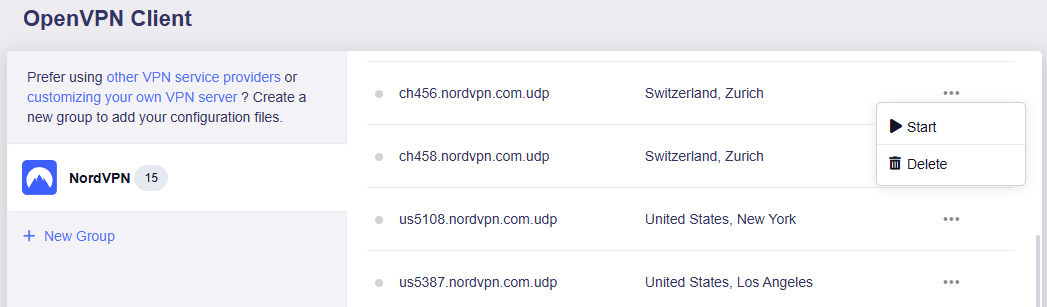
7. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

NordVPN GLiNet OpenVPN Start

8. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

GLiNet VPN Dashboard

NordVPN Dedicated IP Setup for GLiNet

1. Get your NordVPN manual service credentials for OpenVPN connections. Log in to your NordVPN account and select NordVPN from your list of Services.

NordVPN Service

2. At the bottom of the page in the Manual Setup section click Setup NordVPN manually then under the Configuration section go to Service credentials. Click Verify email to receive a code via email and enter the code to view and copy your credentials.

NordVPN Manual OpenVPN
NordVPN Service Credentials

3. Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

4. Navigate to the VPN tab and select OpenVPN Client.

GLiNet VPN Dashboard

5. Download your Dedicated IP configuration file from the NordVPN website.

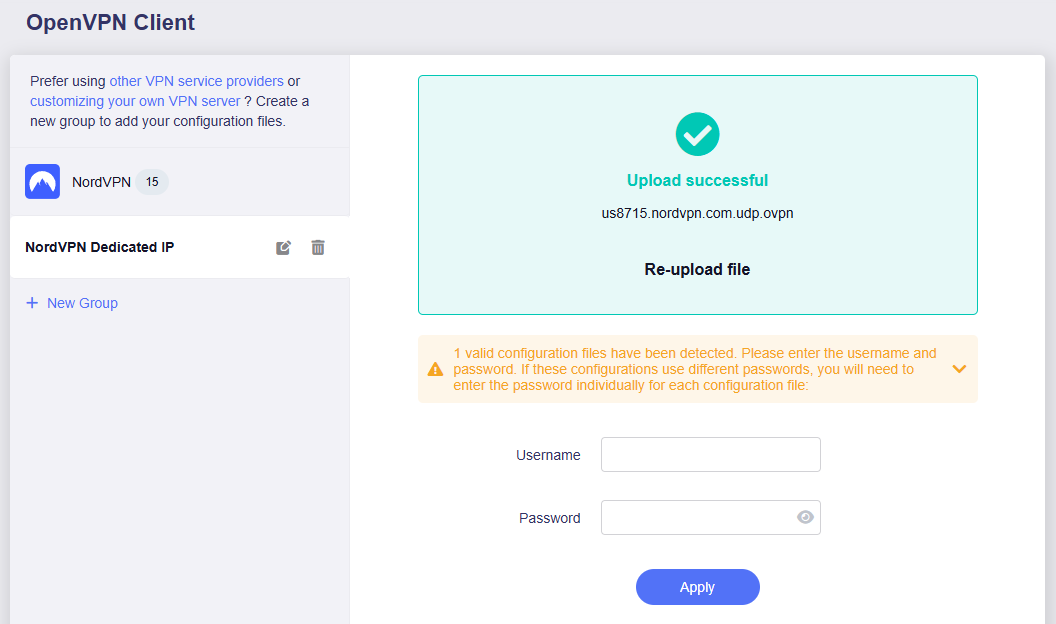
6. Click +New Group and name your NordVPN Dedicated IP connection, then upload the configuration file, enter your manual service credentials and click Apply.

GLiNet Dedicated IP Address Load

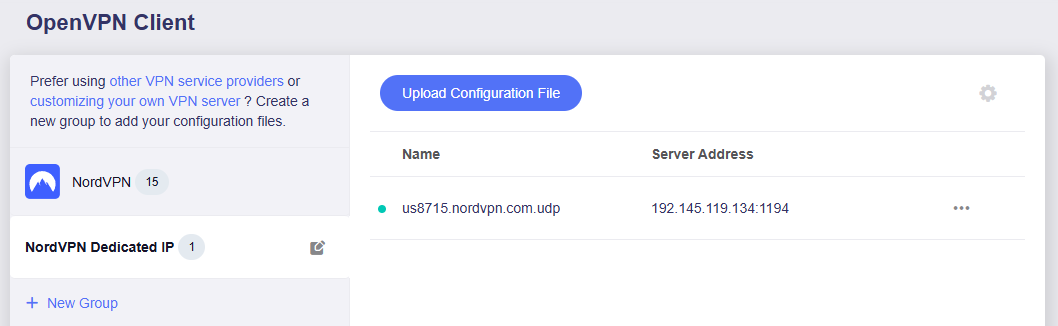
7. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

GLiNet Dedicated IP

8. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

GLiNet Dedicated IP Dashboard
  1. You should now see information appear in the Server Address, Server Listen Port, Traffic Statistics, and Client Virtual IP areas.
  2. Visit NordVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to NordVPN.

🚫📱Do not run NordVPN apps on devices connected to your NordVPN router. Using the app at the same time as the router VPN may cause conflicts and connection issues.

Still having issues?

Feel free to submit a ticket and we will get back to you as soon as possible.

My 5.0GHz network is not showing up

TeamFlashRouters · May 2, 2019 ·

Verify the device supports 5GHz

5.0GHz networks are not compatible with all devices so first make sure that you device’s wireless adapter supports 5GHz wireless frequencies.

If you are not sure, find out if your device support 5 GHz via Google search or by looking in the wireless hardware details in the device’s network settings. If you see Wireless a/b/g/n support then you have a compatible device. If you are missing the Wireless a then this means there is no 5 GHz support.

Enter the recommended wireless settings

Our team has tested the wireless functionality for each FlashRouter that we offer and shared our recommended wireless settings in our Wifi Setup area. Replicate the settings for your FlashRouter model found on that page.

Lower the wireless channel

Some devices do support 5.0GHz connections but not the higher channels that DD-WRT firmware offers.

Navigate to Wireless > Basic Settings

Lower the wireless channel setting for the 5.0GHz band that is not showing. Based on our tests the most broadly compatible channels are 36, 48 and 161.

CLICK APPLY SETTINGS

Refresh your device's network adapter

The easiest way to accomplish this is by rebooting your device as the settings to reset your adapter may vary on all types of internet connected devices.

Review wireless Status

Navigate to Status > Wireless

The readouts on this page can help tell if there are errors with the FlashRouter’s wireless. View our article on how to read the Wireless Status page for more information.

GL.iNet Access Router Settings and Firmware Upgrade

TeamFlashRouters · Apr 3, 2023 ·

Follow this guide to upgrade the firmware of your GL.iNet FlashRouter.

1. Connect your computer, phone, or tablet to the GL.iNet router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 9483C07E70A8 then your WiFi password is Wireless#9483C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to 192.168.8.1

GL.iNet router access

3. Enter openwrt as the admin password to access the GL.iNet firmware settings. Newer devices may have a different admin password set as openwrt1 or glopenwrt1

GL.iNet admin password enter

3. If a new firmware upgrade is available the router settings will either display a banner when you first access the router or a header. Click Install or the Upgrade arrow depending on which appears for you.

GL.iNet Firmware Upgrade Banner
GL.iNet Firmware Upgrade Header

4. Make sure the Keep Settings toggle is pushed to the right so your router does not get reset. Click the Install button to begin the firmware upgrade.

GL.iNet Install Firmware Upgrade

5. The firmware update should take about 2-3 minutes. You may need to reconnect your wireless devices after the network comes back up in your available networks.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

IPVanish Setup for Privacy Hero

TeamFlashRouters · Sep 23, 2025 ·

Privacy Hero supports IPVanish VPN through WireGuard (recommended) and OpenVPN. Both are configured in Privacy Hero using the Custom VPN provider option. You will need an active IPVanish VPN subscription and the configuration file for the protocol and server location you select.

Choose your method: WireGuard uses a generated .conf file and generally provides better performance. OpenVPN uses a downloaded .ovpn file plus your IPVanish VPN username and password.

Privacy Hero is cloud-managed. You can sign in and adjust VPN settings from a computer, phone, or tablet connected to any internet connection. You do not need to be on the Privacy Hero WiFi network to configure the router.

IPVanish Setup Guide

Jump to the instructions you need.

WireGuard File →Generate a WireGuard server configurationWireGuard Setup →Upload your .conf file to Privacy HeroOpenVPN File →Download an IPVanish .ovpn server fileOpenVPN Setup →Enter credentials and upload the configurationVerify Connection →Check your public VPN IP addressTroubleshooting →Fix connection errors and IP issues

Download an IPVanish WireGuard Configuration (Recommended)

Use the WireGuard configuration generator in your IPVanish account to create a server file for your router. A generated WireGuard file contains the connection keys and server details, so keep it private.

  1. Open the IPVanish account sign-in page and log in.
  2. Open WireGuard in the account navigation to access the WireGuard Configuration Generator.
  3. Select your preferred IPVanish server location and choose Generate to download the WireGuard configuration file. Save the downloaded .conf file to the device you are using for setup.

Important: Do not publicly share your WireGuard configuration file. To switch server locations later, generate and upload a new configuration.

Add IPVanish WireGuard to Privacy Hero

  1. Sign in to the Privacy Hero dashboard at app.privacyhero.com.
  2. Open the VPN section, select Change beside the provider, and choose Custom.
  3. Choose WireGuard and upload the IPVanish .conf file you just generated.
  4. Click Save to apply the settings. Wait for Privacy Hero to report Connected.
Privacy Hero Custom WireGuard configuration with WireGuard file upload

WireGuard authentication is contained in the generated configuration file; there is no separate OpenVPN username/password step in this method.


Download an IPVanish OpenVPN Configuration File

OpenVPN is a good alternative if WireGuard is unavailable or fails to connect on your network. It requires an IPVanish .ovpn configuration file and VPN login credentials.

  1. Open the IPVanish OpenVPN server configuration list.
  2. Download an .ovpn file for your preferred available server location. If IPVanish provides both UDP and TCP files, start with UDP and keep a TCP file as a fallback.
  3. Have your IPVanish account username and password available for the OpenVPN setup. Use the credentials accepted by your IPVanish VPN account; these are not Privacy Hero login credentials.

If the linked server directory has changed, check the latest manual OpenVPN configuration downloads offered by IPVanish before selecting a file.

Add IPVanish OpenVPN to Privacy Hero

  1. Sign in at app.privacyhero.com and open VPN.
  2. Select Change, choose Custom, and select OpenVPN.
  3. Upload the IPVanish .ovpn file you downloaded.
  4. Enter your IPVanish username and password in the Custom OpenVPN fields. Do not enter the Privacy Hero account login.
  5. Click Save and wait for the connection status to show Connected.
Privacy Hero Custom OpenVPN configuration showing server file upload and username and password fields

Tip: If OpenVPN UDP times out or cannot connect, try an available IPVanish OpenVPN TCP configuration or another server location.


Verify Your IPVanish VPN Connection

After Privacy Hero displays Connected, verify that a device on the router is actually using IPVanish.

  1. Connect the device you want to test to the Privacy Hero WiFi or LAN network.
  2. Temporarily disconnect any IPVanish app, other VPN app, or device-level VPN connection on that device so you test the router VPN alone.
  3. Open a new private/incognito browser window and visit IPVanish What Is My IP Address.
  4. Confirm that your public IP address and approximate location correspond to the VPN server you selected.

Note: Privacy Hero settings can be managed remotely, but the device used for this IP test must be on the Privacy Hero network.

Streaming Relocation and Your VPN Location

If Streaming Relocation is enabled for a supported streaming service, that service may use the configured Streaming Relocation location instead of the IPVanish server location. See Privacy Hero Streaming Relocation.


IPVanish Not Connecting?

If Privacy Hero remains on Connecting, displays Failed, or reports a timeout, check the following:

  1. Make sure your IPVanish subscription is active and that Custom is selected as the VPN provider in Privacy Hero.
  2. For WireGuard, generate a fresh configuration from your IPVanish account and upload that .conf file again.
  3. For OpenVPN, confirm your IPVanish username/password and upload a fresh .ovpn file for a different server.
  4. Try a different server location. With OpenVPN, also try switching between available UDP and TCP files.
  5. Temporarily disable the Privacy Hero VPN connection and test normal internet access. If enabled, temporarily turn off the VPN Kill Switch for this test, then restore your preferred Kill Switch setting.
  6. Check whether a device-level VPN app, private DNS, proxy, or security software is interfering with the router VPN connection.

VPN Disconnected and No Internet?

The VPN Kill Switch can intentionally block internet access when the VPN disconnects. Review Privacy Hero VPN Kill Switch Setup.

VPN Connected but One Device Shows the Wrong IP?

If only one device shows an unexpected IP address, look for another VPN app, iCloud Private Relay, Private DNS, browser proxy/DNS settings, or security software on that device. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

IVPN Manual OpenVPN Setup

TeamFlashRouters · Apr 16, 2019 ·

Preparing for Manual IVPN Setup

Verify your IVPN login information

If you are not already an IVPN user Sign Up Now.

Log in to your account on the IVPN website.

FlashRouter Privacy App - IVPN Login

Locate and Copy the Username displayed on the VPN Accounts page.

FlashRouters DD-WRT Privacy APP IVPN OpenVPN Specific Username and Password

IVPN Server Addresses

View a full list of IVPN servers.

United States

Atlanta:
us-ga.gw.ivpn.net

Dallas:
us-tx.gw.ivpn.net

Los Angeles
:
us-ca.gw.ivpn.net

Miami
:
us-fl.gw.ivpn.net

New Jersey
:
us-nj.gw.ivpn.net

Salt Lake City
:
us-ut.gw.ivpn.net

DD-WRT Router Setup for IVPN

Navigate to Services > VPN

Enter IVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PureVPN connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

443 for TCP
2049 for UDP

Tunnel Device

TUN

Tunnel Protocol

TCP or UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Enable

Username

Enter the Username you noted from the Home page above.
eg. ivpn1234567

Password

Enter the Password you successfully logged in to your IVPN account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
ac470c93ff9f5602a8aab37dee84a528
14d10f20490ad23c47d5d82120c1bf85
9e93d0696b455d4a1b8d55d40c2685c4
1ca1d0aef29a3efd27274c4ef09020a3
978fe45784b335da6df2d12db97bbb83
8416515f2a96f04715fd28949c6fe296
a925cfada3f8b8928ed7fc963c156327
2f5cf46e5e1d9c845d7703ca881497b7
e6564a9d1dea9358adffd435295479f4
7d5298fabf5359613ff5992cb57ff081
a04dfb81a26513a6b44a9b5490ad265f
8a02384832a59cc3e075ad545461060b
7bcab49bac815163cb80983dd51d5b1f
d76170ffd904d8291071e96efc3fb777
856c717b148d08a510f5687b8a8285dc
ffe737b98916dd15ef6235dee4266d3b
-----END OpenVPN Static key V1-----

Additional Config

tls-client
tls-cipher TLS-DHE-RSA-WITH-AES-256-CBC-SHA
resolv-retry infinite
keepalive 10 60
nobind
persist-key
persist-tun
persist-remote-ip
verb 3

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIGoDCCBIigAwIBAgIJAJjvUclXmxtnMA0GCSqGSIb3DQEBCwUAMIGMMQswCQYD
VQQGEwJDSDEPMA0GA1UECAwGWnVyaWNoMQ8wDQYDVQQHDAZadXJpY2gxETAPBgNV
BAoMCElWUE4ubmV0MQ0wCwYDVQQLDARJVlBOMRgwFgYDVQQDDA9JVlBOIFJvb3Qg
Q0EgdjIxHzAdBgkqhkiG9w0BCQEWEHN1cHBvcnRAaXZwbi5uZXQwHhcNMjAwMjI2
MTA1MjI5WhcNNDAwMjIxMTA1MjI5WjCBjDELMAkGA1UEBhMCQ0gxDzANBgNVBAgM
Blp1cmljaDEPMA0GA1UEBwwGWnVyaWNoMREwDwYDVQQKDAhJVlBOLm5ldDENMAsG
A1UECwwESVZQTjEYMBYGA1UEAwwPSVZQTiBSb290IENBIHYyMR8wHQYJKoZIhvcN
AQkBFhBzdXBwb3J0QGl2cG4ubmV0MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIIC
CgKCAgEAxHVeaQN3nYCLnGoEg6cY44AExbQ3W6XGKYwC9vI+HJbb1o0tAv56ryvc
6eS6BdG5q9M8fHaHEE/jw9rtznioiXPwIEmqMqFPA9k1oRIQTGX73m+zHGtRpt9P
4tGYhkvbqnN0OGI0H+j9R6cwKi7KpWIoTVibtyI7uuwgzC2nvDzVkLi63uvnCKRX
cGy3VWC06uWFbqI9+QDrHHgdJA1F0wRfg0Iac7TE75yXItBMvNLbdZpge9SmplYW
FQ2rVPG+n75KepJ+KW7PYfTP4Mh3R8A7h3/WRm03o3spf2aYw71t44voZ6agvslv
wqGyczDytsLUny0U2zR7/mfEAyVbL8jqcWr2Df0m3TA0WxwdWvA51/RflVk9G96L
ncUkoxuBT56QSMtdjbMSqRgLfz1iPsglQEaCzUSqHfQExvONhXtNgy+Pr2+wGrEu
SlLMee7aUEMTFEX/vHPZanCrUVYf5Vs8vDOirZjQSHJfgZfwj3nL5VLtIq6ekDhS
AdrqCTILP3V2HbgdZGWPVQxl4YmQPKo0IJpse5Kb6TF2o0i90KhORcKg7qZA40sE
bYLEwqTM7VBs1FahTXsOPAoMa7xZWV1TnigF5pdVS1l51dy5S8L4ErHFEnAp242B
DuTClSLVnWDdofW0EZ0OkK7V9zKyVl75dlBgxMIS0y5MsK7IWicCAwEAAaOCAQEw
gf4wHQYDVR0OBBYEFHUDcMOMo35yg2A/v0uYfkDE11CXMIHBBgNVHSMEgbkwgbaA
FHUDcMOMo35yg2A/v0uYfkDE11CXoYGSpIGPMIGMMQswCQYDVQQGEwJDSDEPMA0G
A1UECAwGWnVyaWNoMQ8wDQYDVQQHDAZadXJpY2gxETAPBgNVBAoMCElWUE4ubmV0
MQ0wCwYDVQQLDARJVlBOMRgwFgYDVQQDDA9JVlBOIFJvb3QgQ0EgdjIxHzAdBgkq
hkiG9w0BCQEWEHN1cHBvcnRAaXZwbi5uZXSCCQCY71HJV5sbZzAMBgNVHRMEBTAD
AQH/MAsGA1UdDwQEAwIBBjANBgkqhkiG9w0BAQsFAAOCAgEAABAjRMJy+mXFLezA
Z8iUgxOjNtSqkCv1aU78K1XkYUzbwNNrSIVGKfP9cqOEiComXY6nniws7QEV2IWi
lcdPKm0x57recrr9TExGGOTVGB/WdmsFfn0g/HgmxNvXypzG3qulBk4qQTymICds
l9vIPb1l9FSjKw1KgUVuCPaYq7xiXbZ/kZdZX49xeKtoDBrXKKhXVYoWus/S+k2I
S8iCxvcp599y7LQJg5DOGlbaxFhsW4R+kfGOaegyhPvpaznguv02i7NLd99XqJhp
v2jTUF5F3T23Z4KkL/wTo4zxz09DKOlELrE4ai++ilCt/mXWECXNOSNXzgszpe6W
As0h9R++sH+AzJyhBfIGgPUTxHHHvxBVLj3k6VCgF7mRP2Y+rTWa6d8AGI2+Raey
V9DVVH9UeSoU0Hv2JHiZL6dRERnyg8dyzKeTCke8poLIjXF+gyvI+22/xsL8jcNH
i9Kji3Vpc3i0Mxzx3gu2N+PL71CwJilgqBgxj0firr3k8sFcWVSGos6RJ3IvFvTh
xYx0p255WrWM01fR9TktPYEfjDT9qpIJ8OrGlNOhWhYj+a45qibXDpaDdb/uBEmf
2sSXNifjSeUyqu6cKfZvMqB7pS3l/AhuAOTT80E4sXLEoDxkFD4C78swZ8wyWRKw
sWGIGABGAHwXEAoDiZ/jjFrEZT0=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful IVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit WhatIsMyIPAddress to verify your new IP address, virtual location, and status as Protected at the top of the page.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to IVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the IVPN server

  1. Copy the new IVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Cudy Access Router Settings

TeamFlashRouters · Feb 26, 2024 ·

Follow this guide to access the router settings of your Cudy FlashRouter.

1. Connect your computer, phone, or tablet to the Cudy router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to 192.168.10.1

Cudy local IP access

3. Enter openwrt1 or openwrt as the admin password to access the Cudy firmware settings.

Cudy router access

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ExpressVPN Manual OpenVPN Setup

admin · Feb 19, 2019 ·

Preparing for Manual ExpressVPN Setup

Obtain your ExpressVPN OpenVPN Information

If you are not already an ExpressVPN user Sign Up Now.

1. Log in to your account on the ExpressVPN website.

ExpressVPN login page

2. Successfully log in with your account information. Select More.

3. Select Manual Configuration and copy the Username and Password that are displayed on the right hand side of the screen.

ExpressVPN Manual Configuration
ExpressVPN username and password

ExpressVPN Server Addresses

Americas

usa-atlanta-ca-version-2.expressnetw.com
usa-boston-ca-version-2.expressnetw.com
usa-chicago-ca-version-2.expressnetw.com
usa-dallas-ca-version-2.expressnetw.com
usa-dallas-2-ca-version-2.expressnetw.com
usa-denver-ca-version-2.expressnetw.com
usa-kansascity-ca-version-2.expressnetw.com
usa-losangeles-ca-version-2.expressnetw.com
usa-losangeles-1-ca-version-2.expressnetw.com
usa-losangeles-2-ca-version-2.expressnetw.com
usa-losangeles-3-ca-version-2.expressnetw.com
usa-los-angeles-4-ca-version-2.expressnetw.com
usa-miami-ca-version-2.expressnetw.com
usa-miami-2-ca-version-2.expressnetw.com
usa-minneapolis-ca-version-2.expressnetw.com
usa-newjersey-1-ca-version-2.expressnetw.com
usa-newjersey-3-ca-version-2.expressnetw.com
usa-newyork-ca-version-2.expressnetw.com
us-new-york-2-ca-version-2.expressnetw.com
usa-phoenix-ca-version-2.expressnetw.com
usa-saltlakecity-ca-version-2.expressnetw.com
usa-sanfrancisco-ca-version-2.expressnetw.com
usa-sanjose-ca-version-2.expressnetw.com
usa-seattle-ca-version-2.expressnetw.com
usa-tampa-1-ca-version-2.expressnetw.com
usa-virginia-ca-version-2.expressnetw.com
usa-washingtondc-ca-version-2.expressnetw.com
usa-washingtondc-2-ca-version-2.expressnetw.com
canada-montreal-ca-version-2.expressnetw.com
canada-toronto-ca-version-2.expressnetw.com
canada-toronto-2-ca-version-2.expressnetw.com
canada-vancouver-ca-version-2.expressnetw.com
mexico-ca-version-2.expressnetw.com
argentina-ca-version-2.expressnetw.com
brazil-ca-version-2.expressnetw.com
brazil-2-ca-version-2.expressnetw.com
chile-ca-version-2.expressnetw.com
colombia-ca-version-2.expressnetw.com
costarica-ca-version-2.expressnetw.com
ecuador-ca-version-2.expressnetw.com
guatemala-ca-version-2.expressnetw.com
panama-ca-version-2.expressnetw.com
peru-ca-version-2.expressnetw.com
uruguay-ca-version-2.expressnetw.com
venezuela-ca-version-2.expressnetw.com

Europe

uk-berkshire-ca-version-2.expressnetw.com
uk-berkshire-2-ca-version-2.expressnetw.com
uk-docklands-ca-version-2.expressnetw.com
uk-east-london-ca-version-2.expressnetw.com
uk-kent-ca-version-2.expressnetw.com
uk-london-ca-version-2.expressnetw.com
france-paris-1-ca-version-2.expressnetw.com
france-paris-2-ca-version-2.expressnetw.com
france-strasbourg-ca-version-2.expressnetw.com
germany-darmstadt-ca-version-2.expressnetw.com
germany-frankfurt-1-ca-version-2.expressnetw.com
germany-frankfurt-2-ca-version-2.expressnetw.com
germany-nuremberg-ca-version-2.expressnetw.com
italy-cosenza-ca-version-2.expressnetw.com
italy-milan-ca-version-2.expressnetw.com
netherlands-amsterdam-ca-version-2.expressnetw.com
netherlands-rotterdam-ca-version-2.expressnetw.com
netherlands-thehague-ca-version-2.expressnetw.com
spain-barcelona-ca-version-2.expressnetw.com
spain-ca-version-2.expressnetw.com
sweden-ca-version-2.expressnetw.com
sweden-2-ca-version-2.expressnetw.com
switzerland-ca-version-2.expressnetw.com
switzerland-2-ca-version-2.expressnetw.com
albania-ca-version-2.expressnetw.com
andorra-ca-version-2.expressnetw.com
armenia-ca-version-2.expressnetw.com
austria-ca-version-2.expressnetw.com
azerbaijan-ca-version-2.expressnetw.com
belarus-ca-version-2.expressnetw.com
belgium-ca-version-2.expressnetw.com
bosniaandherzegovina-ca-version-2.expressnetw.com
bulgaria-ca-version-2.expressnetw.com
croatia-ca-version-2.expressnetw.com
cyprus-ca-version-2.expressnetw.com
czechrepublic-ca-version-2.expressnetw.com
denmark-ca-version-2.expressnetw.com
estonia-ca-version-2.expressnetw.com
finland-ca-version-2.expressnetw.com
georgia-ca-version-2.expressnetw.com
greece-ca-version-2.expressnetw.com
hungary-ca-version-2.expressnetw.com
iceland-ca-version-2.expressnetw.com
ireland-ca-version-2.expressnetw.com
isleofman-ca-version-2.expressnetw.com
jersey-ca-version-2.expressnetw.com
latvia-ca-version-2.expressnetw.com
liechtenstein-ca-version-2.expressnetw.com
lithuania-ca-version-2.expressnetw.com
luxembourg-ca-version-2.expressnetw.com
macedonia-ca-version-2.expressnetw.com
malta-ca-version-2.expressnetw.com
moldova-ca-version-2.expressnetw.com
monaco-ca-version-2.expressnetw.com
montenegro-ca-version-2.expressnetw.com
norway-ca-version-2.expressnetw.com
poland-ca-version-2.expressnetw.com
portugal-ca-version-2.expressnetw.com
romania-ca-version-2.expressnetw.com
serbia-ca-version-2.expressnetw.com
slovakia-ca-version-2.expressnetw.com
slovenia-ca-version-2.expressnetw.com
ukraine-ca-version-2.expressnetw.com

Asia Pacific

australia-brisbane-ca-version-2.expressnetw.com
australia-melbourne-ca-version-2.expressnetw.com
australia-perth-ca-version-2.expressnetw.com
australia-sydney-ca-version-2.expressnetw.com
australia-sydney-2-ca-version-2.expressnetw.com
australia-sydney-3-ca-version-2.expressnetw.com
hongkong-2-ca-version-2.expressnetw.com
hongkong4-ca-version-2.expressnetw.com
hongkong-1-ca-version-2.expressnetw.com
japan-tokyo-1-ca-version-2.expressnetw.com
japan-tokyo-2-ca-version-2.expressnetw.com
india-chennai-ca-version-2.expressnetw.com
india-mumbai-1-ca-version-2.expressnetw.com
singapore-cbd-ca-version-2.expressnetw.com
singapore-jurong-ca-version-2.expressnetw.com
southkorea-ca-version-2.expressnetw.com
southkorea2-ca-version-2.expressnetw.com
bangladesh-ca-version-2.expressnetw.com
bhutan-ca-version-2.expressnetw.com
brunei-ca-version-2.expressnetw.com
cambodia-ca-version-2.expressnetw.com
indonesia-ca-version-2.expressnetw.com
kazakhstan-ca-version-2.expressnetw.com
kyrgyzstan-ca-version-2.expressnetw.com
laos-ca-version-2.expressnetw.com
macau-ca-version-2.expressnetw.com
malaysia-ca-version-2.expressnetw.com
mongolia-ca-version-2.expressnetw.com
myanmar-ca-version-2.expressnetw.com
nepal-ca-version-2.expressnetw.com
newzealand-ca-version-2.expressnetw.com
pakistan-ca-version-2.expressnetw.com
ph-via-sing-ca-version-2.expressnetw.com
srilanka-ca-version-2.expressnetw.com
taiwan-3-ca-version-2.expressnetw.com
thailand-ca-version-2.expressnetw.com
vietnam-ca-version-2.expressnetw.com

Middle East and Africa

algeria-ca-version-2.expressnetw.com
israel-ca-version-2.expressnetw.com
kenya-ca-version-2.expressnetw.com
southafrica-ca-version-2.expressnetw.com

DD-WRT Router Setup for ExpressVPN

Navigate to Services > VPN

Enter ExpressVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change ExpressVPN connection locations, THE ONLY SETTING YOU NEED TO CHANGE IS THE EXPRESSVPN SERVER ADDRESS.*

Port

1195

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

User Pass Authentication

Enable

Username

Enter the Username you found in the Manual Config section.

Password

Enter the Password you found in the Manual Config section.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
48d9999bd71095b10649c7cb471c1051
b1afdece597cea06909b99303a18c674
01597b12c04a787e98cdb619ee960d90
a0165529dc650f3a5c6fbe77c91c137d
cf55d863fcbe314df5f0b45dbe974d9b
de33ef5b4803c3985531c6c23ca6906d
6cd028efc8585d1b9e71003566bd7891
b9cc9212bcba510109922eed87f5c8e6
6d8e59cbd82575261f02777372b2cd4c
a5214c4a6513ff26dd568f574fd40d6c
d450fc788160ff68434ce2bf6afb00e7
10a3198538f14c4d45d84ab42637872e
778a6b35a124e700920879f1d003ba93
dccdb953cdf32bea03f365760b0ed800
2098d4ce20d045b45a83a8432cc73767
7aed27125592a7148d25c87fdbe0a3f6
-----END OpenVPN Static key V1-----

Additional Config

persist-key
persist-tun
fragment 1300
mssfix 1450
keysize 256

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIF+DCCA+CgAwIBAgIBATANBgkqhkiG9w0BAQ0FADCBhDELMAkGA1UEBhMCVkcx
DDAKBgNVBAgMA0JWSTETMBEGA1UECgwKRXhwcmVzc1ZQTjETMBEGA1UECwwKRXhw
cmVzc1ZQTjEWMBQGA1UEAwwNRXhwcmVzc1ZQTiBDQTElMCMGCSqGSIb3DQEJARYW
c3VwcG9ydEBleHByZXNzdnBuLmNvbTAeFw0xNTEwMjEwMDAwMDBaFw0yNjA0MDEy
MTEyMDBaMIGEMQswCQYDVQQGEwJWRzEMMAoGA1UECAwDQlZJMRMwEQYDVQQKDApF
eHByZXNzVlBOMRMwEQYDVQQLDApFeHByZXNzVlBOMRYwFAYDVQQDDA1FeHByZXNz
VlBOIENBMSUwIwYJKoZIhvcNAQkBFhZzdXBwb3J0QGV4cHJlc3N2cG4uY29tMIIC
IjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAxzXvHZ25OsESKRMQFINHJNqE
9kVRLWJS50oVB2jxobudPhCsWvJSApvar8CB2RrqkVMhXu2HT3FBtDL91INg070q
AyjjRpzEbDPWqQ1+G0tk0sjiJt2mXPJK2IlNFnhe6rTs09Pkpcp8qRhfZay/dIlm
agohQAr4JvYL1Ajg9A3sLb8JkY03H6GhOF8EKYTqhrEppCcg4sQKQhNSytRoQAm8
Ta+tnTYIedwWpqjUXP9YXFOvljPaixfYug24eAkpTjeuWTcELSyfnuiBeK+z9+5O
YunhqFt2QZMq33kLFZGMN2gHRCzngxxphurypsPRo7jiFgQI1yLt8uZsEZ+otGEK
91jjKfOC+g9TBy2RUtxk1neWcQ6syXDuc3rBNrGA8iM0ZoEqQ1BC8xWr3NYlSjqN
+1mgpTAX3/Dxze4GzHd7AmYaYJV8xnKBVNphlMlg1giCAu5QXjMxPbfCgZiEFq/u
q0SOKQJeT3AI/uVPSvwCMWByjyMbDpKKAK8Hy3UT5m4bCNu8J7bxj+vdnq0A2HPw
tF0FwBl/TIM3zNsyFrZZ0j6jLRT50mFsgDBKcD4L/J5rjdCsKPu5rodhxe38rCx2
GknP1Zkov4yoVCcR48+CQwg3oBkq0/EflvWUvcYApzs9SomUM/g+8Q/V0WOfJmFW
uxN9YntZlnzHRSRjrvMCAwEAAaNzMHEwHQYDVR0OBBYEFIzmQGj8xS+0LLklwqHD
45VVOZRJMB8GA1UdIwQYMBaAFIzmQGj8xS+0LLklwqHD45VVOZRJMA8GA1UdEwEB
/wQFMAMBAf8wCwYDVR0PBAQDAgEGMBEGCWCGSAGG+EIBAQQEAwIBFjANBgkqhkiG
9w0BAQ0FAAOCAgEAbHfuMKtojm1NgX7qSU2Rm2B5L8G0FuFP0L40dj8O5WHt45j2
z8coMK90vrUnQEZNQmRzot7v3XjVzVlxBWYSsCEApTsSDNi/4BNFP8H/BUUtJuy2
GFTO4wDVJnqNkZOHBmyVD75s1Y+W8a+zB4jkMeDEhOHZdwQ0l1fJDDgXal5f1UT5
F5WH6/RwHmWTwX4GxuCiIVtx70CjkXqhM8yZtTp1UtHLRNYcNSIes0vrAPHPgoA5
z9B8UvsOjuP+mfcjzi0LGGrY+2pJu0BKO2dRnarIZZABETIisI3FokoTszx5jpRP
yxyUTuRDKWHrvi0PPtOmC8nFahfugWFUi6uBsqCaSeuex+ahnTPCq0b1l0Ozpg0Y
eE8CW1TL9Y92b01up2c+PP6wZOIm3JyTH+L5smDFbh80V42dKyGNdPXMg5IcJhj3
YfAy4k8h/qbWY57KFcIzKx40bFsoI7PeydbGtT/dIoFLSZRLW5bleXNgG9mXZp27
0UeEC6CpATCS6uVl8LVT1I02uulHUpFaRmTEOrmMxsXGt6UAwYTY55K/B8uuID34
1xKbeC0kzhuN2gsL5UJaocBHyWK/AqwbeBttdhOCLwoaj7+nSViPxICObKrg3qav
GNCvtwy/fEegK9X/wlp2e2CFlIhFbadeXOBr9Fn8ypYPP17mTqe98OJYM04=
-----END CERTIFICATE-----

Public Client Cert

-----BEGIN CERTIFICATE-----
MIIDTjCCAregAwIBAgIDKzZvMA0GCSqGSIb3DQEBCwUAMIGFMQswCQYDVQQGEwJV
UzELMAkGA1UECBMCQ0ExFTATBgNVBAcTDFNhbkZyYW5jaXNjbzEVMBMGA1UEChMM
Rm9ydC1GdW5zdG9uMRgwFgYDVQQDEw9Gb3J0LUZ1bnN0b24gQ0ExITAfBgkqhkiG
9w0BCQEWEm1lQG15aG9zdC5teWRvbWFpbjAgFw0xNjExMDMwMzA2MThaGA8yMDY2
MTEwMzAzMDYxOFowgYoxCzAJBgNVBAYTAlZHMQwwCgYDVQQIDANCVkkxEzARBgNV
BAoMCkV4cHJlc3NWUE4xEzARBgNVBAsMCkV4cHJlc3NWUE4xHDAaBgNVBAMME2V4
cHJlc3N2cG5fY3VzdG9tZXIxJTAjBgkqhkiG9w0BCQEWFnN1cHBvcnRAZXhwcmVz
c3Zwbi5jb20wggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCrOYt/KOi2
uMDGev3pXg8j1SO4J/4EVWDF7vJcKr2jrZlqD/zuAFx2W1YWvwumPO6PKH4PU962
1aNdiumaUkv/RplCfznnnxqobhJuTE2oA+rS1bOq+9OhHwF9jgNXNVk+XX4d0toS
T5uGE6Z3OdmPBur8o5AlCf78PDSAwpFOw5HrgLqOEU4hTweC1/czX2VsvsHv22HR
I6JMZgP8gGQii/p9iukqfaJvGdPciL5p1QRBUQIi8P8pNvEp1pVIpxYj7/LOUqb2
DxFvgmp2v1IQ0Yu88SWsFk84+xAYHzfkLyS31Sqj5uLRBnJqx3fIlOihQ50GI72f
wPMwo+OippvVAgMBAAGjPzA9MAwGA1UdEwEB/wQCMAAwDgYDVR0PAQH/BAQDAgSw
MB0GA1UdDgQWBBSkBM1TCX9kBgFsv2RmOzudMXa9njANBgkqhkiG9w0BAQsFAAOB
gQA+2e4b+33zFmA+1ZQ46kWkfiB+fEeDyMwMLeYYyDS2d8mZhNZKdOw7dy4Ifz9V
qzp4aKuQ6j61c6k1UaQQL0tskqWVzslSFvs9NZyUAJLLdGUc5TT2MiLwiXQwd4Uv
H6bGeePdhvB4+ZbW7VMD7TE8hZhjhAL4F6yAP1EQvg3LDA==
-----END CERTIFICATE-----

Private Client Key

-----BEGIN RSA PRIVATE KEY-----
MIIEpAIBAAKCAQEAqzmLfyjotrjAxnr96V4PI9UjuCf+BFVgxe7yXCq9o62Zag/8
7gBcdltWFr8Lpjzujyh+D1PettWjXYrpmlJL/0aZQn85558aqG4SbkxNqAPq0tWz
qvvToR8BfY4DVzVZPl1+HdLaEk+bhhOmdznZjwbq/KOQJQn+/Dw0gMKRTsOR64C6
jhFOIU8Hgtf3M19lbL7B79th0SOiTGYD/IBkIov6fYrpKn2ibxnT3Ii+adUEQVEC
IvD/KTbxKdaVSKcWI+/yzlKm9g8Rb4Jqdr9SENGLvPElrBZPOPsQGB835C8kt9Uq
o+bi0QZyasd3yJTooUOdBiO9n8DzMKPjoqab1QIDAQABAoIBAHgsekC0SKi+AOcN
OZqJ3pxqophE0V7fQX2KWGXhxZnUZMFxGTc936deMYzjZ1y0lUa6x8cgOUcfqHol
3hDmw9oWBckLHGv5Wi9umdb6DOLoZO62+FQATSdfaJ9jheq2Ub2YxsRN0apaXzB6
KDKz0oM0+sZ4Udn9Kw6DfuIELRIWwEx4w0v3gKW7YLC4Jkc4AwLkPK03xEA/qImf
kCmaMPLhrgVQt+IFfP8bXzL7CCC04rNU/IS8pyjex+iUolnQZlbXntF7Bm4V2mz0
827ZVqrgAb/hEQRlsTW3rRkVh+rrdoUE7BCZRTFmRCbLoShjN6XuSf4sAus8ch4U
EN12gN0CgYEA4o/tSvij1iPaXLmt4KOEuxqmSGB8MLKhFde8lBbNdrDgxiIH9bH7
khKx15XRTX0qLDbs8b2/UJygZG0Aa1kIBqZTXTgeMAuxPRTesALJPdqQ/ROnbJcd
FkI7gllrAG8VB0fH4wTRsRd0vWEB6YlCdE107u6LEsLAHxOj9Q5819cCgYEAwXjx
9RkQ2qITBx5Ewib8YsltA0n3cmRomPicLlsnKV5DfvyCLpFIsZ1h3f9dUpfxRLwz
p8wcoLiq9cCoOGdu1udw/yBTqmhaXWhUK/g77f9Ze2ZB1OEhuyKLYJ1vW/h/Z/a1
aPCMxZqsDTPCePsuO8Cez5gqs8LjM3W7EyzRxDMCgYEAvhHrDFt975fSiLoJgo0M
PIAGAnBXn+8sLwv3m/FpW+rWF8LTFK/Fku12H5wDpNOdvswxijkauIE+GiJMGMLv
dcyx4WHECaC1h73reJRNykOEIZ0Md5BrCZJ1JEzp9Mo8RQhWTEFtvfkkqgApP4g0
pSeaMx0StaGG1kt+4IbP+68CgYBrZdQKlquAck/Vt7u7eyDHRcE5/ilaWtqlb/xi
zz7h++3D5C/v4b5UumTFcyg+3RGVclPKZcfOgDSGzzeSd/hTW46iUTOgeOUQzQVM
kzPRXdoyYgVRQtgSpY5xR3O1vjAbahwx8LZ0SvQPMBhYSDbV/Isr+fBacWjl/Aip
EEwxeQKBgQDdrAEnVlOFoCLw4sUjsPoxkLjhTAgI7CYk5NNxX67Rnj0tp+Y49+sG
Uhl5sCGfMKkLShiON5P2oxZa+B0aPtQjsdnsFPa1uaZkK4c++SS6AetzYRpVDLmL
p7/1CulE0z3O0sBekpwiuaqLJ9ZccC81g4+2j8j6c50rIAct3hxIxw==
-----END RSA PRIVATE KEY-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful ExpressVPN connection

Navigate to Status > OpenVPN.

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit ExpressVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ExpressVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the ExpressVPN server

  1. Copy the new ExpressVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

TP-Link Access Router Settings

TeamFlashRouters · Apr 11, 2024 ·

Follow this guide to access the router settings of your TP-Link FlashRouter.

1. Connect your computer, phone, or tablet to the TP-Link router via wireless (FlashRouter24 / FlashRouter50) or via ethernet cable to one of the LAN ports on the router.

The FlashRouter WiFi password is printed on the sheet that came with the router and is set to Wireless#[First 5 characters of your router MAC]. The router MAC can be found on the bottom of your router if you cannot locate the sheet. For e.g. if your MAC is 1459C07E70A8 then your WiFi password is Wireless#1459C

Be sure to capitalize the W.

2. Once connected via wireless or ethernet on your device open your browser and go to tplinkwifi.net

TP-Link URL Access

3. Enter tp-link as the admin password to access the TP-Link firmware settings.

TP-Link admin password

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero Creating User Profiles and Adding Devices to Profiles

TeamFlashRouters · Apr 3, 2023 ·

Your Privacy Hero router uses Cloud Based router management which means you can access the router settings from anywhere on any device that has an internet connection. You can follow these steps while connected to your phone, other Wi-Fi network, or the Privacy Hero network.

The Privacy Hero router allows for User Profile creation. Doing so allows you to group different user’s devices together to customize the following rules:

  • Internet access scheduler (Bedtime settings)
  • Internet Safe Search
  • Youtube Safe Search
  • Block Adult Content

This makes the Privacy Hero a great router option for families and internet addicts.

1. From any device that has a browser such as a computer, smartphone, or tablet visit app.privacyhero.com

App.PrivacyHero.com

2. Enter your Privacy Hero account email and password. Click Login.

Privacy Hero Access Settings

If you have not created your Privacy Hero account yet please follow these instructions.

3. Click the Profiles symbol.

Privacy Hero Profiles

4. Click Create New Profile.

Privacy Hero Create New Profile

5. Set the Profile Name, select the Profile Icon, and click Save.

Privacy Hero Set Profile Name

6. Click the name of the User Profile.

Privacy Hero Select Profile

7. Select Devices.

Privacy Hero Select Devices

8. Select Manage Devices.

Privacy Hero Select Manage Devices

9. If you have not already connected your devices to the Privacy Hero network via wireless or ethernet you can do so now. Refresh the page after connecting a new device and it will appear in the list where you can select Move to “Profile Name” to move the device to the appropriate profile. By default new devices are in the Shared profile.

Privacy Hero Move to User Profile

If your devices were already connected to the Privacy Hero network and you are having issues identifying them I would recommend the following steps:

  1. Click the Devices icon.
  2. Select the device in question.
  3. Click Nerd and note down the IP Address of the device.
  4. Go to the network settings of your device where it will display the local IP Address and match that to the IP Address noted in Privacy Hero.

This is how you can identify a device that is not properly named.

10. Now that your devices are assigned you can set the Bedtime Settings (Internet Scheduler) and Safe Surf settings for your new Profile.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero Bedtime Settings (Internet Scheduler)

TeamFlashRouters · Apr 3, 2023 ·

Your Privacy Hero router uses Cloud Based router management which means you can access the router settings from anywhere on any device that has an internet connection. You can follow these steps while connected to your phone, other Wi-Fi network, or the Privacy Hero network.

The Bedtime settings feature allows users to schedule when internet access will be turned off for specific user profiles. All devices assigned to this profile will have these rules applied.

1. From any device that has a browser such as a computer, smartphone, or tablet visit app.privacyhero.com

App.PrivacyHero.com

2. Enter your Privacy Hero account email and password. Click Login.

Privacy Hero Access Settings

If you have not created your Privacy Hero account yet please follow these instructions.

3. Click the Profiles symbol.

Privacy Hero Profiles

4. Click the name of the User Profile.

Privacy Hero Select Profile

5. Click Schoolnights or Weekends depending on which you need to set rules for.

Privacy Hero Bedtime School Nights Weekends

6. Select the time that you want the Internet to turn off and the days you want this rule to apply to. Click Save.

Privacy Hero Set Bedtime

7. Set the Bedtime toggle to On.

Privacy Hero Enable Bedtime

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Hotspot Shield Manual OpenVPN Setup

TeamFlashRouters · Jul 15, 2020 ·

Preparing for Manual Hotspot Shield Setup

Obtain your Hotspot Shield OpenVPN Information

If you are not already a Hotspot Shield user Sign Up Now.

1. Log in to your account on the Hotspot Shield website.

2. Click Hotspot Shield on the left side navigation.

Hotspot Shield - Website Admin

3. Under Choose your device click Router.

Hotspot Shield - Select Router

4. In the Set up your router section Select your desired virtual location and then click Download file.

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the <cert> and <key> from the .ovpn file. All Hotspot Shield servers have different keys and certificates.

Hotspot Shield - Download Configuration File

5. Copy the VPN Username, and Password that appear under Step 2 to a notepad, you will need this information later in the setup process.

Hotspot Shield - OpenVPN username and password

DD-WRT Router Setup for Hotspot Shield

Navigate to Services > VPN

Enter Hotspot Shield settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote universitycalendar.us 8041
universitycalendar.us is your Hotspot Shield server name. Enter the server name in this field.

Port

8041

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your Hotspot Shield account.

Password

Enter the Password you obtained in your Hotspot Shield account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

No

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping 15
ping-restart 0
reneg-sec 0
remote-cert-tls server

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIFazCCA1OgAwIBAgIRAIIQz7DSQONZRGPgu2OCiwAwDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTUwNjA0MTEwNDM4
WhcNMzUwNjA0MTEwNDM4WjBPMQswCQYDVQQGEwJVUzEpMCcGA1UEChMgSW50ZXJu
ZXQgU2VjdXJpdHkgUmVzZWFyY2ggR3JvdXAxFTATBgNVBAMTDElTUkcgUm9vdCBY
MTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAK3oJHP0FDfzm54rVygc
h77ct984kIxuPOZXoHj3dcKi/vVqbvYATyjb3miGbESTtrFj/RQSa78f0uoxmyF+
0TM8ukj13Xnfs7j/EvEhmkvBioZxaUpmZmyPfjxwv60pIgbz5MDmgK7iS4+3mX6U
A5/TR5d8mUgjU+g4rk8Kb4Mu0UlXjIB0ttov0DiNewNwIRt18jA8+o+u3dpjq+sW
T8KOEUt+zwvo/7V3LvSye0rgTBIlDHCNAymg4VMk7BPZ7hm/ELNKjD+Jo2FR3qyH
B5T0Y3HsLuJvW5iB4YlcNHlsdu87kGJ55tukmi8mxdAQ4Q7e2RCOFvu396j3x+UC
B5iPNgiV5+I3lg02dZ77DnKxHZu8A/lJBdiB3QW0KtZB6awBdpUKD9jf1b0SHzUv
KBds0pjBqAlkd25HN7rOrFleaJ1/ctaJxQZBKT5ZPt0m9STJEadao0xAH0ahmbWn
OlFuhjuefXKnEgV4We0+UXgVCwOPjdAvBbI+e0ocS3MFEvzG6uBQE3xDk3SzynTn
jh8BCNAw1FtxNrQHusEwMFxIt4I7mKZ9YIqioymCzLq9gwQbooMDQaHWBfEbwrbw
qHyGO0aoSCqI3Haadr8faqU9GY/rOPNk3sgrDQoo//fb4hVC1CLQJ13hef4Y53CI
rU7m2Ys6xt0nUW7/vGT1M0NPAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNV
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBR5tFnme7bl5AFzgAiIyBpY9umbbjANBgkq
hkiG9w0BAQsFAAOCAgEAVR9YqbyyqFDQDLHYGmkgJykIrGF1XIpu+ILlaS/V9lZL
ubhzEFnTIZd+50xx+7LSYK05qAvqFyFWhfFQDlnrzuBZ6brJFe+GnY+EgPbk6ZGQ
3BebYhtF8GaV0nxvwuo77x/Py9auJ/GpsMiu/X1+mvoiBOv/2X/qkSsisRcOj/KK
NFtY2PwByVS5uCbMiogziUwthDyC3+6WVwW6LLv3xLfHTjuCvjHIInNzktHCgKQ5
ORAzI4JMPJ+GslWYHb4phowim57iaztXOoJwTdwJx4nLCgdNbOhdjsnvzqvHu7Ur
TkXWStAmzOVyyghqpZXjFaH3pO3JLF+l+/+sKAIuvtd7u+Nxe5AW0wdeRlN8NwdC
jNPElpzVmbUq4JUagEiuTDkHzsxHpFKVK7q4+63SM1N95R1NbdWhscdCb+ZAJzVc
oyi3B43njTOQ5yOf+1CceWxG1bQVs5ZufpsMljq4Ui0/1lvh+wjChP4kqKOJ2qxq
4RgqsahDYVvTH9w7jXbyLeiNdd8XM2w9U/t7y0Ff/9yi0GE44Za4rF2LN9d11TPA
mRGunUHBcnWEvgJBQl9nJEiU0Zsnvgc/ubhPgXRR4Xq37Z0j4r7g1SgEEzwxA57d
emyPxgcYxn/eR44/KJ4EBs+lVDR3veyJm+kXQ99b21/+jh5Xos1AnX5iItreGCc=
—–END CERTIFICATE—–
—–BEGIN CERTIFICATE—–
MIIFjTCCA3WgAwIBAgIRANOxciY0IzLc9AUoUSrsnGowDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTYxMDA2MTU0MzU1
WhcNMjExMDA2MTU0MzU1WjBKMQswCQYDVQQGEwJVUzEWMBQGA1UEChMNTGV0J3Mg
RW5jcnlwdDEjMCEGA1UEAxMaTGV0J3MgRW5jcnlwdCBBdXRob3JpdHkgWDMwggEi
MA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCc0wzwWuUuR7dyXTeDs2hjMOrX
NSYZJeG9vjXxcJIvt7hLQQWrqZ41CFjssSrEaIcLo+N15Obzp2JxunmBYB/XkZqf
89B4Z3HIaQ6Vkc/+5pnpYDxIzH7KTXcSJJ1HG1rrueweNwAcnKx7pwXqzkrrvUHl
Npi5y/1tPJZo3yMqQpAMhnRnyH+lmrhSYRQTP2XpgofL2/oOVvaGifOFP5eGr7Dc
Gu9rDZUWfcQroGWymQQ2dYBrrErzG5BJeC+ilk8qICUpBMZ0wNAxzY8xOJUWuqgz
uEPxsR/DMH+ieTETPS02+OP88jNquTkxxa/EjQ0dZBYzqvqEKbbUC8DYfcOTAgMB
AAGjggFnMIIBYzAOBgNVHQ8BAf8EBAMCAYYwEgYDVR0TAQH/BAgwBgEB/wIBADBU
BgNVHSAETTBLMAgGBmeBDAECATA/BgsrBgEEAYLfEwEBATAwMC4GCCsGAQUFBwIB
FiJodHRwOi8vY3BzLnJvb3QteDEubGV0c2VuY3J5cHQub3JnMB0GA1UdDgQWBBSo
SmpjBH3duubRObemRWXv86jsoTAzBgNVHR8ELDAqMCigJqAkhiJodHRwOi8vY3Js
LnJvb3QteDEubGV0c2VuY3J5cHQub3JnMHIGCCsGAQUFBwEBBGYwZDAwBggrBgEF
BQcwAYYkaHR0cDovL29jc3Aucm9vdC14MS5sZXRzZW5jcnlwdC5vcmcvMDAGCCsG
AQUFBzAChiRodHRwOi8vY2VydC5yb290LXgxLmxldHNlbmNyeXB0Lm9yZy8wHwYD
VR0jBBgwFoAUebRZ5nu25eQBc4AIiMgaWPbpm24wDQYJKoZIhvcNAQELBQADggIB
ABnPdSA0LTqmRf/Q1eaM2jLonG4bQdEnqOJQ8nCqxOeTRrToEKtwT++36gTSlBGx
A/5dut82jJQ2jxN8RI8L9QFXrWi4xXnA2EqA10yjHiR6H9cj6MFiOnb5In1eWsRM
UM2v3e9tNsCAgBukPHAg1lQh07rvFKm/Bz9BCjaxorALINUfZ9DD64j2igLIxle2
DPxW8dI/F2loHMjXZjqG8RkqZUdoxtID5+90FgsGIfkMpqgRS05f4zPbCEHqCXl1
eO5HyELTgcVlLXXQDgAWnRzut1hFJeczY1tjQQno6f6s+nMydLN26WuU4s3UYvOu
OsUxRlJu7TSRHqDC3lSE5XggVkzdaPkuKGQbGpny+01/47hfXXNB7HntWNZ6N2Vw
p7G6OfY+YQrZwIaQmhrIqJZuigsrbe3W+gdn5ykE9+Ky0VgVUsfxo52mwFYs1JKY
2PGDuWx8M6DlS6qQkvHaRUo0FMd8TsSlbF0/v965qGFKhSDeQoMpYnwcmQilRh/0
ayLThlHLN81gSkJjVrPI0Y8xCVPB4twb1PFUd2fPM3sA1tJ83sZ5v8vgFv2yofKR
PB0t6JzUA81mSqM3kxl5e+IZwhYAyO0OTg3/fs8HqGTNKd9BqoUwSRBzp06JMg5b
rUCGwbCUDI0mxadJ3Bz4WxR6fyNpBK2yAinWEsikxqEt
—–END CERTIFICATE—–

Public Client Cert

In the .ovpn file Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

In the .ovpn file Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Hotspot Shield connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit Hotspot Shield’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Hotspot Shield.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Hotspot Shield server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new Public Client Cert and Private Client Key.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

My 2.4GHz network is not showing up

TeamFlashRouters · May 2, 2019 ·

If you ever have an issue with WiFi, you can always wire directly into the FlashRouter to verify and/or update your current WiFi settings.

Enter the recommended wireless settings

Our team has tested the wireless functionality for each FlashRouter that we offer and shared our recommended wireless settings in our Wifi Setup area. Replicate the settings for your FlashRouter model found on that page if the 2.4GHz is not showing.

Change the wireless channel

Navigate to Wireless > Basic Settings

Change the wireless channel setting for the 2.4GHz band that is not appearing. The most broadly compatible channels are 6 and 11.

CLICK APPLY SETTINGS

Refresh your device's network adapter

In rare instances the wireless adapter for your device may stop picking up WiFi networks and must be reset. This will be different for each device, that is why the best way to refresh your wireless adapter is to simply reboot any device in question and see if the adapter now picks up your WiFi networks.

Review wireless Status

Navigate to Status > Wireless

The readouts on this page can help tell if there are errors with the FlashRouter’s wireless. View our article on how to read the Wireless Status page for more information.

Surfshark Setup for Privacy Hero

TeamFlashRouters · Sep 23, 2025 ·

Privacy Hero supports Surfshark through WireGuard and OpenVPN using the Custom VPN provider option.

WireGuard is recommended for most users. It requires a Surfshark WireGuard key pair and a downloaded server configuration file. OpenVPN uses a downloaded .ovpn file and Surfshark’s separate Manual Setup credentials, not your usual Surfshark login email and password.

Privacy Hero is cloud-managed. You can change these settings from any computer, smartphone, or tablet with an internet connection; you do not need to be on the Privacy Hero WiFi to configure the VPN.

Choose Your Surfshark Setup

Select the connection method or instructions you need.

WireGuard Setup →Recommended · Key pair and server fileOpenVPN Setup →Manual credentials and UDP .ovpn fileUpload WireGuard →Import your configuration into Privacy HeroUpload OpenVPN →Add the file and service credentialsVerify Connection →Check your VPN IP and locationTroubleshooting →Fix connection failures and no internet

Surfshark WireGuard Setup (Recommended)

WireGuard uses a key pair for authentication. A separate Surfshark username and password is not needed for the WireGuard configuration.

Create or Select Your Surfshark WireGuard Key Pair

  1. Sign in to your Surfshark account.
  2. Open VPN → Manual Setup, choose the Router setup option, and select WireGuard.
  3. If you already registered a key pair with Surfshark, select I have a key pair and follow the prompts to register your public key. Otherwise, select I don’t have a key pair.
  4. If generating a new key pair, enter a name and choose Generate a new key pair. Save the generated keys securely when prompted.

Important: Your WireGuard private key is sensitive. Do not publish or send it in a support ticket. Surfshark notes that you may not be able to view the generated keys again after leaving that screen.

Download a Surfshark WireGuard Server File

  1. After setting up the key pair, select Choose a location or open the Locations section.
  2. Choose an available Surfshark server and download its WireGuard configuration file to your device.

Do not download the WireGuard configuration before setting up the key pair. Surfshark warns that a file downloaded too early can be missing the required key information. For more detail, see Surfshark’s manual WireGuard router instructions.

Upload WireGuard to Privacy Hero

  1. Open app.privacyhero.com and log in to your Privacy Hero account.
  2. Open the VPN section, click Change, and choose Custom as the VPN provider.
  3. Select WireGuard and upload the Surfshark WireGuard configuration file you downloaded.
  4. Click Save and allow Privacy Hero to establish the connection. Confirm the VPN status shows Connected.
Privacy Hero Custom WireGuard configuration and file upload panel

Surfshark OpenVPN Setup

OpenVPN is an alternative to WireGuard. It requires a Surfshark Manual Setup username and password and a downloaded OpenVPN configuration (.ovpn) file.

Get Your Surfshark OpenVPN Credentials

  1. Sign in to your Surfshark account.
  2. Open VPN → Manual Setup, choose Router, and select OpenVPN.
  3. Open the Credentials tab. If credentials are not yet available, select Generate credentials.
  4. Copy the Manual Setup username and password, or keep the tab open to enter them into Privacy Hero later.

Important: These are not your regular Surfshark website email and password. Keep the service credentials private.

Download a Surfshark OpenVPN Server File

  1. In Surfshark’s OpenVPN Manual Setup area, open the Locations tab.
  2. Select a country or server and download its UDP .ovpn configuration file. UDP is the recommended starting option; a TCP configuration may be worth trying later if needed.

Download a new .ovpn file whenever you want to switch to a different Surfshark server location. See Surfshark’s manual server selection instructions.

Upload OpenVPN to Privacy Hero

  1. Open app.privacyhero.com, sign in, and select the VPN section.
  2. Click Change, select Custom, and choose OpenVPN.
  3. Upload the Surfshark UDP .ovpn file you downloaded.
  4. Enter the Surfshark Manual Setup username and password into the Custom OpenVPN fields.
  5. Click Save, then confirm the VPN status shows Connected.
Privacy Hero Custom OpenVPN screen with configuration file upload and username and password fields

Verify Your Surfshark Connection

Privacy Hero showing Connected confirms the router connection status. Test a device on the Privacy Hero network to confirm it is using Surfshark.

  1. Connect your device to the Privacy Hero WiFi or LAN.
  2. Disconnect the Surfshark app or any other VPN app running directly on the testing device.
  3. Open a fresh private/incognito browser window.
  4. Visit Surfshark’s IP address checker.
  5. Confirm the displayed public IP and approximate location correspond to your selected Surfshark server.

You can change Privacy Hero settings while using another WiFi network or cellular data, but the device performing this VPN IP test must be connected to Privacy Hero. Avoid running a separate VPN app on the same testing device, as that creates a double-VPN connection.

Streaming Relocation and Your VPN Location

When Streaming Relocation is enabled for a supported streaming service, that service may use its Streaming Relocation region instead of the Surfshark VPN server region. See Privacy Hero Streaming Relocation.


Surfshark Not Connecting?

If Privacy Hero displays Failed, remains on Connecting, or reports a timeout, try these steps:

  1. Confirm your Surfshark subscription is active and that Custom is selected as the VPN provider in Privacy Hero.
  2. If using WireGuard, confirm that the key pair was created or registered before downloading the server file. If necessary, generate a new key pair, download a fresh configuration, and upload it again.
  3. If using OpenVPN, double-check your separate Surfshark Manual Setup username and password, not your regular website login.
  4. Download a fresh server configuration for another available Surfshark location and try again.
  5. If OpenVPN UDP continues to fail, try a Surfshark TCP .ovpn configuration file to check for a protocol-specific issue.
  6. Temporarily disable the VPN Kill Switch while checking whether internet access works without the VPN, then restore your preferred Kill Switch setting.

No Internet After Surfshark Disconnects?

The VPN Kill Switch may intentionally block normal internet traffic when the VPN connection is unavailable. See Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting.

VPN Connected but One Device Shows the Wrong IP?

If other Privacy Hero devices display the expected Surfshark VPN IP, review the affected device for VPN apps, iCloud Private Relay, Private DNS, proxy settings, antivirus filtering, or other security software. See Device Settings That Can Interfere With Your Router VPN.

Related Privacy Hero Guides

  • Privacy Hero VPN Kill Switch Setup
  • VPN Kill Switch: No Internet or WiFi
  • Privacy Hero Streaming Relocation
  • Device Settings That Can Interfere With Your Router VPN
  • FlashRouters Router Troubleshooting

ProtonVPN Setup Guide for GL.iNet Routers

Dave · Mar 23, 2026 ·

You can connect to ProtonVPN on your GL.iNet router using Wireguard or OpenVPN.

Quick Options

  • Wireguard: Download your preferred server .conf configuration file from the ProtonVPN website.

  • OpenVPN: Download your preferred server .ovpn configuration file from the ProtonVPN website.

:point_right: If you are not already a ProtonVPN user Sign Up Now.

ProtonVPN Wireguard Setup for GLiNet (Recommended)

1. Login to your ProtonVPN account and go to the Downloads section of your ProtonVPN account page

2. Scroll down to find the WireGuard configuration section. Name your configuration and then select Router as the platform, and select Standard server configs.

3. Click Create button to choose the recommended server or scroll down to choose and Download any of the available server files from the list.

4.  Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

5. Navigate to the VPN tab and select WireGuard Client then click + New Group and name your connection and click the check to save.

6. Upload the configuration file and click Apply.

7. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

8. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

ProtonVPN OpenVPN Setup for GLiNet

1. Log in to your ProtonVPN account and navigate to the Account tab. Scroll down to find your OpenVPN specific Username and Password.

2. Go to the Downloads section of your ProtonVPN account page

ProtonVPN Downloads

3. Scroll down to find the OpenVPN configuration Files. Select Router as the platform, UDP as the protocol, and select Standard server configs. Choose your preferred country and download the configuration file.

4. Login to GL.iNet firmware settings (usually 192.168.8.1) in a browser on any computer or smart device connected to the GL.iNet FlashRouter’s network.

View our guide for more instructions on how to access GL.iNet firmware settings.

5. Navigate to the VPN tab and select OpenVPN Client.

GL.iNet VPN OpenVPN Client

6. Select Add Manually then click + New Group and name your connection and click the check to save.

7. Upload the configuration file and input your username and password, click Apply.

8. Start a connection by clicking the 3 dots (…) > Start next to your chosen server.

9. A green dot confirms success. You can also switch between Global Mode or Policy Mode for routing in the VPN Dashboard.

  1. You should now see information appear in the Server Address, Server Listen Port, Traffic Statistics, and Client Virtual IP areas.
  2. Visit ProtonVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

🚫📱Do not run ProtonVPN apps on devices connected to your ProtonVPN router. Using the app at the same time as the router VPN may cause conflicts and connection issues.

Still having issues?

Feel free to submit a ticket and we will get back to you as soon as possible.

How do I access my Roqos device settings?

TeamFlashRouters · Mar 8, 2022 ·

Your Roqos Core’s settings or UI (User Interface) is accessible via a secure cloud based connection rather than the typical local access of other routers. This means that you can manage your Roqos from anywhere in the world not just at home.

Visit the Roqos Login URL

From any device that has a browser such as a computer, smartphone, or tablet visit login.roqos.com

Roqos Login URL

Login with your Roqos account

Enter in the email and password that you set when your Roqos was initially setup. If you still need to create your Roqos account and activate your Roqos follow our Activate and Connect Roqos to Internet guide.

Roqos UI Login

Proceed with making the changes to the settings you desire

Now that you are logged in to your Roqos UI you adjust any settings as you see fit for your network. For guides on how to make specific changes to your Roqos view our Roqos Setup Guide area.

Roqos UI Logged in
« Previous Page
Next Page »

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer