• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: over the air internet

PureVPN Merlin WireGuard Setup

TeamFlashRouters · Jul 20, 2023 ·

Preparing for PureVPN Merlin Setup

Download your PureVPN .conf file

If you are not already an PureVPN user Sign Up Now.

1. Log in to your account on the PureVPN website.
PureVPN Login

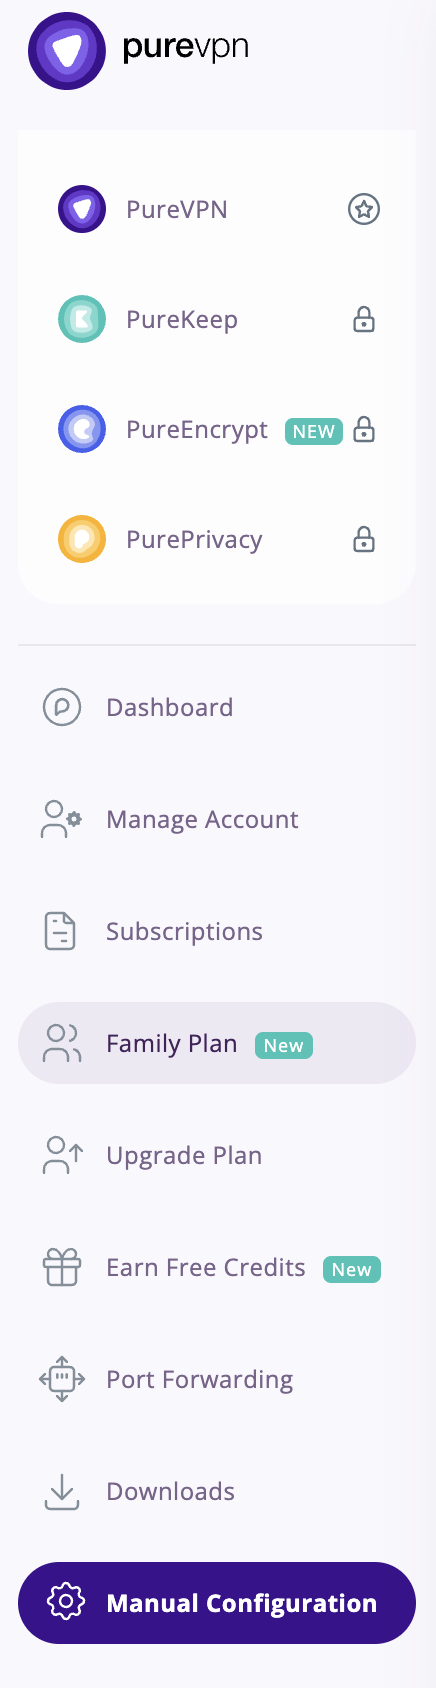
2. Select Manual Configuration.

PureVPN Manual Configuration

3. Select the Server Location you want to connect to and then click Download.
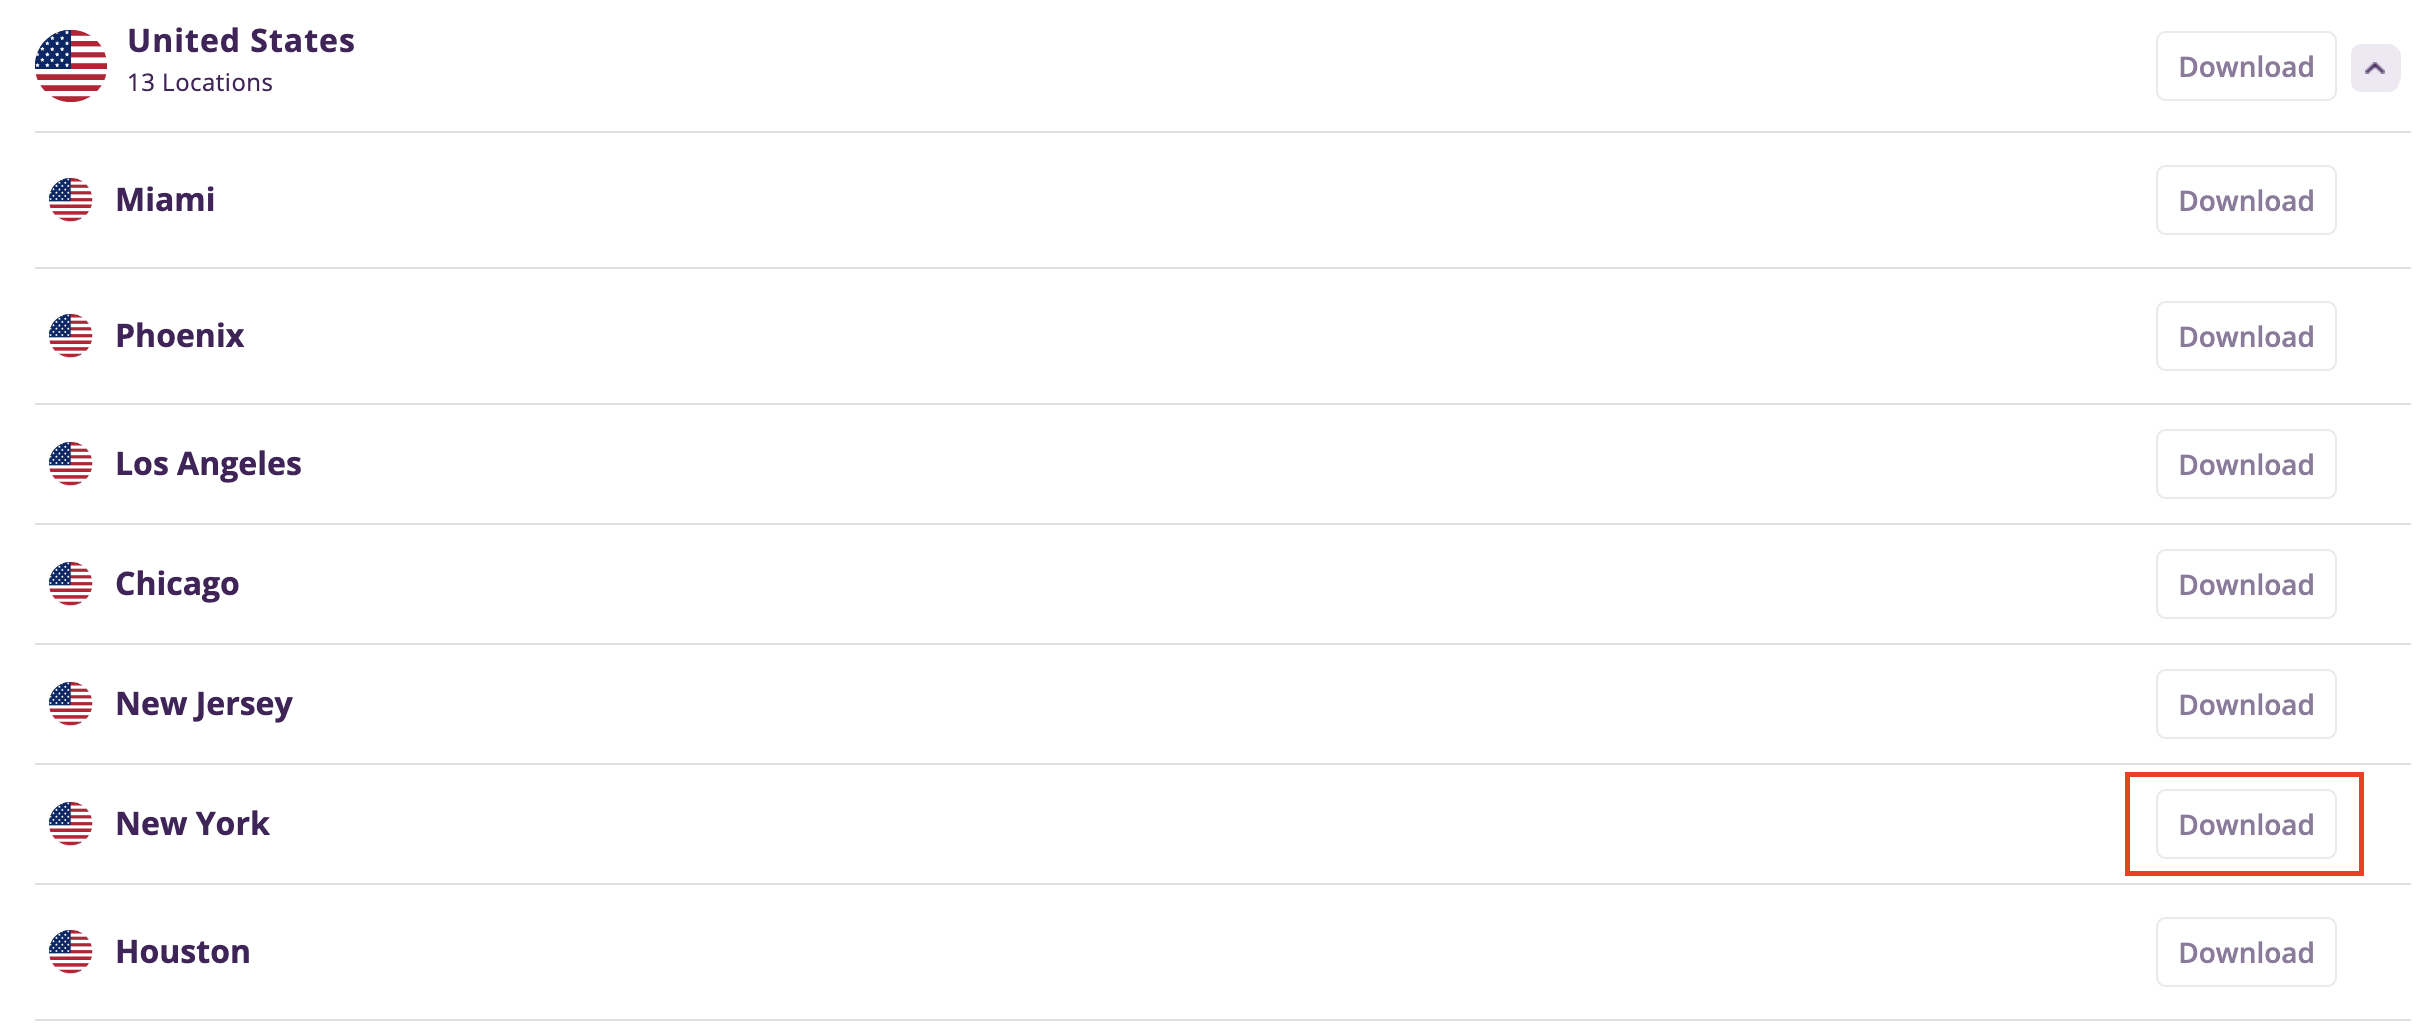
PureVPN select server location

4. In the Select Protocol dropdown choose WireGuard.
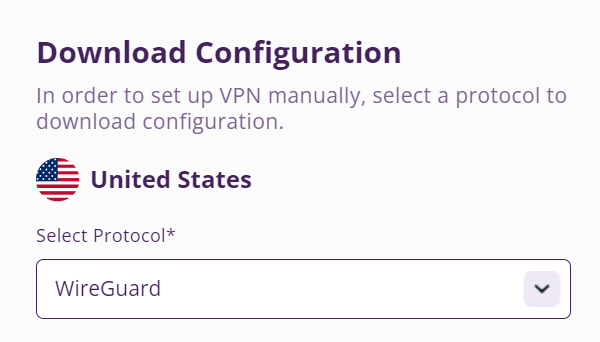
PureVPN WireGuard

5. In the Select Device dropdown choose DD-WRT. Then click Generate Configuration. This will save a .conf file to your computer.
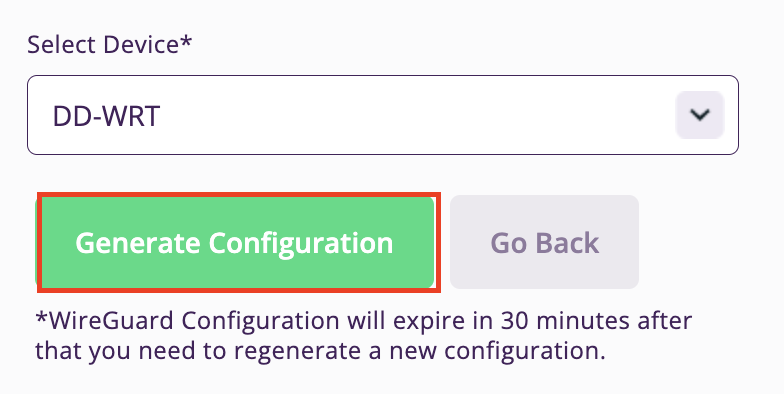
PureVPN Generate Config

Merlin Router Setup for PureVPN

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.
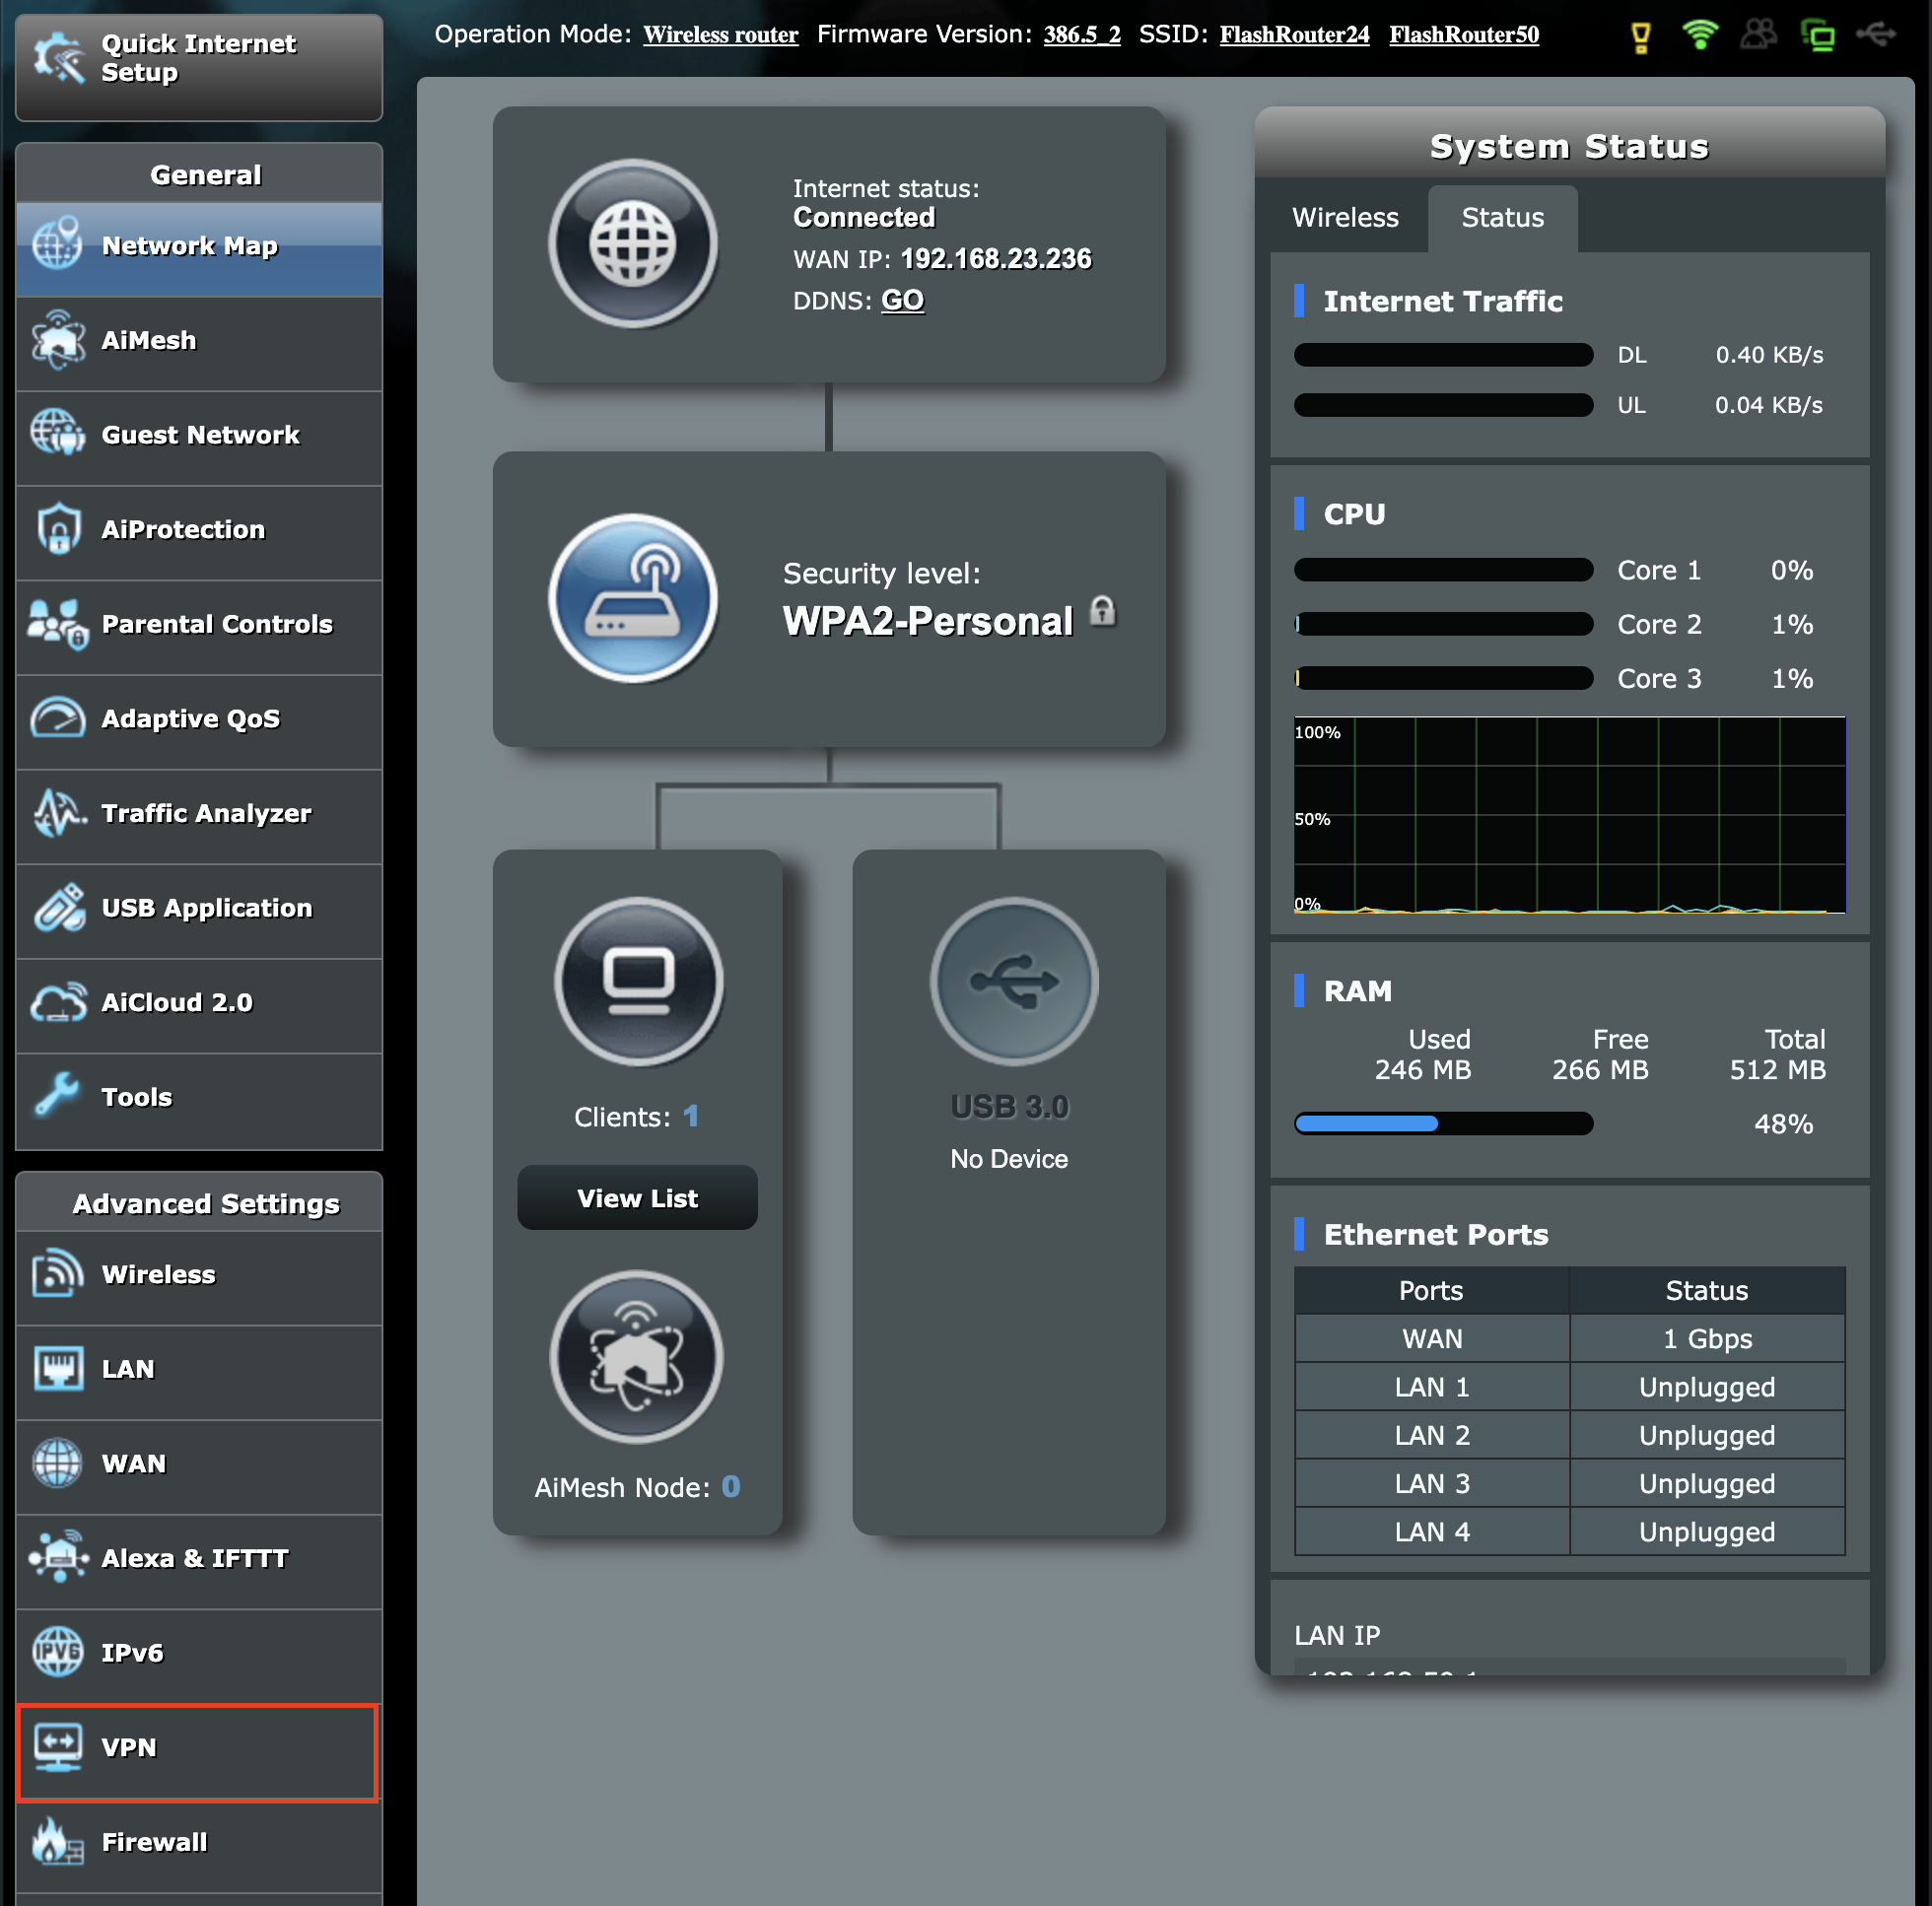
Merlin VPN Tab

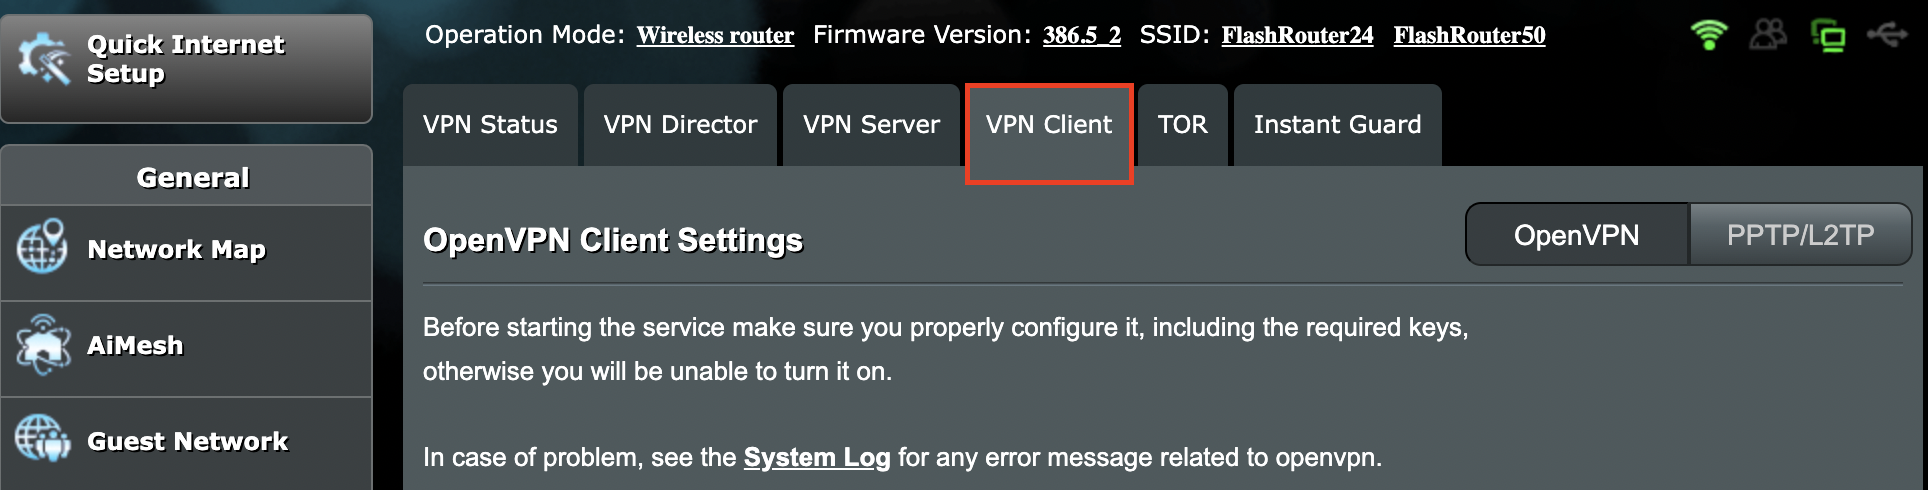
2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Select WireGuard as the VPN Protocol.
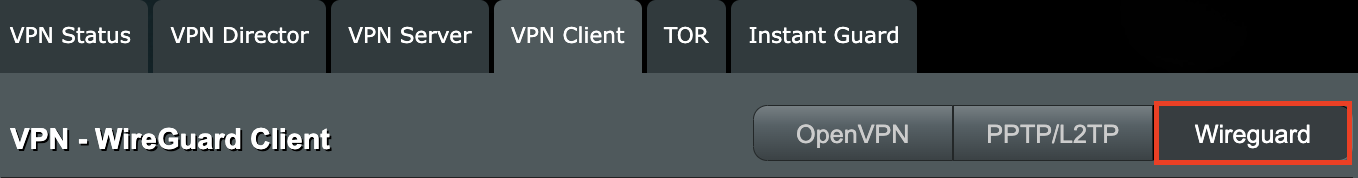
Merlin VPN Client WireGuard

4. Click Choose file and select the .conf file you downloaded earlier. Then click Upload.
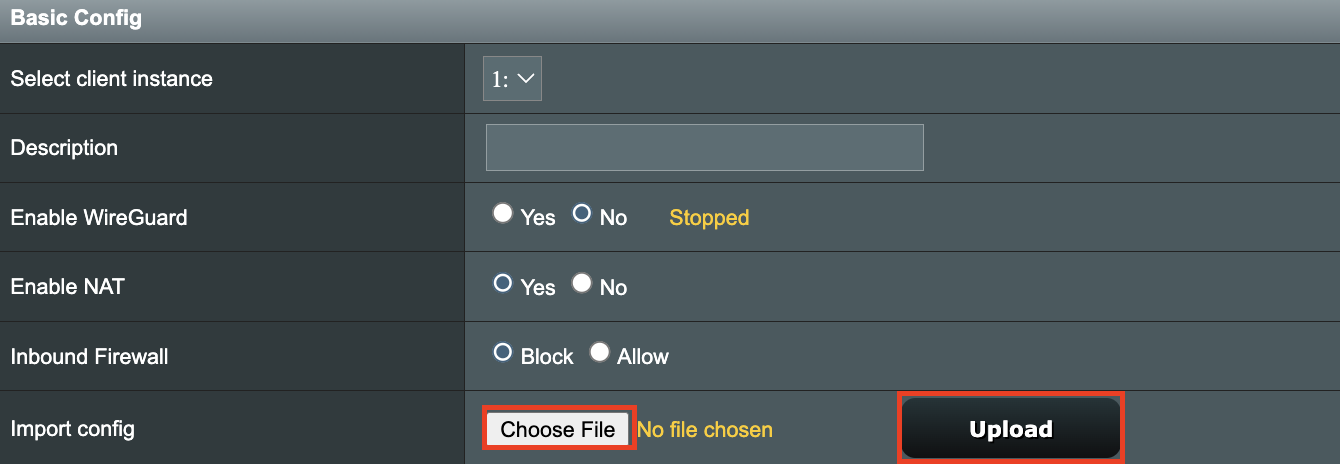
Merlin WireGuard Choose File Upload

5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location here.
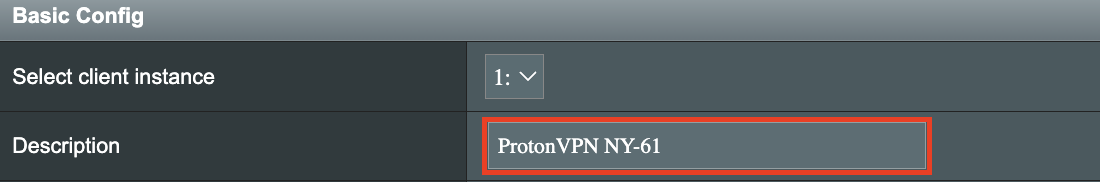
Merlin WireGuard ProtonVPN Description

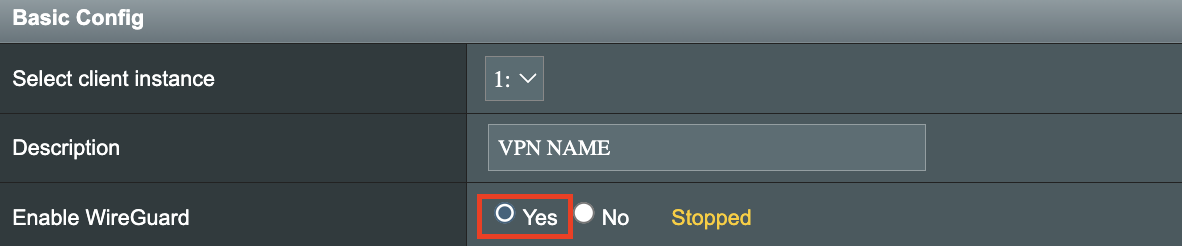
6. Set Enable WireGuard to Yes.

Merlin Enable WireGuard

7. Click Apply at the bottom of the page and you should then see a Connected message appear.
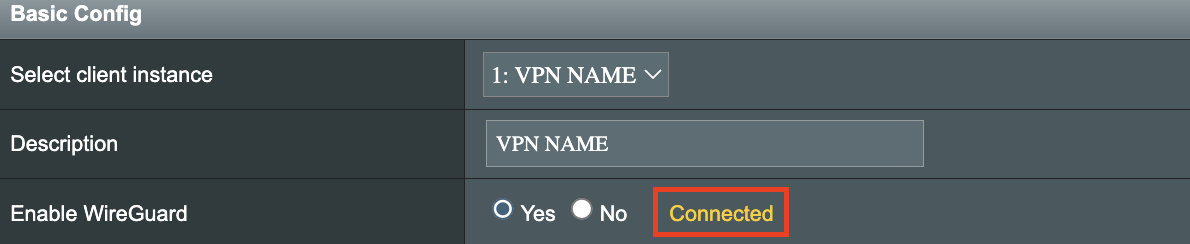
Merlin WireGuard Connected

8. By default no devices are assigned to the new active WireGuard connection profile. Click the VPN Director tab to assign specific devices to the new WireGuard profile. Your IP will not be changed on your devices yet.
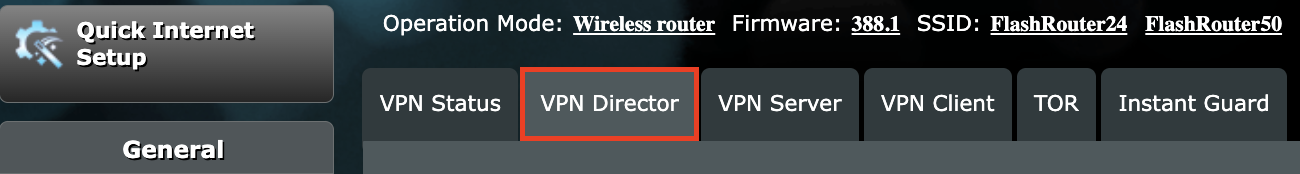
WireGuard select VPN Director

9. On the VPN Director page click the + symbol next to Add new rule.
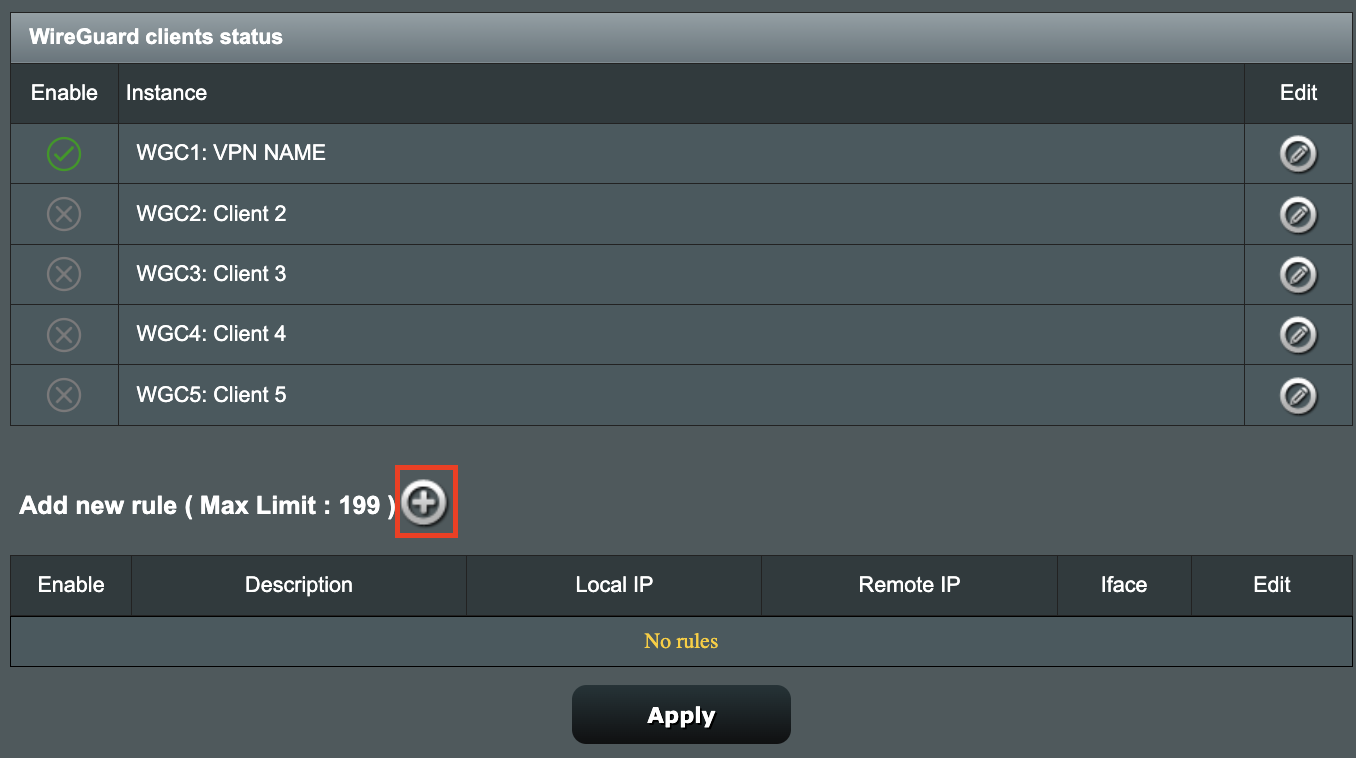
WireGuard VPN Director Add new rule

10. Select the new WireGuard profile in the Interface dropdown.
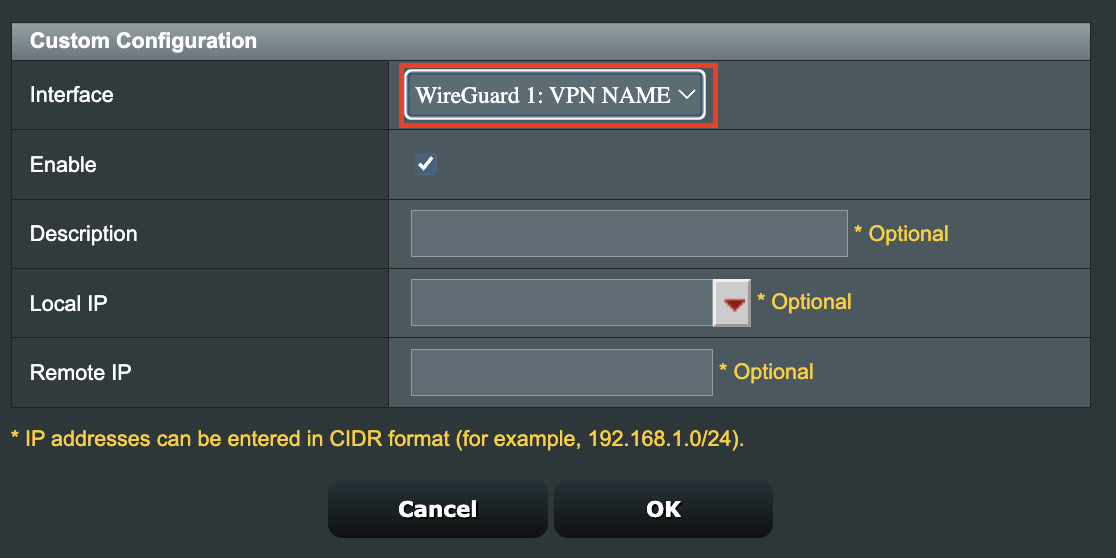
WireGuard VPN Director select Interface

11. In the Local IP field enter in 192.168.50.0/24 if you want ALL devices connected to the FlashRouter’s network to use the WireGuard VPN connection. Click OK.

If you only want certain devices to connect to the WireGuard Client profile you have setting up instead of all the devices connected to the FlashRouter’s network please complete the instructions on our VPN Director guide.

12. Then click Apply at the bottom of the page.

Verify a successful PureVPN connection

Visit PureVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PureVPN.

How to change the PureVPN server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

How do I check for static network settings on my devices?

TeamFlashRouters · May 8, 2019 ·

Static network settings set on a device from a previous connection will interfere with the FlashRouter’s network. Typically the FlashRouter’s network performs best when connected devices are set to automatically use the FlashRouter’s IP Address and DNS.

Make sure you are connected to the FlashRouter’s network via ethernet or WiFi. Keep in mind these instructions may vary based on your current software version.

Check for Static IP Address in Windows

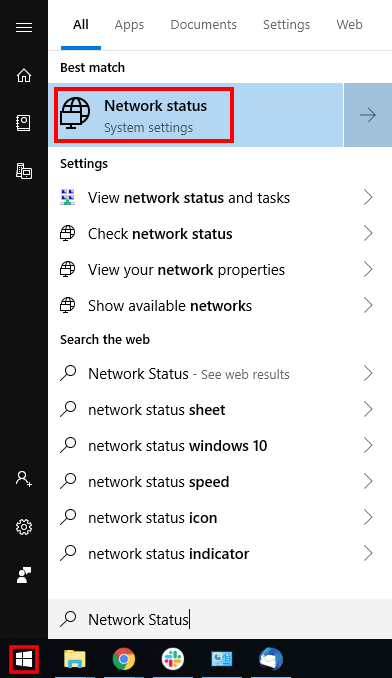
1.  Open the Window search box, and search “Network Status”

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer

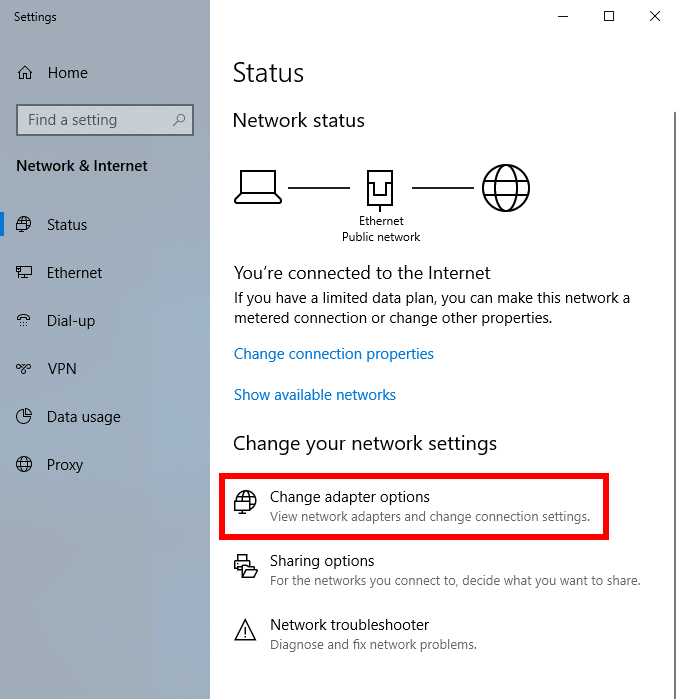
2. Select “Change adapter optons”

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer 2

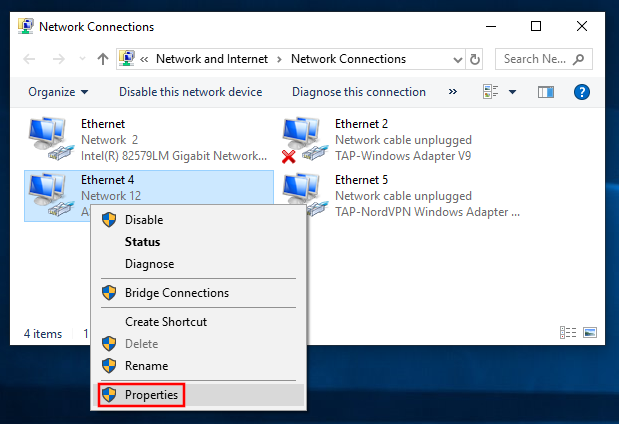
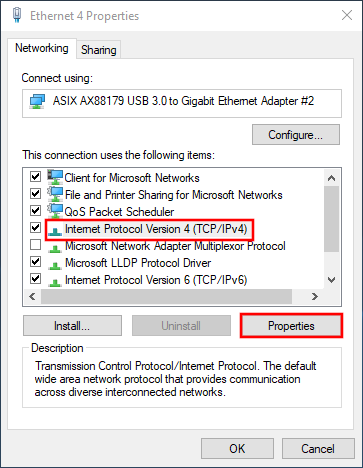
3. Right click on the WiFi and/or ethernet adapter and select Properties.

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer 3

4. Highlight Internet Protocol Version 4 (TCP/IPv4) and click Properties.

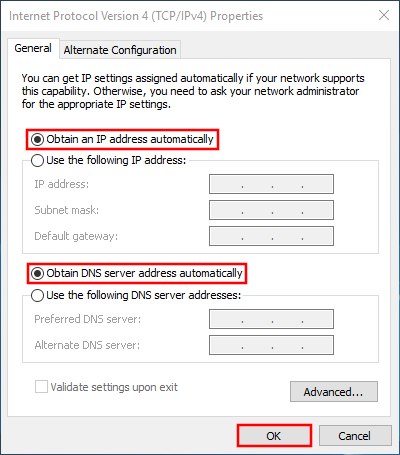
5. Delete the values entered for IP address, Subnet mask, Default gateway, Preferred DNS server, and Alternate DNS server.

6. Select Obtain an IP address automatically and Obtain DNS server address automatically.

7. Click OK.

Find Static DNS settings for FlashRouter DD-WRT in Windows Computer 4

Check for Static IP Address in Apple / Mac

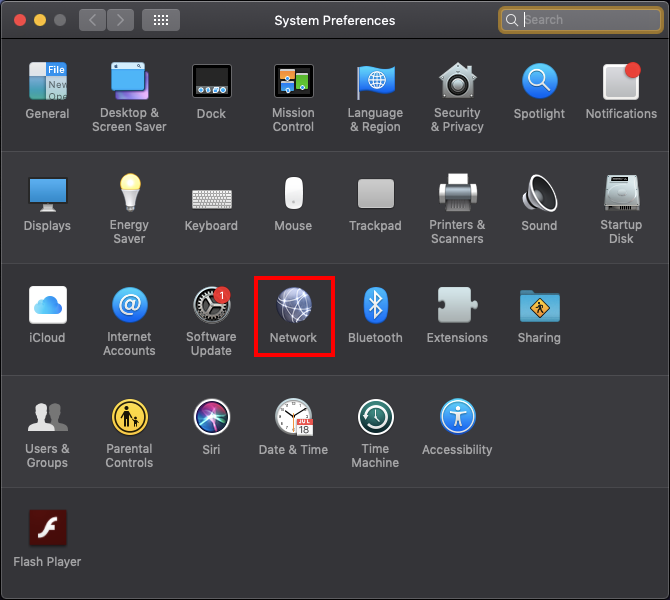
1. Open System Preferences, and select Network.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer

2. Select the adapter that is connected via ethernet or wireless. This will vary based on your current connection.

3. Select Advanced.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer 2

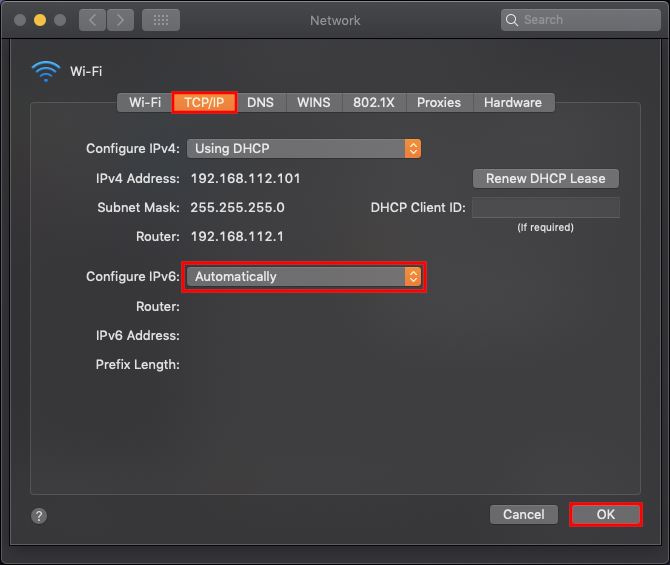
4. Select the TCP/IP tab.

5. Set Configure IPv4 to Automatically.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer 4

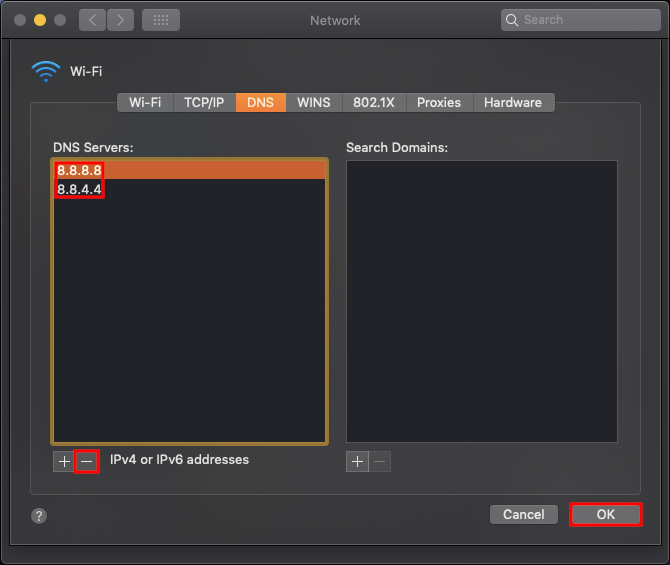
6. Select the DNS field and highlight any DNS servers you see there. If they can be removed you should click the minus symbol below.

Find Static DNS settings for FlashRouter DD-WRT Using a MAC Computer 5

7. Click OK.

8. Click Apply.

Check for Static IP Address in iOS

1.  Open Settings

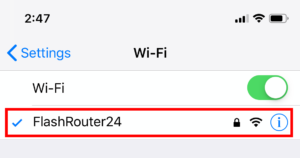
2. Select WiFi, and select the blue icon next to your current connection.

Select FlashRouters DD-WRT Wireless Network in order to Check Static IP Network Settings on iOS Mobile Device

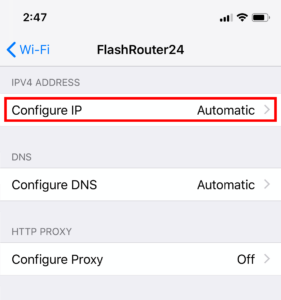
3. Make sure Configure IP is set to Automatically.

Check Static IP Network Settings on iOS Mobile Device and set Configure IP to Automatic

Check for Static IP Address in Android

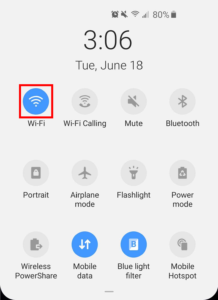
1. From the top of the screen, swipe down to display settings.

2. Select WiFi.

WiFi Icon and Settings in Android Mobile Device

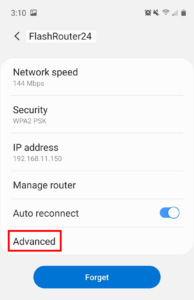
3. Select your current network.

4. Select Advanced.

Advanced Settings Button in Android Mobile Device

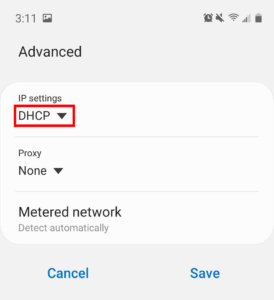
5. Make sure that IP settings is set to DHCP.

Check Static IP DHCP Network Settings in Android Mobile Device

PrivateInternetAccess (PIA) TP-Link OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for PIA TP-Link Setup

Download your PIA .ovpn file

If you are not already a PIA user Sign Up Now.

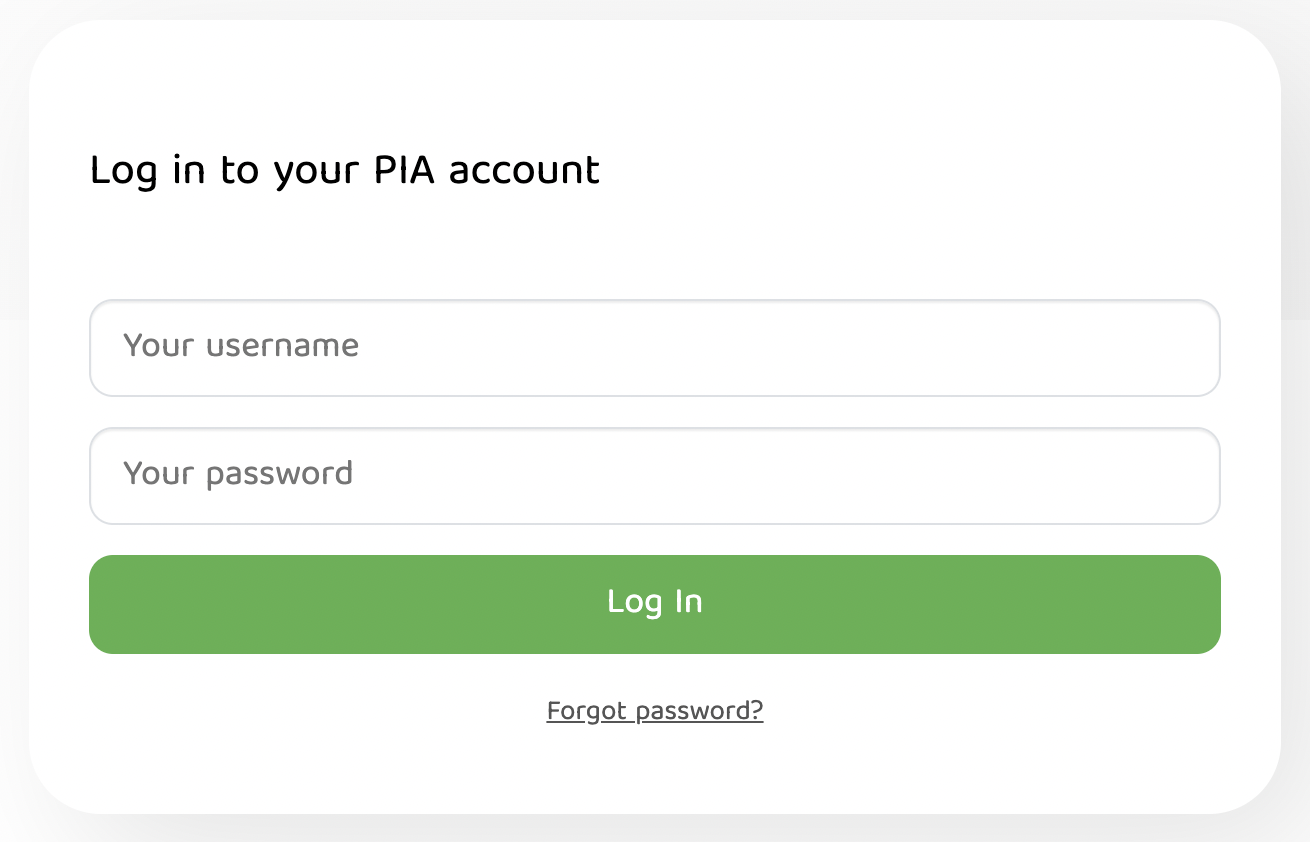
1. Log in to your account on the PIA website.

PIA login

2. Successfully log in with your account information then go to PIA’s OpenVPN Config Generator.

3. On the OpenVPN Configuration Generator select the following:

OpenVPN Version: OpenVPN 2.4 or newer

Select Platform: Linux

Select Region: Choose the server location you’d like to connect to

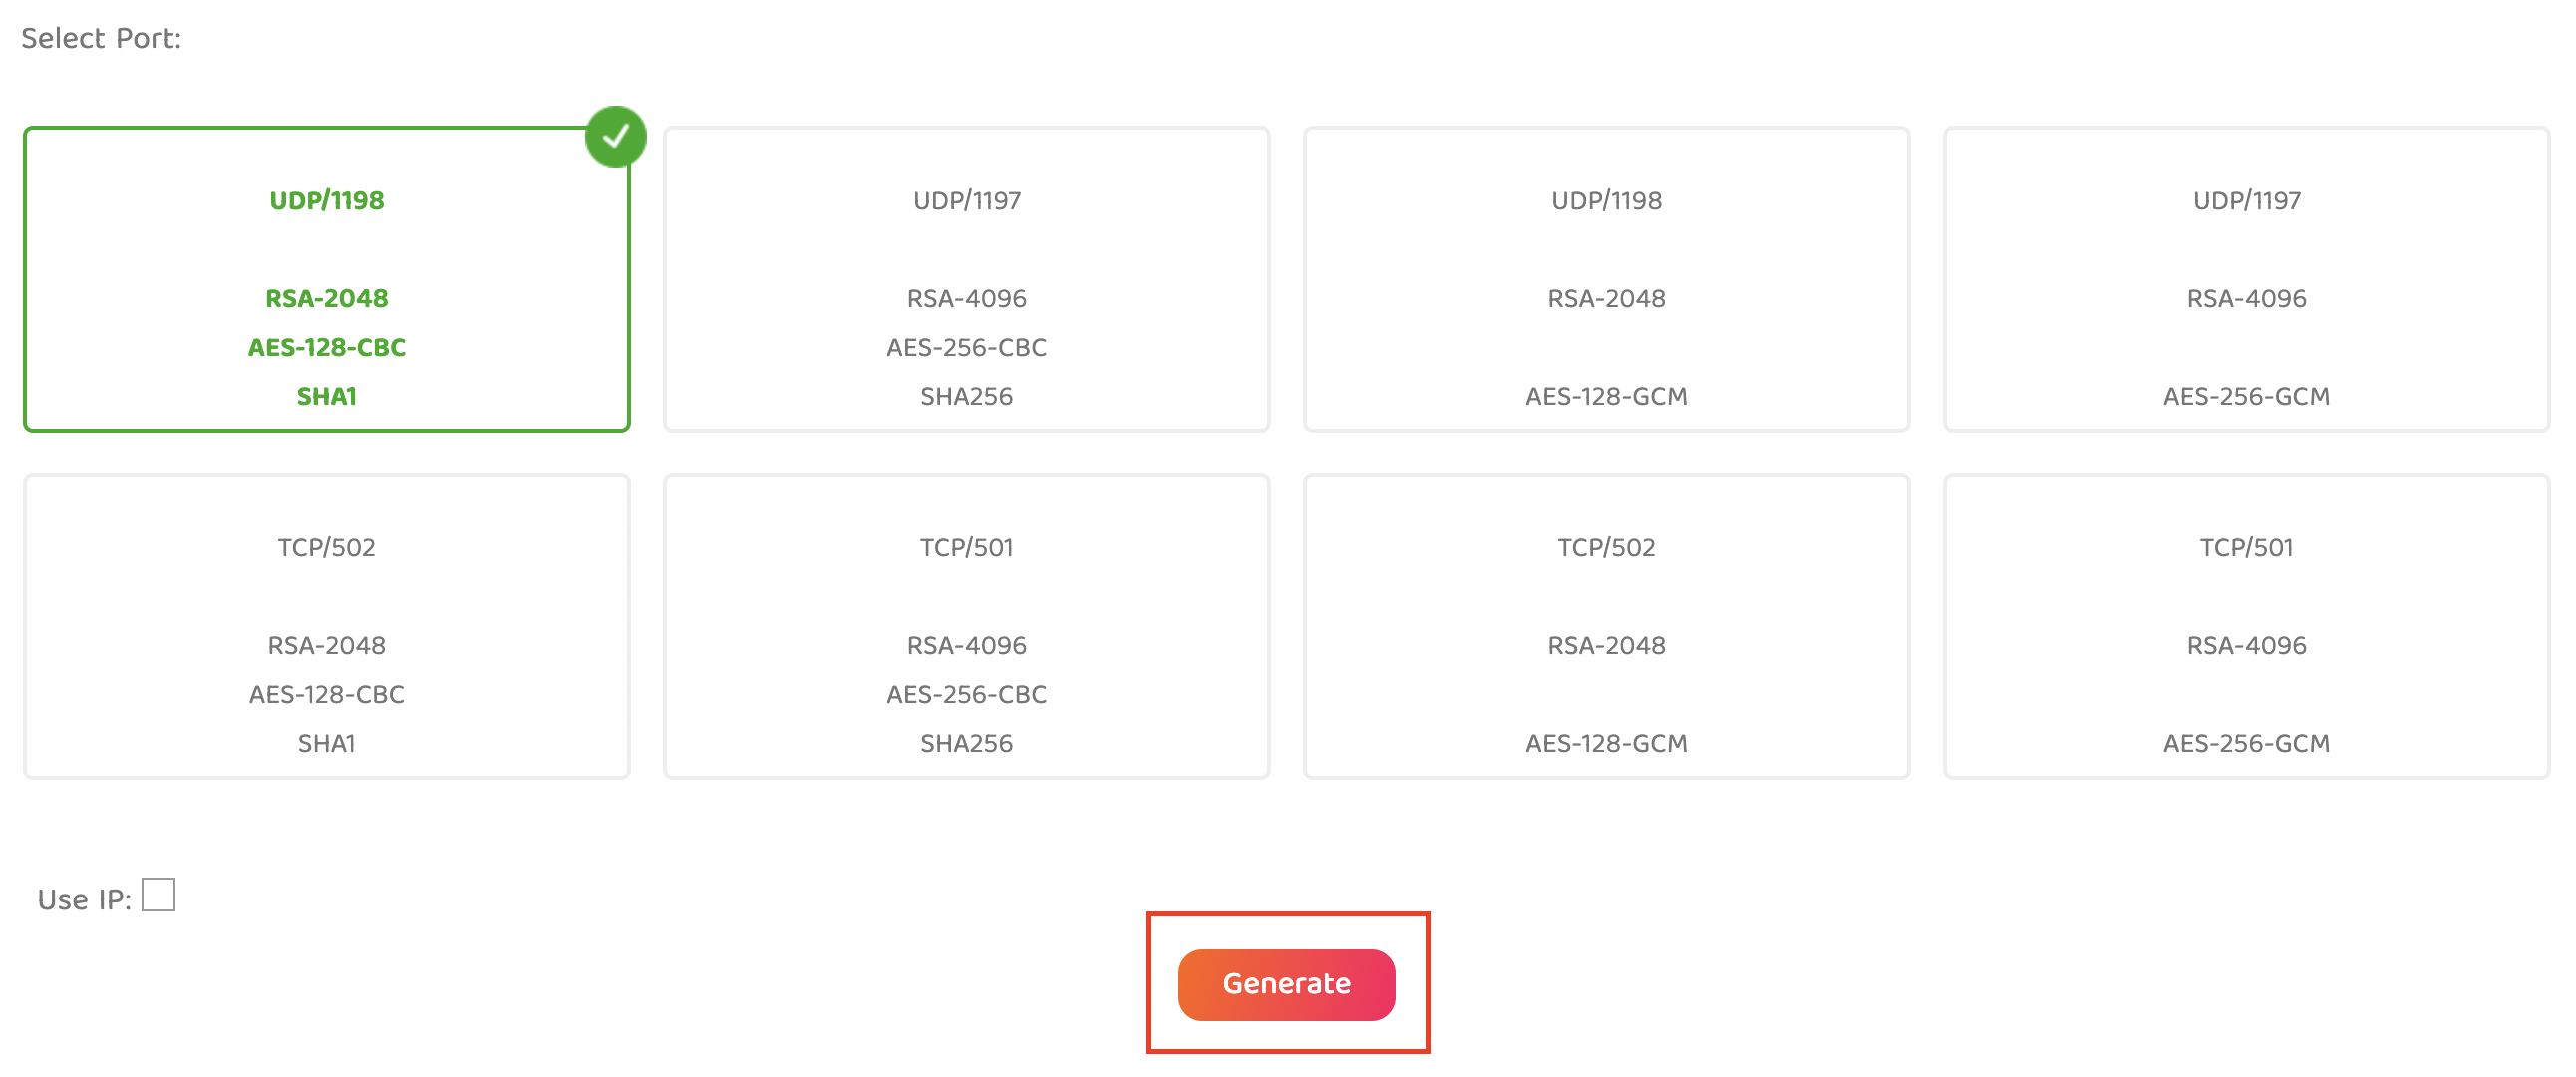
Select Port: Typically we recommend UDP/1198 RSA-2048 AES-128-CBC SHA1 for best speeds but feel free to select the one you want to use.

4. Click Generate to download the .ovpn file. Do not open this file once it is downloaded.

PIA Generate .ovpn file

TP-Link Router Setup for PIA

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

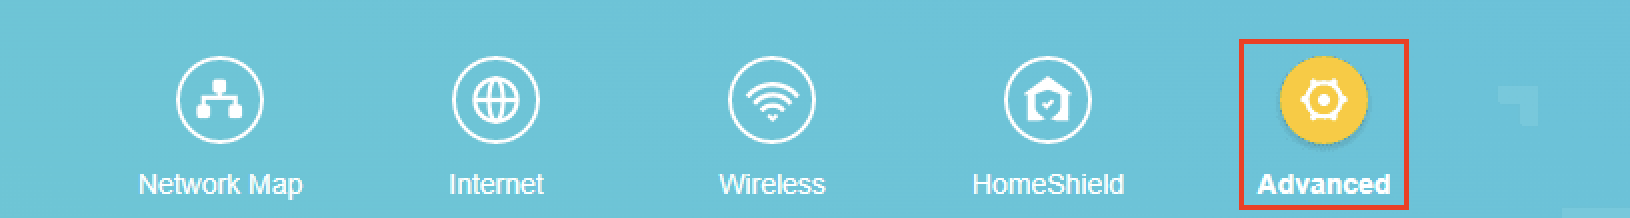
1. Navigate to the Advanced tab.

TP-Link Advanced settings

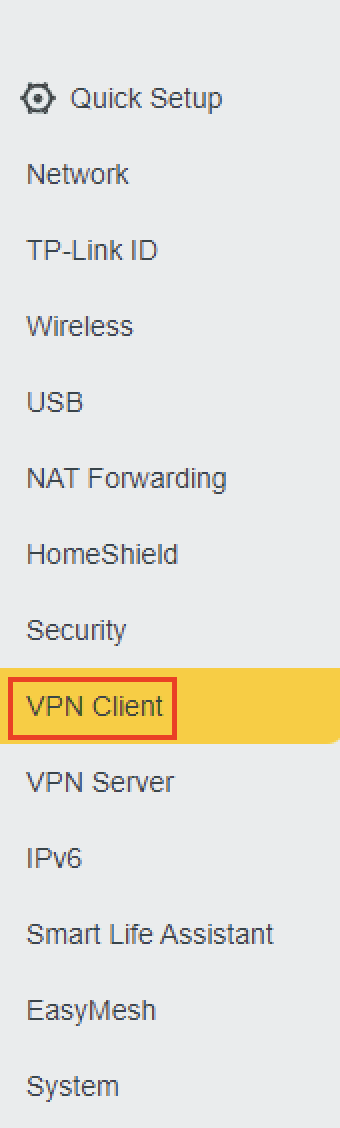
2. Navigate to the VPN Client tab.

TP-Link VPN Client

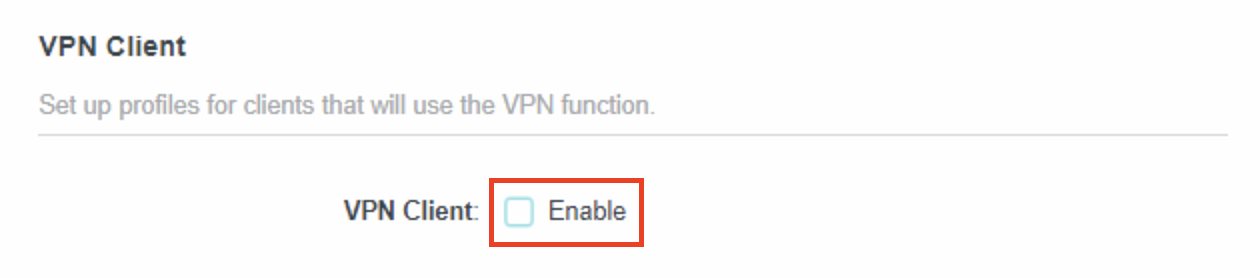
3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

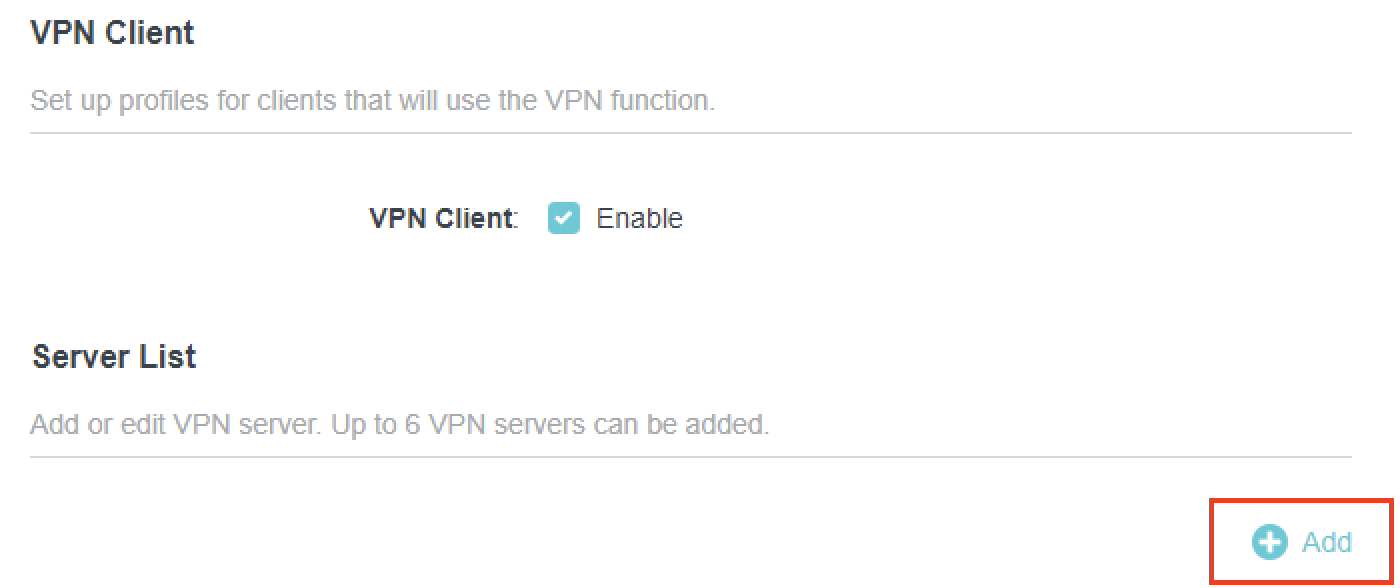
4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location. Our example server was New York so I have entered in PIA New York.

Set the VPN Type to OpenVPN.

In the Username and Password fields paste in the PIA username and password you use to successfully login to your PIA website account.

Click Browse and select the .ovpn file you downloaded earlier. Then click Save.

TP-Link PIA

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

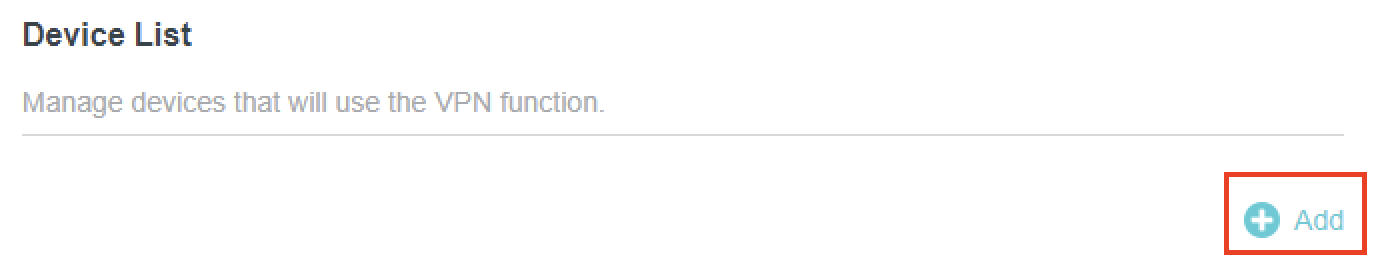
6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

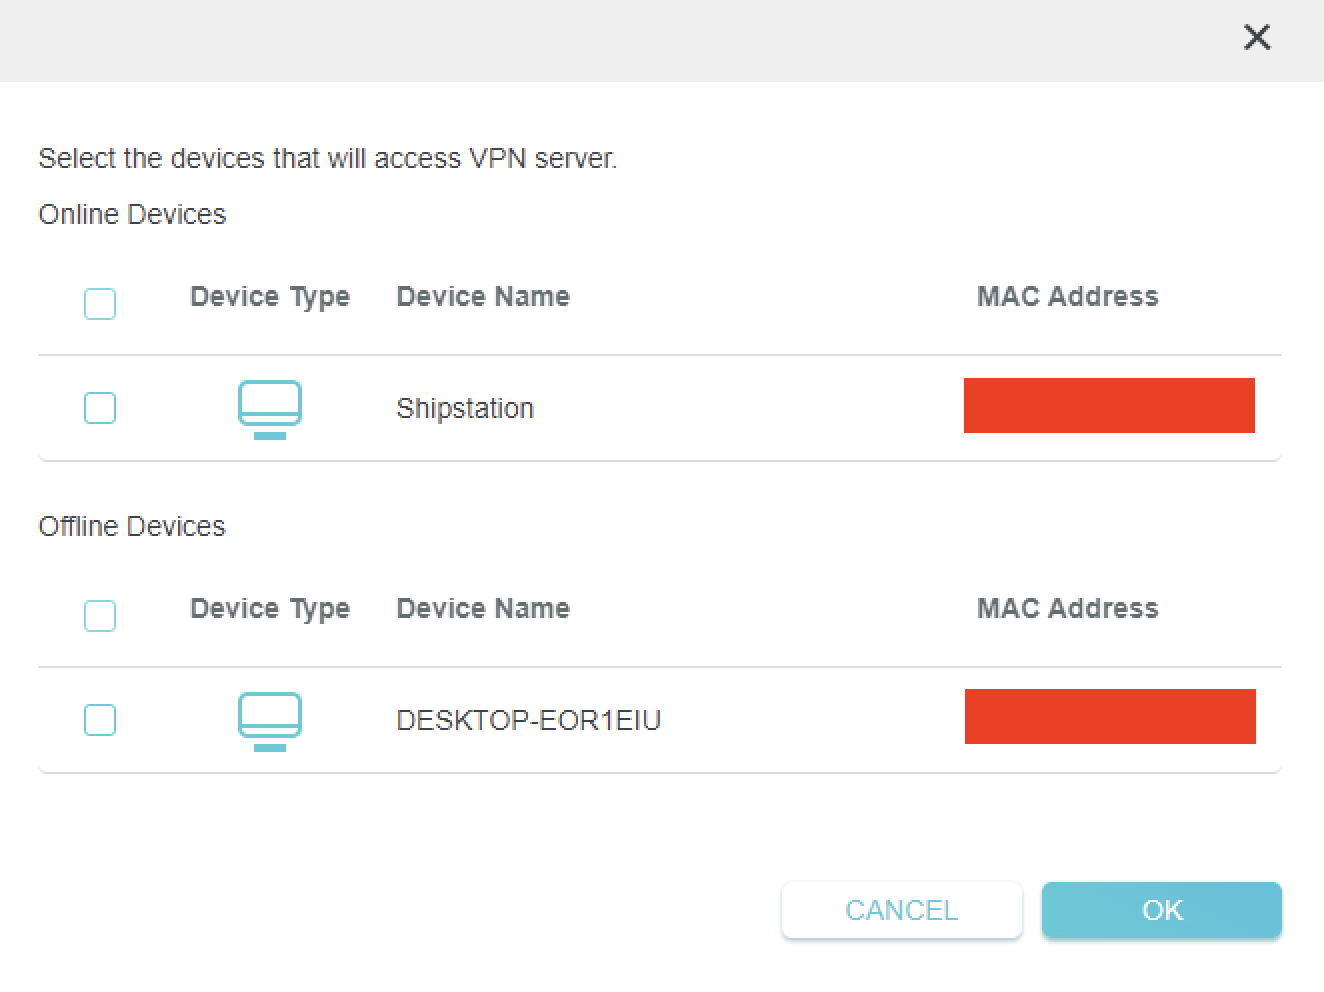
7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link PIA Connected

Verify a successful PIA connection

  1. You should now see a CONNECTED message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

How to change the PIA server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

CyberGhost Manual OpenVPN Setup

TeamFlashRouters · Apr 9, 2019 ·

Preparing for Manual CyberGhost Setup

Obtain your CyberGhost OpenVPN Information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.

CyberGhost Website Login

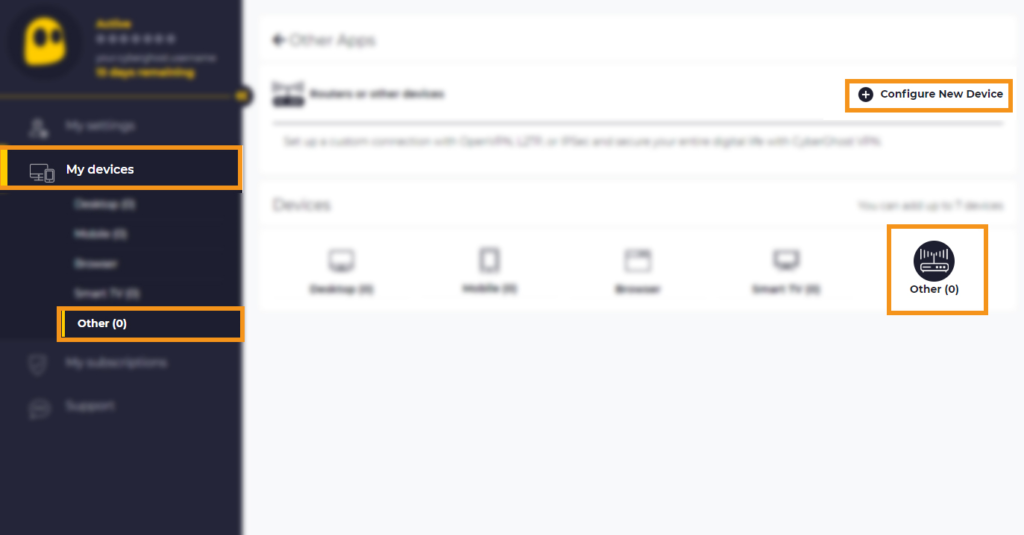
2. Select My Devices.

3. Select Other and then Configure New Device.

CyberGhost Website OpenVPN Configuration Files Generator Cyberghost - Website Screen CyberGhost Website OpenVPN Configuration Files Generator

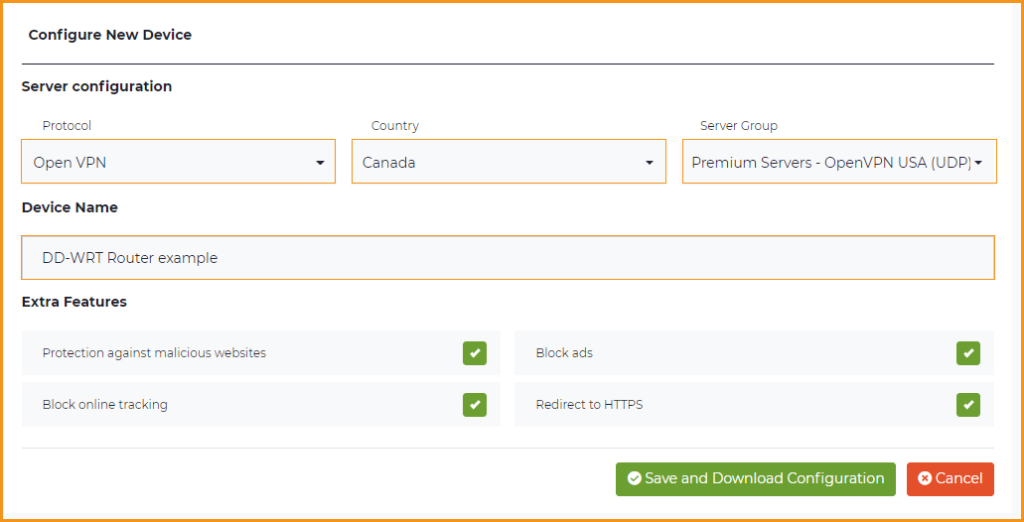
4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 3

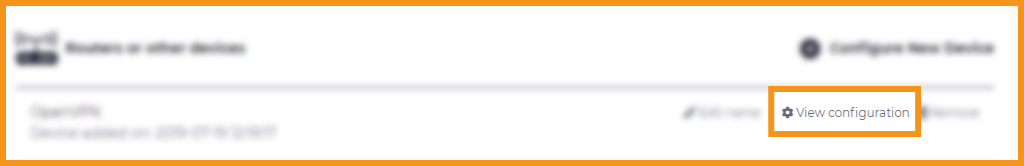
5. Press View configuration.

CyberGhost Website OpenVPN Configuration Files Generator 2

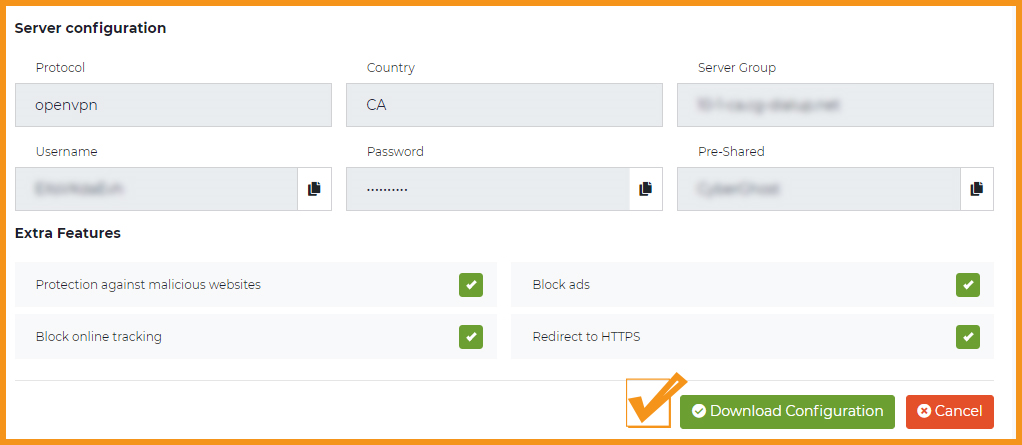
6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.

CyberGhost Website OpenVPN Configuration Files Generator 1

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the ca.crt, client.crt, and client.key files. All CyberGhost servers have different keys and certificates.

DD-WRT Router Setup for CyberGhost

Navigate to Services > VPN

Enter CyberGhost settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you selected in your account. Be sure there are no extra spaces or characters.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your CyberGhost account.

Password

Enter the Password you obtained in your CyberGhost account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

tun-mtu 1500
fragment 1300
mssfix 1300

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIGWjCCBEKgAwIBAgIJAJxUG61mxDS7MA0GCSqGSIb3DQEBDQUAMHsxCzAJBgNV
BAYTAlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3Qg
Uy5BLjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkB
FhJpbmZvQGN5YmVyZ2hvc3Qucm8wHhcNMTcwNjE5MDgxNzI1WhcNMzcwNjE0MDgx
NzI1WjB7MQswCQYDVQQGEwJSTzESMBAGA1UEBxMJQnVjaGFyZXN0MRgwFgYDVQQK
Ew9DeWJlckdob3N0IFMuQS4xGzAZBgNVBAMTEkN5YmVyR2hvc3QgUm9vdCBDQTEh
MB8GCSqGSIb3DQEJARYSaW5mb0BjeWJlcmdob3N0LnJvMIICIjANBgkqhkiG9w0B
AQEFAAOCAg8AMIICCgKCAgEA7O8+mji2FlQhJXn/G4VLrKPjGtxgQBAdjo0dZEQz
KX08q14dLkslmOLgShStWKrOiLXGAvB1rPvvk613jtA0KjQLpgyLy9lIWohQKYjj
5jrJYXMZMkbSHBYI9L8L7iezBEFYrjYKdDo51nq99wRFhKdbyKKjDh3e2L2SVEZL
T1ogkK5gWzjvH+mjjtjUUicK+YjGwWOz6I+KKaG4Ve/D/cE6nCLbhHIMMnargZEu
7sqA6BFeS4kEP/ZdCZoTSX2n43XV1q63nJt/v0KDetbZDciFVW9h9SVPG4qT44p0
550N+Mom7zTX7S/ID5T9dplgU8sRGtIMrG0cIMD9zmpFgUnMusCrR7jJFr0sMAve
TbgZg95LmstV6R6WKZkSFdUrE0DHl4dHoZvTFX+1LhwhHgjgDLaosX0vhG/C/7Lp
oVWimd6RRQT3M9o4Fa1TuhfvBzQ20QHrmRV/yKvGNK0xckZ6EZ/QY7Z55ORU15Tg
ab4ebnblYPWoEmn0mIYP3LFFeoR5OS1EX7+j4kPv+bwPGsmpHjxmZyq2Y7sJBpbO
CJgbkn52WZdPBIRDpPdIHQ8pAJC4T0iMK9xvAwWNl/V6EYYNpR97osyEDXn+BTdA
HlhJ5fck9KlwI9mb1Kg1bhbvbmaIAiOLenSULYf3j6rI1ygo3R2cCyybtuAq8M7z
0OECAwEAAaOB4DCB3TAdBgNVHQ4EFgQU6tdK1g/He5qzjeAoM5eHt4in9iUwga0G
A1UdIwSBpTCBooAU6tdK1g/He5qzjeAoM5eHt4in9iWhf6R9MHsxCzAJBgNVBAYT
AlJPMRIwEAYDVQQHEwlCdWNoYXJlc3QxGDAWBgNVBAoTD0N5YmVyR2hvc3QgUy5B
LjEbMBkGA1UEAxMSQ3liZXJHaG9zdCBSb290IENBMSEwHwYJKoZIhvcNAQkBFhJp
bmZvQGN5YmVyZ2hvc3Qucm+CCQCcVButZsQ0uzAMBgNVHRMEBTADAQH/MA0GCSqG
SIb3DQEBDQUAA4ICAQDNyQ92kj4qiNjnHk99qvnFw9qGfwB9ofaPL74zh0G5hEe3
Wgb2o4fqUGnvUNgOu53gJksz3DcPQ8t40wfmm9I1Z8tiM9qrqvkuQ+nKcLgdooXt
EsTybPIYDZ2cWR/5E0TKRvC7RFzKgQ4D77Vbi4TdaHiDV7ZNfU1iLCoBGcYm80hc
UHEs5KIVLwUmcSOTmbZBySJxcSD0yUpS7nlZGwLY6VQrU+JFwDSisbXT4DXf3iSz
p7FzW0/u/SFvWsPHrjE0hkPoZPalYvouaJEHKAhip0ZwSmitlxbBnmm8+K/3c9mL
A5/uXrirfpuhhs8V3lyV2mczVtSiTl6gpi88gc//JY80JeHdupjO25T3XEzY9cpx
ecmkWaUEjLMx4wVoXQuUiPonfILM6OLwi+zUS8gQErdFeGvcQXbncPa4SdJuHkF8
lgiX2i8S8fPGdXvU37E9bdAXwP5nZriYq1s0D59Qfvz+vLXVkmyZp6ztxjKjKole
mPMak0Y5c1Q4RjNF6tmQoFuy/ACSkWy14Tzu2dFp7UiVbGg1FOvKhfs48zC2/IUQ
v1arqmPT/9LVq3B2DVT9UKXRUXX/f/jSSsVjkz4uUe2jUyL+XHX1nSmROTPHSAJ+
oKf0BLnfqUxFkEUTwLnayssP2nwGgq35b7wEbTFIXdrjHGFUVQIDeERz8UThew==
—–END CERTIFICATE—–

Public Client Cert

Copy and paste all contents of the client.crt file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and paste all contents of the client.key file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful CyberGhost connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit CyberGhost’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to CyberGhost.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the CyberGhost server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new ca.crt, client.crt, and client.key
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Using Device Groups to bypass VPN on ExpressVPN/Aircove firmware

TeamFlashRouters · May 12, 2022 ·

Bypassing the ExpressVPN tunnel on certain devices allows you to have multiple IP Addresses while connected to the same router. This feature is very helpful with certain websites where VPN is blocked such as streaming services and banking information.

1. Connect to the FlashRouter’s network via ethernet cable or wireless.

2. Open your web browser and enter expressvpnrouter.com or 192.168.132.1 in the URL.

ExpressVPNrouter.com
192.168.132.1

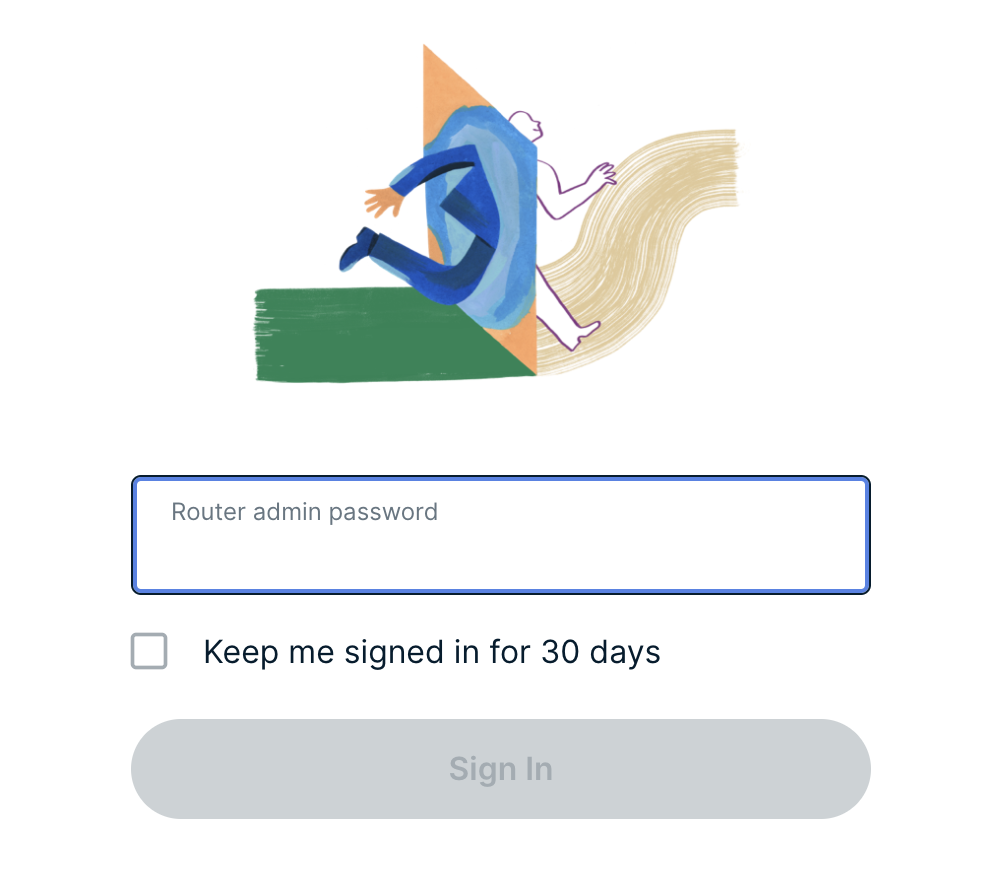
3. Login with your ExpressVPN FlashRouter admin password.

ExpressVPN Router admin login

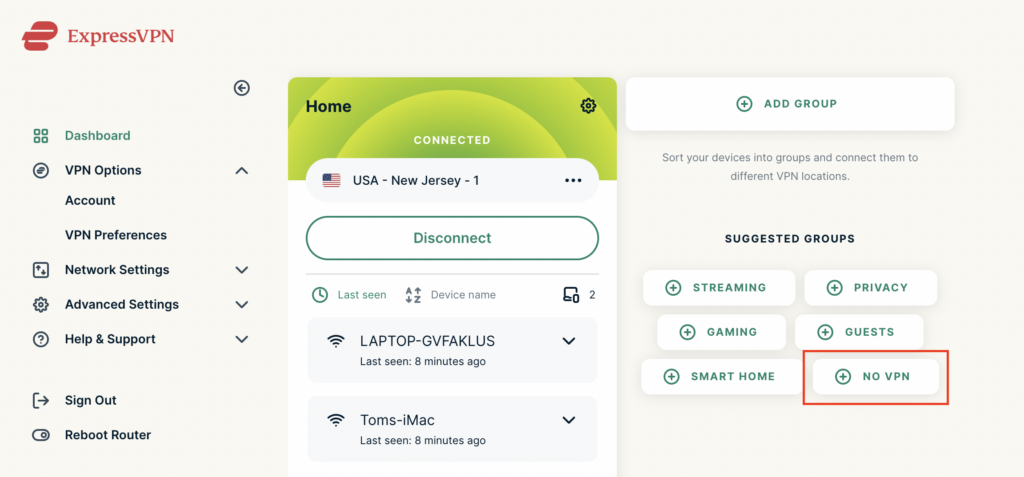
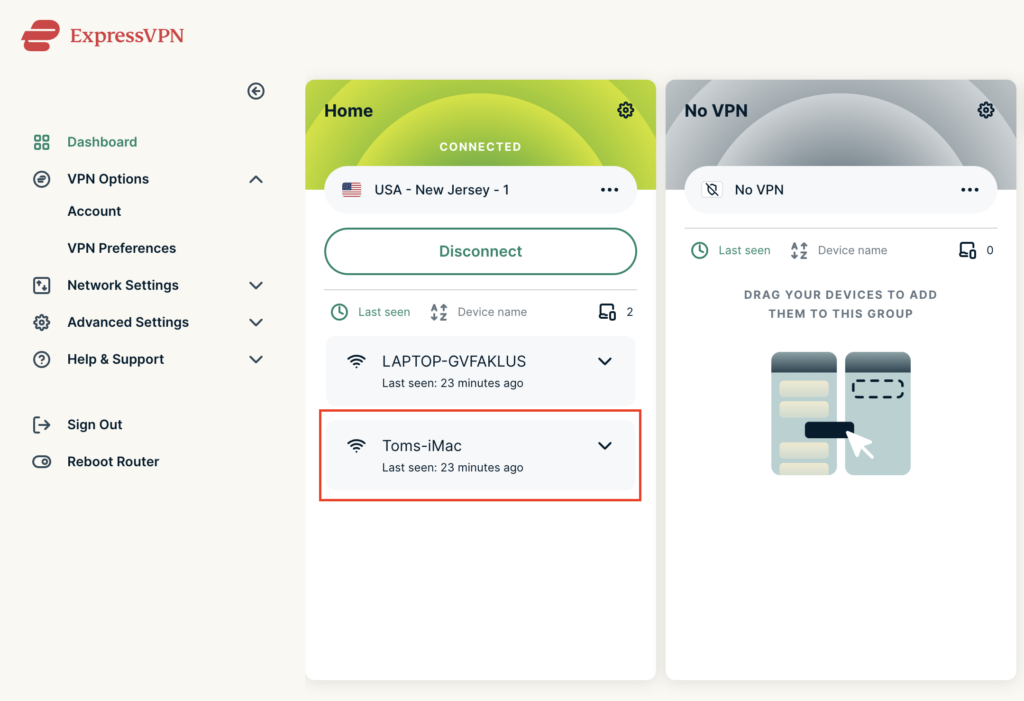
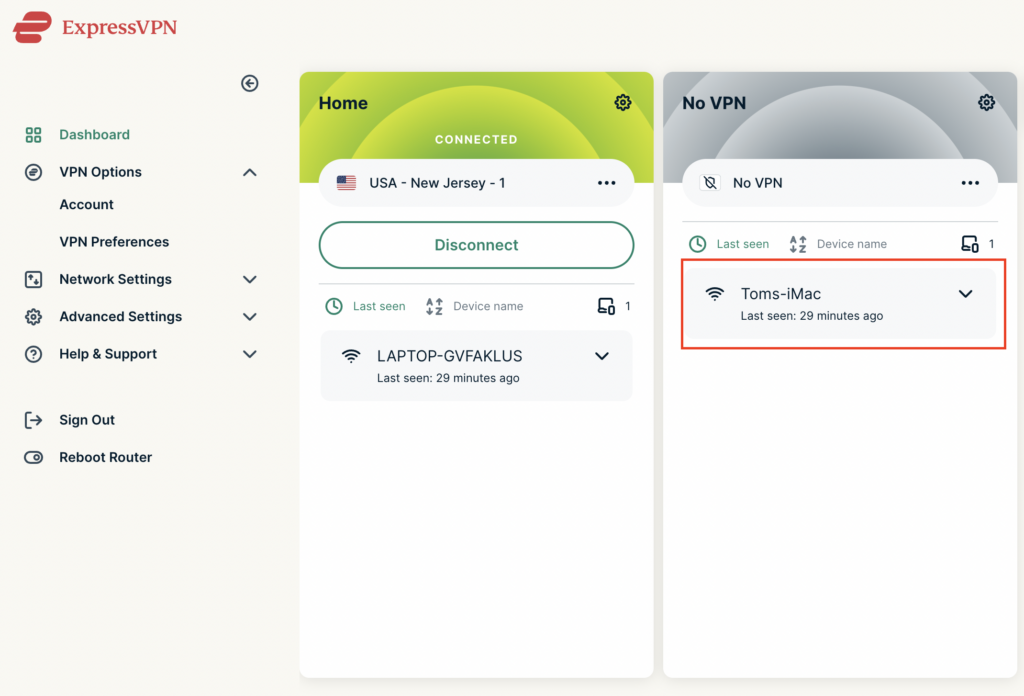
4. Select VPN Off on the right hand side of the menu.

ExpressVPN select No VPN

5. Click and drag the device that you want to bypass the VPN tunnel to the No VPN area.

ExpressVPN No VPN select device
ExpressVPN No VPN select device 2

The devices assigned to No VPN will now correct directly to your ISP internet while the devices in the VPN group will remain connected to the VPN server.

AirVPN Manual OpenVPN Setup

TeamFlashRouters · Jun 11, 2019 ·

Preparing for Manual AirVPN Setup

Obtain your AirVPN OpenVPN Information

If you are not already a AirVPN user Sign Up Now.

1. Log in to your account on the AirVPN website.

AIRVPN OpenVPN Client Login for FlashRouter DD-WRT VPN Configuration

2. Click on the Client Area tab.

AIRVPN OpenVPN Client Area for FlashRouter DD-WRT VPN Configuration

3. Click on the Config Generator subtab.

AIRVPN OpenVPN Configuration Generator for FlashRouter DD-WRT VPN Configuration

4. Click on the Router icon under Choose your Operating System.

AIRVPN OpenVPN FlashRouter DD-WRT VPN Configuration

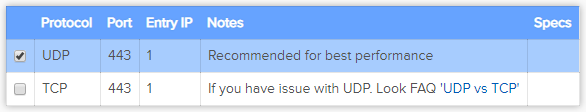
5. Select a Protocol under the Protocols section. We recommend UDP.

Select AIRVPN OpenVPN Encryption Protocol for FlashRouter DD-WRT VPN Configuration

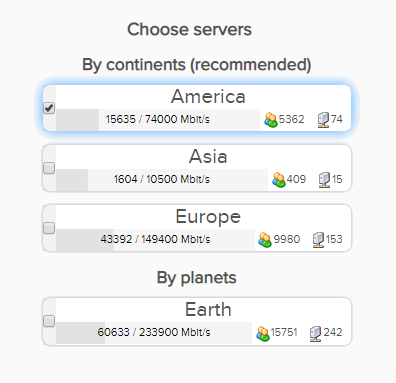
6. Select one option under the Choose Servers section. AirVPN sorts these servers by Planet, Continent, Country, and Single servers. Choose whichever best suits your needs.

Sort AIRVPN OpenVPN Specific Certificates for FlashRouter DD-WRT VPN Configuration

7. Scroll down towards the bottom of the page and click on Generate.

Generate AIRVPN OpenVPN Specific Certificates for FlashRouter DD-WRT VPN Configuration

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You will be copying the Server IP/Name, client.crt and client.key from this file.

Please note, all VPN servers have different keys and certificates. If you wish to change servers in the future, you will have to go through steps 1-7 again.

DD-WRT Router Setup for AirVPN

Navigate to Services > VPN

Enter AirVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you selected in your account. Be sure there are no extra spaces or characters.

Port

443

Tunnel Device

TUN

Tunnel Protocol

UDP or TCP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA1

User Pass Authentication

Disable

Advanced Options

Enable

TLS Cipher

None

LZO Compression

No

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

TLS Auth Key

—–BEGIN OpenVPN Static key V1—–
7bb7a23a0f5f28d01e792df68f1764ab
f2688719288808bf58e8a2d4f9354ecf
132625dfb895fc3f6330ae1e868e4dfa
c164c0931593d7f9a7da9595cf353433
8896e1d0a987a0d19838944af8fea4e5
215a3a0c76f4c67d5a4aee6a53be66a4
c88b84f850030840fb30f8550ed8068f
35c1ef34ee8f40a0ea5862dfb6f8d3c5
7ab5e27ac2799cf93e8765ff63cd8cd8
6b391b813925cd373bb202796f64d16f
003d042ca828d1b07f18ba1d0cb0323d
df3ee9287e9e084e655699efb3cffa92
3626946fa372e7beee245e7a95b4c1d8
7d16cae685218d4b8afc019b22e41083
476ee9883fe666d236301e55b2062551
4d91c8a69467a758293994df1e6fa7ae
—–END OpenVPN Static key V1—–

CA Cert

—–BEGIN CERTIFICATE—–
MIIGVDCCBDygAwIBAgIJAIzYQ+/kXyADMA0GCSqGSIb3DQEBBQUAMHkxCzAJBgNV
BAYTAklUMQswCQYDVQQIEwJJVDEQMA4GA1UEBxMHUGVydWdpYTETMBEGA1UEChMK
YWlydnBuLm9yZzEWMBQGA1UEAxMNYWlydnBuLm9yZyBDQTEeMBwGCSqGSIb3DQEJ
ARYPaW5mb0BhaXJ2cG4ub3JnMB4XDTE0MDQxMTEwMTU0NVoXDTI0MDQwODEwMTU0
NVoweTELMAkGA1UEBhMCSVQxCzAJBgNVBAgTAklUMRAwDgYDVQQHEwdQZXJ1Z2lh
MRMwEQYDVQQKEwphaXJ2cG4ub3JnMRYwFAYDVQQDEw1haXJ2cG4ub3JnIENBMR4w
HAYJKoZIhvcNAQkBFg9pbmZvQGFpcnZwbi5vcmcwggIiMA0GCSqGSIb3DQEBAQUA
A4ICDwAwggIKAoICAQDGG3ZrJbP61PNjGc4mjTx0TLkUjP7IXZ3wnpPjwF/lwK9n
HgRqoPL0KY/ABJuzMViD8ChtwthNfc7PuJ7vSPtN84lSJ4JGmTxvZkNeLQLZsu1F
f88OcSpjW5ErBM05iVBeF8/ljwaajgFfbgop9W/UK5yMji4qgq5KHxxXqsB8R4rC
eFpWHoNTwFjvXhtVyMgXiT9XAh/vBYim021m8onio4K48q7YRZ4qU8gvE79h5M0g
miIlt6v1vaZskw9cqIBbCYefGMsvBRk2x824ChPf6FazMwAnQHsuBHt6eXAARvfF
DBDanzPHlRSiCP6Je6Vod/MPyepiTZgjgk2VxYUc1ohNxEEGzPGTayeNzLJUldou
P4B+tjJ0Xly30+wvlahADlqjtz3CGQmKMj7btZjd+Uo61B7gau5YiXR/IO7ZpFAC
PCZJSbrwFs6rt9Kewqk8zslfVIro8oDndXRkVsa/c8Qmd6ZE7V+oMGl2OggdWOLl
mDEjkytzx+Bw2sSSalJRAQmOQO8V0anOI6jGYLuU2jnFDsnqSHuwIK11xb6iHmh7
ONsRLUtQ+d64TzB00w2M0fCvGqUIp0N+lf7nsZKsEcU08OoHQYUuwX75ZEOYNSZJ
rqAXohcXdVUHqgRlJRErfSkjcGMM0yqjHkvopcnBIRXKMYTDVXvzRJboyJiVpQID
AQABo4HeMIHbMB0GA1UdDgQWBBTlFdcTqJ4x49Ew1/Ef9OJj0lDIiDCBqwYDVR0j
BIGjMIGggBTlFdcTqJ4x49Ew1/Ef9OJj0lDIiKF9pHsweTELMAkGA1UEBhMCSVQx
CzAJBgNVBAgTAklUMRAwDgYDVQQHEwdQZXJ1Z2lhMRMwEQYDVQQKEwphaXJ2cG4u
b3JnMRYwFAYDVQQDEw1haXJ2cG4ub3JnIENBMR4wHAYJKoZIhvcNAQkBFg9pbmZv
QGFpcnZwbi5vcmeCCQCM2EPv5F8gAzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEB
BQUAA4ICAQCUVAQteCtgNQiZMXV0wCdqivlxlCCuj5sD+XvEuoDqb7dH70u1KQ90
OAbkeotHlIbqJU10xWtvHEjnXg8QG5VOzaWnWWev+ivdPCkGWe8E7C8shsr4WMlA
EF8PPRtzOwCKayxjR713x+Tc2Sb6/rDsXcY5LV6RNmE9HWBM6IoHdqruR8PHkYge
2CPXMuLByEADri6xmvussAjCWEDplJNY7tQsUGT7vjrwrNSNBx/SvxkXnWBj0wYa
EwNu43jrjcRfM/3eGcKDX3cQqTfRQd3j3OA7zmJOXPeExRUIWZTNCvQItGy1TJdw
JTphflw15Bui4l2mYfDqK08zm4aJODrCjoQnVVzM5uOzSTOjmneI6AHj3MjjL3A/
CFA5PCSquBhUycF4UEVf3aPGiV0vAthCBUqM4eKE+rbjWPSaxKghVdr/S82o7Wzz
9mGwnOZDqWk+8AWSsGBjamMk3mNMR45E9FRfPF/dyjOSbVyyTsd1VzlTFEJa0wjB
l3yq3r3iZAM3UtevocAyTEAu0vDYBbS6TgWmWEDOizybB0hNrTx5u/SEI0Kwcthc
rilYxD+n4kmV7TvIR0ZSaYpgYALWQV27zOqY51Ol4UT98WCOokge9HdoFcGJU2Uj
5VneGp14/Oklh7y6BxxxGC3zNGjKGNQYuHGTIgw1DoASmRUdkPkn/w==
—–END CERTIFICATE—–

Public Client Cert

Copy and paste all contents between <cert> and </cert> make sure to also include the following lines when copying and pasting:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

Copy and paste all contents between <key> and </key> make sure to also include the following lines when copying and pasting:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful AirVPN connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit whatismyipaddress.com to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to AirVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the AirVPN server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new client.key and private.key
  4. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Privacy Hero Adblocking Malware and Phishing Prevention Setup

TeamFlashRouters · Apr 3, 2023 ·

Your Privacy Hero router uses Cloud Based router management which means you can access the router settings from anywhere on any device that has an internet connection. You can follow these steps while connected to your phone, other Wi-Fi network, or the Privacy Hero network.

Use these steps to enable Privacy Hero’s adblocking, malware, and phishing prevention settings to add extra security to your network.

1. From any device that has a browser such as a computer, smartphone, or tablet visit app.privacyhero.com

App.PrivacyHero.com

2. Enter your Privacy Hero account email and password. Click Login.

Privacy Hero Access Settings

If you have not created your Privacy Hero account yet please follow these instructions.

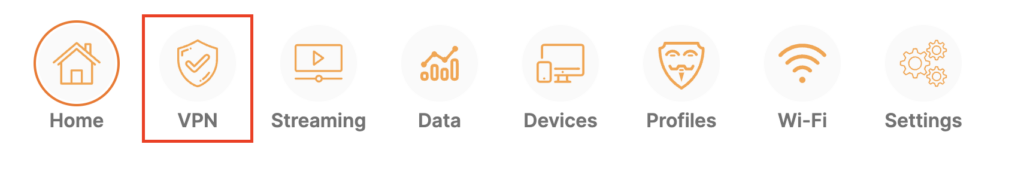
3. Click the VPN symbol.

Privacy Hero Setup VPN

4. Toggle the Adblocking and Malware & Phishing switches to On.

Privacy Hero Adblocking Malware and Phishing

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

IPVanish TP-Link OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for IPVanish TP-Link Setup

Download your IPVanish .ovpn file

If you are not already an IPVanish user Sign Up Now.

1. Log in to your account on the IPVanish website.

IPVanish login

2. Successfully log in with your account information then go to IPVanish .ovpn file page.

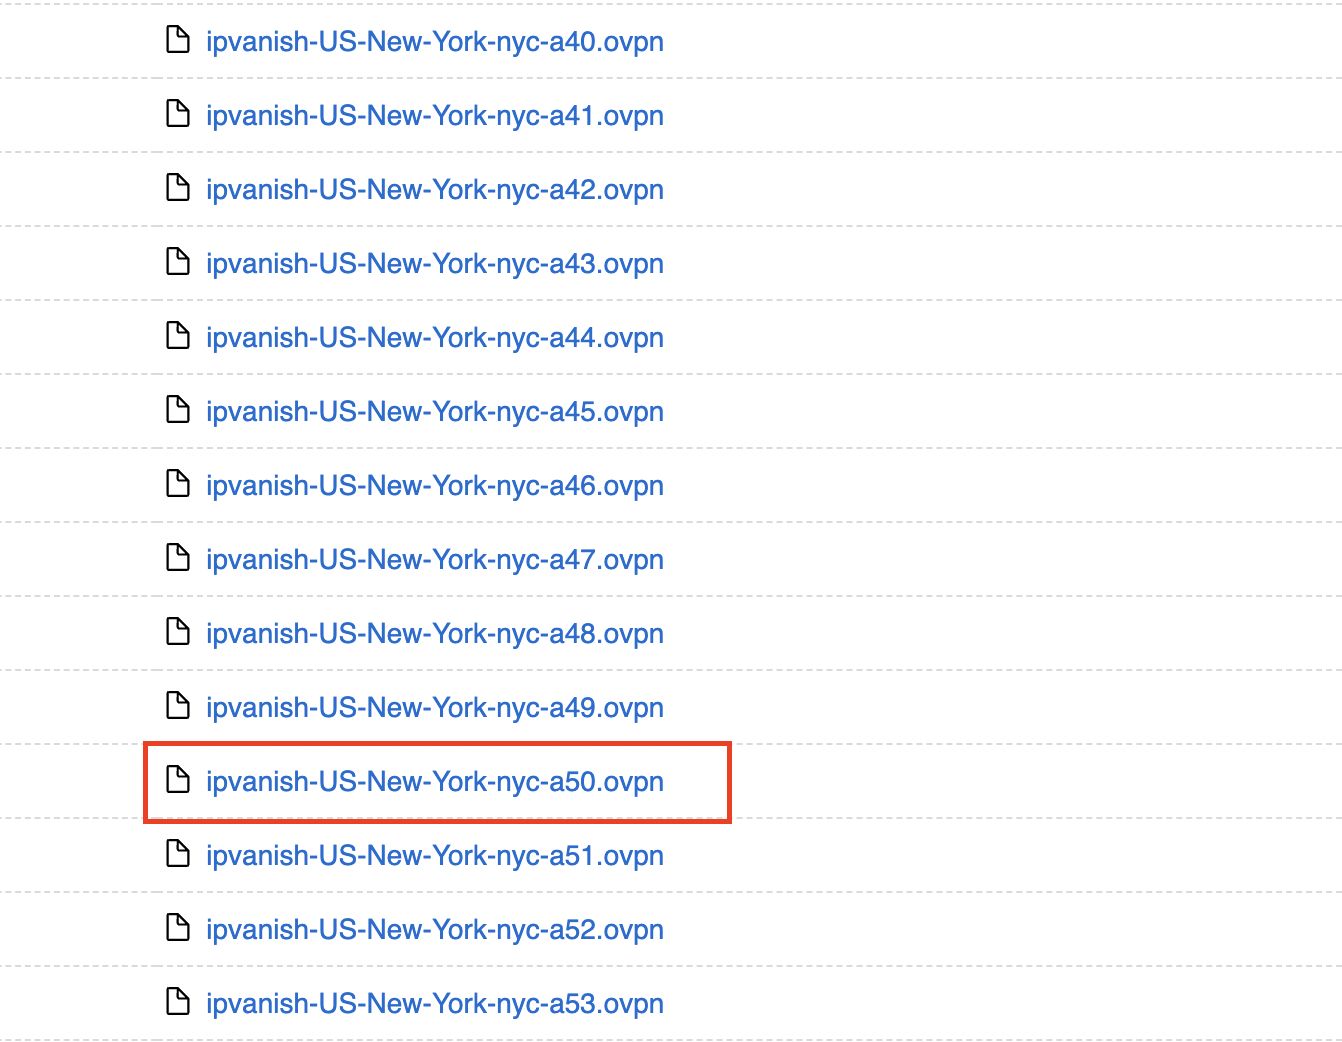
3. Click on the .ovpn file for the server location you want to use to dowloand the .ovpn file. Do not open this file.

IPVanish download ovpn

TP-Link Router Setup for IPVanish

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location. Our example server was New York so I have entered in IPVanish New York.

Set the VPN Type to OpenVPN.

In the Username and Password fields paste in the IPVanish email and password you use to successfully login to your IPVanish website account.

Click Browse and select the .ovpn file you downloaded earlier. Then click Save.

TP-Link IPVanish

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link IPVanish Connected

Verify a successful IPVanish connection

  1. You should now see a CONNECTED message.
  2. Visit IPVanish’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to IPVanish.

How to change the IPVanish server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark TP-Link WireGuard Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for Surfshark TP-Link Setup

Download your Surfshark .conf file

If you are not already a Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

Surfshark Account Login

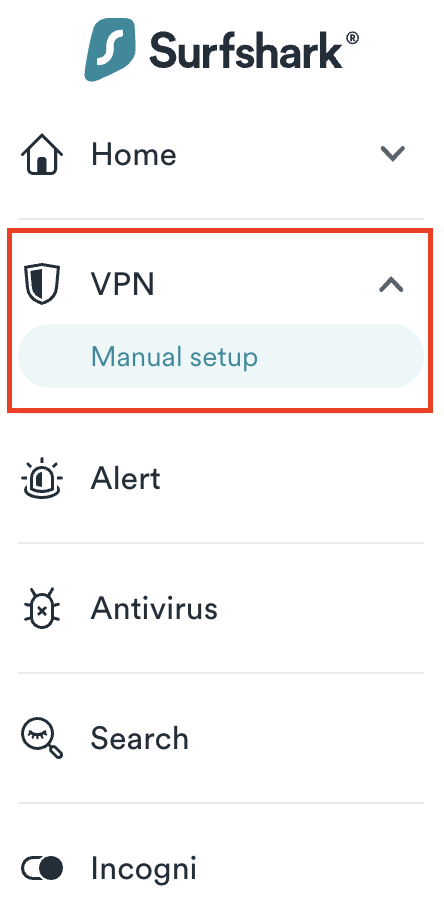
2. Click VPN Manual Setup.

Surfshark VPN Manual Setup

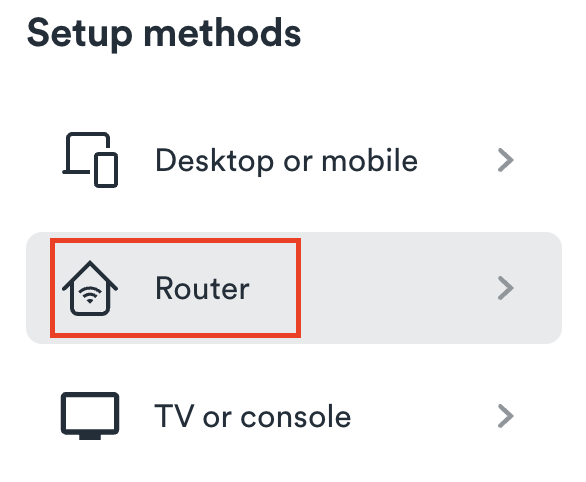
3. Select Router as the Setup method.

Surfshark setup method Router

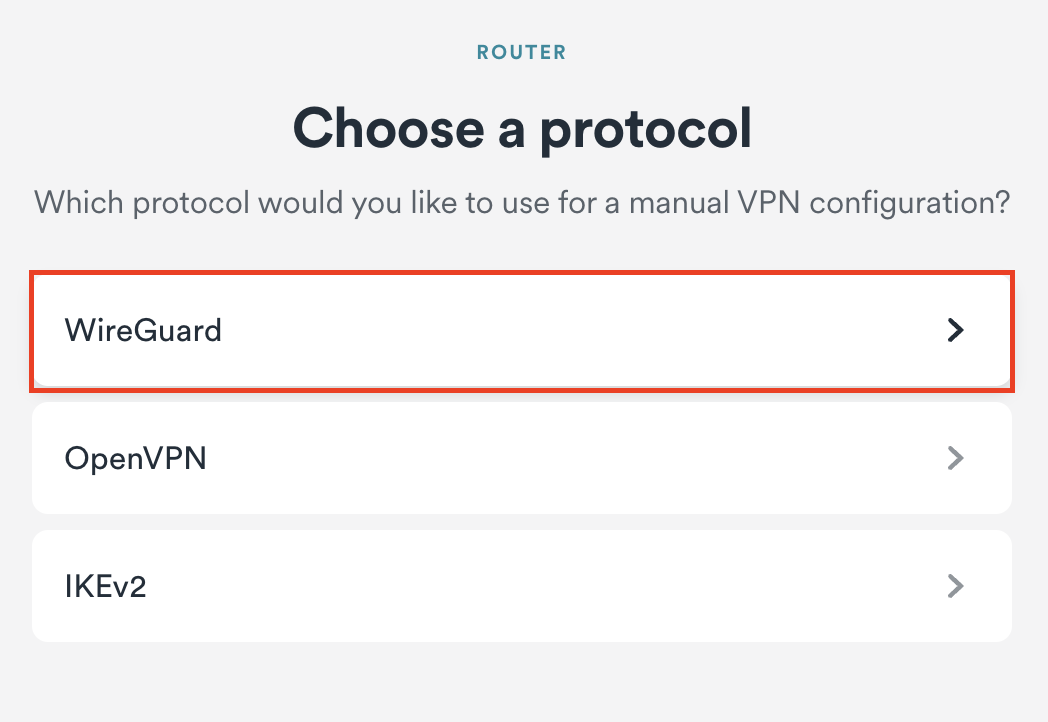
4. Select WireGuard as the Protocol.

Surfshark select WireGuard

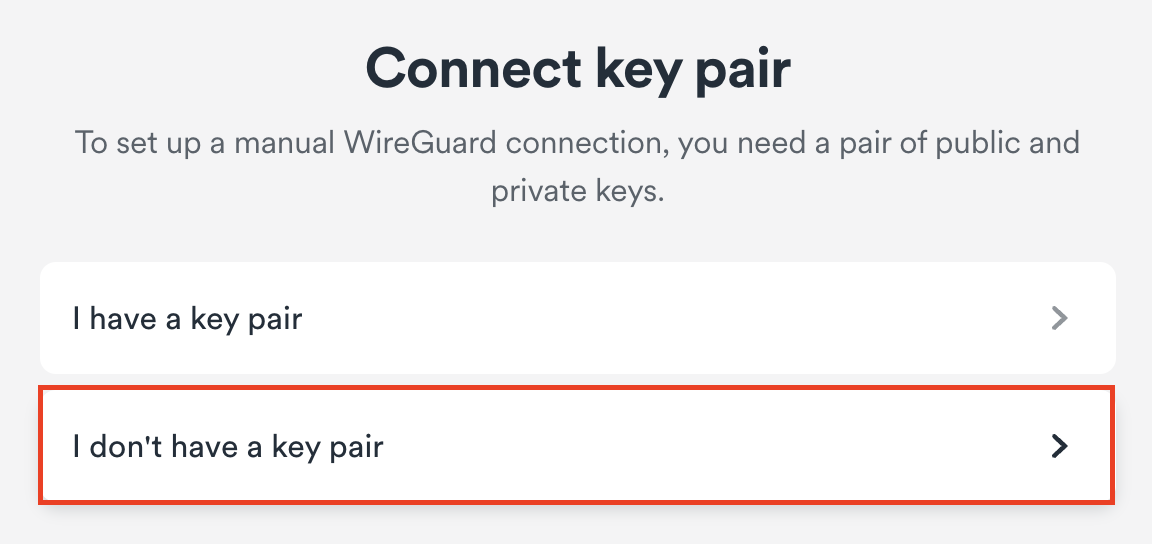
5. Select I don’t have a key pair.

Surfshark No Key Pair

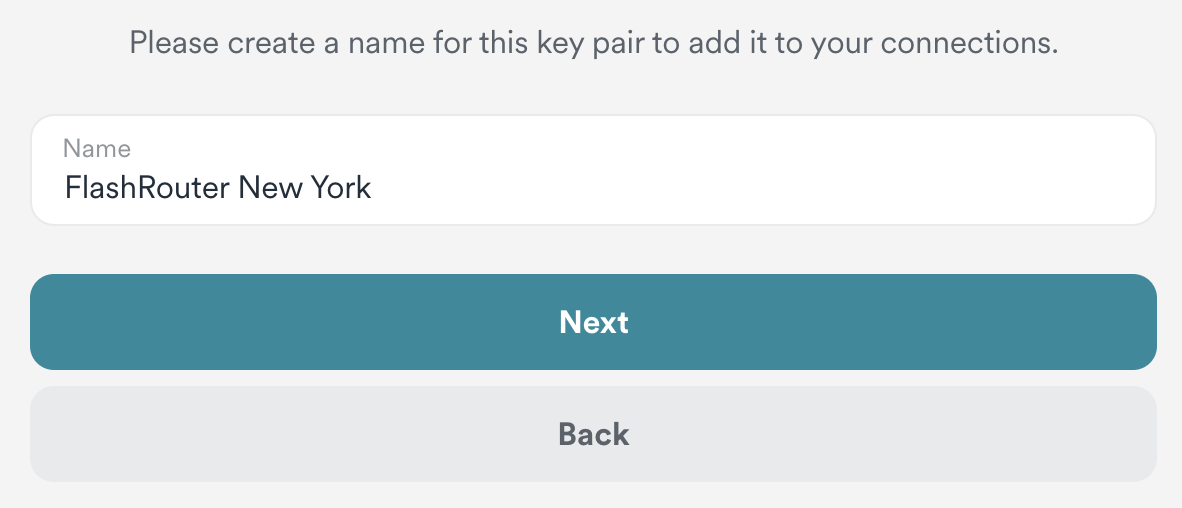
6. Enter FlashRouter as the name of the connection and click Next.

Surfshark Connection Name

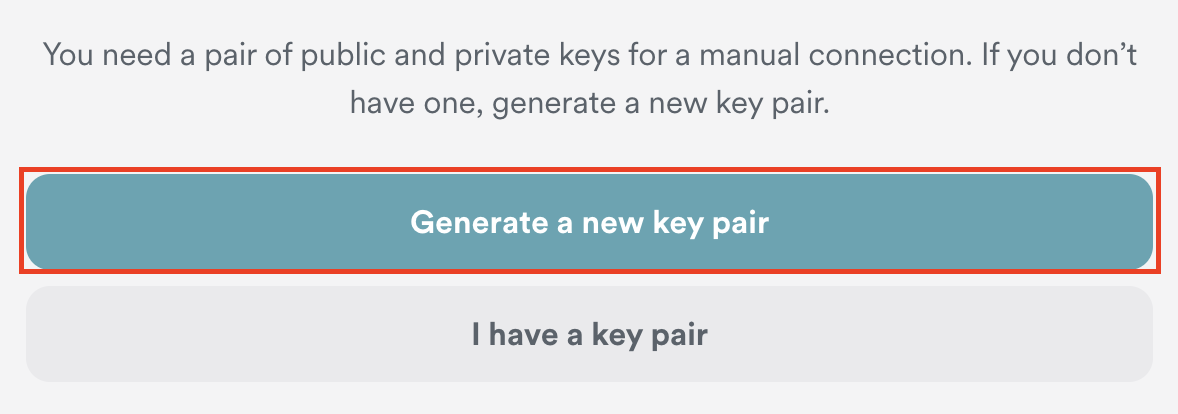
7. Click Generate a new key pair.

Surfshark Generate new Key Pair

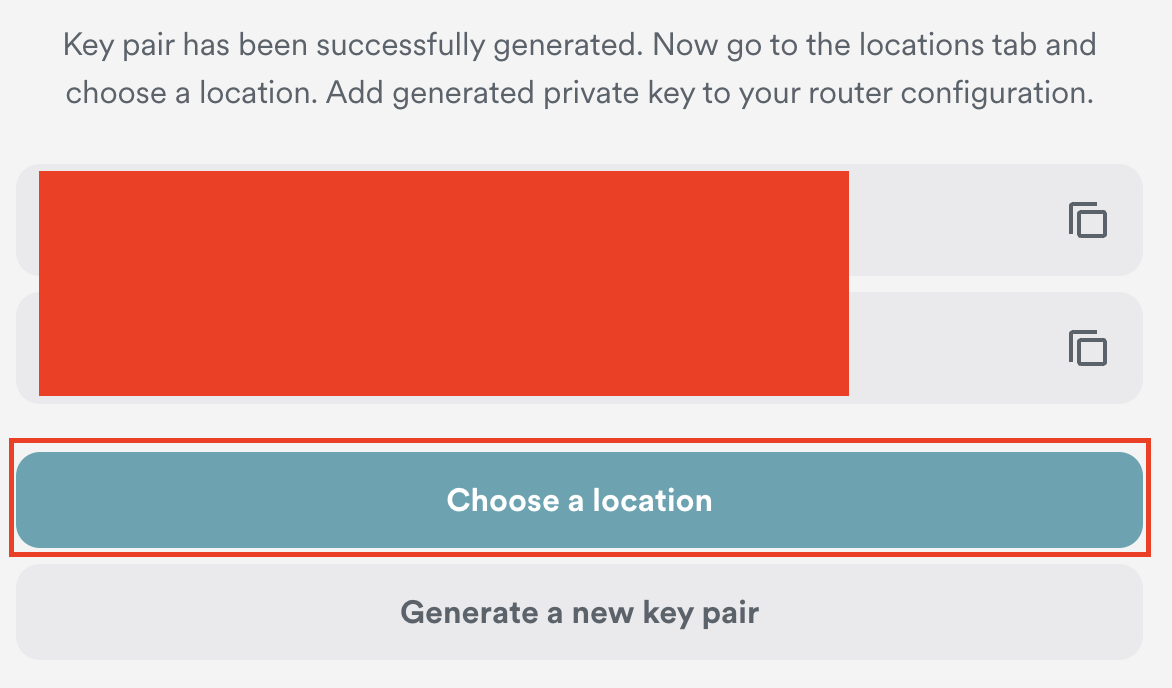
8. Click Choose a location.

Surfshark Choose a Location

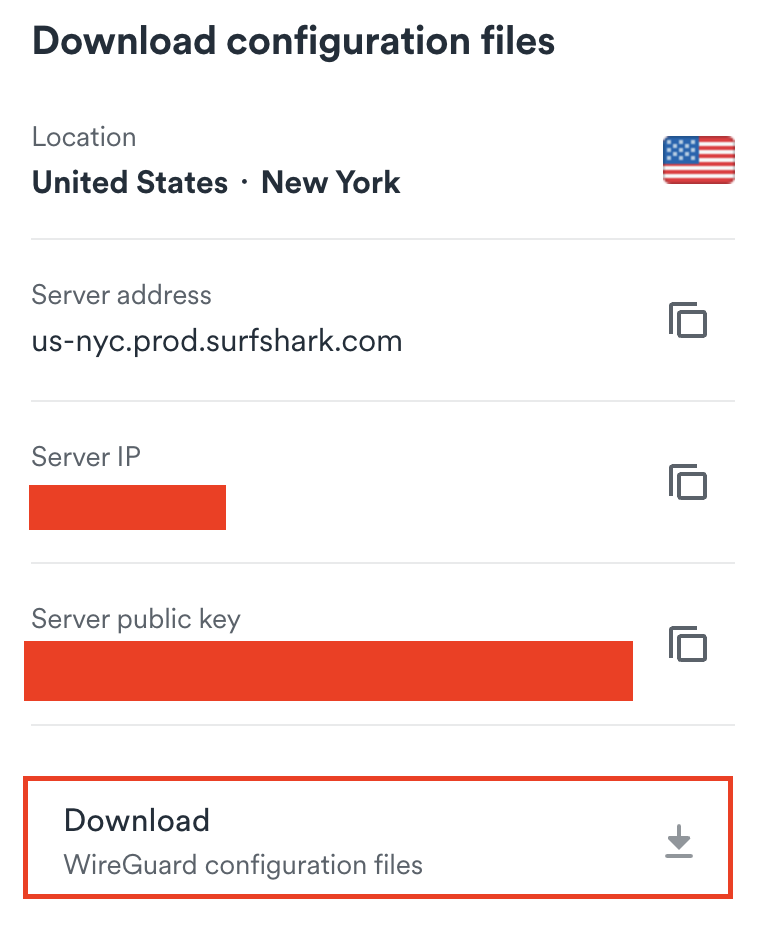
9. Select the server location you want to connect to. Unless you need a specific location we recommend using Surfshark’s recommended Fastest server. Click Download to download the .conf file for this Surfshark server location.

Surfshark download conf file

TP-Link Router Setup for Surfshark

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

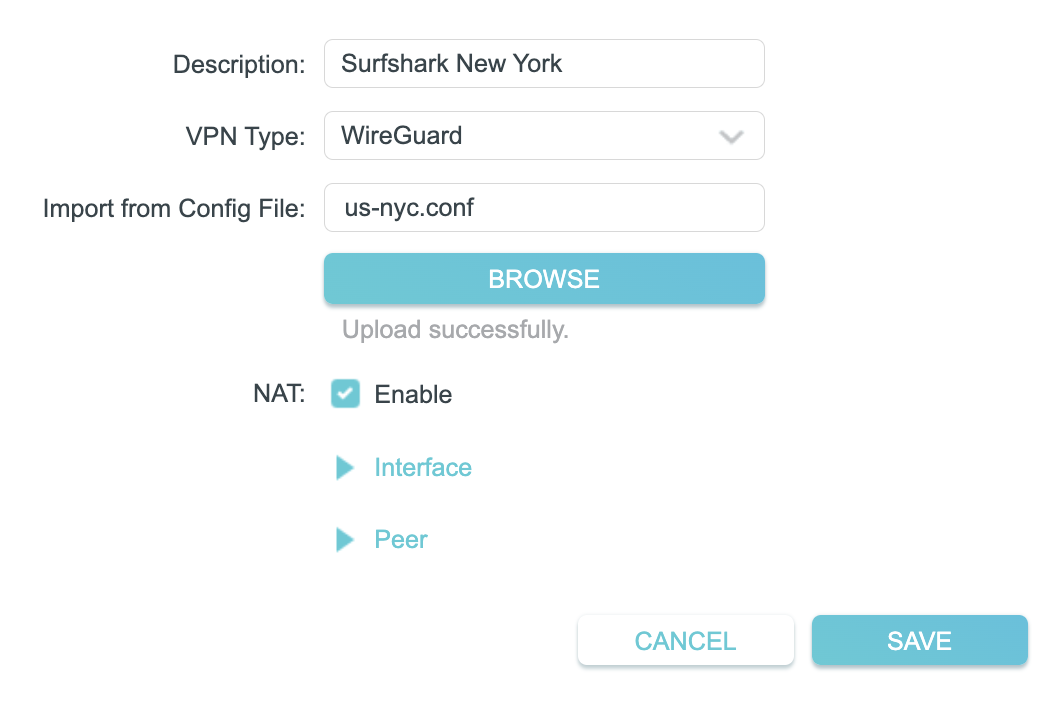
5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location. Our example server was New York so I have entered in Surfshark New York.

Set the VPN Type to WireGuard.

Click Browse and select the .conf file you downloaded earlier. Then click Save.

TP-Link Surfshark WireGuard

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

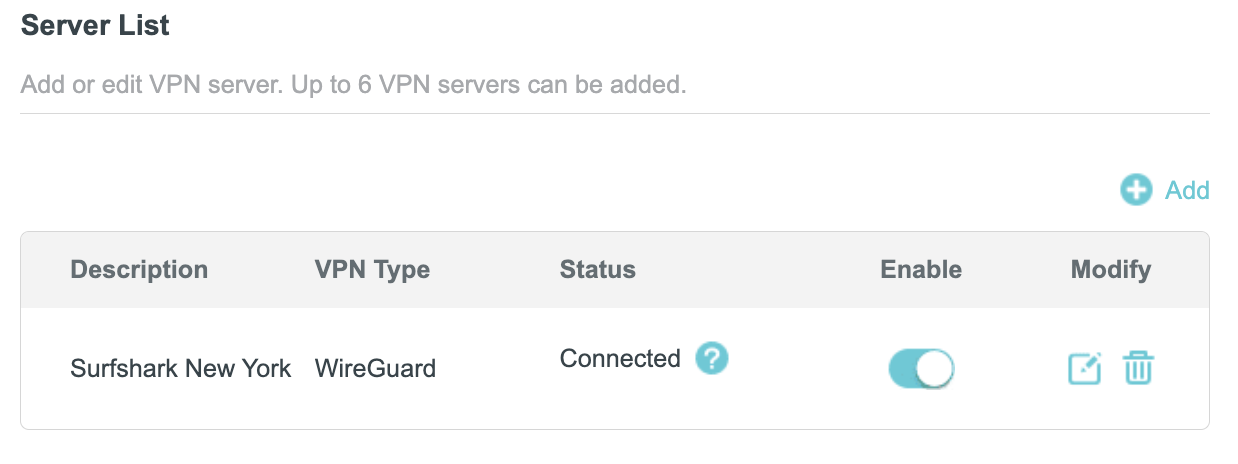
8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link Surfshark WireGuard Connected

Verify a successful Surfshark connection

  1. You should now see a CONNECTED message.
  2. Visit Surfshark’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark.

How to change the Surfshark server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Surfshark TP-Link OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for Surfshark TP-Link Setup

Download your Surfshark .ovpn file

If you are not already a Surfshark user Sign Up Now.

1. Log in to your account on the Surfshark website.

Surfshark Account Login

2. Click VPN Manual Setup.

Surfshark VPN Manual Setup

3. Select Router as the Setup method.

Surfshark setup method Router

4. Select OpenVPN as the Protocol.

Surfshark OpenVPN Protocol

5. Copy and paste your Surfshark manual username and password to a secure location. This is the username and password you will enter into the router settings to connect to Surfshark.

Surfshark OpenVPN credentials

6. Click Location and select the server location you want to connect to. Unless you need a specific location we recommend using Surfshark’s recommended Fastest server. Click Download to download the UDP .ovpn file for this Surfshark server location.

Surfshark download .ovpn file

TP-Link Router Setup for Surfshark

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location. Our example server was New York so I have entered in Surfshark New York.

Set the VPN Type to OpenVPN.

In the Username and Password fields paste in the Surfshark username and password we obtained earlier.

Click Browse and select the .ovpn file you downloaded earlier. Then click Save.

TP-Link Surfshark OpenVPN

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link Surfshark OpenVPN connected

Verify a successful Surfshark connection

  1. You should now see a CONNECTED message.
  2. Visit Surfshark’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Surfshark.

How to change the Surfshark server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN TP-Link WireGuard Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for ProtonVPN TP-Link Setup

Download your ProtonVPN .conf file

If you are not already an ProtonVPN user Sign Up Now.

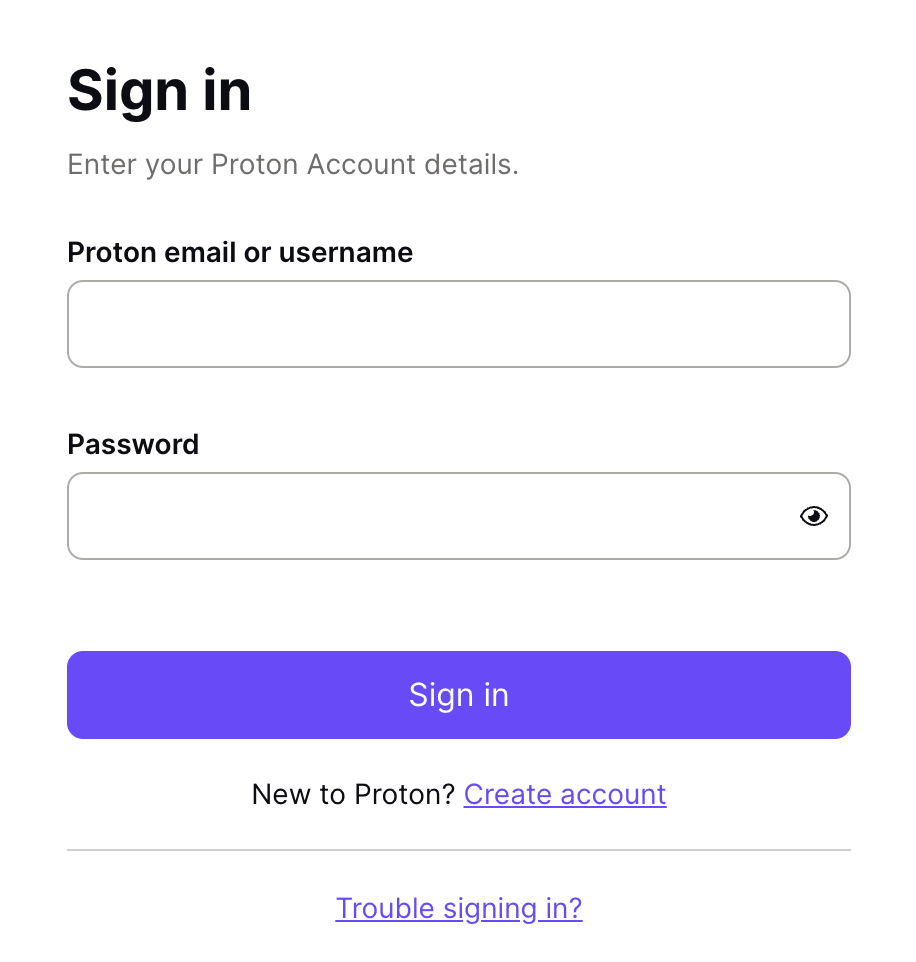
1. Log in to your account on the ProtonVPN website.

ProtonVPN Account Sign in

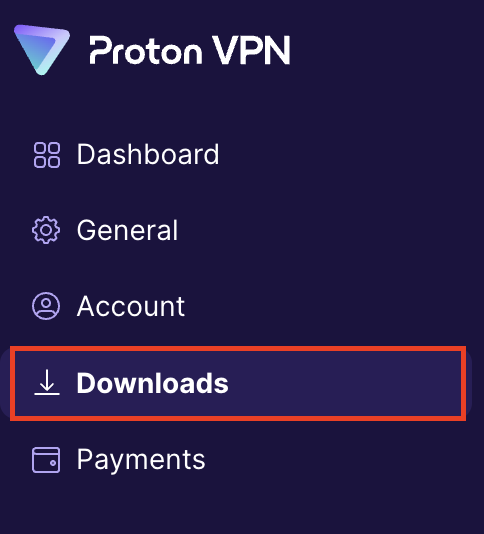
2. Click Downloads.

ProtonVPN Downloads

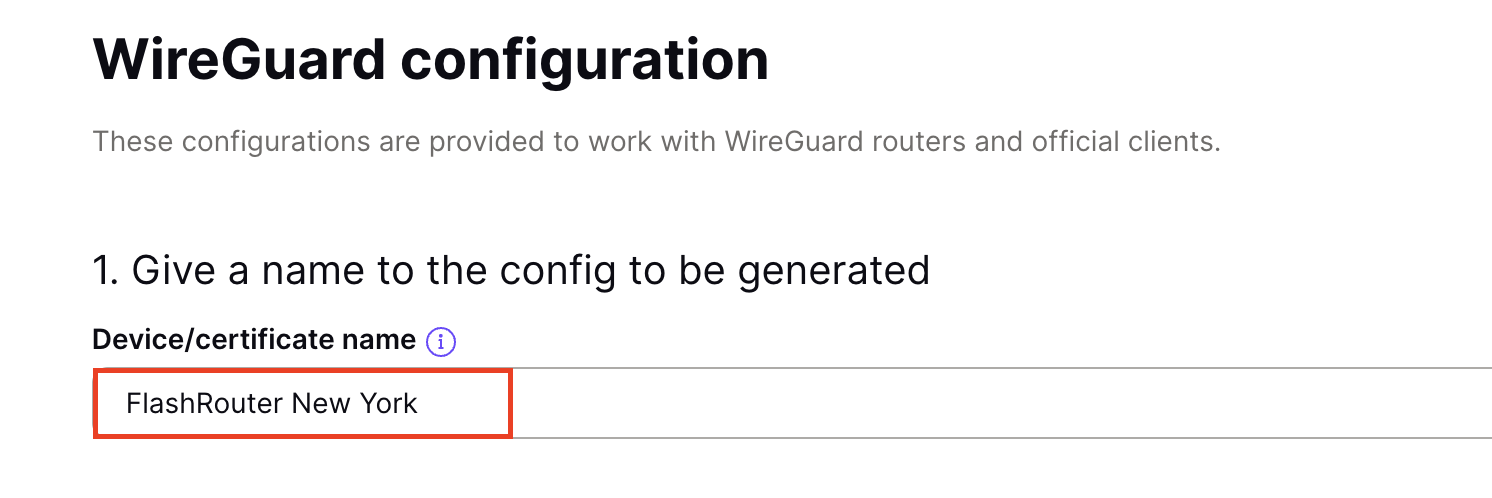
3. Scroll down to WireGuard configuration and name the device FlashRouter.

ProtonVPN WireGuard Configuration Name

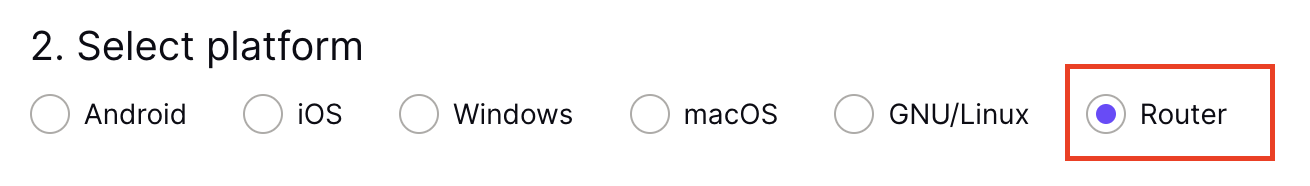
4. Select Router as the platform.

ProtonVPN WireGuard select Platform

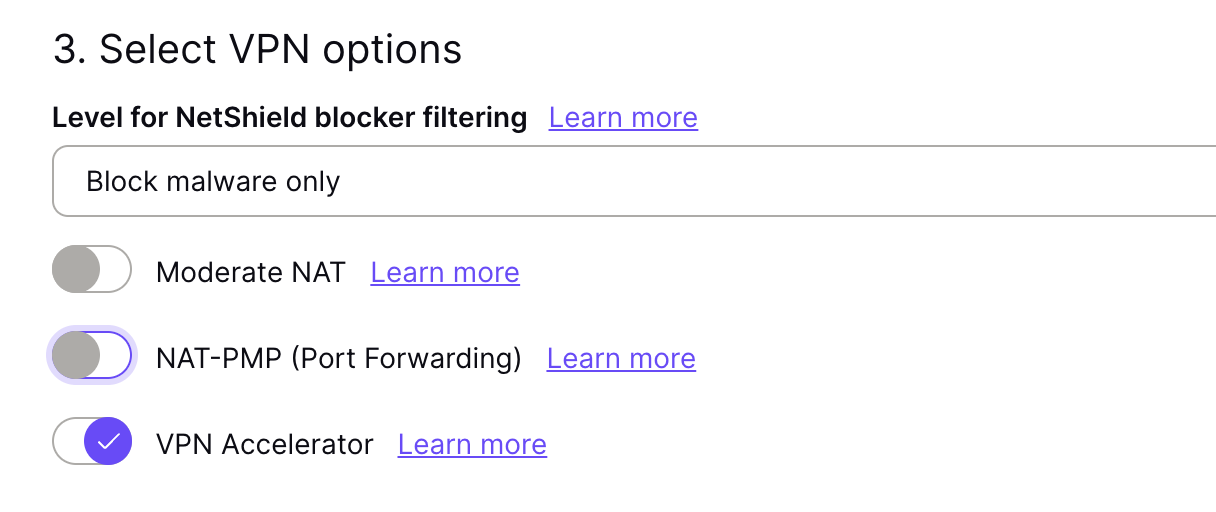
5. Select the VPN options that best fit your needs. We typically use the settings as seen in the screenshot here if you are unsure.

ProtonVPN WireGuard VPN options

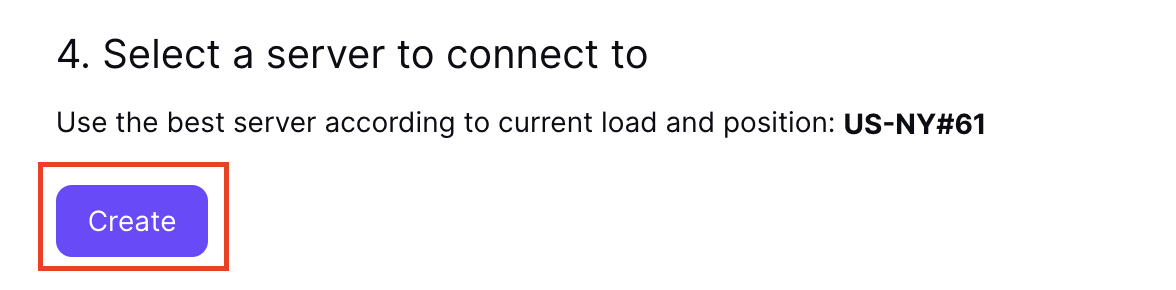
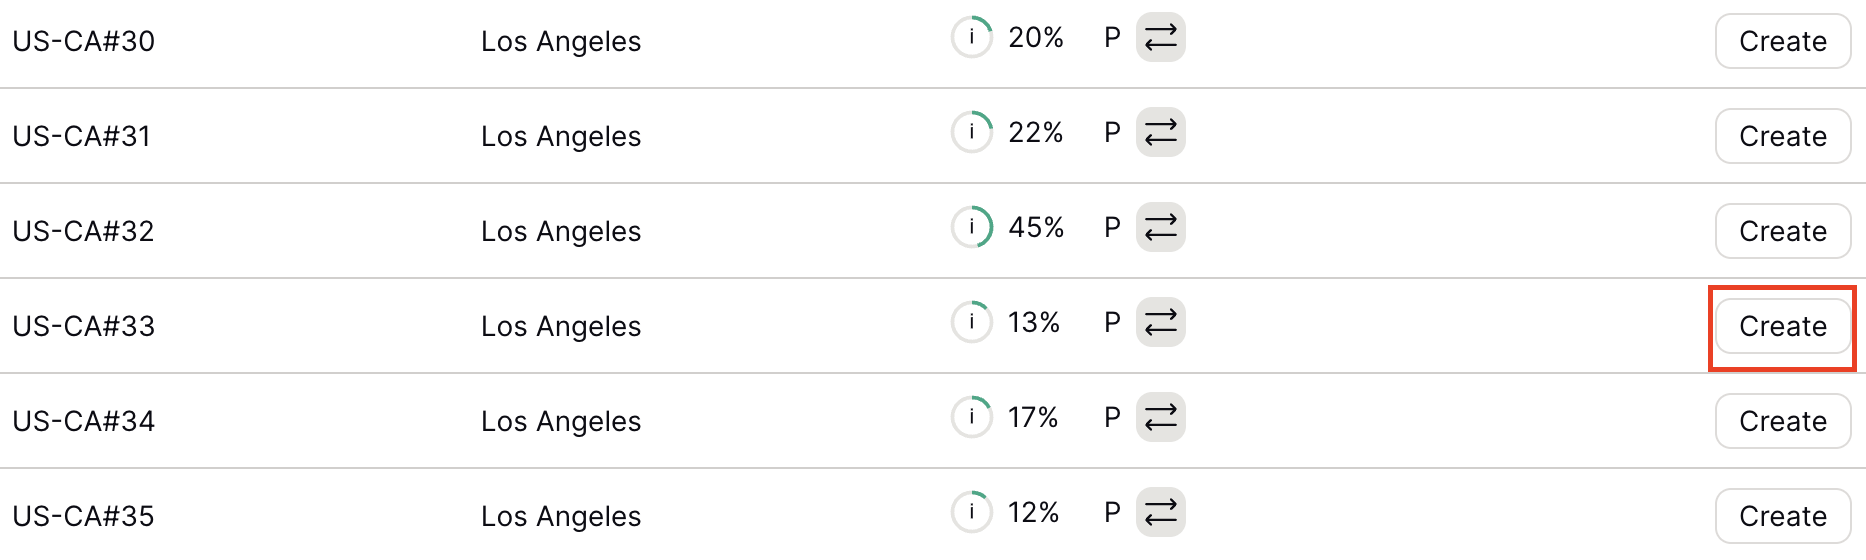
6. Next select the server that you would like to connect to and click Create. At the top of the page you’ll see ProtonVPN’s recommended server which we recommend using unless you need to connect to a specific location.

If you need a specific server location find it in the list and click Create.

ProtonVPN WireGuard recommended server
ProtonVPN WireGuard specific server

7. After clicking Create a new window will appear. Click Download to download the .conf file to your computer.

TP-Link Router Setup for ProtonVPN

Login to TP-Link firmware settings in a browser on any computer or smart device connected to the FlashRouter’s network.

1. Navigate to the Advanced tab.

TP-Link Advanced settings

2. Navigate to the VPN Client tab.

TP-Link VPN Client

3. Check the Enable box next to VPN Client. Then click Save at the bottom of the page.

TP-Link VPN Client enable

4. Click the Add button in the Server List area.

TP-Link Add server button

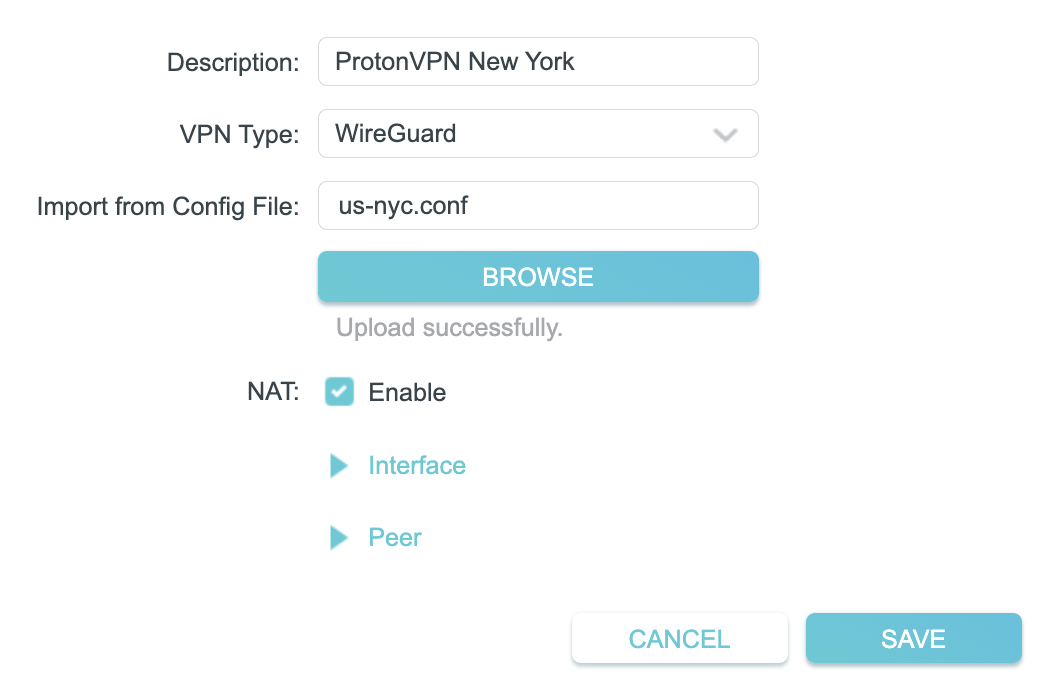
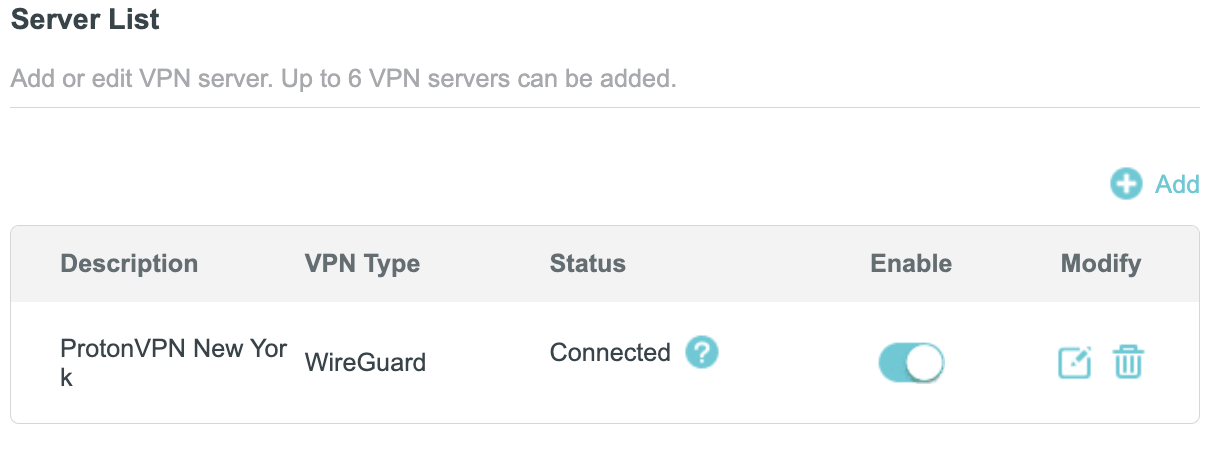
5. In the Description field enter in the name you’d like to use for this WireGuard Client profile. We typically advise entering in the location. Our example server was New York so I have entered in ProtonVPN New York.

Set the VPN Type to WireGuard.

Click Browse and select the .conf file you downloaded earlier. Then click Save.

TP-Link ProtonVPN WireGuard

By default no devices will be assigned to the VPN Tunnel. With TP-Link firmware you must manually assign the devices that you want connected to the VPN tunnel. Proceed with the next steps to do so for all devices you want connected to VPN.

6. Click the Add button in the Device List area.

TP-Link add devices to VPN tunnel

7. A list of devices connected to the FlashRouter’s network will appear. Check the devices that you want to connect to VPN. Then click OK.

TP-Link select devices to add to VPN tunnel

8. Now that the devices have been assigned to the VPN connection click the Enable toggle in the Server List area.

TP-Link ProtonVPN WireGuard connected

Verify a successful ProtonVPN connection

  1. You should now see a CONNECTED message.
  2. Visit ProtonVPN’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ProtonVPN.

How to change the ProtonVPN server

  1. Follow the steps at the top of the page to obtain a new .conf file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Hotspot Shield Manual OpenVPN Setup

TeamFlashRouters · Jul 15, 2020 ·

Preparing for Manual Hotspot Shield Setup

Obtain your Hotspot Shield OpenVPN Information

If you are not already a Hotspot Shield user Sign Up Now.

1. Log in to your account on the Hotspot Shield website.

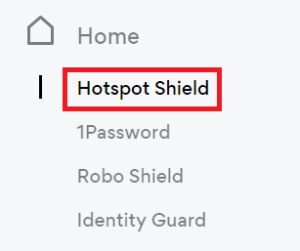
2. Click Hotspot Shield on the left side navigation.

Hotspot Shield - Website Admin

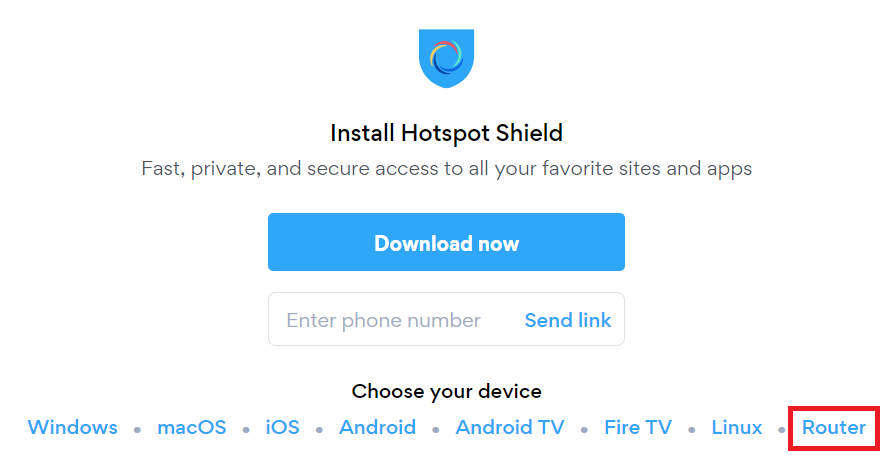
3. Under Choose your device click Router.

Hotspot Shield - Select Router

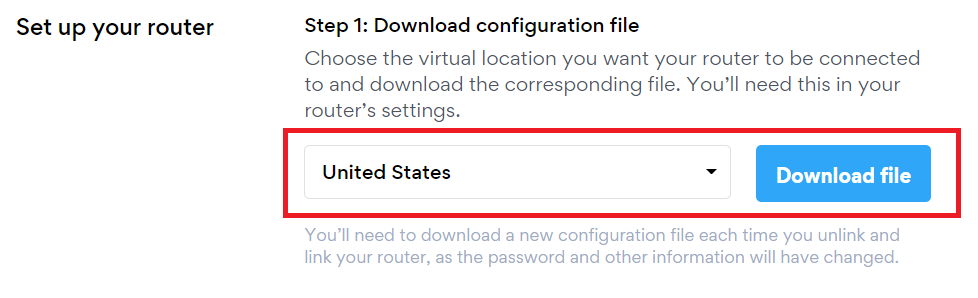
4. In the Set up your router section Select your desired virtual location and then click Download file.

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the <cert> and <key> from the .ovpn file. All Hotspot Shield servers have different keys and certificates.

Hotspot Shield - Download Configuration File

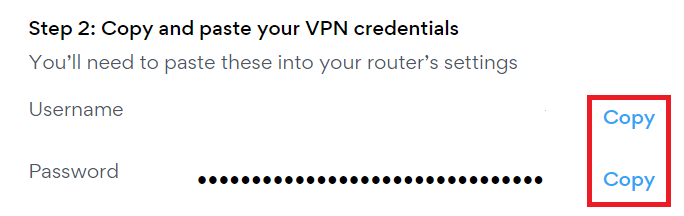
5. Copy the VPN Username, and Password that appear under Step 2 to a notepad, you will need this information later in the setup process.

Hotspot Shield - OpenVPN username and password

DD-WRT Router Setup for Hotspot Shield

Navigate to Services > VPN

Enter Hotspot Shield settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote universitycalendar.us 8041
universitycalendar.us is your Hotspot Shield server name. Enter the server name in this field.

Port

8041

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your Hotspot Shield account.

Password

Enter the Password you obtained in your Hotspot Shield account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

No

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping 15
ping-restart 0
reneg-sec 0
remote-cert-tls server

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIFazCCA1OgAwIBAgIRAIIQz7DSQONZRGPgu2OCiwAwDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTUwNjA0MTEwNDM4
WhcNMzUwNjA0MTEwNDM4WjBPMQswCQYDVQQGEwJVUzEpMCcGA1UEChMgSW50ZXJu
ZXQgU2VjdXJpdHkgUmVzZWFyY2ggR3JvdXAxFTATBgNVBAMTDElTUkcgUm9vdCBY
MTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAK3oJHP0FDfzm54rVygc
h77ct984kIxuPOZXoHj3dcKi/vVqbvYATyjb3miGbESTtrFj/RQSa78f0uoxmyF+
0TM8ukj13Xnfs7j/EvEhmkvBioZxaUpmZmyPfjxwv60pIgbz5MDmgK7iS4+3mX6U
A5/TR5d8mUgjU+g4rk8Kb4Mu0UlXjIB0ttov0DiNewNwIRt18jA8+o+u3dpjq+sW
T8KOEUt+zwvo/7V3LvSye0rgTBIlDHCNAymg4VMk7BPZ7hm/ELNKjD+Jo2FR3qyH
B5T0Y3HsLuJvW5iB4YlcNHlsdu87kGJ55tukmi8mxdAQ4Q7e2RCOFvu396j3x+UC
B5iPNgiV5+I3lg02dZ77DnKxHZu8A/lJBdiB3QW0KtZB6awBdpUKD9jf1b0SHzUv
KBds0pjBqAlkd25HN7rOrFleaJ1/ctaJxQZBKT5ZPt0m9STJEadao0xAH0ahmbWn
OlFuhjuefXKnEgV4We0+UXgVCwOPjdAvBbI+e0ocS3MFEvzG6uBQE3xDk3SzynTn
jh8BCNAw1FtxNrQHusEwMFxIt4I7mKZ9YIqioymCzLq9gwQbooMDQaHWBfEbwrbw
qHyGO0aoSCqI3Haadr8faqU9GY/rOPNk3sgrDQoo//fb4hVC1CLQJ13hef4Y53CI
rU7m2Ys6xt0nUW7/vGT1M0NPAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNV
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBR5tFnme7bl5AFzgAiIyBpY9umbbjANBgkq
hkiG9w0BAQsFAAOCAgEAVR9YqbyyqFDQDLHYGmkgJykIrGF1XIpu+ILlaS/V9lZL
ubhzEFnTIZd+50xx+7LSYK05qAvqFyFWhfFQDlnrzuBZ6brJFe+GnY+EgPbk6ZGQ
3BebYhtF8GaV0nxvwuo77x/Py9auJ/GpsMiu/X1+mvoiBOv/2X/qkSsisRcOj/KK
NFtY2PwByVS5uCbMiogziUwthDyC3+6WVwW6LLv3xLfHTjuCvjHIInNzktHCgKQ5
ORAzI4JMPJ+GslWYHb4phowim57iaztXOoJwTdwJx4nLCgdNbOhdjsnvzqvHu7Ur
TkXWStAmzOVyyghqpZXjFaH3pO3JLF+l+/+sKAIuvtd7u+Nxe5AW0wdeRlN8NwdC
jNPElpzVmbUq4JUagEiuTDkHzsxHpFKVK7q4+63SM1N95R1NbdWhscdCb+ZAJzVc
oyi3B43njTOQ5yOf+1CceWxG1bQVs5ZufpsMljq4Ui0/1lvh+wjChP4kqKOJ2qxq
4RgqsahDYVvTH9w7jXbyLeiNdd8XM2w9U/t7y0Ff/9yi0GE44Za4rF2LN9d11TPA
mRGunUHBcnWEvgJBQl9nJEiU0Zsnvgc/ubhPgXRR4Xq37Z0j4r7g1SgEEzwxA57d
emyPxgcYxn/eR44/KJ4EBs+lVDR3veyJm+kXQ99b21/+jh5Xos1AnX5iItreGCc=
—–END CERTIFICATE—–
—–BEGIN CERTIFICATE—–
MIIFjTCCA3WgAwIBAgIRANOxciY0IzLc9AUoUSrsnGowDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTYxMDA2MTU0MzU1
WhcNMjExMDA2MTU0MzU1WjBKMQswCQYDVQQGEwJVUzEWMBQGA1UEChMNTGV0J3Mg
RW5jcnlwdDEjMCEGA1UEAxMaTGV0J3MgRW5jcnlwdCBBdXRob3JpdHkgWDMwggEi
MA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCc0wzwWuUuR7dyXTeDs2hjMOrX
NSYZJeG9vjXxcJIvt7hLQQWrqZ41CFjssSrEaIcLo+N15Obzp2JxunmBYB/XkZqf
89B4Z3HIaQ6Vkc/+5pnpYDxIzH7KTXcSJJ1HG1rrueweNwAcnKx7pwXqzkrrvUHl
Npi5y/1tPJZo3yMqQpAMhnRnyH+lmrhSYRQTP2XpgofL2/oOVvaGifOFP5eGr7Dc
Gu9rDZUWfcQroGWymQQ2dYBrrErzG5BJeC+ilk8qICUpBMZ0wNAxzY8xOJUWuqgz
uEPxsR/DMH+ieTETPS02+OP88jNquTkxxa/EjQ0dZBYzqvqEKbbUC8DYfcOTAgMB
AAGjggFnMIIBYzAOBgNVHQ8BAf8EBAMCAYYwEgYDVR0TAQH/BAgwBgEB/wIBADBU
BgNVHSAETTBLMAgGBmeBDAECATA/BgsrBgEEAYLfEwEBATAwMC4GCCsGAQUFBwIB
FiJodHRwOi8vY3BzLnJvb3QteDEubGV0c2VuY3J5cHQub3JnMB0GA1UdDgQWBBSo
SmpjBH3duubRObemRWXv86jsoTAzBgNVHR8ELDAqMCigJqAkhiJodHRwOi8vY3Js
LnJvb3QteDEubGV0c2VuY3J5cHQub3JnMHIGCCsGAQUFBwEBBGYwZDAwBggrBgEF
BQcwAYYkaHR0cDovL29jc3Aucm9vdC14MS5sZXRzZW5jcnlwdC5vcmcvMDAGCCsG
AQUFBzAChiRodHRwOi8vY2VydC5yb290LXgxLmxldHNlbmNyeXB0Lm9yZy8wHwYD
VR0jBBgwFoAUebRZ5nu25eQBc4AIiMgaWPbpm24wDQYJKoZIhvcNAQELBQADggIB
ABnPdSA0LTqmRf/Q1eaM2jLonG4bQdEnqOJQ8nCqxOeTRrToEKtwT++36gTSlBGx
A/5dut82jJQ2jxN8RI8L9QFXrWi4xXnA2EqA10yjHiR6H9cj6MFiOnb5In1eWsRM
UM2v3e9tNsCAgBukPHAg1lQh07rvFKm/Bz9BCjaxorALINUfZ9DD64j2igLIxle2
DPxW8dI/F2loHMjXZjqG8RkqZUdoxtID5+90FgsGIfkMpqgRS05f4zPbCEHqCXl1
eO5HyELTgcVlLXXQDgAWnRzut1hFJeczY1tjQQno6f6s+nMydLN26WuU4s3UYvOu
OsUxRlJu7TSRHqDC3lSE5XggVkzdaPkuKGQbGpny+01/47hfXXNB7HntWNZ6N2Vw
p7G6OfY+YQrZwIaQmhrIqJZuigsrbe3W+gdn5ykE9+Ky0VgVUsfxo52mwFYs1JKY
2PGDuWx8M6DlS6qQkvHaRUo0FMd8TsSlbF0/v965qGFKhSDeQoMpYnwcmQilRh/0
ayLThlHLN81gSkJjVrPI0Y8xCVPB4twb1PFUd2fPM3sA1tJ83sZ5v8vgFv2yofKR
PB0t6JzUA81mSqM3kxl5e+IZwhYAyO0OTg3/fs8HqGTNKd9BqoUwSRBzp06JMg5b
rUCGwbCUDI0mxadJ3Bz4WxR6fyNpBK2yAinWEsikxqEt
—–END CERTIFICATE—–

Public Client Cert

In the .ovpn file Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

In the .ovpn file Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Hotspot Shield connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit Hotspot Shield’s website to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Hotspot Shield.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Hotspot Shield server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new Public Client Cert and Private Client Key.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PrivateInternetAccess (PIA) AsusWRT OpenVPN Setup

TeamFlashRouters · Apr 29, 2024 ·

Preparing for PIA AsusWRT Setup

Download your PIA .ovpn file

If you are not already a PIA user Sign Up Now.

1. Log in to your account on the PIA website.

PIA login

2. Successfully log in with your account information then go to PIA’s OpenVPN Config Generator.

3. On the OpenVPN Configuration Generator select the following:

OpenVPN Version: OpenVPN 2.4 or newer

Select Platform: Linux

Select Region: Choose the server location you’d like to connect to

Select Port: Typically we recommend UDP/1198 RSA-2048 AES-128-CBC SHA1 for best speeds but feel free to select the one you want to use.

4. Click Generate to download the .ovpn file. Do not open this file once it is downloaded.

PIA Generate .ovpn file

AsusWRT Router Setup for PIA

Login to AsusWRT firmware settings in a browser on any computer or smart device connected to the AsusWRT FlashRouter’s network.

1. Navigate to the VPN tab.

Merlin VPN Tab

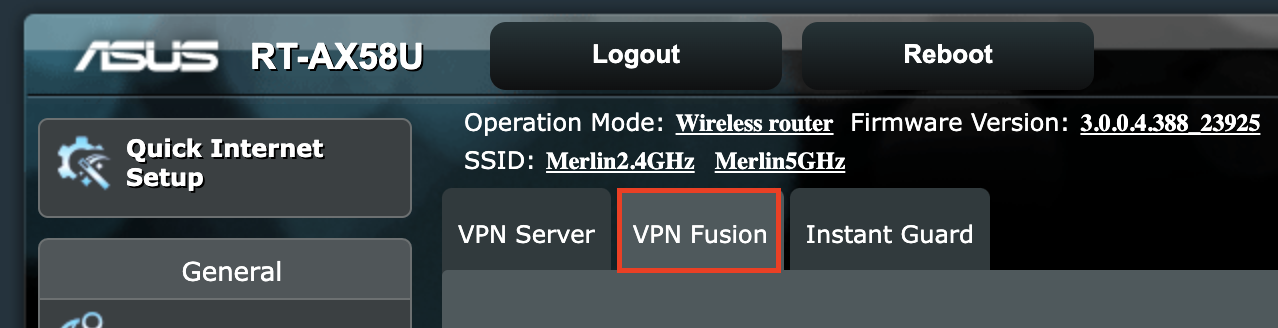
2. Navigate to the VPN Fusion tab.

Asus VPN Fusion

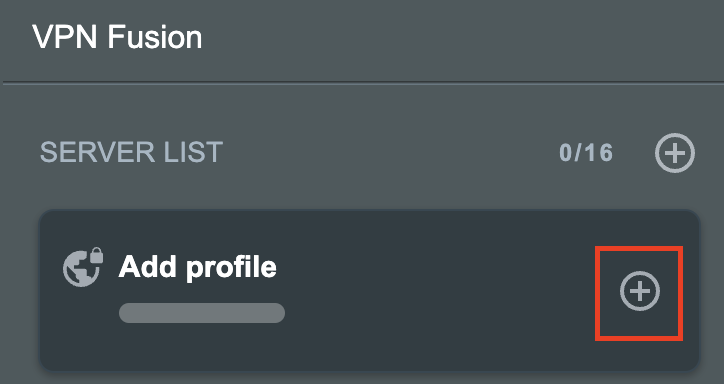
3. Click Add profile.

Asus Add profile

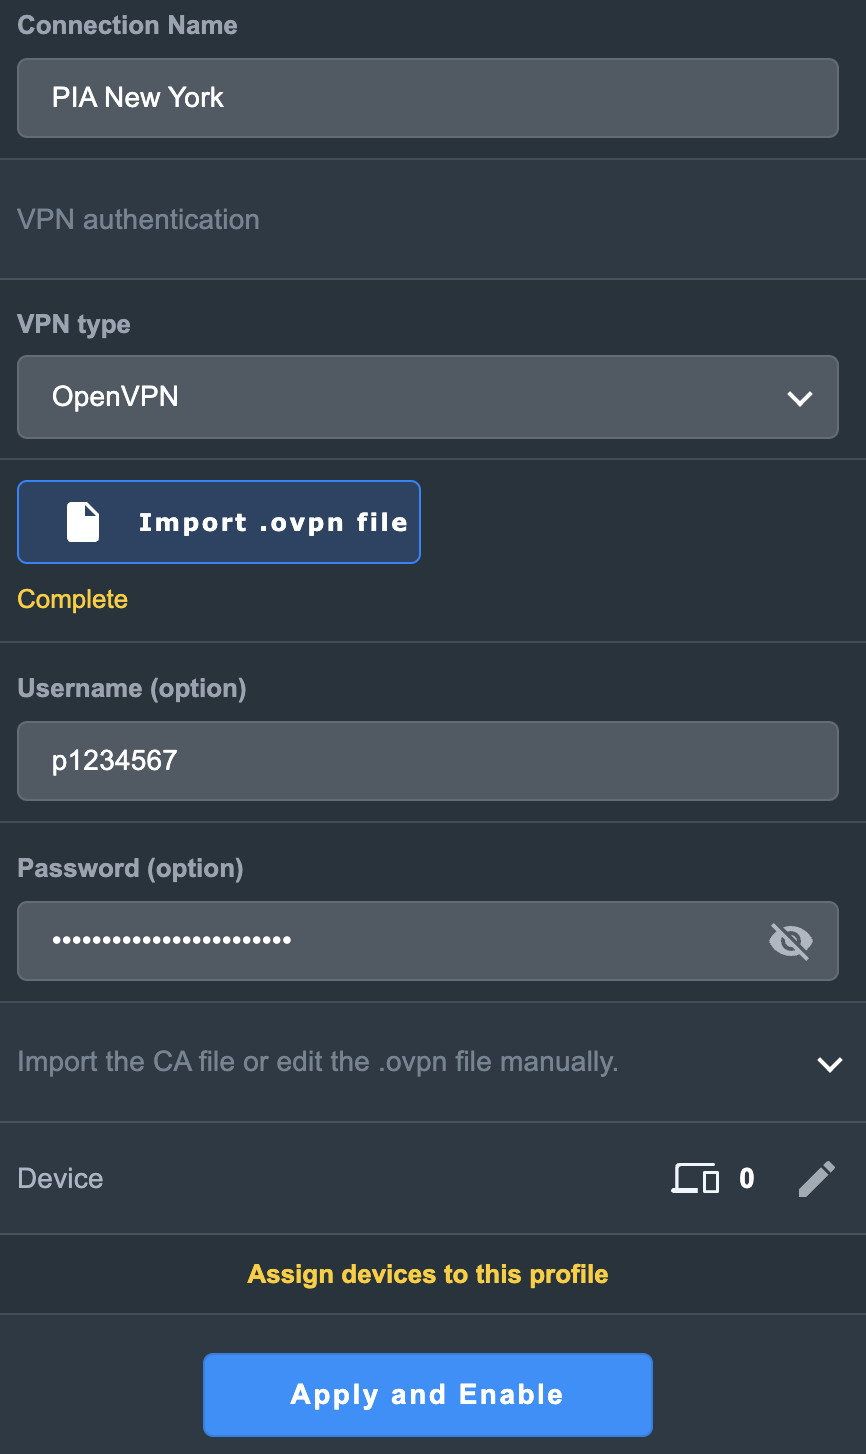
4. In the Connection Name field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location or server number here. Our example server was in New York so I have entered in PIA New York.

5. In the VPN Type dropdown select OpenVPN.

6. Click Import .ovpn file and select the .ovpn file you downloaded earlier. Then click Upload.

7. In the Username and Password fields paste in the PIA username and password you use to successfully login to your PIA website account.

8. Click Apply and Enable at the bottom of the page.

Asus PIA profile

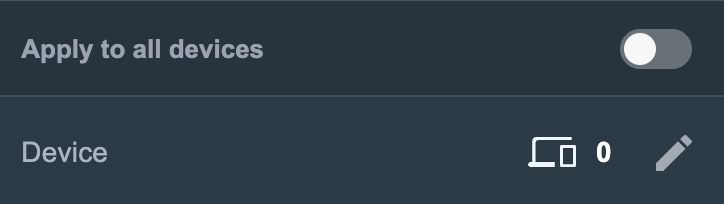
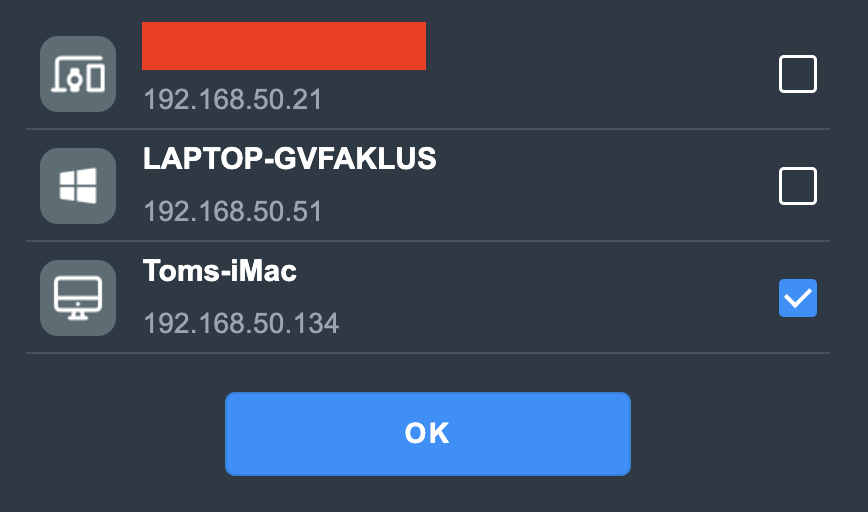
If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network click into the profile and disable Apply to all devices. Then click Devices and select the devices that you want to connect to VPN.

Asus VPN devices
Asus VPN select devices

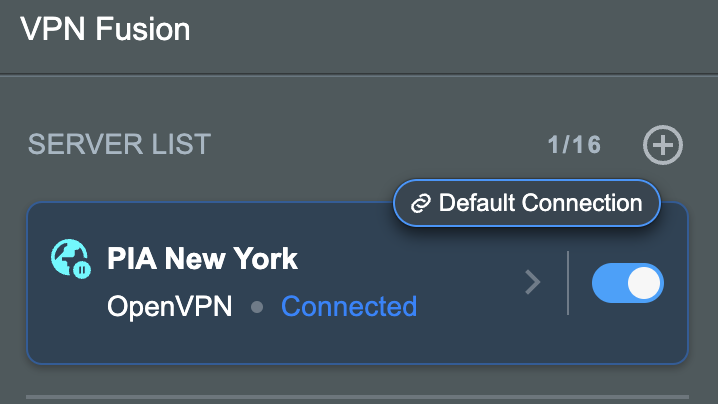
9. At the top of the page set the Service State toggle to ON to activate the VPN connection.

Asus PIA Connected

Verify a successful PIA connection

  1. You should now see a CONNECTED message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.

In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

How to change the PIA server

  1. Follow the steps at the top of the page to obtain a new .ovpn file.
  2. Then proceed with the settings same as initial setup.
TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.
Troubleshoot Here

Roqos VPN Connected, but my device IP is unchanged

TeamFlashRouters · Mar 8, 2022 ·

If your VPN Out page in your Roqos settings is reporting that you are Connected to your VPN provider but your IP Address and location have not changed when you visit What is my IP address? follow the below checklist.

Double check that your device is connected to the Roqos network

Since the Roqos UI is being accessed securely via the cloud you can change the settings while your device is not connected to the Roqos network. This would result in your IP Address not updating when you connect to VPN.

Make sure that you are connected to your Roqos WiFi network or from an ethernet port on the back of the Roqos directly to your device and not another network.

Assign Devices To Connect To VPN in the Roqos

By default there are no devices assigned to the VPN tunnel. To assign devices to the Roqos’ VPN connection.

1. Login to your Roqos UI.

2. Select the VPN tab on the left hand menu and select VPN Out.

Roqos VPN Out

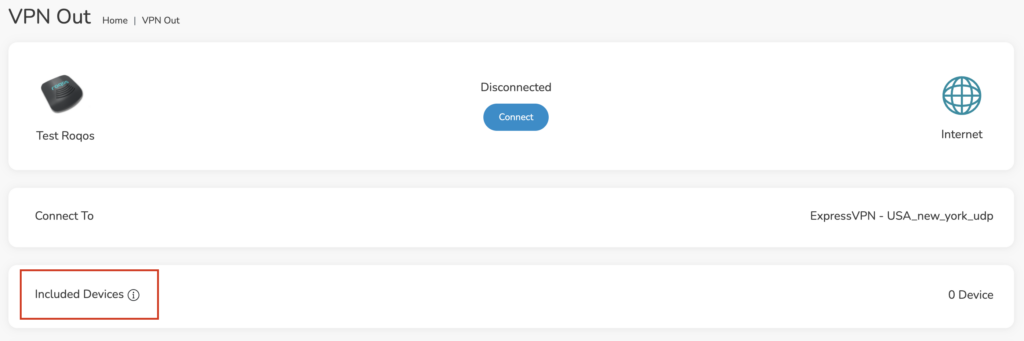
3. Click Included Devices. From this page you can choose if all devices should connect to VPN or only certain devices.

Roqos VPN Included Devices

4. From the dropdown select Include all devices if you want every device that connects to the Roqos to connect to VPN or if you only want specific devices to connect to VPN while others bypass the VPN connection select Include selected devices from the dropdown and then toggle the sliders for the devices you want connected to VPN. Click Save.

Turn off VPN device applications

Connecting to VPN via a device application or browser extension at the same time while connecting via your Roqos is not recommended. Doubling up on VPN connections can cause issues with speeds and stability.

When you are connected to the Roqos VPN network at home you should leave all VPN applications and extensions disconnected and unopened.

« Previous Page

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer