• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: button guard

CyberGhost Merlin OpenVPN Setup

TeamFlashRouters · Mar 30, 2023 ·

Preparing for CyberGhost Setup

Obtain your CyberGhost OpenVPN information

If you are not already a CyberGhost user Sign Up Now.

1. Log in to your account on the CyberGhost website.
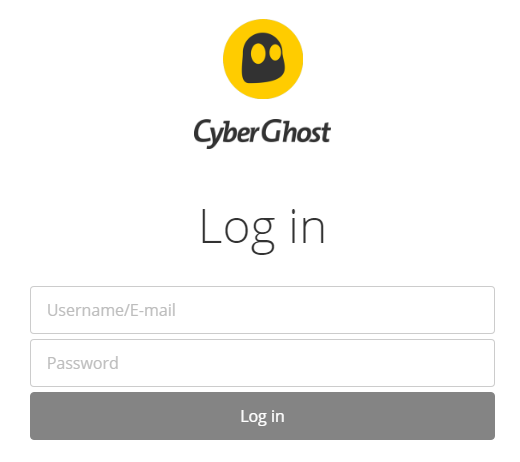
CyberGhost Website Login

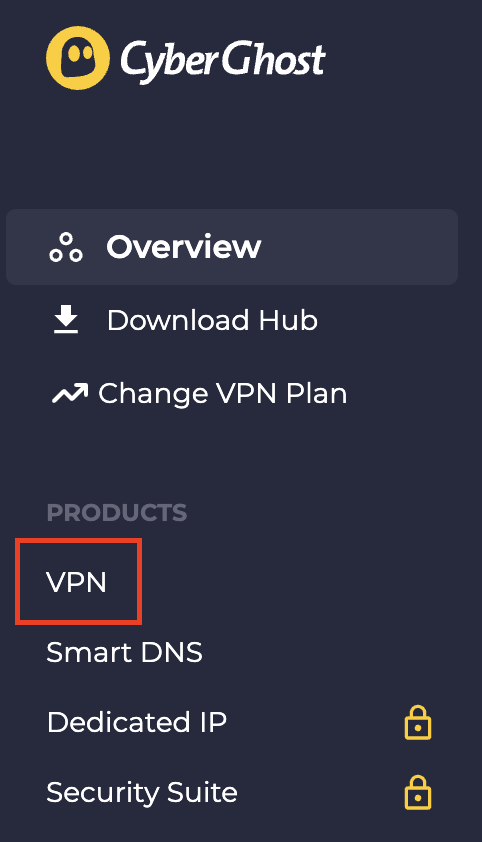
2. Select VPN.

CyberGhost VPN

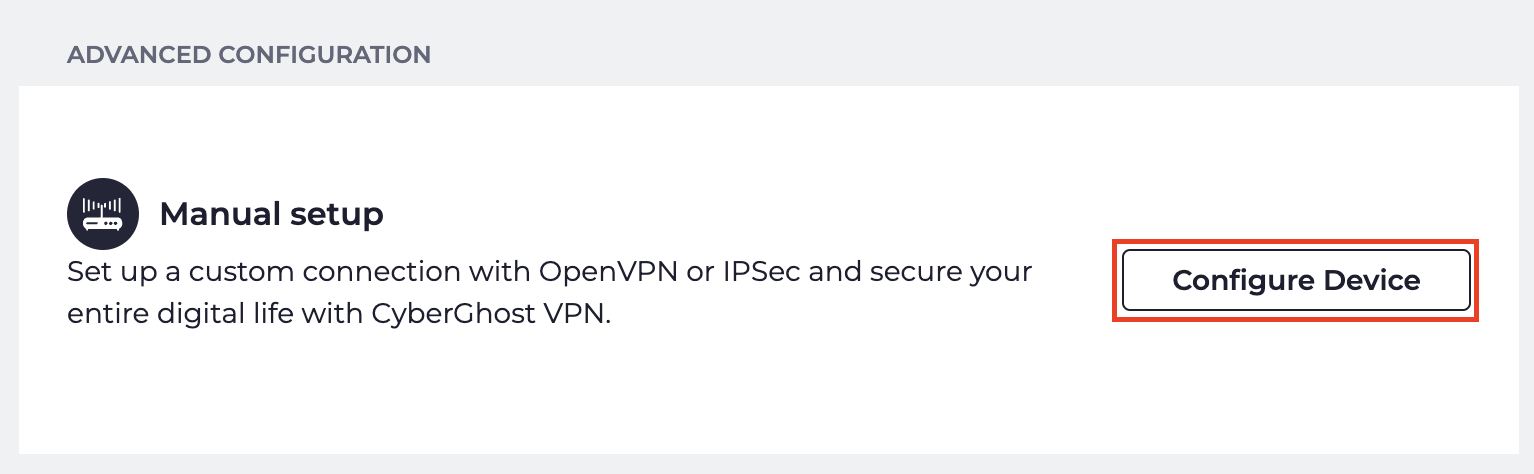
3. Click Configure New Device.

CyberGhost Configure Device

4. Set Protocol to OpenVPN. Select the Country you would like to connect to. Select the Server Group. Name the device in the Device Name field. Click Save Configuration.
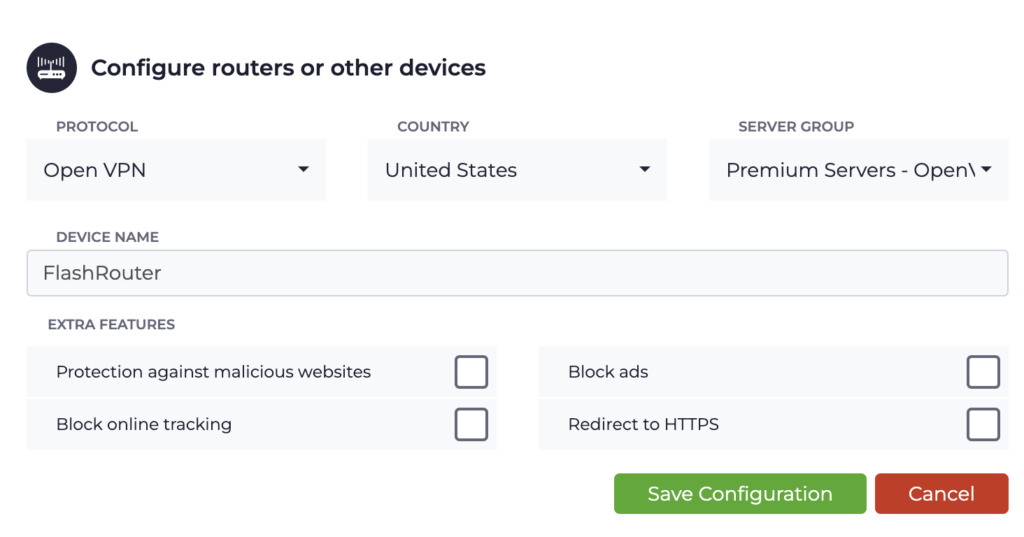
CyberGhost protocol and location

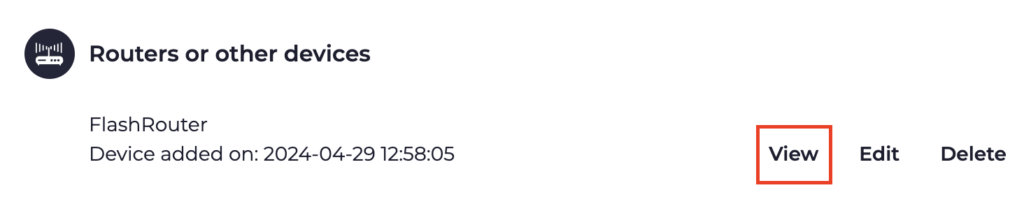
5. Press View configuration.

CyberGhost view configuration

6. Copy the Username, and Password that appear to a notepad, since you will need this information later in the setup process. Click Download Configuration.
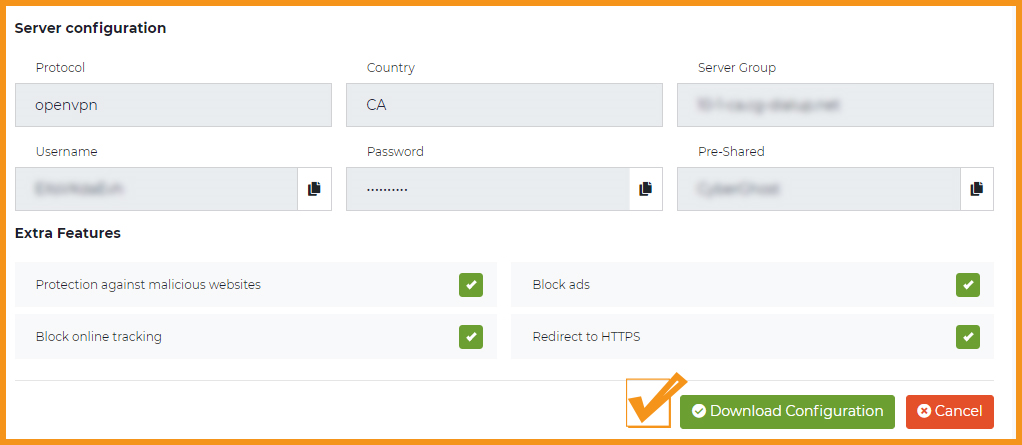
CyberGhost Website OpenVPN Configuration Files Generator 1

Open the folder that was downloaded. Then open the ca.crt the client.crt, and client.key files with NotePad++ for Windows or TextEdit for Apple. All CyberGhost servers have different keys and certificates.

Merlin Router Setup for CyberGhost

Login to Asus Merlin firmware settings in a browser on any computer or smart device connected to the Merlin FlashRouter’s network.

1. Navigate to the VPN tab.
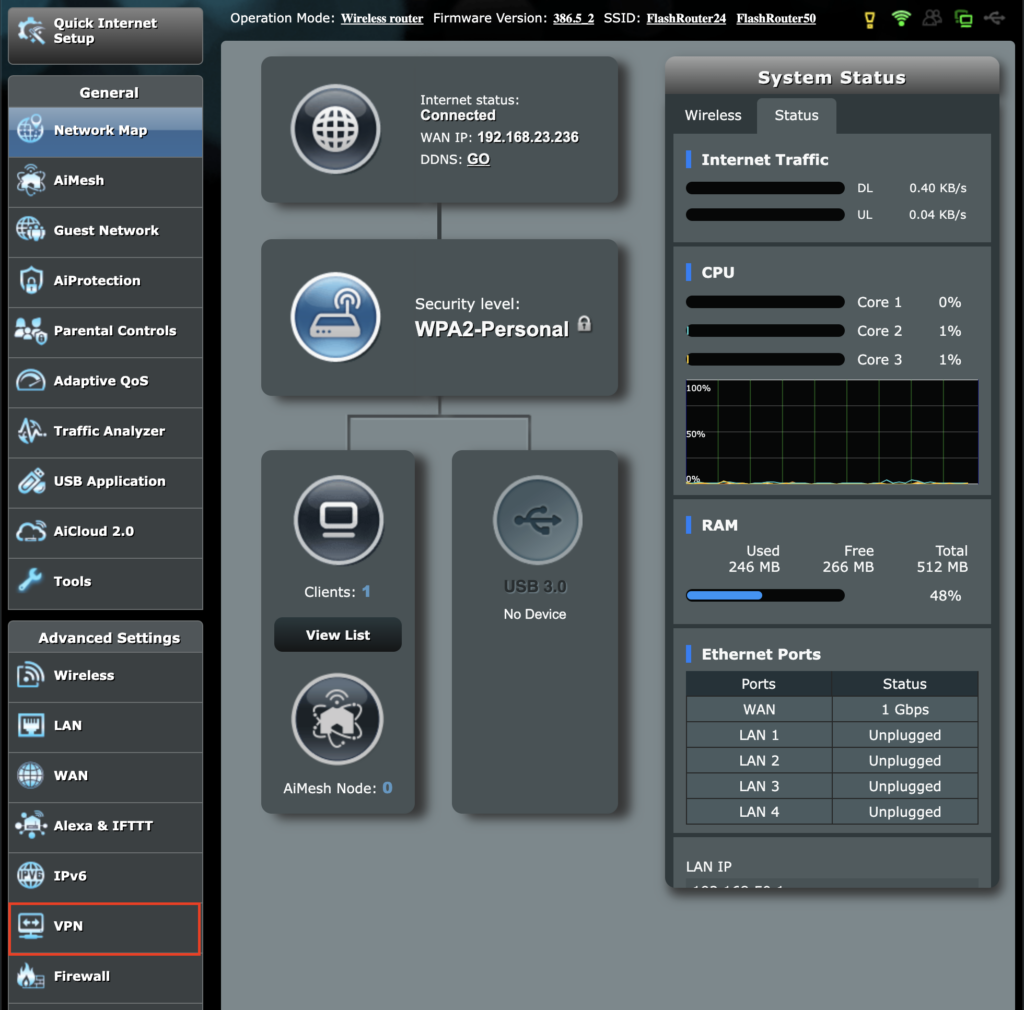
Merlin VPN Tab

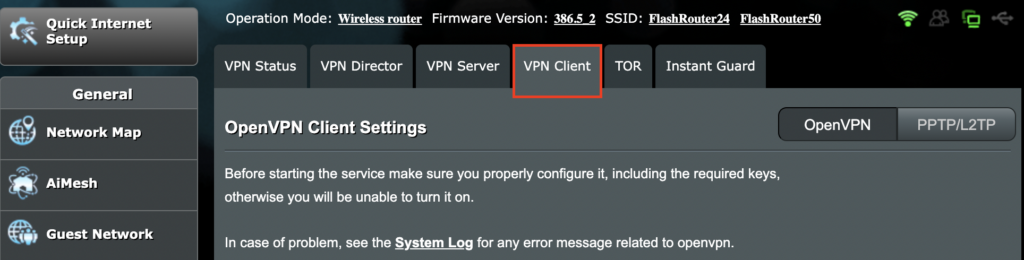
2. Navigate to the VPN Client tab.

Merlin VPN Client Tab

3. Click Choose file and select the .ovpn file from the folder you downloaded earlier. Then click Upload.
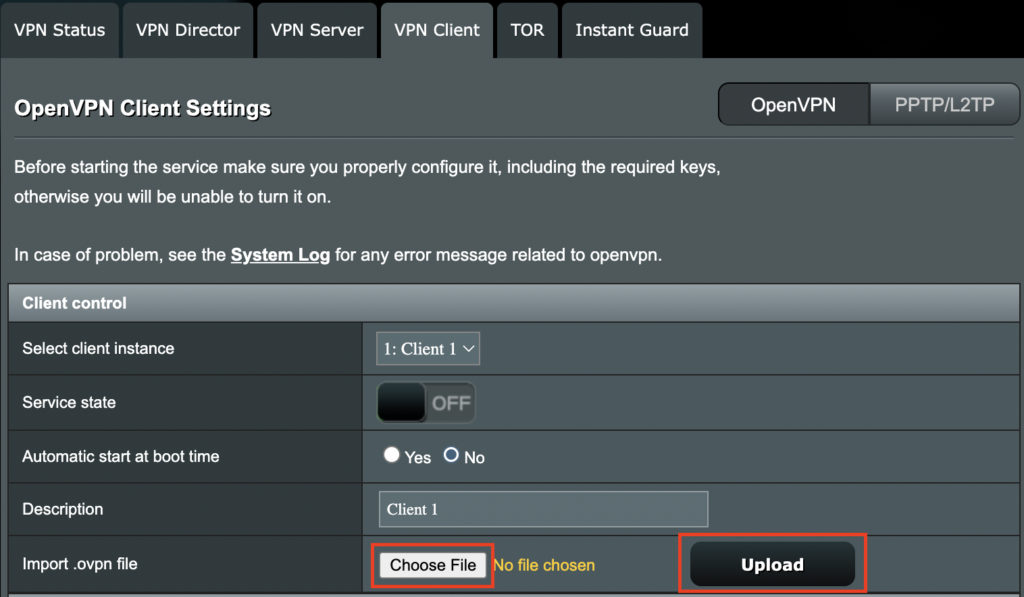
Merlin Choose File Upload

4. Set Automatic Start at boot time to Yes if you want the VPN connection to begin automatically when the router is powered off and back on.
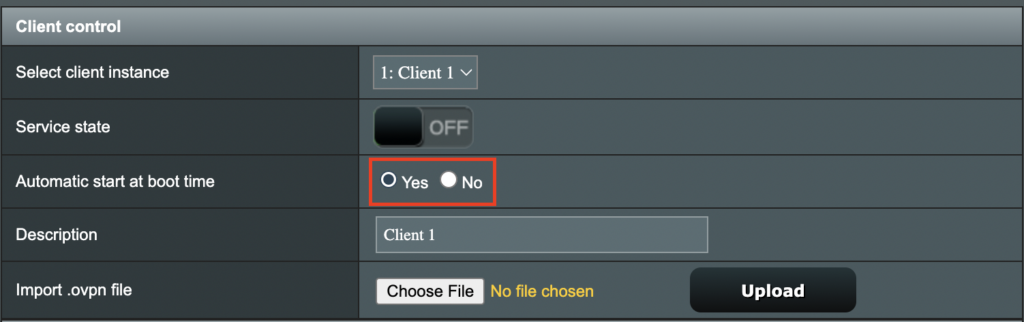
Merlin Automatic Start at boot time

5. In the Description field enter in the name you’d like to use for this OpenVPN Client profile. We typically advise entering in the location here. Our example server was in USA so I have entered in CyberGhost USA.
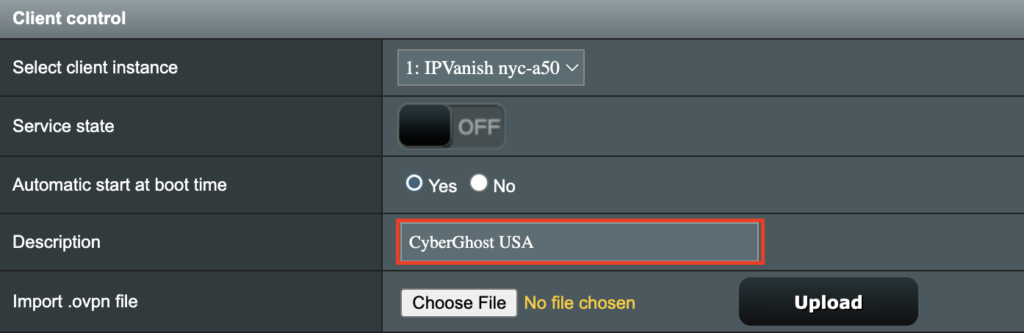
Merlin CyberGhost Description field

6. Set Accept DNS Configuration to Strict. Set Redirect Internet traffic through tunnel to Yes (all). Set Kill Switch to Yes or No depending on if you want the Internet to be killed if the VPN connection drops.
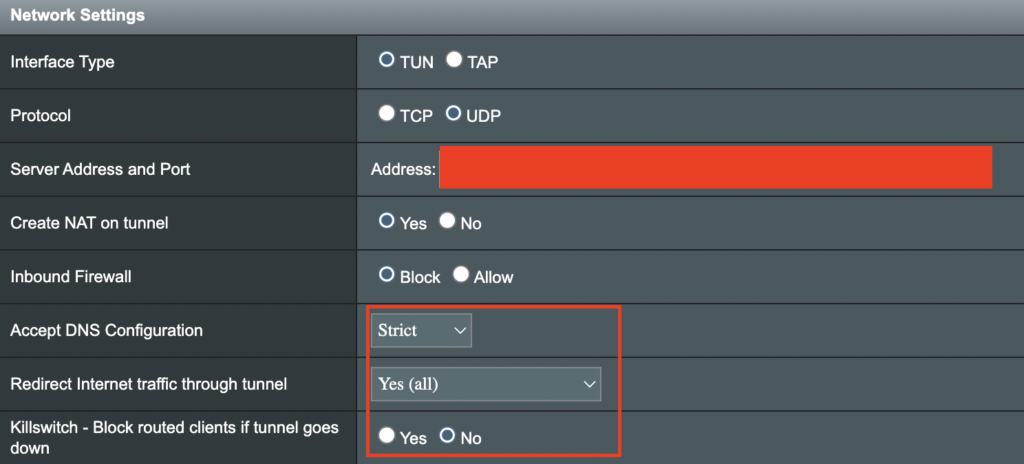
Merlin Accept DNS configuration Redirect Internet and Kill Switch

If you only want certain devices to connect to the OpenVPN Client profile you are setting up instead of all the devices connected to the FlashRouter’s network please set the Redirect Internet traffic through tunnel to VPN Director. Then complete the instructions on this page and then view our VPN Director guide.

7. Enter your CyberGhost OpenVPN username and password that you obtained earlier. Do not enter your account login.
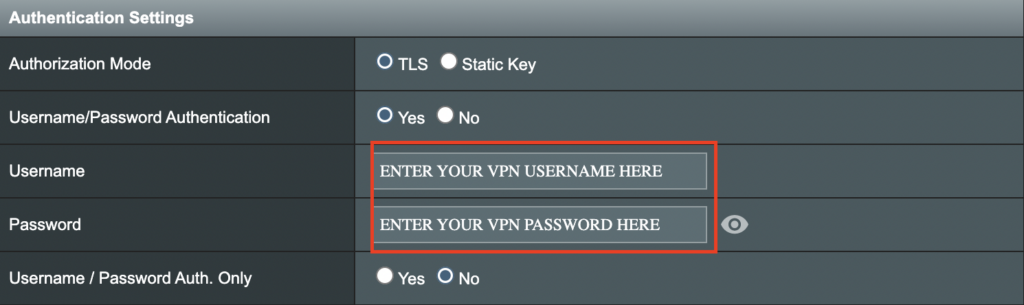
Merlin VPN Username and Password

8. Click the Edit button in the Keys and Certificates area.
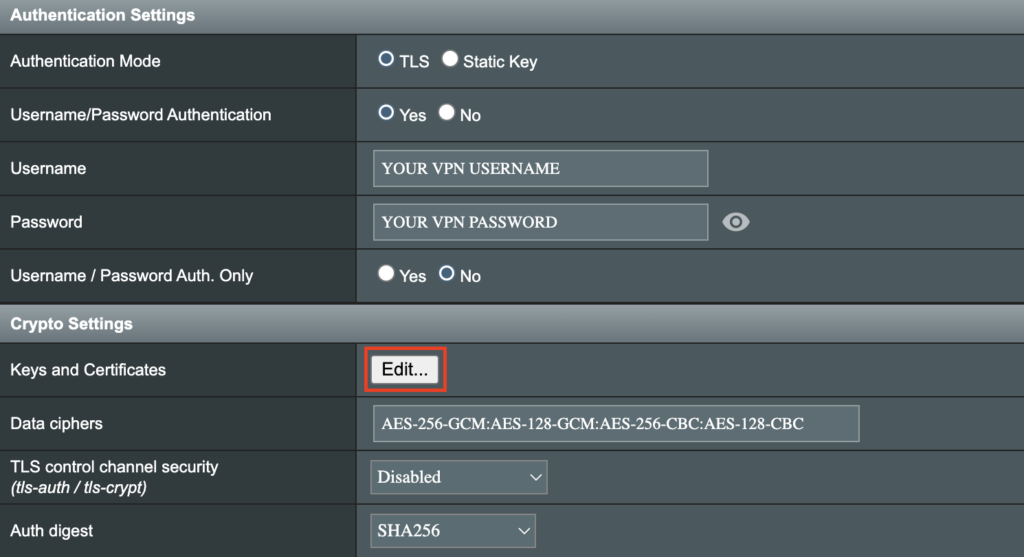
Merlin Keys and Certificates Edit button

9. In the Certificate Authority field paste in the entire content of the ca.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).
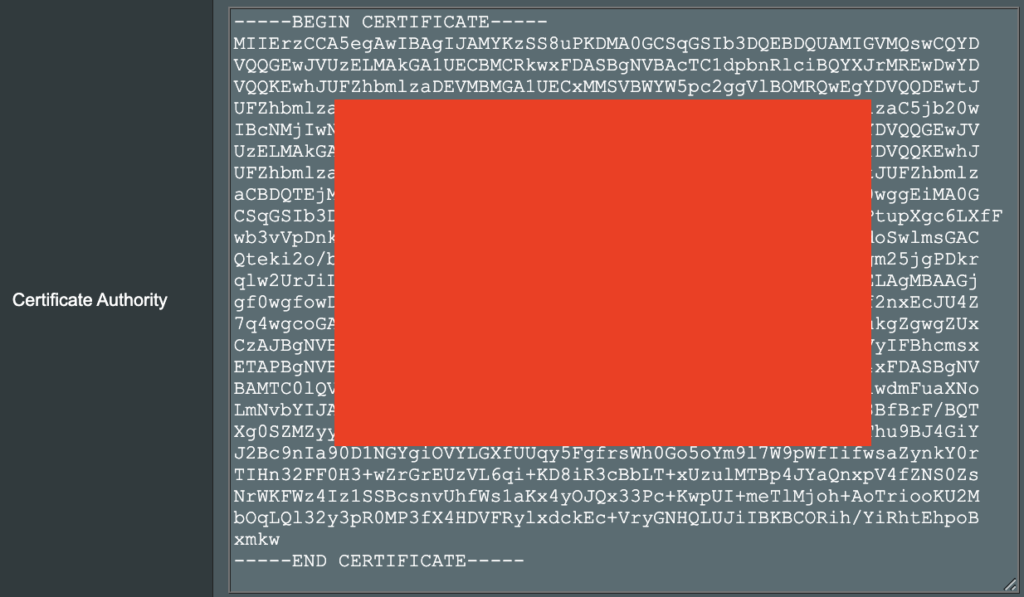
Merlin Certificate Authority

10. In the Client Certificate field paste in the entire content of the client.crt file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).
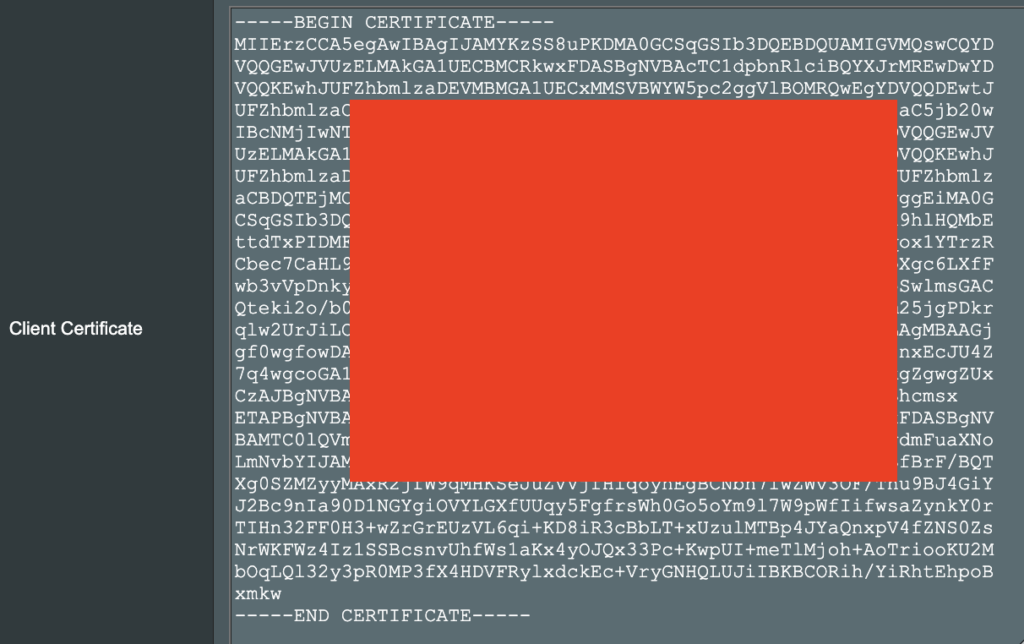
Merlin Client Certificate

11. In the Client Key field paste in the entire content of the client.key file.

—– BEGIN xxx —– / —– END xxx —– block (including those two lines).
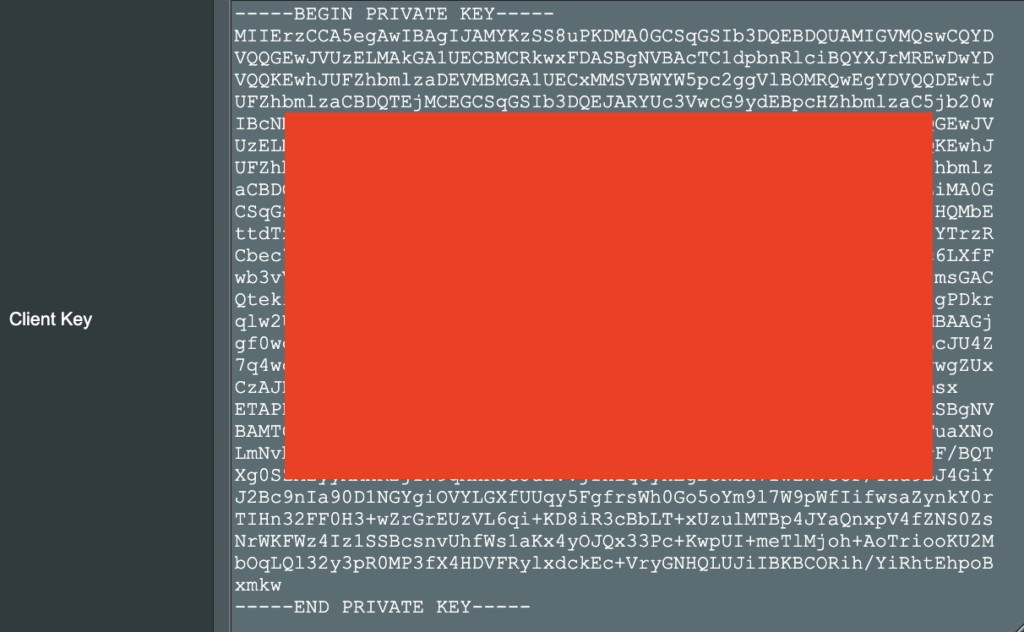
Merlin Client Key

12. Click Save at the bottom of that window.

13. Click Apply at the bottom of the page.

14. At the top of the page set the Service State toggle to ON to activate the VPN connection.
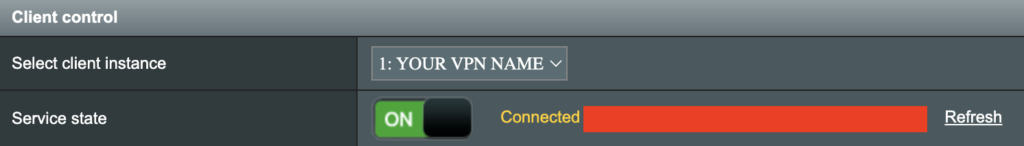
Merlin Service State All Providers

Verify a successful CyberGhost connection

  1. You should now see a CONNECTED message.
  2. Visit What is my IP Address from a private/incognito browser to verify your new IP address and virtual location.
TROUBLESHOOTING

Still having issues? Visit the FR Privacy App Troubleshooting section.

Troubleshoot Here

Roqos Core Internet Setup and Activation

TeamFlashRouters · Mar 15, 2022 ·

Follow this article when you receive your new Roqos Core router to create your Roqos account, connect your Roqos to the Internet, and customize your network so it is ready to use.

Create your Roqos account

1. From any device that has a browser such as a computer, smartphone, or tablet visit login.roqos.com

Roqos Login URL

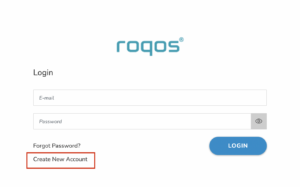
2. Select Create Account.

Roqos Create Account

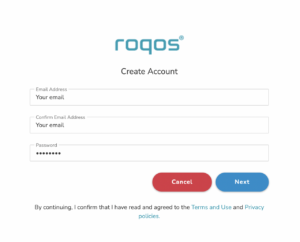
3. Enter the Email address and password you want to set for your Roqos account. This will be your login to the Roqos settings moving forward. Click Next.

Roqos Enter Email

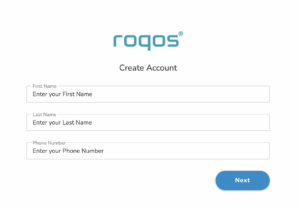
4. Enter the name and phone number you want associated with your Roqos. Click Next.

Roqos Enter Name and Number

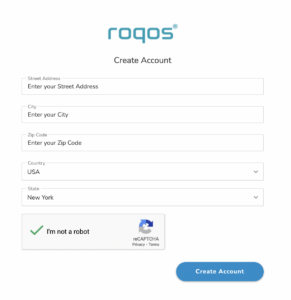
5. Enter the address where your Roqos is located. This section may require a CAPTCHA to be completed to authenticate you are human. Click Create Account.

Roqos Enter Address

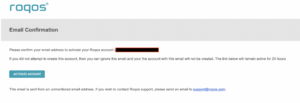
6. You have now created your Roqos account. In a new tab proceed to open the email from Roqos and click the Activate account button.

Roqos email activation

Activate your Roqos Internet

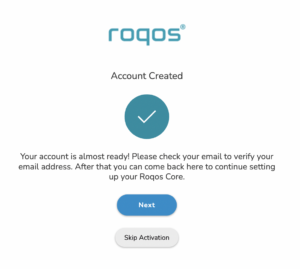
1. From the Account created page click Next to begin the Internet Setup of the Roqos.

Roqos Account Created

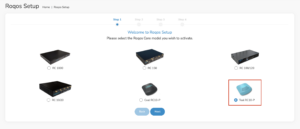
2. Select the Roqos model Teal RC10-P. Click Next.

Roqos Model

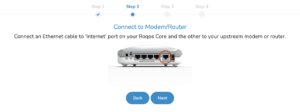
3. Connect the ethernet cable that came with your Roqos from the port labeled INTERNET on the back of your Roqos to an open ethernet port on your ISP Modem or other router in your network.

Roqos Wiring

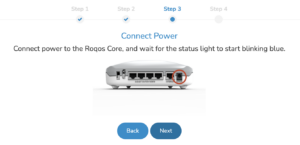
4. Then connect the power adapter that came with the Roqos to the back of the Roqos. Wait for the light on the Roqos to begin blinking blue. Once your see the blinking blue lights on the Roqos click Next.

Roqos Power On

If your Roqos lights does not begin blinking blue after a long while please see the steps in this article and contact us.

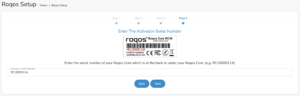
5. Enter in the Roqos serial number found on the bottom of the device exactly as it appears there. Click Next.

Roqos Activation Code

Setup your Roqos Network

1. Enter in a name that you would like to call the Roqos. This is just the Roqo’s device name and it is not the WiFi network name. Click Next.

Roqos Device Name

2. Select the Time Zone of your actual location from the dropdown. Click Next.

Roqos Time Zone

3. Set the WiFi name and password for the Roqos. The WiFi name should be unique and not a duplicate of an existing wireless network. This will be the name that appears in your wireless devices available network list and the password to join the devices to the network. Click Next.

Roqos Set WiFi Name and Password

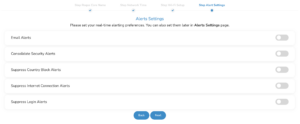
4. Select the custom alert settings as you best see fit using the toggle switches. We typically recommend having the first two toggles selected for Email Alerts and Consolidate Security Alerts. Click Next.

Begin connecting your devices to the Roqos network

You are now done setting up your Roqos to connect to the Internet and can begin joining your wireless devices to the Roqos network and exploring the Roqos Core Features.

Roqos Setup Done

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

PrivateInternetAccess (PIA) Manual OpenVPN Setup

TeamFlashRouters · Apr 5, 2019 ·

Preparing for Manual PIA Setup

Verify your PIA login information

If you are not already a PIA user Sign Up Now.

Log in to your account on the PIA website.

FlashRouters Privacy App - PIA Login

PIA Server Addresses

The below servers are the only servers compatible with PIA router connections. Dedicated IP Addresses are not able to connect via routers.

United States

us-california.privacy.network
us-newjersey.privacy.network
us-chicago.privacy.network
us-texas.privacy.network
us-florida.privacy.network
us-seattle.privacy.network
us3.privacy.network
us-siliconvalley.privacy.network
us-newyorkcity.privacy.network
us-washingtondc.privacy.network
us-atlanta.privacy.network
us-houston.privacy.network
us-denver.privacy.network

United Kingdom

uk-london.privacy.network
uk-manchester.privacy.network

Canada

ca-toronto.privacy.network
ca-montreal.privacy.network

Australia

au-sydney.privacy.network
aus-melbourne.privacy.network
aus-perth.privacy.network

Germany

de-berlin.privacy.network
de-frankfurt.privacy.network

Rest of the World

ae.privacy.network
austria.privacy.network
dz.privacy.network
ad.privacy.network
ar.privacy.network
yerevan.privacy.network
bahamas.privacy.network
bangladesh.privacy.network
brussels.privacy.network
sofia.privacy.network
cambodia.privacy.network
china.privacy.network
cyprus.privacy.network
czech.privacy.network
denmark.privacy.network
egypt.privacy.network
fi.privacy.network
france.privacy.network
georgia.privacy.network
greenland.privacy.network
hungary.privacy.network
is.privacy.network
in.privacy.network
iran.privacy.network
ireland.privacy.network
man.privacy.network
israel.privacy.network
italy.privacy.network
japan.privacy.network
kazakhstan.privacy.network
liechtenstein.privacy.network
lu.privacy.network
macau.privacy.network
malta.privacy.network
mexico.privacy.network
md.privacy.network
monaco.privacy.network
mongolia.privacy.network
montenegro.privacy.network
morocco.privacy.network
nl-amsterdam.privacy.network
nz.privacy.network
nigeria.privacy.network
no.privacy.network
panama.privacy.network
philippines.privacy.network
poland.privacy.network
qatar.privacy.network
ro.privacy.network
rs.privacy.network
saudiarabia.privacy.network
spain.privacy.network
srilanka.privacy.network
sweden.privacy.network
swiss.privacy.network
sg.privacy.network
tr.privacy.network
taiwan.privacy.network
ua.privacy.network
venezuela.privacy.network
vietnam.privacy.network
za.privacy.network

DD-WRT Router Setup for PIA

Navigate to Services > VPN

PIA offers two different Encryption levels.
Default Encryption (AES-128) typically provides faster speeds.
Strong Encryption (AES-256) provides stronger encryption.
Follow the table below of the one that fits your needs.

Enter PIA settings (Default Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1198

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA1

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Disabled

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIFqzCCBJOgAwIBAgIJAKZ7D5Yv87qDMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzM1
MThaFw0zNDA0MTIxNzM1MThaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAPXD
L1L9tX6DGf36liA7UBTy5I869z0UVo3lImfOs/GSiFKPtInlesP65577nd7UNzzX
lH/P/CnFPdBWlLp5ze3HRBCc/Avgr5CdMRkEsySL5GHBZsx6w2cayQ2EcRhVTwWp
cdldeNO+pPr9rIgPrtXqT4SWViTQRBeGM8CDxAyTopTsobjSiYZCF9Ta1gunl0G/
8Vfp+SXfYCC+ZzWvP+L1pFhPRqzQQ8k+wMZIovObK1s+nlwPaLyayzw9a8sUnvWB
/5rGPdIYnQWPgoNlLN9HpSmsAcw2z8DXI9pIxbr74cb3/HSfuYGOLkRqrOk6h4RC
OfuWoTrZup1uEOn+fw8CAwEAAaOCAVQwggFQMB0GA1UdDgQWBBQv63nQ/pJAt5tL
y8VJcbHe22ZOsjCCAR8GA1UdIwSCARYwggESgBQv63nQ/pJAt5tLy8VJcbHe22ZO
sqGB7qSB6zCB6DELMAkGA1UEBhMCVVMxCzAJBgNVBAgTAkNBMRMwEQYDVQQHEwpM
b3NBbmdlbGVzMSAwHgYDVQQKExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4G
A1UECxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBAMTF1ByaXZhdGUg
SW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQpExdQcml2YXRlIEludGVybmV0IEFjY2Vz
czEvMC0GCSqGSIb3DQEJARYgc2VjdXJlQHByaXZhdGVpbnRlcm5ldGFjY2Vzcy5j
b22CCQCmew+WL/O6gzAMBgNVHRMEBTADAQH/MA0GCSqGSIb3DQEBDQUAA4IBAQAn
a5PgrtxfwTumD4+3/SYvwoD66cB8IcK//h1mCzAduU8KgUXocLx7QgJWo9lnZ8xU
ryXvWab2usg4fqk7FPi00bED4f4qVQFVfGfPZIH9QQ7/48bPM9RyfzImZWUCenK3
7pdw4Bvgoys2rHLHbGen7f28knT2j/cbMxd78tQc20TIObGjo8+ISTRclSTRBtyC
GohseKYpTS9himFERpUgNtefvYHbn70mIOzfOJFTVqfrptf9jXa9N8Mpy3ayfodz
1wiqdteqFXkTYoSDctgKMiZ6GdocK9nMroQipIQtpnwd4yBDWIyC6Bvlkrq5TQUt
YDQ8z9v+DMO6iwyIDRiU
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Enter PIA settings (Strong Encryption)

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change PIA connection locations, THIS IS THE ONLY FIELD YOU NEED TO CHANGE.

Port

1197

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA256

First Data Cipher

Not set

Second Data Cipher

Not set

Third Data Cipher

Not set

Userpass Authentication

Enable

Username

Enter the Username you successfully logged in to your PIA account with.

Password

Enter the Password you successfully logged in to your PIA account with.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

Additional Config

persist-key
persist-tun

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIHqzCCBZOgAwIBAgIJAJ0u+vODZJntMA0GCSqGSIb3DQEBDQUAMIHoMQswCQYD
VQQGEwJVUzELMAkGA1UECBMCQ0ExEzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNV
BAoTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIElu
dGVybmV0IEFjY2VzczEgMB4GA1UEAxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3Mx
IDAeBgNVBCkTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkB
FiBzZWN1cmVAcHJpdmF0ZWludGVybmV0YWNjZXNzLmNvbTAeFw0xNDA0MTcxNzQw
MzNaFw0zNDA0MTIxNzQwMzNaMIHoMQswCQYDVQQGEwJVUzELMAkGA1UECBMCQ0Ex
EzARBgNVBAcTCkxvc0FuZ2VsZXMxIDAeBgNVBAoTF1ByaXZhdGUgSW50ZXJuZXQg
QWNjZXNzMSAwHgYDVQQLExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UE
AxMXUHJpdmF0ZSBJbnRlcm5ldCBBY2Nlc3MxIDAeBgNVBCkTF1ByaXZhdGUgSW50
ZXJuZXQgQWNjZXNzMS8wLQYJKoZIhvcNAQkBFiBzZWN1cmVAcHJpdmF0ZWludGVy
bmV0YWNjZXNzLmNvbTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBALVk
hjumaqBbL8aSgj6xbX1QPTfTd1qHsAZd2B97m8Vw31c/2yQgZNf5qZY0+jOIHULN
De4R9TIvyBEbvnAg/OkPw8n/+ScgYOeH876VUXzjLDBnDb8DLr/+w9oVsuDeFJ9K
V2UFM1OYX0SnkHnrYAN2QLF98ESK4NCSU01h5zkcgmQ+qKSfA9Ny0/UpsKPBFqsQ
25NvjDWFhCpeqCHKUJ4Be27CDbSl7lAkBuHMPHJs8f8xPgAbHRXZOxVCpayZ2SND
fCwsnGWpWFoMGvdMbygngCn6jA/W1VSFOlRlfLuuGe7QFfDwA0jaLCxuWt/BgZyl
p7tAzYKR8lnWmtUCPm4+BtjyVDYtDCiGBD9Z4P13RFWvJHw5aapx/5W/CuvVyI7p
Kwvc2IT+KPxCUhH1XI8ca5RN3C9NoPJJf6qpg4g0rJH3aaWkoMRrYvQ+5PXXYUzj
tRHImghRGd/ydERYoAZXuGSbPkm9Y/p2X8unLcW+F0xpJD98+ZI+tzSsI99Zs5wi
jSUGYr9/j18KHFTMQ8n+1jauc5bCCegN27dPeKXNSZ5riXFL2XX6BkY68y58UaNz
meGMiUL9BOV1iV+PMb7B7PYs7oFLjAhh0EdyvfHkrh/ZV9BEhtFa7yXp8XR0J6vz
1YV9R6DYJmLjOEbhU8N0gc3tZm4Qz39lIIG6w3FDAgMBAAGjggFUMIIBUDAdBgNV
HQ4EFgQUrsRtyWJftjpdRM0+925Y6Cl08SUwggEfBgNVHSMEggEWMIIBEoAUrsRt
yWJftjpdRM0+925Y6Cl08SWhge6kgeswgegxCzAJBgNVBAYTAlVTMQswCQYDVQQI
EwJDQTETMBEGA1UEBxMKTG9zQW5nZWxlczEgMB4GA1UEChMXUHJpdmF0ZSBJbnRl
cm5ldCBBY2Nlc3MxIDAeBgNVBAsTF1ByaXZhdGUgSW50ZXJuZXQgQWNjZXNzMSAw
HgYDVQQDExdQcml2YXRlIEludGVybmV0IEFjY2VzczEgMB4GA1UEKRMXUHJpdmF0
ZSBJbnRlcm5ldCBBY2Nlc3MxLzAtBgkqhkiG9w0BCQEWIHNlY3VyZUBwcml2YXRl
aW50ZXJuZXRhY2Nlc3MuY29tggkAnS7684Nkme0wDAYDVR0TBAUwAwEB/zANBgkq
hkiG9w0BAQ0FAAOCAgEAJsfhsPk3r8kLXLxY+v+vHzbr4ufNtqnL9/1Uuf8NrsCt
pXAoyZ0YqfbkWx3NHTZ7OE9ZRhdMP/RqHQE1p4N4Sa1nZKhTKasV6KhHDqSCt/dv
Em89xWm2MVA7nyzQxVlHa9AkcBaemcXEiyT19XdpiXOP4Vhs+J1R5m8zQOxZlV1G
tF9vsXmJqWZpOVPmZ8f35BCsYPvv4yMewnrtAC8PFEK/bOPeYcKN50bol22QYaZu
LfpkHfNiFTnfMh8sl/ablPyNY7DUNiP5DRcMdIwmfGQxR5WEQoHL3yPJ42LkB5zs
6jIm26DGNXfwura/mi105+ENH1CaROtRYwkiHb08U6qLXXJz80mWJkT90nr8Asj3
5xN2cUppg74nG3YVav/38P48T56hG1NHbYF5uOCske19F6wi9maUoto/3vEr0rnX
JUp2KODmKdvBI7co245lHBABWikk8VfejQSlCtDBXn644ZMtAdoxKNfR2WTFVEwJ
iyd1Fzx0yujuiXDROLhISLQDRjVVAvawrAtLZWYK31bY7KlezPlQnl/D9Asxe85l
8jO5+0LdJ6VyOs/Hd4w52alDW/MFySDZSfQHMTIc30hLBJ8OnCEIvluVQQ2UQvoW
+no177N9L2Y+M9TcTA62ZyMXShHQGeh20rb4kK8f+iFX8NxtdHVSkxMEFSfDDyQ=
-----END CERTIFICATE-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful PIA connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit PIA’s IP Check to verify your new IP address and virtual location.
In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to PIA.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the PIA server

  1. Copy the new PIA server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Why is the power light on my FlashRouter blinking?

Dave · May 2, 2019 ·

A slowly blinking power light means that the FlashRouter was somehow put into Rescue/Restore/Recovery Mode. This usually happens if the reset button was held down for too long.

This may also happen if you have incorrectly tried to update the firmware on your FlashRouter. The first thing to try is a simple reboot of the router to see if it exits restore mode.

If a reboot does not clear up the issue then try to reset and reconfigure your FlashRouter.

ExpressVPN Manual OpenVPN Setup

admin · Feb 19, 2019 ·

Preparing for Manual ExpressVPN Setup

Obtain your ExpressVPN OpenVPN Information

If you are not already an ExpressVPN user Sign Up Now.

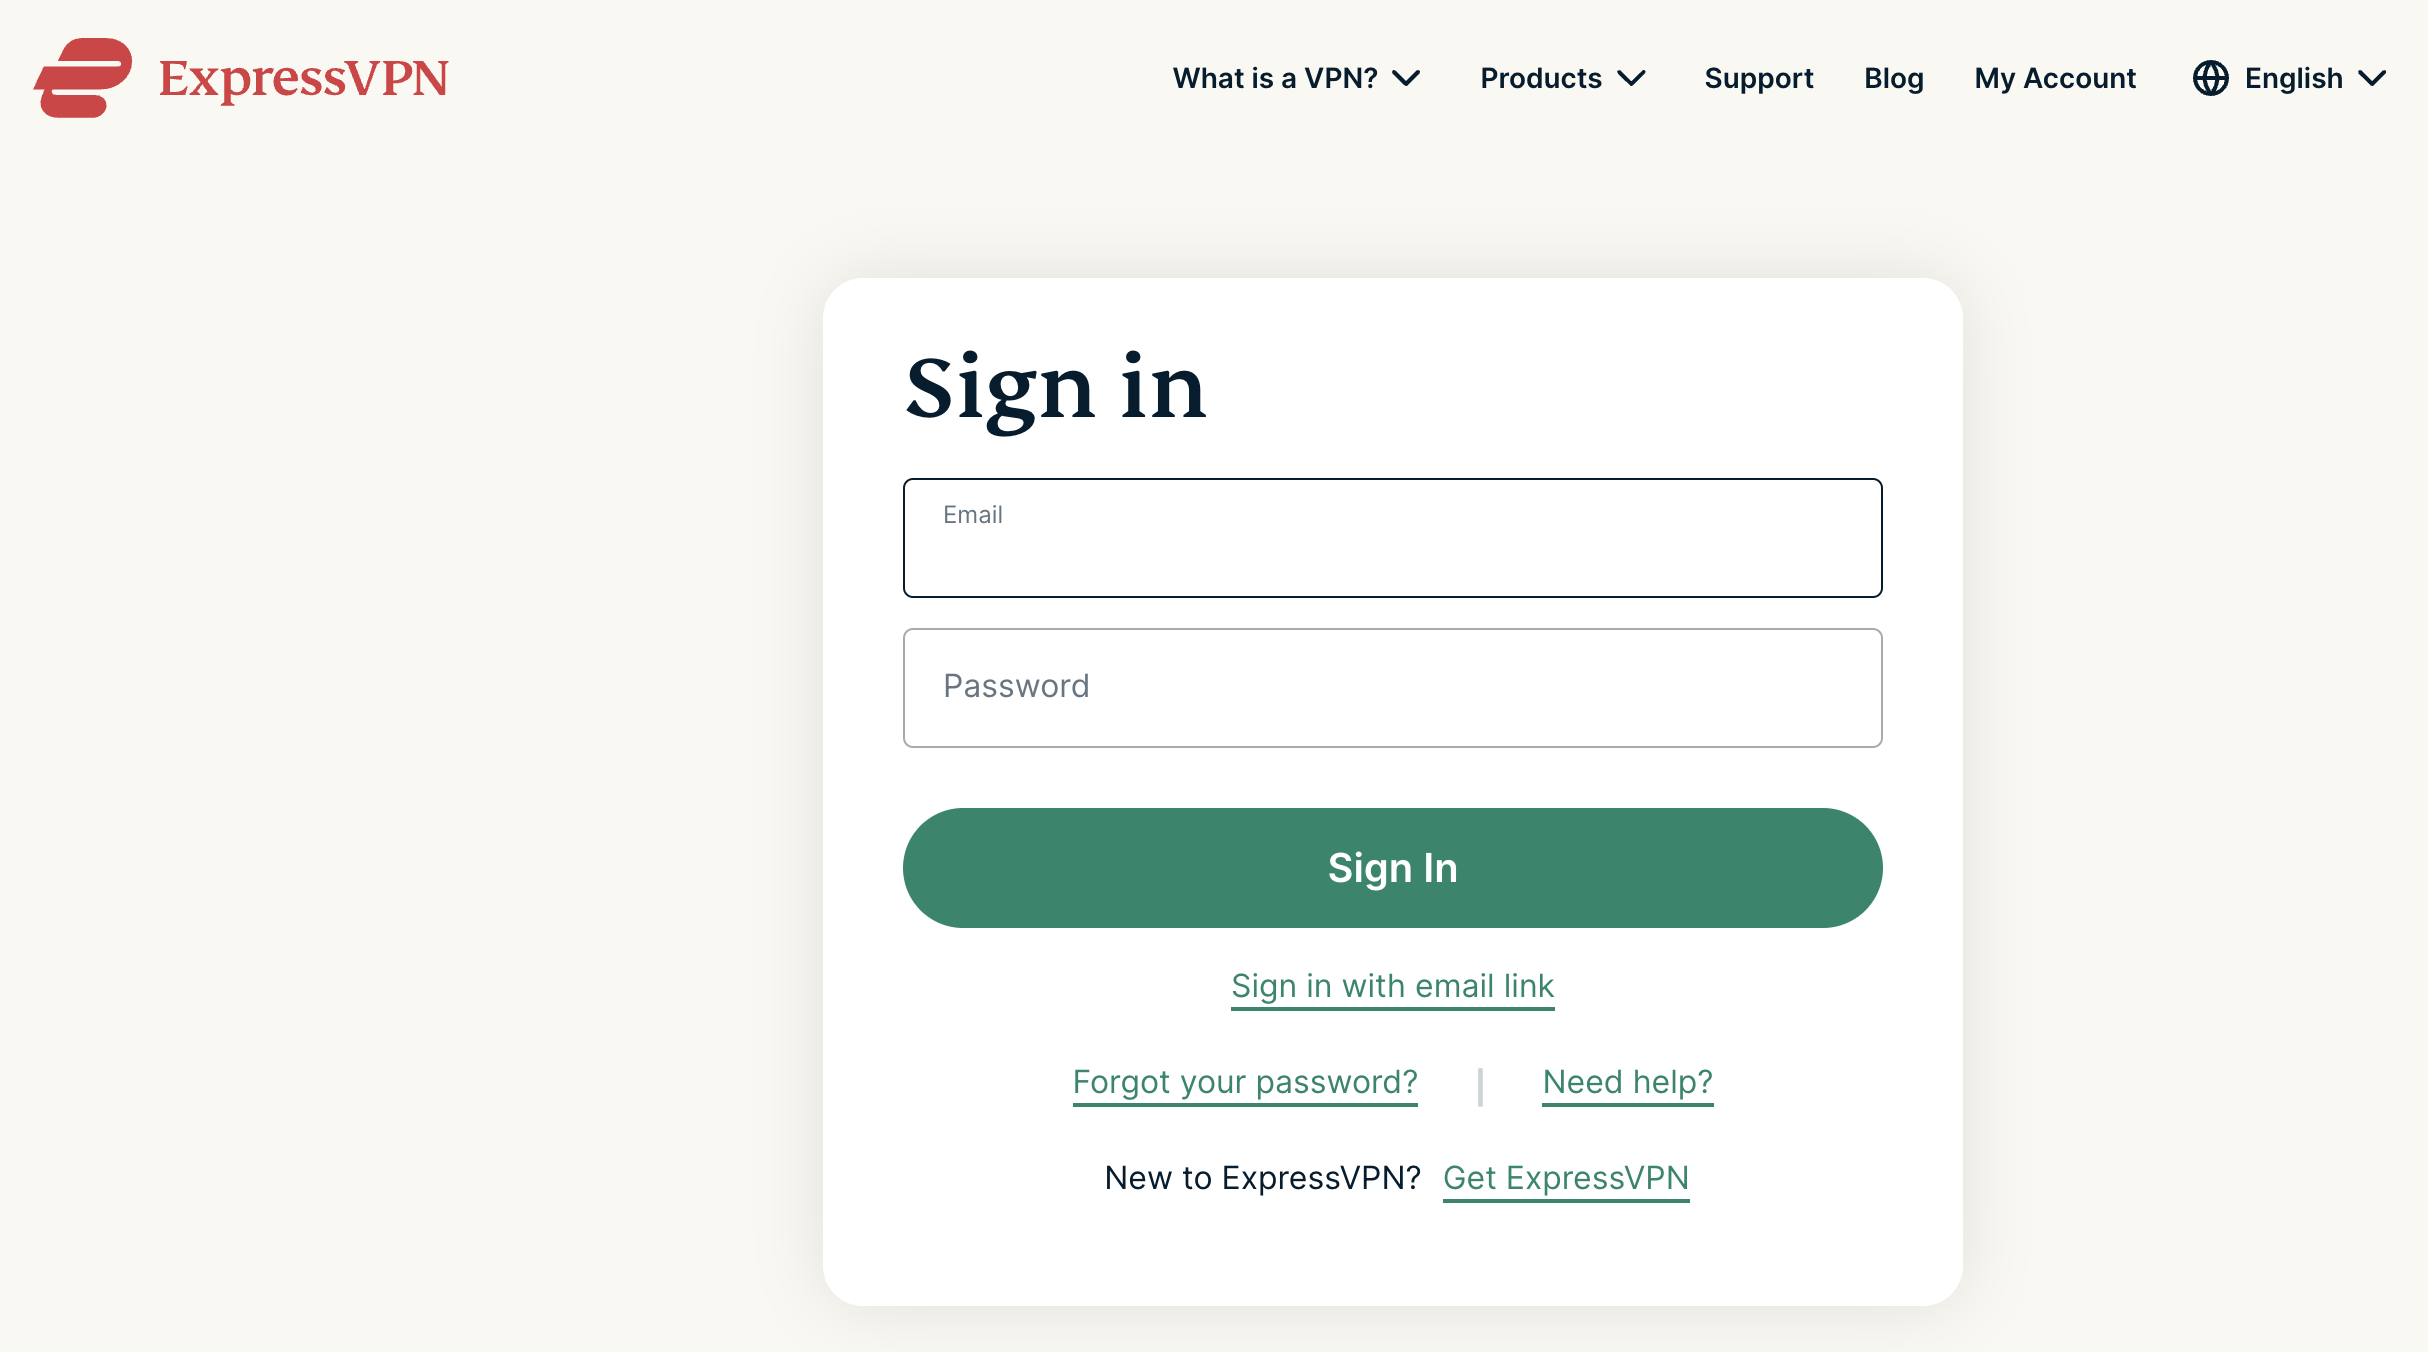
1. Log in to your account on the ExpressVPN website.

ExpressVPN login page

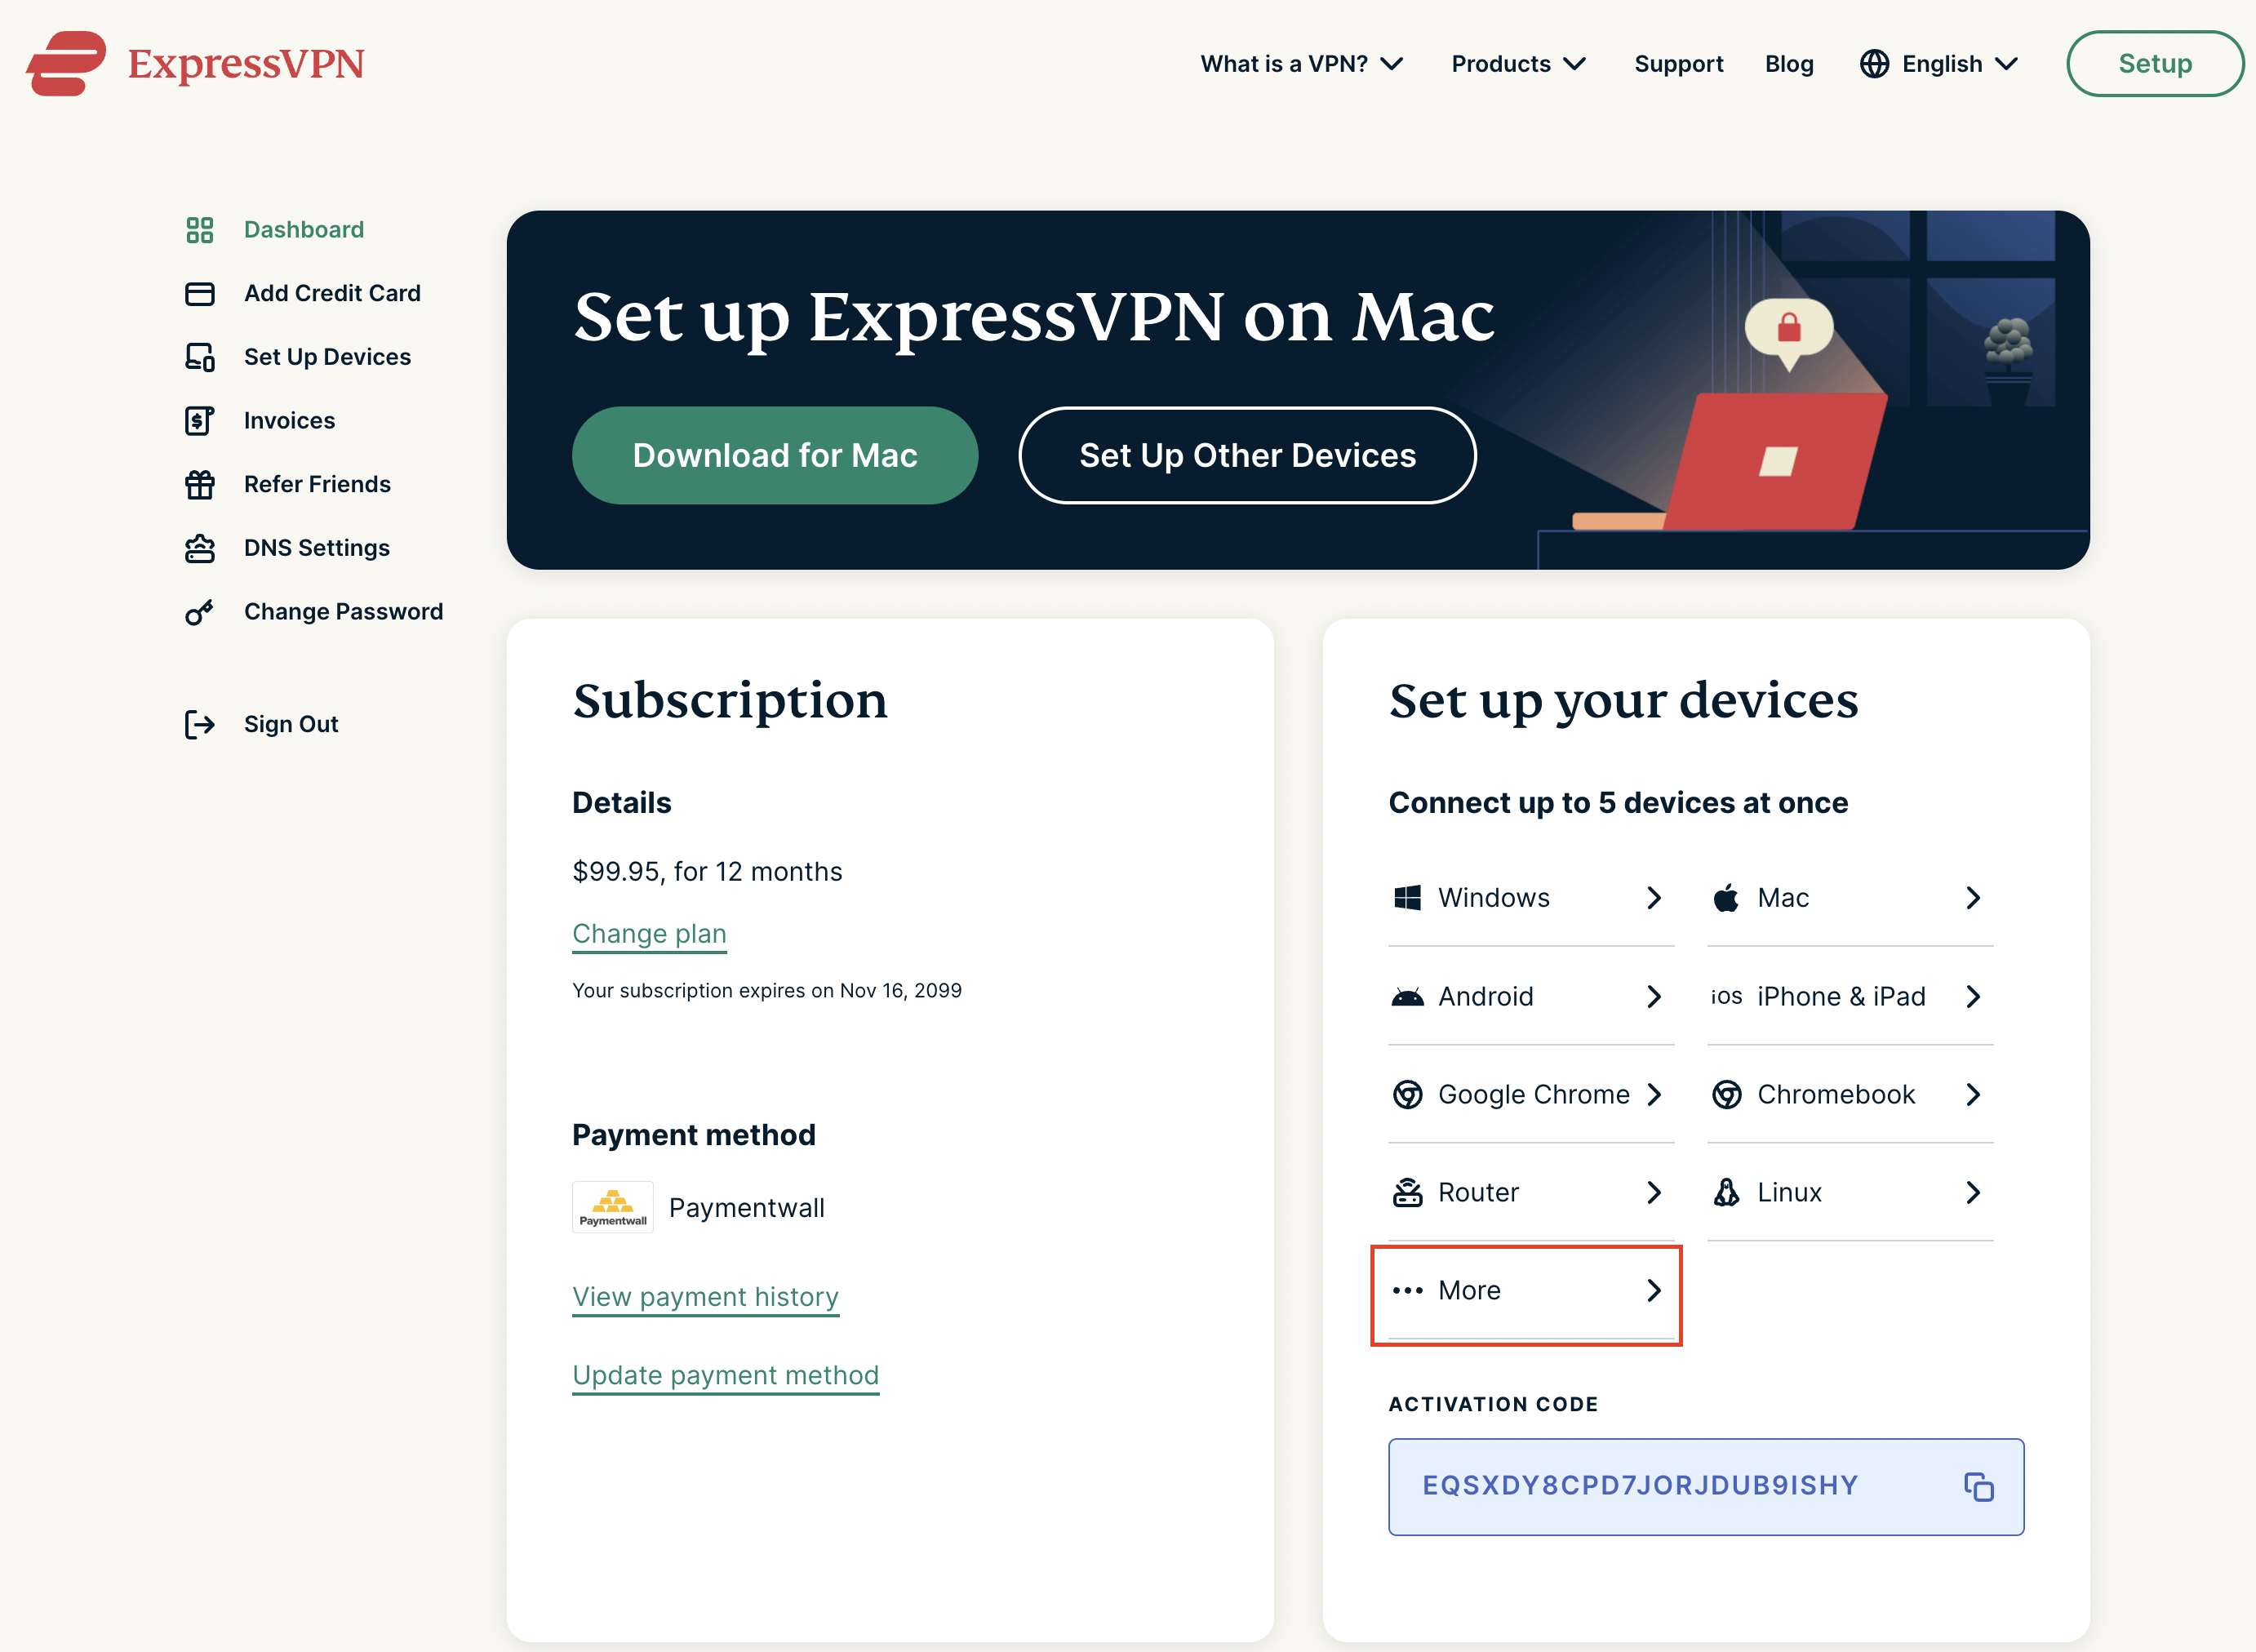
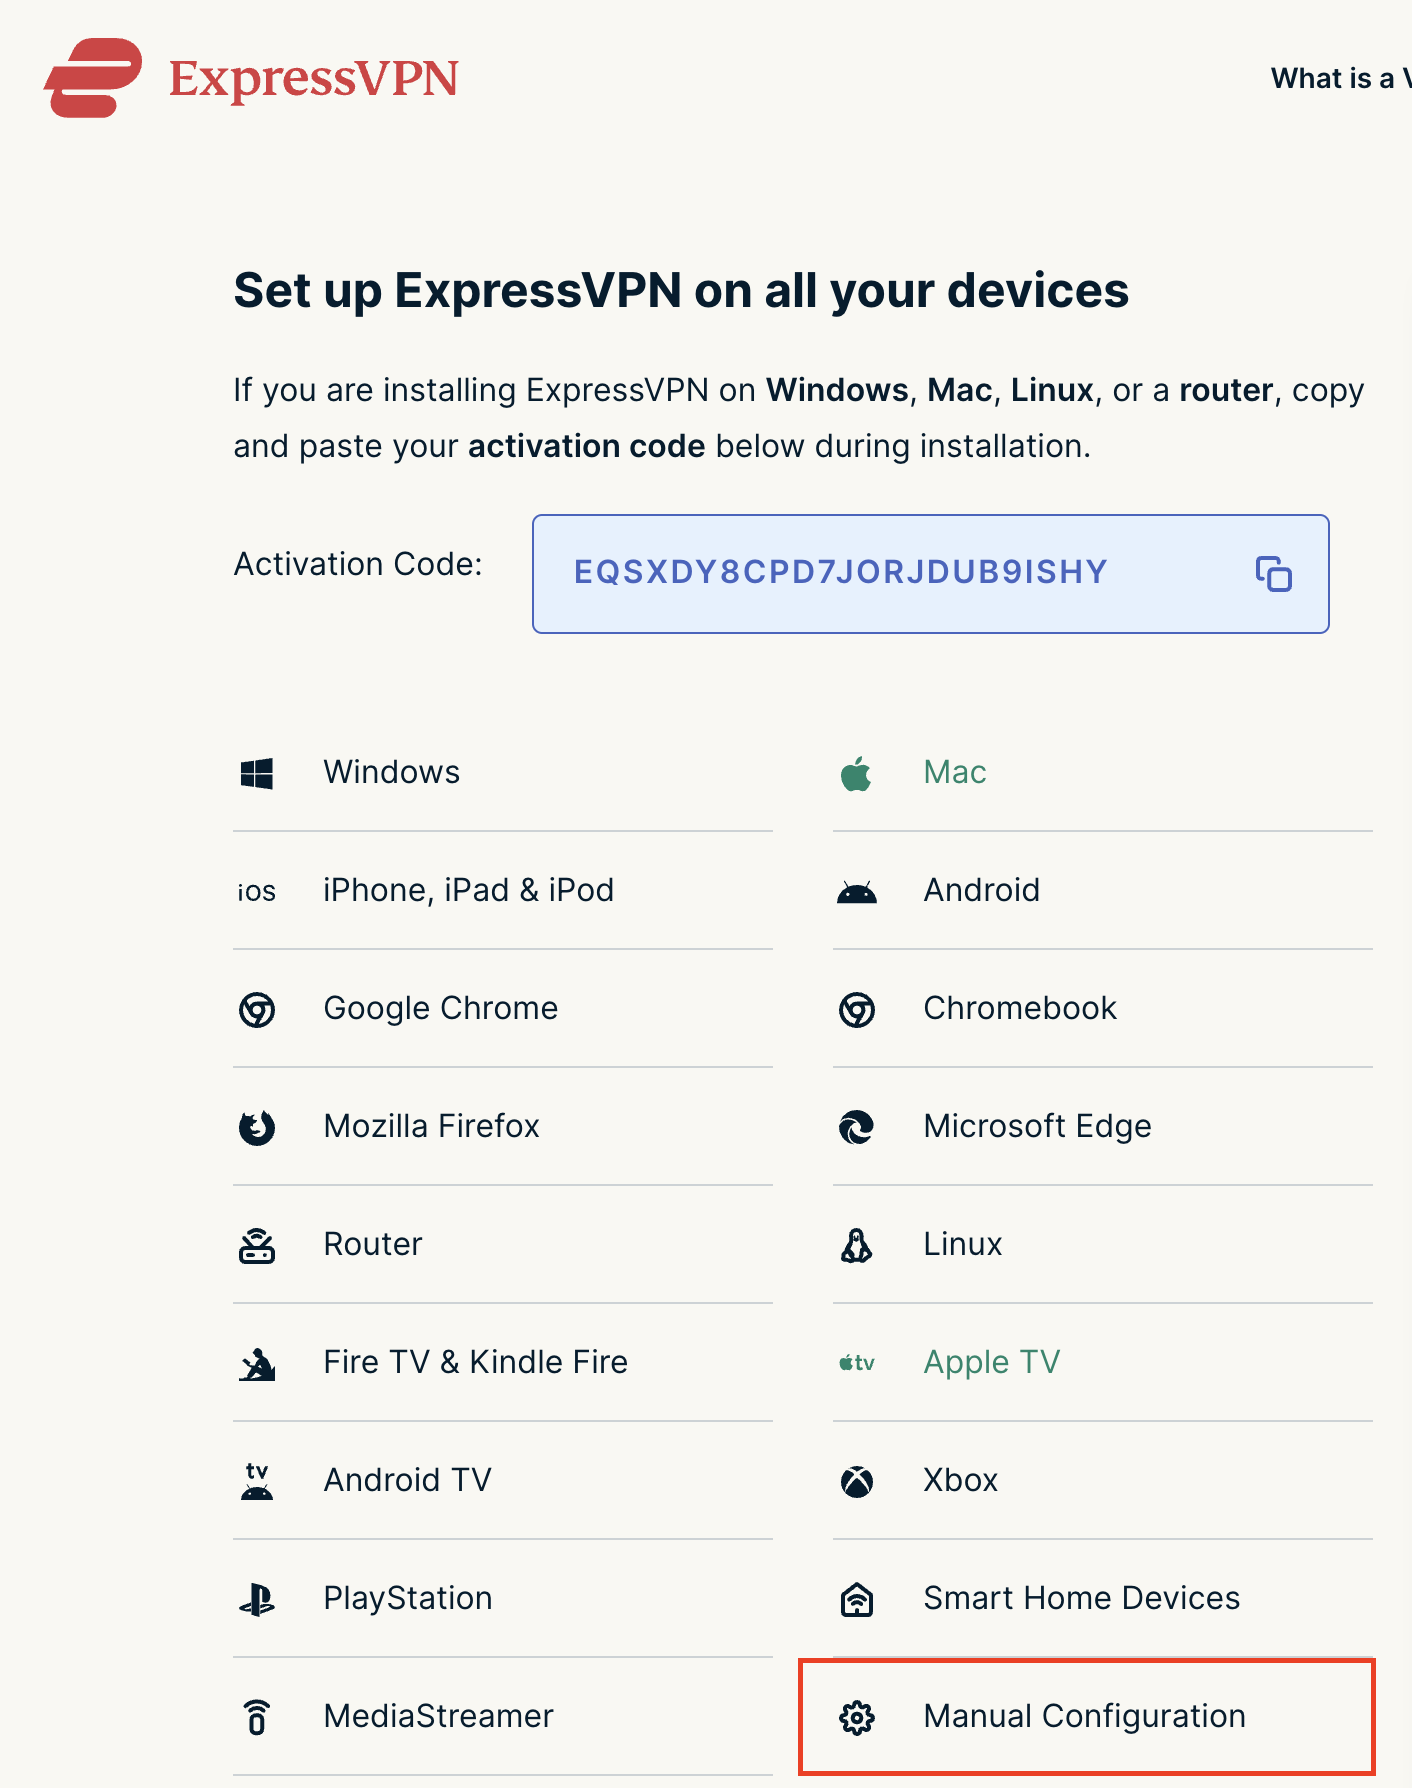
2. Successfully log in with your account information. Select More.

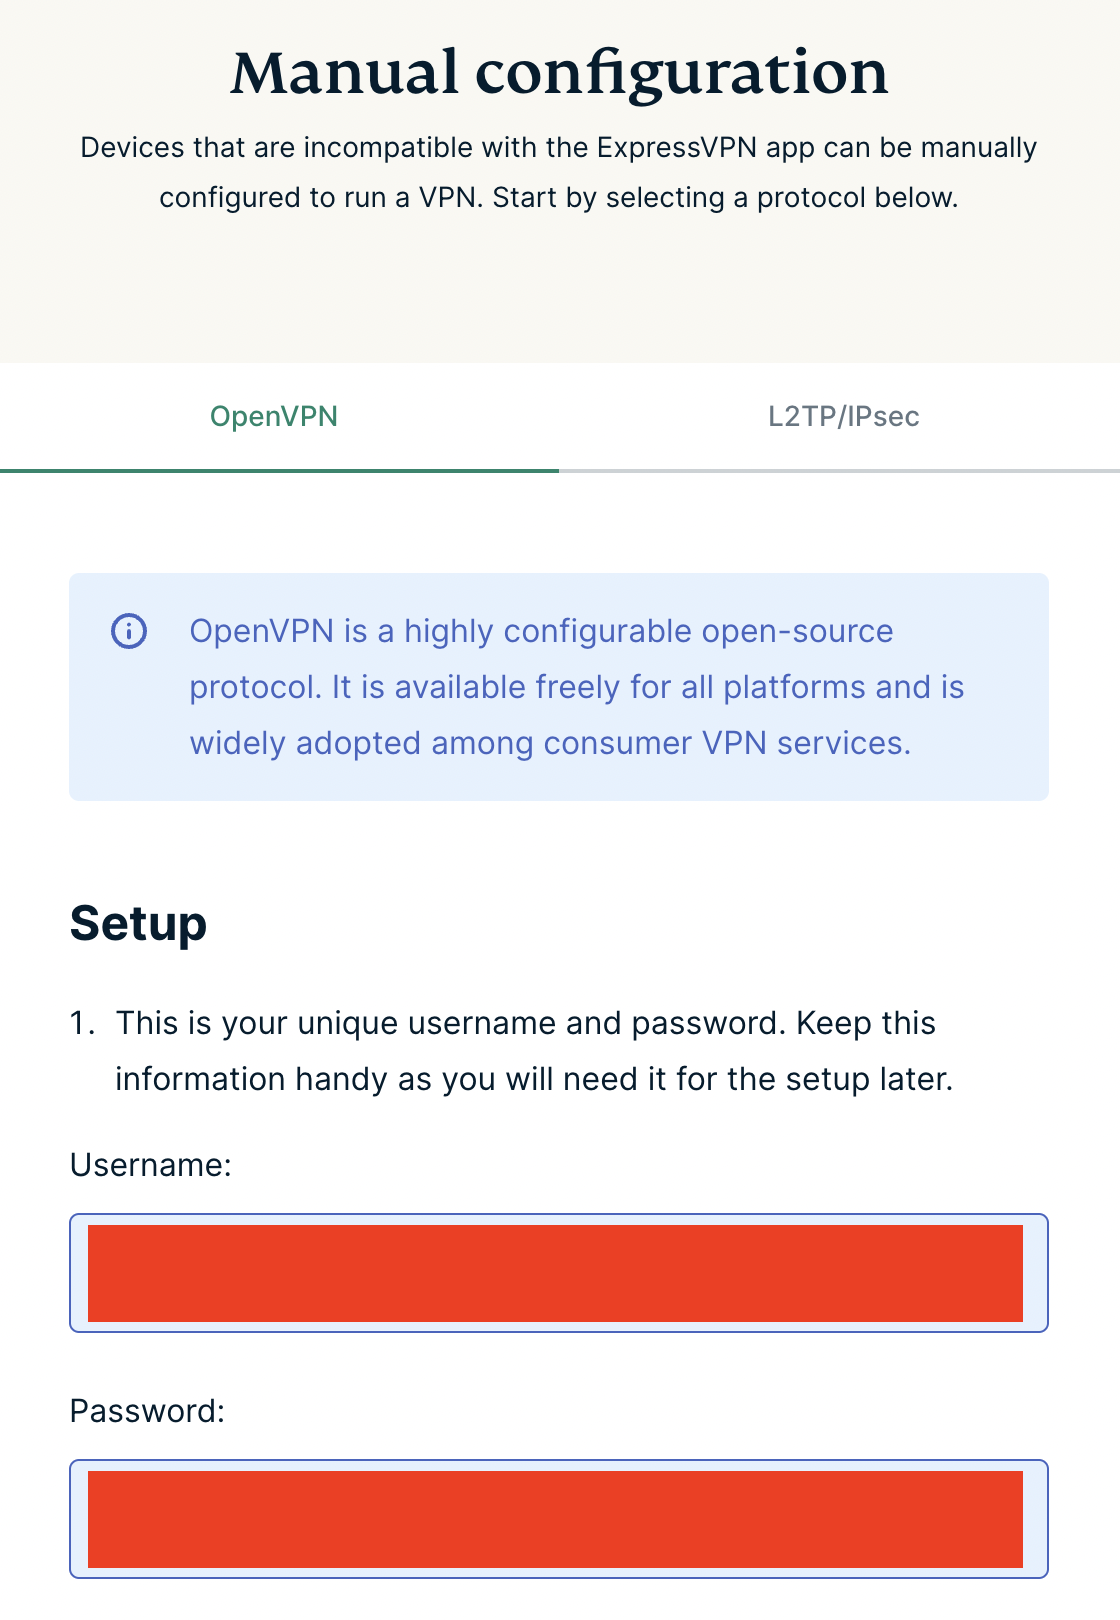
3. Select Manual Configuration and copy the Username and Password that are displayed on the right hand side of the screen.

ExpressVPN Manual Configuration
ExpressVPN username and password

ExpressVPN Server Addresses

Americas

usa-atlanta-ca-version-2.expressnetw.com
usa-boston-ca-version-2.expressnetw.com
usa-chicago-ca-version-2.expressnetw.com
usa-dallas-ca-version-2.expressnetw.com
usa-dallas-2-ca-version-2.expressnetw.com
usa-denver-ca-version-2.expressnetw.com
usa-kansascity-ca-version-2.expressnetw.com
usa-losangeles-ca-version-2.expressnetw.com
usa-losangeles-1-ca-version-2.expressnetw.com
usa-losangeles-2-ca-version-2.expressnetw.com
usa-losangeles-3-ca-version-2.expressnetw.com
usa-los-angeles-4-ca-version-2.expressnetw.com
usa-miami-ca-version-2.expressnetw.com
usa-miami-2-ca-version-2.expressnetw.com
usa-minneapolis-ca-version-2.expressnetw.com
usa-newjersey-1-ca-version-2.expressnetw.com
usa-newjersey-3-ca-version-2.expressnetw.com
usa-newyork-ca-version-2.expressnetw.com
us-new-york-2-ca-version-2.expressnetw.com
usa-phoenix-ca-version-2.expressnetw.com
usa-saltlakecity-ca-version-2.expressnetw.com
usa-sanfrancisco-ca-version-2.expressnetw.com
usa-sanjose-ca-version-2.expressnetw.com
usa-seattle-ca-version-2.expressnetw.com
usa-tampa-1-ca-version-2.expressnetw.com
usa-virginia-ca-version-2.expressnetw.com
usa-washingtondc-ca-version-2.expressnetw.com
usa-washingtondc-2-ca-version-2.expressnetw.com
canada-montreal-ca-version-2.expressnetw.com
canada-toronto-ca-version-2.expressnetw.com
canada-toronto-2-ca-version-2.expressnetw.com
canada-vancouver-ca-version-2.expressnetw.com
mexico-ca-version-2.expressnetw.com
argentina-ca-version-2.expressnetw.com
brazil-ca-version-2.expressnetw.com
brazil-2-ca-version-2.expressnetw.com
chile-ca-version-2.expressnetw.com
colombia-ca-version-2.expressnetw.com
costarica-ca-version-2.expressnetw.com
ecuador-ca-version-2.expressnetw.com
guatemala-ca-version-2.expressnetw.com
panama-ca-version-2.expressnetw.com
peru-ca-version-2.expressnetw.com
uruguay-ca-version-2.expressnetw.com
venezuela-ca-version-2.expressnetw.com

Europe

uk-berkshire-ca-version-2.expressnetw.com
uk-berkshire-2-ca-version-2.expressnetw.com
uk-docklands-ca-version-2.expressnetw.com
uk-east-london-ca-version-2.expressnetw.com
uk-kent-ca-version-2.expressnetw.com
uk-london-ca-version-2.expressnetw.com
france-paris-1-ca-version-2.expressnetw.com
france-paris-2-ca-version-2.expressnetw.com
france-strasbourg-ca-version-2.expressnetw.com
germany-darmstadt-ca-version-2.expressnetw.com
germany-frankfurt-1-ca-version-2.expressnetw.com
germany-frankfurt-2-ca-version-2.expressnetw.com
germany-nuremberg-ca-version-2.expressnetw.com
italy-cosenza-ca-version-2.expressnetw.com
italy-milan-ca-version-2.expressnetw.com
netherlands-amsterdam-ca-version-2.expressnetw.com
netherlands-rotterdam-ca-version-2.expressnetw.com
netherlands-thehague-ca-version-2.expressnetw.com
spain-barcelona-ca-version-2.expressnetw.com
spain-ca-version-2.expressnetw.com
sweden-ca-version-2.expressnetw.com
sweden-2-ca-version-2.expressnetw.com
switzerland-ca-version-2.expressnetw.com
switzerland-2-ca-version-2.expressnetw.com
albania-ca-version-2.expressnetw.com
andorra-ca-version-2.expressnetw.com
armenia-ca-version-2.expressnetw.com
austria-ca-version-2.expressnetw.com
azerbaijan-ca-version-2.expressnetw.com
belarus-ca-version-2.expressnetw.com
belgium-ca-version-2.expressnetw.com
bosniaandherzegovina-ca-version-2.expressnetw.com
bulgaria-ca-version-2.expressnetw.com
croatia-ca-version-2.expressnetw.com
cyprus-ca-version-2.expressnetw.com
czechrepublic-ca-version-2.expressnetw.com
denmark-ca-version-2.expressnetw.com
estonia-ca-version-2.expressnetw.com
finland-ca-version-2.expressnetw.com
georgia-ca-version-2.expressnetw.com
greece-ca-version-2.expressnetw.com
hungary-ca-version-2.expressnetw.com
iceland-ca-version-2.expressnetw.com
ireland-ca-version-2.expressnetw.com
isleofman-ca-version-2.expressnetw.com
jersey-ca-version-2.expressnetw.com
latvia-ca-version-2.expressnetw.com
liechtenstein-ca-version-2.expressnetw.com
lithuania-ca-version-2.expressnetw.com
luxembourg-ca-version-2.expressnetw.com
macedonia-ca-version-2.expressnetw.com
malta-ca-version-2.expressnetw.com
moldova-ca-version-2.expressnetw.com
monaco-ca-version-2.expressnetw.com
montenegro-ca-version-2.expressnetw.com
norway-ca-version-2.expressnetw.com
poland-ca-version-2.expressnetw.com
portugal-ca-version-2.expressnetw.com
romania-ca-version-2.expressnetw.com
serbia-ca-version-2.expressnetw.com
slovakia-ca-version-2.expressnetw.com
slovenia-ca-version-2.expressnetw.com
ukraine-ca-version-2.expressnetw.com

Asia Pacific

australia-brisbane-ca-version-2.expressnetw.com
australia-melbourne-ca-version-2.expressnetw.com
australia-perth-ca-version-2.expressnetw.com
australia-sydney-ca-version-2.expressnetw.com
australia-sydney-2-ca-version-2.expressnetw.com
australia-sydney-3-ca-version-2.expressnetw.com
hongkong-2-ca-version-2.expressnetw.com
hongkong4-ca-version-2.expressnetw.com
hongkong-1-ca-version-2.expressnetw.com
japan-tokyo-1-ca-version-2.expressnetw.com
japan-tokyo-2-ca-version-2.expressnetw.com
india-chennai-ca-version-2.expressnetw.com
india-mumbai-1-ca-version-2.expressnetw.com
singapore-cbd-ca-version-2.expressnetw.com
singapore-jurong-ca-version-2.expressnetw.com
southkorea-ca-version-2.expressnetw.com
southkorea2-ca-version-2.expressnetw.com
bangladesh-ca-version-2.expressnetw.com
bhutan-ca-version-2.expressnetw.com
brunei-ca-version-2.expressnetw.com
cambodia-ca-version-2.expressnetw.com
indonesia-ca-version-2.expressnetw.com
kazakhstan-ca-version-2.expressnetw.com
kyrgyzstan-ca-version-2.expressnetw.com
laos-ca-version-2.expressnetw.com
macau-ca-version-2.expressnetw.com
malaysia-ca-version-2.expressnetw.com
mongolia-ca-version-2.expressnetw.com
myanmar-ca-version-2.expressnetw.com
nepal-ca-version-2.expressnetw.com
newzealand-ca-version-2.expressnetw.com
pakistan-ca-version-2.expressnetw.com
ph-via-sing-ca-version-2.expressnetw.com
srilanka-ca-version-2.expressnetw.com
taiwan-3-ca-version-2.expressnetw.com
thailand-ca-version-2.expressnetw.com
vietnam-ca-version-2.expressnetw.com

Middle East and Africa

algeria-ca-version-2.expressnetw.com
israel-ca-version-2.expressnetw.com
kenya-ca-version-2.expressnetw.com
southafrica-ca-version-2.expressnetw.com

DD-WRT Router Setup for ExpressVPN

Navigate to Services > VPN

Enter ExpressVPN settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

Copy and paste the server you would like to connect to from the server list above. Be sure there are no extra spaces or characters.

If you wish to change ExpressVPN connection locations, THE ONLY SETTING YOU NEED TO CHANGE IS THE EXPRESSVPN SERVER ADDRESS.*

Port

1195

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-256-CBC

Hash Algorithm

SHA512

User Pass Authentication

Enable

Username

Enter the Username you found in the Manual Config section.

Password

Enter the Password you found in the Manual Config section.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

Adaptive

NAT

Enable

Firewall Protection

Enable

nsCertType verification

Checked

TLS Auth Key

-----BEGIN OpenVPN Static key V1-----
48d9999bd71095b10649c7cb471c1051
b1afdece597cea06909b99303a18c674
01597b12c04a787e98cdb619ee960d90
a0165529dc650f3a5c6fbe77c91c137d
cf55d863fcbe314df5f0b45dbe974d9b
de33ef5b4803c3985531c6c23ca6906d
6cd028efc8585d1b9e71003566bd7891
b9cc9212bcba510109922eed87f5c8e6
6d8e59cbd82575261f02777372b2cd4c
a5214c4a6513ff26dd568f574fd40d6c
d450fc788160ff68434ce2bf6afb00e7
10a3198538f14c4d45d84ab42637872e
778a6b35a124e700920879f1d003ba93
dccdb953cdf32bea03f365760b0ed800
2098d4ce20d045b45a83a8432cc73767
7aed27125592a7148d25c87fdbe0a3f6
-----END OpenVPN Static key V1-----

Additional Config

persist-key
persist-tun
fragment 1300
mssfix 1450
keysize 256

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

-----BEGIN CERTIFICATE-----
MIIF+DCCA+CgAwIBAgIBATANBgkqhkiG9w0BAQ0FADCBhDELMAkGA1UEBhMCVkcx
DDAKBgNVBAgMA0JWSTETMBEGA1UECgwKRXhwcmVzc1ZQTjETMBEGA1UECwwKRXhw
cmVzc1ZQTjEWMBQGA1UEAwwNRXhwcmVzc1ZQTiBDQTElMCMGCSqGSIb3DQEJARYW
c3VwcG9ydEBleHByZXNzdnBuLmNvbTAeFw0xNTEwMjEwMDAwMDBaFw0yNjA0MDEy
MTEyMDBaMIGEMQswCQYDVQQGEwJWRzEMMAoGA1UECAwDQlZJMRMwEQYDVQQKDApF
eHByZXNzVlBOMRMwEQYDVQQLDApFeHByZXNzVlBOMRYwFAYDVQQDDA1FeHByZXNz
VlBOIENBMSUwIwYJKoZIhvcNAQkBFhZzdXBwb3J0QGV4cHJlc3N2cG4uY29tMIIC
IjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAxzXvHZ25OsESKRMQFINHJNqE
9kVRLWJS50oVB2jxobudPhCsWvJSApvar8CB2RrqkVMhXu2HT3FBtDL91INg070q
AyjjRpzEbDPWqQ1+G0tk0sjiJt2mXPJK2IlNFnhe6rTs09Pkpcp8qRhfZay/dIlm
agohQAr4JvYL1Ajg9A3sLb8JkY03H6GhOF8EKYTqhrEppCcg4sQKQhNSytRoQAm8
Ta+tnTYIedwWpqjUXP9YXFOvljPaixfYug24eAkpTjeuWTcELSyfnuiBeK+z9+5O
YunhqFt2QZMq33kLFZGMN2gHRCzngxxphurypsPRo7jiFgQI1yLt8uZsEZ+otGEK
91jjKfOC+g9TBy2RUtxk1neWcQ6syXDuc3rBNrGA8iM0ZoEqQ1BC8xWr3NYlSjqN
+1mgpTAX3/Dxze4GzHd7AmYaYJV8xnKBVNphlMlg1giCAu5QXjMxPbfCgZiEFq/u
q0SOKQJeT3AI/uVPSvwCMWByjyMbDpKKAK8Hy3UT5m4bCNu8J7bxj+vdnq0A2HPw
tF0FwBl/TIM3zNsyFrZZ0j6jLRT50mFsgDBKcD4L/J5rjdCsKPu5rodhxe38rCx2
GknP1Zkov4yoVCcR48+CQwg3oBkq0/EflvWUvcYApzs9SomUM/g+8Q/V0WOfJmFW
uxN9YntZlnzHRSRjrvMCAwEAAaNzMHEwHQYDVR0OBBYEFIzmQGj8xS+0LLklwqHD
45VVOZRJMB8GA1UdIwQYMBaAFIzmQGj8xS+0LLklwqHD45VVOZRJMA8GA1UdEwEB
/wQFMAMBAf8wCwYDVR0PBAQDAgEGMBEGCWCGSAGG+EIBAQQEAwIBFjANBgkqhkiG
9w0BAQ0FAAOCAgEAbHfuMKtojm1NgX7qSU2Rm2B5L8G0FuFP0L40dj8O5WHt45j2
z8coMK90vrUnQEZNQmRzot7v3XjVzVlxBWYSsCEApTsSDNi/4BNFP8H/BUUtJuy2
GFTO4wDVJnqNkZOHBmyVD75s1Y+W8a+zB4jkMeDEhOHZdwQ0l1fJDDgXal5f1UT5
F5WH6/RwHmWTwX4GxuCiIVtx70CjkXqhM8yZtTp1UtHLRNYcNSIes0vrAPHPgoA5
z9B8UvsOjuP+mfcjzi0LGGrY+2pJu0BKO2dRnarIZZABETIisI3FokoTszx5jpRP
yxyUTuRDKWHrvi0PPtOmC8nFahfugWFUi6uBsqCaSeuex+ahnTPCq0b1l0Ozpg0Y
eE8CW1TL9Y92b01up2c+PP6wZOIm3JyTH+L5smDFbh80V42dKyGNdPXMg5IcJhj3
YfAy4k8h/qbWY57KFcIzKx40bFsoI7PeydbGtT/dIoFLSZRLW5bleXNgG9mXZp27
0UeEC6CpATCS6uVl8LVT1I02uulHUpFaRmTEOrmMxsXGt6UAwYTY55K/B8uuID34
1xKbeC0kzhuN2gsL5UJaocBHyWK/AqwbeBttdhOCLwoaj7+nSViPxICObKrg3qav
GNCvtwy/fEegK9X/wlp2e2CFlIhFbadeXOBr9Fn8ypYPP17mTqe98OJYM04=
-----END CERTIFICATE-----

Public Client Cert

-----BEGIN CERTIFICATE-----
MIIDTjCCAregAwIBAgIDKzZvMA0GCSqGSIb3DQEBCwUAMIGFMQswCQYDVQQGEwJV
UzELMAkGA1UECBMCQ0ExFTATBgNVBAcTDFNhbkZyYW5jaXNjbzEVMBMGA1UEChMM
Rm9ydC1GdW5zdG9uMRgwFgYDVQQDEw9Gb3J0LUZ1bnN0b24gQ0ExITAfBgkqhkiG
9w0BCQEWEm1lQG15aG9zdC5teWRvbWFpbjAgFw0xNjExMDMwMzA2MThaGA8yMDY2
MTEwMzAzMDYxOFowgYoxCzAJBgNVBAYTAlZHMQwwCgYDVQQIDANCVkkxEzARBgNV
BAoMCkV4cHJlc3NWUE4xEzARBgNVBAsMCkV4cHJlc3NWUE4xHDAaBgNVBAMME2V4
cHJlc3N2cG5fY3VzdG9tZXIxJTAjBgkqhkiG9w0BCQEWFnN1cHBvcnRAZXhwcmVz
c3Zwbi5jb20wggEiMA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCrOYt/KOi2
uMDGev3pXg8j1SO4J/4EVWDF7vJcKr2jrZlqD/zuAFx2W1YWvwumPO6PKH4PU962
1aNdiumaUkv/RplCfznnnxqobhJuTE2oA+rS1bOq+9OhHwF9jgNXNVk+XX4d0toS
T5uGE6Z3OdmPBur8o5AlCf78PDSAwpFOw5HrgLqOEU4hTweC1/czX2VsvsHv22HR
I6JMZgP8gGQii/p9iukqfaJvGdPciL5p1QRBUQIi8P8pNvEp1pVIpxYj7/LOUqb2
DxFvgmp2v1IQ0Yu88SWsFk84+xAYHzfkLyS31Sqj5uLRBnJqx3fIlOihQ50GI72f
wPMwo+OippvVAgMBAAGjPzA9MAwGA1UdEwEB/wQCMAAwDgYDVR0PAQH/BAQDAgSw
MB0GA1UdDgQWBBSkBM1TCX9kBgFsv2RmOzudMXa9njANBgkqhkiG9w0BAQsFAAOB
gQA+2e4b+33zFmA+1ZQ46kWkfiB+fEeDyMwMLeYYyDS2d8mZhNZKdOw7dy4Ifz9V
qzp4aKuQ6j61c6k1UaQQL0tskqWVzslSFvs9NZyUAJLLdGUc5TT2MiLwiXQwd4Uv
H6bGeePdhvB4+ZbW7VMD7TE8hZhjhAL4F6yAP1EQvg3LDA==
-----END CERTIFICATE-----

Private Client Key

-----BEGIN RSA PRIVATE KEY-----
MIIEpAIBAAKCAQEAqzmLfyjotrjAxnr96V4PI9UjuCf+BFVgxe7yXCq9o62Zag/8
7gBcdltWFr8Lpjzujyh+D1PettWjXYrpmlJL/0aZQn85558aqG4SbkxNqAPq0tWz
qvvToR8BfY4DVzVZPl1+HdLaEk+bhhOmdznZjwbq/KOQJQn+/Dw0gMKRTsOR64C6
jhFOIU8Hgtf3M19lbL7B79th0SOiTGYD/IBkIov6fYrpKn2ibxnT3Ii+adUEQVEC
IvD/KTbxKdaVSKcWI+/yzlKm9g8Rb4Jqdr9SENGLvPElrBZPOPsQGB835C8kt9Uq
o+bi0QZyasd3yJTooUOdBiO9n8DzMKPjoqab1QIDAQABAoIBAHgsekC0SKi+AOcN
OZqJ3pxqophE0V7fQX2KWGXhxZnUZMFxGTc936deMYzjZ1y0lUa6x8cgOUcfqHol
3hDmw9oWBckLHGv5Wi9umdb6DOLoZO62+FQATSdfaJ9jheq2Ub2YxsRN0apaXzB6
KDKz0oM0+sZ4Udn9Kw6DfuIELRIWwEx4w0v3gKW7YLC4Jkc4AwLkPK03xEA/qImf
kCmaMPLhrgVQt+IFfP8bXzL7CCC04rNU/IS8pyjex+iUolnQZlbXntF7Bm4V2mz0
827ZVqrgAb/hEQRlsTW3rRkVh+rrdoUE7BCZRTFmRCbLoShjN6XuSf4sAus8ch4U
EN12gN0CgYEA4o/tSvij1iPaXLmt4KOEuxqmSGB8MLKhFde8lBbNdrDgxiIH9bH7
khKx15XRTX0qLDbs8b2/UJygZG0Aa1kIBqZTXTgeMAuxPRTesALJPdqQ/ROnbJcd
FkI7gllrAG8VB0fH4wTRsRd0vWEB6YlCdE107u6LEsLAHxOj9Q5819cCgYEAwXjx
9RkQ2qITBx5Ewib8YsltA0n3cmRomPicLlsnKV5DfvyCLpFIsZ1h3f9dUpfxRLwz
p8wcoLiq9cCoOGdu1udw/yBTqmhaXWhUK/g77f9Ze2ZB1OEhuyKLYJ1vW/h/Z/a1
aPCMxZqsDTPCePsuO8Cez5gqs8LjM3W7EyzRxDMCgYEAvhHrDFt975fSiLoJgo0M
PIAGAnBXn+8sLwv3m/FpW+rWF8LTFK/Fku12H5wDpNOdvswxijkauIE+GiJMGMLv
dcyx4WHECaC1h73reJRNykOEIZ0Md5BrCZJ1JEzp9Mo8RQhWTEFtvfkkqgApP4g0
pSeaMx0StaGG1kt+4IbP+68CgYBrZdQKlquAck/Vt7u7eyDHRcE5/ilaWtqlb/xi
zz7h++3D5C/v4b5UumTFcyg+3RGVclPKZcfOgDSGzzeSd/hTW46iUTOgeOUQzQVM
kzPRXdoyYgVRQtgSpY5xR3O1vjAbahwx8LZ0SvQPMBhYSDbV/Isr+fBacWjl/Aip
EEwxeQKBgQDdrAEnVlOFoCLw4sUjsPoxkLjhTAgI7CYk5NNxX67Rnj0tp+Y49+sG
Uhl5sCGfMKkLShiON5P2oxZa+B0aPtQjsdnsFPa1uaZkK4c++SS6AetzYRpVDLmL
p7/1CulE0z3O0sBekpwiuaqLJ9ZccC81g4+2j8j6c50rIAct3hxIxw==
-----END RSA PRIVATE KEY-----

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful ExpressVPN connection

Navigate to Status > OpenVPN.

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit ExpressVPN’s IP Check to verify your new IP address and virtual location.
In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to ExpressVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the ExpressVPN server

  1. Copy the new ExpressVPN server address from the above server list.
  2. Paste the server into the Server IP/Name field.
  3. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

StrongVPN WireGuard Setup

TeamFlashRouters · Jan 8, 2021 ·

DD-WRT Router Setup for StrongVPN WireGuard

StrongVPN Wireguard DD-WRT setup is now officially supported by FlashRouters. Follow the steps below to gather all the required information to complete your Wireguard router setup.

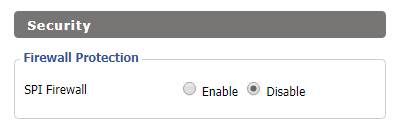
Navigate to Security > Firewall

Set SPI Firewall to Disable.

Wireless Client Bridge Setup on FlashRouter DD-WRT - Disable Firewall

Click Save at the bottom of the page.

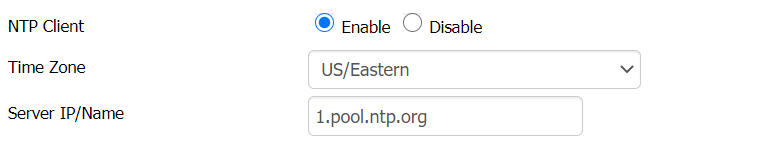
Select your actual time zone for you physical location from the dropdown and enter 1.pool.ntp.org in the Server IP/Name dropdown.

WireGuard for StrongVPN DD-WRT set Time Zone

Click Apply Settings at the bottom of the page.

Preparing for StrongVPN WireGuard Setup

Obtain your StrongVPN WireGuard Information

If you are not already a StrongVPN user Sign Up Now.

1. Log in to your account on the StrongVPN website.

WireGuard for StrongVPN account login

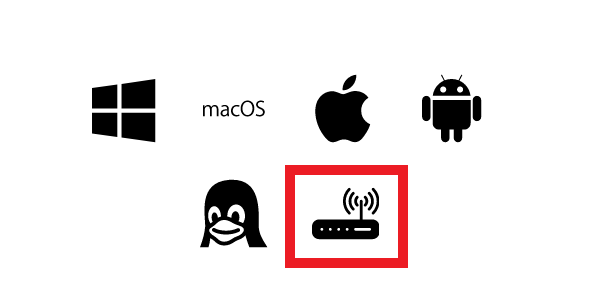
2. Select Router icon as the Platform

Select Router for StrongVPN WireGuard Platform

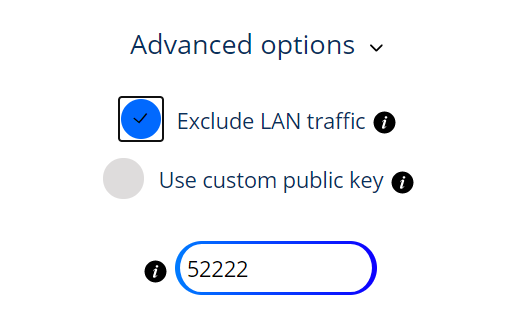
3. Select the Advanced Options dropdown and then check Exclude LAN Traffic and set any value between 52000 and 60000 in the Custom Port field.

WireGuard for StrongVPN set Custom Port

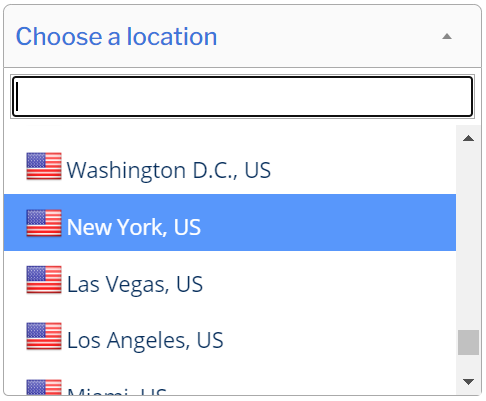
4. Select the Server Location from the dropdown that you would like to connect to.

Select the StrongVPN Wireguard server location

5. Select the Generate at the bottom of the page.

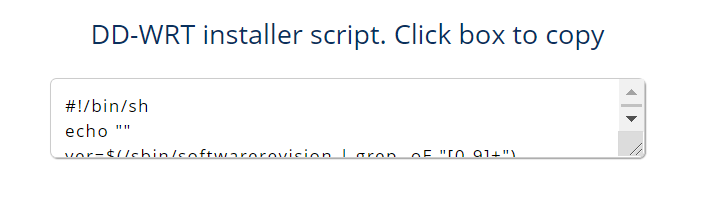
6. Click the DD-WRT installer script box to copy.

DD-WRT installer script WireGuard for StrongVPN

Enter StrongVPN WireGuard Script

Navigate to Administration > Commands

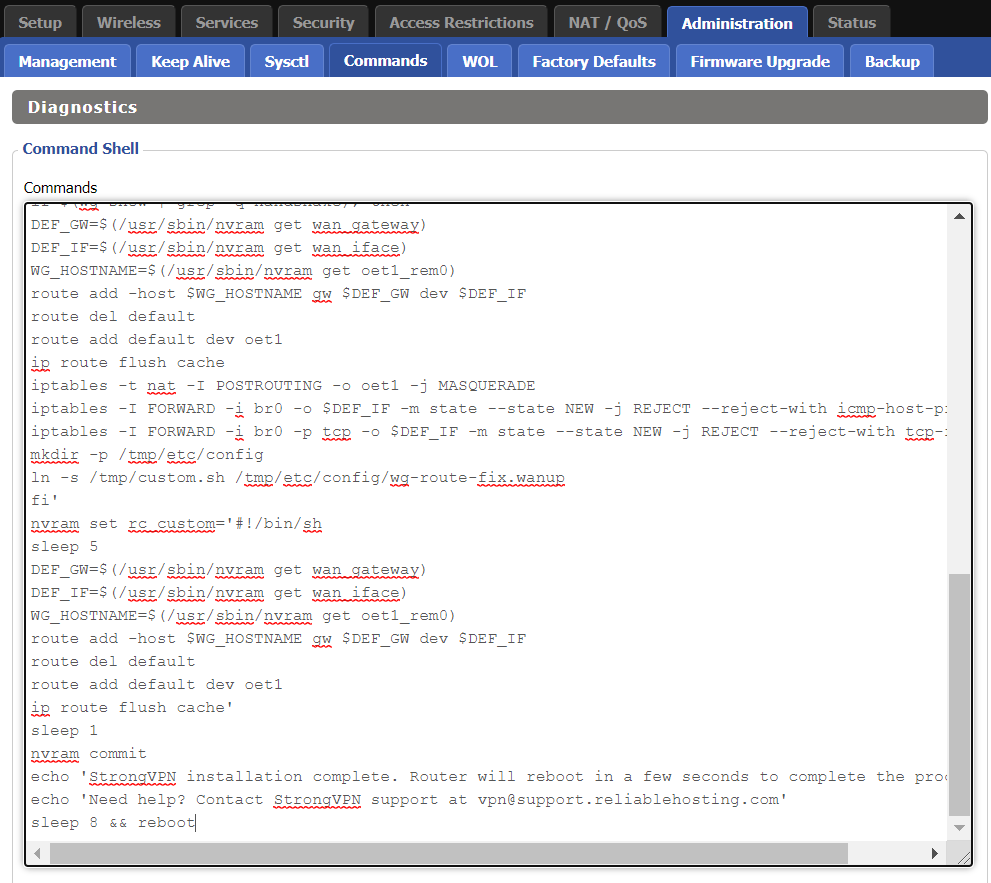
Paste the StrongVPN Script that was copied in the empty Commands Shell.

WireGuard for StrongVPN install script

Delete the very last line sleep 8 && reboot.

Click Save Custom (or Save Custom Script may appear depending on your firmware build, they are the same thing)

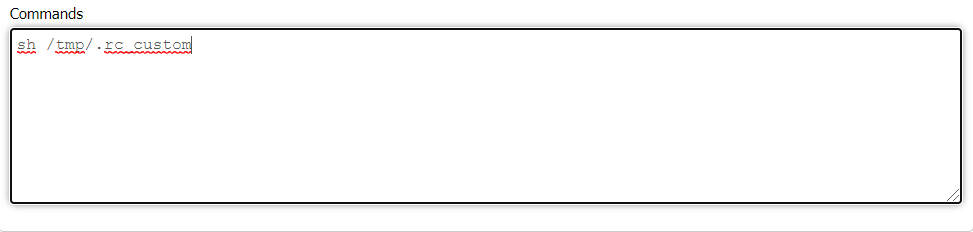
Copy the line below and paste into the empty Commands Shell.

WireGuard for StrongVPN script 2
sh /tmp/.rc_custom

Click Run Commands.

Wait two minutes and then power the FlashRouter off and back on. Reconnect to the FlashRouter’s network when it has booted back up.

Verify a successful StrongVPN WireGuard connection

Navigate to Setup > Tunnels

  1. You should now see that page filled in with WireGuard info.
  2. Visit StrongVPN’s IP Check to verify your new IP address and virtual location.
Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Device Settings That Can Interfere With Your Router VPN

Dave · Oct 6, 2026 ·

If your router VPN is connected and working on other devices but one phone, tablet, computer, or streaming device shows the wrong IP address, wrong location, cannot access certain websites, or behaves differently, check the affected device before changing the router.

VPN applications, privacy features, custom DNS settings, antivirus software, firewalls, browser settings, and corporate security software can all change how traffic is handled directly on a device.

This guide applies to all FlashRouter types and VPN providers.


Jump to a Section

  • Start Here: Router or Device?
  • Device VPN Applications
  • iPhone & iPad Privacy Settings
  • Android VPN & DNS Settings
  • Security, Firewall & Browser Settings
  • Run a Clean VPN Test

Start Here: Is the Problem the Router or One Device?

Before changing your router VPN configuration, compare the affected device with another device connected to the same FlashRouter.

If several devices show the correct VPN IP and location while only one device does not, the router VPN is already demonstrating that it can route traffic through the VPN.

Focus troubleshooting on the affected device.

If every device connected to the FlashRouter has the same VPN problem, continue with router-level VPN troubleshooting instead.

Privacy Hero users should also check the Privacy Hero dashboard. If the VPN itself displays Failed, Disconnected, Connecting, or a timeout error, troubleshoot that connection before changing device settings.

  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero NordVPN Not Connecting or Showing Timeout Errors

Disconnect VPN Applications Running on the Device

Do not run a VPN application directly on the device while troubleshooting a VPN running on your router.

This includes applications from NordVPN, ExpressVPN, Surfshark, Proton VPN, IPVanish, Private Internet Access, Mullvad, corporate VPN providers, and other VPN services.

If both the router VPN and device VPN are active, the device VPN can take control of that device’s traffic after it passes through the router.

This can cause:

  • An unexpected public IP address.
  • An unexpected VPN location.
  • Websites or applications not loading.
  • Streaming region problems.
  • DNS problems.
  • Slow or unstable connections.
  • One device behaving differently from other devices on the same router.

Disconnect the VPN application completely before testing the router VPN.

Closing the VPN app window may not disconnect the VPN. Confirm in the application or device network settings that the device-level VPN is actually disconnected.

iPhone and iPad: Check Private Relay and Limit IP Address Tracking

Apple devices include privacy features that can change how supported internet traffic is handled and make router VPN testing more difficult.

Limit IP Address Tracking

To temporarily disable Limit IP Address Tracking for your FlashRouter WiFi network:

  1. Open Settings.
  2. Select Wi-Fi.
  3. Tap the information button next to the FlashRouter WiFi network.
  4. Find Limit IP Address Tracking.
  5. Turn it Off.
  6. Disconnect from WiFi and reconnect.
  7. Test the connection again.

This setting is configured per WiFi network, so make sure you are changing it for the FlashRouter network being tested.

iCloud Private Relay

iCloud Private Relay can also alter IP address visibility for supported traffic.

For troubleshooting:

  1. Open Settings.
  2. Tap your Apple Account/name.
  3. Select iCloud.
  4. Select Private Relay.
  5. Temporarily turn Private Relay Off.
  6. Reconnect to the FlashRouter.
  7. Test the IP address and connection again.

These settings can be restored after testing.

Android: Check Private DNS and Always-On VPN

Android devices can have DNS and VPN settings that operate independently of the router.

Private DNS

Android Private DNS can send DNS requests to a selected DNS provider instead of relying solely on the DNS configuration supplied by the router.

If you are troubleshooting DNS, website access, streaming, filtering, or location behavior:

  1. Open Settings.
  2. Select Network & internet.
  3. Select Private DNS.
  4. Temporarily select Off.
  5. Save the setting.
  6. Reconnect to the FlashRouter WiFi.
  7. Test again.

Android menus vary by manufacturer and Android version. Search the device Settings for Private DNS if necessary.

Always-On VPN

An Android VPN application can be configured to automatically reconnect even after you believe the VPN has been disconnected.

  1. Open Settings.
  2. Select Network & internet.
  3. Select VPN.
  4. Select the configured VPN.
  5. Disable Always-on VPN while testing.
  6. Check whether Block connections without VPN is enabled and temporarily disable it if necessary for testing.

Then reconnect to the FlashRouter and test the router VPN again.

Check Antivirus, Firewall, Browser, and Work Security Settings

If the problem affects a computer or only occurs in one browser, check for software that modifies network traffic directly on the device.

Antivirus and Internet Security Software

Security applications may include network features such as:

  • Web Protection.
  • Safe Browsing or Secure Web.
  • Network Protection.
  • DNS Protection.
  • HTTPS scanning.
  • Tracking protection.
  • Built-in VPN services.
  • Firewall controls.

Temporarily disable the relevant network protection feature and test again. You do not normally need to disable the entire antivirus product.

Third-Party Firewalls

A third-party firewall can block applications, DNS requests, VPN-related traffic, or specific network interfaces.

Temporarily disable the firewall and test the connection. If the problem disappears, re-enable the firewall and review its network rules.

Browser VPN, Proxy, and Secure DNS

Browsers and browser extensions can also use their own:

  • VPN services.
  • Proxy connections.
  • Secure DNS or DNS-over-HTTPS.
  • Privacy or filtering extensions.
  • Location-changing extensions.

If the problem occurs only in one browser, test another browser without extensions or custom networking settings.

Work and Corporate Devices

Company-managed computers and mobile devices may use corporate VPN clients, DNS filtering, web filtering, endpoint security, device-management profiles, or zero-trust networking software.

These systems may intentionally override the local router’s network behavior.

If a personal device works correctly on the same FlashRouter while a company-managed device does not, the company security configuration may be responsible.

Run a Clean Router VPN Test

For the cleanest test, temporarily remove device-level networking variables and let the FlashRouter VPN handle the connection.

  • FlashRouter VPN: On
  • Device VPN: Off
  • iCloud Private Relay: Off while testing
  • Limit IP Address Tracking: Off while testing
  • Android Private DNS/custom DNS: Off while testing
  • Always-On VPN: Off while testing
  • Third-party network filtering: Off while testing

Then:

  1. Disconnect the affected device from WiFi.
  2. Reconnect it to the FlashRouter.
  3. Open a fresh private/incognito browser window.
  4. Check the device’s public IP address and location.
  5. Compare the result with another device connected to the same FlashRouter.

If the second device shows the correct VPN IP but the affected device does not, continue troubleshooting settings or software on the affected device.

If all devices show the same incorrect IP address or all devices fail to use the VPN, continue with router-level VPN troubleshooting.

Privacy Hero VPN Connected but Device Still Shows the Wrong IP?

Privacy Hero provides device-level VPN controls. Make sure the affected device is actually assigned to use the VPN.

  1. Open app.privacyhero.com.
  2. Open the Devices section.
  3. Select the affected device.
  4. Confirm VPN protection is enabled for that device.
  5. Disconnect any VPN application running directly on the device.
  6. Test the public IP address again.

If other Privacy Hero devices show the correct VPN IP and only one device remains incorrect, continue with the device-level checks above.


Related FlashRouters Guides

  • Should I Be Using My Computer, Phone, or Tablet VPN App While Connected to the FlashRouter?
  • What Is a DNS Leak and How Can I Prevent a DNS Leak in My Router?
  • FlashRouters VPN FAQs
  • FlashRouters Router Troubleshooting
  • Privacy Hero VPN Kill Switch: No Internet or WiFi Troubleshooting
  • Privacy Hero NordVPN Not Connecting or Showing Timeout Errors
  • Privacy Hero VPN Kill Switch Setup

Windscribe WireGuard Setup

TeamFlashRouters · Oct 13, 2021 ·

Preparing for Windscribe WireGuard Setup

Verify your Windscribe login information

If you are not already a Windscribe user Sign Up Now.

Log in to your account on the Windscribe website.

Windscribe Login

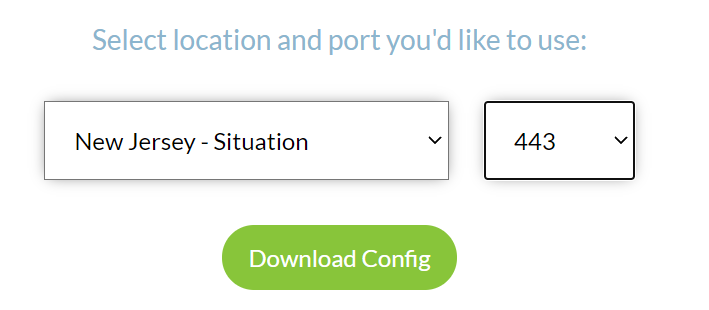
Go to the Windscribe WireGuard config generator page and select the Server location and Port you would like to use. Click Download Config.

Windscribe Wireguard select server location

Open the .conf file that is downloaded using Notepad in Windows or TextEdit in Mac.

DD-WRT Router Setup for Windscribe WireGuard

Navigate to Setup > Tunnels 

Enter Winscribe WireGuard settings

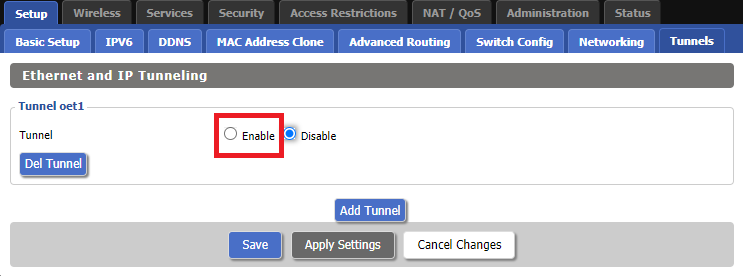
1. Click Add Tunnel.

2. Set Tunnel to Enable.

Setup - Tunnel - Enable Tunnel

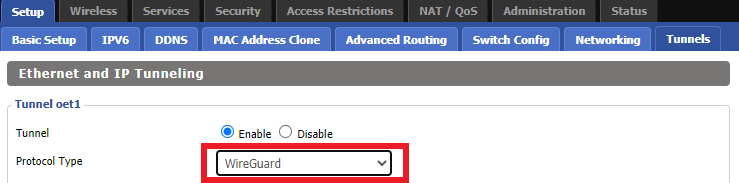
3. Select Wireguard from the dropdown.

Setup - Tunnel - Select Wireguard

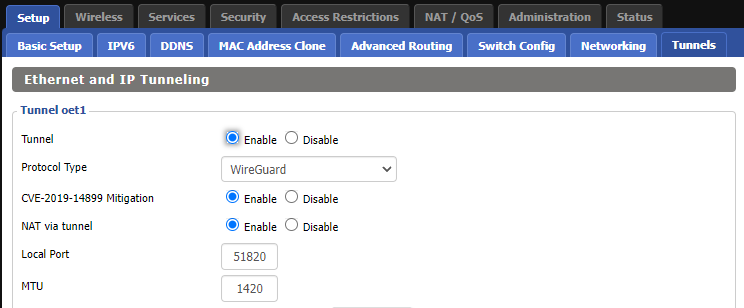
3. Set CVE-2019-14899 Mitigation to Enable. Set NAT via Tunnel to Enable. Set Local Port to 51820. Set MTU to 1420.

Windscribe Wireguard Basic Settings

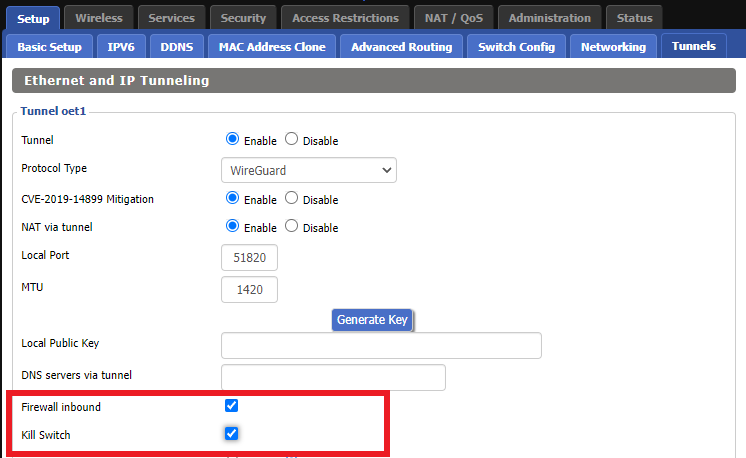
4. Check Firewall inbound and Kill Switch.

Windscribe Wireguard enable Firewall and Kill Switch

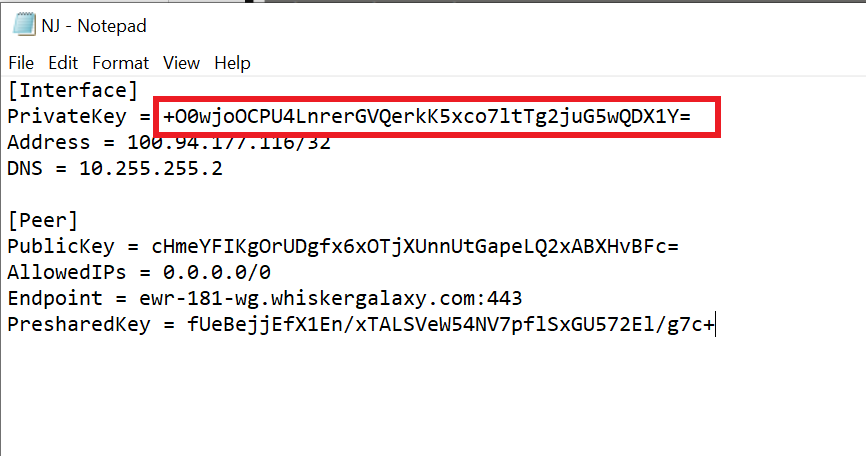
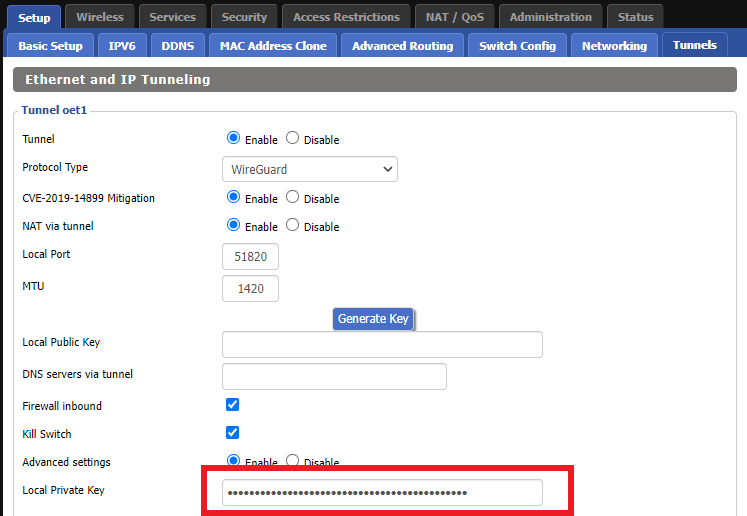
5. Set Advanced Settings to Enable and copy the PrivateKey from the .conf file and paste it into the Local Private Key field.

Windscribe Wireguard conf file PrivateKey
Windscribe Wireguard Local Private Key

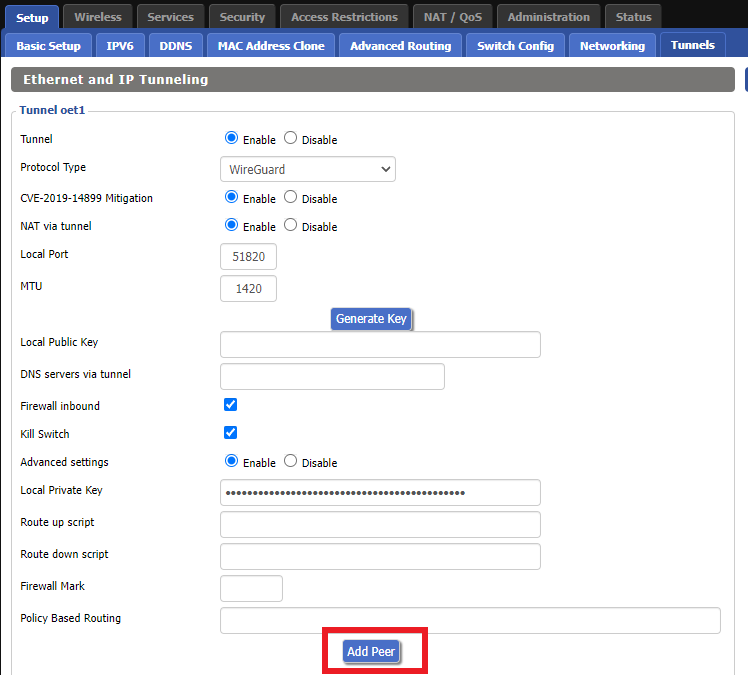
6. Click Add Peer.

Windscribe Wireguard Add Peer

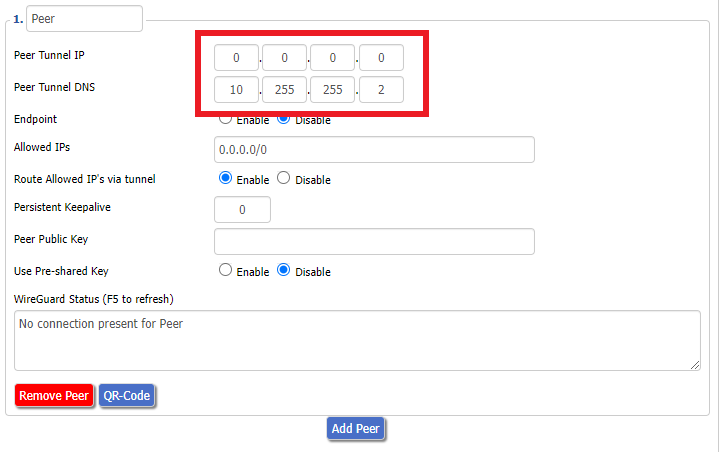
7. Set Peer Tunnel IP to 0.0.0.0. Set Peer Tunnel DNS to the DNS found in the .conf file.

Windscribe Wireguard Peer Tunnel IP and DNS

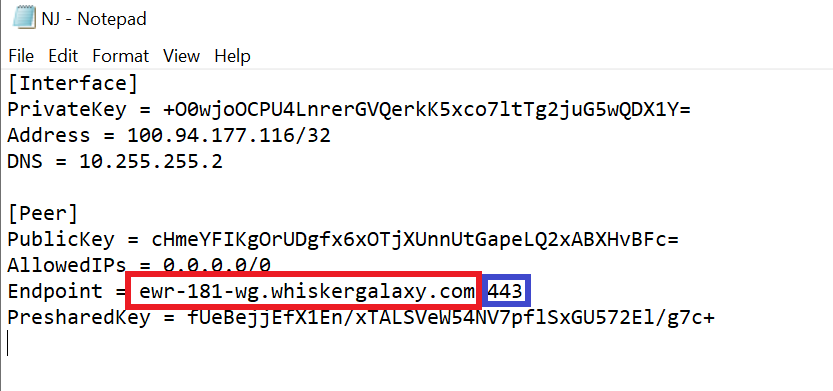
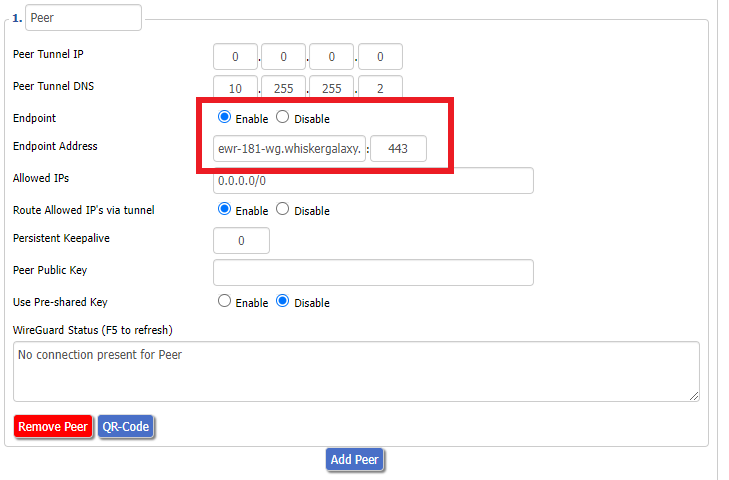
8. Set Endpoint to Enable. Copy and Paste the Endpoint from the .conf file and paste it into the Endpoint Address field. Enter the same Port that appears next to the Endpoint.

Windscribe Wireguard conf file Endpoint
Windscribe Wireguard paste Endpoint

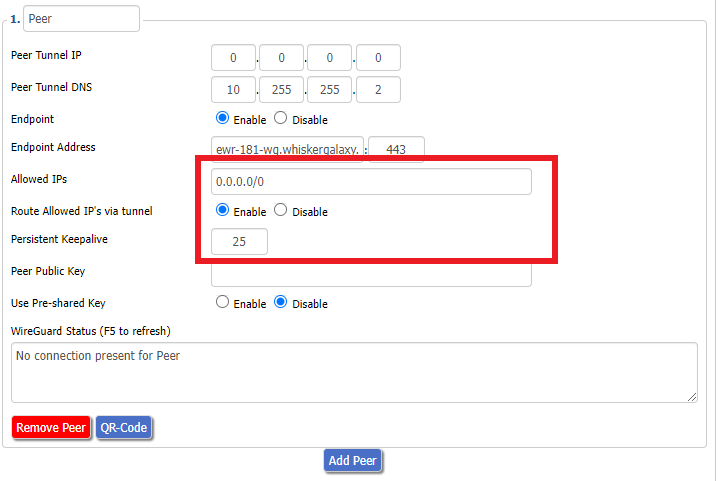
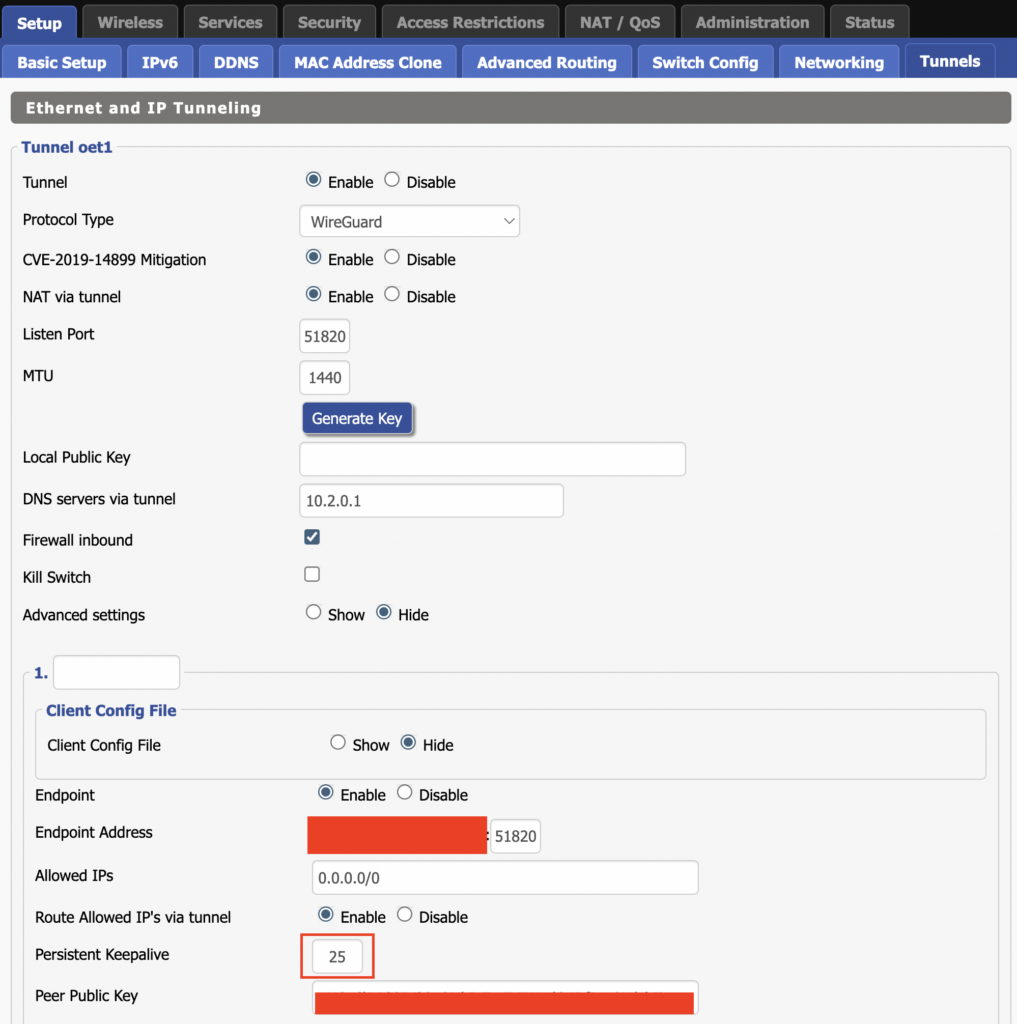
9. Leave Allowed IPs as 0.0.0.0/0. Set Router Allowed IP’s via tunnel to Enable. Set Persistent Keep Alive to 25.

Windscribe Wireguard settings

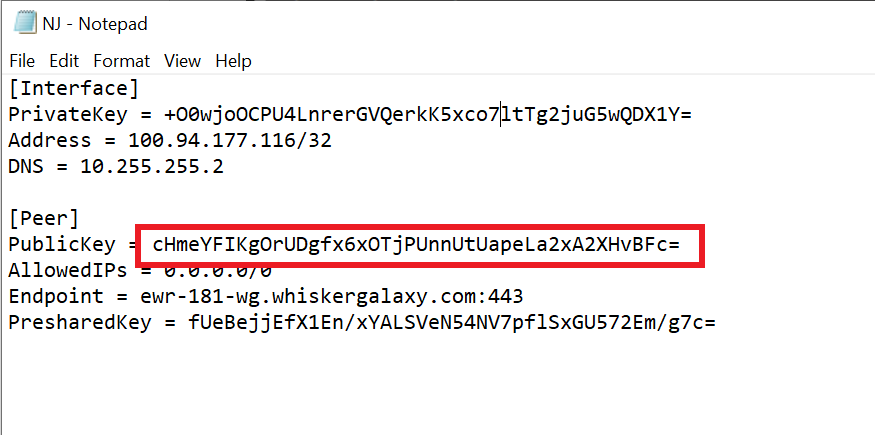
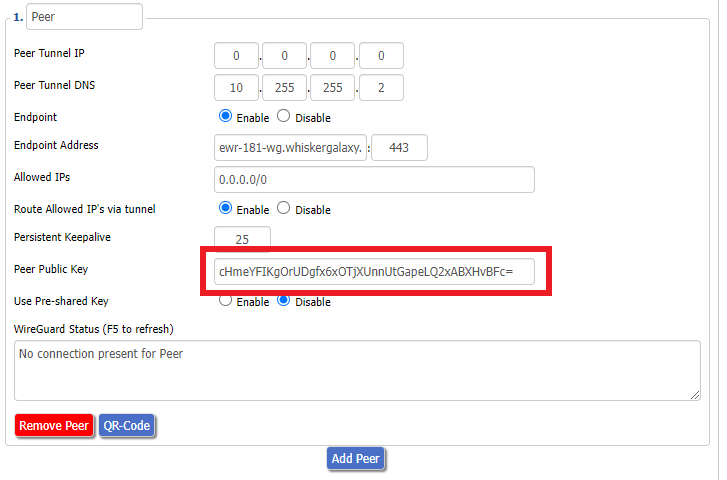
10. Copy and Paste the PublicKey from the .conf file and paste it into the Peer Public Key field.

Windscribe Wireguard conf file PublicKey
Windscribe Wireguard Peer Public Key

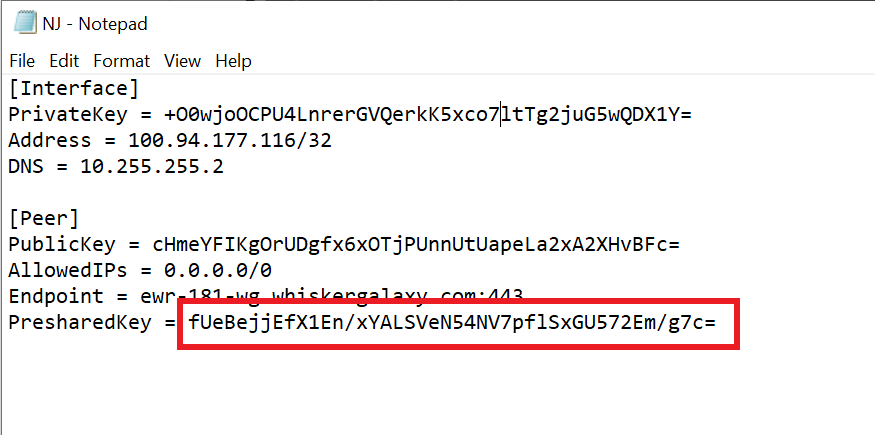
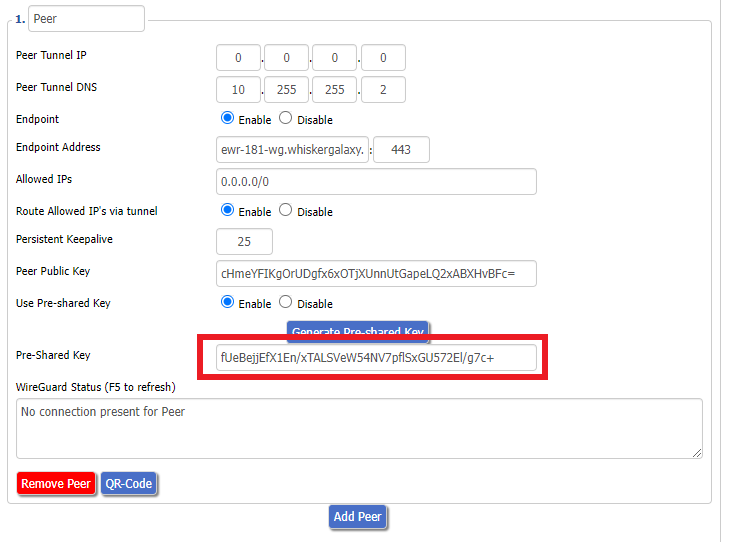
11. Set Use Pre-shared Key to Enable. Copy and Paste the Presharedkey from the .conf file and paste it into the Pre-Shared Key field.

Windscribe Wireguard conf file PresharedKey
Windscribe Wireguard Pre-shared Key

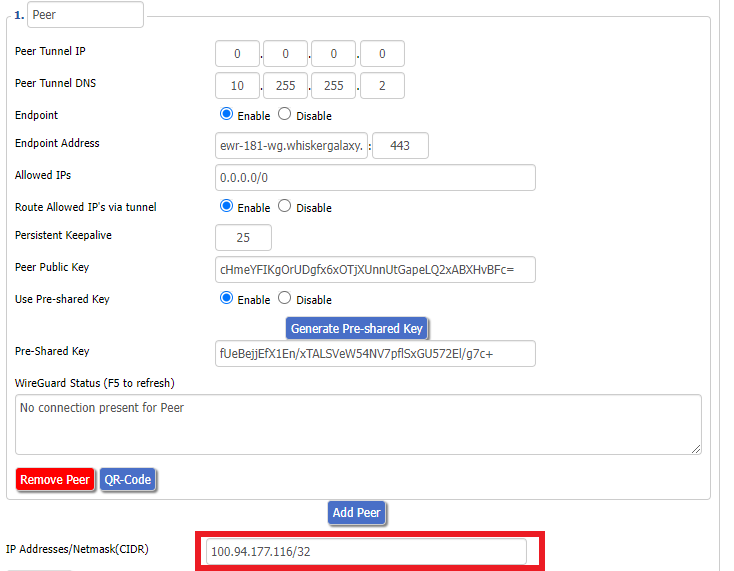
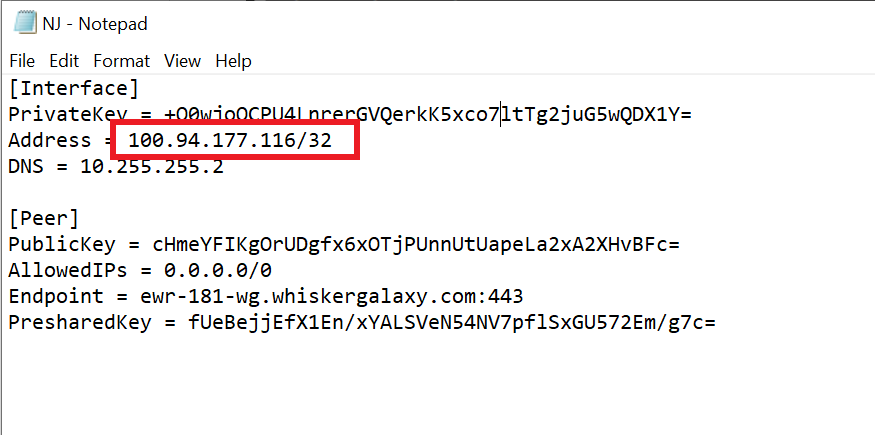
12. Copy the Address from the .conf file and paste it into the IP Addresses/Netmask(CIDR) field.

Windscribe Wireguard IP Address
Windscribe Wireguard conf file Address

Certain DD-WRT builds will show two separate fields here: IP Address and Subnet Mask. If that is the case set the IP Address field to the Address without the /32 added and set the Subnet Mask to 255.255.255.255

21. At the bottom of the page click Save and then click Apply Settings.

Verify a successful Winscribe connection

Navigate to Setup > Tunnels

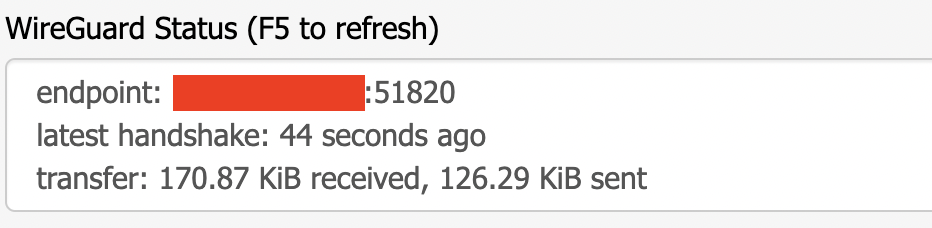
  1. You should Endpoint, Latest handshake, and Transfer in the WireGuard status area.
  2. Visit whatismyipaddress.com to verify your status as using Winscribe.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

ProtonVPN WireGuard Setup

TeamFlashRouters · Jun 15, 2022 ·

Preparing for ProtonVPN WireGuard Setup

Verify your ProtonVPN login information

If you are not already a ProtonVPN user Sign Up Now.

Log in to your account on the ProtonVPN website.

ProtonVPN Account login

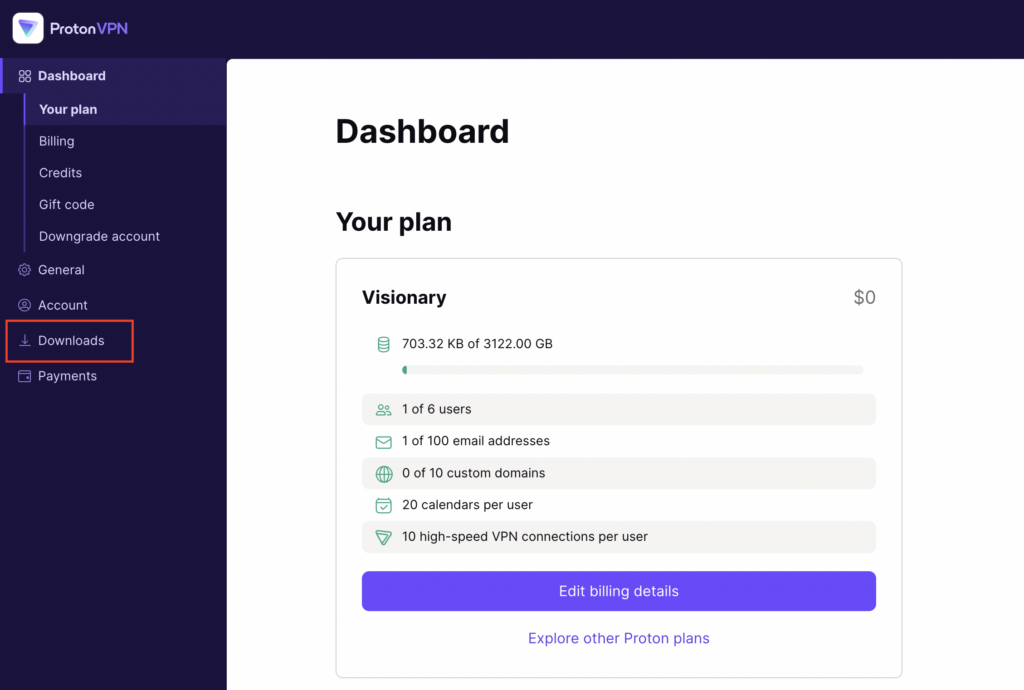
1. On the left hand side select Downloads.

ProtonVPN Downloads

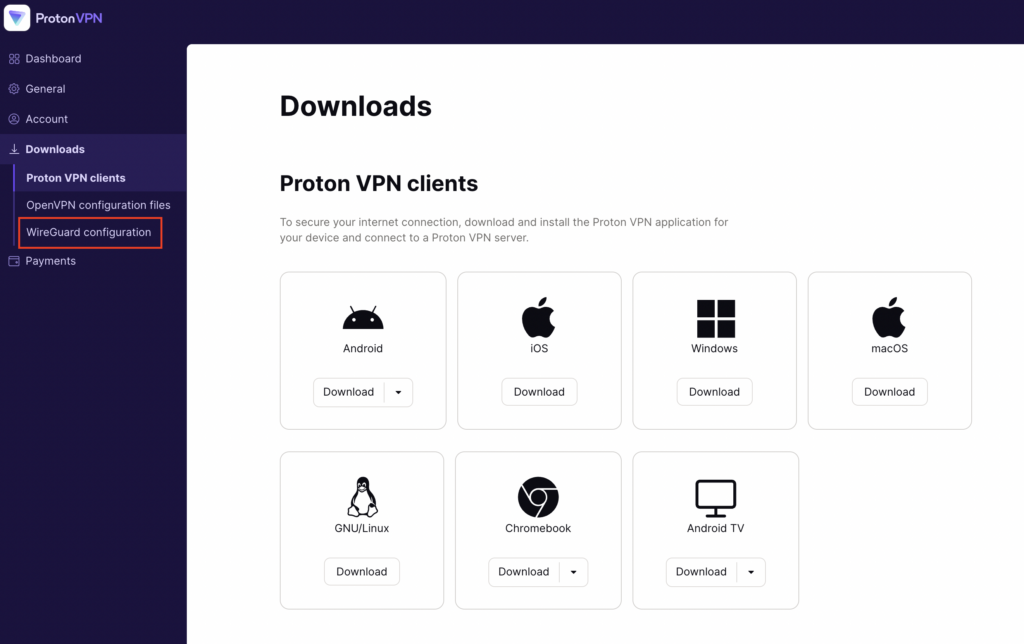
2. Then select WireGuard Configuration.

ProtonVPN WireGuard Configuration

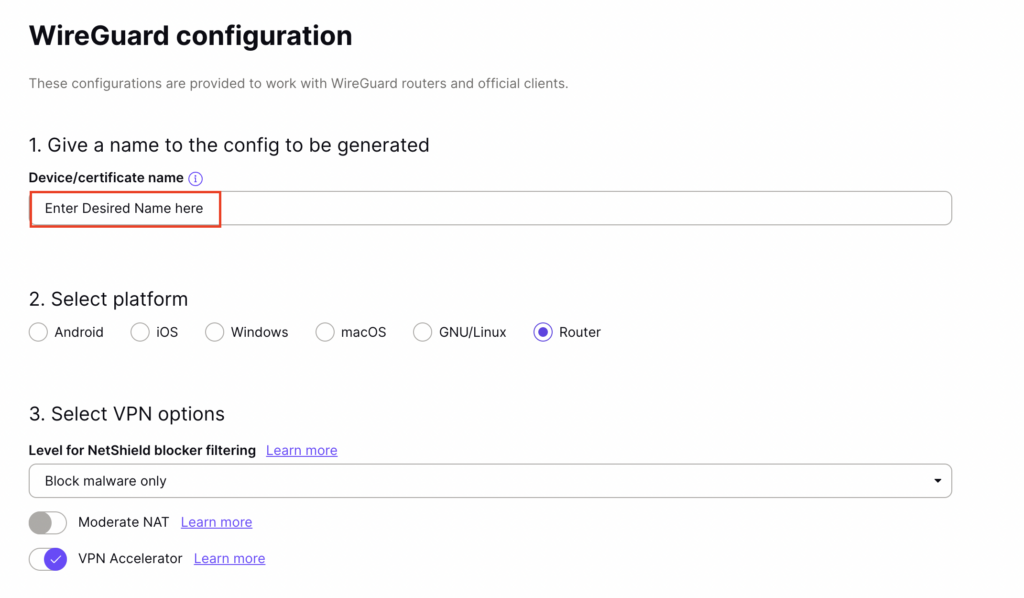
3. Enter the Device Name to assign the FlashRouter to identify it among your ProtonVPN connections.

ProtonVPN WireGuard Desired Name

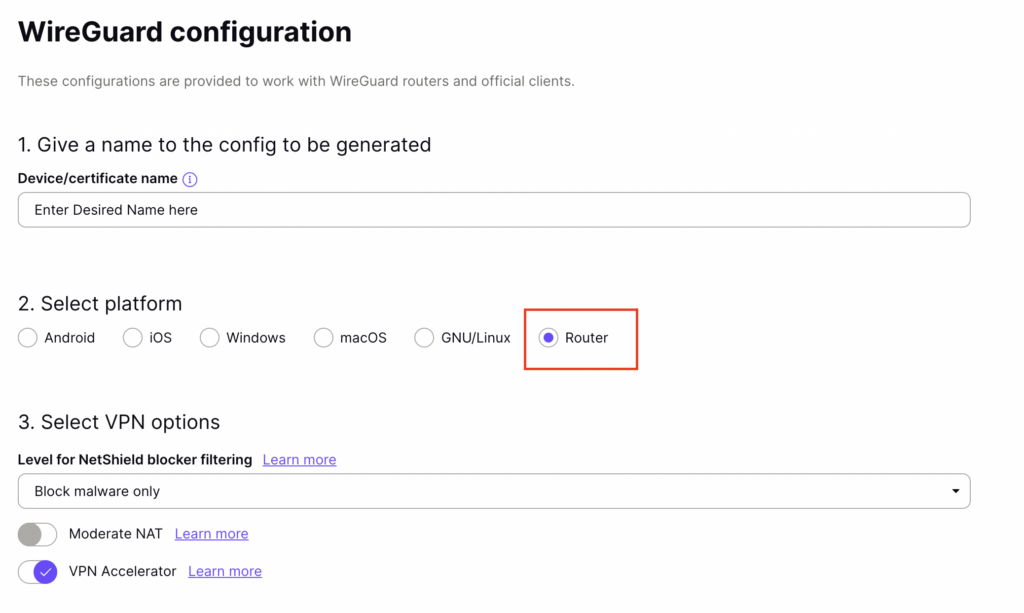
4. Set the Device platform as Router.

ProtonVPN WireGuard select Router

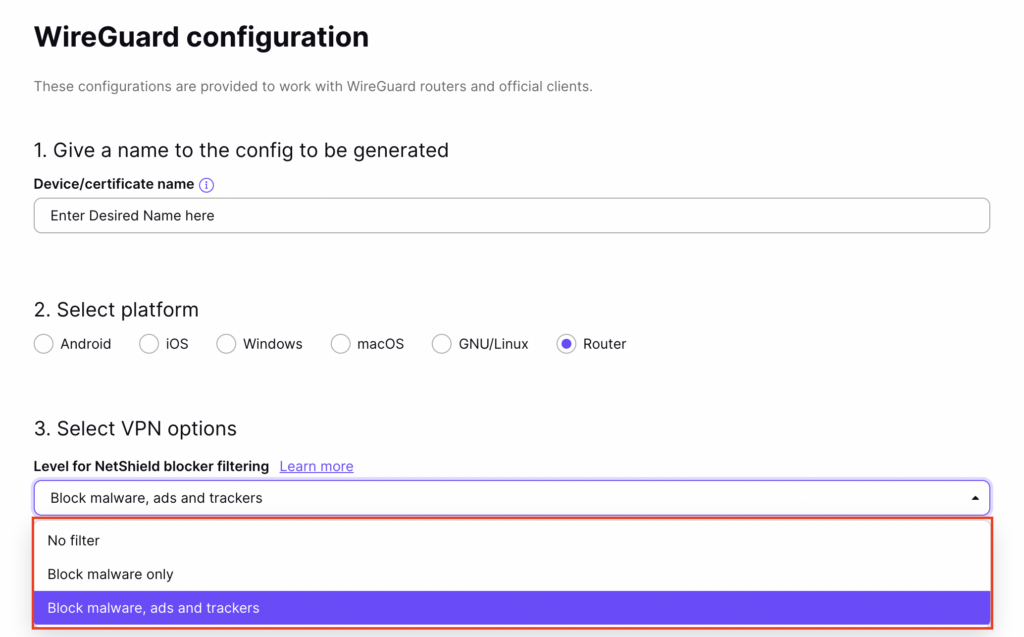
5. Select the VPN Options that you would like to connect with.

ProtonVPN WireGuard VPN Options

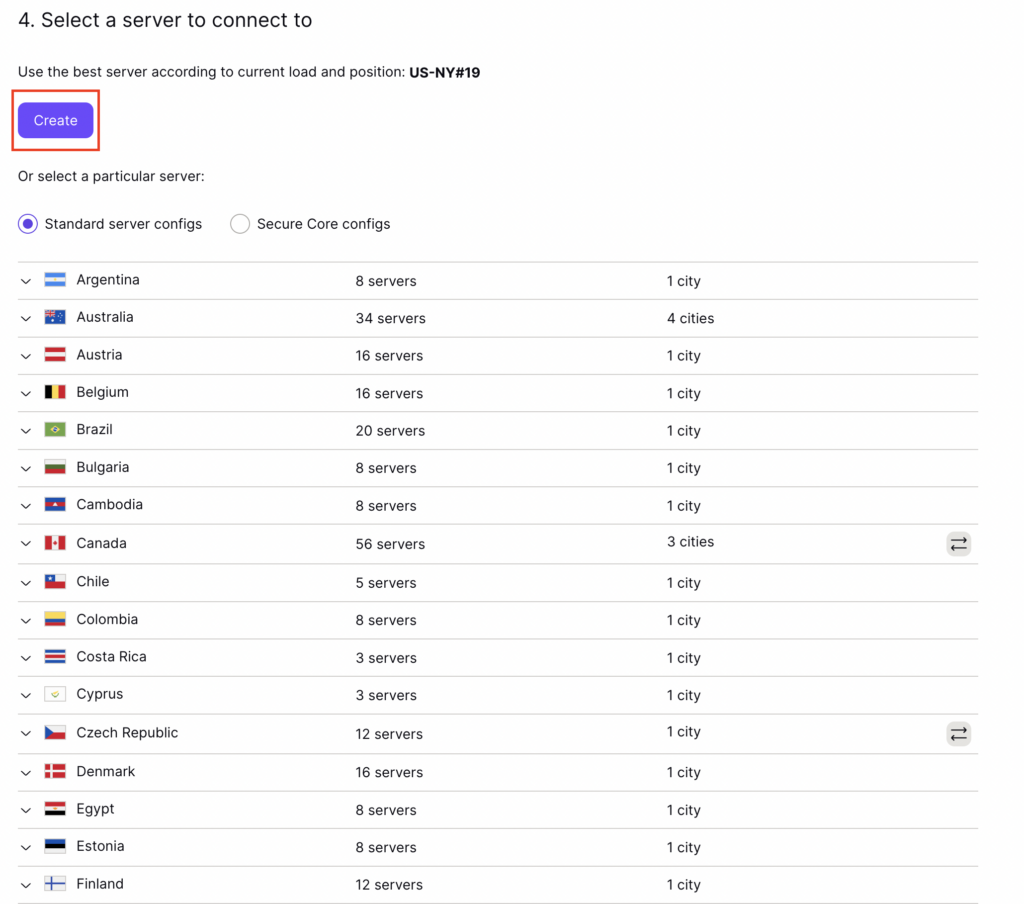
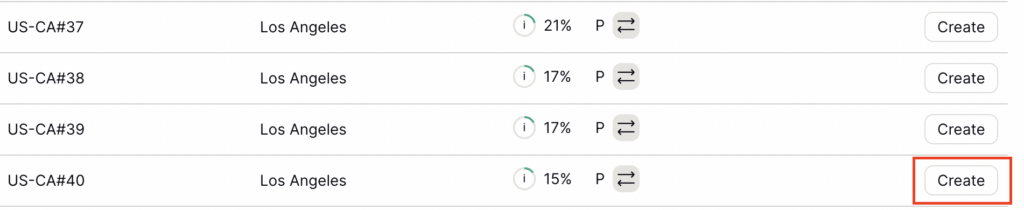
6. ProtonVPN will recommend the ideal server for you to connect to based on your location. Click Create or scroll down and select the server you wish to connect to and click Create next to the server number.

ProtonVPN WireGuard select server
ProtonVPN WireGuard select servers

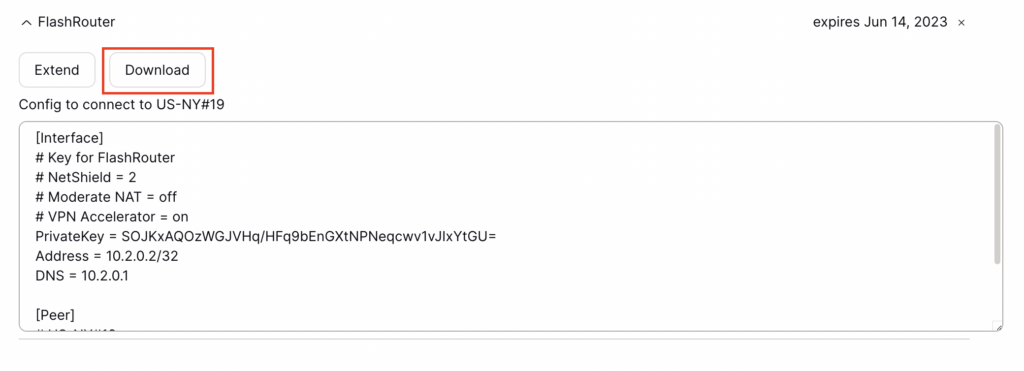
7. Click Download to download the .conf file of the server you selected.

ProtonVPN WireGuard download configuration

DD-WRT Router Setup for ProtonVPN WireGuard

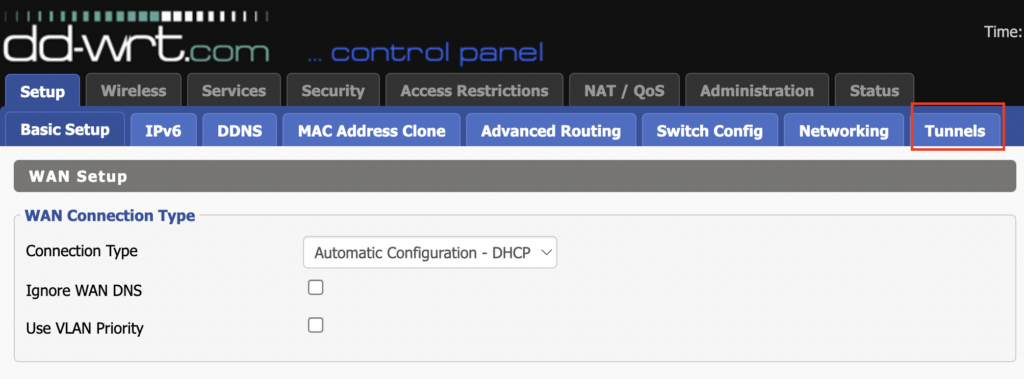
Navigate to Setup > Tunnels 

ProtonVPN WireGuard DD-WRT Tunnels

Enter ProtonVPN WireGuard settings

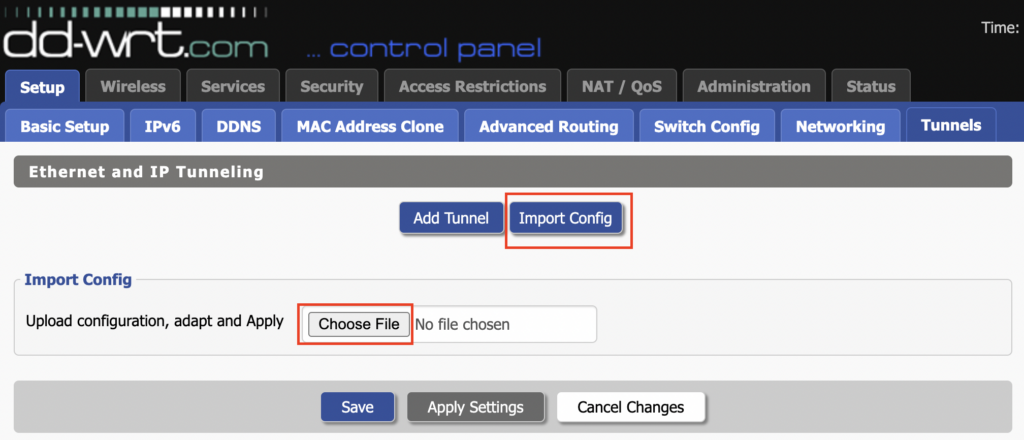
1. Click Import Config and then select Choose file. Select the .conf file that was downloaded earlier.

ProtonVPN WireGuard Import Config and Choose File

2. All settings will be loaded into the DD-WRT firmware the only field that needs to be adjusted is setting Persistent Keepalive to 25.

ProtonVPN WireGuard Persistent Keep Alive

3. Click Apply Settings at the bottom of the page.

4. After 30 seconds or so refresh the page until you see the WireGuard Status on the page is populated as seen below.

ProtonVPN WireGuard Status

Verify a successful ProtonVPN connection

Navigate to Setup > Tunnels

  1. You should Endpoint, Latest handshake, and Transfer in the WireGuard status area.
  2. Visit whatismyipaddress.com to verify your status as using ProtonVPN.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.

Troubleshoot Here

Hotspot Shield Manual OpenVPN Setup

TeamFlashRouters · Jul 15, 2020 ·

Preparing for Manual Hotspot Shield Setup

Obtain your Hotspot Shield OpenVPN Information

If you are not already a Hotspot Shield user Sign Up Now.

1. Log in to your account on the Hotspot Shield website.

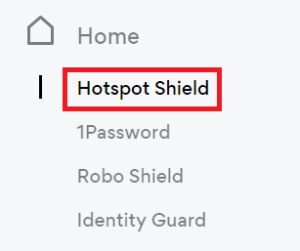
2. Click Hotspot Shield on the left side navigation.

Hotspot Shield - Website Admin

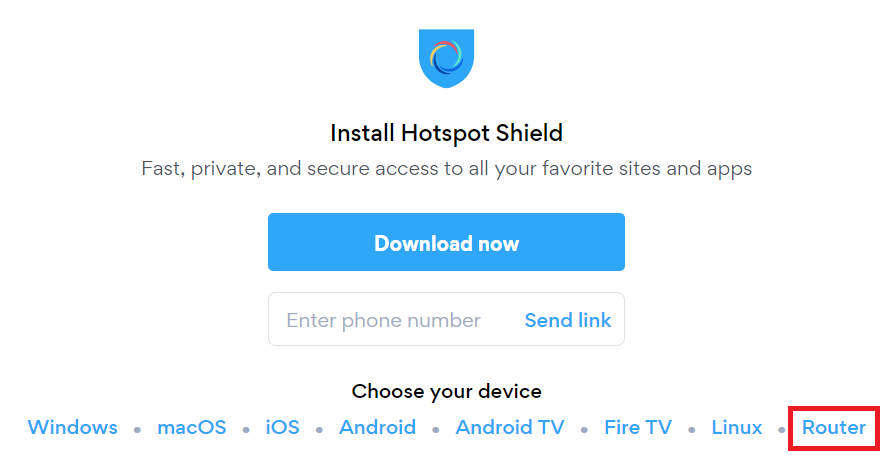
3. Under Choose your device click Router.

Hotspot Shield - Select Router

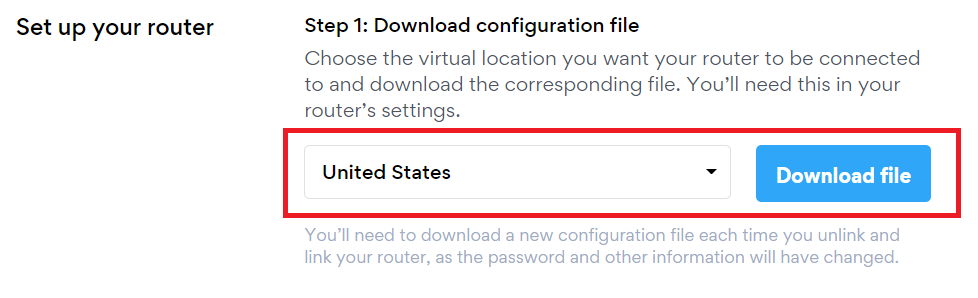
4. In the Set up your router section Select your desired virtual location and then click Download file.

Open the file that was downloaded with NotePad++ for Windows or TextEdit for Apple. You only need the <cert> and <key> from the .ovpn file. All Hotspot Shield servers have different keys and certificates.

Hotspot Shield - Download Configuration File

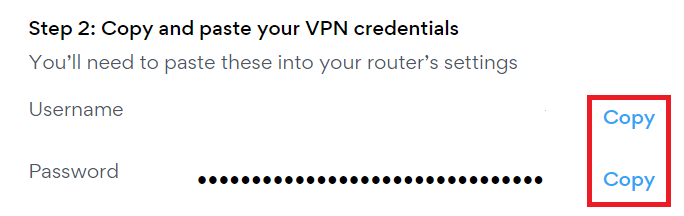
5. Copy the VPN Username, and Password that appear under Step 2 to a notepad, you will need this information later in the setup process.

Hotspot Shield - OpenVPN username and password

DD-WRT Router Setup for Hotspot Shield

Navigate to Services > VPN

Enter Hotspot Shield settings

OpenVPN Client

Start OpenVPN Client

If you wish to disable your VPN connection simply set this to Disable at any time and click Apply Settings.

Server IP/Name

At the top of the .ovpn file you downloaded above, there is a line e.g.:
remote universitycalendar.us 8041
universitycalendar.us is your Hotspot Shield server name. Enter the server name in this field.

Port

8041

Tunnel Device

TUN

Tunnel Protocol

UDP

Encryption cipher

AES-128-CBC

Hash Algorithm

SHA256

User Pass Authentication

Enable

Username

Enter the Username you obtained in your Hotspot Shield account.

Password

Enter the Password you obtained in your Hotspot Shield account.

Advanced Options

Enable

TLS Cipher

None

LZO Compression

No

NAT

Enable

Firewall Protection

Enable

Additional Config

resolv-retry infinite
remote-random
nobind
tun-mtu 1500
tun-mtu-extra 32
mssfix 1450
persist-key
persist-tun
ping 15
ping-restart 0
reneg-sec 0
remote-cert-tls server

Policy Based Routing

This field can be used for split VPN and Dual Gateway routing.

CA Cert

—–BEGIN CERTIFICATE—–
MIIFazCCA1OgAwIBAgIRAIIQz7DSQONZRGPgu2OCiwAwDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTUwNjA0MTEwNDM4
WhcNMzUwNjA0MTEwNDM4WjBPMQswCQYDVQQGEwJVUzEpMCcGA1UEChMgSW50ZXJu
ZXQgU2VjdXJpdHkgUmVzZWFyY2ggR3JvdXAxFTATBgNVBAMTDElTUkcgUm9vdCBY
MTCCAiIwDQYJKoZIhvcNAQEBBQADggIPADCCAgoCggIBAK3oJHP0FDfzm54rVygc
h77ct984kIxuPOZXoHj3dcKi/vVqbvYATyjb3miGbESTtrFj/RQSa78f0uoxmyF+
0TM8ukj13Xnfs7j/EvEhmkvBioZxaUpmZmyPfjxwv60pIgbz5MDmgK7iS4+3mX6U
A5/TR5d8mUgjU+g4rk8Kb4Mu0UlXjIB0ttov0DiNewNwIRt18jA8+o+u3dpjq+sW
T8KOEUt+zwvo/7V3LvSye0rgTBIlDHCNAymg4VMk7BPZ7hm/ELNKjD+Jo2FR3qyH
B5T0Y3HsLuJvW5iB4YlcNHlsdu87kGJ55tukmi8mxdAQ4Q7e2RCOFvu396j3x+UC
B5iPNgiV5+I3lg02dZ77DnKxHZu8A/lJBdiB3QW0KtZB6awBdpUKD9jf1b0SHzUv
KBds0pjBqAlkd25HN7rOrFleaJ1/ctaJxQZBKT5ZPt0m9STJEadao0xAH0ahmbWn
OlFuhjuefXKnEgV4We0+UXgVCwOPjdAvBbI+e0ocS3MFEvzG6uBQE3xDk3SzynTn
jh8BCNAw1FtxNrQHusEwMFxIt4I7mKZ9YIqioymCzLq9gwQbooMDQaHWBfEbwrbw
qHyGO0aoSCqI3Haadr8faqU9GY/rOPNk3sgrDQoo//fb4hVC1CLQJ13hef4Y53CI
rU7m2Ys6xt0nUW7/vGT1M0NPAgMBAAGjQjBAMA4GA1UdDwEB/wQEAwIBBjAPBgNV
HRMBAf8EBTADAQH/MB0GA1UdDgQWBBR5tFnme7bl5AFzgAiIyBpY9umbbjANBgkq
hkiG9w0BAQsFAAOCAgEAVR9YqbyyqFDQDLHYGmkgJykIrGF1XIpu+ILlaS/V9lZL
ubhzEFnTIZd+50xx+7LSYK05qAvqFyFWhfFQDlnrzuBZ6brJFe+GnY+EgPbk6ZGQ
3BebYhtF8GaV0nxvwuo77x/Py9auJ/GpsMiu/X1+mvoiBOv/2X/qkSsisRcOj/KK
NFtY2PwByVS5uCbMiogziUwthDyC3+6WVwW6LLv3xLfHTjuCvjHIInNzktHCgKQ5
ORAzI4JMPJ+GslWYHb4phowim57iaztXOoJwTdwJx4nLCgdNbOhdjsnvzqvHu7Ur
TkXWStAmzOVyyghqpZXjFaH3pO3JLF+l+/+sKAIuvtd7u+Nxe5AW0wdeRlN8NwdC
jNPElpzVmbUq4JUagEiuTDkHzsxHpFKVK7q4+63SM1N95R1NbdWhscdCb+ZAJzVc
oyi3B43njTOQ5yOf+1CceWxG1bQVs5ZufpsMljq4Ui0/1lvh+wjChP4kqKOJ2qxq
4RgqsahDYVvTH9w7jXbyLeiNdd8XM2w9U/t7y0Ff/9yi0GE44Za4rF2LN9d11TPA
mRGunUHBcnWEvgJBQl9nJEiU0Zsnvgc/ubhPgXRR4Xq37Z0j4r7g1SgEEzwxA57d
emyPxgcYxn/eR44/KJ4EBs+lVDR3veyJm+kXQ99b21/+jh5Xos1AnX5iItreGCc=
—–END CERTIFICATE—–
—–BEGIN CERTIFICATE—–
MIIFjTCCA3WgAwIBAgIRANOxciY0IzLc9AUoUSrsnGowDQYJKoZIhvcNAQELBQAw
TzELMAkGA1UEBhMCVVMxKTAnBgNVBAoTIEludGVybmV0IFNlY3VyaXR5IFJlc2Vh
cmNoIEdyb3VwMRUwEwYDVQQDEwxJU1JHIFJvb3QgWDEwHhcNMTYxMDA2MTU0MzU1
WhcNMjExMDA2MTU0MzU1WjBKMQswCQYDVQQGEwJVUzEWMBQGA1UEChMNTGV0J3Mg
RW5jcnlwdDEjMCEGA1UEAxMaTGV0J3MgRW5jcnlwdCBBdXRob3JpdHkgWDMwggEi
MA0GCSqGSIb3DQEBAQUAA4IBDwAwggEKAoIBAQCc0wzwWuUuR7dyXTeDs2hjMOrX
NSYZJeG9vjXxcJIvt7hLQQWrqZ41CFjssSrEaIcLo+N15Obzp2JxunmBYB/XkZqf
89B4Z3HIaQ6Vkc/+5pnpYDxIzH7KTXcSJJ1HG1rrueweNwAcnKx7pwXqzkrrvUHl
Npi5y/1tPJZo3yMqQpAMhnRnyH+lmrhSYRQTP2XpgofL2/oOVvaGifOFP5eGr7Dc
Gu9rDZUWfcQroGWymQQ2dYBrrErzG5BJeC+ilk8qICUpBMZ0wNAxzY8xOJUWuqgz
uEPxsR/DMH+ieTETPS02+OP88jNquTkxxa/EjQ0dZBYzqvqEKbbUC8DYfcOTAgMB
AAGjggFnMIIBYzAOBgNVHQ8BAf8EBAMCAYYwEgYDVR0TAQH/BAgwBgEB/wIBADBU
BgNVHSAETTBLMAgGBmeBDAECATA/BgsrBgEEAYLfEwEBATAwMC4GCCsGAQUFBwIB
FiJodHRwOi8vY3BzLnJvb3QteDEubGV0c2VuY3J5cHQub3JnMB0GA1UdDgQWBBSo
SmpjBH3duubRObemRWXv86jsoTAzBgNVHR8ELDAqMCigJqAkhiJodHRwOi8vY3Js
LnJvb3QteDEubGV0c2VuY3J5cHQub3JnMHIGCCsGAQUFBwEBBGYwZDAwBggrBgEF
BQcwAYYkaHR0cDovL29jc3Aucm9vdC14MS5sZXRzZW5jcnlwdC5vcmcvMDAGCCsG
AQUFBzAChiRodHRwOi8vY2VydC5yb290LXgxLmxldHNlbmNyeXB0Lm9yZy8wHwYD
VR0jBBgwFoAUebRZ5nu25eQBc4AIiMgaWPbpm24wDQYJKoZIhvcNAQELBQADggIB
ABnPdSA0LTqmRf/Q1eaM2jLonG4bQdEnqOJQ8nCqxOeTRrToEKtwT++36gTSlBGx
A/5dut82jJQ2jxN8RI8L9QFXrWi4xXnA2EqA10yjHiR6H9cj6MFiOnb5In1eWsRM
UM2v3e9tNsCAgBukPHAg1lQh07rvFKm/Bz9BCjaxorALINUfZ9DD64j2igLIxle2
DPxW8dI/F2loHMjXZjqG8RkqZUdoxtID5+90FgsGIfkMpqgRS05f4zPbCEHqCXl1
eO5HyELTgcVlLXXQDgAWnRzut1hFJeczY1tjQQno6f6s+nMydLN26WuU4s3UYvOu
OsUxRlJu7TSRHqDC3lSE5XggVkzdaPkuKGQbGpny+01/47hfXXNB7HntWNZ6N2Vw
p7G6OfY+YQrZwIaQmhrIqJZuigsrbe3W+gdn5ykE9+Ky0VgVUsfxo52mwFYs1JKY
2PGDuWx8M6DlS6qQkvHaRUo0FMd8TsSlbF0/v965qGFKhSDeQoMpYnwcmQilRh/0
ayLThlHLN81gSkJjVrPI0Y8xCVPB4twb1PFUd2fPM3sA1tJ83sZ5v8vgFv2yofKR
PB0t6JzUA81mSqM3kxl5e+IZwhYAyO0OTg3/fs8HqGTNKd9BqoUwSRBzp06JMg5b
rUCGwbCUDI0mxadJ3Bz4WxR6fyNpBK2yAinWEsikxqEt
—–END CERTIFICATE—–

Public Client Cert

In the .ovpn file Copy and Paste all contents in between the <cert> and </cert> lines from your .ovpn file starting and ending with:
—–BEGIN CERTIFICATE—–
…
—–END CERTIFICATE—–

Private Client Key

In the .ovpn file Copy and Paste all contents in between the <key> and </key> lines from your .ovpn file starting and ending with:
—–BEGIN PRIVATE KEY—–
…
—–END PRIVATE KEY—–

CLICK APPLY SETTINGS

Leave all settings not mentioned above as their default setting.

Verify a successful Hotspot Shield connection

Navigate to Status > OpenVPN

  1. You should now see a CONNECTED SUCCESS message.
  2. Visit Hotspot Shield’s website to verify your new IP address and virtual location.
In some cases you may notice that the location is not showing the same location as the server you have input in your router settings; this is because geo tracking tools are often tricked by VPN connections. As long as you see an IP address that is not the same as your normal Internet IP address then you are indeed connected to Hotspot Shield.

Back up your settings

Navigate to Administration > Backup

  1. Click the Backup button.
  2. A file named nvrambak.bin will be saved to your computer.
  3. You can load nvrambak.bin to restore your settings in the event of a reset.

How to change the Hotspot Shield server

  1. Follow the instructions for obtaining the OpenVPN information from above.
  2. Enter the new Server Address in the Server IP/Name field.
  3. Enter the new Username and Password.
  4. Enter the new Public Client Cert and Private Client Key.
  5. Click Apply Settings.

TROUBLESHOOTING

Still having issues? Visit the VPN Troubleshooting section.
Troubleshoot Here
« Previous Page

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer