• Skip to primary navigation
  • Skip to main content
  • Skip to primary sidebar
  • Skip to footer

FlashRouters Support Portal

Prioritizing Privacy

  • SETUP GUIDES
    • Privacy Hero Router Setup Guide
    • ASUS-WRT Router Setup Guide
    • AsusWRT-Merlin Router Setup Guide
    • DD-WRT Router Setup Guide
    • ExpressVPN Router Setup Guide
    • GL.iNet Router Setup Guide
    • Roqos Core Router Setup Guide
  • TROUBLESHOOTING
    • Router Access
    • WiFi Connectivity
    • Internet Connection Issues
    • General VPN Issues
    • DD-WRT Firmware
    • TeamViewer Remote Support
  • FAQs
    • Router FAQs
    • VPN FAQs
    • Warranty and Returns FAQs
    • Sales FAQs
    • Shipping FAQs
    • Service Plan FAQs
  • Show Search
Hide Search

Search Results for: client ghost m

NordVPN Setup for AsusWRT: Token, WireGuard & OpenVPN

TeamFlashRouters · Oct 15, 2025 ·

Set up NordVPN on an ASUS router using AsusWRT VPN Fusion. Supported ASUS firmware offers three different VPN types: NordVPN (access-token integration), WireGuard (downloadable .conf file), and OpenVPN (manual service credentials plus an .ovpn file). Choose the method that matches your needs and your router’s available options.

All configuration is completed directly through your ASUS router’s administration interface using VPN Fusion. Before starting, make sure your router is connected to the internet, your firmware supports VPN Fusion, and you have an active NordVPN subscription.

Before starting, join the ASUS router WiFi or LAN and sign in to http://www.asusrouter.com or your router’s LAN IP (commonly 192.168.50.1). Open VPN > VPN Fusion > Add profile. Router model, firmware, and region affect which VPN types appear. See Access Your AsusWRT Settings.

In This Guide

Choose a VPN Type →NordVPN, WireGuard, or OpenVPNNordVPN Token Setup →Built-in NordLynx integrationWireGuard File Setup →Download and import a .confOpenVPN Setup →Manual credentials and .ovpnDedicated IP Setup →OpenVPN onlyDevices & Troubleshooting →Route devices and verify IP

Which NordVPN Option Should You Choose?

1. NordVPN

NordVPN access token and a country/region dropdown. The built-in ASUS/NordVPN integration is the simplest approach if you only need a country, not an exact server file.

Follow token setup →

2. WireGuard

Import a NordVPN .conf configuration file for a server selected in Nord Account. Useful when you want a downloaded profile for a particular server.

Follow WireGuard setup →

3. OpenVPN

Import a NordVPN .ovpn server file and enter your separate manual service username and password. Also used for NordVPN Dedicated IP.

Follow OpenVPN setup →

Dedicated IP uses OpenVPN only in this guide. Select OpenVPN in VPN Fusion and import your Dedicated IP .ovpn file. Do not use the standard NordVPN token/region dropdown for a Dedicated IP.

Option 1: NordVPN Dropdown — Token-Based NordLynx

Select the NordVPN type inside VPN Fusion. This is the integrated token-based setup and offers a country/region selection, rather than a manually imported server file.

  1. In Nord Account, open NordVPN Access Tokens and complete email/account verification if requested.
  2. Generate an access token, choose an expiry period if NordVPN offers that setting, and copy the token immediately (it may only be displayed once).
  3. On your ASUS router, open VPN > VPN Fusion > Add profile.
  4. Set VPN Type to NordVPN. Name the profile, select your preferred Region, and paste the token.
  5. Choose Apply to all devices if you want it as the default route, or assign only selected devices (see the VPN Fusion guide below).
  6. Click Apply and Enable / Apply all settings, as shown in your firmware, and verify the profile connects.
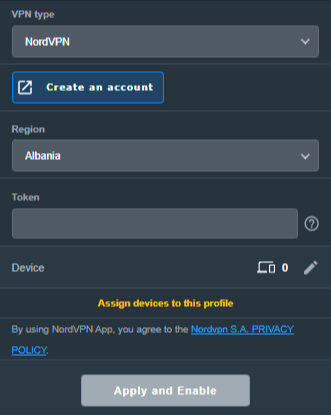
ASUS VPN Fusion NordVPN VPN type with Region and Token fields
Keep: existing ASUS NordVPN region/token form (remove any private token before publishing).

Need a specific server? Use the separate WireGuard file method below or the OpenVPN configuration-file method. Do not expect the token-based country dropdown to accept a .conf or .ovpn file.

Option 2: WireGuard Dropdown — Import a NordVPN .conf File

NordVPN now provides downloadable WireGuard configuration files through its manual server recommendation page. This is different from the built-in NordVPN token option in VPN Fusion.

  1. Sign in to Nord Account and open NordVPN Server Recommendation.
  2. Choose your preferred country and server; use the available filters if you need to narrow the list. Select a currently available server.
  3. Choose Get setup configuration, select WireGuard from the protocol menu, and click Download config. Save the downloaded .conf file.
  4. In your ASUS router settings open VPN > VPN Fusion > Add profile, then set VPN Type to WireGuard (not NordVPN).
  5. Use the ASUS Import configuration / file-import control to select the NordVPN .conf file. Confirm the imported parameters and save the profile.
  6. Choose the target devices or enable the default/all-devices route. Click Apply and Enable, then check the VPN status and your public IP.


WireGuard configuration files may contain a private key. Do not share an actual customer .conf file or publish a screenshot exposing its key material. When changing servers, download/import a different file and choose the desired active profile.

NordVPN’s official instructions: How to download WireGuard and OpenVPN configuration files.

Option 3: OpenVPN Dropdown — Credentials + .ovpn File

OpenVPN requires two separate items: the configuration file for your desired server and NordVPN’s manual service credentials. Your normal Nord Account email/password is not the correct credential pair for this method.

  1. Open NordVPN Manual Service Credentials and copy the service username and service password after any required verification.
  2. Open NordVPN OpenVPN Configuration Files and choose a server/location. Download its UDP .ovpn file, or TCP .ovpn if UDP does not work on your network.
  3. On ASUS, go to VPN > VPN Fusion > Add profile and set VPN Type to OpenVPN.
  4. Enter a connection name, Import .ovpn file, and paste the NordVPN manual service username and password in the corresponding fields.
  5. Choose devices or Apply to all devices, then click Apply and Enable. Confirm VPN Fusion shows a successful connection.
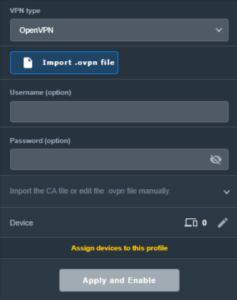
ASUS VPN Fusion OpenVPN VPN type with OVPN import and username password fields
Keep: existing ASUS OpenVPN profile form. New screenshots should use a larger clean capture if available.

Server selection: The location is controlled by the server named in the imported .ovpn file. To switch locations, import another server file or use a separate OpenVPN profile.

NordVPN Dedicated IP — OpenVPN Only

If you have purchased and activated the NordVPN Dedicated IP add-on, use your specific Dedicated IP OpenVPN configuration file. Do not select the ordinary NordVPN token integration or a regular shared server.

  1. In your Nord Account, open the Dedicated IP details and download the assigned server’s OpenVPN UDP or TCP configuration file, following NordVPN Dedicated IP manual configuration instructions.
  2. Open NordVPN Manual Service Credentials and copy the manual username and password.
  3. In ASUS VPN Fusion > Add profile, choose OpenVPN.
  4. Import the Dedicated IP .ovpn file, enter manual service credentials, save, enable, and verify the public IP matches your assigned Dedicated IP.

The Dedicated IP add-on must be active on the NordVPN account. A regular shared-server .ovpn file will not give you the Dedicated IP.

Assign Devices, Verify the VPN, and Troubleshoot

One VPN for everyone, or different VPNs for different devices?

VPN Fusion lets you use a VPN profile as the default connection for all devices or assign specific client devices to different profiles. Some supported ASUS models can maintain one WireGuard tunnel alongside multiple OpenVPN profiles, but the number of simultaneous tunnels is model/firmware dependent; creating multiple profiles does not mean all can be active simultaneously.

For step-by-step device assignments, default routing, profile conflicts, and bypassing the VPN, see How to Use ASUS VPN Fusion and Assign Devices to VPN Profiles. For a dedicated WiFi network with VPN or ISP routing, see ASUS Guest Network VPN / No-VPN Setup.

Verify the IP of the actual device

  1. Confirm your chosen profile shows Connected in VPN Fusion.
  2. Join the ASUS WiFi or LAN using a device that is actually assigned to that VPN profile.
  3. Open NordVPN IP Address Check and compare the public IP/location with the intended server or Dedicated IP.
  4. If the device shows an ISP IP, first check Apply to all devices and the per-device assignments in VPN Fusion.
  5. Disconnect a NordVPN app, Apple iCloud Private Relay, browser VPN/proxy, or other device-level network service during testing. Follow Router VPN Shows Wrong IP? Check Device Settings.

If VPN Fusion will not connect

  1. Temporarily disable the failing profile and confirm the ASUS router works using its normal ISP internet connection.
  2. For NordVPN type, check that the access token is valid and hasn’t expired; regenerate if needed.
  3. For WireGuard, import a fresh .conf from the Nord server recommendation page and make sure the profile is enabled.
  4. For OpenVPN, double-check manual service credentials (not website credentials) and try a different server file or TCP instead of UDP.
  5. Check that device-assignment rules point to the intended active profile, then retest with one clean device.

NordVPN Routers & Offers

Shop NordVPN-Ready FlashRouters

Compare ASUS and Privacy Hero router options and choose the hardware that fits your VPN and network requirements.

Browse NordVPN Routers →

NordVPN Partner Offer

Need NordVPN service? See the current FlashRouters NordVPN promotional offer. Subscription pricing and terms are shown on the offer page.

See NordVPN Offer →

Related AsusWRT Guides

  • ASUS VPN Fusion: Assign Devices and Manage Multiple Profiles
  • ASUS Guest Network: WiFi With or Without a VPN
  • AsusWRT Router Login Guide
  • Router VPN Shows Wrong IP? Device Settings

Upgrade your ASUS router

Explore the Latest WiFi 7 ASUS FlashRouters

Looking for a newer ASUS router? Browse WiFi 7 models available from FlashRouters and compare features to find the right fit for your home or office. VPN Fusion and other features vary by router model and firmware.
Shop ASUS WiFi 7 Routers →

How do I set a Static IP for my device in DD-WRT?

TeamFlashRouters · May 30, 2019 ·

It can be very useful to setup static local IP addresses for devices on your FlashRouter network. By assigning specific IP’s to specific devices you can better control and manage how your network and the internet interacts with each device.

Once you setup a static IP you can set access restrictions, monitor and control bandwidth, as well as bypass a router VPN connection or setup a device specific Kill Switch. Without a static IP assignment you may lose device specific settings when the DHCP lease to the router expires.

Navigate to Services > Services

Set Static IP by Device MAC Address in FlashRouter DD-WRT Settings
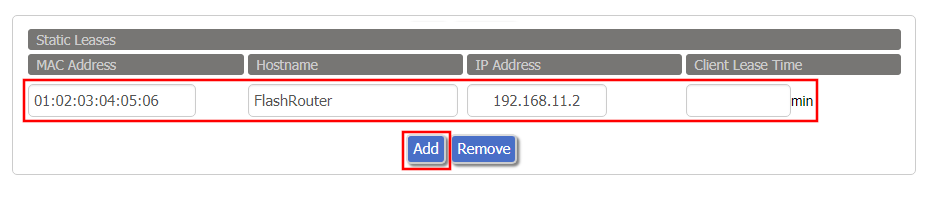
  1. Under Static Leases click Add once.
  2. Fill in the newly appeared fields.
    • MAC Address: Enter the device’s MAC address which can be found on the device itself or on the Status > LAN page.
    • Hostame: Enter a name for the device. Make sure that there are no spaces.
    • IP Address: Enter the desired static IP Address of the device. It should be on the same subnet as the FlashRouter (192.168.11.x)
    • Client Lease Time: Leave this field blank.
  3. Click Apply Settings
  4. Repeat the steps above for each individual static IP address you would like to setup. If you click Add before clicking Apply Settings you will lose the configuration.

If a device has wireless and ethernet capabilities the MAC Addresses will be different for a wireless connection and an ethernet connection. Make sure to set a static IP for both MAC Addresses in this case.

Why is my Time Zone set to Europe/Berlin?

TeamFlashRouters · May 30, 2019 ·

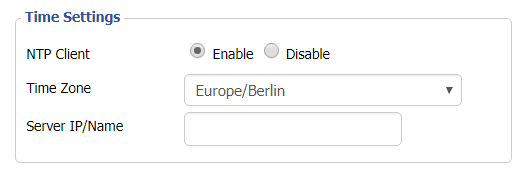
Europe/Berlin is the default Time Zone setting for DD-WRT firmware.

To change this to your location’s actual Time Zone do the following.

Navigate to Setup > Basic Setup

Select your actual Time Zone from the dropdown field. Leave the Server IP/Name field blank.

CLICK APPLY SETTINGS

The network may reboot for a moment. Simply reconnect when it is back up.

Disabling the NTP Client setting will result in the VPN connection not working so we ask that you please leave it enabled at all times.

What are some extra steps I can take to secure my network?

TeamFlashRouters · May 30, 2019 ·

DD-WRT open source firmware removes many firmware vulnerabilities and backdoor access issues that may cause problems in stock firmware. DD-WRT is also updated more frequently than stock firmware, so be sure to always check with the FlashRouter support team to see which DD-WRT build we recommend for the highest level of security for your router at any time.

Aside from avoiding common issues and flaws with stock firmware, DD-WRT give you more control over the firmware settings and allows you to take some extra steps to really lock down your network security. In this article we highlight additional options for WiFi network security and also preventative measures for remote execution attacks.

Wireless MAC Filtering

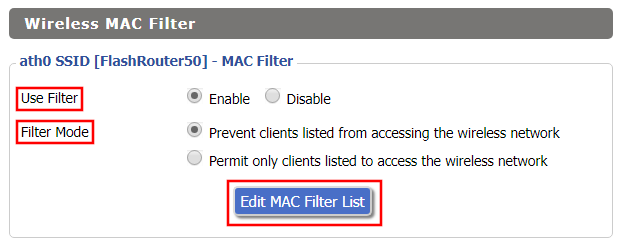
Navigate to Wireless > MAC Filter

Access FlashRouters DD-WRT Admin Enable MAC Filtering
  1. Set Use Filter to Enable.
  2. Select either Prevent or Permit
    • Choose Prevent to add MAC addresses that you don’t want to join your network.
    • Choose Permit to add MAC addresses that you do want to join your network, automatically blocking all others.
  3. Select Edit MAC Filter List.
  4. Add the MAC Address of the wireless devices you want to prevent or permit. Be sure to use the xx:xx:xx:xx:xx:xx format. Hint: You can see a list of connected devices MAC Address by clicking Wireless Client MAC List.
  5. Click Save.
  6. Replicate the steps above for each wireless band.
  7. Click Apply Settings.

Disable Remote Access

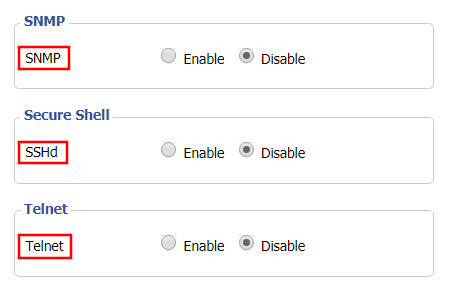
Navigate to Services > Services

Access FlashRouters DD-WRT Admin Settings and Disable Remote Access
  1. Set SNMP to Disable – this setting disables Simple Network Management Protocol, which prevents software from polling your network for information about connected devices.
  2. Set SSHd to Disable – disabling the Secure Shell is a simple way to prevent root access and brute force attacks on your network.
  3. Set Telnet to Disable – Telnet is a less secure version of SSH to manage your local router network via command line.
  4. Click Apply Settings.

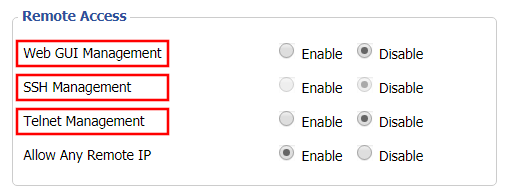
Navigate to Administration > Management

Access FlashRouters DD-WRT Admin Settings and Disable Remote Access 2
  1. Set Web GUI Management to Disable.
  2. Set SSH Management to Disable.
  3. Set Telnet Management to Disable.
  4. Set Allow Any Remote IP to Enable – Even though this setting is set to Enable there is no remote access because Web GUI Management is already set to Disable. 
  5. Click Apply Settings.
« Previous Page

Primary Sidebar

  • Troubleshooting
  • Router Access
  • Internet Connection Issues
  • WiFi Connectivity
  • General VPN Issues
  • TeamViewer Remote Support
  • DD-WRT Firmware
  • Facebook
  • Twitter
  • Instagram
  • Pinterest
  • YouTube

Footer